
CobaltStrikeParser
 sentinel-one/cobaltstrikeparser
Python parser for extracting CobaltStrike Beacon configurations from PE files, memory dumps, and C2 URLs using heuristic XOR decryption and…
binary-analysiscommand-and-controlmalware-analysis+1
1.1k
sentinel-one/cobaltstrikeparserPython parser for extracting CobaltStrike Beacon configurations from PE files, memory dumps, and C2 URLs using heuristic XOR decryption and…
 washi1337/asmresolver
A library for creating, reading and editing PE files and .NET modules.

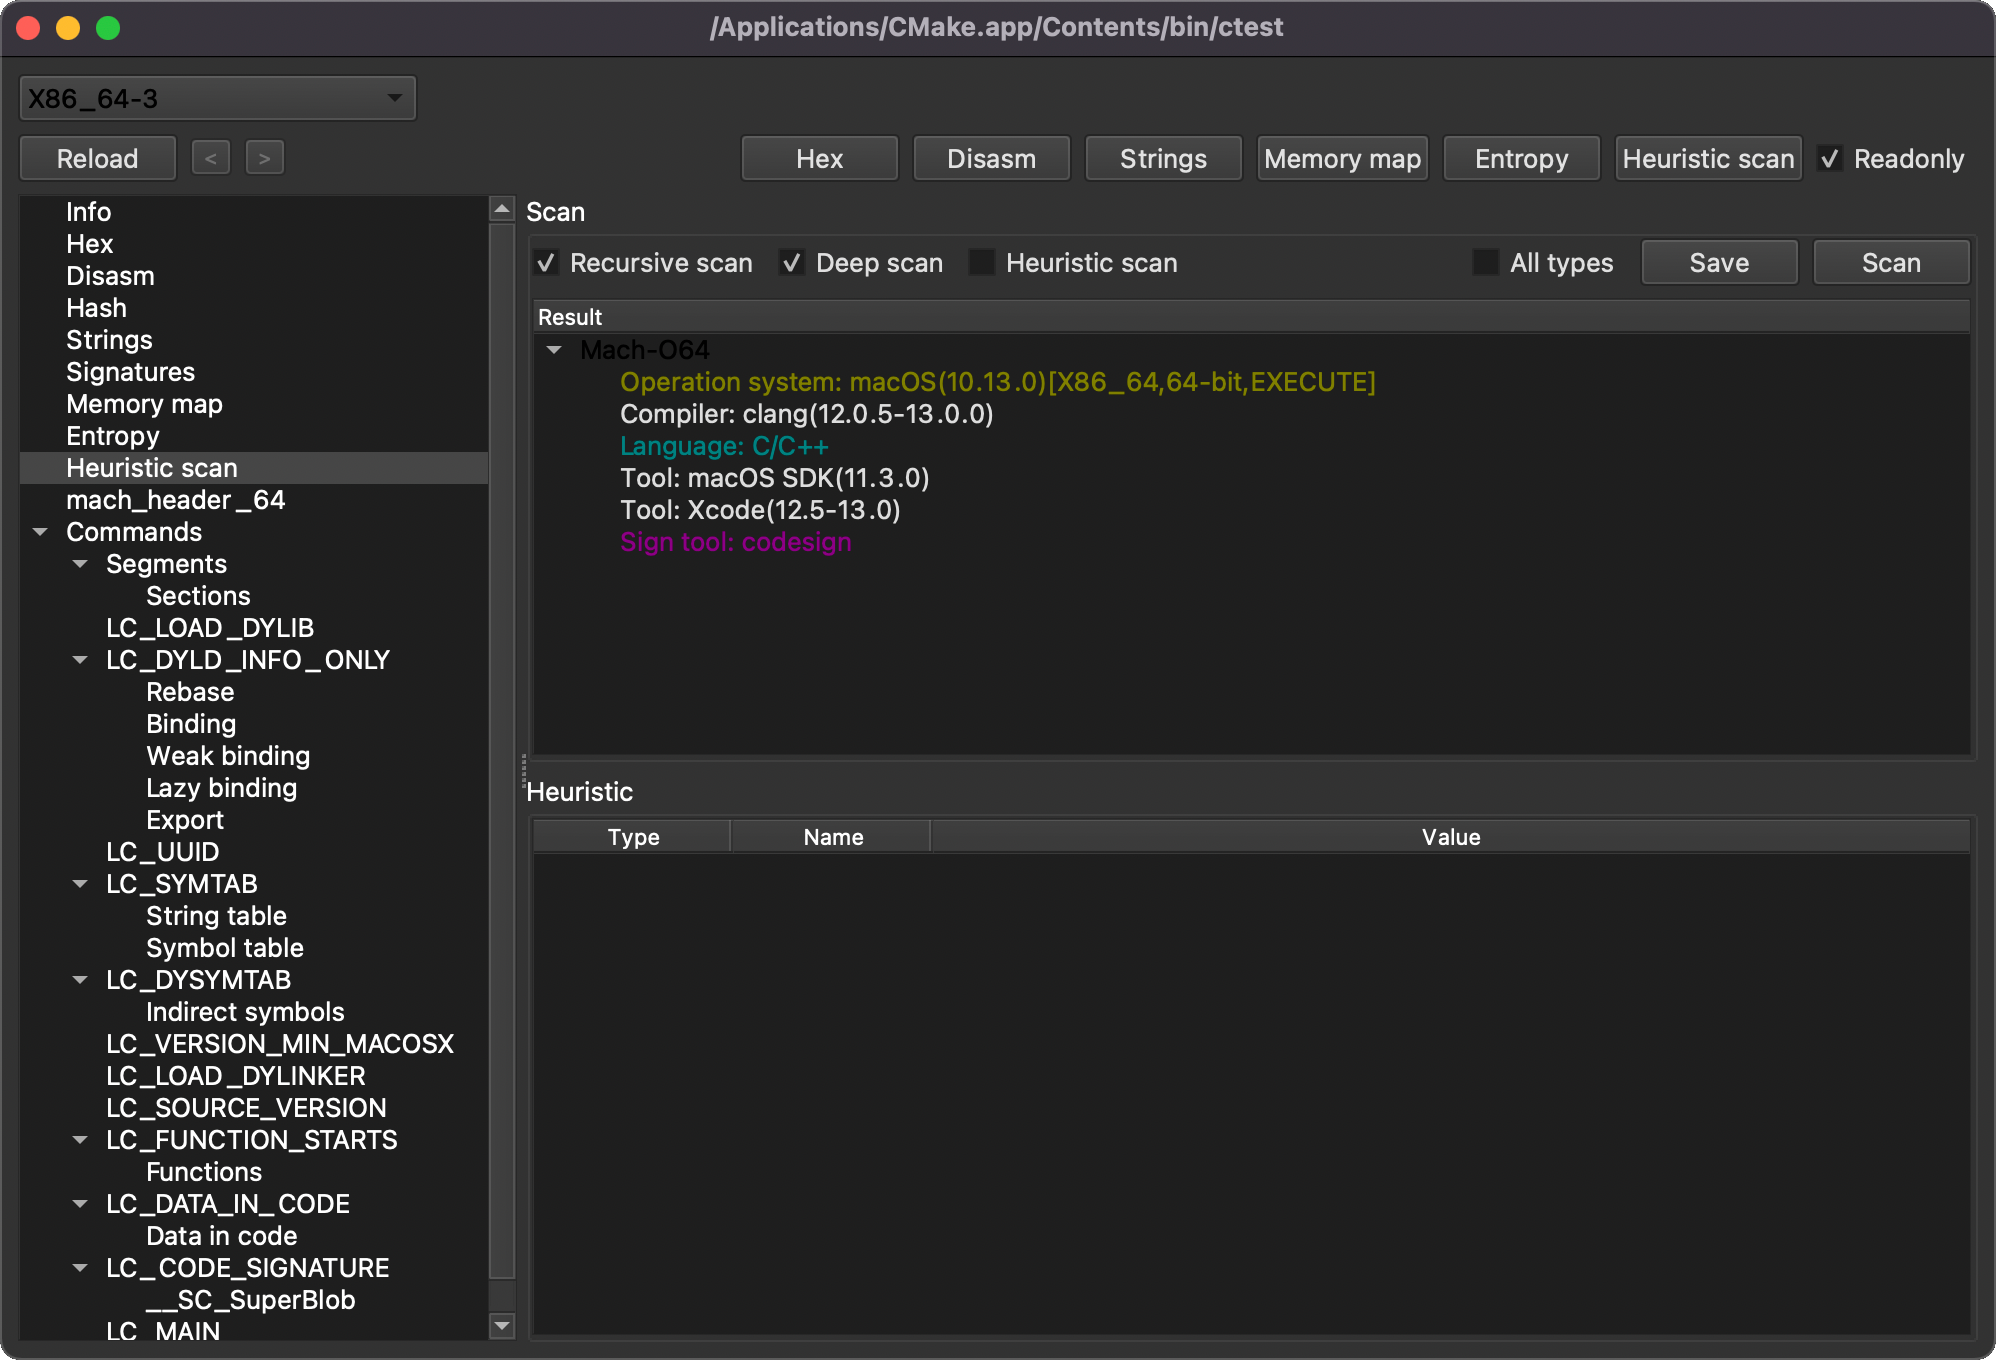 horsicq/xmachoviewer
XMachOViewer is a Mach-O viewer for Windows, Linux and MacOS
 endgameinc/xori
Xori is an automation-ready disassembly and static analysis library for PE32, 32+ and shellcode
 radareorg/r2ai
Radare2 AI plugin using local or remote LLMs for decompilation, function explanation, vulnerability detection, renaming, and scripted reverse…
 mr-un1k0d3r/redteamccode
Red Team C code repo
 mandiant/stringsifter
A machine learning tool that ranks strings based on their relevance for malware analysis.
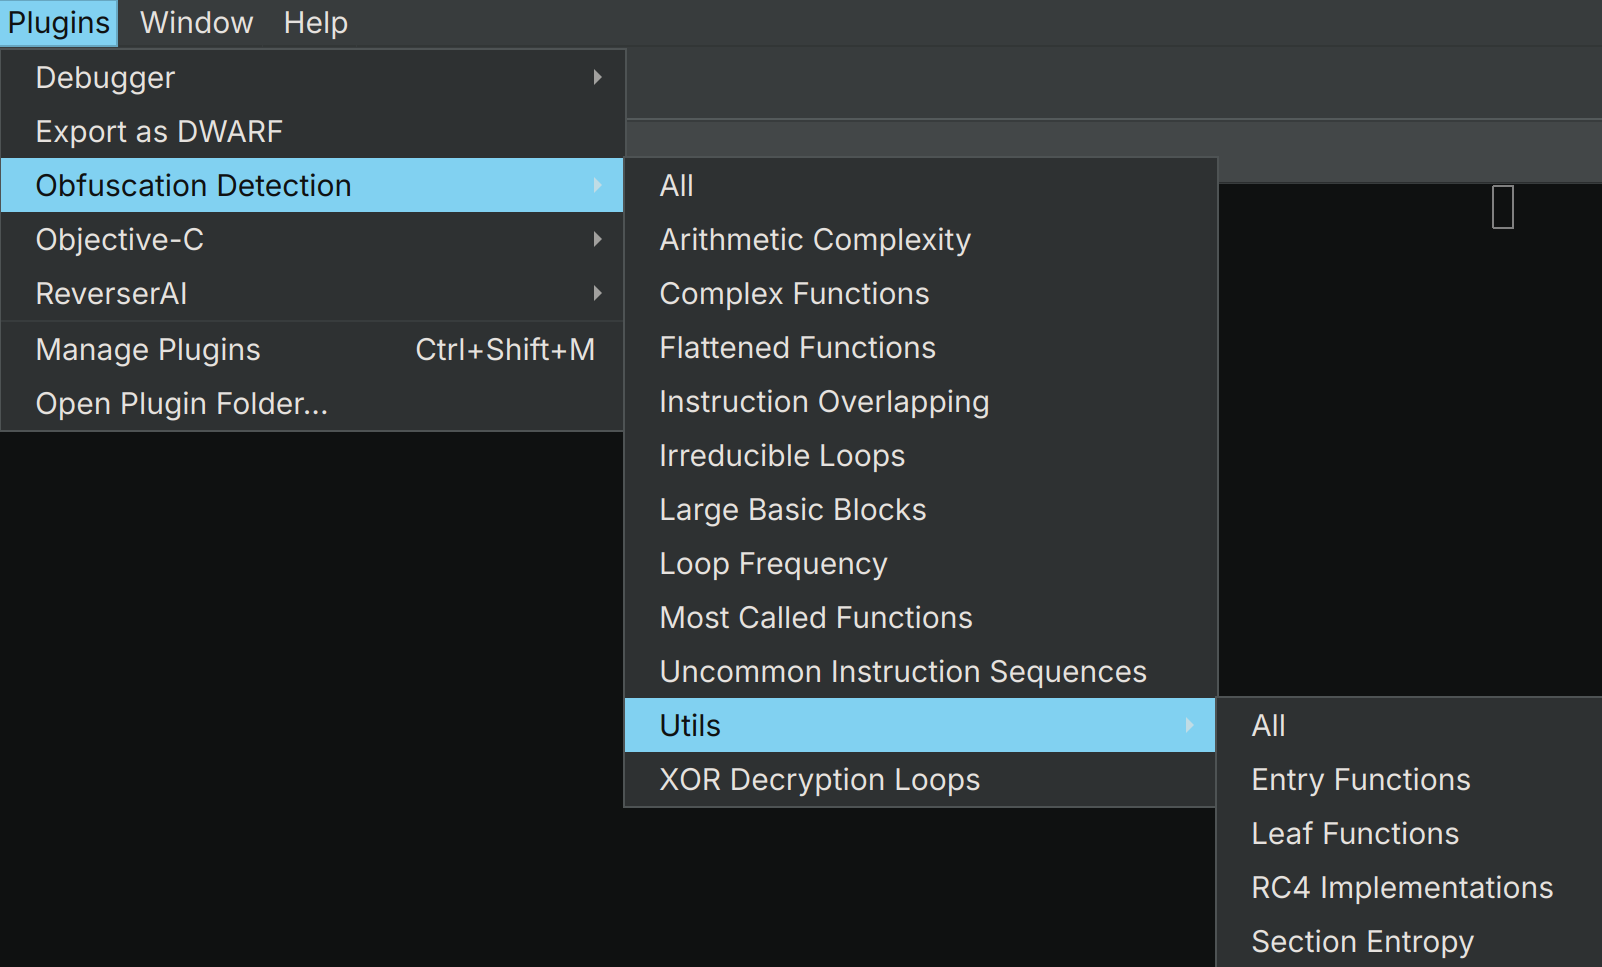 mrphrazer/obfuscation_detection
Binary Ninja plugin to identify obfuscated code and other interesting code constructs
 hasherezade/pe-bear-old
PE-bear (builds only)
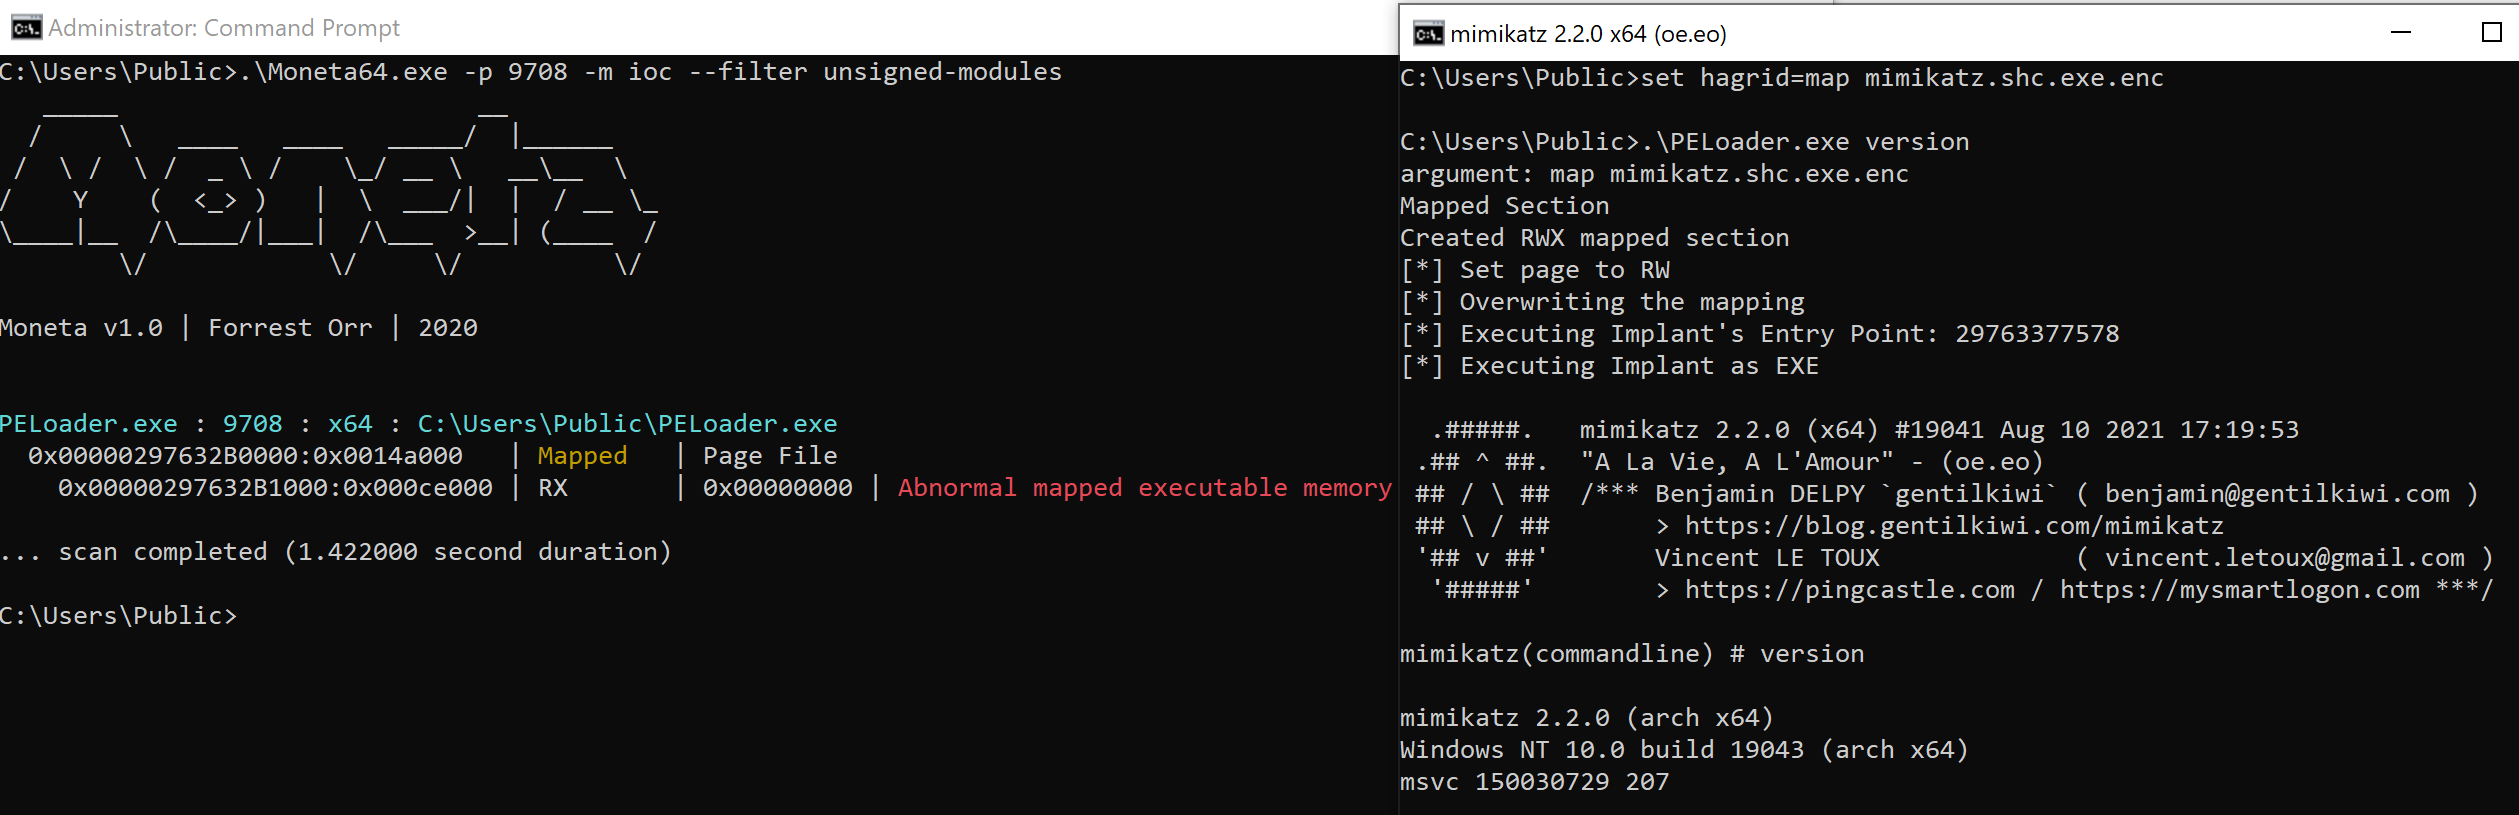 hagrid29/peloader
PE loader with various shellcode injection techniques
 suleram/view8
Decompiles serialized V8 bytecode (JSC files) into high-level readable JavaScript-like code, with support for multiple V8 versions, tree output, and…
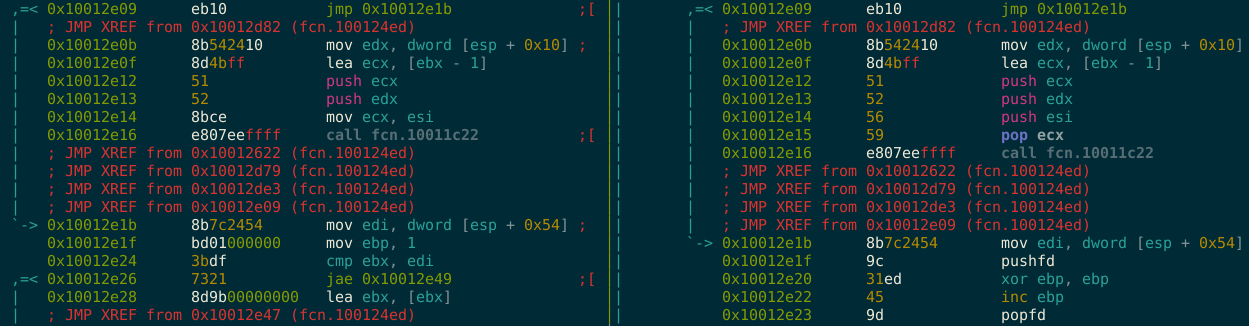 a0rtega/metame
metame is a metamorphic code engine for arbitrary executables
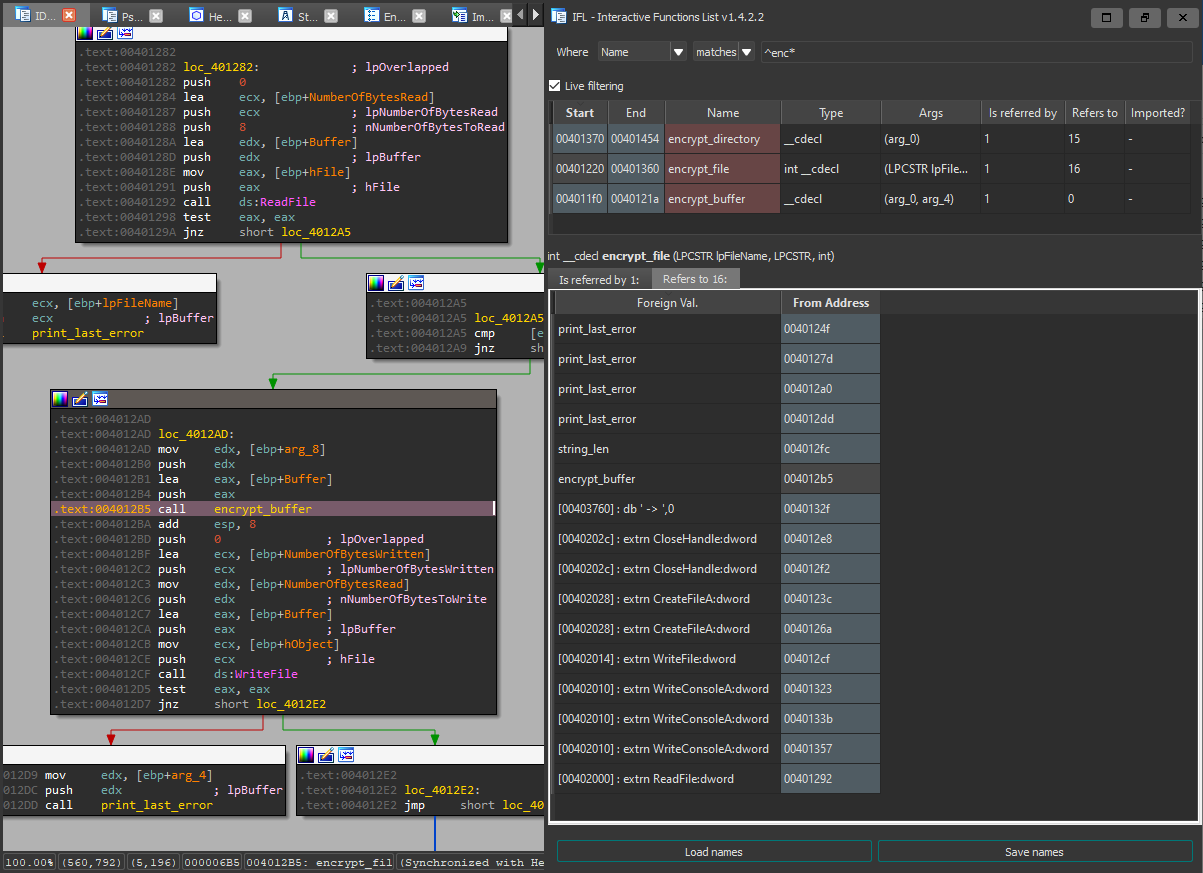 hasherezade/ida_ifl
IFL - Interactive Functions List (plugin for IDA Pro)
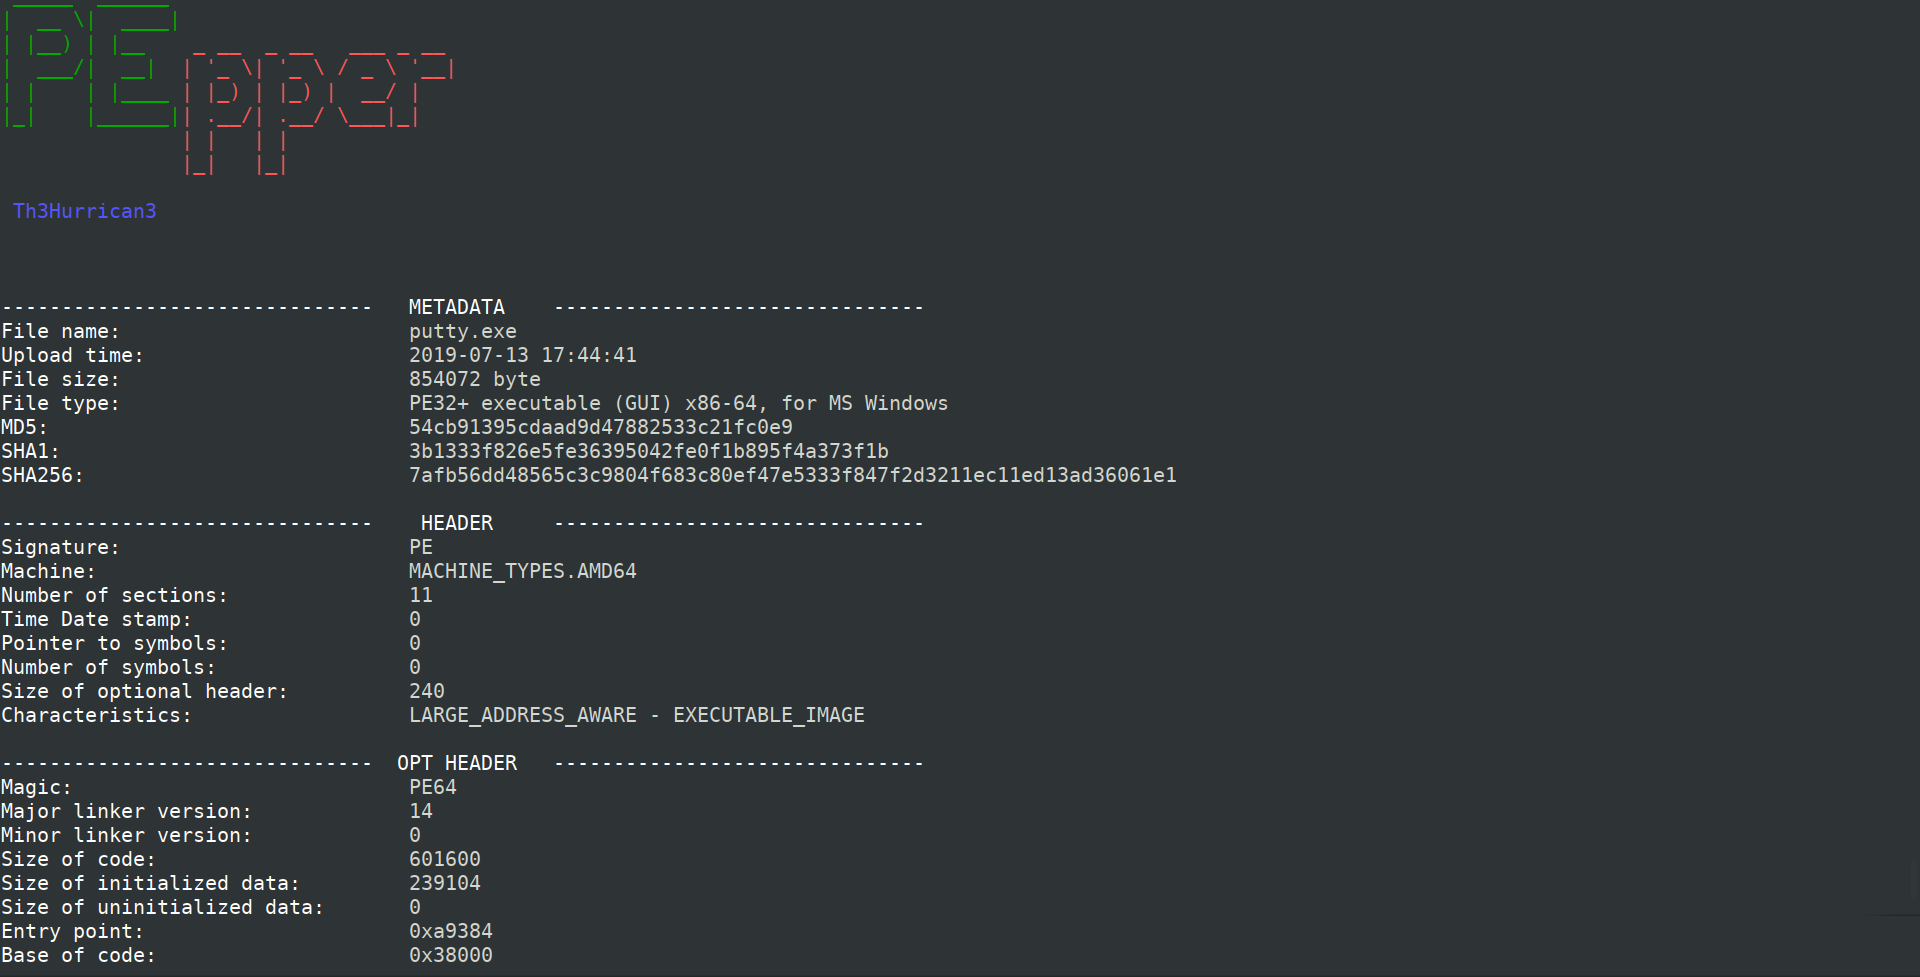 0x0be/pepper
An open source script to perform malware static analysis on Portable Executable
 michaelweber/macrome
Excel Macro Document Reader/Writer for Red Teamers & Analysts
 matheuzsecurity/furtex
Post-exploitation and evasion research toolkit for Linux.
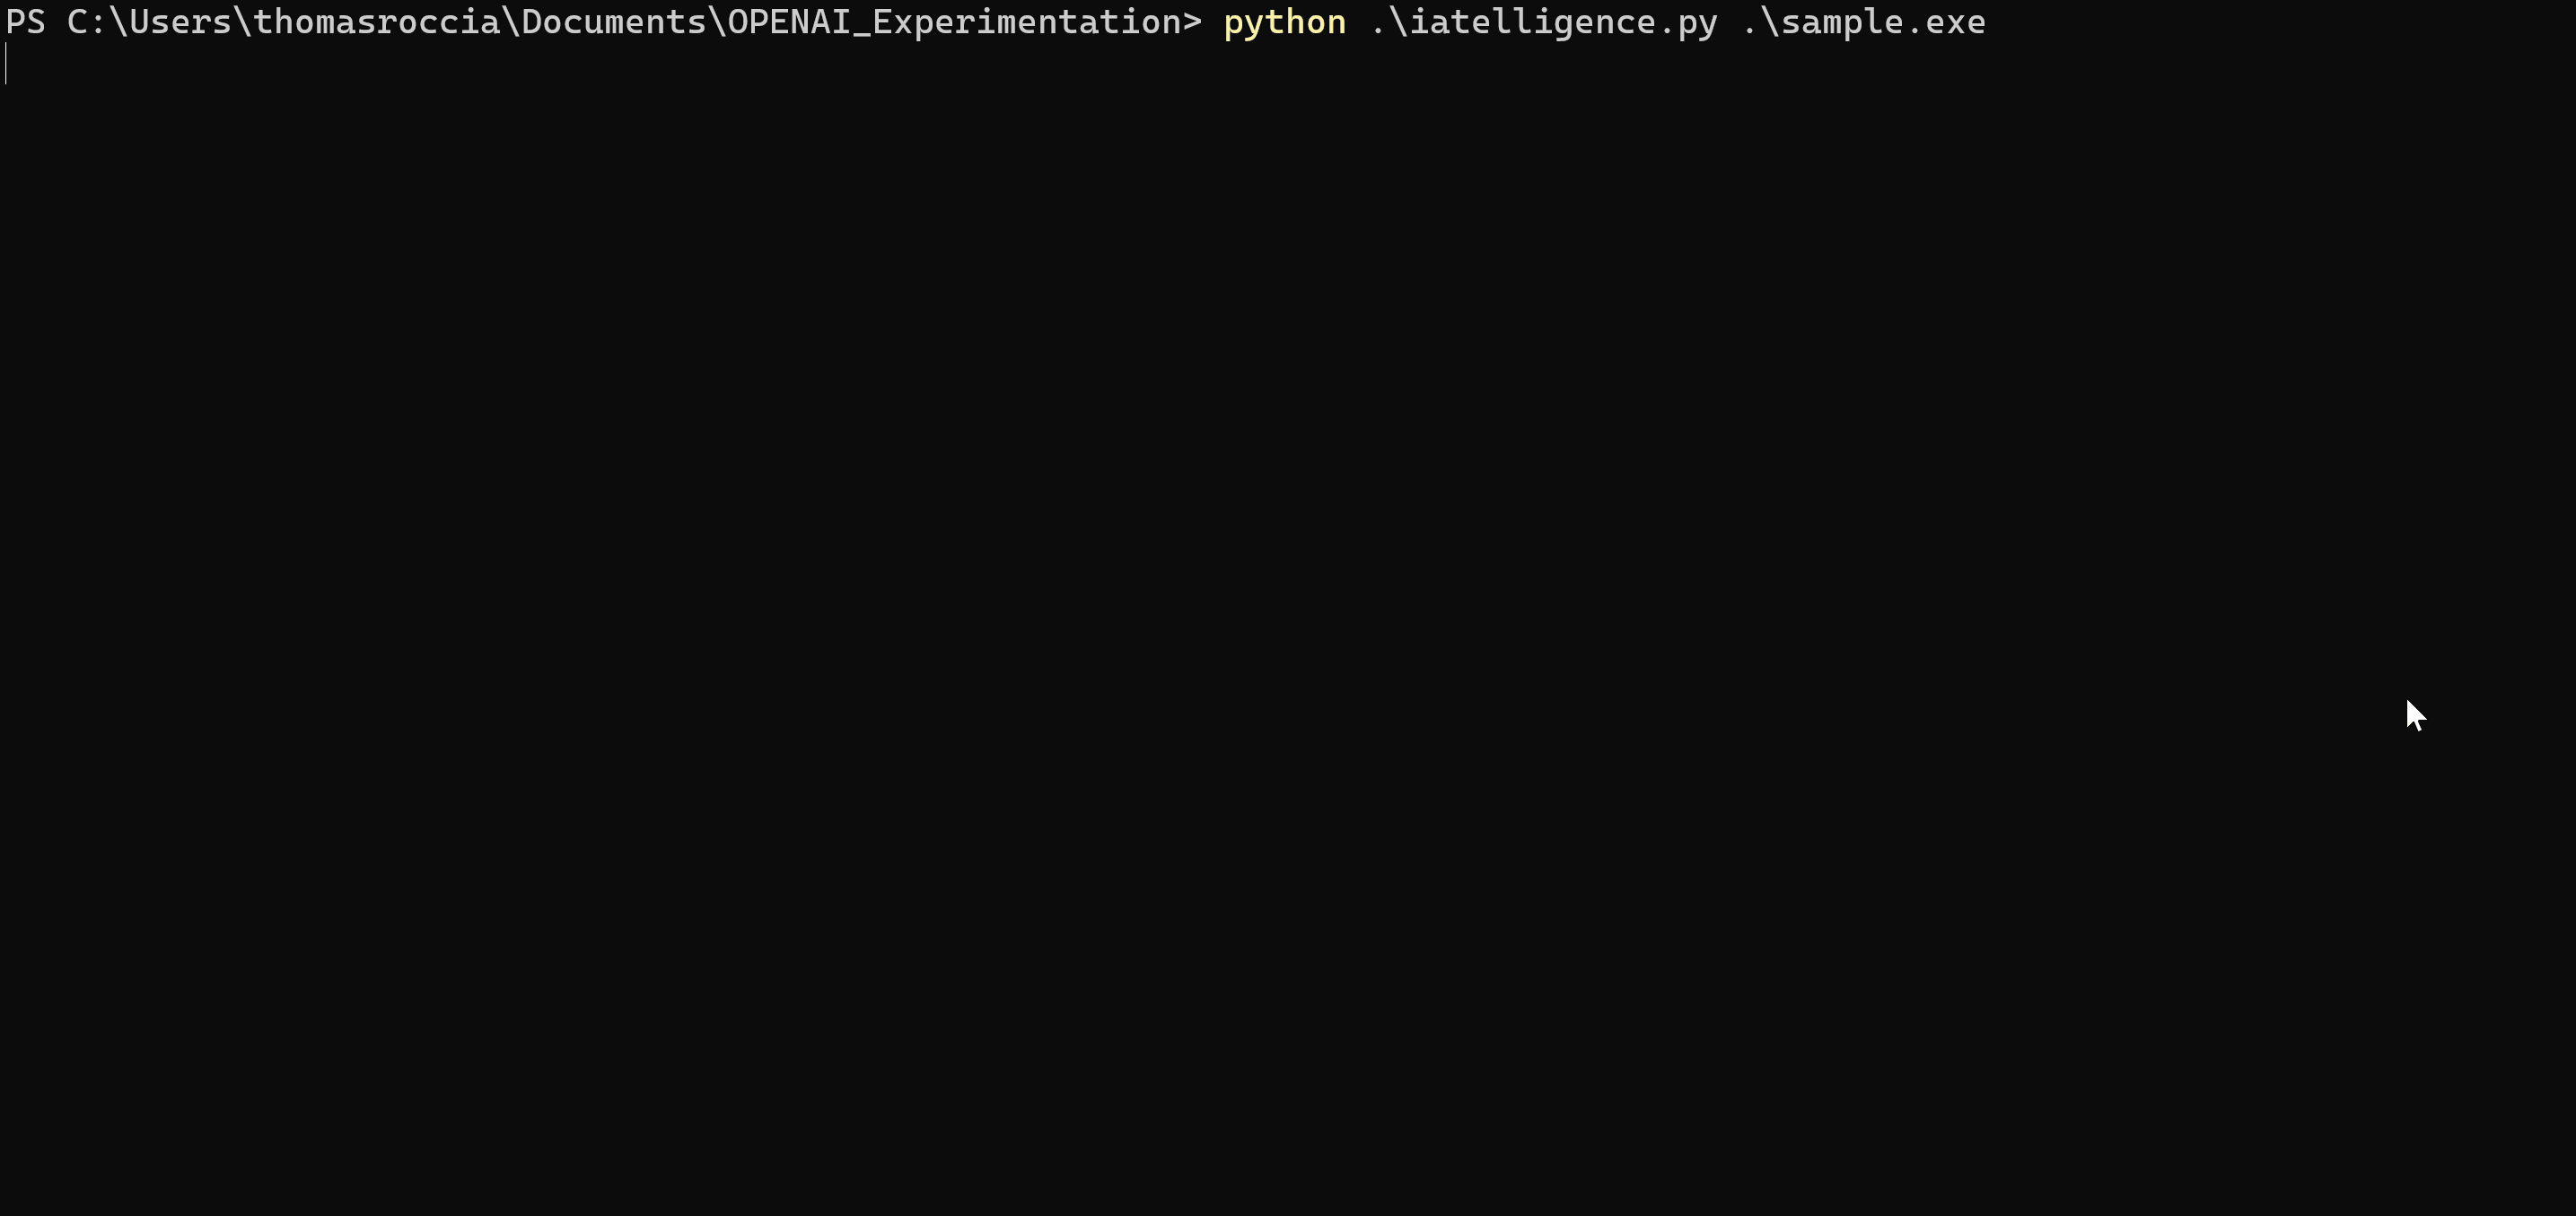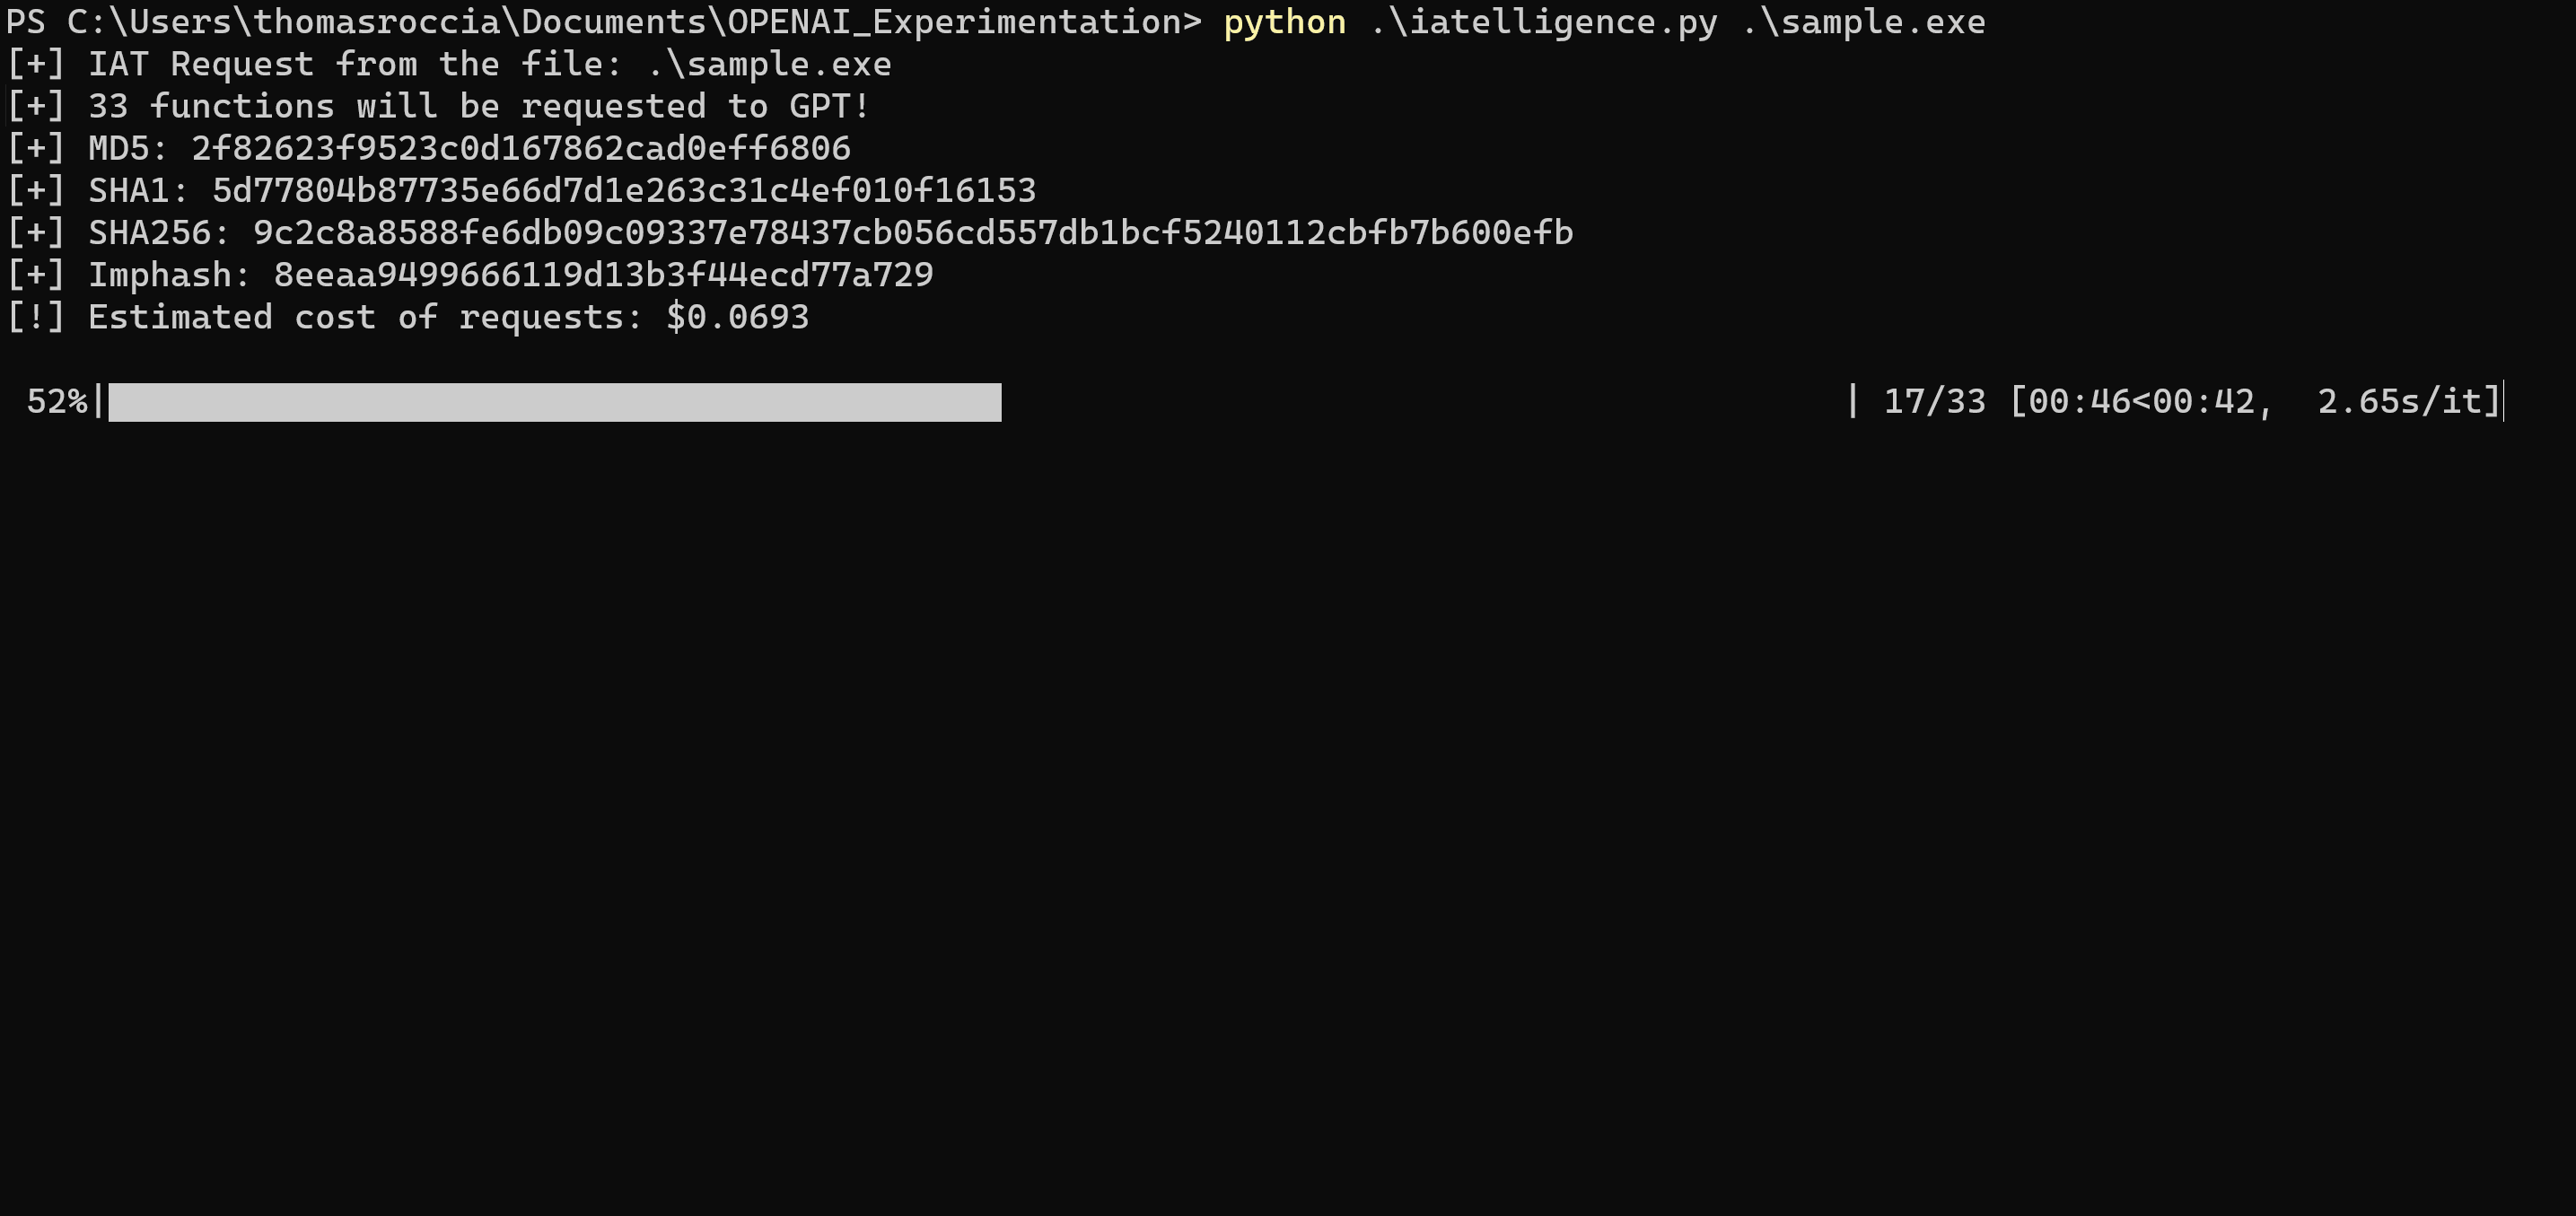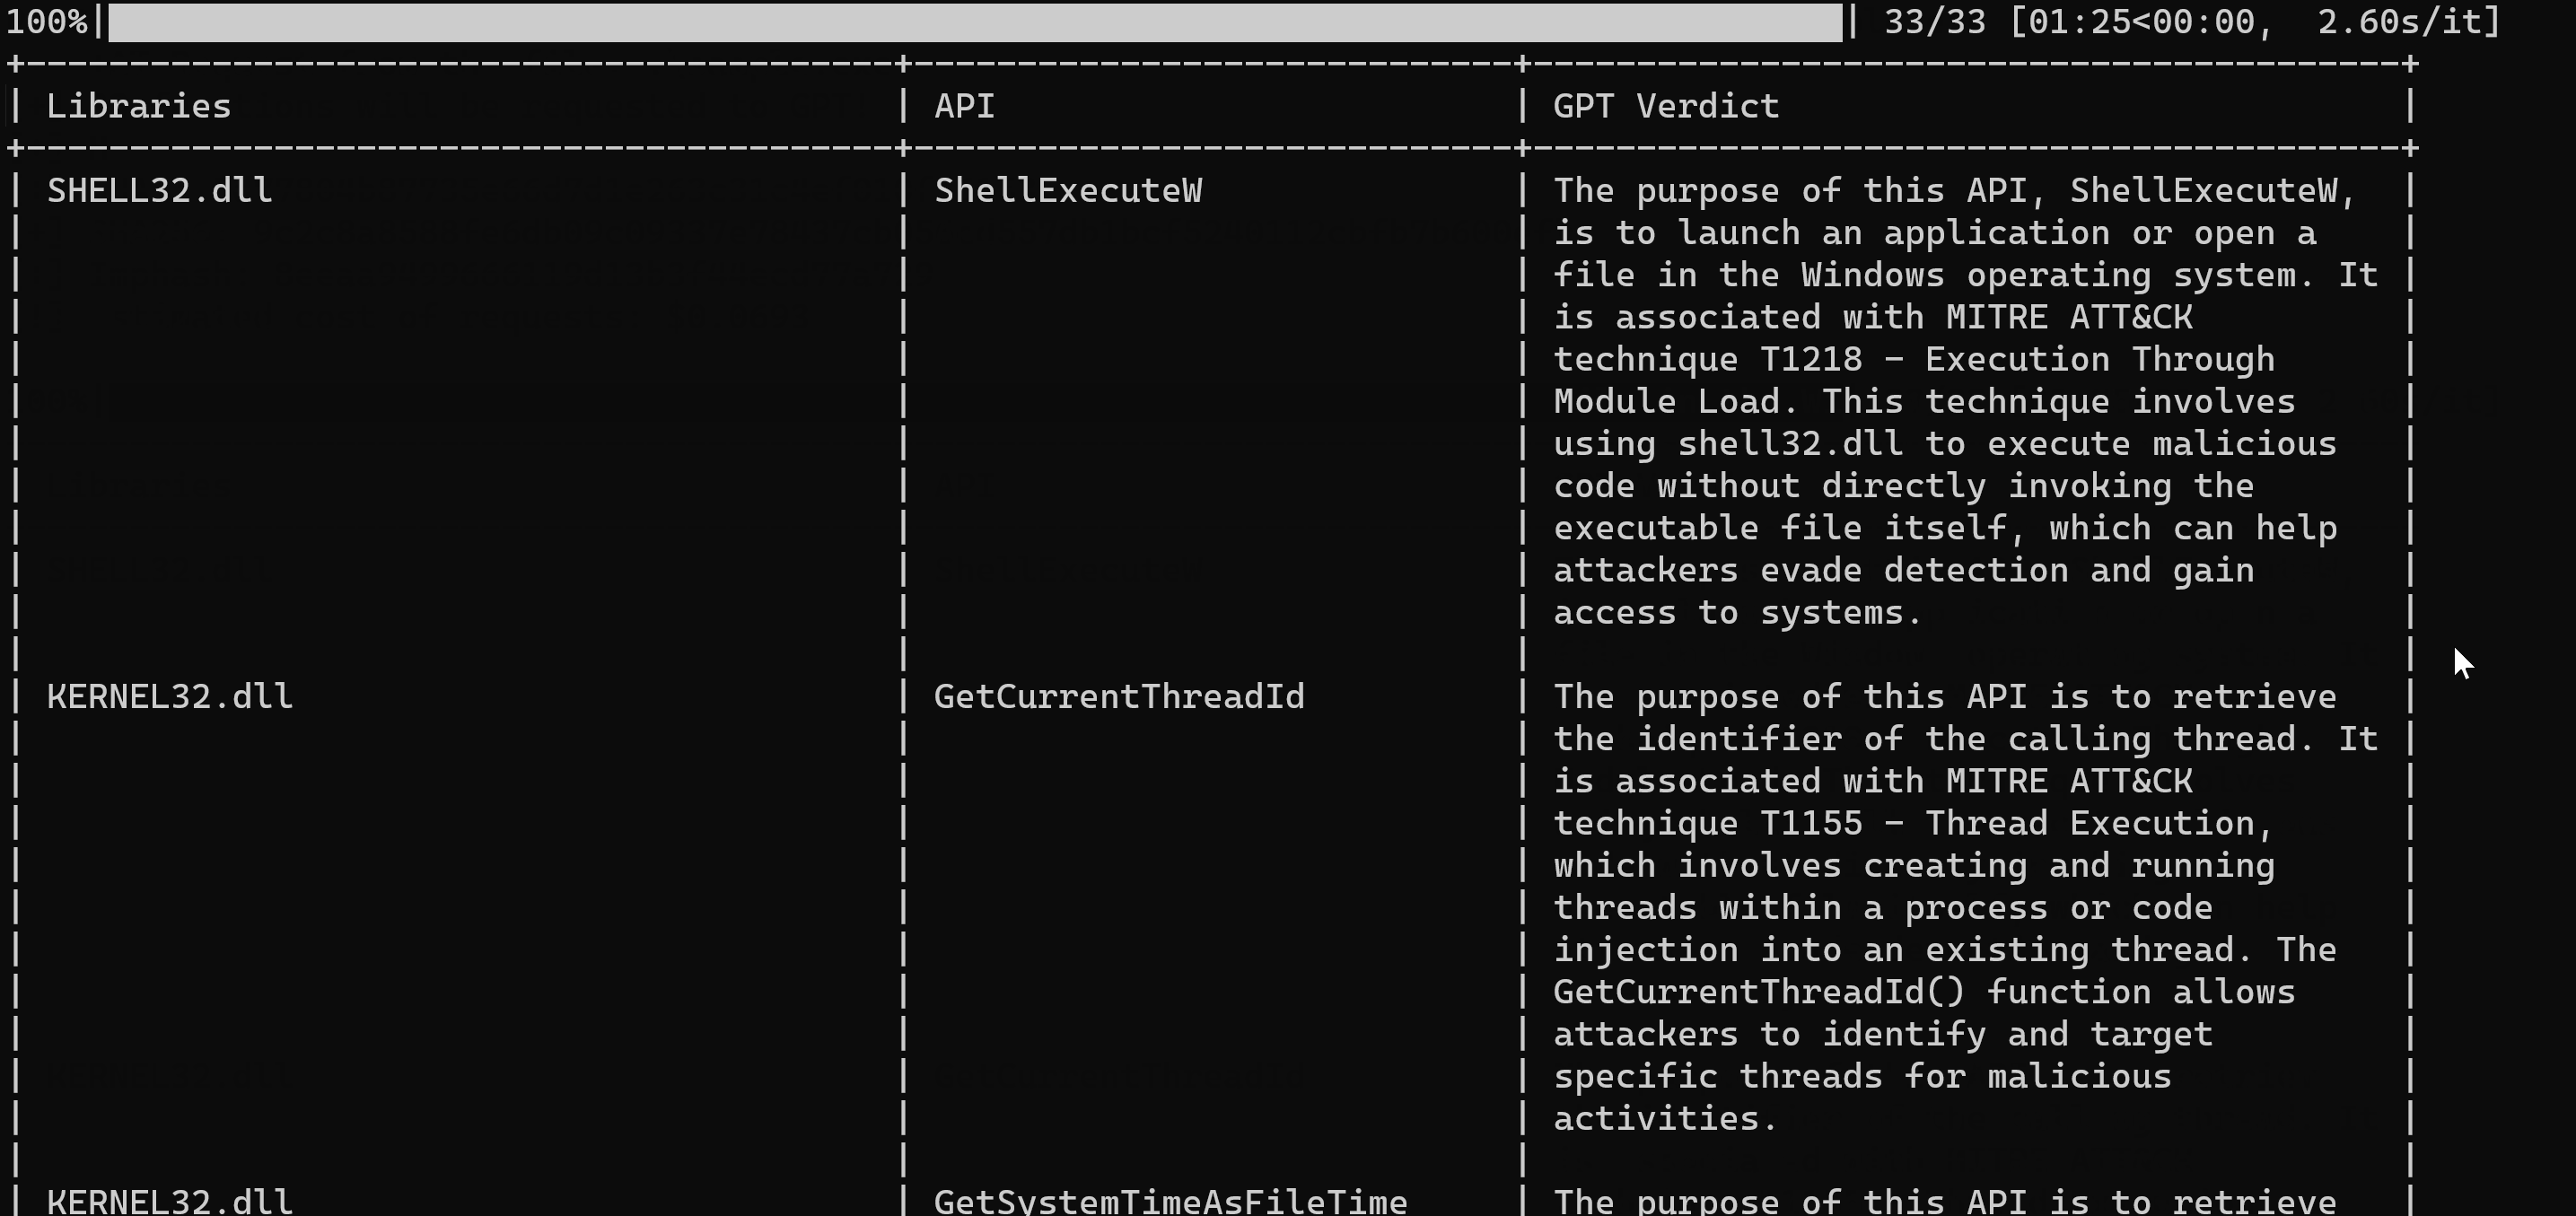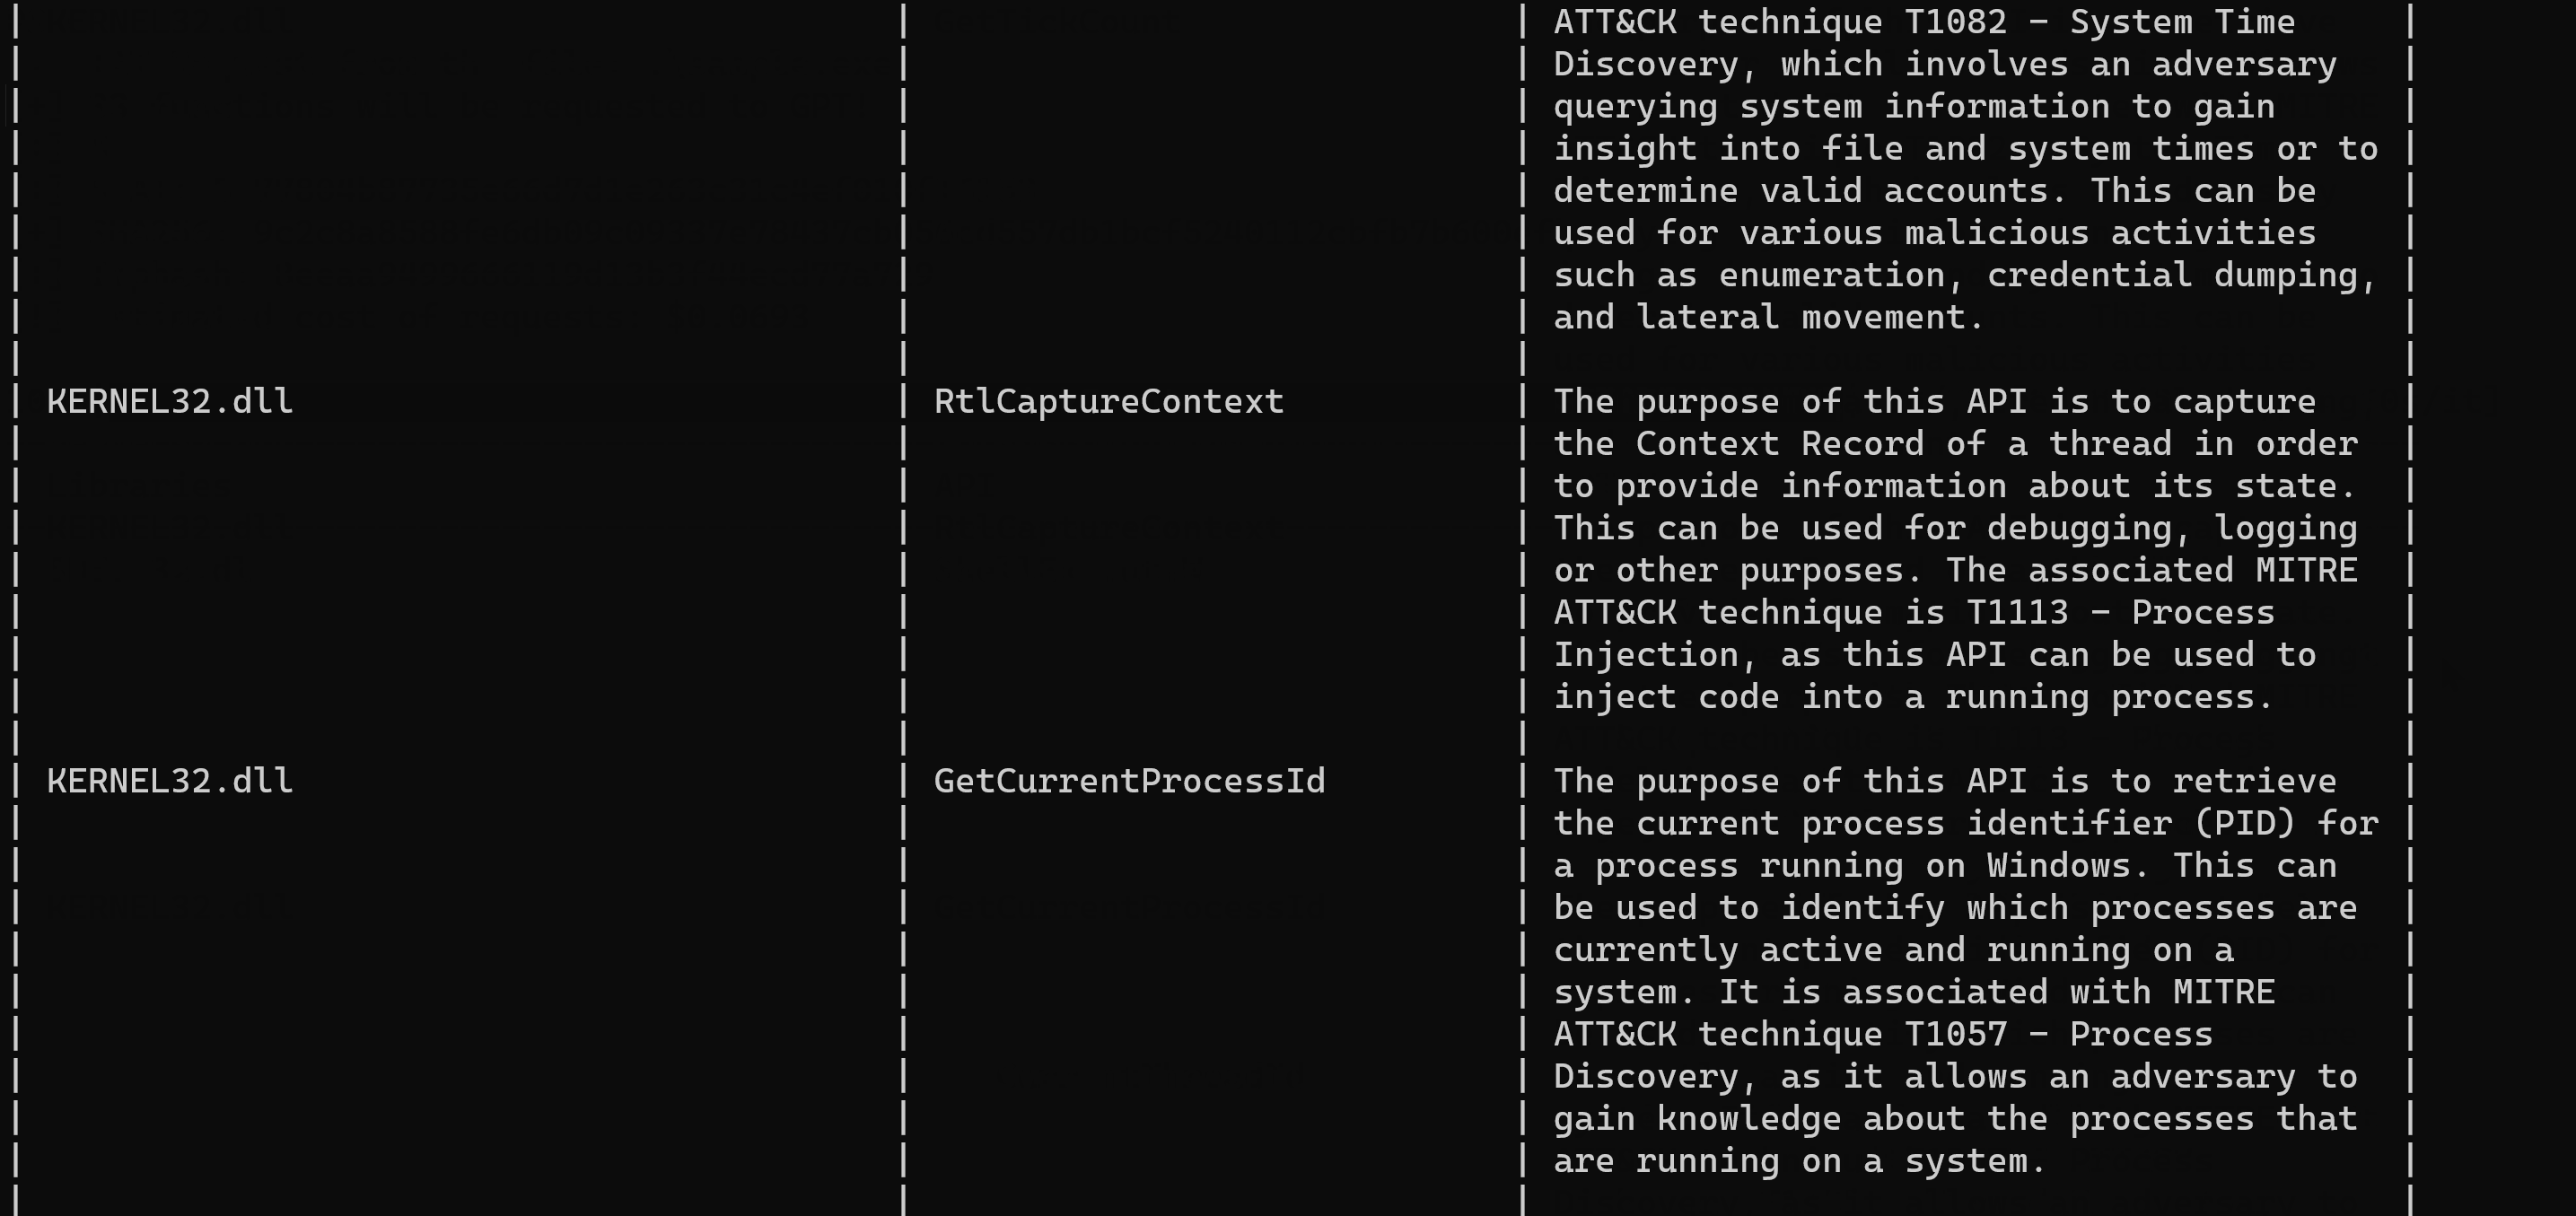 fr0gger/iatelligence
IATelligence is a Python script that will extract the IAT of a PE file and request GPT to get more information about the API and the ATT&CK matrix…