
apxutil
 finngineering/apxutil
A tool to manipulate Schneider Electric PLC archive files
binary-analysisembedded-systems-securityexploitation+5
118 months ago
finngineering/apxutilA tool to manipulate Schneider Electric PLC archive files
 yasharote/dll-injector
A desktop tool that allows injecting DLLs, hooking WinAPI functions like CreateFileW, and modifying process behavior at runtime — designed for…
 freddierice/cve-2020-35498-flag
C-based exploit tool to detect and trigger CVE-2020-35498 via raw socket injection with BPF filter, targeting wireless interfaces for vulnerability…
 ospg/binwalk
Firmware Analysis Tool
 hasherezade/pe-sieve
Scans a given process. Recognizes and dumps a variety of potentially malicious implants (replaced/injected PEs, shellcodes, hooks, in-memory patches).

 zodiacon/alltools
All reasonably stable tools
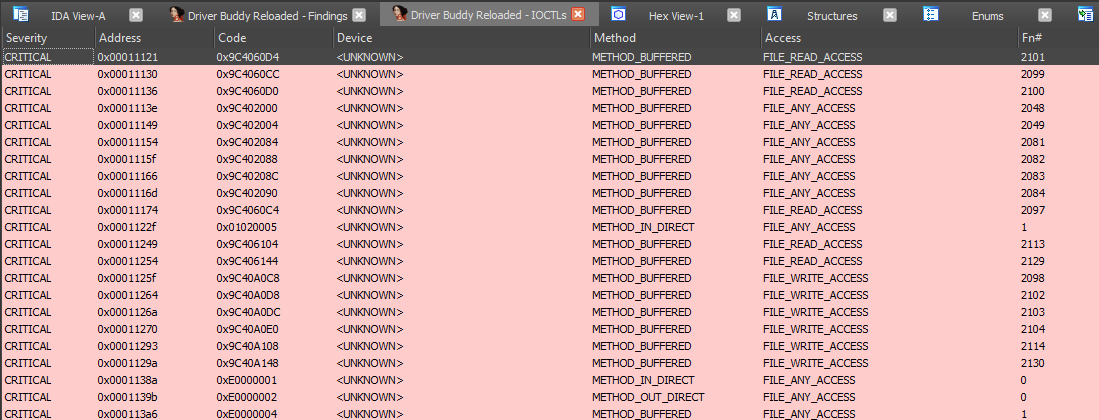 voidsec/driverbuddyreloaded
Driver Buddy Reloaded is an IDA Pro Python plugin that helps automate some tedious Windows Kernel Drivers reverse engineering tasks
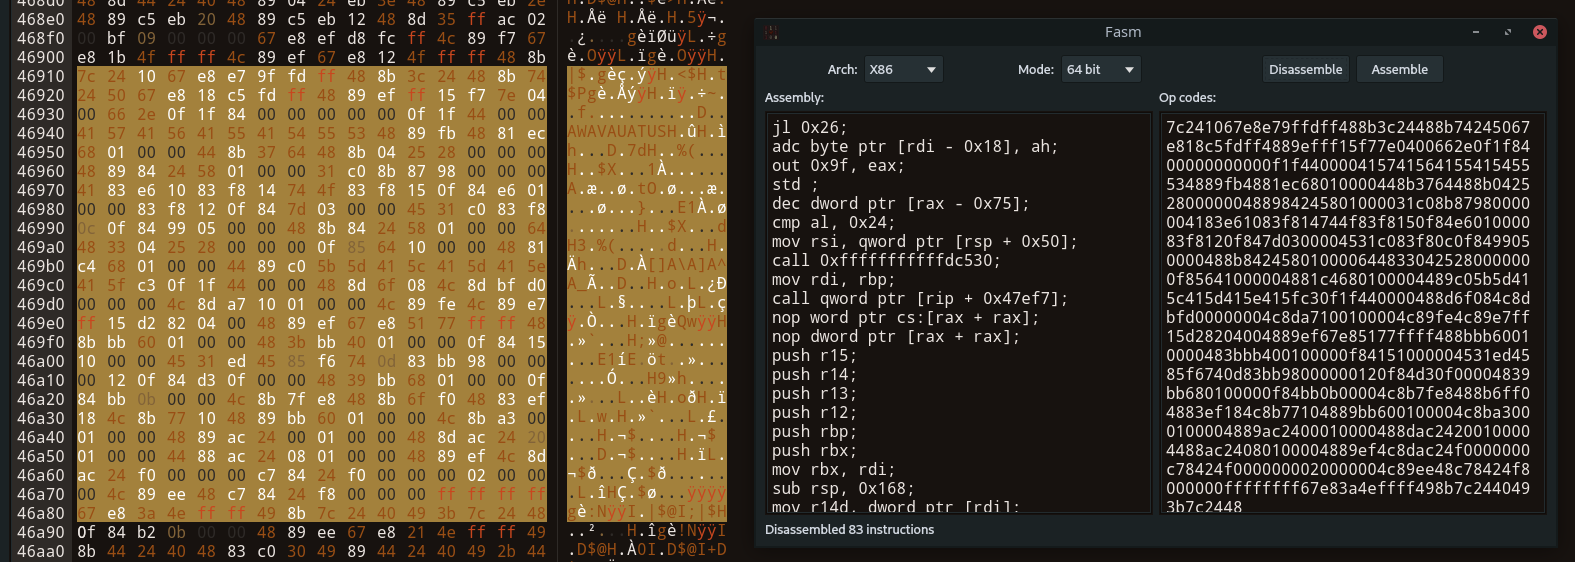 echo-devim/fhex
A Full-Featured HexEditor compatible with Linux/Windows/MacOS
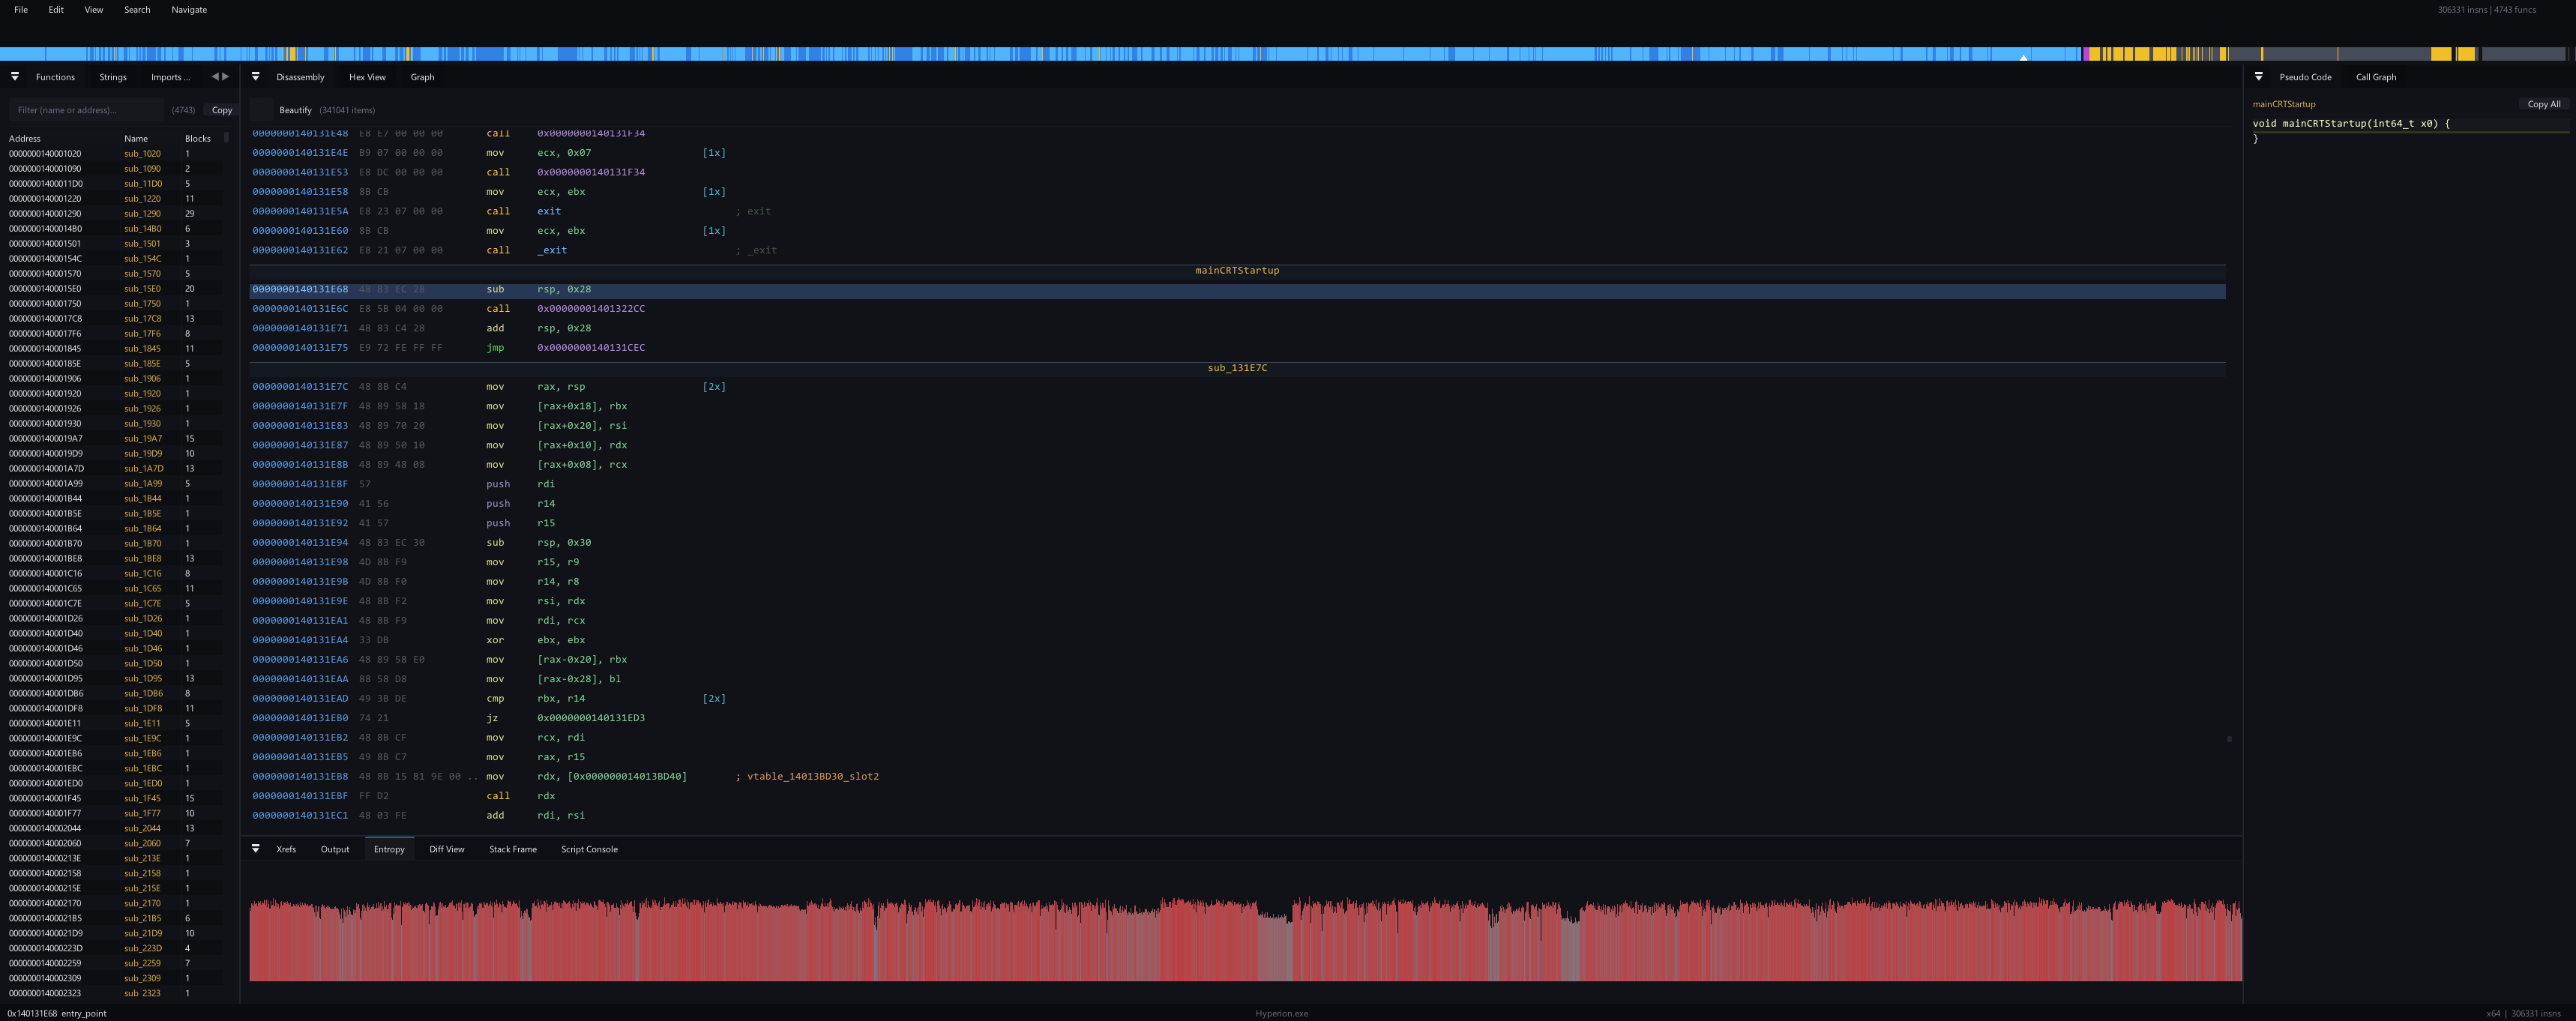 sidenai/hyperion-disassembler
Native multi-arch disassembler & decompiler - PE/ELF/Mach-O, x86/x64/ARM64, Lua scripting, RTTI recovery
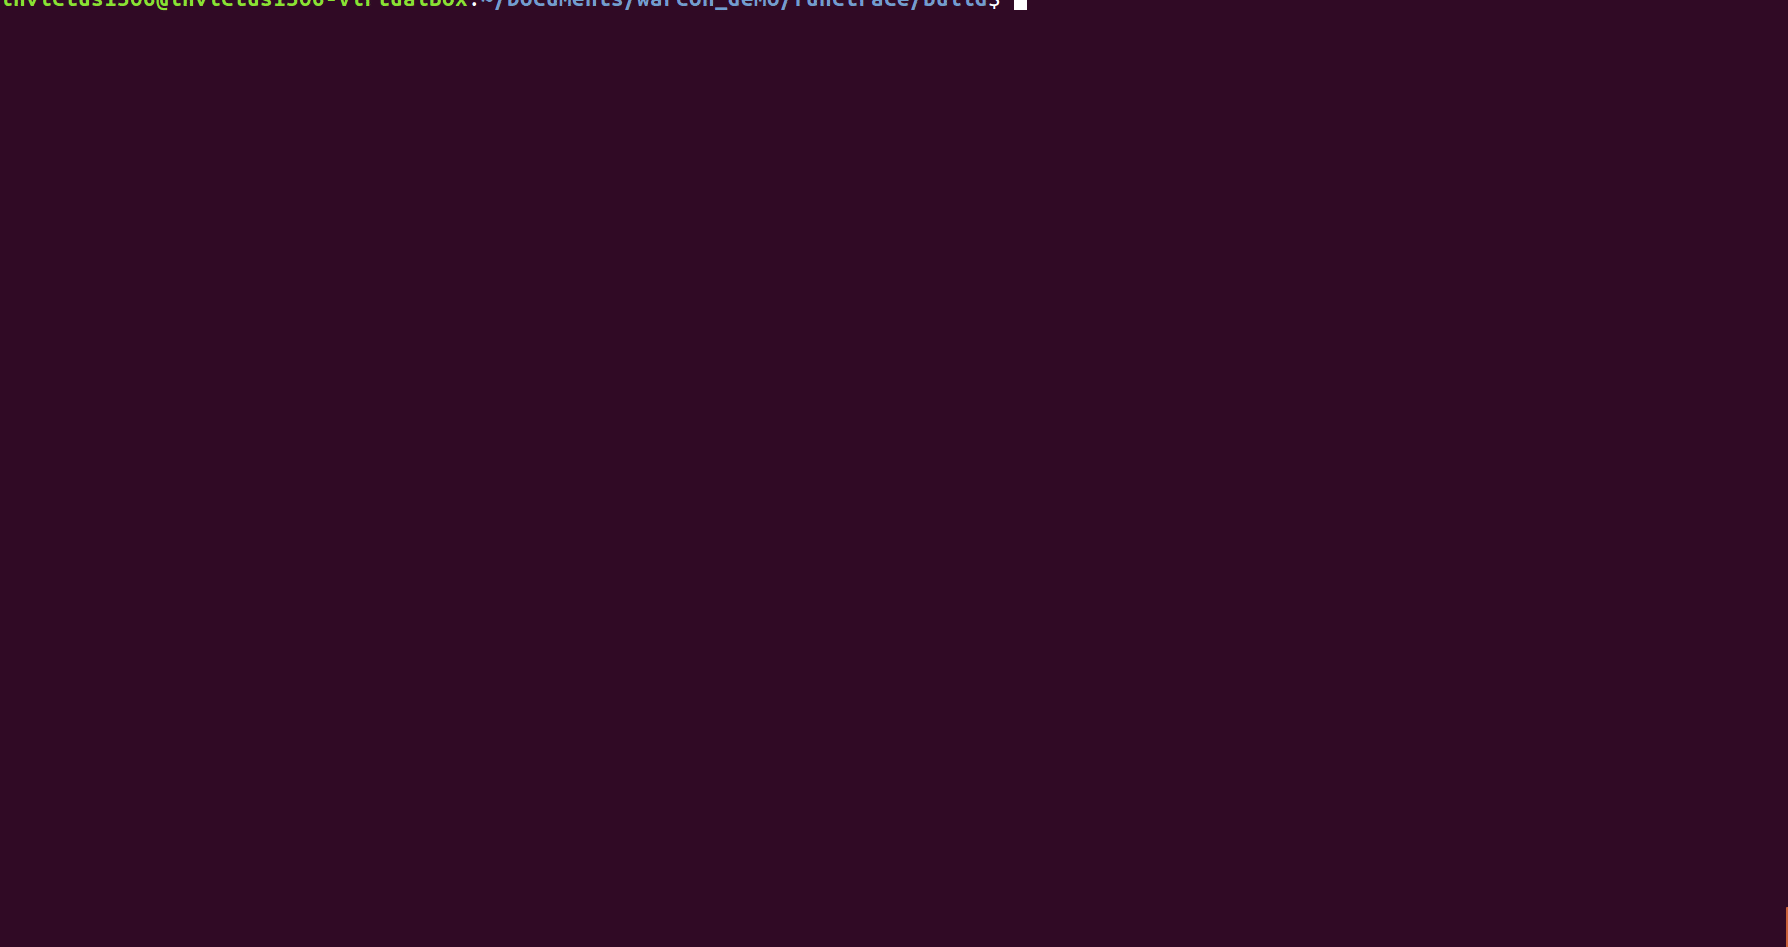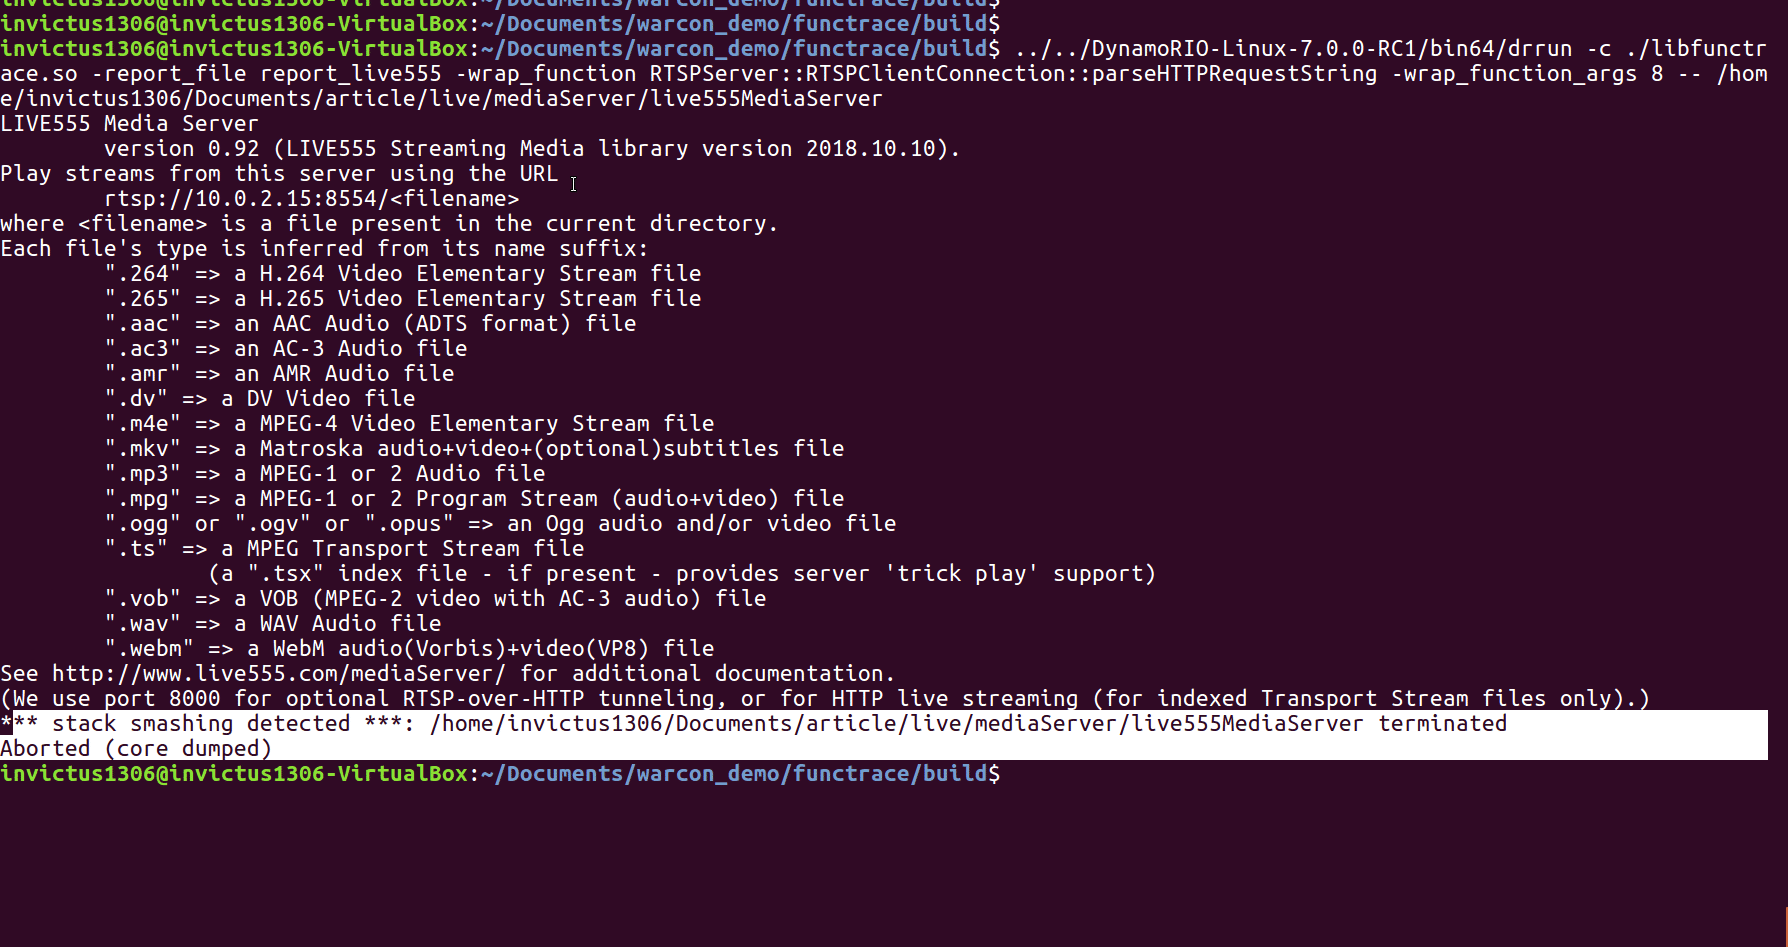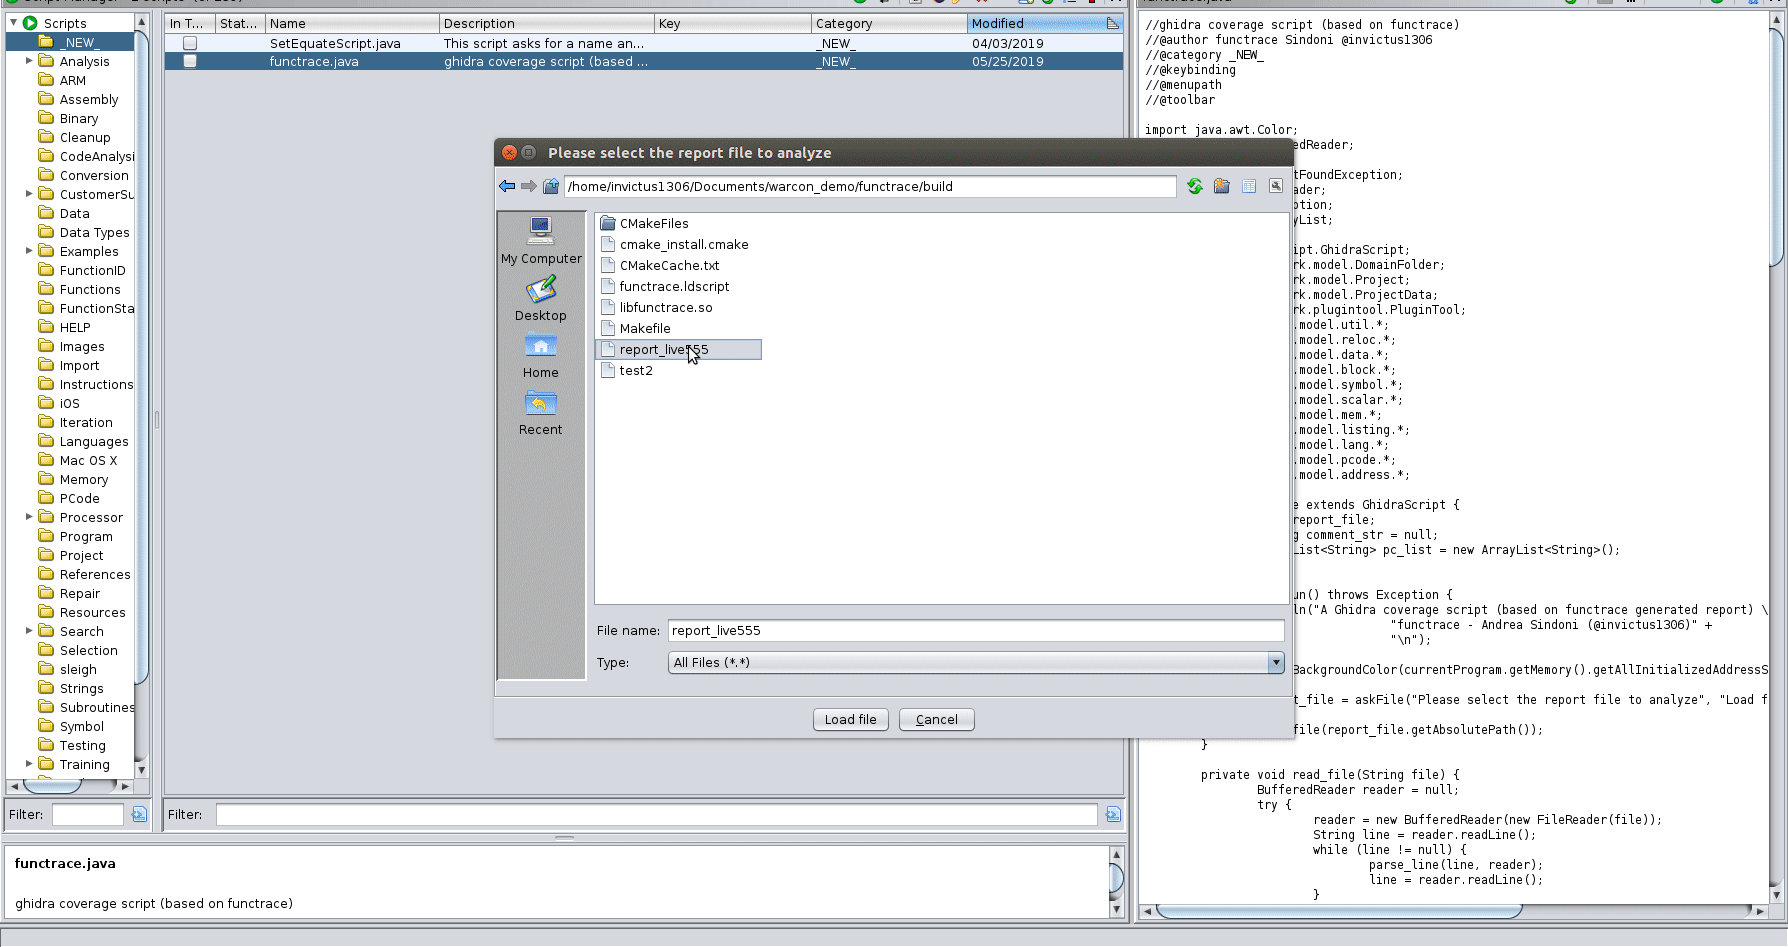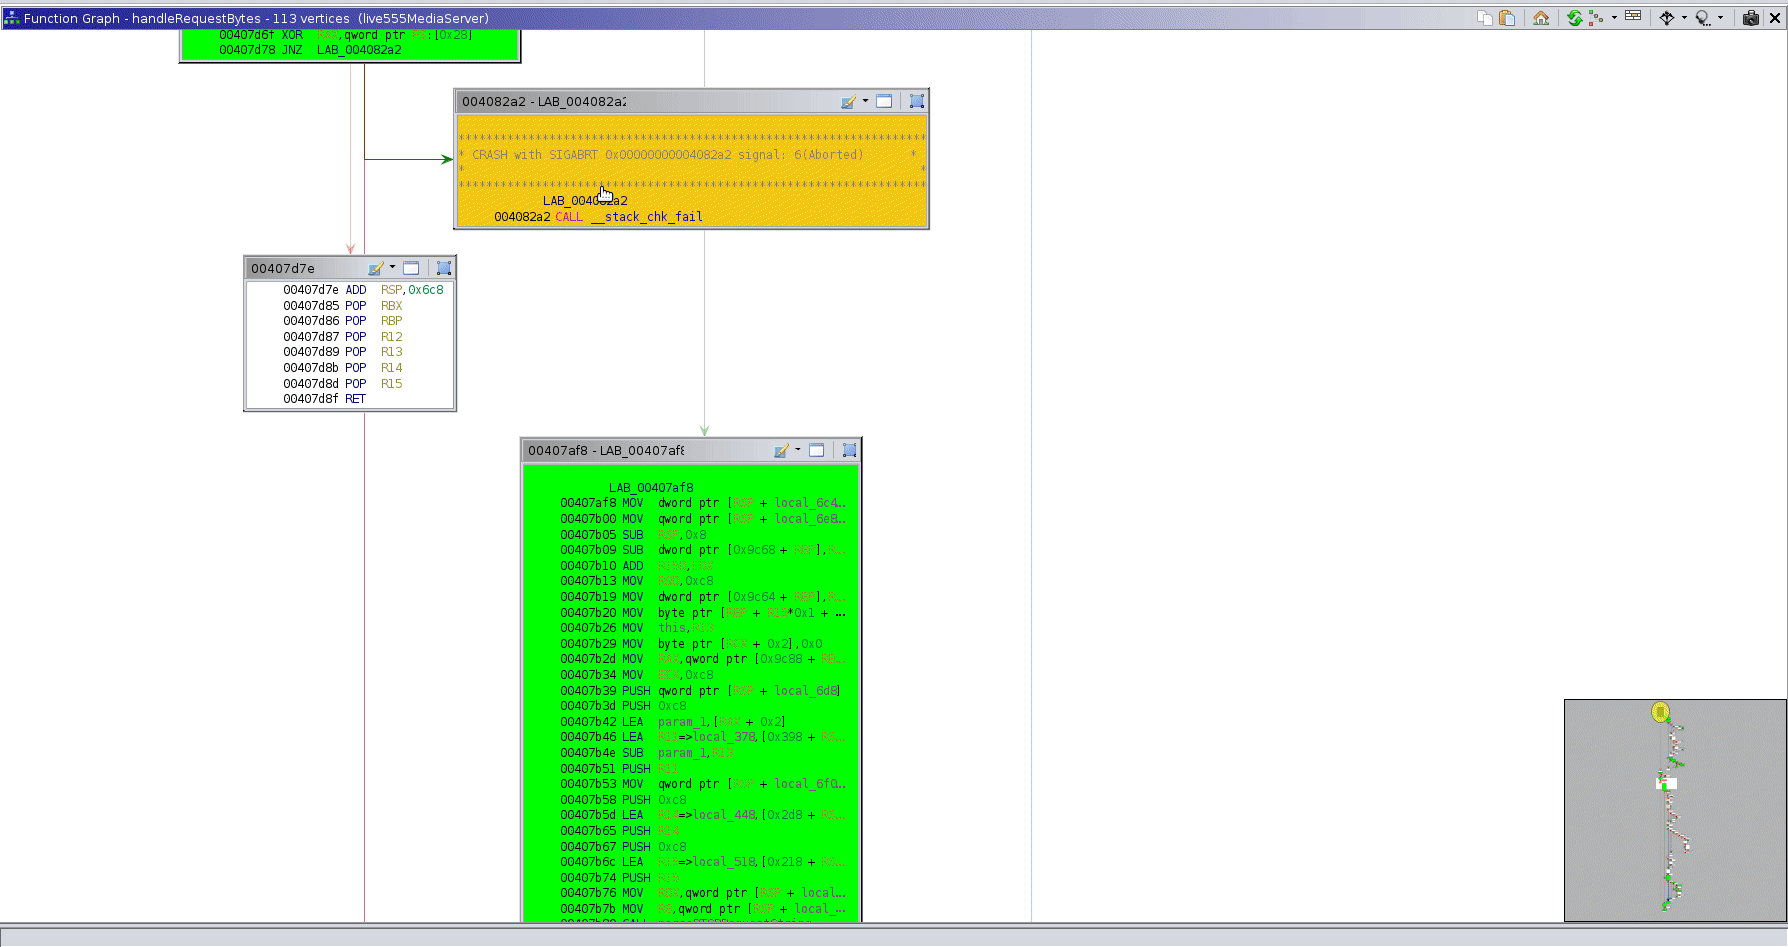 invictus1306/functrace
A function tracer
 synacktiv/captainhook
Traces user inputs to detect injection vulnerabilities in Java methods via JDWP and Frida, identifying potential command and SQL injection points.
 gmh5225/asm-obfuscator
Obfuscates x86-64 assembly with instruction injection, junk code, constant obfuscation, and runtime decryption to hinder reverse engineering and…
 ret5et/watchguard_webui_unpacker
Watchguard Sysa-dl file format
 google/path-auditor
Runtime libc function auditor that detects file access race conditions and symlink vulnerabilities by hooking filesystem syscalls via LD_PRELOAD,…
 netspooky/inhale
A malware analysis and classification tool.