

OffensiveCSharp
 matterpreter/offensivecsharp
Collection of Offensive C# Tooling
binary-analysiscode-analysisexploitation+7
1.5k
matterpreter/offensivecsharpCollection of Offensive C# Tooling
 gaasedelen/lighthouse
A Coverage Explorer for Reverse Engineers
 reclassnet/reclass.net
More than a ReClass port to the .NET platform.
 bootleg/ret-sync
ret-sync is a set of plugins that helps to synchronize a debugging session (WinDbg/GDB/LLDB/OllyDbg2/x64dbg) with IDA/Ghidra/Binary Ninja…
 boku7/bokuloader
A proof-of-concept Cobalt Strike Reflective Loader which aims to recreate, integrate, and enhance Cobalt Strike's evasion features!
 theopolis/uefi-firmware-parser
Parse BIOS/Intel ME/UEFI firmware related structures: Volumes, FileSystems, Files, etc
 intelxed/xed
Low-level library for encoding and decoding IA32/Intel64 x86 instructions, exposing APIs for instruction length, operands, categories, control-flow…
 fr0gger/awesome-ida-x64-olly-plugin
A curated list of IDA x64DBG, Ghidra and OllyDBG plugins.
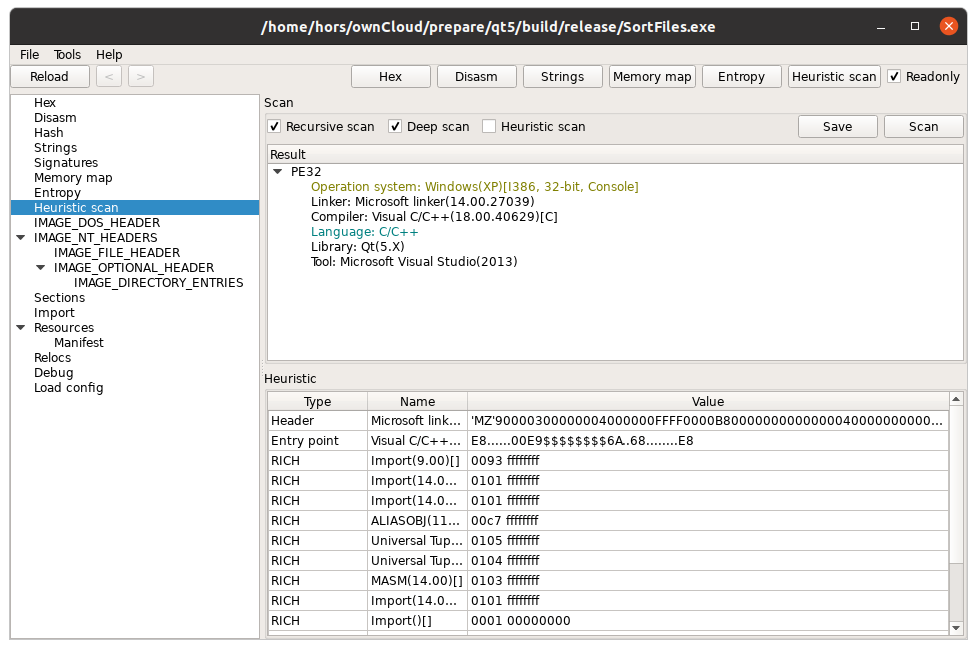 horsicq/xpeviewer
PE file viewer/editor for Windows, Linux and MacOS.
 rasta-mouse/threatcheck
Identifies the bytes that Microsoft Defender / AMSI Consumer flags on.
 rizinorg/rz-ghidra
Deep ghidra decompiler and sleigh disassembler integration for rizin
 jonathansalwan/vmprotect-devirtualization
Playing with the VMProtect software protection. Automatic deobfuscation of pure functions using symbolic execution and LLVM.
 mandiant/goresym
Parses Go binaries to recover symbols, function metadata, types, file paths, and embedded strings, including stripped or UPX-packed samples, with IDA…
 lauriewired/malimite
iOS and macOS Decompiler
 igio90/dwarf
Full featured multi arch/os debugger built on top of PyQt5 and frida
 med0x2e/sigflip
SigFlip is a tool for patching authenticode signed PE files (exe, dll, sys ..etc) without invalidating or breaking the existing signature.
 withsecurelabs/python-exe-unpacker
A helper script for unpacking and decompiling EXEs compiled from python code.
 0xgalz/virtuailor
IDAPython tool for creating automatic C++ virtual tables in IDA Pro