
HolyGrail
 blacksnufkin/holygrail
BYOVD hunter to help prioritize windows drivers worth manual analysis
binary-analysisexploitationpenetration-testing+2
1331 year ago
blacksnufkin/holygrailBYOVD hunter to help prioritize windows drivers worth manual analysis
 nccgroup/psr
Pointer Sequence Reverser - enable you to see how Windows C++ application is accessing a particular data member or object.
 mandiant/flare-qdb
Command-line and Python debugger for instrumenting and modifying native software behavior on Windows and Linux.
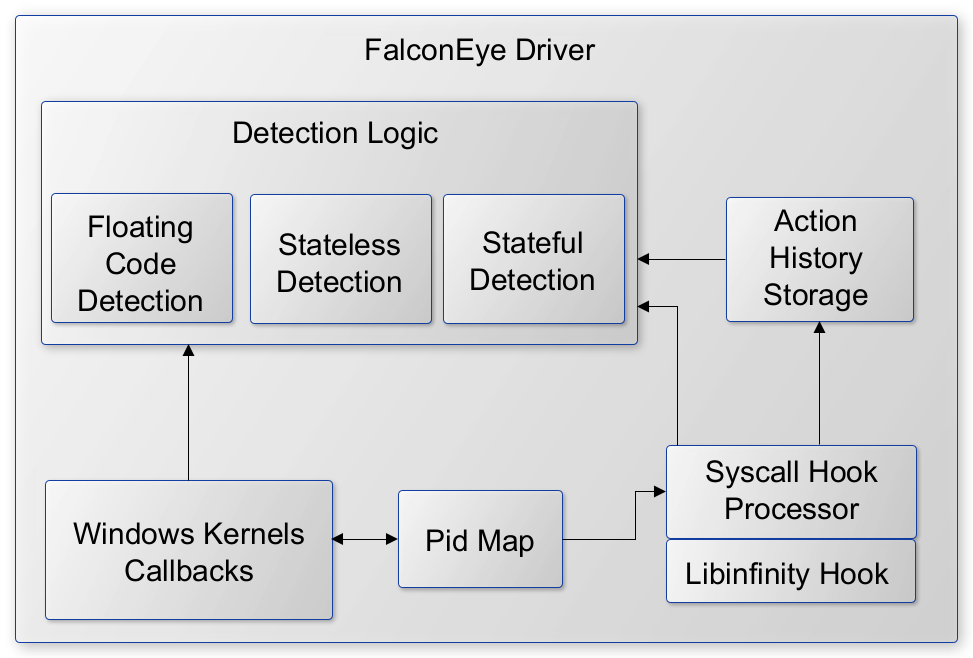 rajiv2790/falconeye
Kernel-mode Windows driver for real-time detection of process injection techniques, including shellcode, DLL, and reflective injection, with syscall…
 gmh5225/access_updated
Kernel-mode syscall wrapper with Zydis-based dynamic pattern finding for Windows 10/11
 adem-hosni/mappedimagesdetector
Lightweight native Windows memory scanner for AV/EDR platforms, detecting suspicious mapped images and manual DLL injection techniques by IAT thunk
 baptisterajaut/radmin-vpn-linux
Run Radmin VPN on Linux via Wine — custom driver, TAP bridge, zero packet loss
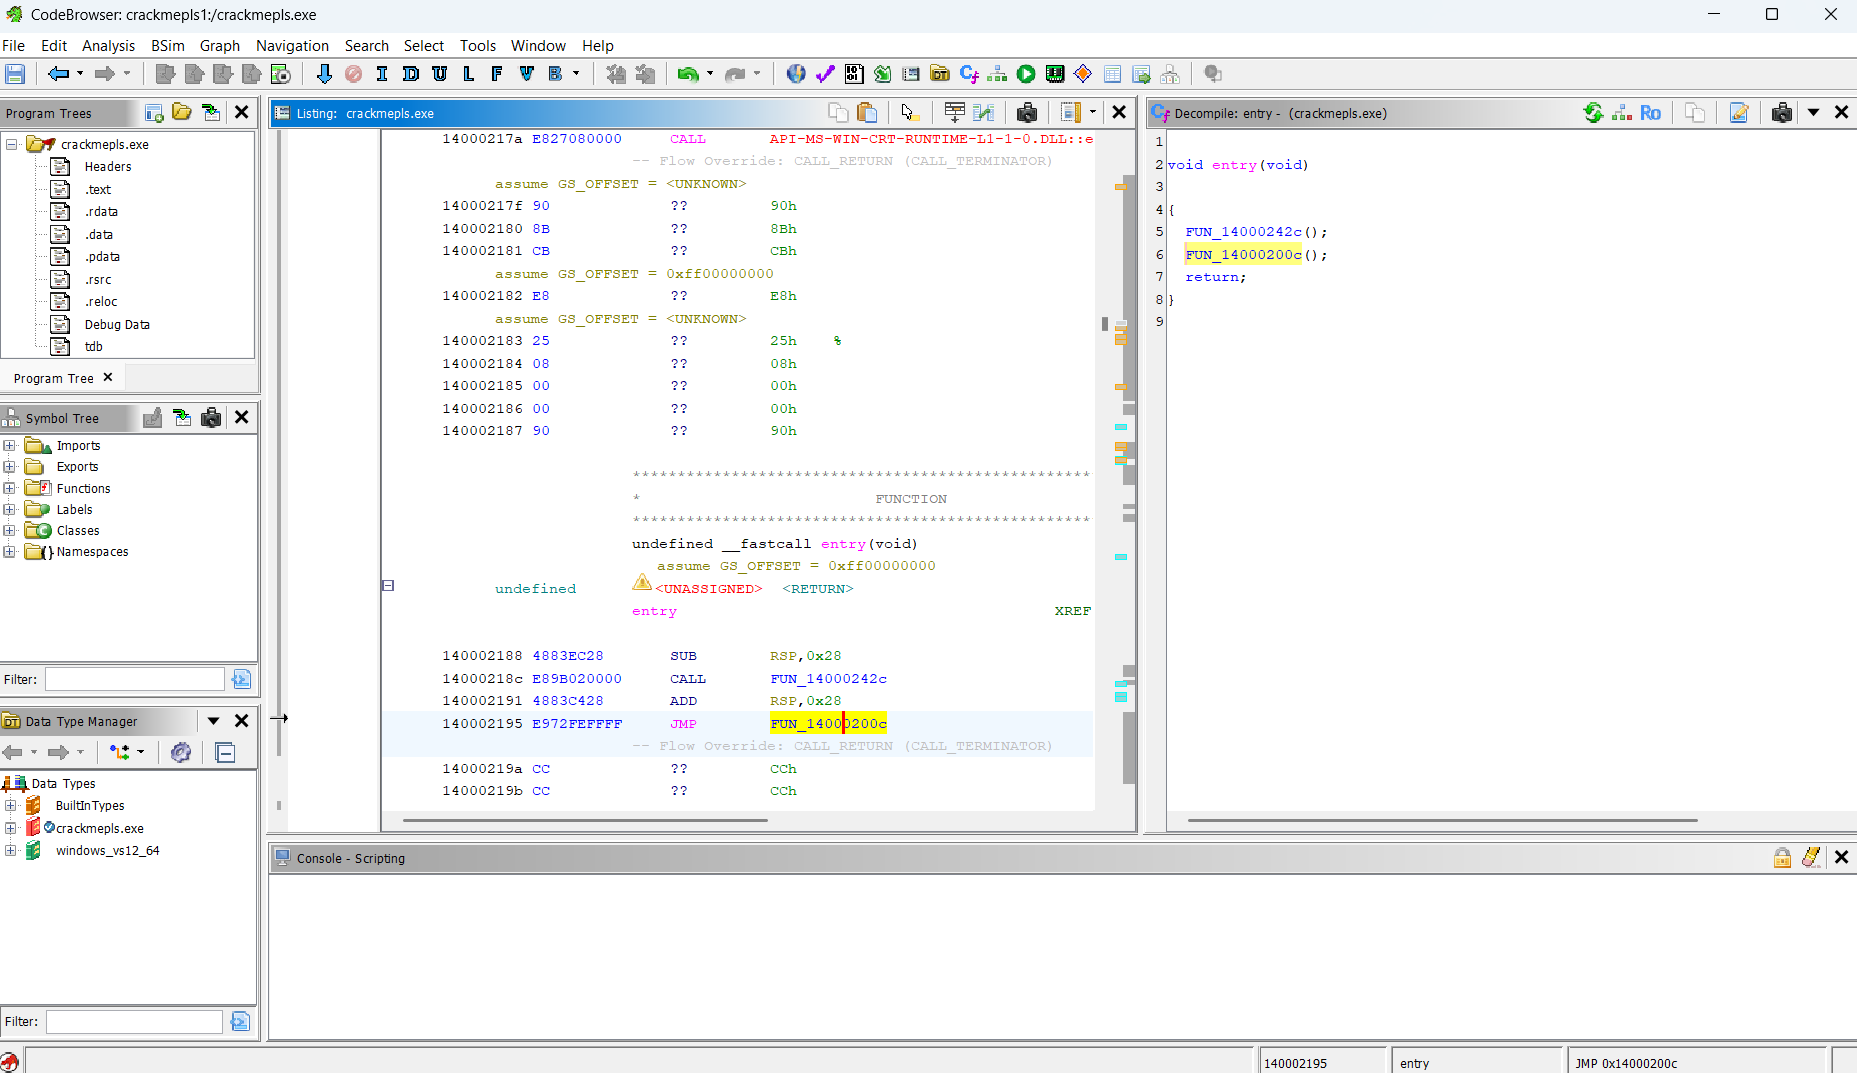 markoglasgow/gemma_crackme_tutorial
Step-by-step tutorial on using Google's Gemma 4 E4B local AI model to reverse engineer a Windows crackme with Ghidra, including setup for local…
 amperclock/cve-2025-9491_poc
Proof-of-Concept of the CVE-2025-9491 using invisible characters in the arguments of a Windows shortcut file (.lnk)
 lunixbochs/revsync
realtime cross-tool collaborative reverse engineering
 xyrem/hyperdeceit
HyperDeceit is the ultimate all-in-one library that emulates Hyper-V for Windows, giving you the ability to intercept and manipulate operating system…
 frank2/packer-tutorial
A tutorial on how to write a packer for Windows!
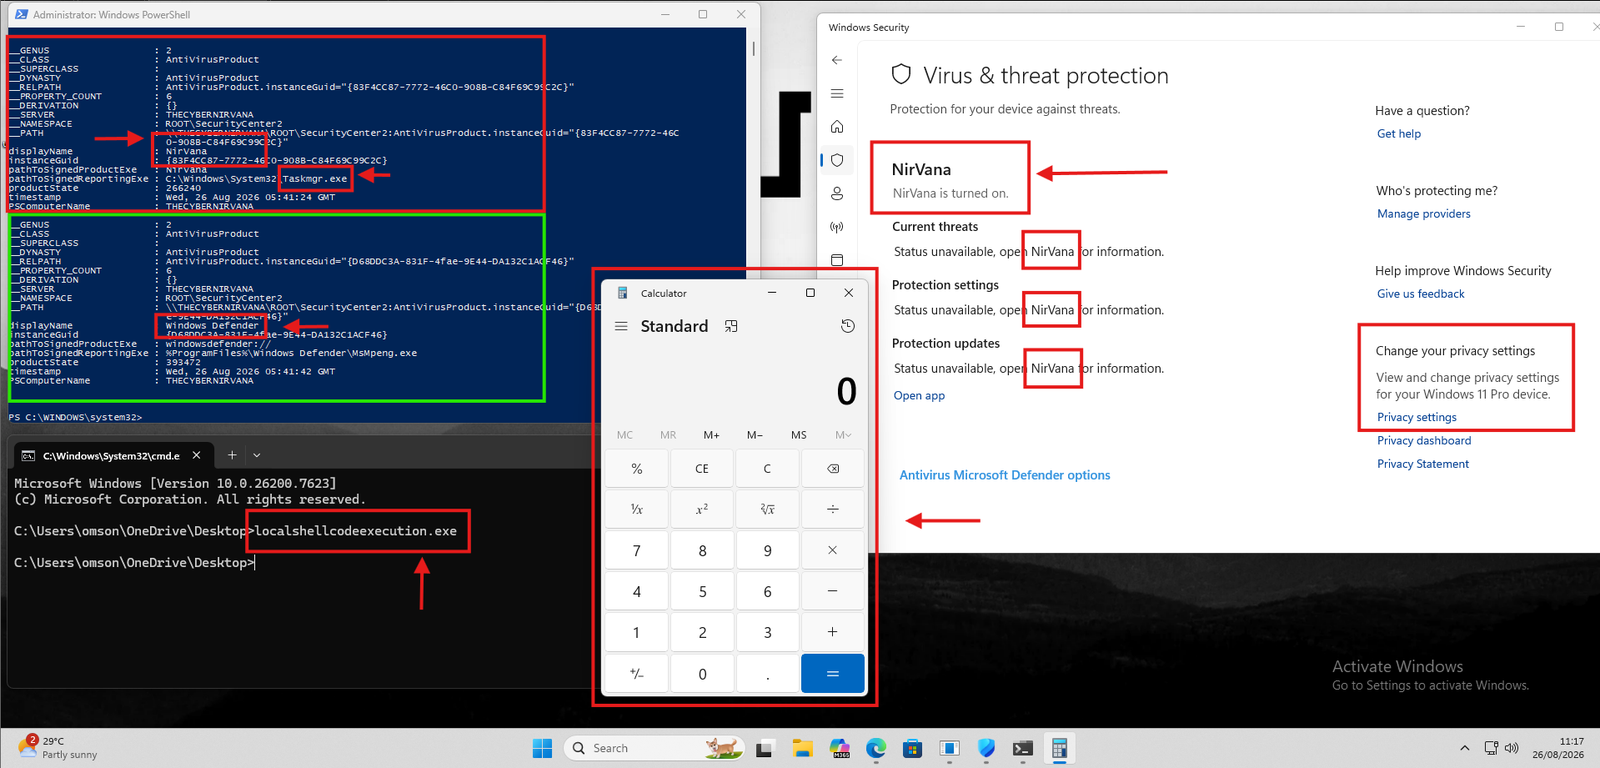 nirvanaon/own-defender
Research project reverse-engineering Windows Security Center COM interfaces to trace AV registration through ATL, vtable, WSCAPI, and RPC, with…
 own2pwn/r0ak
r0ak ("roak") is the Ring 0 Army Knife -- A Command Line Utility To Read/Write/Execute Ring Zero on for Windows 10 Systems
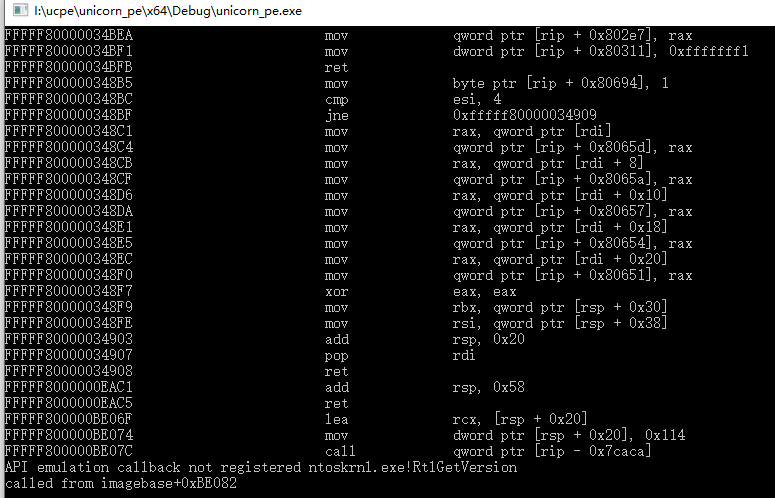 hzqst/unicorn_pe
Emulates Windows PE execution using Unicorn engine for malware analysis, unpacking packed binaries, and decrypting VMProtect strings and imports.
 ivan-sincek/invoker
Penetration testing utility and antivirus assessment tool.
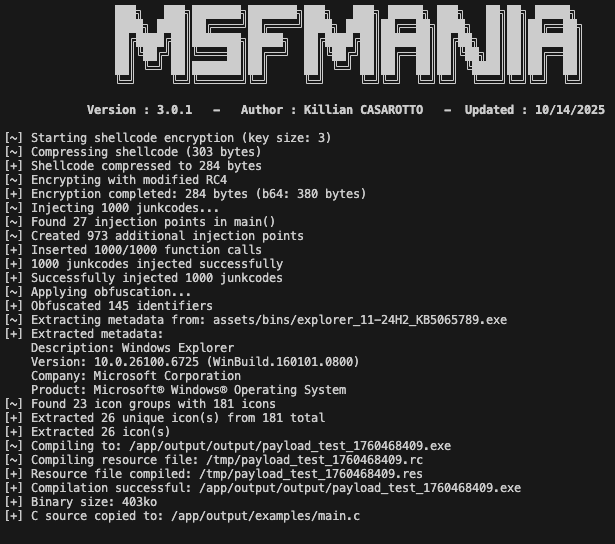 lepotekil/msfmania
Python AV Evasion Tools
