Frida-Labs
 dere-ad2001/frida-labs
The repo contains a series of challenges for learning Frida for Android Exploitation.
android-securitybinary-analysisctf+6
1.3k8 months ago
dere-ad2001/frida-labsThe repo contains a series of challenges for learning Frida for Android Exploitation.
 honeynet/apkinspector
APKinspector is a powerful GUI tool for analysts to analyze the Android applications.
 maoabc/nmmp
dex-vm used to protect the android classes.dex file
 ejfkdev/ddc
Android DEX → Java decompiler in Rust, built for speed — full apps in seconds, queries in milliseconds. Progressive analysis, javac-verified output,…
 ucsb-seclab/bootstomp
BootStomp: a bootloader vulnerability finder
 droidefense/engine
Droidefense: Advance Android Malware Analysis Framework
 rovellipaolo/ninjadroid
Ninja Reverse Engineering on Android APK packages
 hamz-a/frida-android-libbinder
PoC Frida script to view Android libbinder traffic
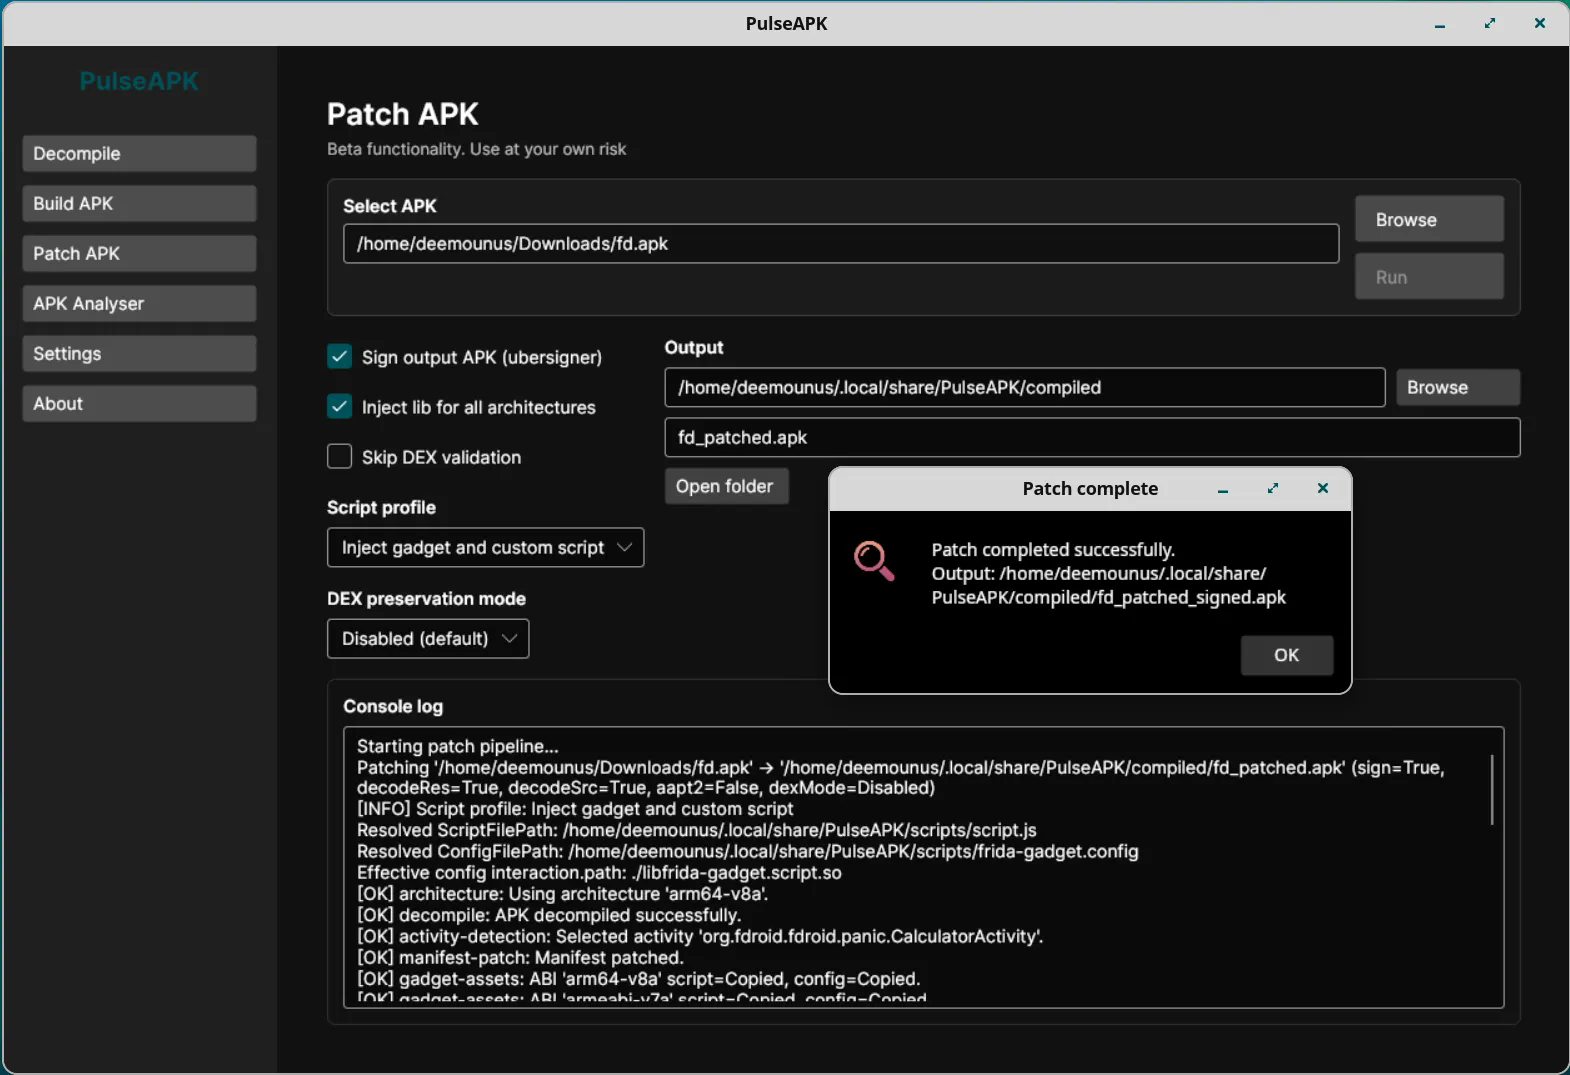 deemoun/pulseapk-core
PulseAPK Core: Cross-Platform tool for working with APK files: Decompilation, Analysis, Building
 brnpl/flutter-reverse-engineering-labs
Hands-on challenges for learning how to reverse engineer Flutter applications.
 ejfkdev/avdroot
Root an Android Studio emulator by patching its ramdisk with Magisk — in pure Go.
 ariyanpegu/ghostlock-app
GhostLock One-Tap Execution App (CVE-2026-43499)
 bishopfox/mauidll
Extract the managed (.NET) assemblies out of a MAUI Android assembly store.