
IDA2Obj
 jhftss/ida2obj
Static binary instrumentation tool that dumps COFF object files from executables, enabling code/data insertion at any location for black-box fuzzing…
binary-analysisdebuggersfuzzing+2
122
jhftss/ida2objStatic binary instrumentation tool that dumps COFF object files from executables, enabling code/data insertion at any location for black-box fuzzing…
 secretsquirrel/recomposer
Randomly changes Win32/64 PE Files for 'safer' uploading to malware and sandbox sites.
 idiom/pftriage
Python tool and library to help analyze files during malware triage and analysis.
 user1342/obfu-de-scate
Fuzzy comparison tool for deobfuscating Android APKs by identifying renamed functions across versions, generating mapping files and interactive HTML…
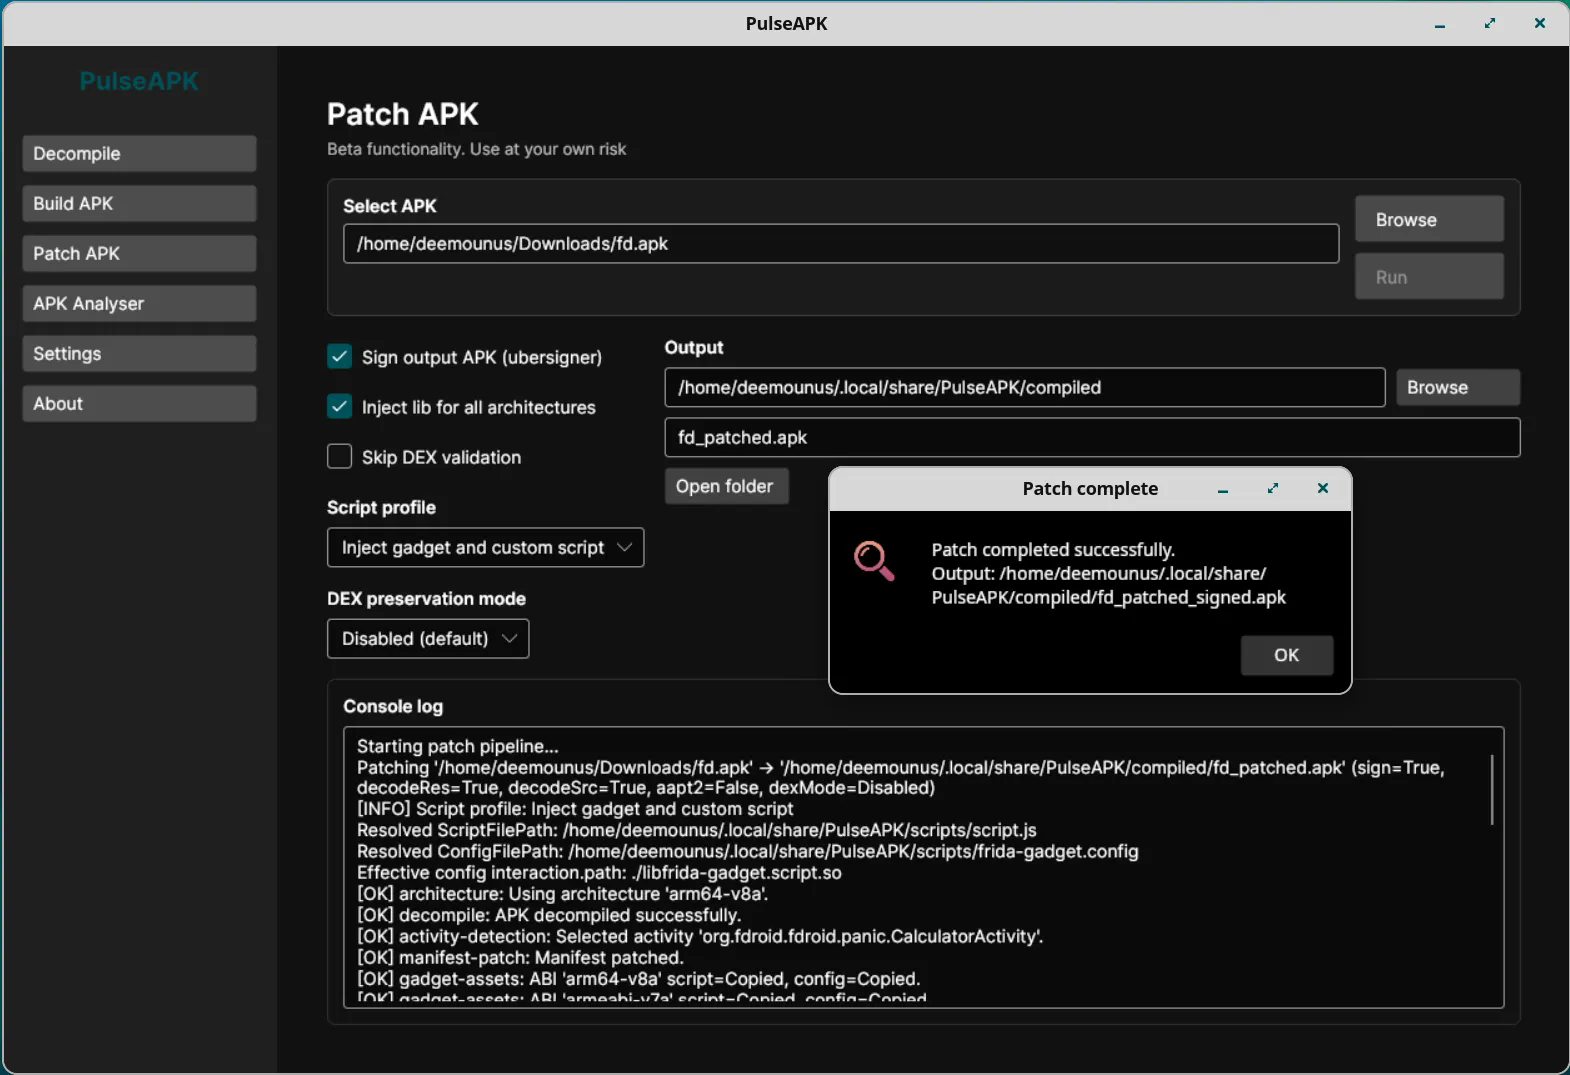 deemoun/pulseapk-core
PulseAPK Core: Cross-Platform tool for working with APK files: Decompilation, Analysis, Building
 utkonos/lst2x64dbg
Extract labels from IDA, Ghidra, Binary Ninja, and Relyze files and export x64dbg database. Including radare2 main address.
 hiddenillusion/nomorexor
Tool to help guess a files 256 byte XOR key by using frequency analysis
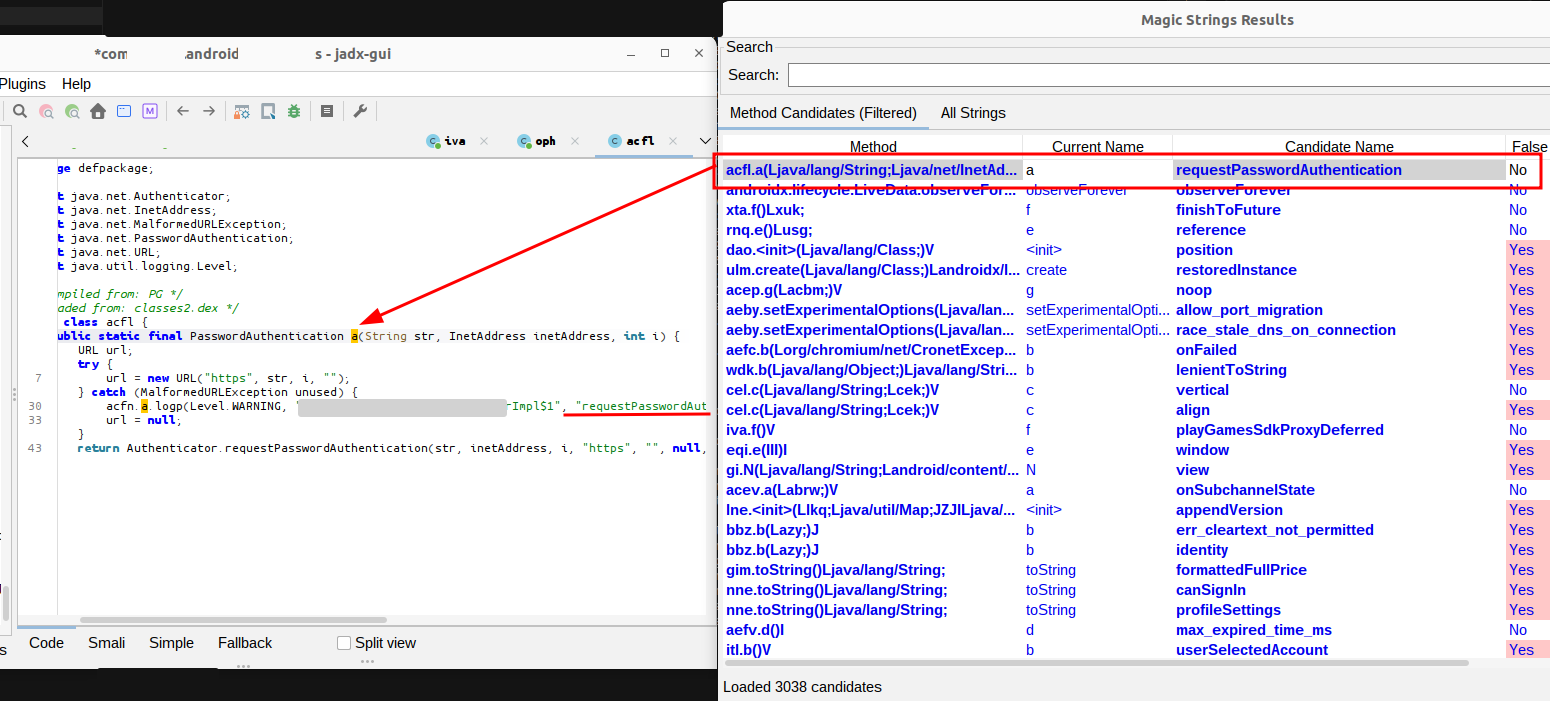 0rshemesh/jadx-magic-strings
JADX plugin that extracts method names, class references, and source file paths from string constants found in DEX files and decompiled Android code.
 aaron-kidwell/golol
goLoL is a Windows host scanner with dual support for LOLBAS binaries and LOLDrivers. It lists LOLBAS techniques runnable at your current privilege…
 hasherezade/pe2pic
Small visualizator for PE files
 pstirparo/machofile
machofile is a module to parse Mach-O binary files
 xchwarze/magic-extractor
Universal Windows extraction tool that detects unknown files and routes them to the right bundled extractor.
 cxiao/rust-reversing-workshop-recon-2024
Slides and files for the Reversing Rust Binaries: One step beyond strings workshop at REcon 2024, presented on June 28, 2024.
 iilegacyyii/exportdumper
A small tool I made to dump the export table of PE files. The primary use case was intended for use within DLL proxying.
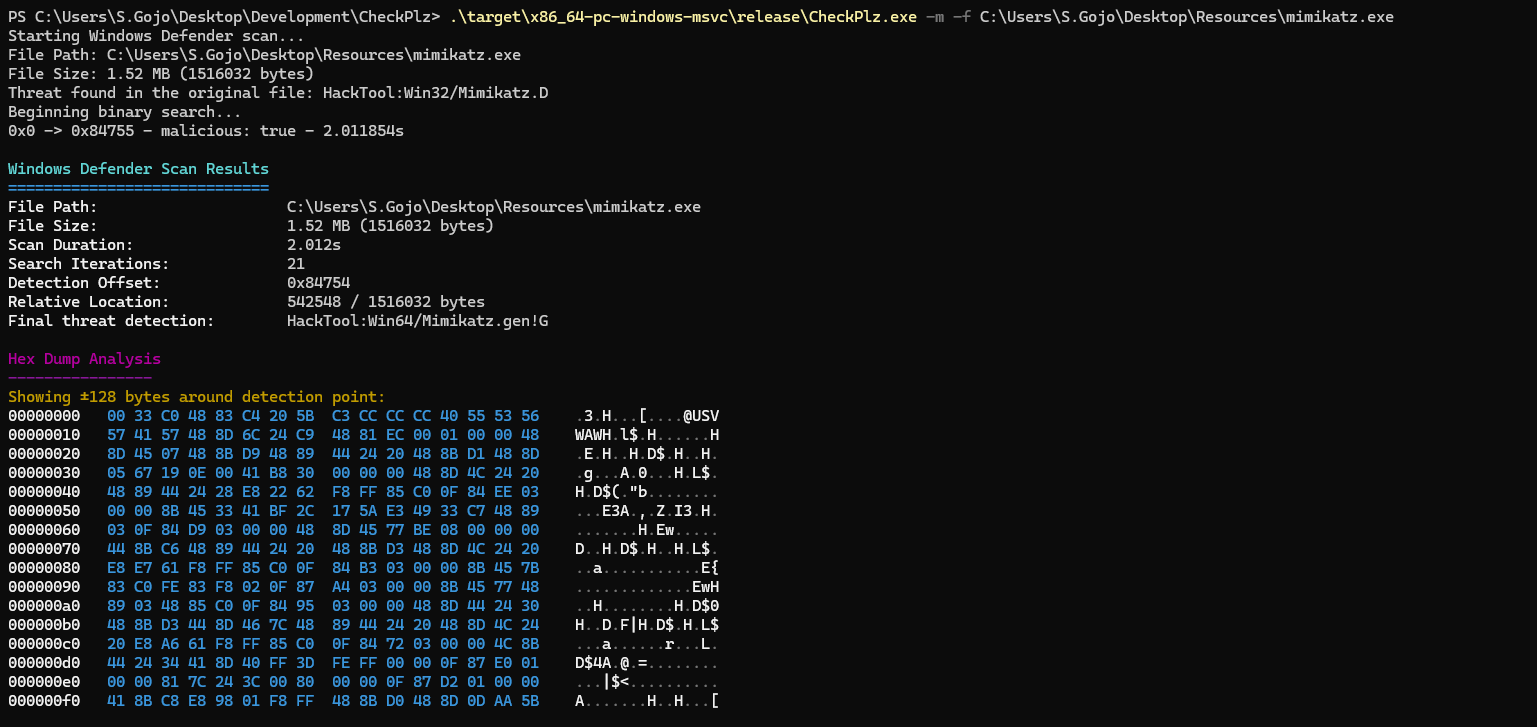 blacksnufkin/checkplz
Scan files for potential threats while leveraging AMSI (Antimalware Scan Interface) and Windows Defender. By isolating malicious content.
 iss4cf0ng/dotnetpeloader
A C# PE loader for x64 and x86 PE files.