

rr
 rr-debugger/rr
Record and replay framework for deterministic debugging of multi-threaded applications, enabling reverse execution, hardware watchpoints, and…
binary-analysisdebuggersdynamic-code-analysis
rr-debugger/rrRecord and replay framework for deterministic debugging of multi-threaded applications, enabling reverse execution, hardware watchpoints, and…
 fuzzysecurity/powershell-suite
My musings with PowerShell
 airbus-seclab/bincat
Binary code static analyser, with IDA integration. Performs value and taint analysis, type reconstruction, use-after-free and double-free detection
 seekbytes/ipa
GUI analyzer for deep-diving into PDF files. Detect malicious payloads, understand object relationships, and extract key information for threat…
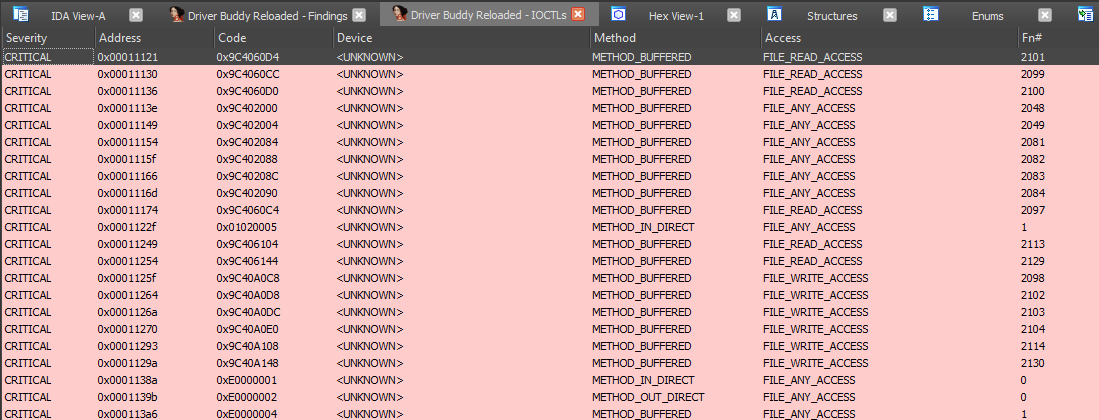 voidsec/driverbuddyreloaded
Driver Buddy Reloaded is an IDA Pro Python plugin that helps automate some tedious Windows Kernel Drivers reverse engineering tasks
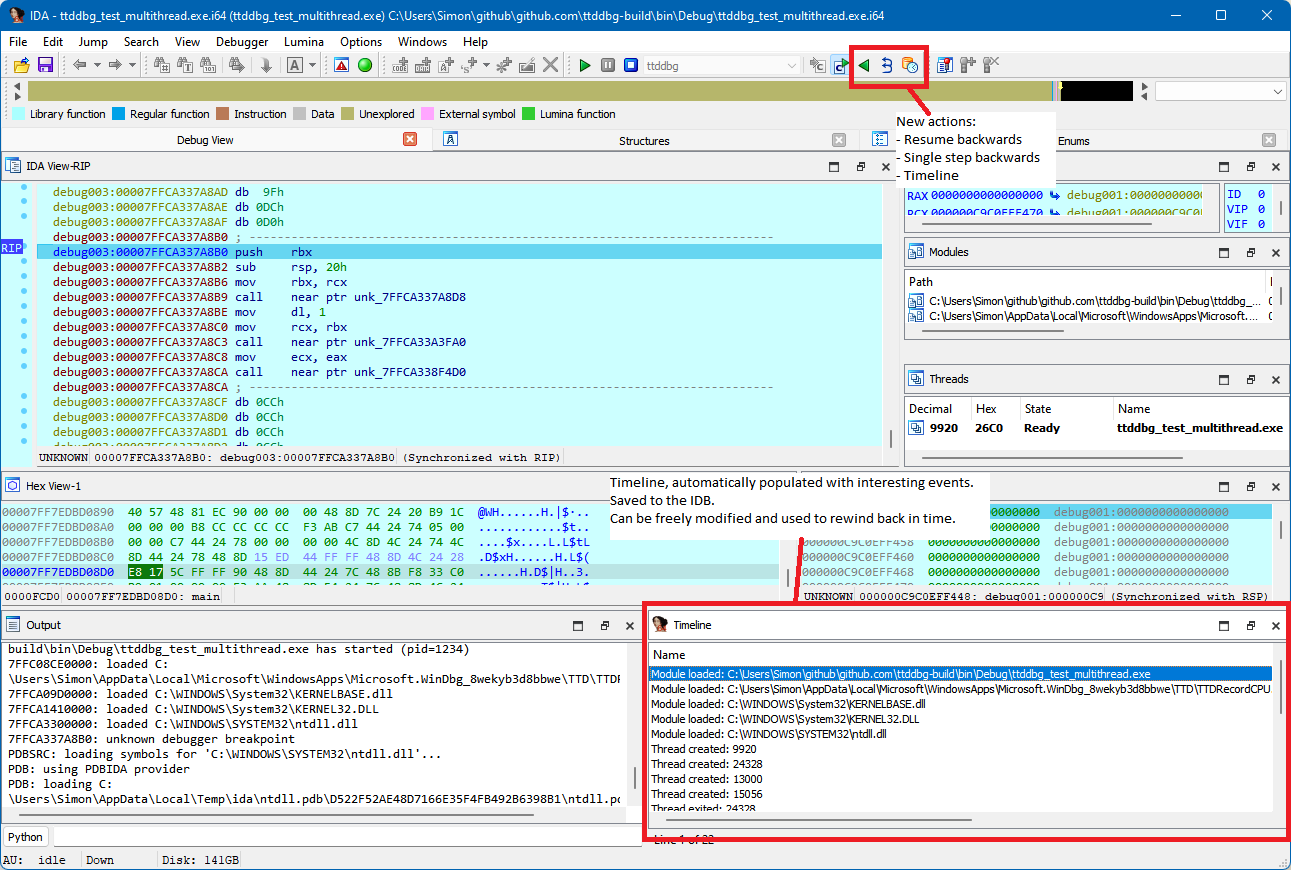 airbus-cert/ttddbg
Time Travel Debugging IDA plugin
 gui774ume/krie
Linux Kernel Runtime Integrity with eBPF
 byt3bl33d3r/nimdllsideload
DLL sideloading/proxying with Nim!
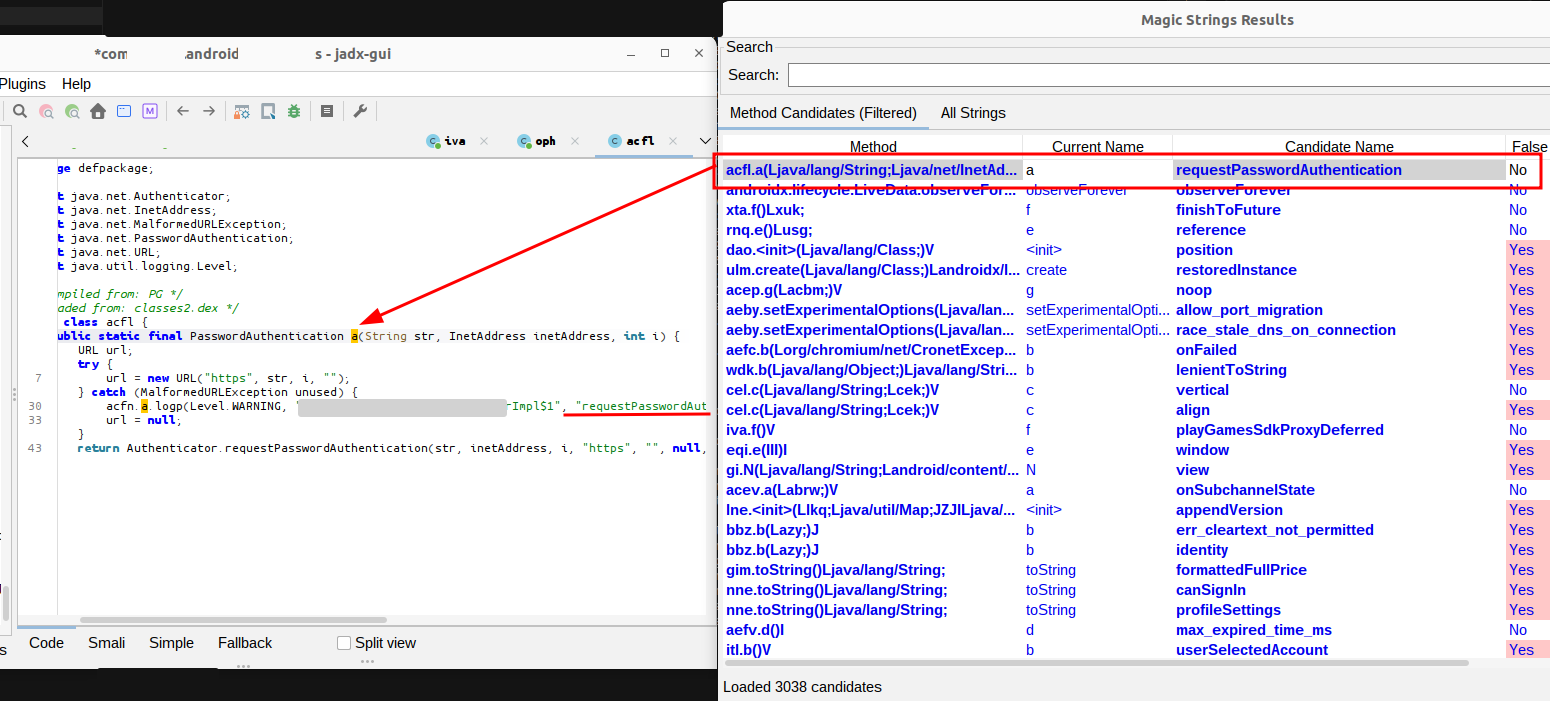 0rshemesh/jadx-magic-strings
JADX plugin that extracts method names, class references, and source file paths from string constants found in DEX files and decompiled Android code.
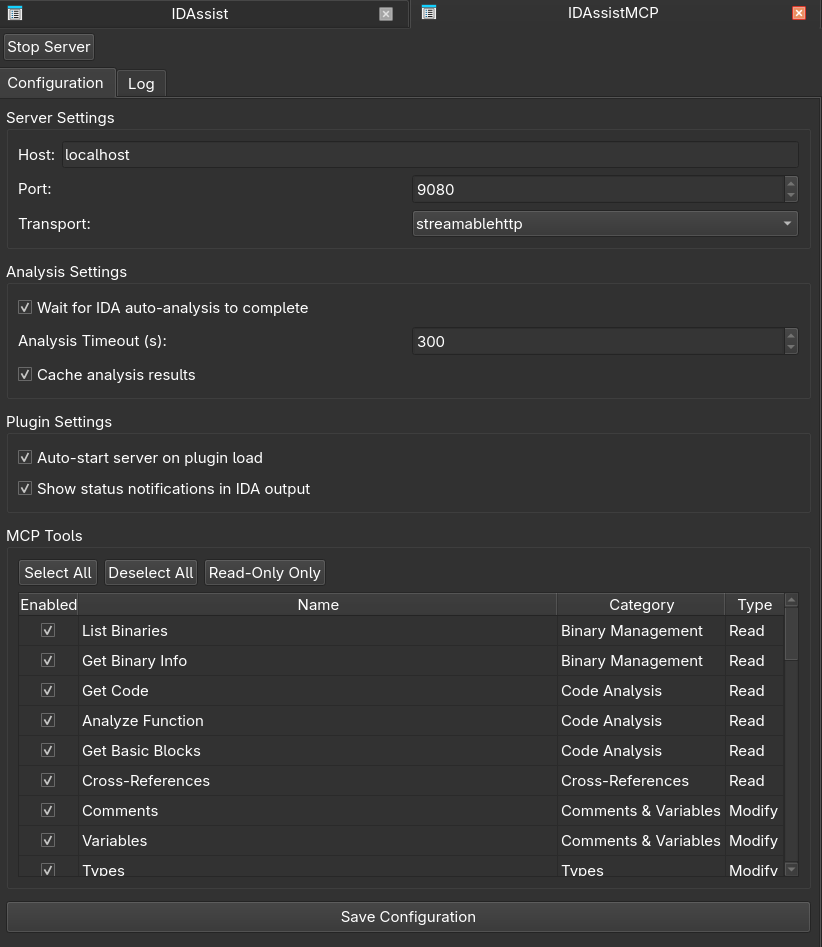 symgraph/idassistmcp
Standalone MCP server plugin for IDA Pro.
 elevenpaths/pesto
Extracts and analyzes PE file security characteristics (ASLR, DEP, CFG, NO_SEH) from DLLs and EXEs across directories, storing results in a SQLite…
 hasherezade/pesieve-go
Golang bindings for PE-sieve
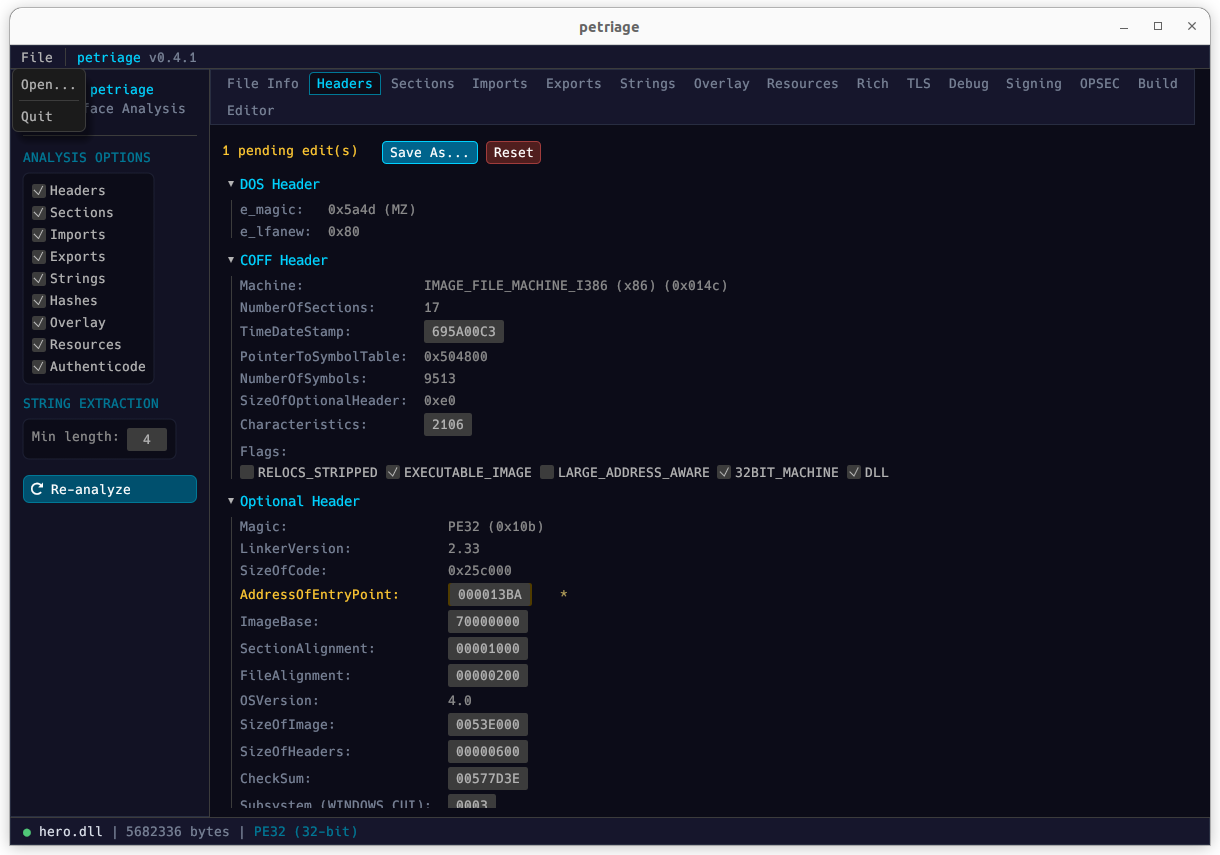 uky007/petriage
PETriage: A symbol-unified PE file reader for triage, built for multi-platform and multi-interface use.
 farazsth98/freebsd-dirent-info-leak-bugs
CVE-2020-25578 and CVE-2020-25579: Some FreeBSD info leak bugs I found in 2020.
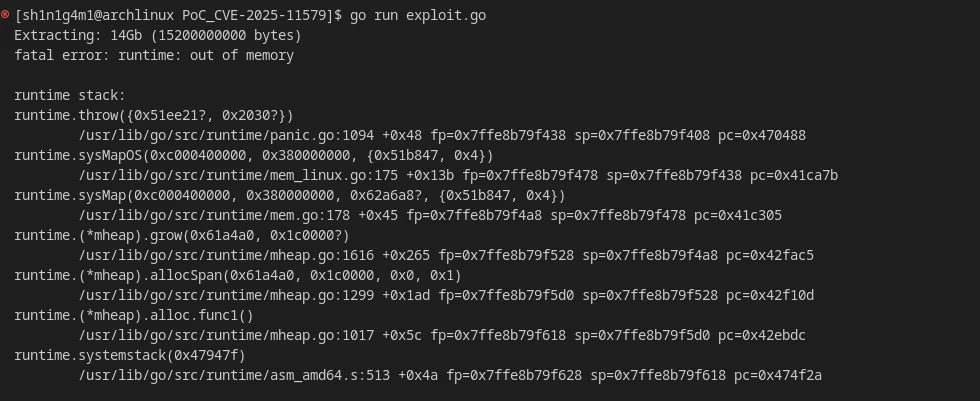 shinigami-777/poc_cve-2025-11579
Proof-of-concept exploit for CVE-2025-11579, a denial-of-service vulnerability in rardecode that triggers an out-of-memory crash via a crafted RAR…
 aflplusplus/aflplusplus
AFL++ is a state-of-the-art fuzzer, and #1 in benchmarks. It was originally based on AFL. Today it comes with qemu 5.1, collision-free coverage,…
 keystone-engine/keystone
Multi-architecture assembler framework that converts assembly source into machine code for Arm, x86, MIPS, PowerPC, RISC-V, and more, with a…
 0vercl0k/wtf
Distributed, code-coverage guided snapshot-based fuzzer for user and kernel-mode targets on Windows and Linux, with emulator and hypervisor backends.