
LibPNG_OSS-Fuzz
 enessar/libpng_oss-fuzz
Security research project on fuzzing libpng with OSS-Fuzz. Includes seed corpus analysis, custom read/write fuzzers, and a proof-of-concept exploit…
binary-analysiscode-analysiseducation+3
1
enessar/libpng_oss-fuzzSecurity research project on fuzzing libpng with OSS-Fuzz. Includes seed corpus analysis, custom read/write fuzzers, and a proof-of-concept exploit…
 gmh5225/frida-medit
Cross-platform CUI process memory scanner built on Frida for finding, filtering, patching, and dumping live process memory during reverse engineering…
 kevinbackhouse/djvulibre-poc-cve-2025-53367
Proof-of-concept exploit for CVE-2025-53367, a vulnerability in the DjVuLibre library. Demonstrates exploitation of a memory corruption bug in DjVu…
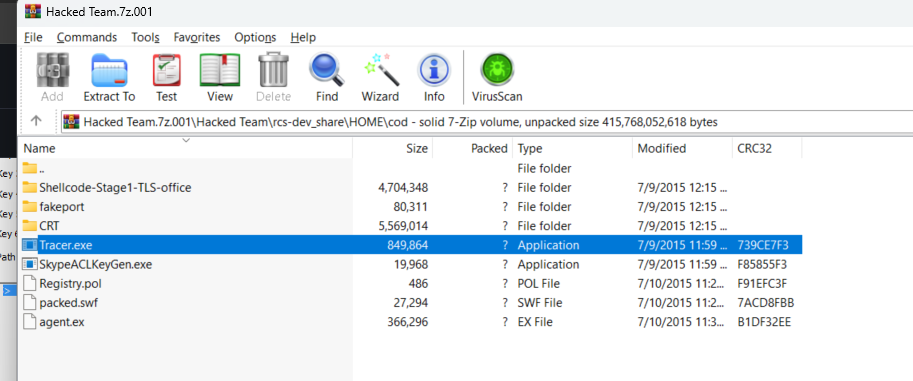 spiralbl0ck/skypeaclkeygen.exe-analysis-for-hacking-team
SkypeACLKeyGen.exe analysis for hacking team
 intrigus-lgtm/cve-2020-14955
Proof-of-concept exploit for CVE-2020-14955 targeting a kernel driver IOCTL vulnerability in Jiangmin Antivirus 16.0.13.129 on Windows 7 x32.
 gleaming0/cve-2019-13288
CVE-2019-13288 analysis repository: bundles the Xpdf PDF parser source and documentation to reproduce, analyze, and patch the vulnerable parsing…
 googleprojectzero/brokentype
TrueType and OpenType font fuzzing toolset
 avast/retdec
RetDec is a retargetable machine-code decompiler based on LLVM.
 hasherezade/pe-bear
Portable Executable reversing tool with a friendly GUI
 erocarrera/pefile
pefile is a Python module to read and work with PE (Portable Executable) files
 hasherezade/pe-sieve
Scans a given process. Recognizes and dumps a variety of potentially malicious implants (replaced/injected PEs, shellcodes, hooks, in-memory patches).
 glmcdona/process-dump
Windows tool for dumping malware PE files from memory back to disk for analysis.
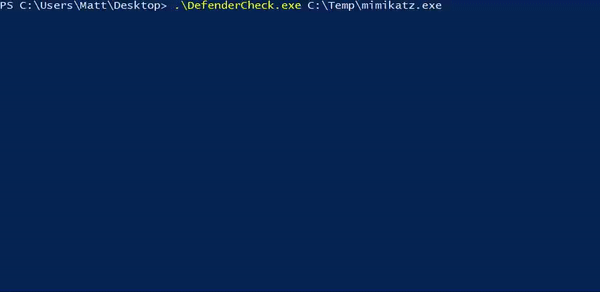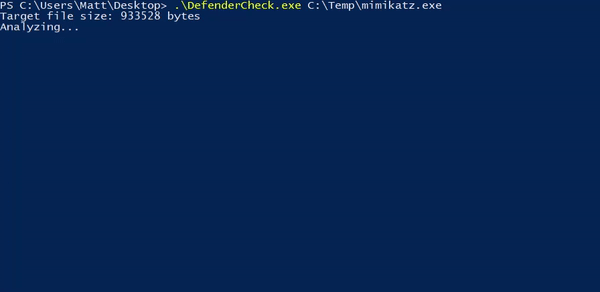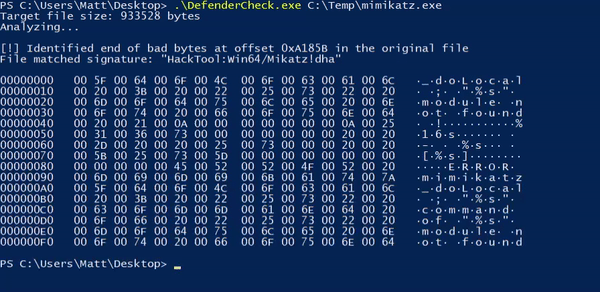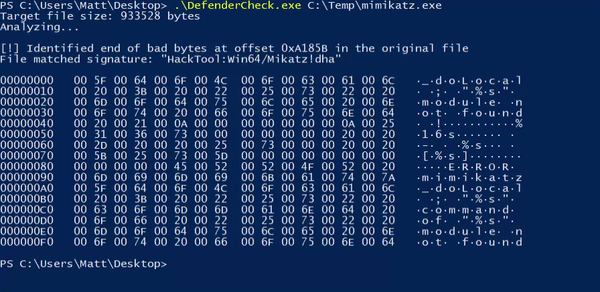 matterpreter/defendercheck
Identifies the bytes that Microsoft Defender flags on.
 justicerage/manalyze
Static analyzer for PE executables with plugin-based detection of packers, compilers, suspicious imports, cryptographic constants, and ClamAV…
 justasmasiulis/lazy_importer
library for importing functions from dlls in a hidden, reverse engineer unfriendly way
 hasherezade/libpeconv
Custom PE loading and manipulation library for manual mapping, IAT hooking, memory dumping, and rebuilding imports for malware analysis and reverse…
 rasta-mouse/threatcheck
Identifies the bytes that Microsoft Defender / AMSI Consumer flags on.