
Archived
uefi_retool
 yeggor/uefi_retool
A tool for UEFI firmware reverse engineering
binary-analysisembedded-systems-securityfirmware-analysis+3
yeggor/uefi_retoolA tool for UEFI firmware reverse engineering
 fuzzinglabs/octopus
Security Analysis tool for WebAssembly module (wasm) and Blockchain Smart Contracts (BTC/ETH/NEO/EOS)
 skylot/jadx
Command-line and GUI tool for decompiling Android Dex and APK files into readable Java source code, with resource decoding, deobfuscation, and Smali…
 ibotpeaches/apktool
A tool for reverse engineering Android apk files
 mr-un1k0d3r/edrs
Red team tool for EDR evasion: dynamically resolves syscall IDs, patches ntdll stubs, unhooks IAT hooks, and lists hooked APIs from major EDR vendors.
 honeynet/apkinspector
APKinspector is a powerful GUI tool for analysts to analyze the Android applications.
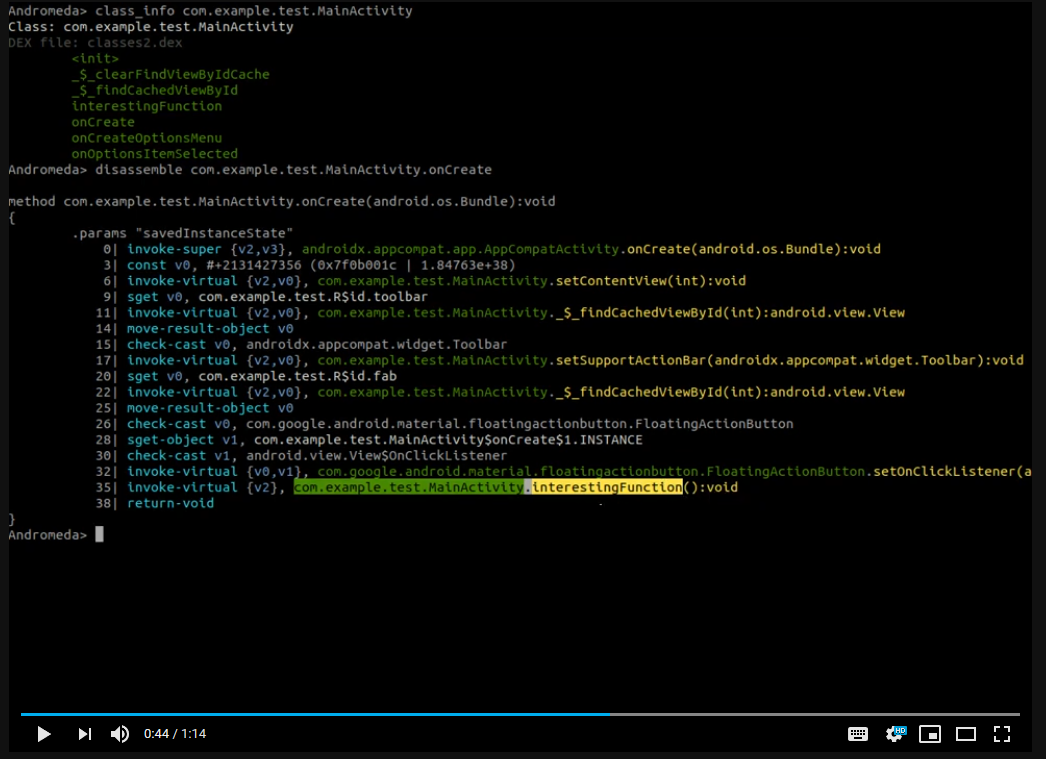 secrary/andromeda
C/C++ interactive reverse engineering tool for Android applications, enabling fast static analysis and binary inspection of APK files.
 foundryzero/binder-trace
Binder Trace is a tool for intercepting and parsing Android Binder messages. Think of it as "Wireshark for Binder".
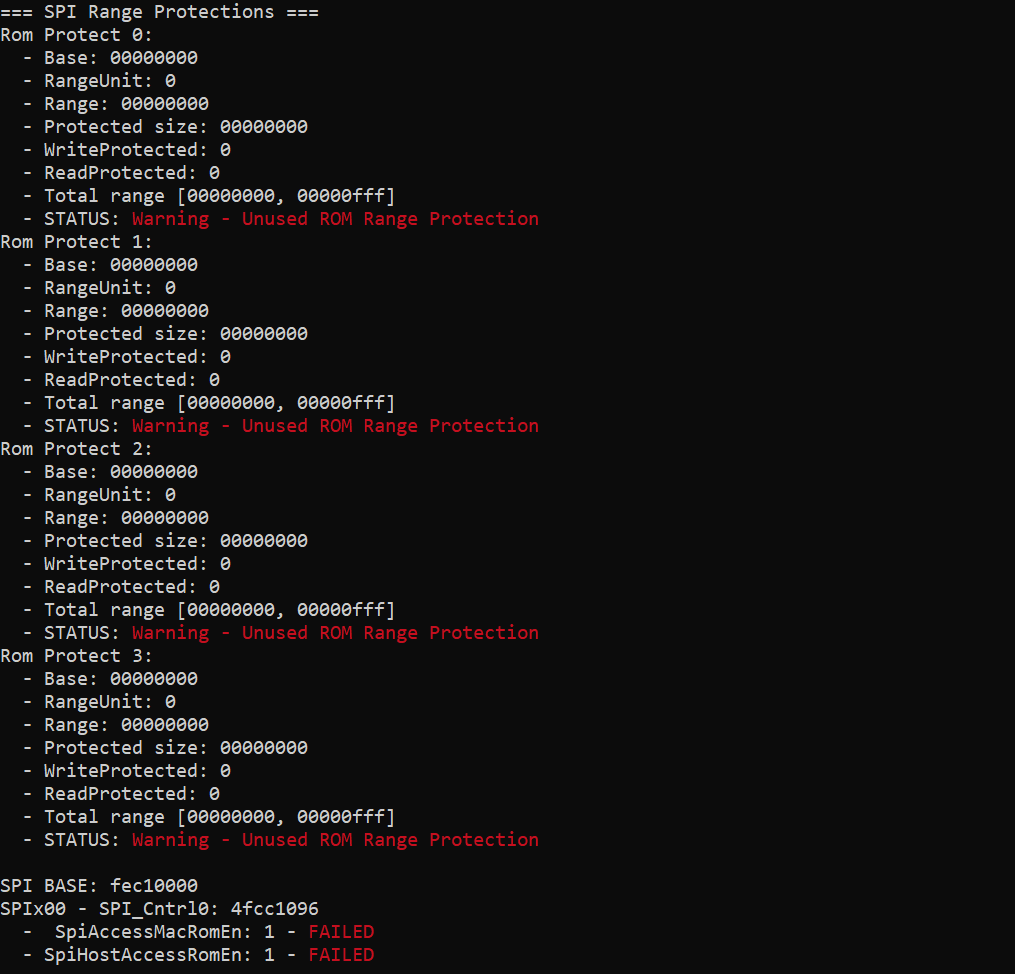 ioactive/platbox
Platform security assessment tool for dumping and analyzing UEFI/SMM registers, PCI config space, physical memory, SPI flash, and S3 bootscripts with…
 sterrasec/ipa-medit
Memory modification tool for re-signed ipa supports iOS apps running on iPhone and Apple Silicon Mac without jailbreaking.
 user1342/obfu-de-scate
Fuzzy comparison tool for deobfuscating Android APKs by identifying renamed functions across versions, generating mapping files and interactive HTML…
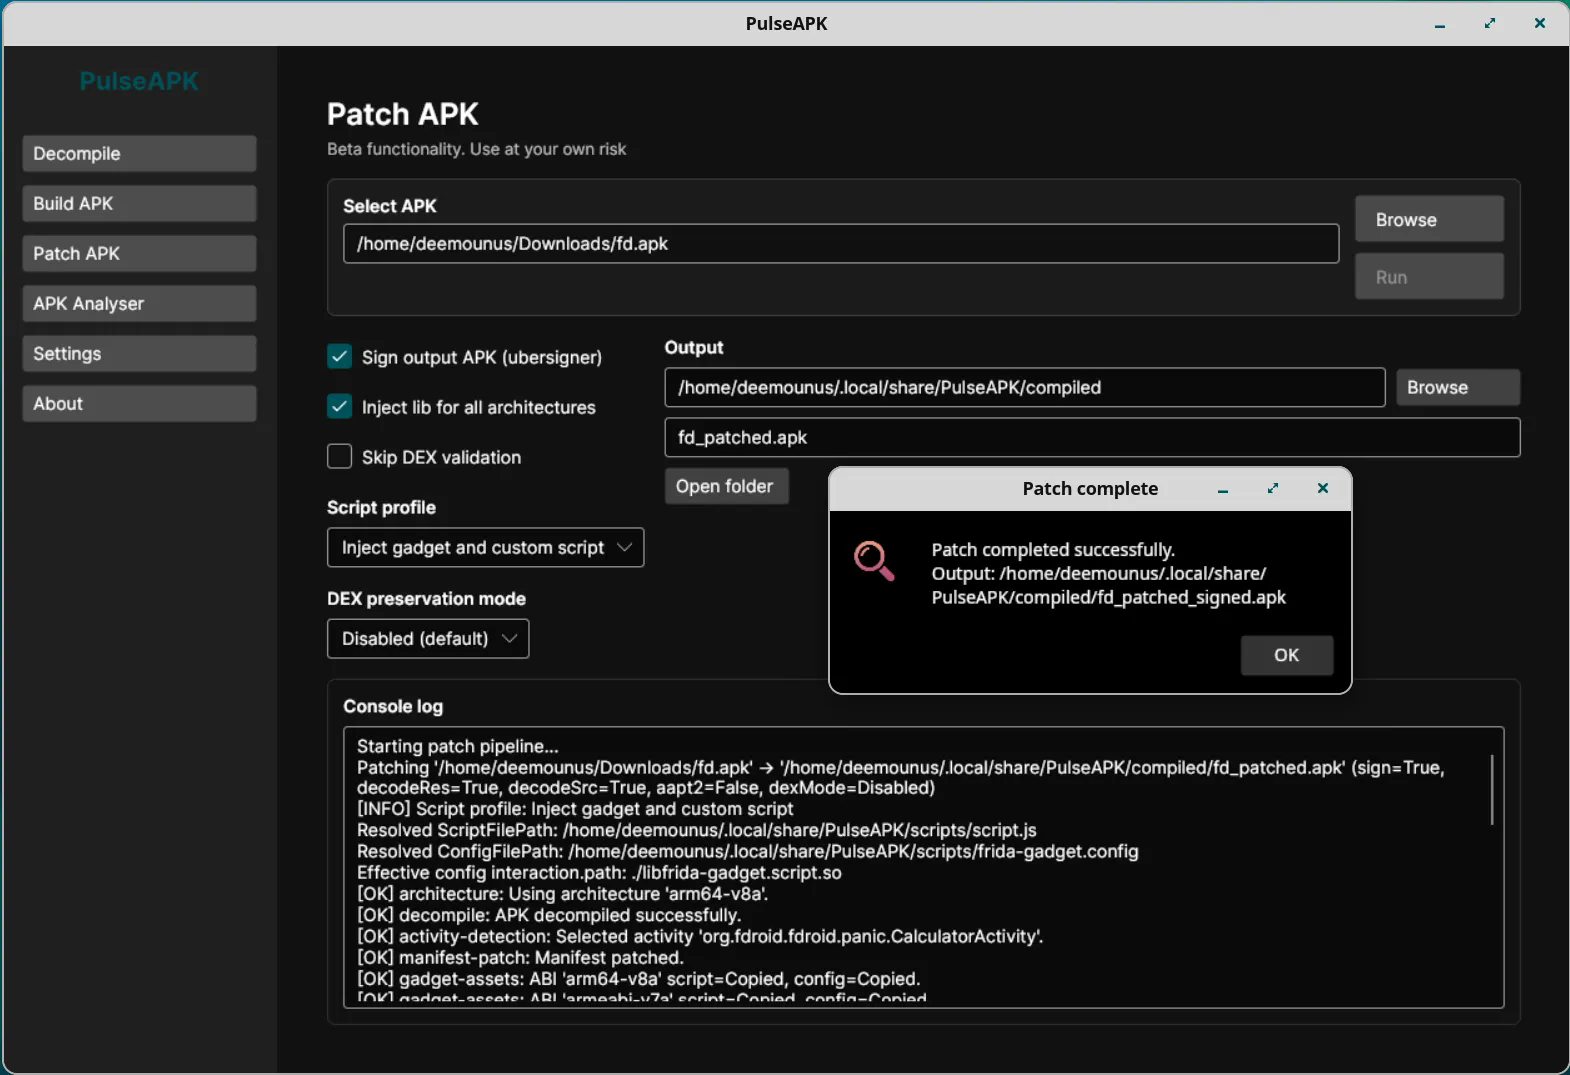 deemoun/pulseapk-core
PulseAPK Core: Cross-Platform tool for working with APK files: Decompilation, Analysis, Building
 dzmitry-savitski/android-pentest-tool
Android penetration testing tool for Kali linux
 m0n1x90/elfxtract
Automated ELF binary analysis tool for CTF/PWN challenges. Extracts security mitigations, ROP gadgets, PLT/GOT tables, and decompiles ASM to C using…
 oldboy21/shgenob
Python based tool for generating Shellcode from PIC C
 sonyxperiadev/apkanalyser
Static analysis tool for Android APKs that inspects Dalvik bytecode, decodes XML resources, and detects potential issues. Supports binary…
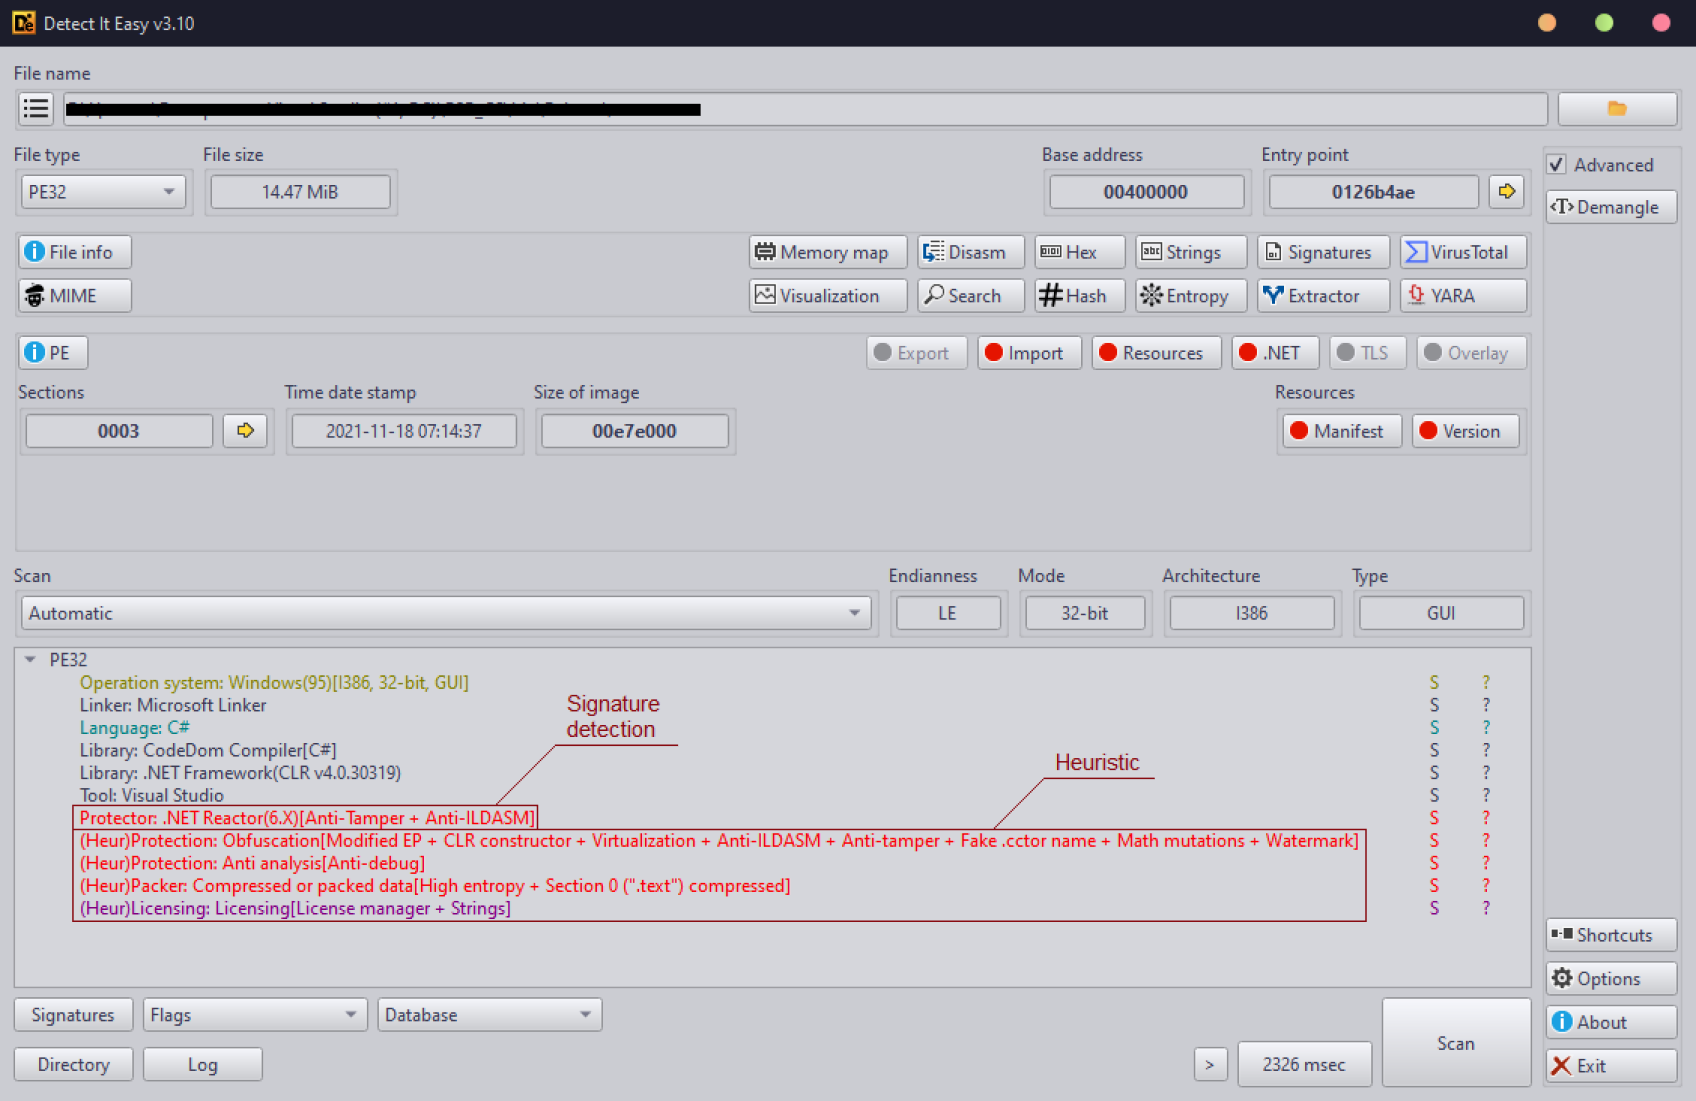 horsicq/detect-it-easy
Program for determining types of files for Windows, Linux and MacOS.
 rr-debugger/rr
Record and replay framework for deterministic debugging of multi-threaded applications, enabling reverse execution, hardware watchpoints, and…