
class-dump
 nygard/class-dump
Generate Objective-C headers from Mach-O files.
binary-analysisios-securityreverse-engineering+1
nygard/class-dumpGenerate Objective-C headers from Mach-O files.
 nowsecure/r2frida
Radare2 and Frida better together.
 reversenseorg/dexcalibur
[Official] Android reverse engineering tool focused on dynamic instrumentation automation leveraging Frida. It disassembles dex, analyzes it…
 0xdea/frida-scripts
A collection of my Frida instrumentation scripts to reverse engineer mobile apps and more.
 dere-ad2001/frida-labs
The repo contains a series of challenges for learning Frida for Android Exploitation.
 chichou/grapefruit
Open-source mobile security testing suite for iOS and Android. Previously Passionfruit
 honeynet/apkinspector
APKinspector is a powerful GUI tool for analysts to analyze the Android applications.
 xtiankisutsa/mara_framework
MARA is a Mobile Application Reverse engineering and Analysis Framework. It is a toolkit that puts together commonly used mobile application reverse…
 chichou/vscode-frida
Unofficial frida extension for VSCode
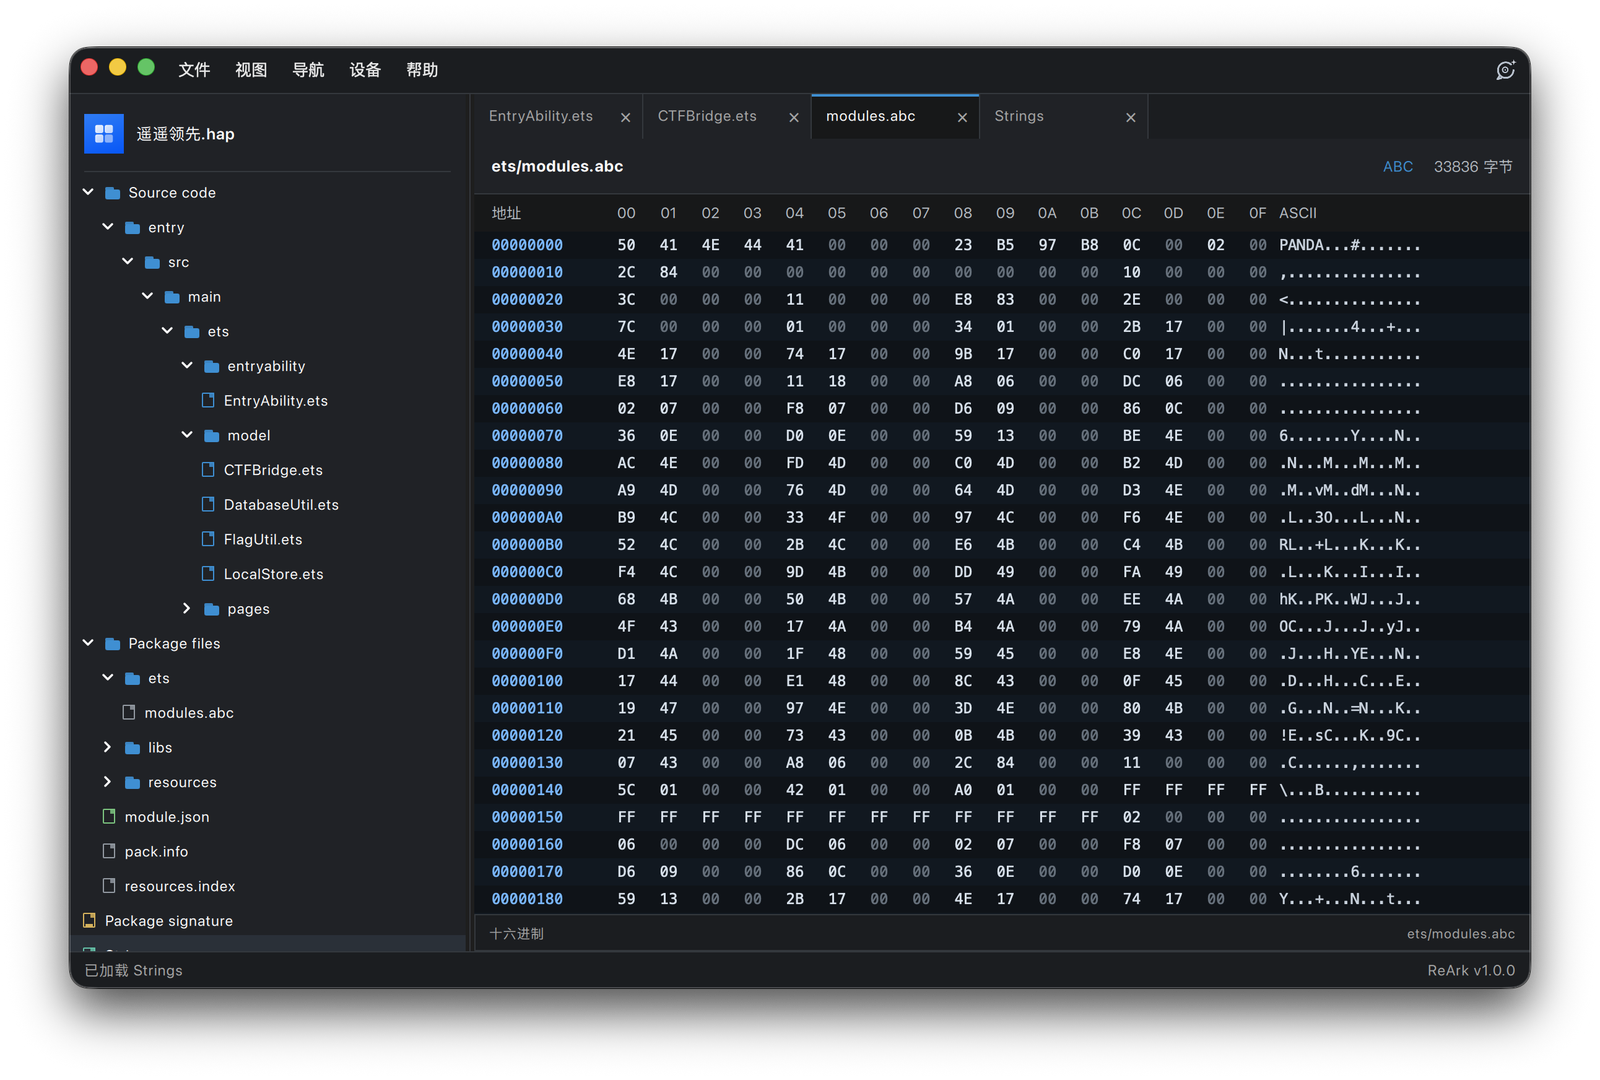 lkimuk/reark
An intelligent reverse engineering analysis tool designed for multiple target platforms, currently supporting HarmonyOS (HAP/APP/ABC) and Android…
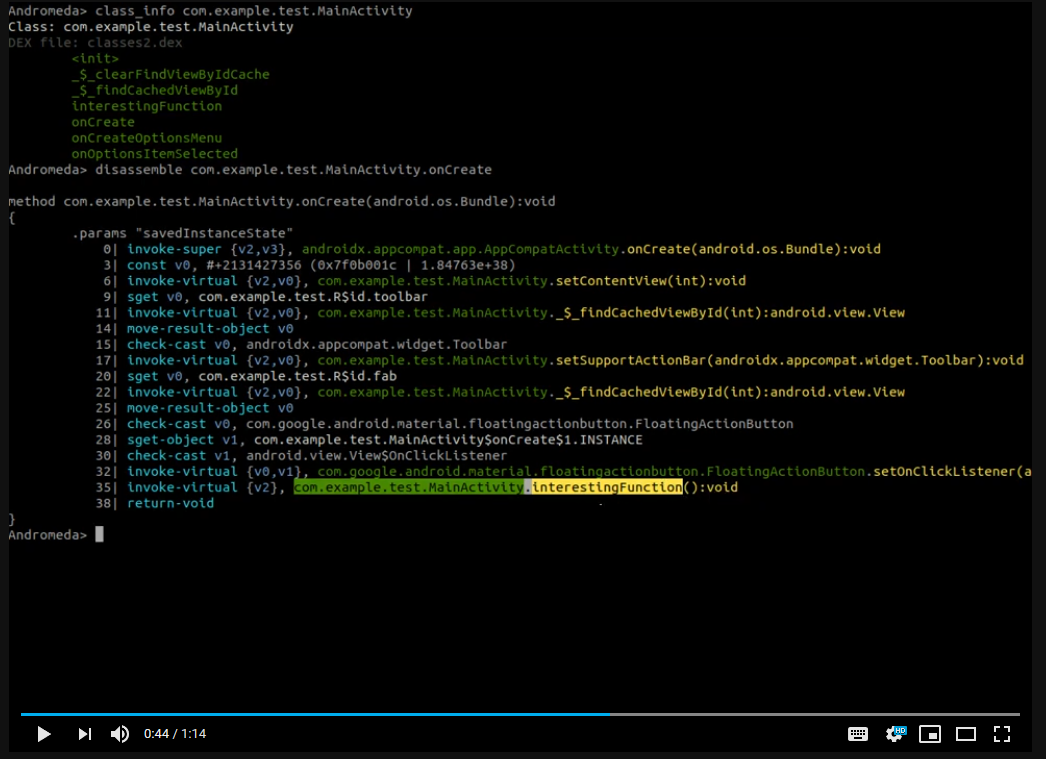 secrary/andromeda
C/C++ interactive reverse engineering tool for Android applications, enabling fast static analysis and binary inspection of APK files.
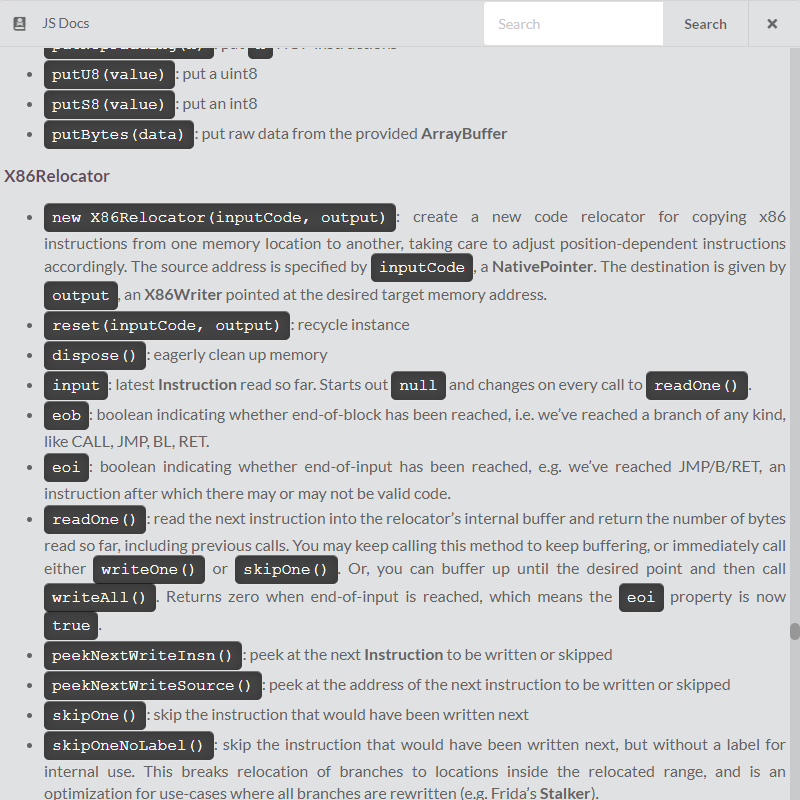 fuzzysecurity/fermion
Fermion, an electron wrapper for Frida & Monaco.
 droidefense/engine
Droidefense: Advance Android Malware Analysis Framework
 arguslab/argus-saf
Scala-based static analysis framework for Android and Java bytecode with flow analysis, decompilation, and native code analysis via symbolic…
 rovellipaolo/ninjadroid
Ninja Reverse Engineering on Android APK packages
 symbioticsec/hermes-decomp
A powerful decompiler that lets you reverse-engineer React Native mobile apps by converting their compiled Hermes bytecode (.hbc) files back into…
 plum-umd/redexer
The Redexer binary instrumentation framework for Dalvik bytecode