
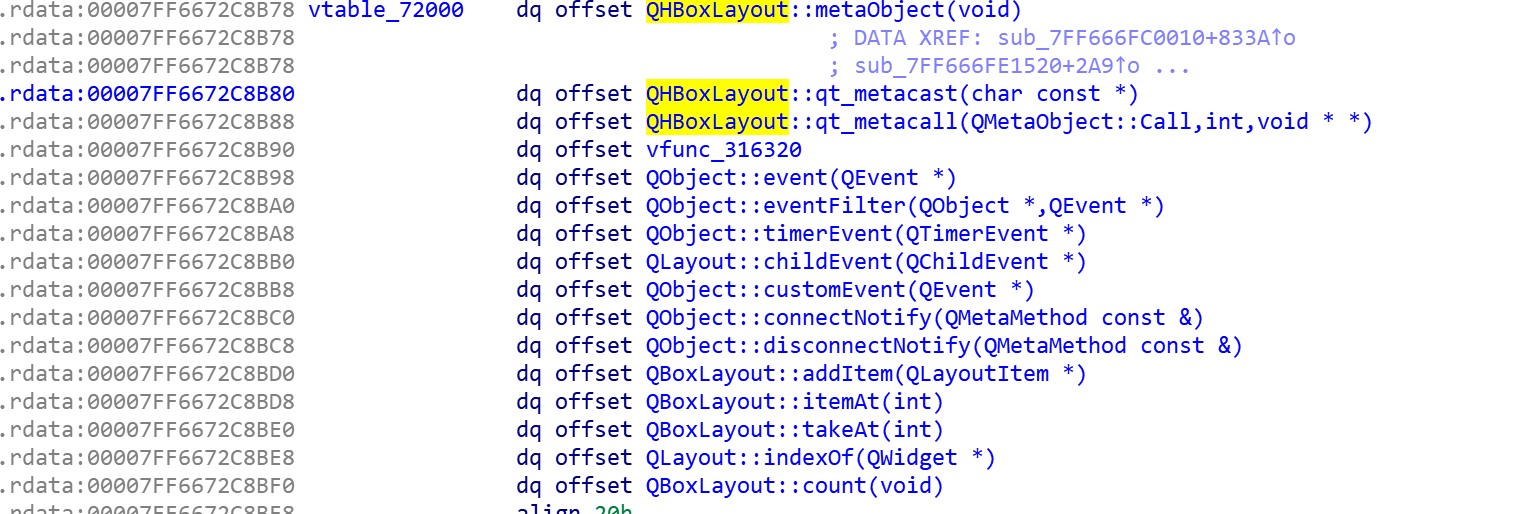
Virtuailor
 0xgalz/virtuailor
IDAPython tool for creating automatic C++ virtual tables in IDA Pro
binary-analysisdebuggersdynamic-analysis-sandboxing+2
1.4k6 years ago
0xgalz/virtuailorIDAPython tool for creating automatic C++ virtual tables in IDA Pro
 marin-m/vmlinux-to-elf
A tool to recover a fully analyzable .ELF from a raw kernel, through extracting the kernel symbol table (kallsyms)
 glmcdona/process-dump
Windows tool for dumping malware PE files from memory back to disk for analysis.
 honeynet/apkinspector
APKinspector is a powerful GUI tool for analysts to analyze the Android applications.
 gjduck/e9patch
A powerful static binary rewriting tool
 rscloura/doldrums
A Flutter/Dart reverse engineering tool
 noobpk/frida-ios-hook
A tool that helps you easy trace classes, functions, and modify the return values of methods on iOS platform
 steven-michaud/hookcase
Tool for reverse engineering macOS/OS X
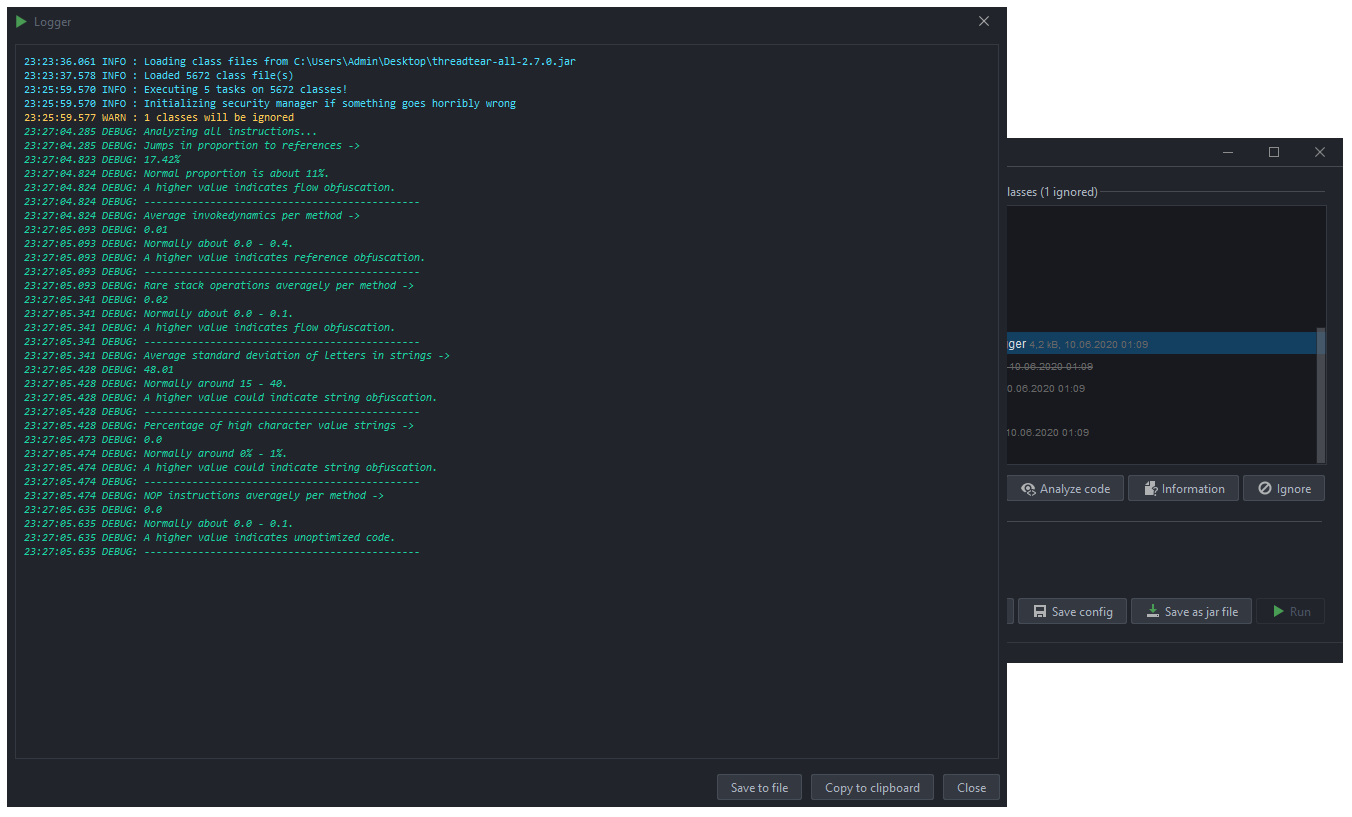 loerting/threadtear
Multifunctional java deobfuscation tool suite
 ucsb-seclab/dr_checker
DR.CHECKER : A Soundy Vulnerability Detection Tool for Linux Kernel Drivers
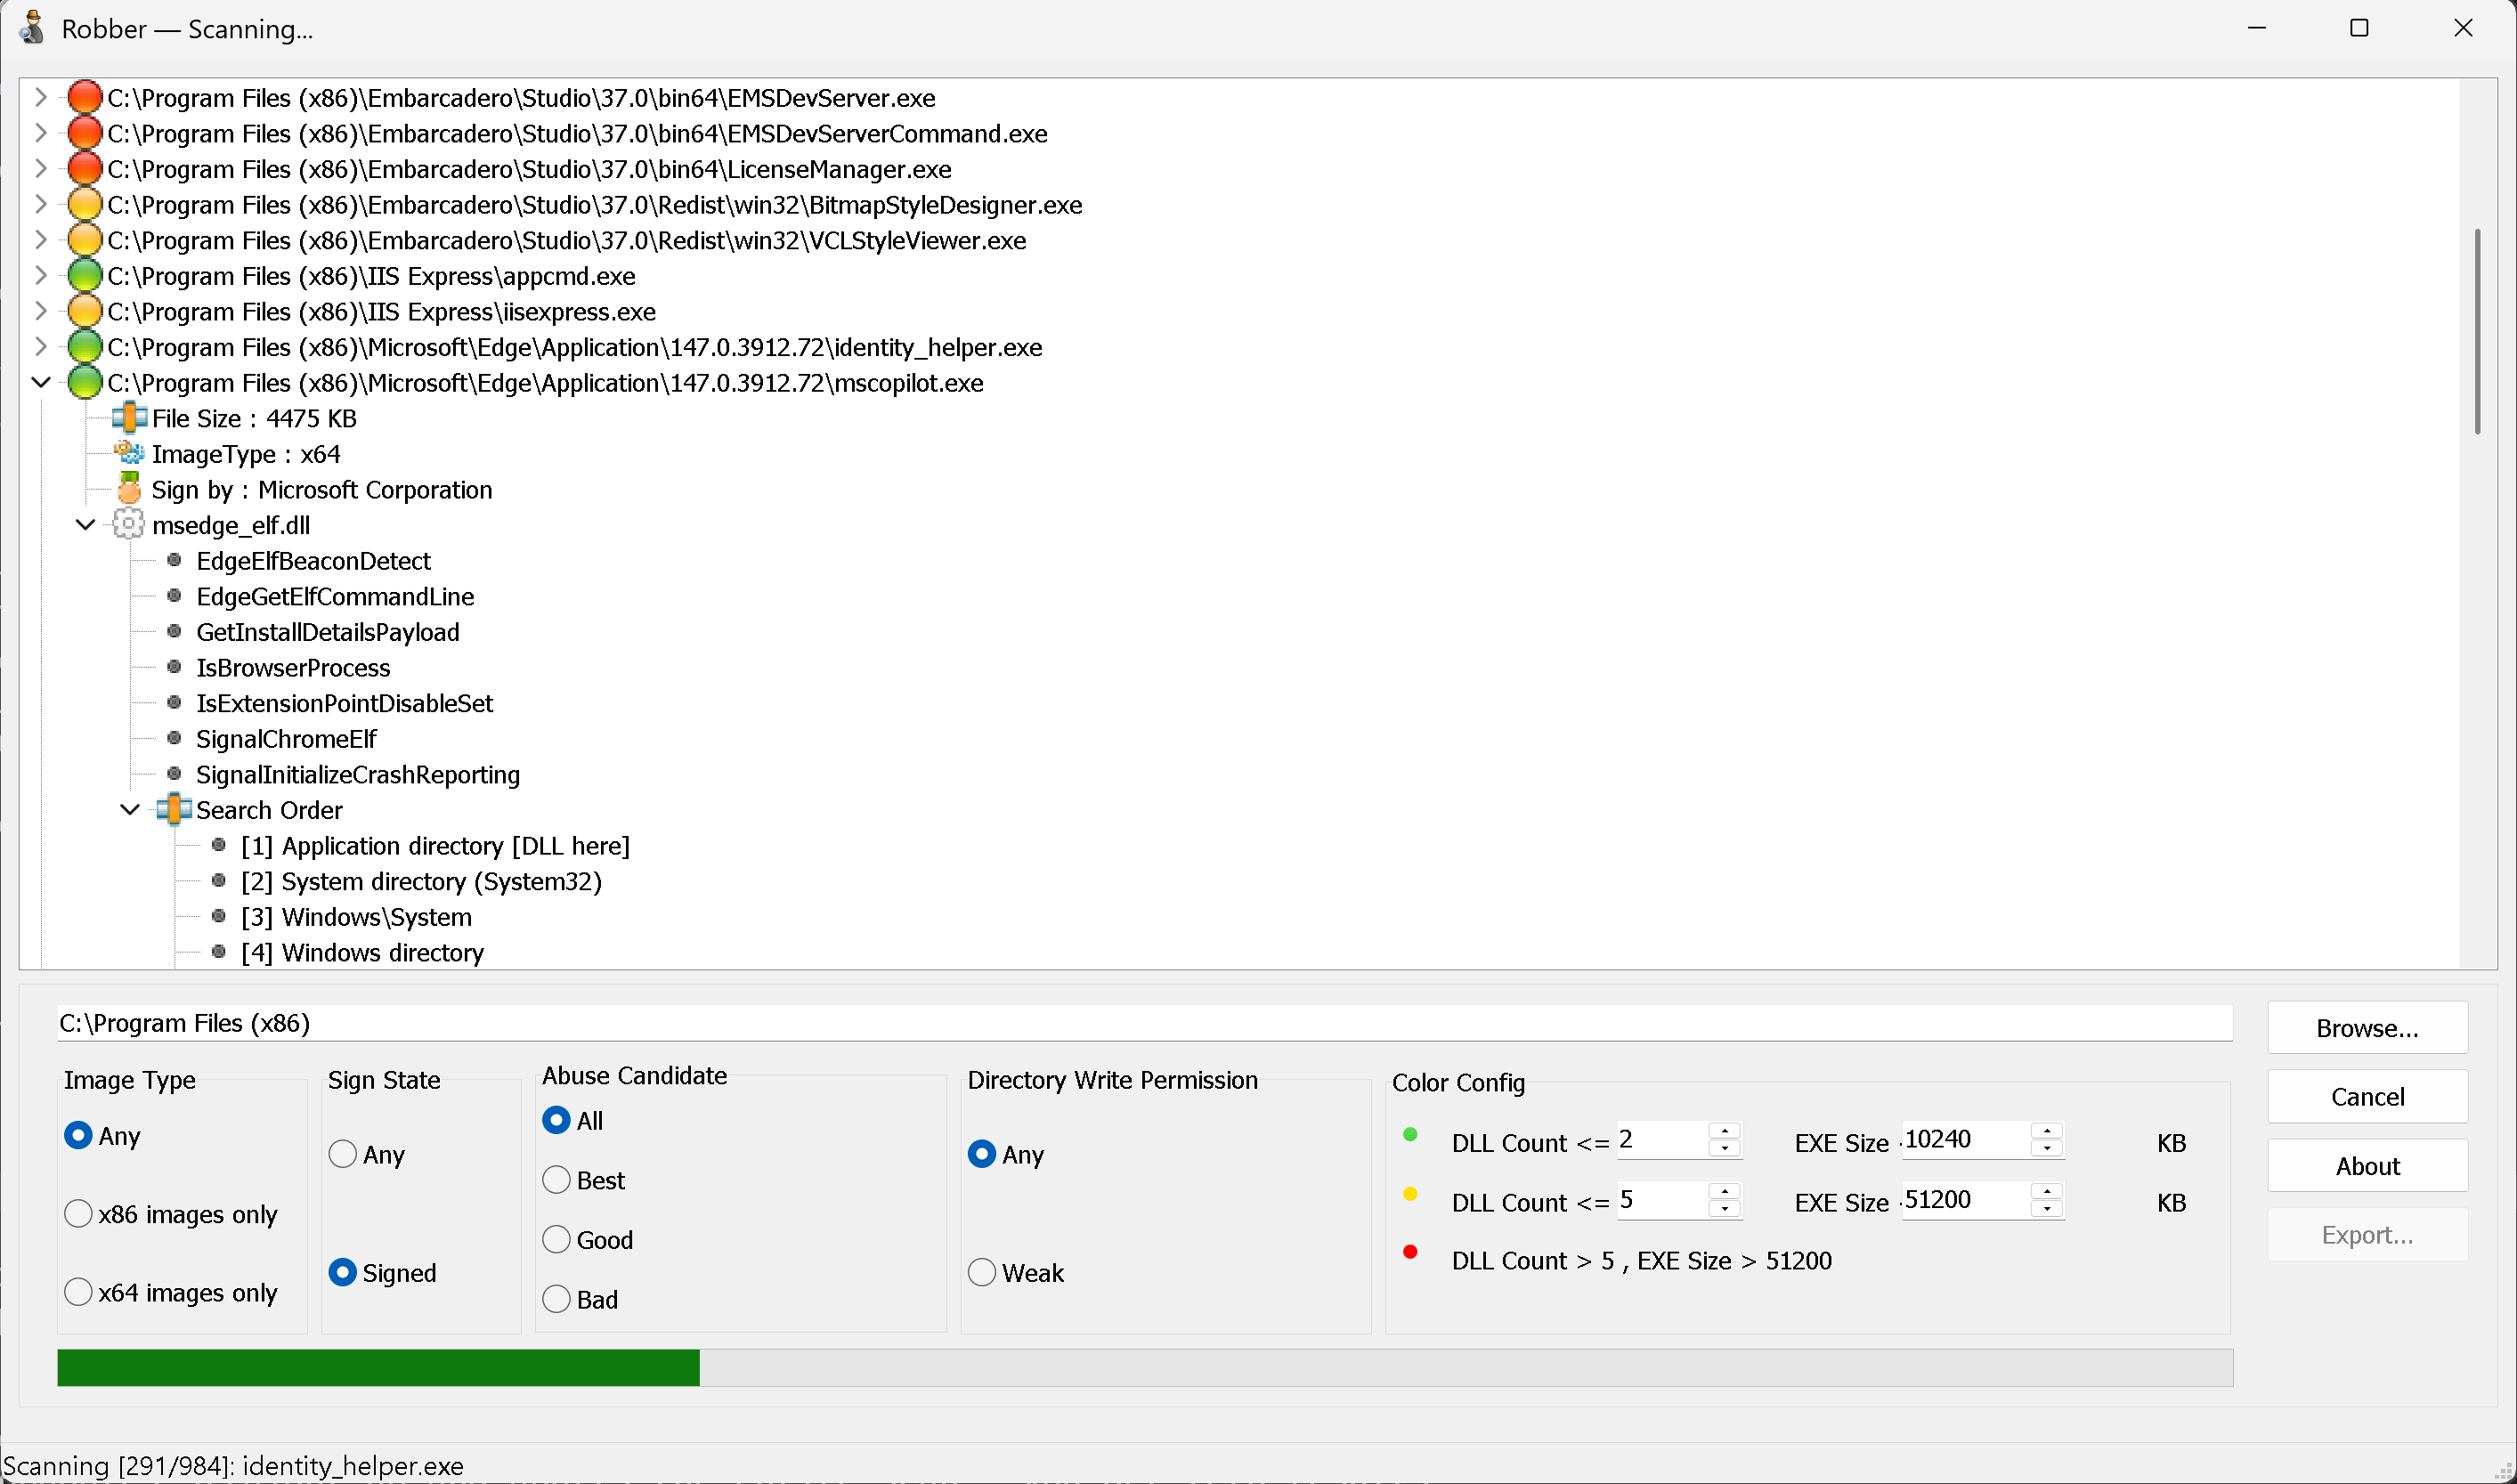 mojtabatajik/robber
Robber is open source tool for finding executables prone to DLL hijacking
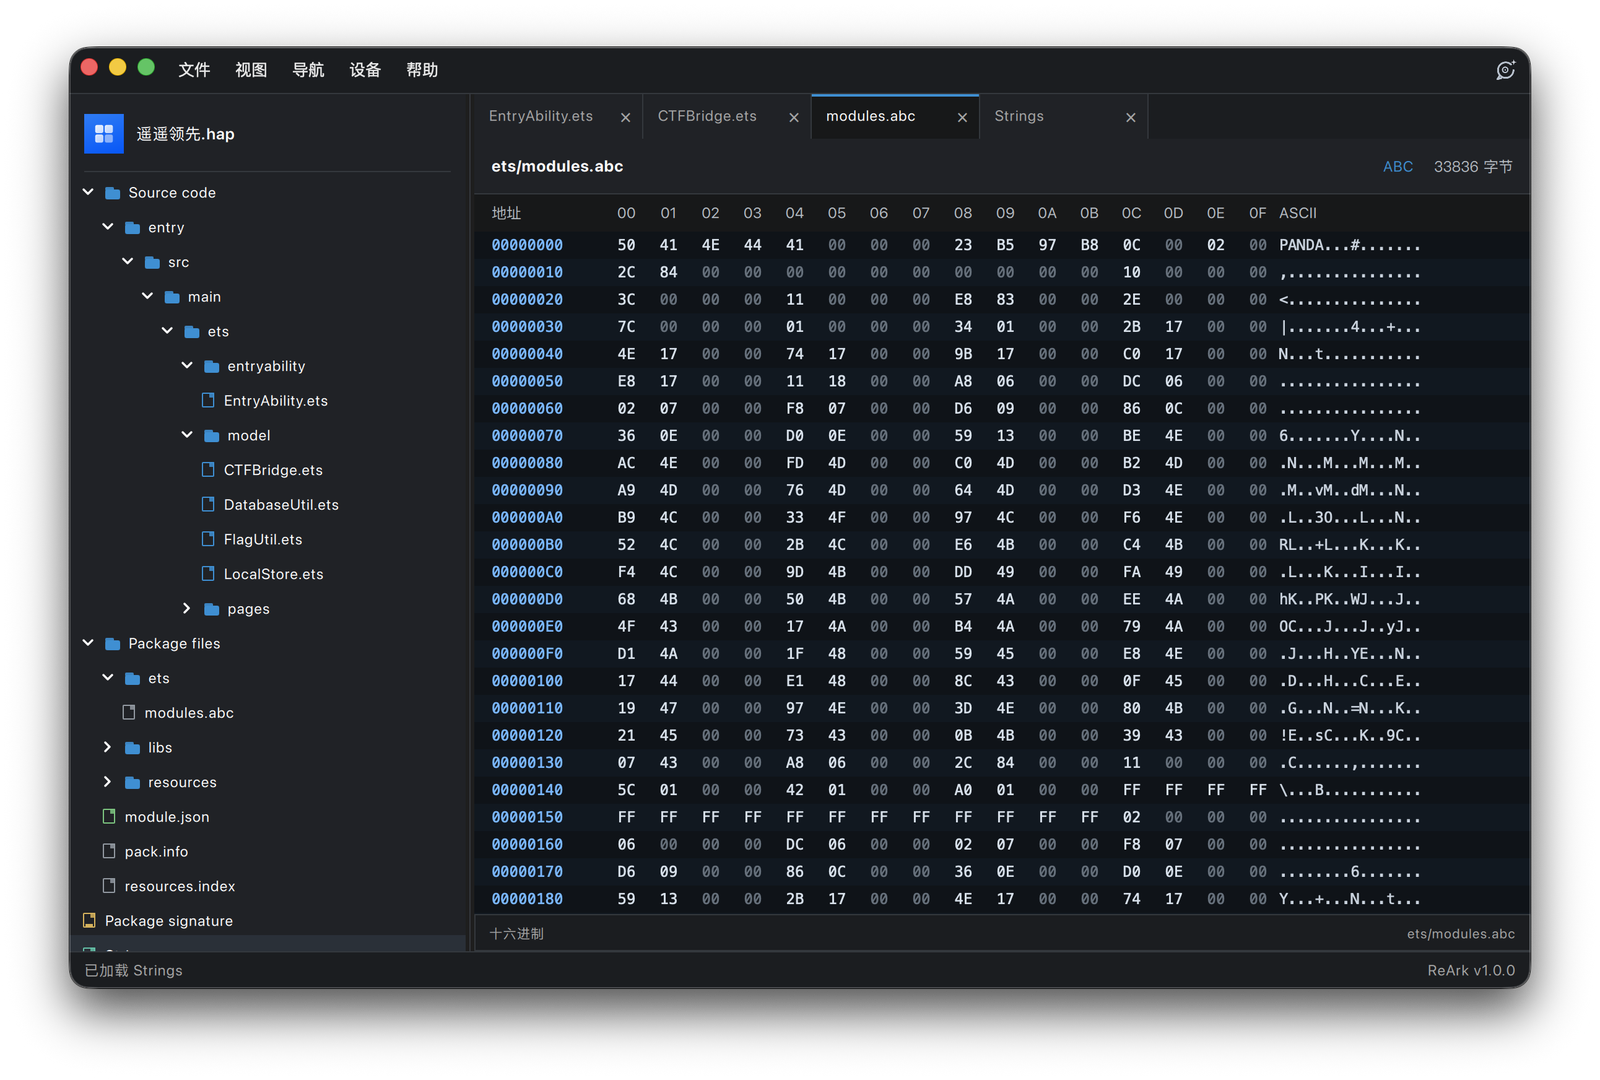 lkimuk/reark
An intelligent reverse engineering analysis tool designed for multiple target platforms, currently supporting HarmonyOS (HAP/APP/ABC) and Android…
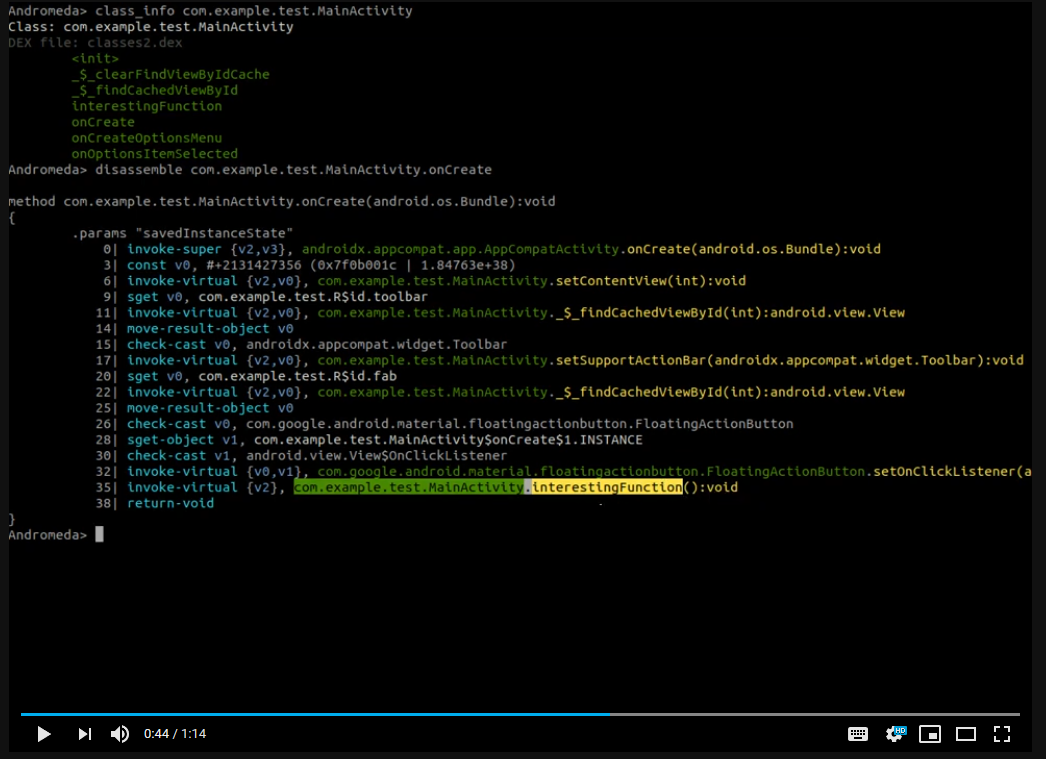 secrary/andromeda
C/C++ interactive reverse engineering tool for Android applications, enabling fast static analysis and binary inspection of APK files.
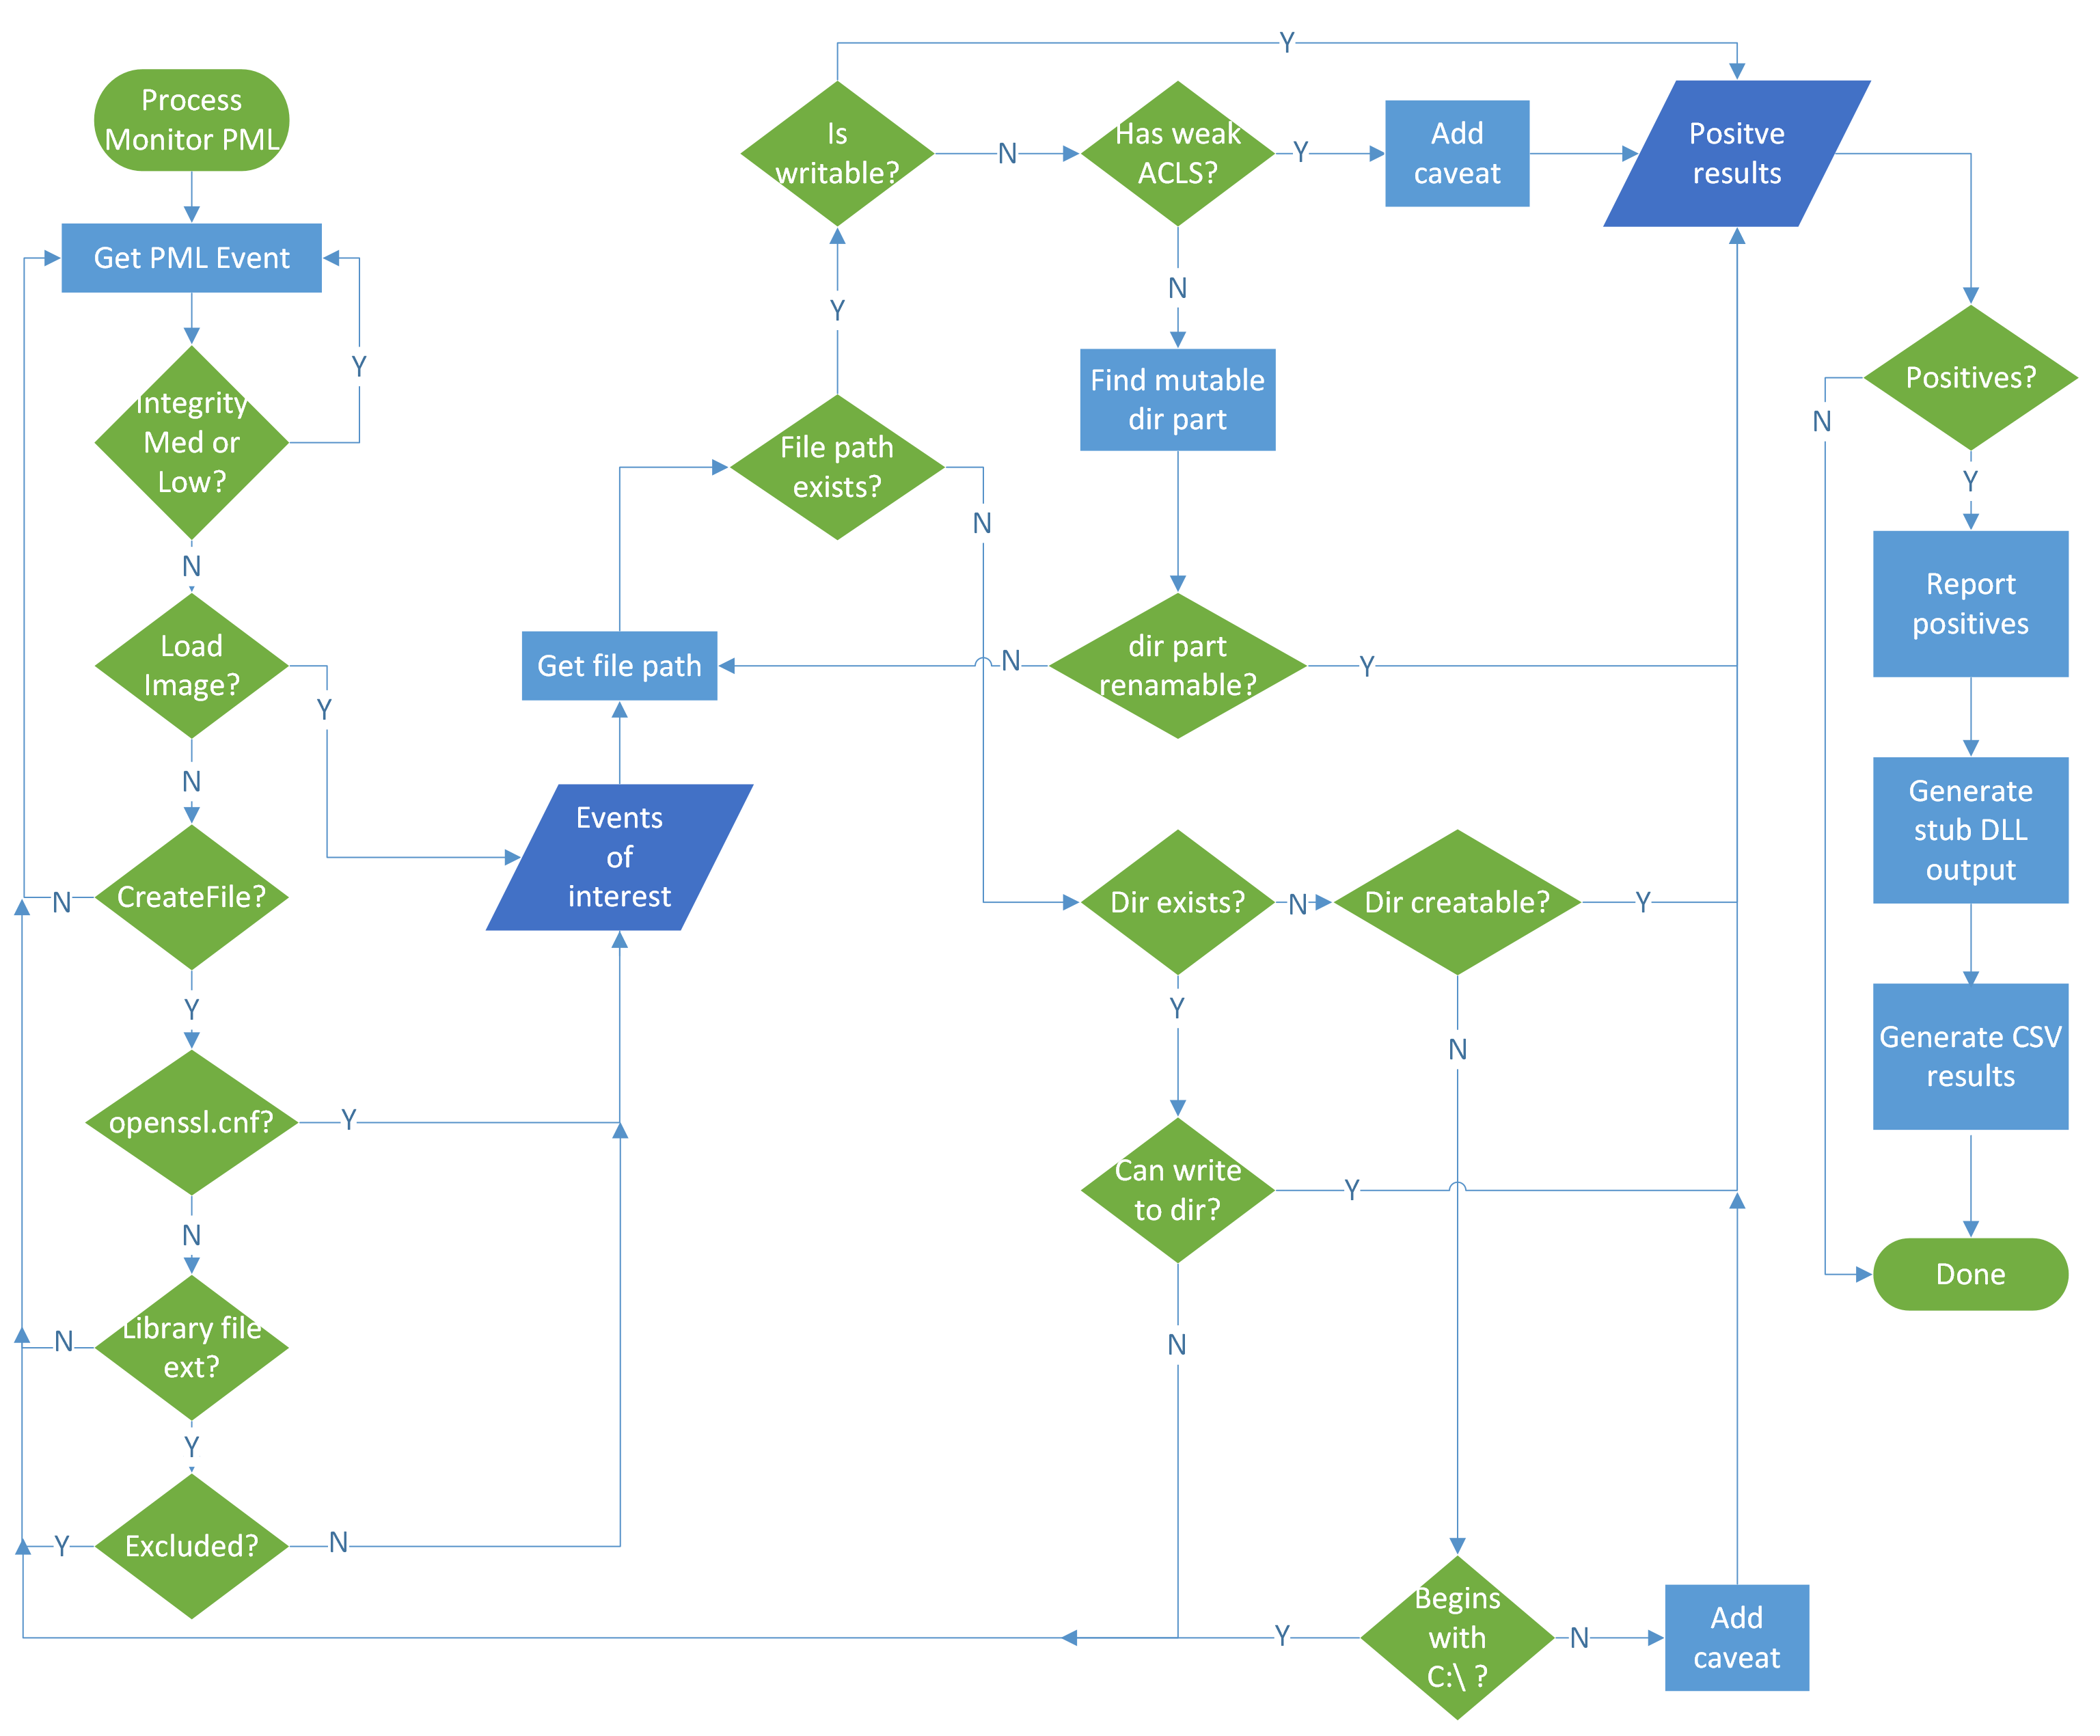 vu-ls/crassus
Windows privilege escalation discovery tool that parses Process Monitor boot logs to identify DLL hijacking, weak ACLs, and other elevation paths,…
 zeze-zeze/ioctlance
A tool that is used to hunt vulnerabilities in x64 WDM drivers
 mandiant/stringsifter
A machine learning tool that ranks strings based on their relevance for malware analysis.
 trailofbits/polytracker
An LLVM-based instrumentation tool for universal taint tracking, dataflow analysis, and tracing.