

moria
 nmatt0/moria
IoT firmware identification and extraction
binary-analysisdigital-forensicsembedded-systems-security+7
nmatt0/moriaIoT firmware identification and extraction
 kaandemir993/salat-stealer-telegram-proxy-decoy-c2-analysis
"Reverse engineering analysis of Salat Stealer, a Go-based info-stealer that uses a Telegram proxy decoy, C2 communication, and encrypted memory…
 wheregoes/byd-dolphin-hacking
Reverse engineering the BYD Dolphin head unit — CAN bus, AVAS, NFC keys, OTA, and more. DiLink 3 / Android 10.
 jatinkapilaq1/intel-me-research
Talk to your Intel Management Engine directly — zero-dependency Python tool. Finds memory leaks, partition manifest, live MKHI probing. First public…
 horsicq/detect-it-easy
Program for determining types of files for Windows, Linux and MacOS.
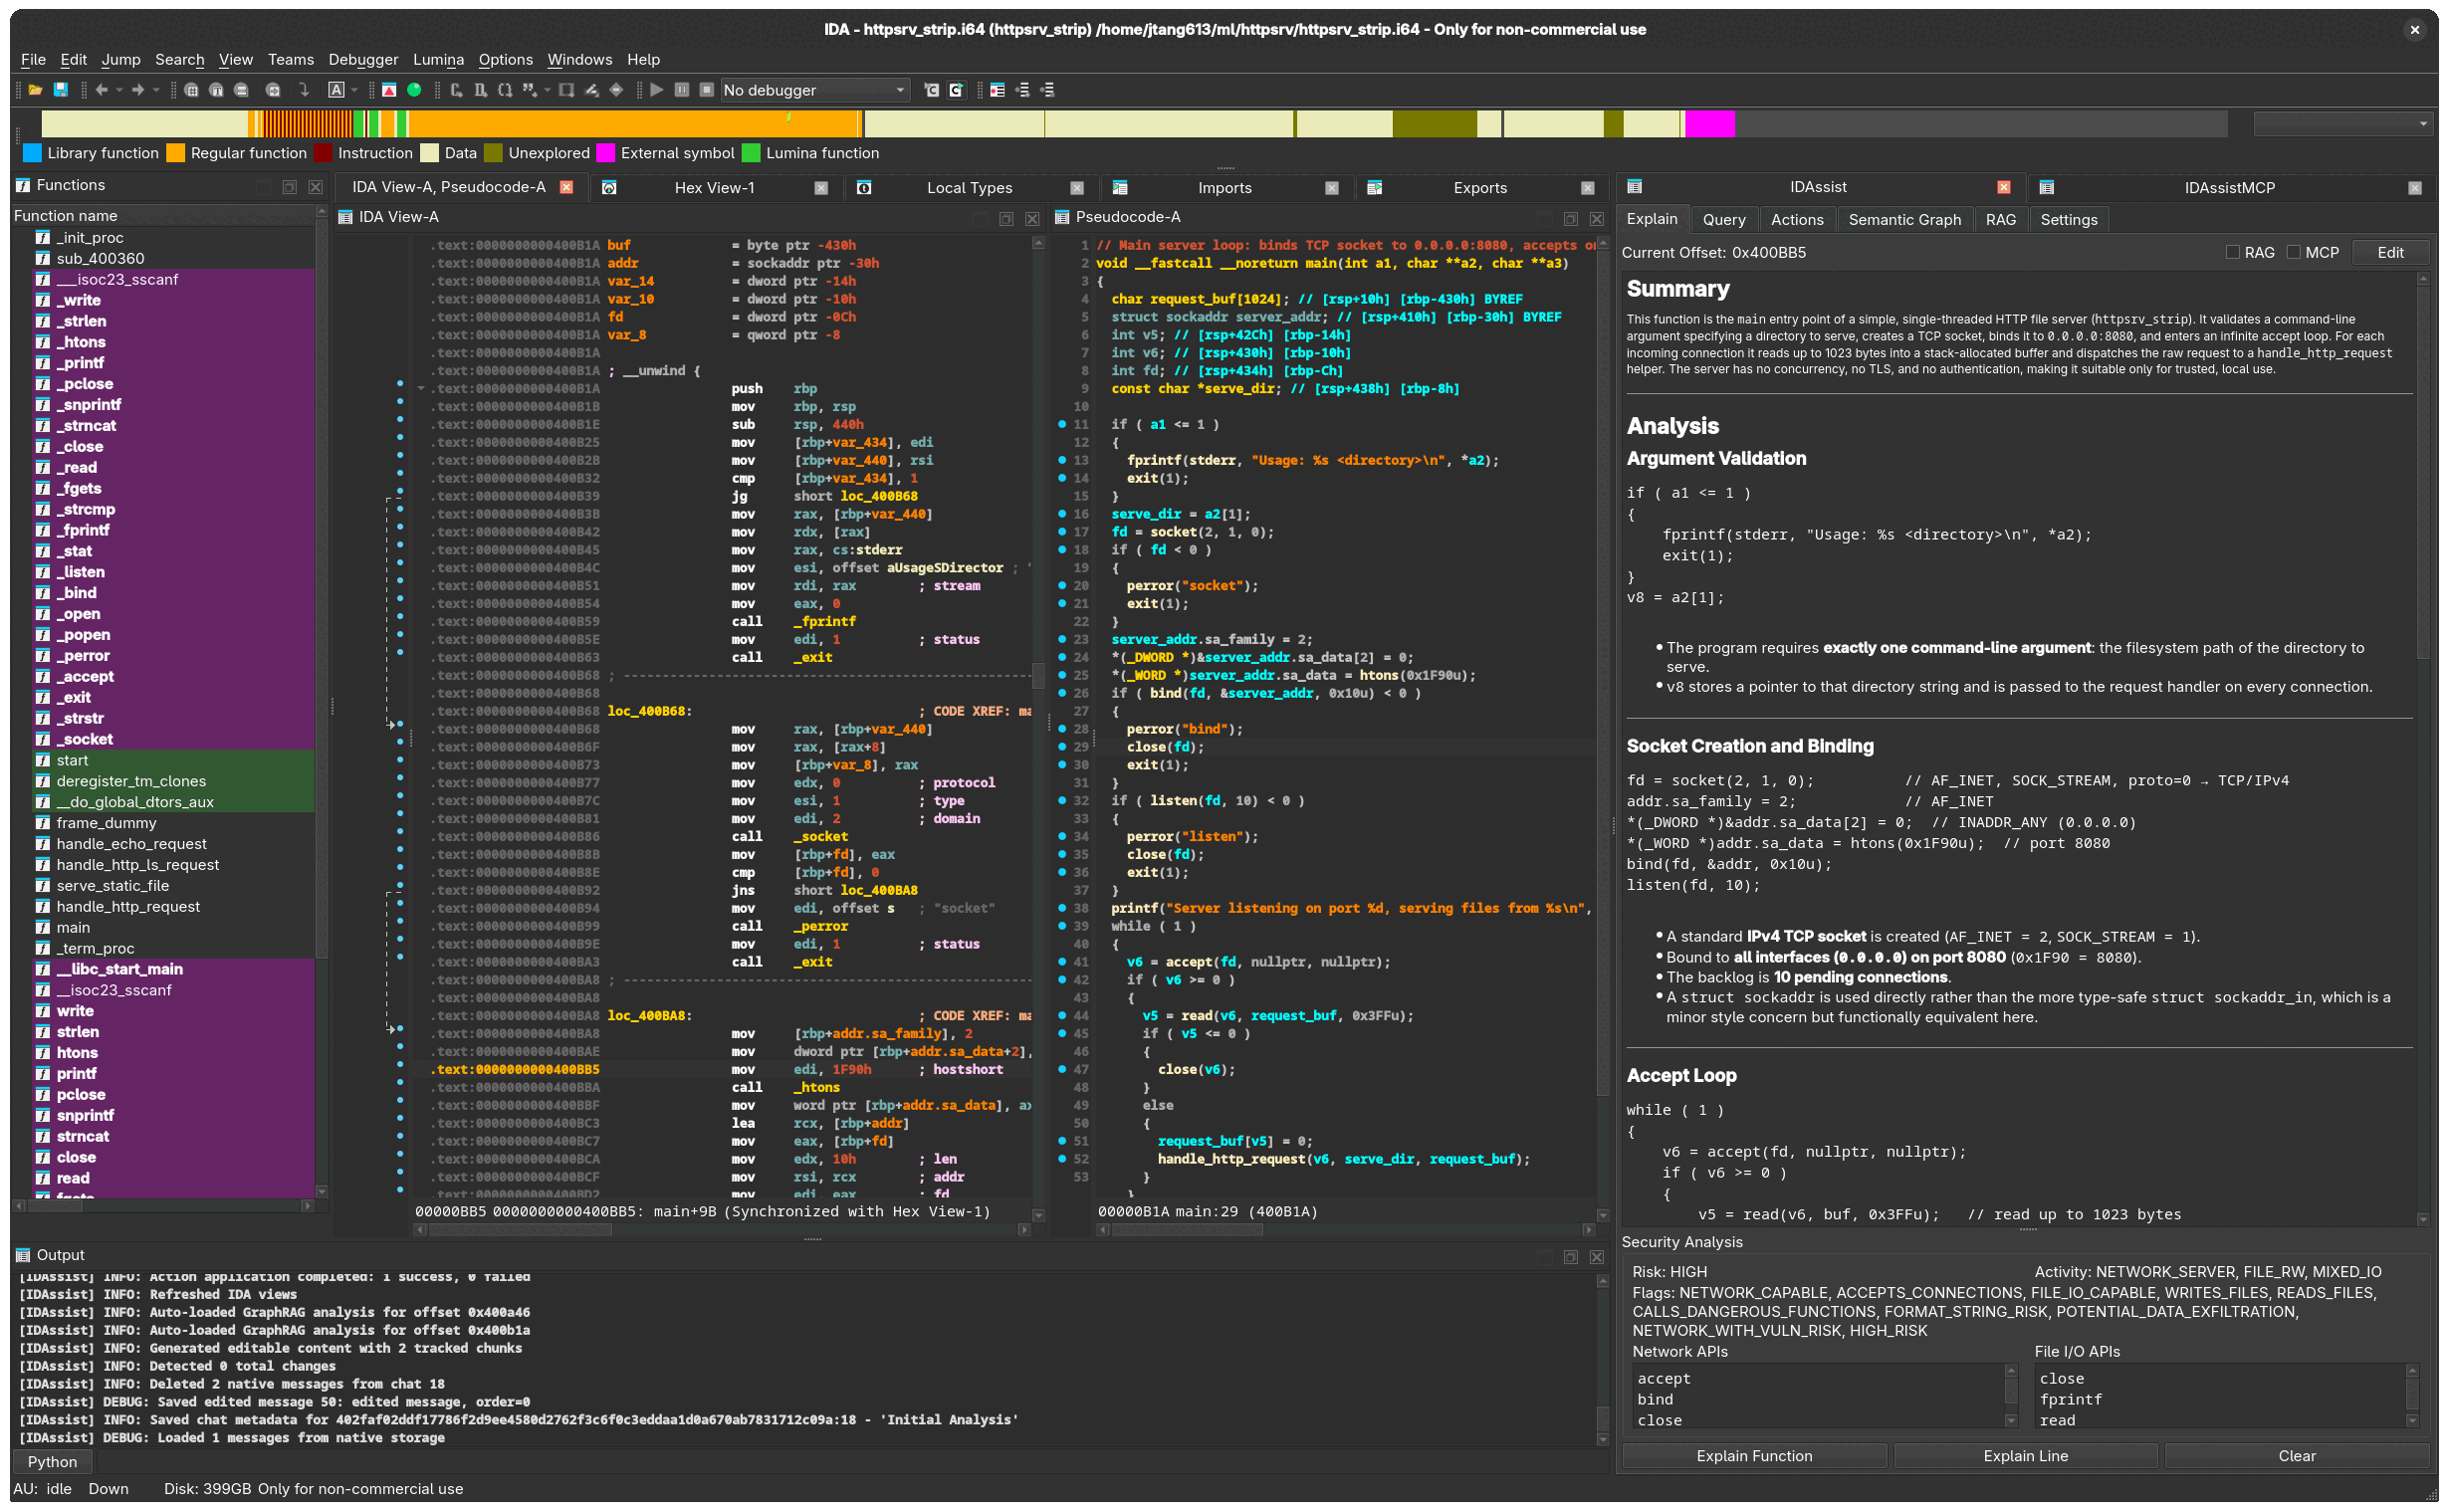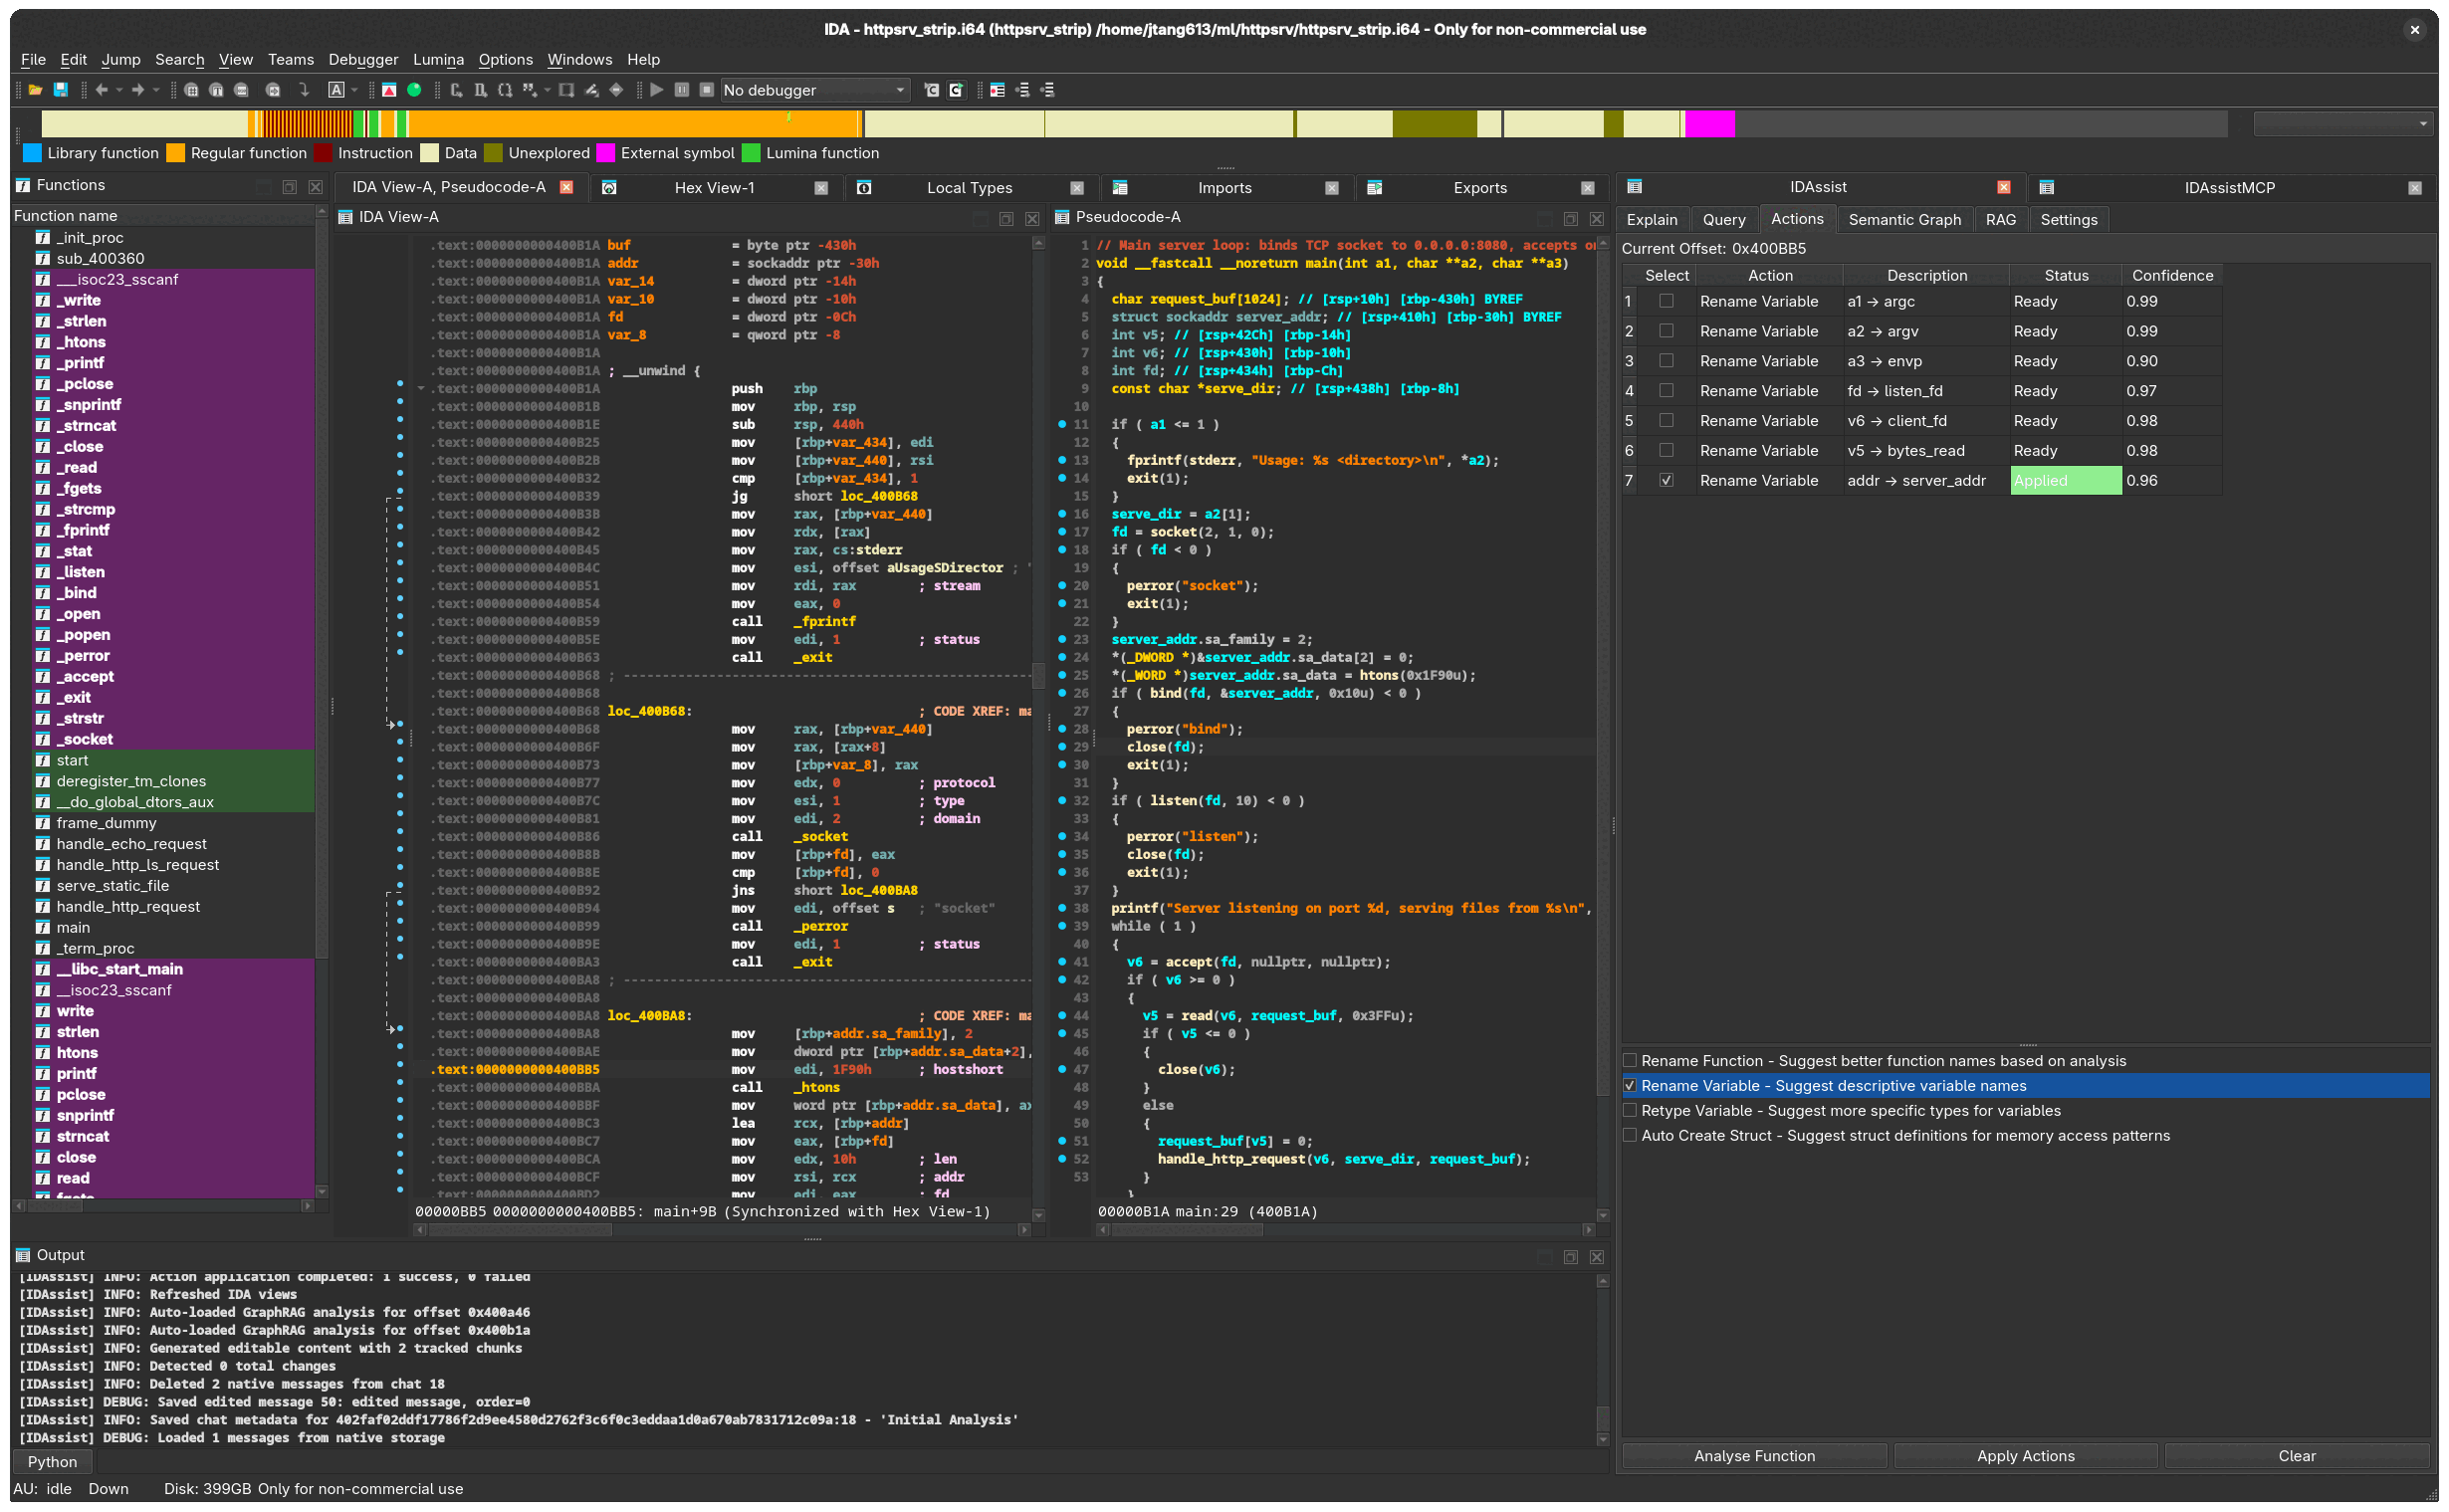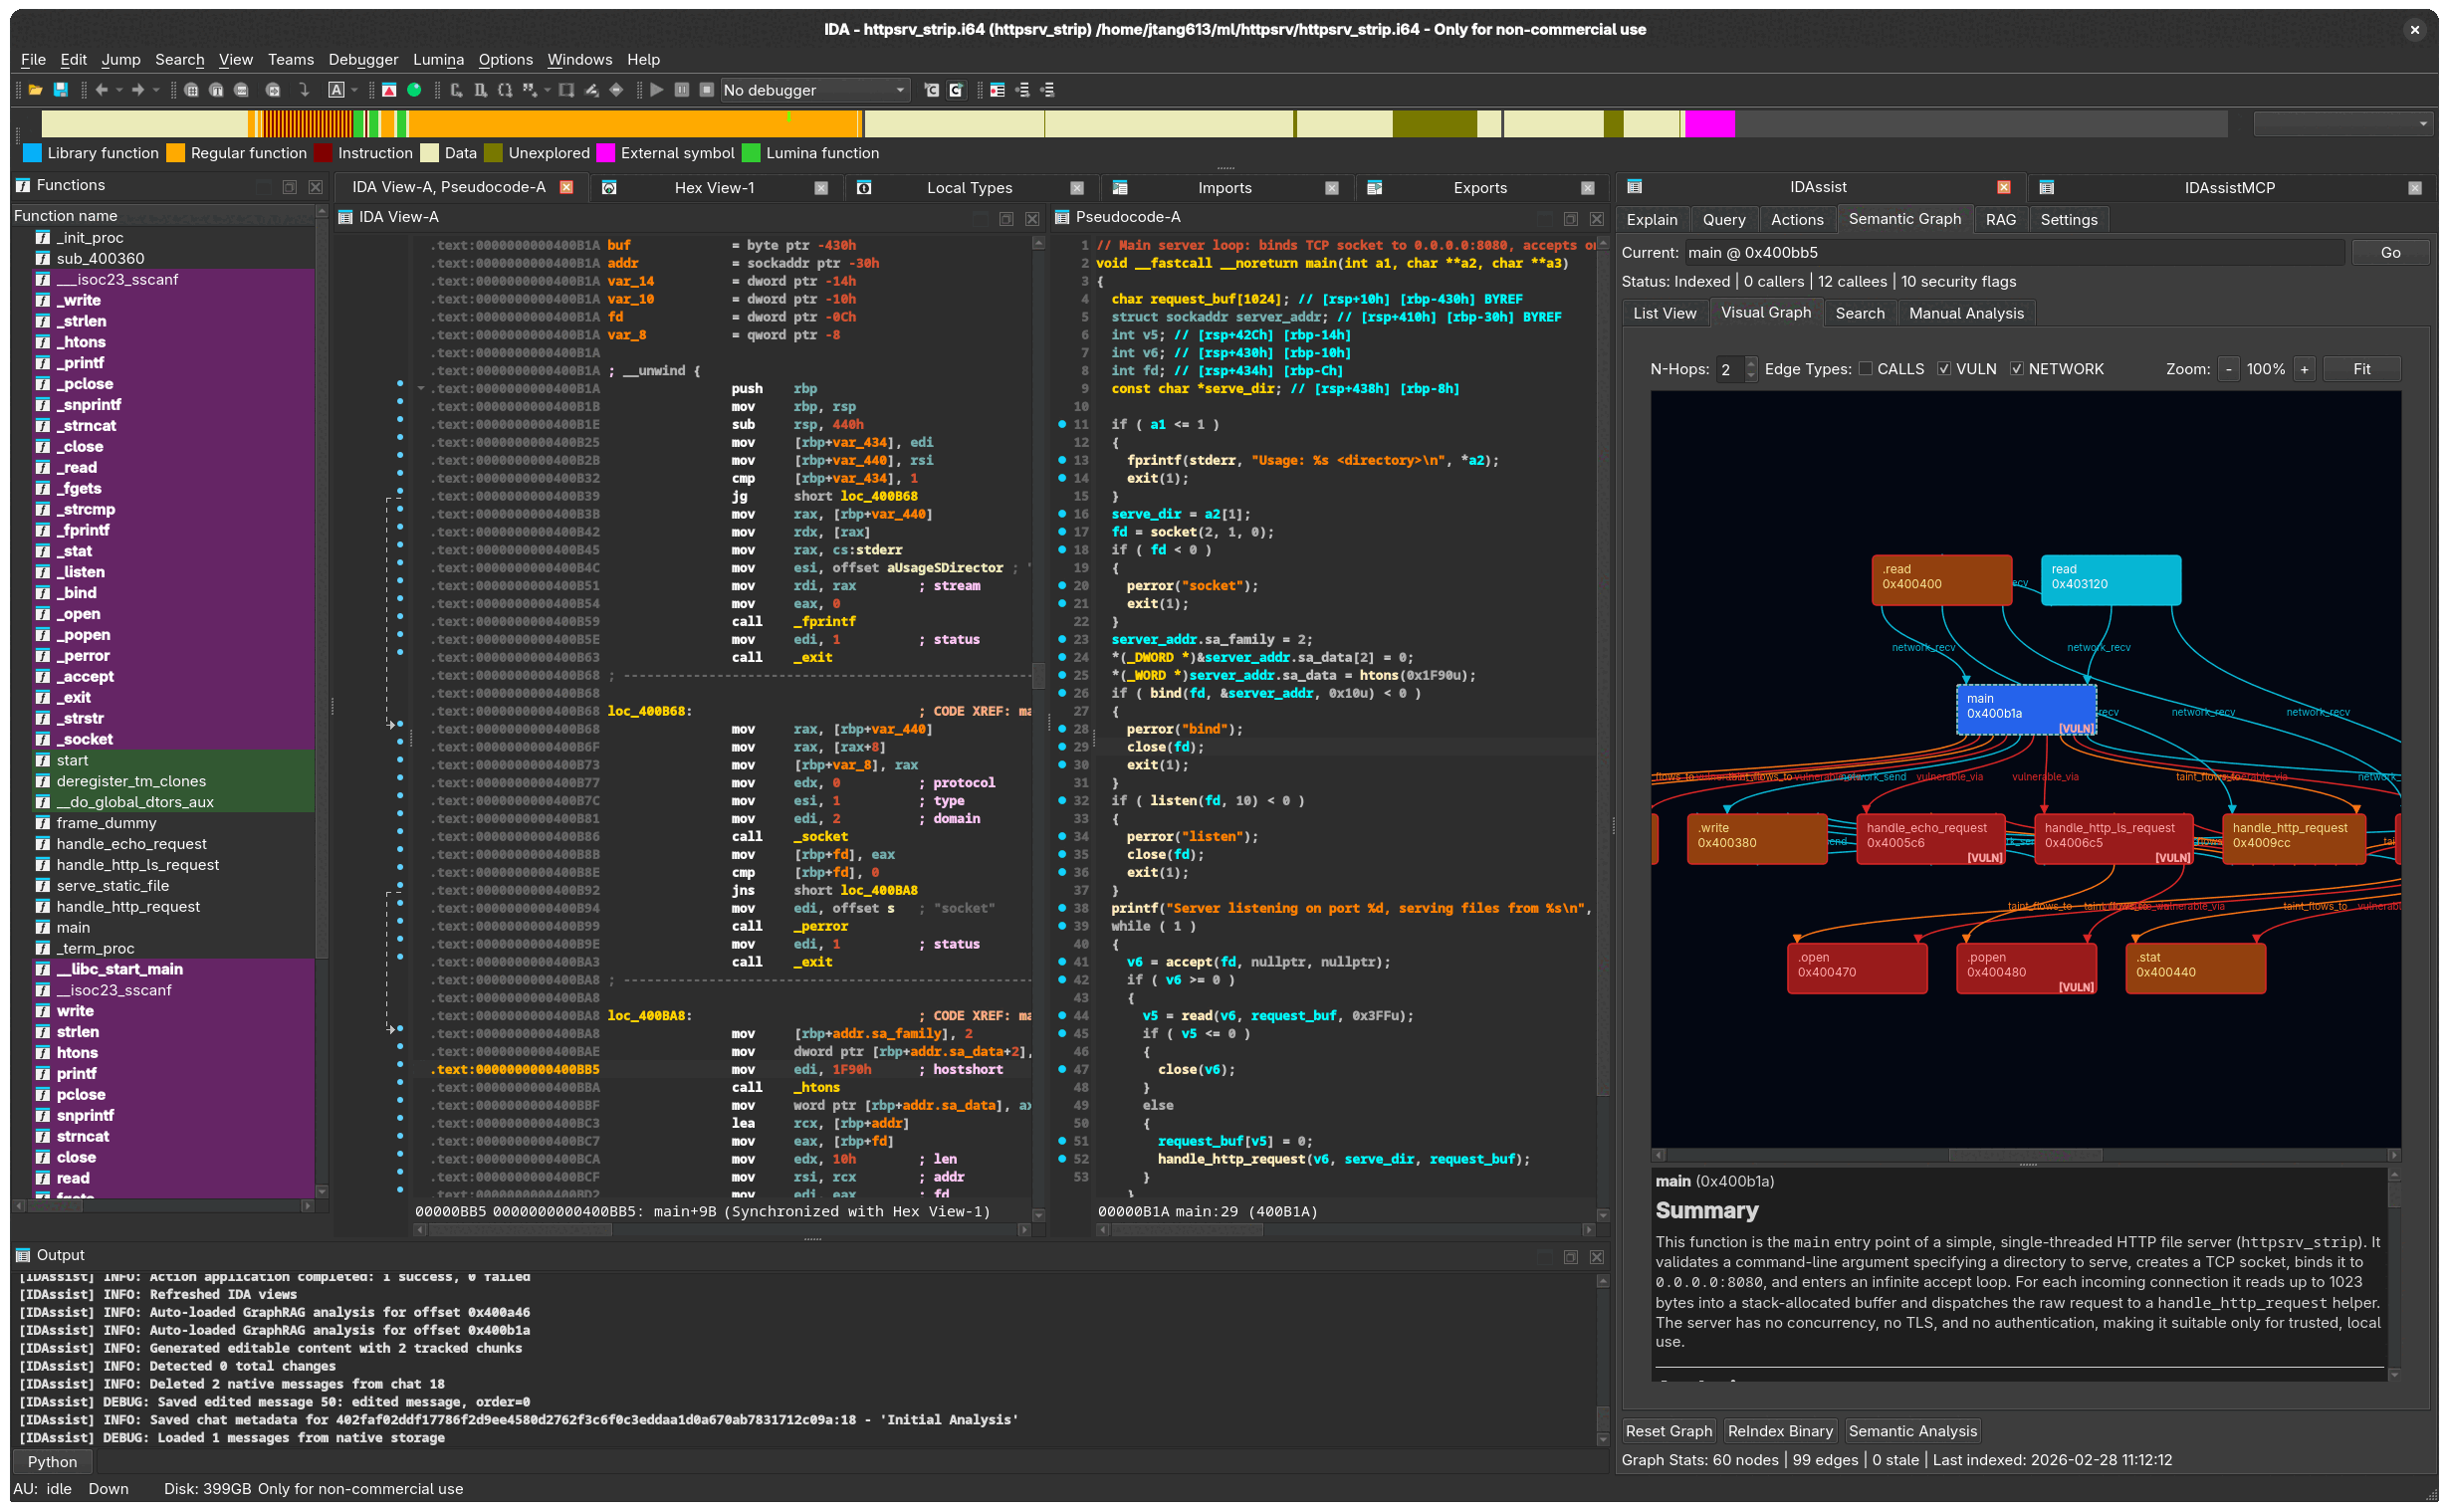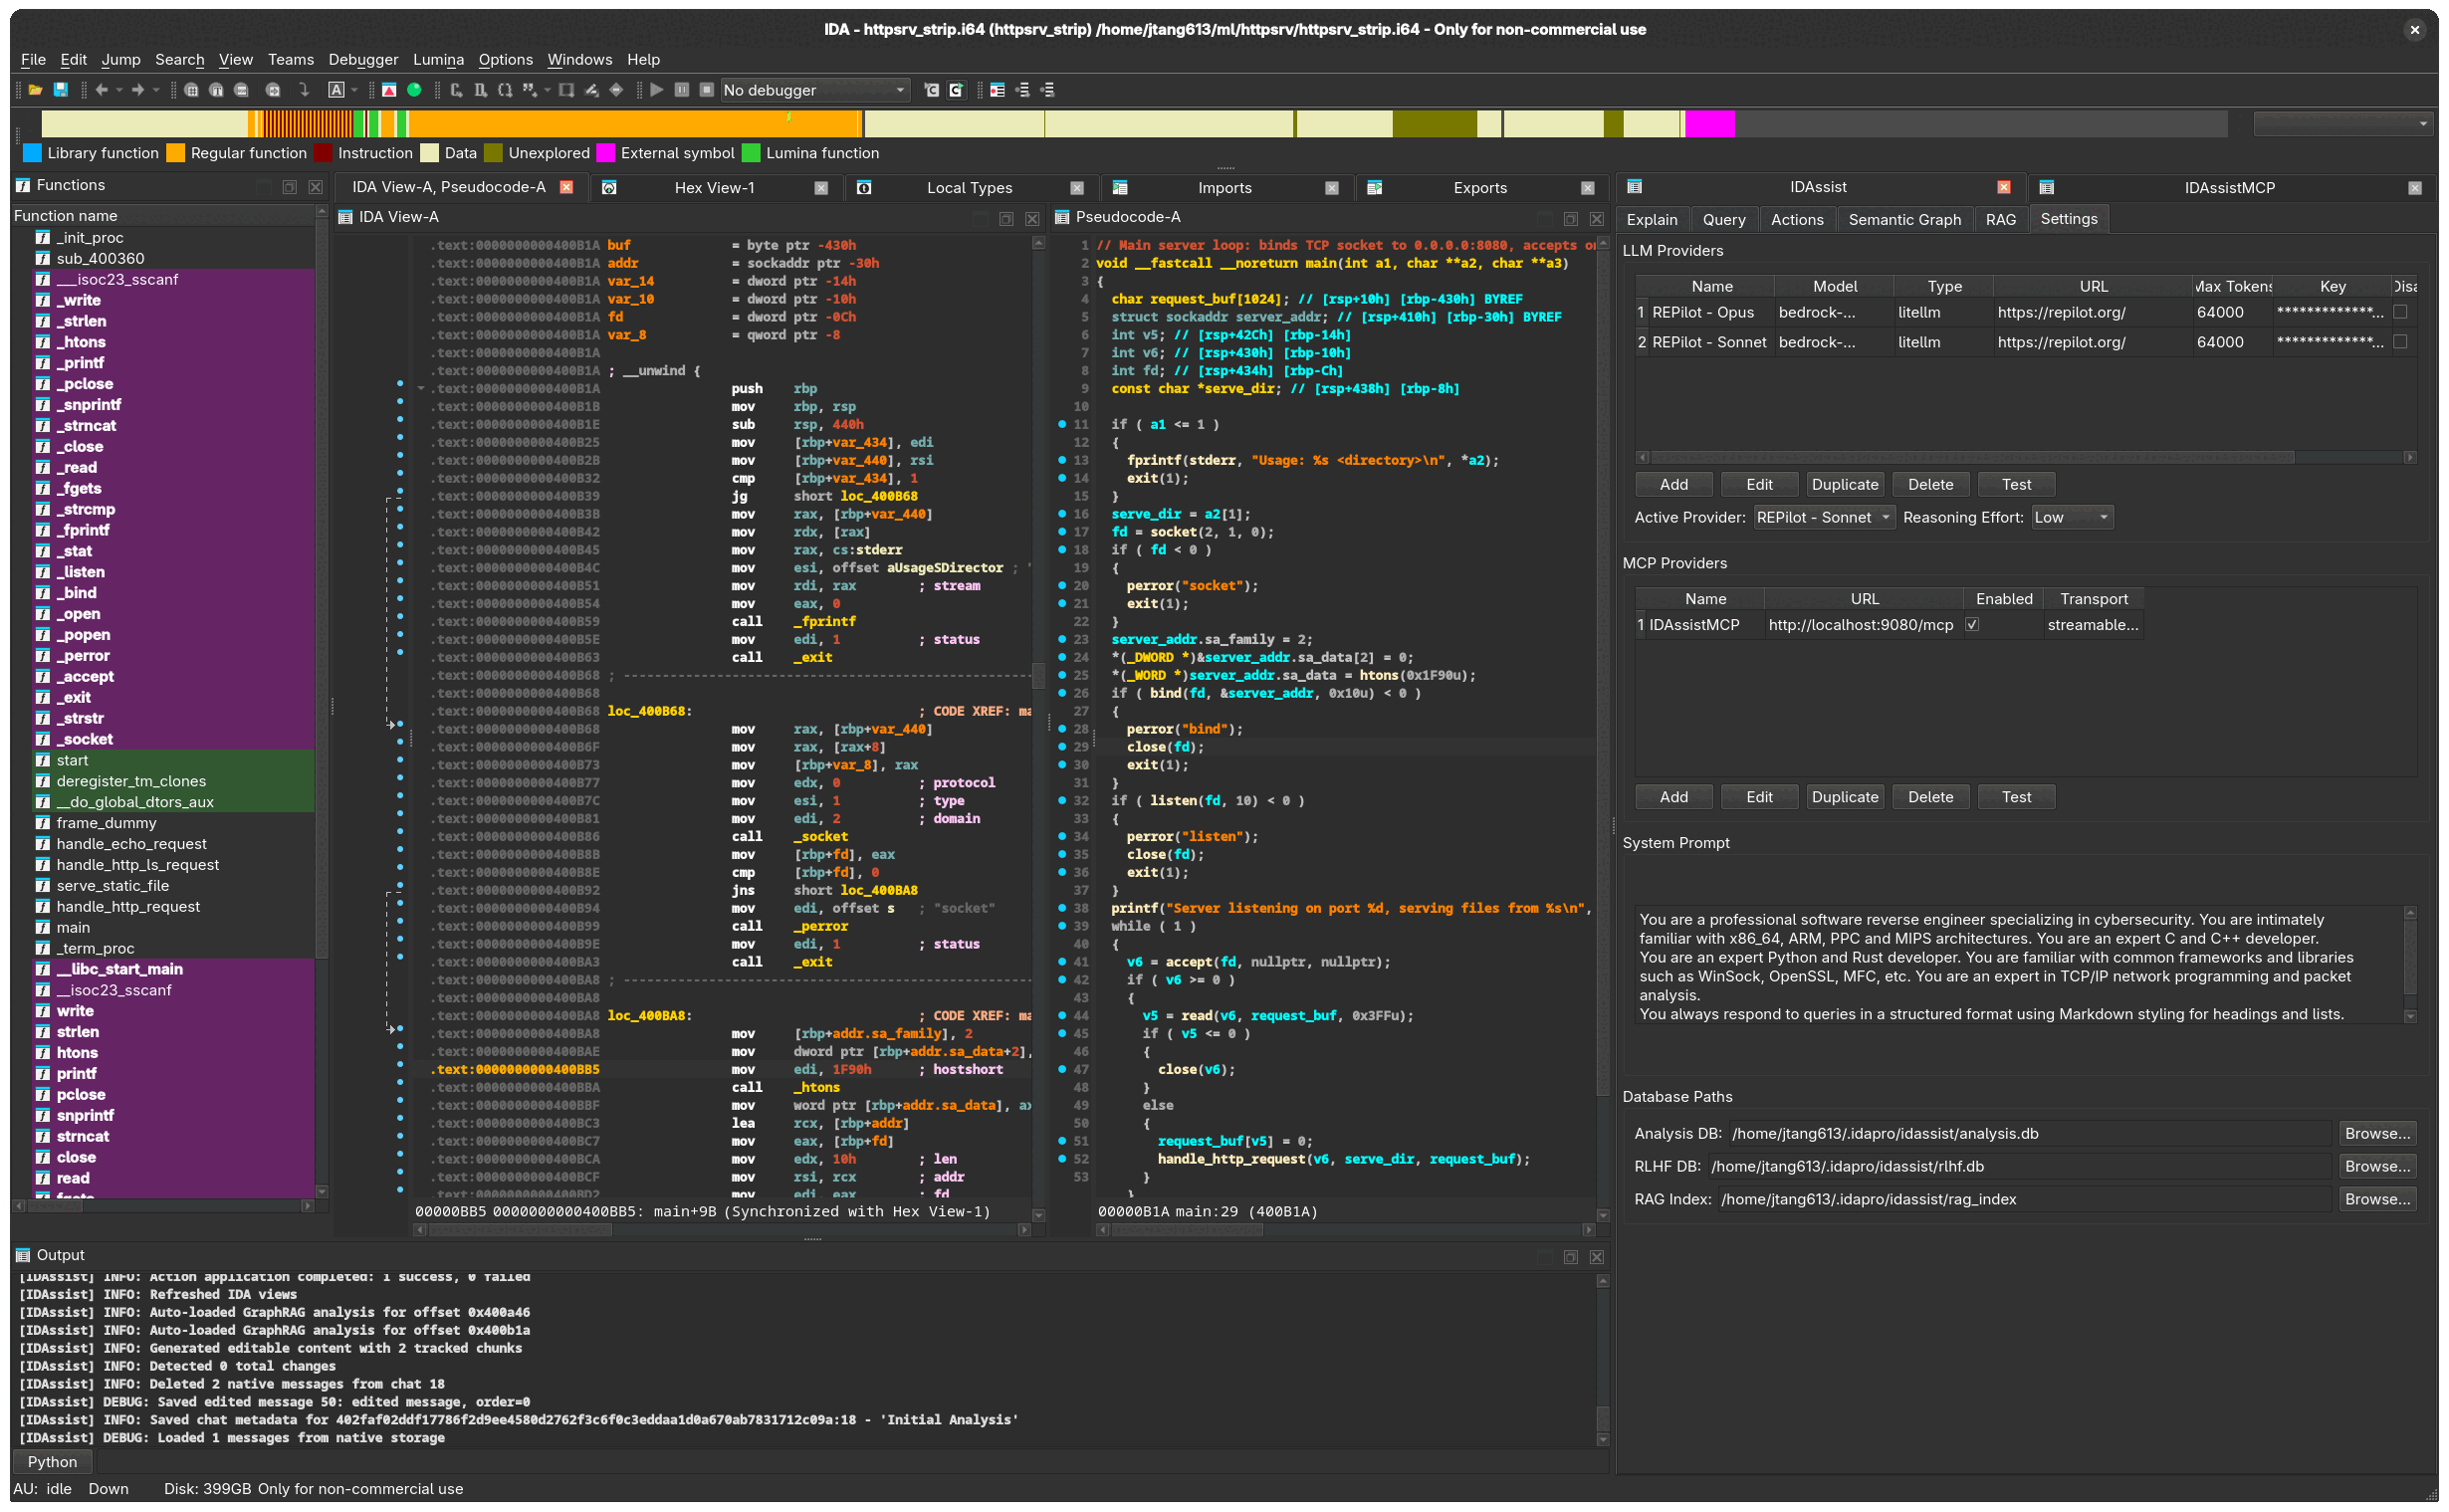 symgraph/idassist
AI-Powered Reverse Engineering Plugin for IDA Pro
 dougwithseismic/dezlock-dump
Runtime schema + RTTI extraction tool for Deadlock, CS2, Dota, and others (Source 2). No source2gen required.
 kartoffelpflanze/odis-project-explorer
Python dumper/explorer for MCD Runtime Projects used by ODIS
 waleedassar/cve-2021-1656
Proof-of-concept exploit for CVE-2021-1656, an information disclosure vulnerability in the Windows TPM driver (tpm.sys). Demonstrates kernel memory…
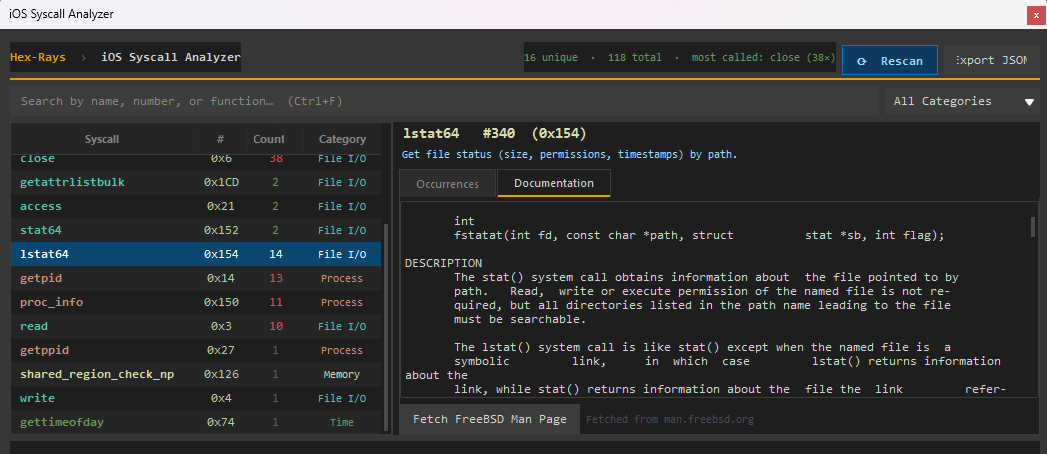 stolevchristian/sylvia
iOS Syscall Explorer for IDA 9.X
 waleedassar/cve-2021-1699
POC for CVE-2021-1699
 waleedassar/cve-2022-24483
POC For CVE-2022-24483
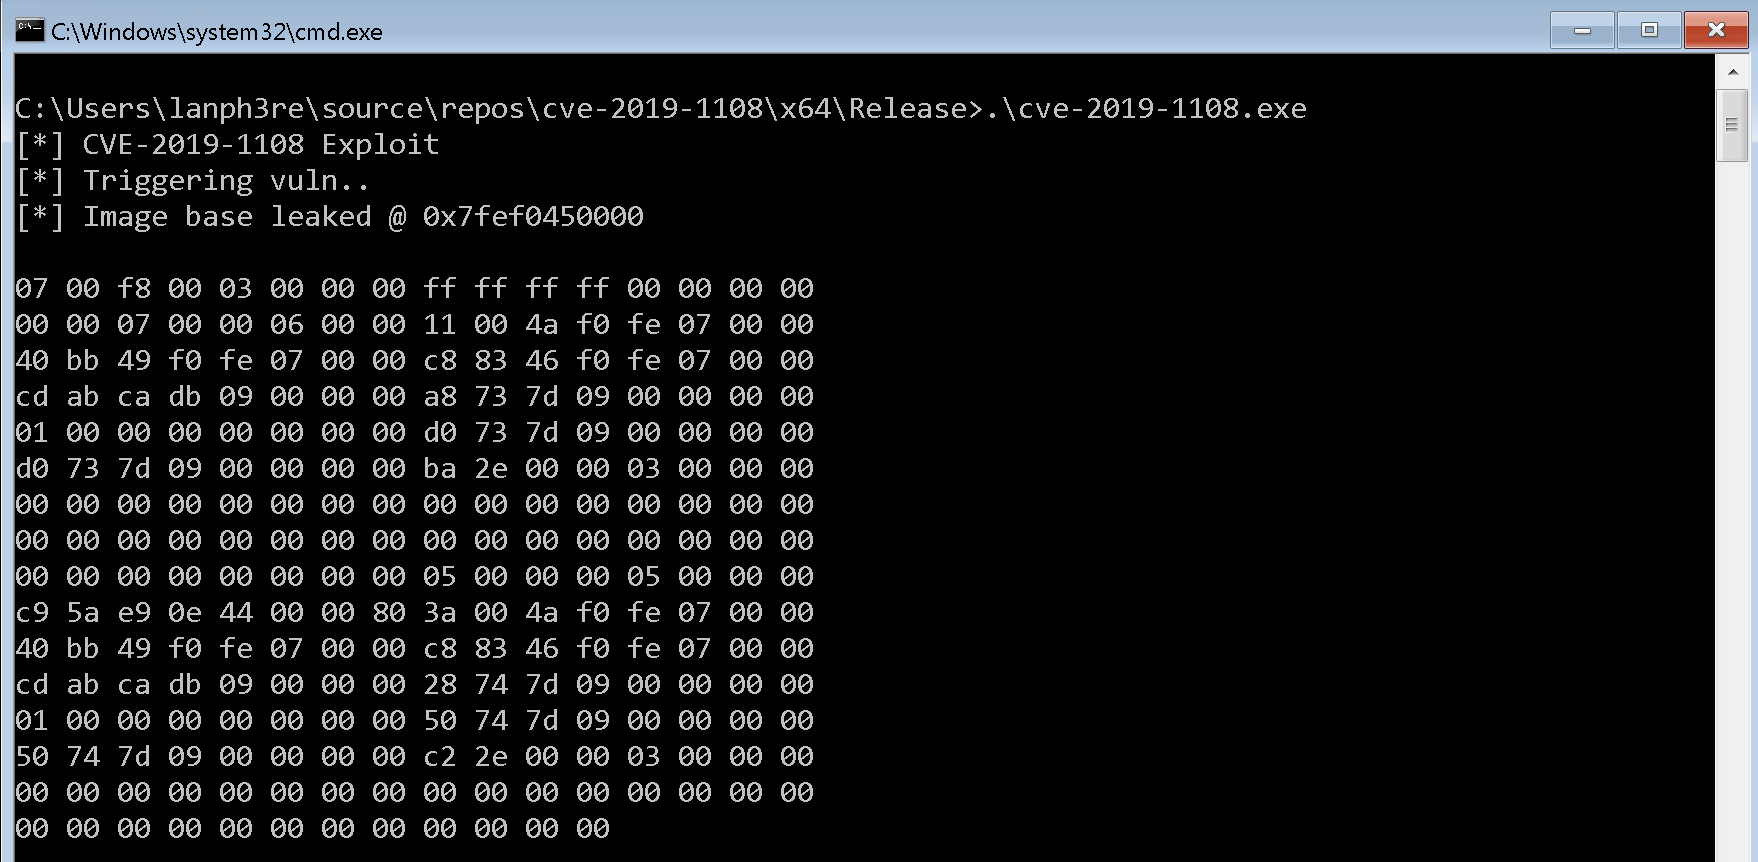 lanph3re/cve-2019-1108
Proof-of-concept exploit for CVE-2019-1108, an RDP client information disclosure vulnerability that leaks memory contents via specially crafted…
 maherazzouzi/cve-2022-36163
Proof-of-concept exploit for CVE-2022-36163, a format string vulnerability in pdftoroff hovacui 1.1.0 PDF reader, demonstrating local…
 tamatahyt/cve-2017-8481
Exploit code for CVE-2017-8481, a Windows privilege escalation vulnerability.
 spiralbl0ck/cve-2024-24684
Crash File ( Poc for CVE-2024-24684)
 likekabin/cve-2017-0541
Proof-of-concept and vulnerability analysis for CVE-2017-0541, demonstrating exploitation techniques and binary-level impact assessment.