
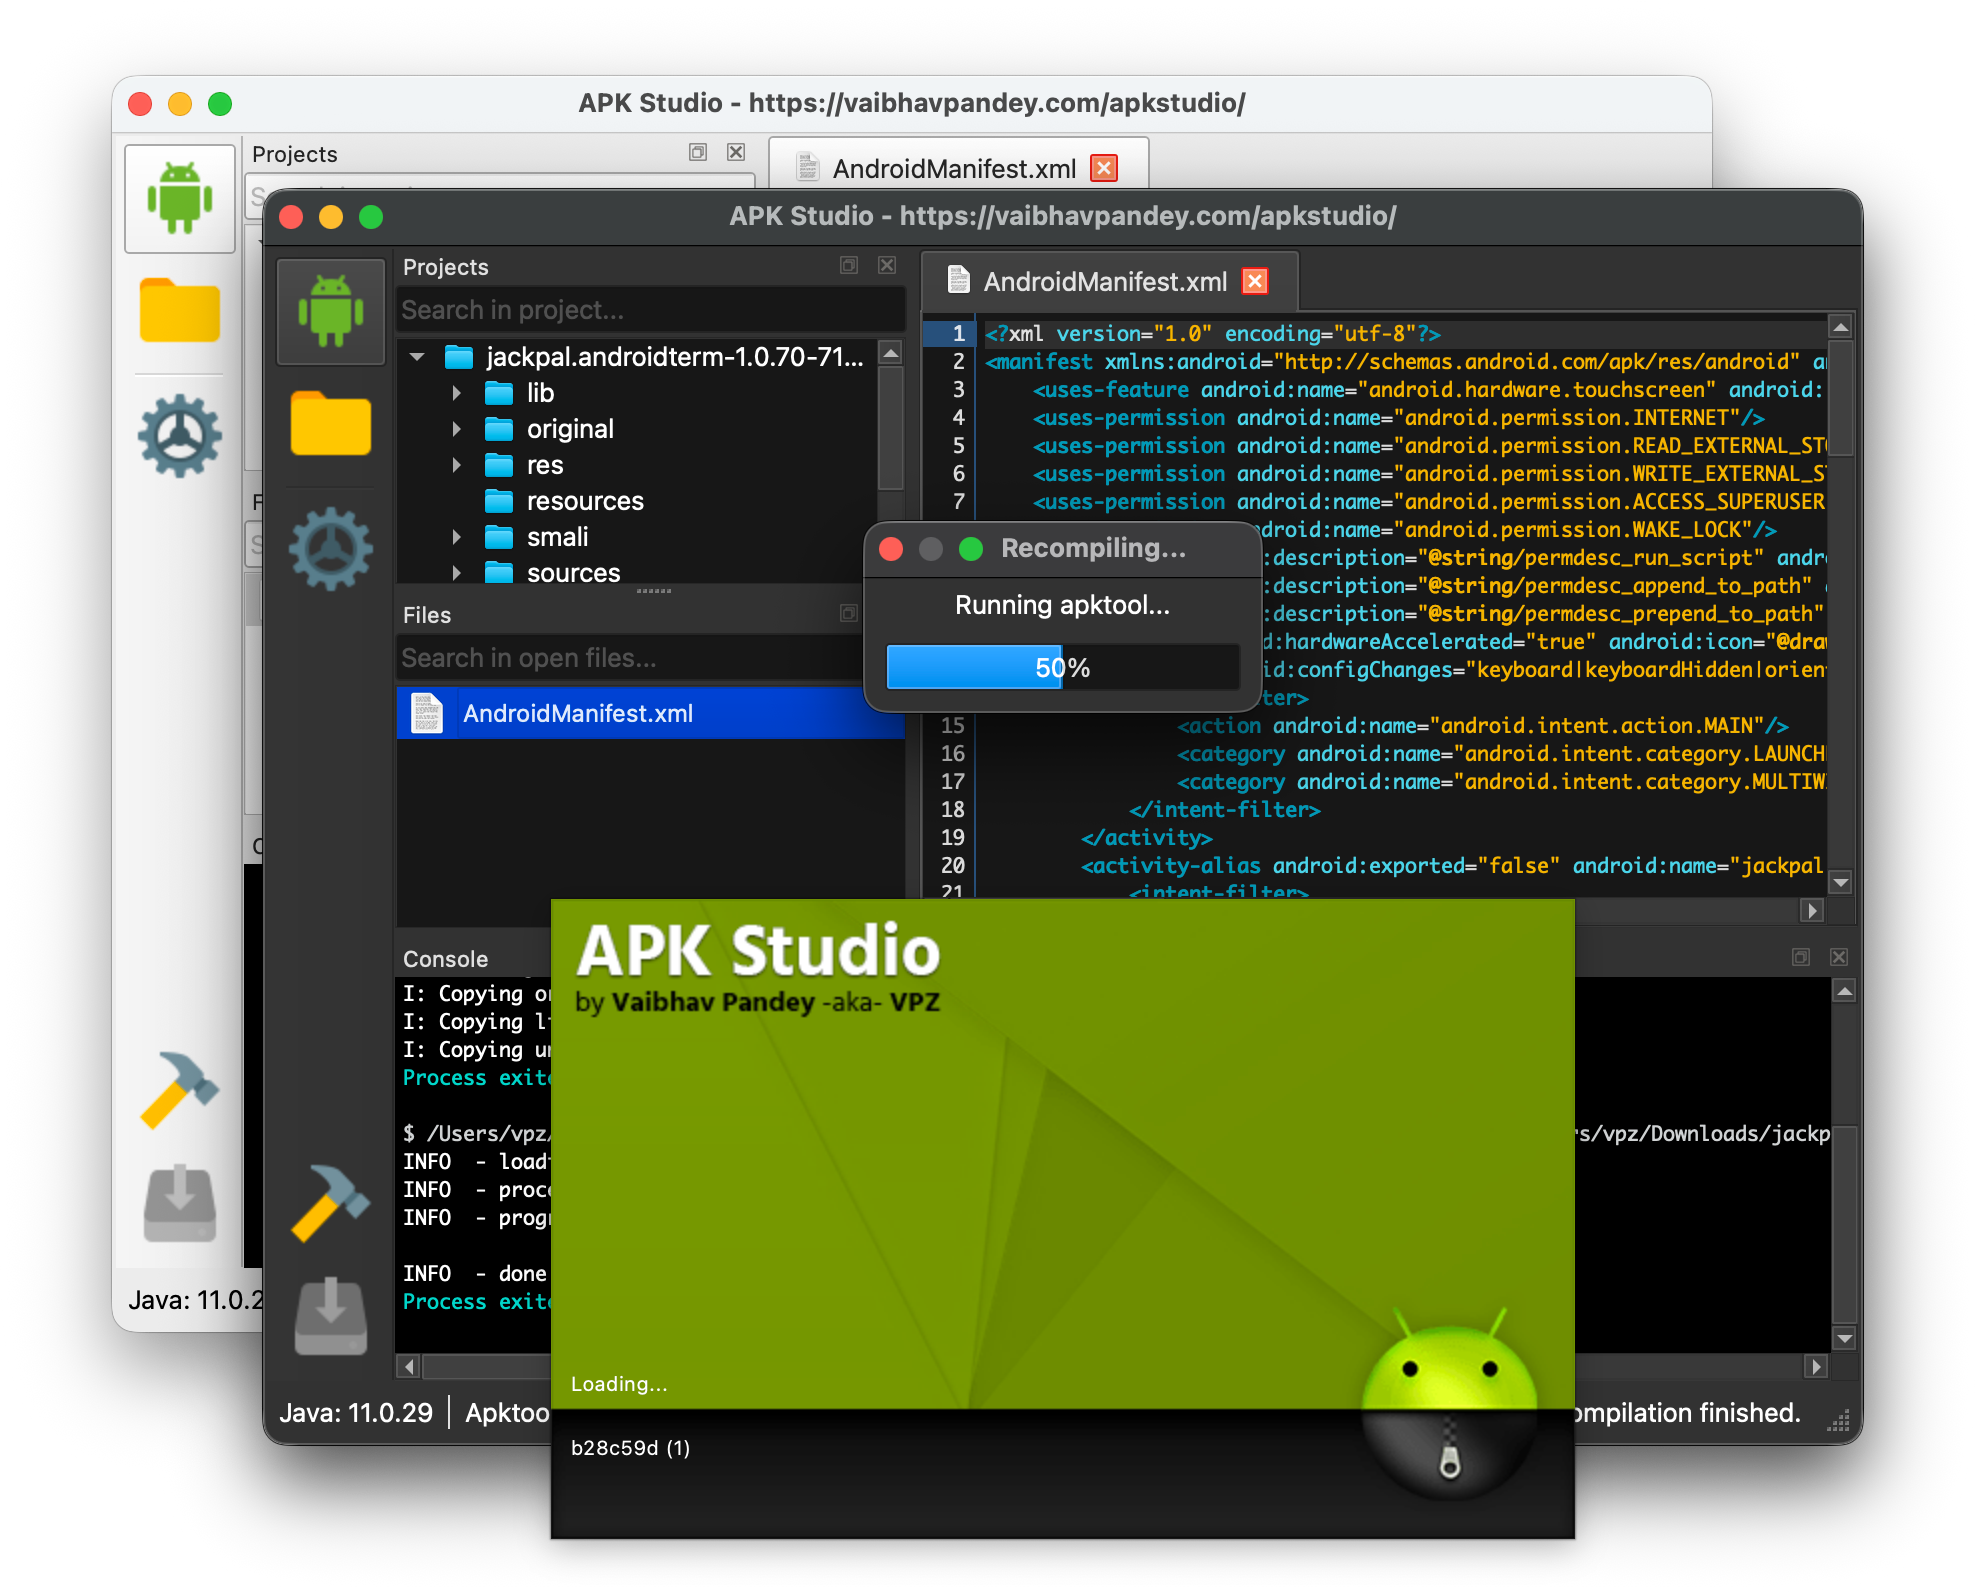
apkstudio
 vaibhavpandeyvpz/apkstudio
Open-source, cross platform Qt6 based IDE for reverse-engineering Android application packages. It features a friendly IDE-like layout including code…
android-securitybinary-analysisdebuggers+5
4.7k
vaibhavpandeyvpz/apkstudioOpen-source, cross platform Qt6 based IDE for reverse-engineering Android application packages. It features a friendly IDE-like layout including code…
 honeynet/apkinspector
APKinspector is a powerful GUI tool for analysts to analyze the Android applications.
 federicodotta/brida
The new bridge between Burp Suite and Frida!
 lkimuk/reark
An intelligent reverse engineering analysis tool designed for multiple target platforms, currently supporting HarmonyOS (HAP/APP/ABC) and Android…
 foundryzero/binder-trace
Binder Trace is a tool for intercepting and parsing Android Binder messages. Think of it as "Wireshark for Binder".
 symbioticsec/hermes-decomp
A powerful decompiler that lets you reverse-engineer React Native mobile apps by converting their compiled Hermes bytecode (.hbc) files back into…
 hamz-a/frida-android-libbinder
PoC Frida script to view Android libbinder traffic
 murf-xd/cve-2023-20768
Android kernel CVE analysis and PoC for a MediaTek ION allocator type confusion, covering root-cause diffing, unprivileged trigger, and…
 darioi/droidcarve
Android Reverse Engineering Framework
 pazhanivelmani/external_libcap-android10_r33_cve-2023-2603
POSIX.1e capability library for Android 10, addressing CVE-2023-2603 with tools for setting and getting process capabilities to manage privilege…
 1-3-7/disrobe
Rust CLI suite that statically decompiles, deobfuscates, and unpacks native code, bytecode, scripts, firmware, and app packages across 15+ ecosystems…
 bishopfox/mauidll
Extract the managed (.NET) assemblies out of a MAUI Android assembly store.
 andreafioraldi/frida-fuzzer
This experimetal fuzzer is meant to be used for API in-memory fuzzing.
 trustedsec/coffloader
Run Beacon Object Files (BOFs) outside Cobalt Strike by parsing 64-bit COFF object files, with Beacon-compatible argument generation and helper…
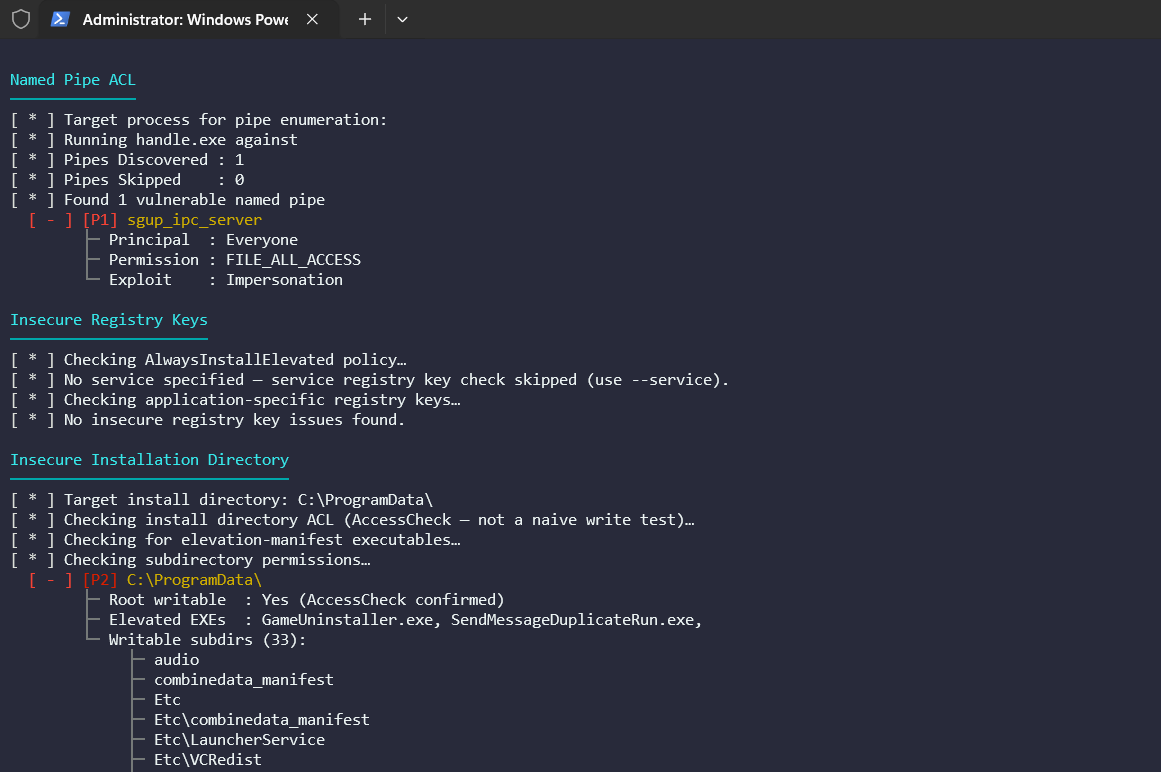 shellkraft/anvil
Anvil is a runtime-first attack surface assessment tool for Windows thick client applications, built for penetration testers and security researchers…
 amlweems/xzbot
notes, honeypot, and exploit demo for the xz backdoor (CVE-2024-3094)
 416rehman/deepzero
Find zero-days while you sleep. DeepZero is an automated vulnerability research framework that parses, decompiles, and analyzes thousands of Windows…
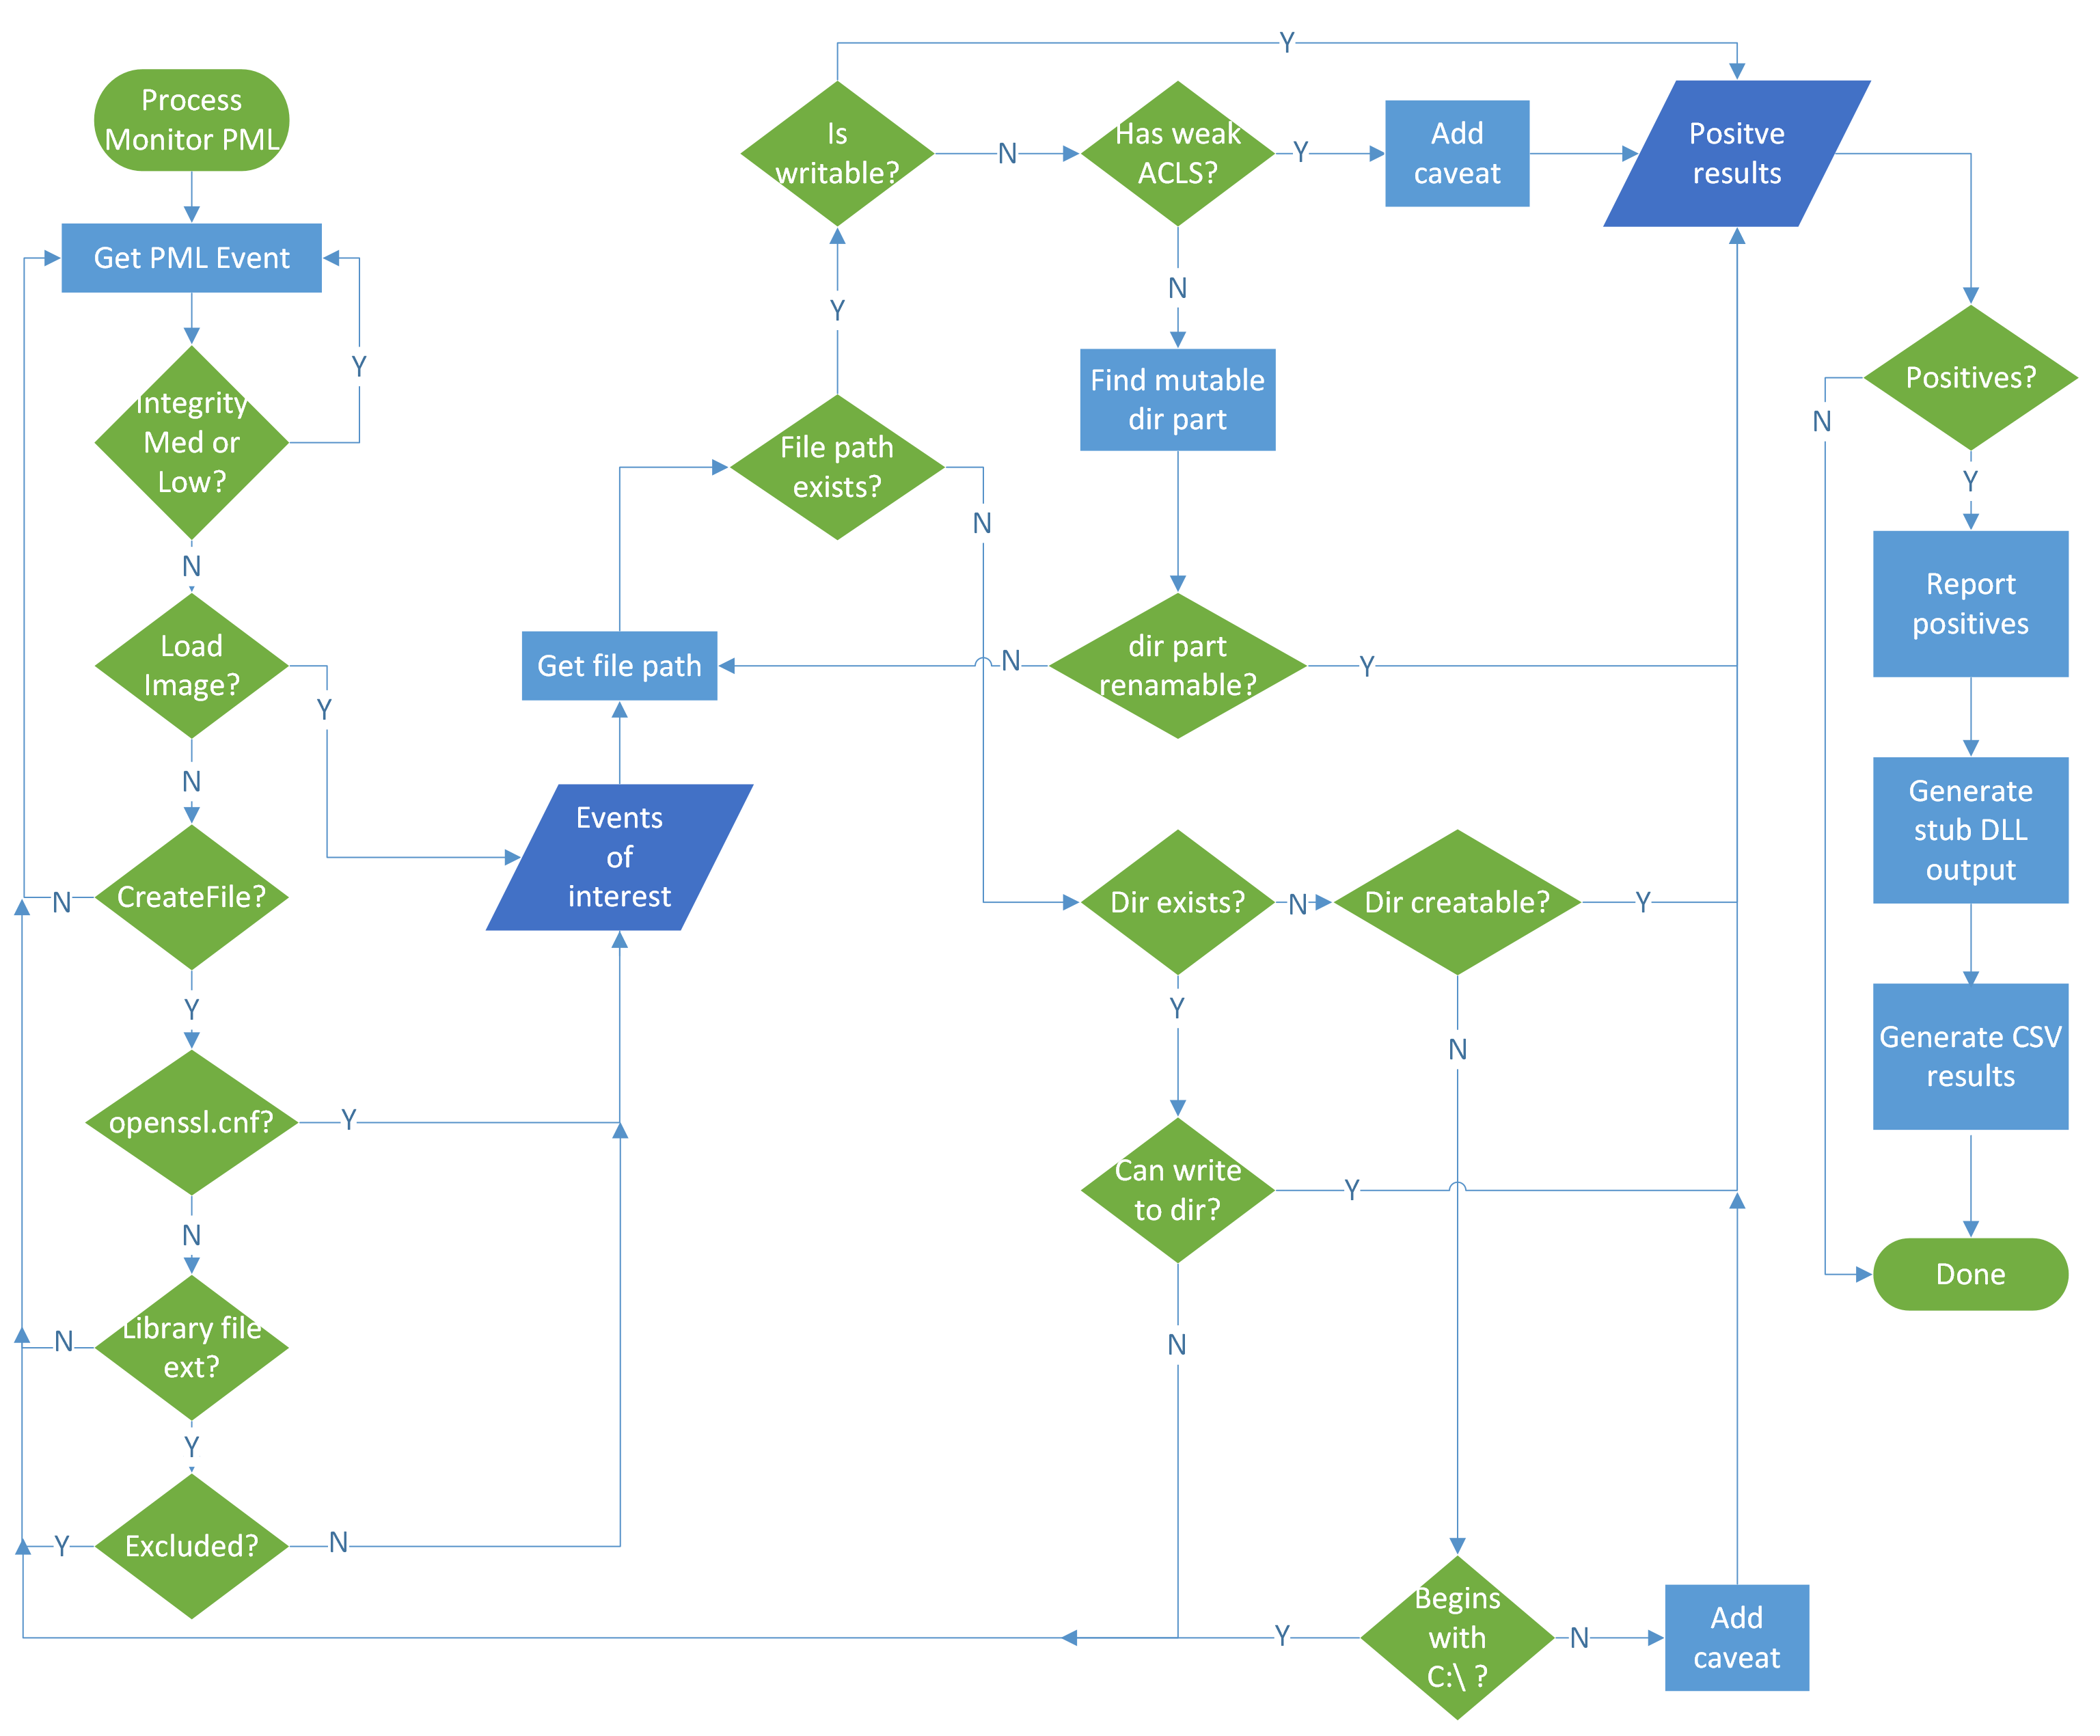 vu-ls/crassus
Windows privilege escalation discovery tool that parses Process Monitor boot logs to identify DLL hijacking, weak ACLs, and other elevation paths,…