GIGABYTE-H510M-K-V2-BIOS-SMM-Reverse-Engineering-CVE-2025-7026-7027-7028-7029-Research

Static reverse-engineering of a GIGABYTE H510M K V2 (`H510MKV2.F3`) BIOS image: full UEFI firmware-volume extraction analysis of the PI-spec SMM Core…

Static reverse-engineering of a GIGABYTE H510M K V2 (`H510MKV2.F3`) BIOS image: full UEFI firmware-volume extraction analysis of the PI-spec SMM Core…

This repo contain a PoC I have done when blind analysis the dbutil_2_3.sys driver for vulnerability. This was created by personal analysis without…

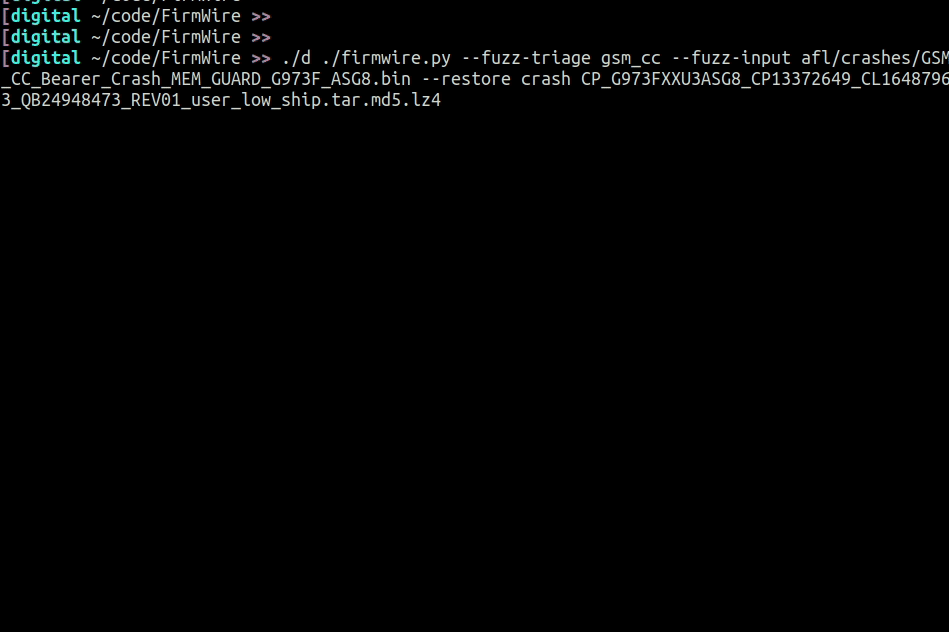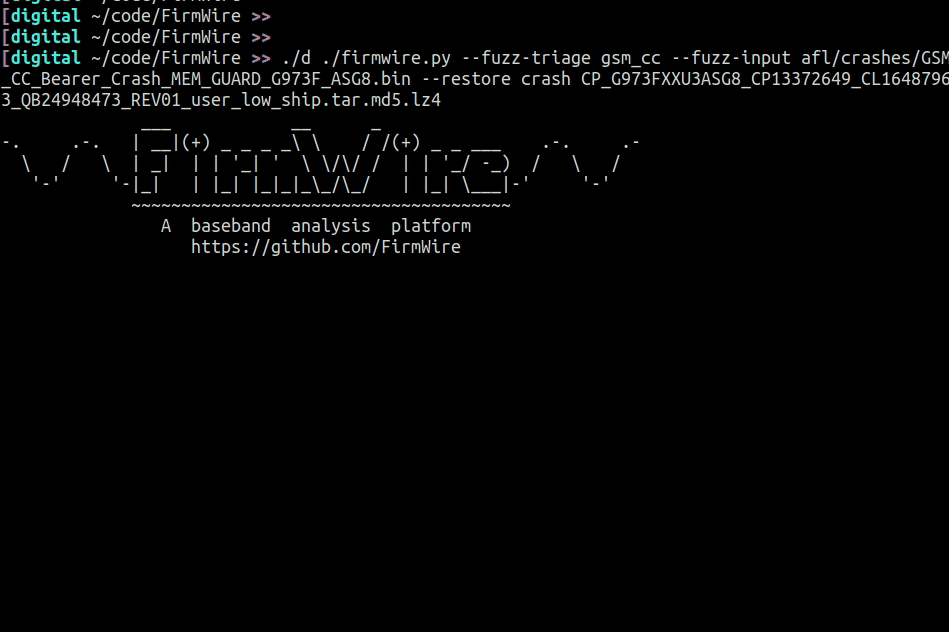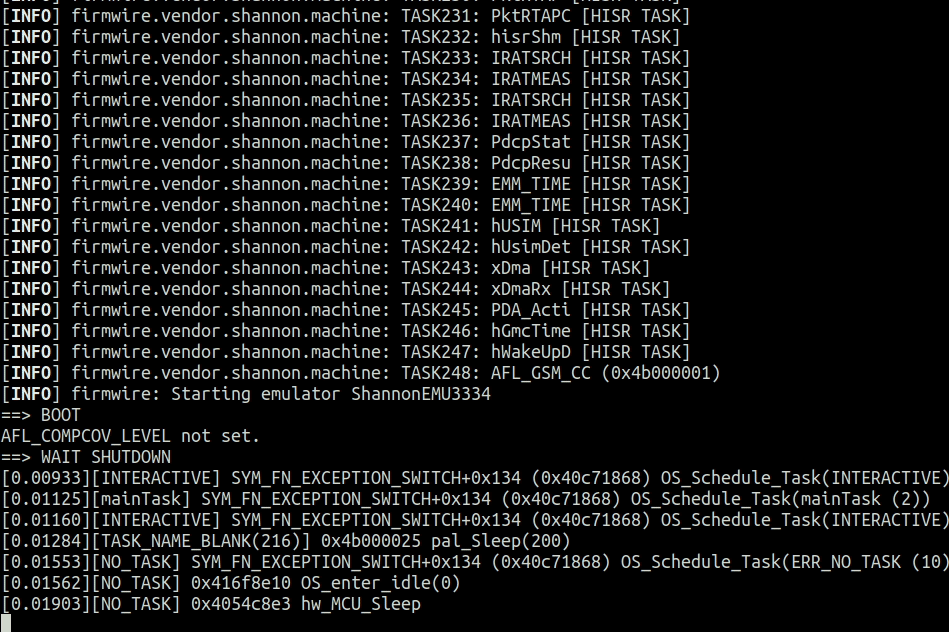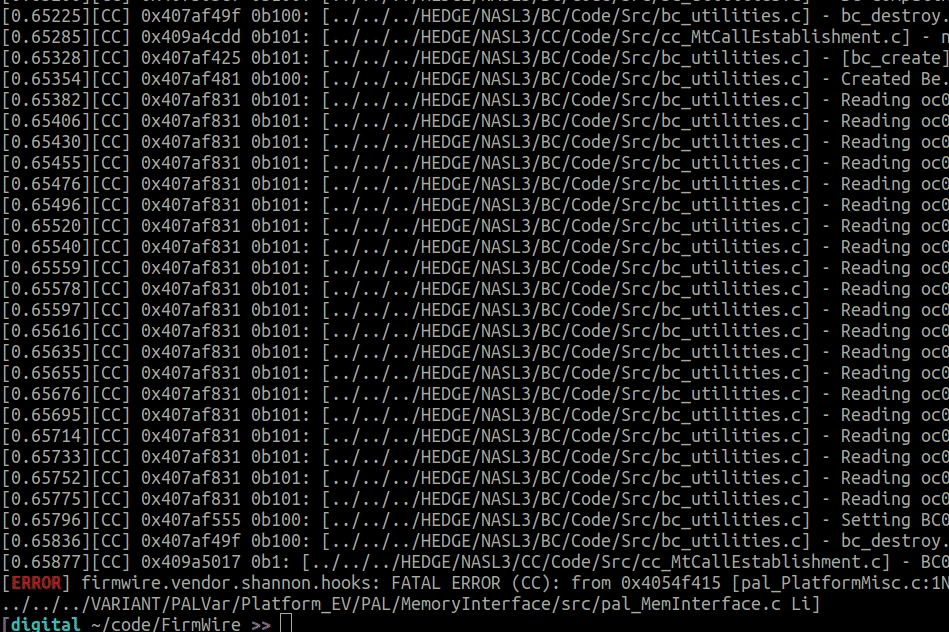
FirmWire is a full-system baseband firmware emulation platform for fuzzing, debugging, and root-cause analysis of smartphone baseband firmwares

Reverse engineering software using a full system simulator

HyperDeceit is the ultimate all-in-one library that emulates Hyper-V for Windows, giving you the ability to intercept and manipulate operating system…

A multi-platform fuzzer for poking at userland binaries, network clients and servers

unleash the full power of your BES-based headphones! :)

Proof-of-concept exploit for a Java gadget chain in the Mojarra library, demonstrating deserialization vulnerability exploitation for versions 2.3…

Red team tool for EDR evasion: dynamically resolves syscall IDs, patches ntdll stubs, unhooks IAT hooks, and lists hooked APIs from major EDR vendors.

Full featured multi arch/os debugger built on top of PyQt5 and frida

Reverse engineering analysis of Formbook, an info-stealer that uses .NET assembly manipulation and XOR decryption. Full payload extracted via x32dbg,…

Full ML-KEM-1024 key recovery from a partial Fujisaki-Okamoto comparison in wolfSSL (CVE-2026-6330 NEON, CVE-2026-10097 AVX2)

Reverse engineering analysis of Dropper GCleaner, a malware that uses a resilient C2 infrastructure, kernel driver loading, PowerShell/Conhost…

"Reverse engineering analysis of Agent Tesla, a .NET-based info-stealer that uses APC injection, token manipulation, and registry persistence.…

7-Zip XZ Decoder Heap Buffer Overflow - Full analysis, root cause, PoC, and RCE exploitation roadmap

From Solder to Shell: Full Hardware Exploitation of the Linksys WRT54GL Router (CVE-2022-43973)

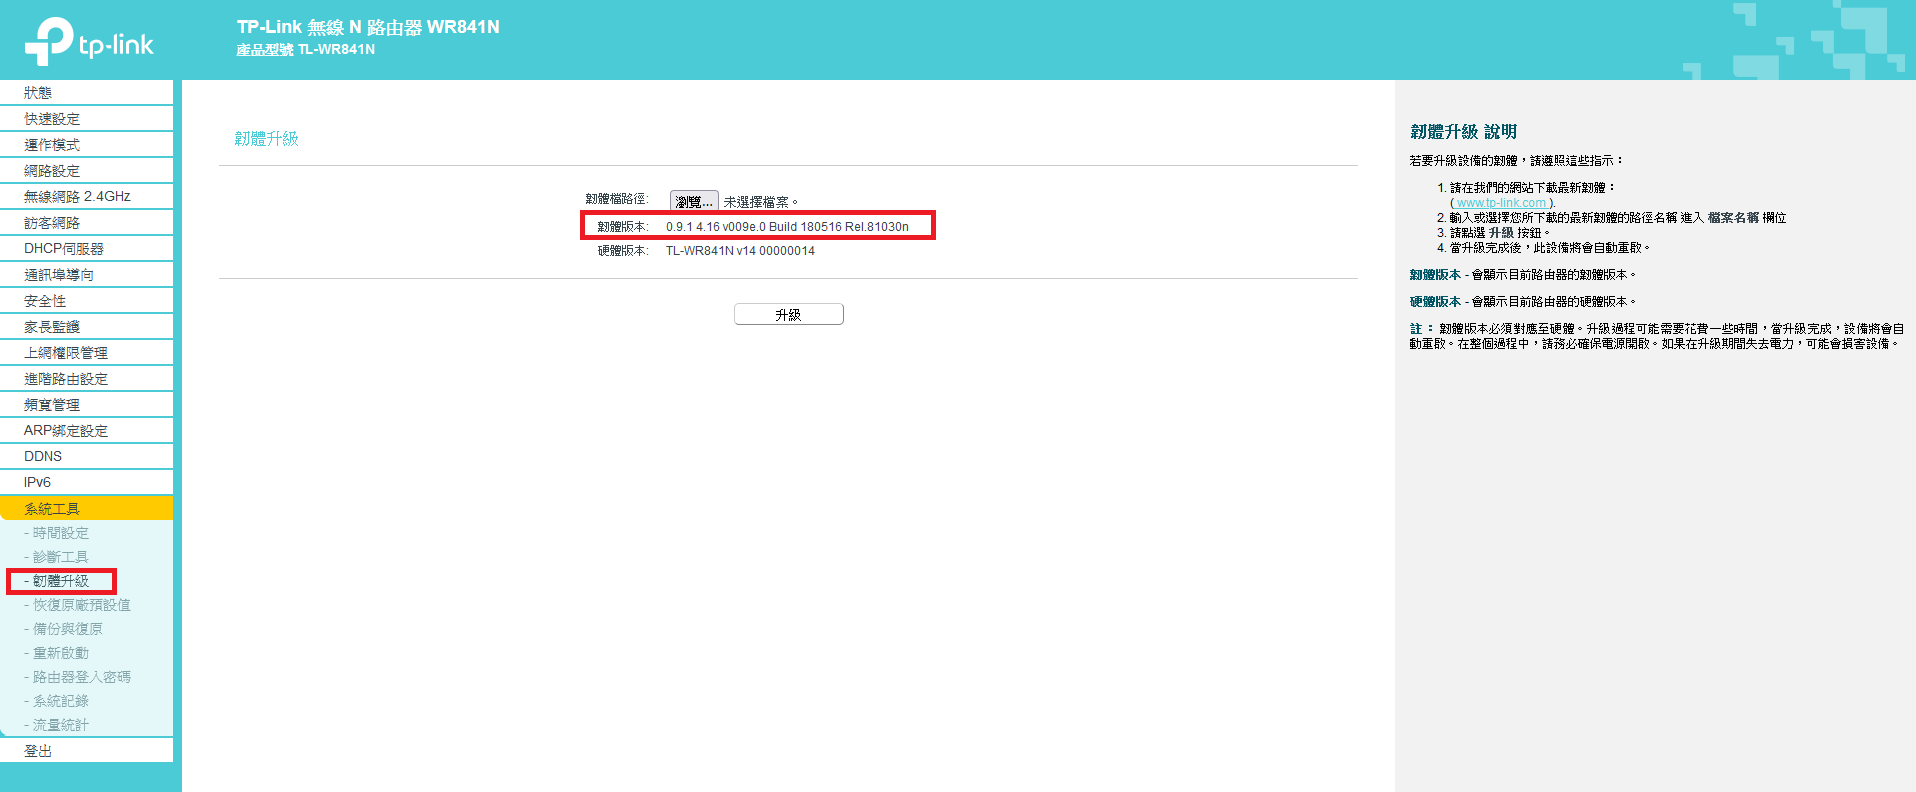
This repo contains dumped flash partitions with firmware version vulnerable to CVE-2019-17147, and some useful binaries to downgrade and debug your…

This repo contains instructions to reproduce CVE-2025-13425: Null Pointer dereference / Array over-indexing vulnerability that I found in Google's…