IDA2Obj
 jhftss/ida2obj
Static binary instrumentation tool that dumps COFF object files from executables, enabling code/data insertion at any location for black-box fuzzing…
binary-analysisdebuggersfuzzing+2
jhftss/ida2objStatic binary instrumentation tool that dumps COFF object files from executables, enabling code/data insertion at any location for black-box fuzzing…
 hfiref0x/wdextract
Extract Windows Defender database from vdm files and unpack it
 webraybtl/cve-2022-1068
Modbus Slave缓冲区溢出漏洞CVE-2022-1068分析与复现
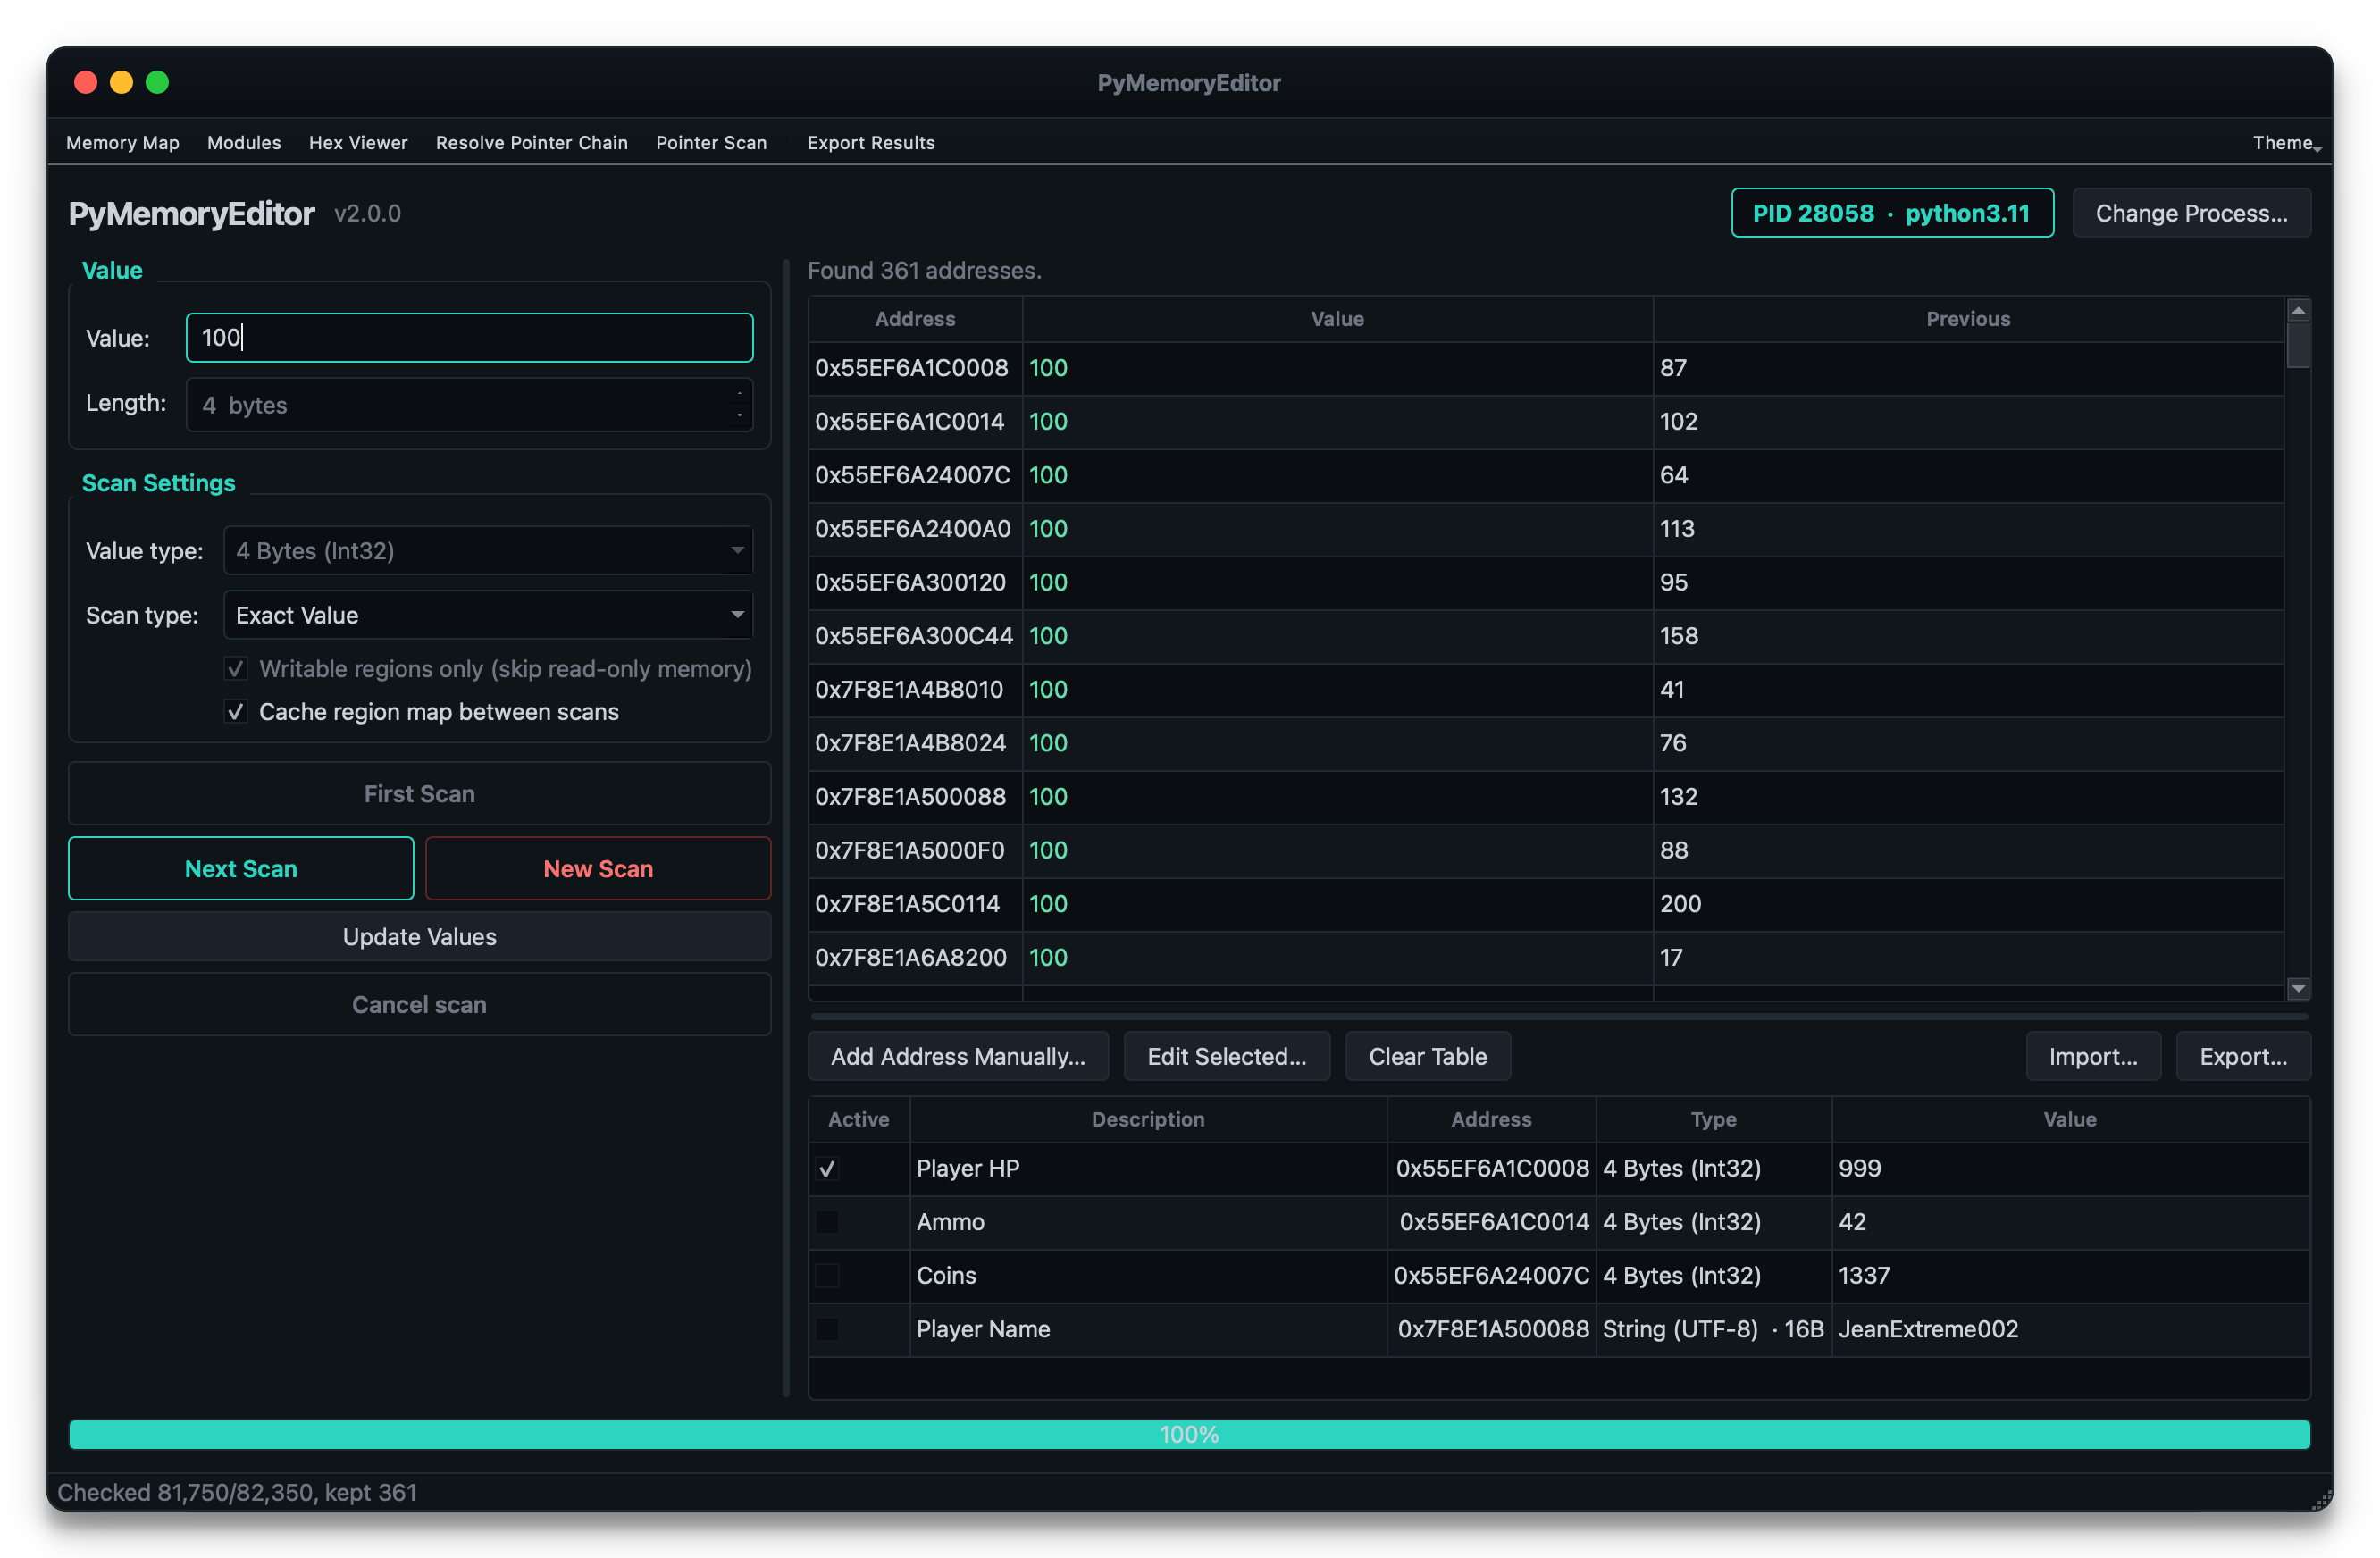 jeanextreme002/pymemoryeditor
A pure-Python library that lets you inspect, modify and search the memory of any running process in a few lines of Python :snake: .
 securityronin/memory-forensic
Walk any memory dump. Find what's hidden. Linux + Windows kernel forensics from a single static Rust binary — no Python required.
 forentfraps/pe-signgen
Universal signature generation for any system function from all Windows Builds using Winbindex
 dynamorio/dynamorio
Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
 fabrimagic72/malware-samples
A collection of malware samples caught by several honeypots i manage
 vardhan0257/upb-any-recursion-audit
Audit harness testing whether the CVE-2026-0994 Any-unwrapping recursion bug class affects upb's C core in Ruby and PHP protobuf bindings, with…
 yasharote/dll-injector
A desktop tool that allows injecting DLLs, hooking WinAPI functions like CreateFileW, and modifying process behavior at runtime — designed for…
 sf0rzin/cve-2025-61155
CVE-2025-61155 — arbitrary process termination in GameDriverX64.sys (Tower of Fantasy anti-cheat). Original IDA Pro teardown, PoC, YARA, IOCs,…