
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
47 results
awesome-list preview

awesome-list

GitHub0xor0ne/awesome-list

Cybersecurity oriented awesome list

binary-analysisctfcurated-resources+6
4.3k3 days ago
ghidra-scripts preview

ghidra-scripts

GitHub0xdea/ghidra-scripts

Curated Ghidra scripts to automate reverse engineering and vulnerability analysis: locate insecure functions, extract decompiler pseudocode, fix…
binary-analysisreverse-engineeringstatic-code-analysis+1
30210 days ago
PrivKit preview

PrivKit

GitHubmertdas/privkit

PrivKit is a simple beacon object file that detects privilege escalation vulnerabilities caused by misconfigurations on Windows OS.
binary-analysisexploitationpenetration-testing+4
6309 months ago
static-arm-bins preview

static-arm-bins

GitHubtherealsaumil/static-arm-bins

Statically compiled ARM binaries for debugging and runtime analysis
binary-analysisdebuggersdynamic-analysis-sandboxing+6
5295 years ago
Rusty-Playground preview

Rusty-Playground

GitHubblacksnufkin/rusty-playground

Some Rust program I wrote while learning Malware Development
binary-analysisexploitationmalware-analysis+6
1631 year ago
datadome-vm preview

datadome-vm

GitHubxkiian/datadome-vm

Reverse engineering the new Datadome VM 🔥
anti-botbinary-analysiscaptcha-bypass+3
1328 months ago
virt-firmware preview

virt-firmware

GitLabkraxel/virt-firmware

Toolkit for decoding, inspecting, and modifying UEFI firmware volumes and variable stores. Supports secure boot certificate enrollment, PE binary…

binary-analysisdigital-forensicsembedded-systems-security+3
1317 days ago
IDA-Processor-Modules preview

IDA-Processor-Modules

GitHubmr-wolf-is-me/ida-processor-modules

IDA Pro processor modules adding disassembly support for uncommon CPU, DSP, and GPU architectures including XMOS xCORE, TI C7x/PRU, MicroBlaze, and…
binary-analysisdebuggersembedded-systems-security+4
87 days ago
vmp2 preview
Archived

vmp2

GitHubaftermathlabs/vmp2

Unpack and deobfuscate VMProtect 2 protected binaries with an emulation-based VM explorer, handler profiler, and experimental LLVM recompiler for…
binary-analysiscode-analysisdynamic-code-analysis+3
13211 months ago
GoRedOps preview
Archived

GoRedOps

GitHubkiexitdispatcher/goredops

🦫 | GoRedOps is a repository dedicated to gathering and sharing advanced techniques and offensive malware for Red Team, with a specific focus on…

anti-botbinary-analysiscommand-and-control+9
6701 year ago
frida-il2cpp-datacollector preview

frida-il2cpp-datacollector

GitHubgmh5225/frida-il2cpp-datacollector

Frida-based tool that ports Cheat Engine's MonoDataCollector to Android and iOS, enabling runtime Mono/IL2CPP data collection and memory inspection…
android-securitybinary-analysisdebuggers+5
134 years ago
ProtectMyTooling preview

ProtectMyTooling

GitHubmgeeky/protectmytooling

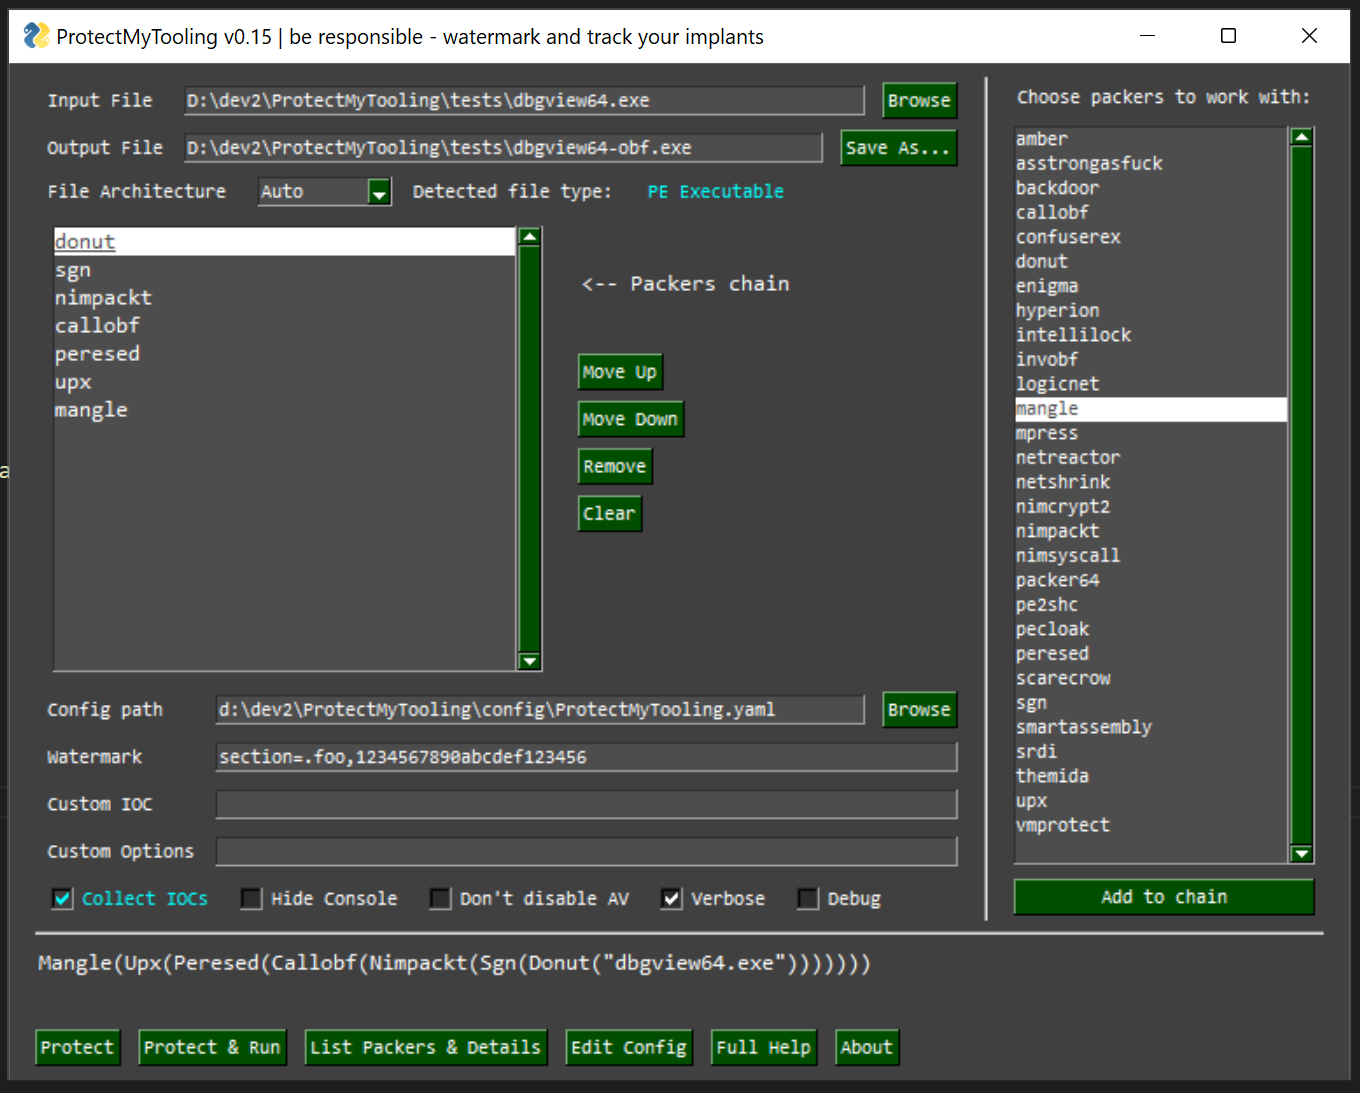
Multi-Packer wrapper letting us daisy-chain various packers, obfuscators and other Red Team oriented weaponry. Featured with artifacts watermarking,…

binary-analysisexploit-frameworksioc-management+5
1.1k1 year ago
pe-sieve preview

pe-sieve

GitHubhasherezade/pe-sieve

Scans a given process. Recognizes and dumps a variety of potentially malicious implants (replaced/injected PEs, shellcodes, hooks, in-memory patches).
binary-analysisforensicsmalware-analysis+2
3.9k4 months ago
Hunt-Sleeping-Beacons preview

Hunt-Sleeping-Beacons

GitHubtheflink/hunt-sleeping-beacons

Callstack scanner that identifies IOCs of unpacked or injected C2 agents by analyzing thread idle behavior, unbacked memory, module stomping, APCs,…
binary-analysisdefensive-toolsforensics+3
6889 months ago
yaralyzer preview

yaralyzer

GitHubmichelcrypt4d4mus/yaralyzer

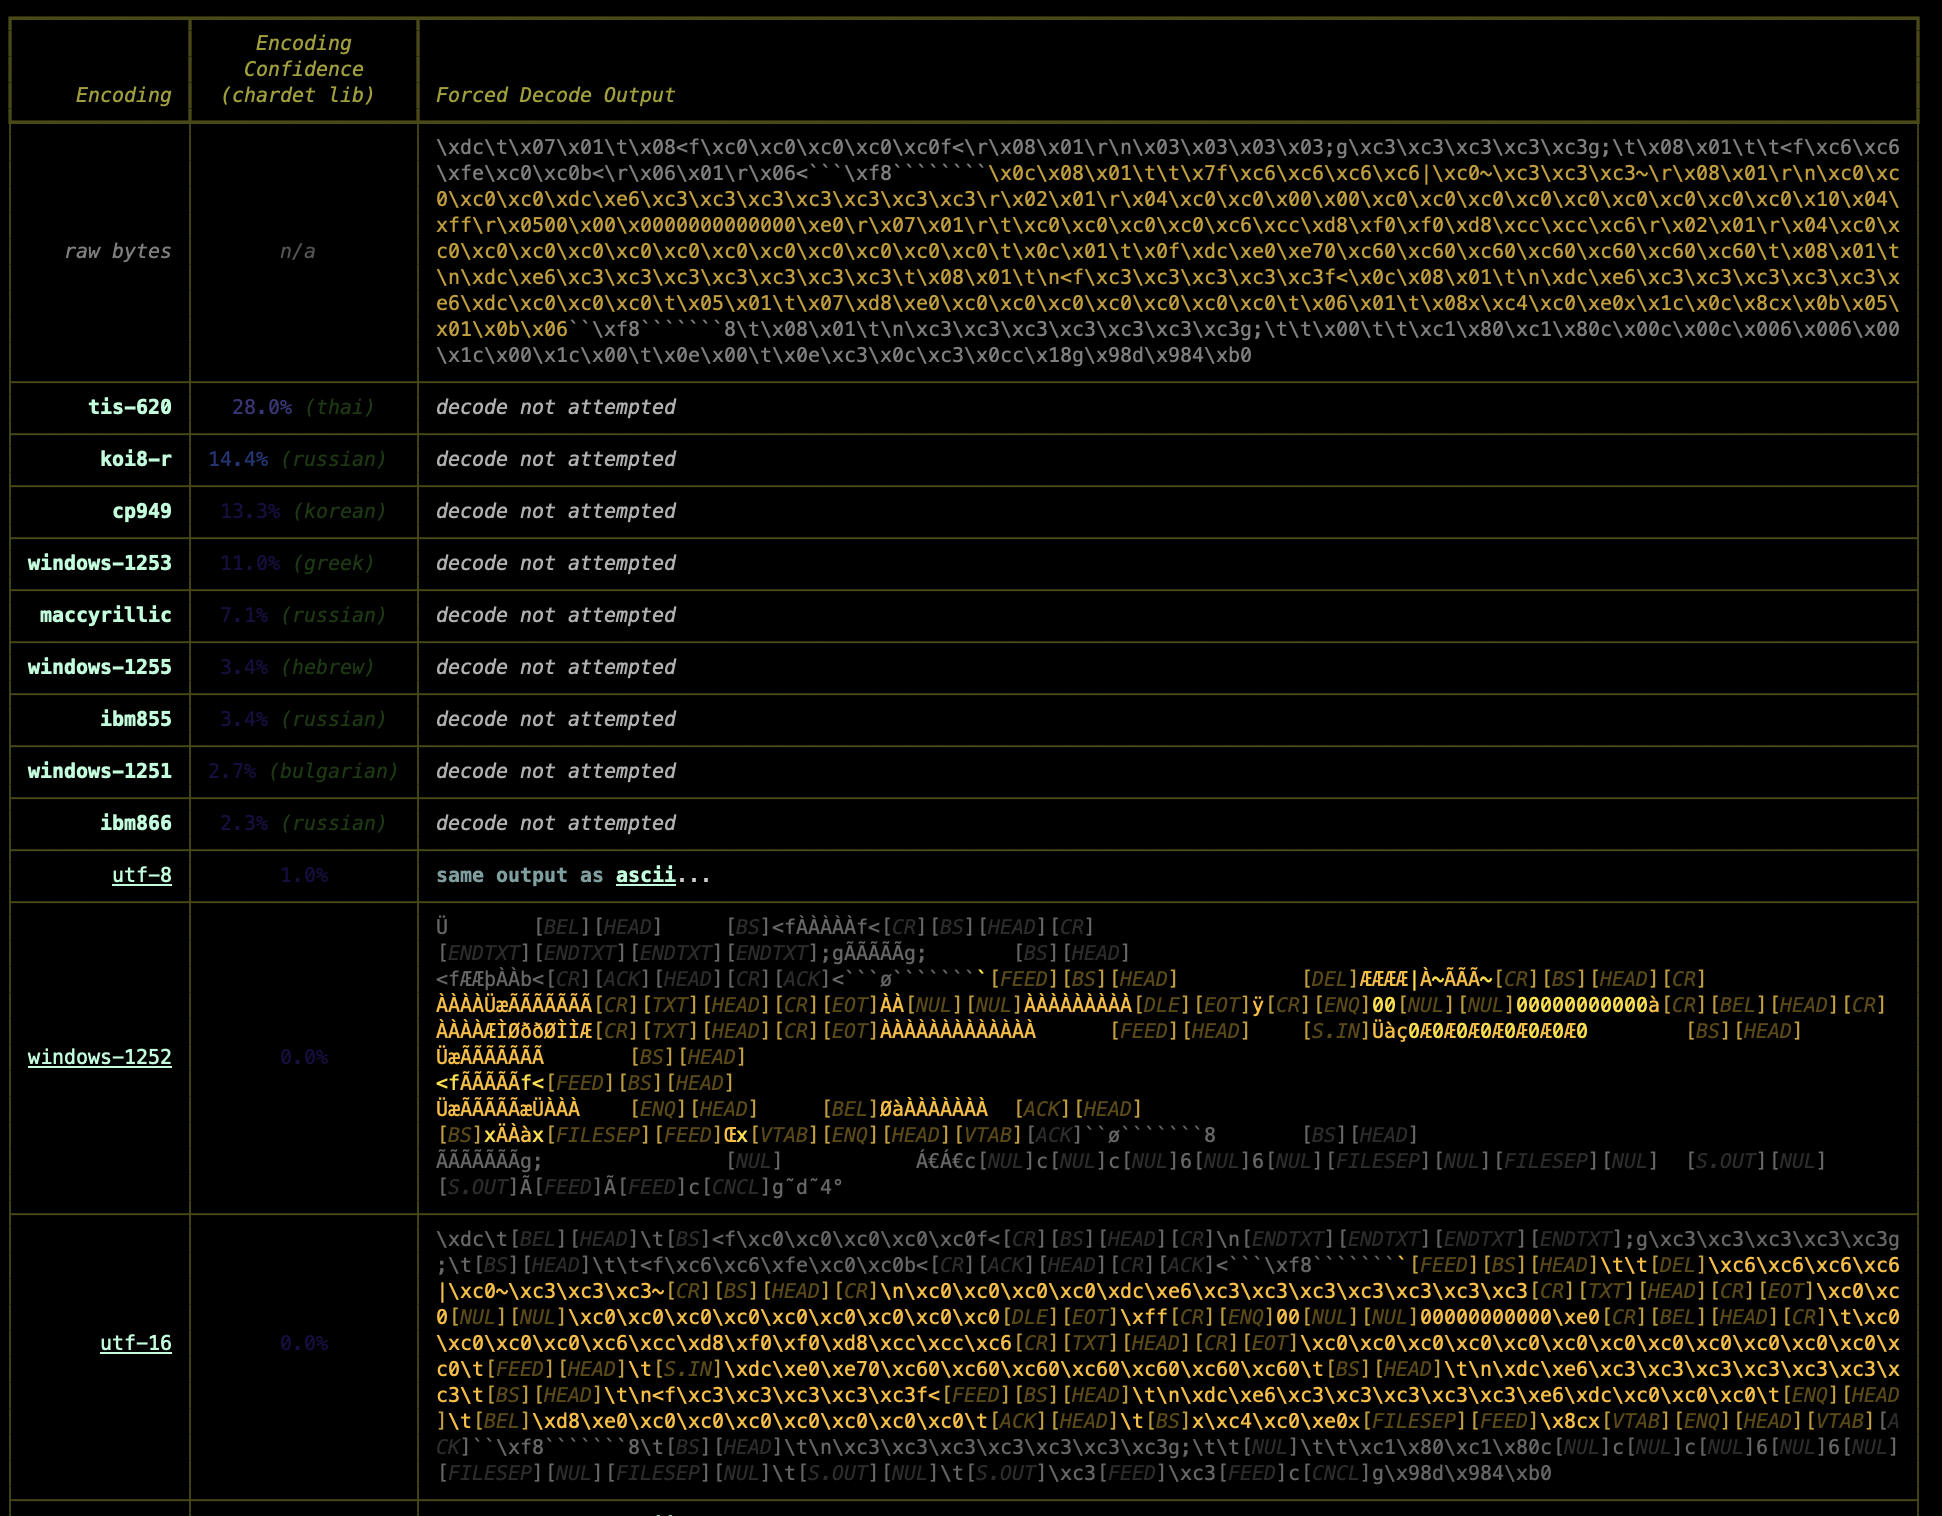
Visually inspect and force decode YARA and regex matches found in both binary and text data with colors. Lots of colors.
binary-analysisforensicsmalware-analysis+1
1539 months ago
NeuroCore preview

NeuroCore

GitHubfarukalpay/neurocore

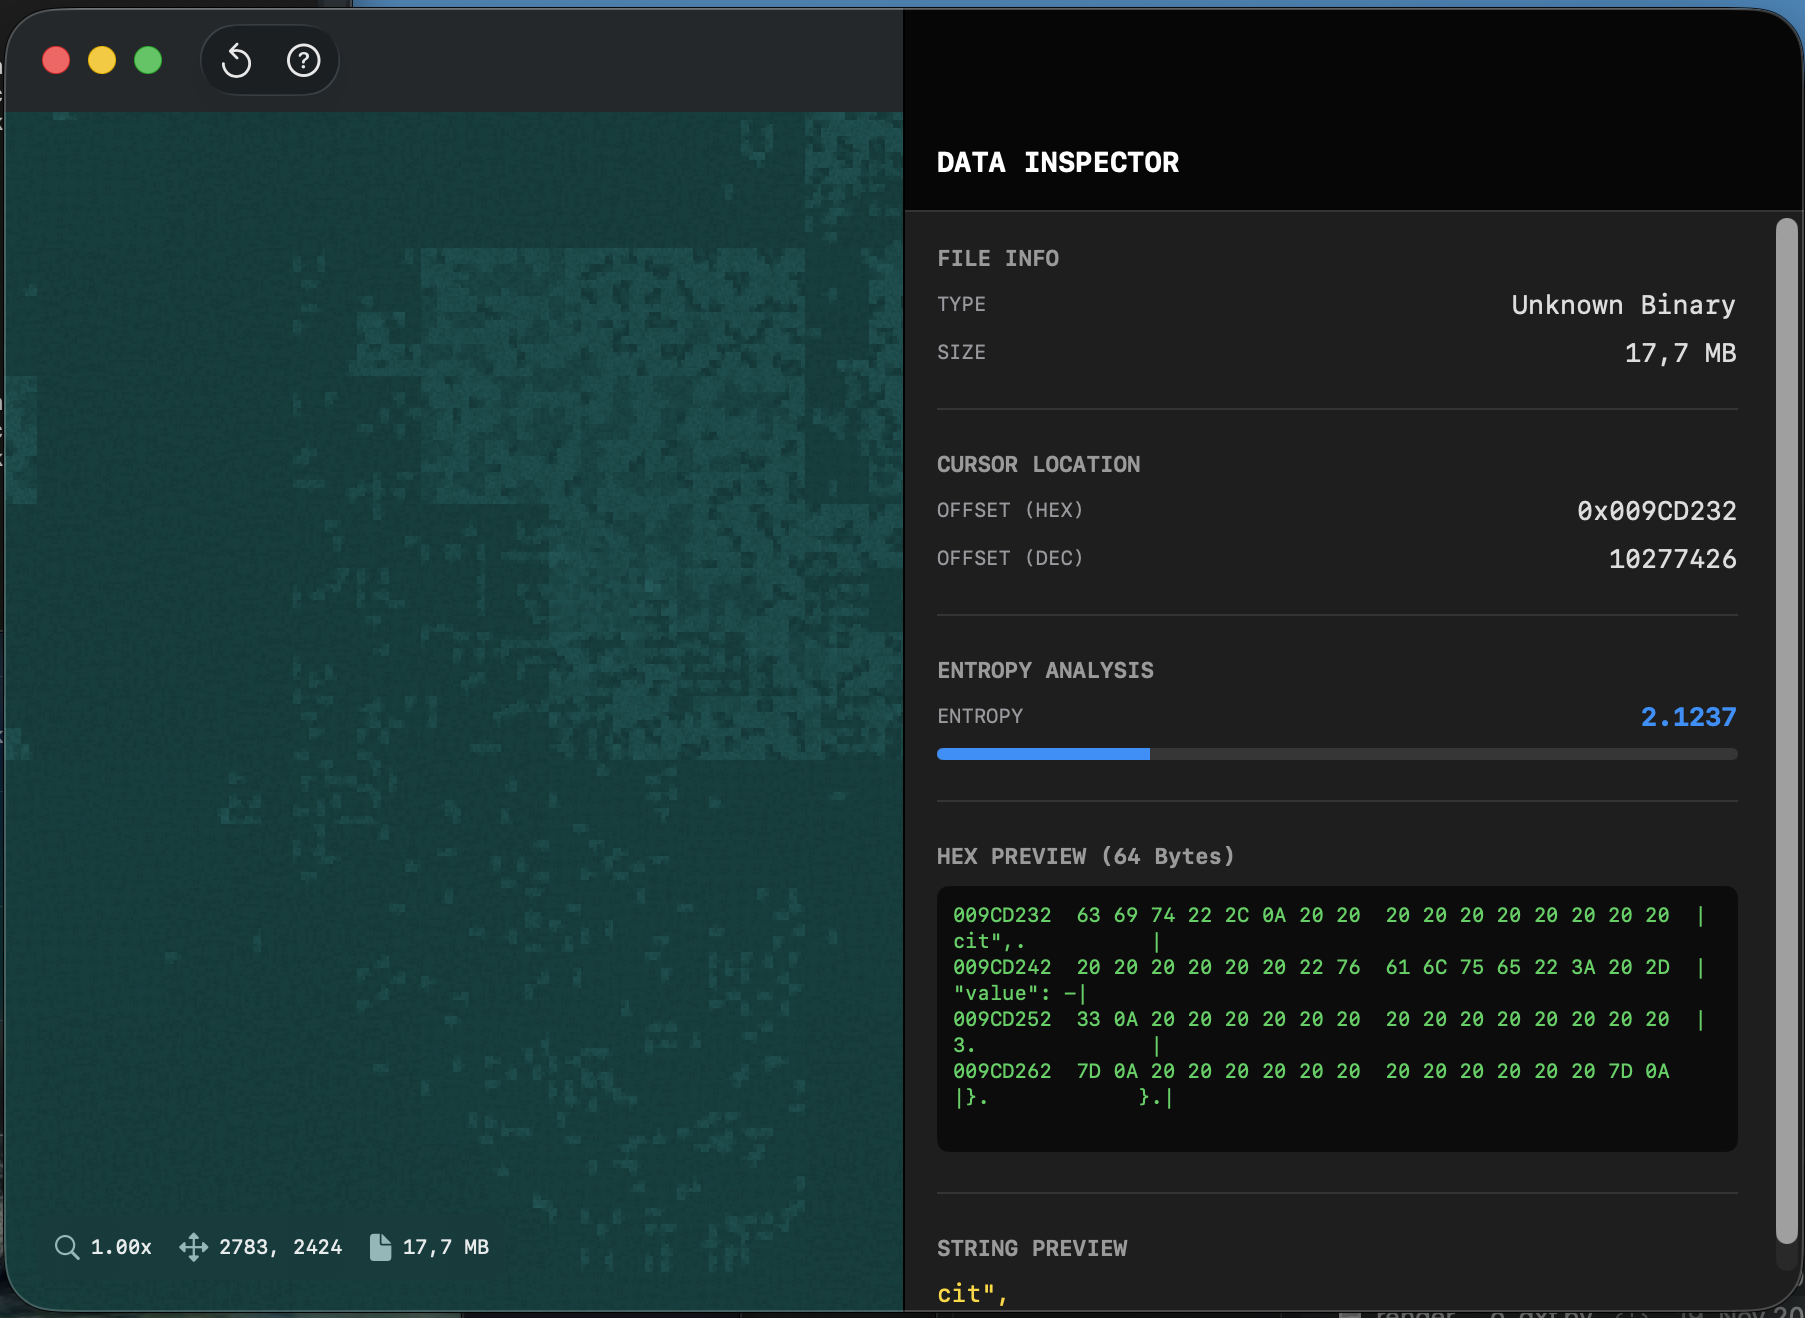
NeuroCore is a native macOS application that visualizes the internal structure of binary files using a Hilbert Curve mapping and Shannon Entropy…
binary-analysisdigital-forensicsforensics+3
289 months ago
BiBi-Windows-Wiper-Analysis preview

BiBi-Windows-Wiper-Analysis

GitHubknight0x07/bibi-windows-wiper-analysis

Technical Analysis of Bibi-Windows Wiper Targeting Israeli Organizations
binary-analysisdigital-forensicsincident-response+3
92 years ago
cve-2025-24985 preview

cve-2025-24985

GitHubairbus-cert/cve-2025-24985

Detection of malicious VHD files for CVE-2025-24985

binary-analysisdigital-forensicsexploitation+3
21 year ago
Previous123Next