
RPC-Triage
 talha-nazeef-ahmed/rpc-triage
A zero-symbol static analysis engine that extracts and mathematically ranks the Windows RPC attack surface using an AHP-based risk model.
binary-analysisreconnaissancered-teaming+3
14
talha-nazeef-ahmed/rpc-triageA zero-symbol static analysis engine that extracts and mathematically ranks the Windows RPC attack surface using an AHP-based risk model.
 xenokovah/inteltxe-poc
Intel Management Engine JTAG Proof of Concept - 2022 Instructions
 thisistfs/rogue-framework
Desktop workbench for AFL++ fuzzing, cross-architecture QEMU emulation, harness development, Ghidra headless analysis, custom mutators, and patch…
 zxgio/ghidra_stack_strings
A script to detect stack-strings by using emulation (leveraging Unicorn)
 crissyfield/super-trouper
MCP server exposing Frida instrumentation as tools for coding agents to connect to devices, inspect processes, manage sessions, and load JavaScript…
 vichhka-git/renef-skills
Agent Skill for operating renef.io — Android ARM64 dynamic instrumentation: hook native/Java, patch memory, trace syscalls, bypass SSL pinning/root…
 tjnel/certgraveyard_yara
Automated YARA rule generation from the Cert Central compromised certificate database.
 nccgroup/libmempool
Heap analysis tooling for mempool
 martyx00/vulnfanatic-ng
BianryNinja plugin for identifying vulnerabilities in decompiled binaries with both programmatic scans and LLM support.
 binref/agent
Language Model Agent Instructions for Binary Refinery
 myrtus0x0/smoke_conf_extract
Static config extractor for SmokeLoader samples that deobfuscates, unpacks, and emulates protected routines to recover final-stage C2 settings.
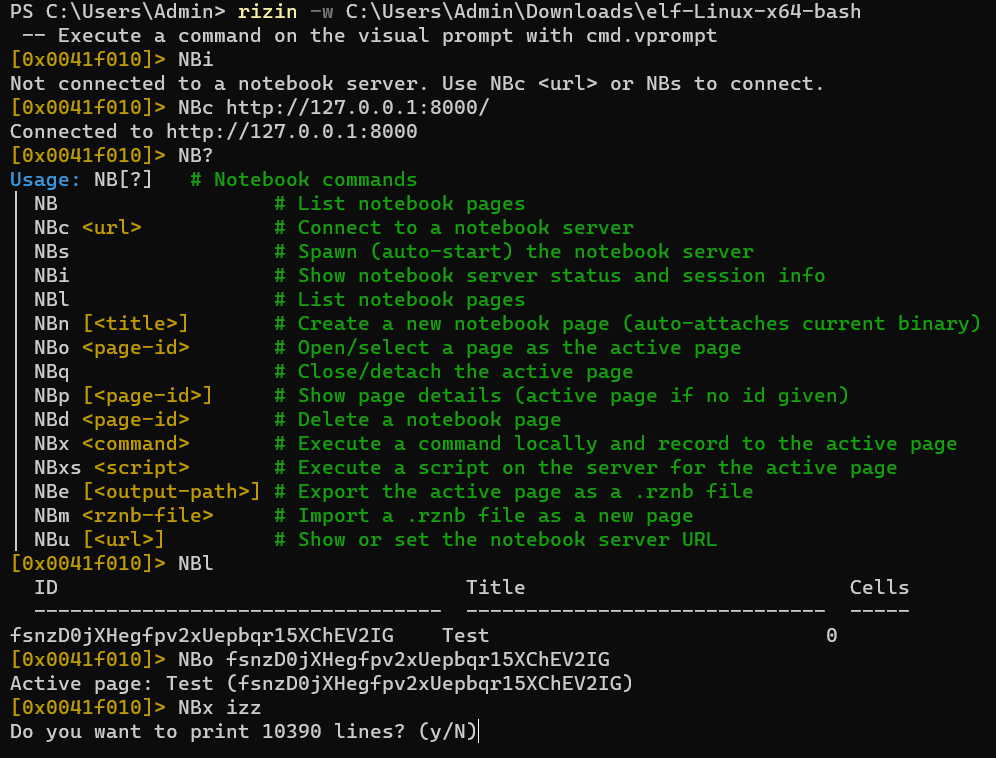 rizinorg/rizin-notebook
A notebook where to writes notes while using rizin!
 e-gleba/world_conqueror_4_ru
Translated strings for World Conqueror 4 (RU)
 indalok/rizin-notebook
A notebook where to writes notes while using Rizin & Cutter!
 mdshoaibuddinchanda/zombieguard
ML-based detection of Zombie ZIP archive header evasion attacks (CVE-2026-0866)
 jwalker/frida-ios-dump-modern
An updated Frida iOS dump tool supporting the latest Frida 17.5.2 APIs