
CallObfuscator
 d35ha/callobfuscator
Obfuscate specific windows apis with different apis
binary-analysisdefensive-toolsdynamic-analysis-sandboxing+4
1.0k
d35ha/callobfuscatorObfuscate specific windows apis with different apis
 osirislab/awesome-rust-security
Curated list of awesome projects and resources related to Rust and computer security
 cybereason/siofra
Simulates the Windows PE loader to identify DLL hijacking vulnerabilities, generates weaponized DLLs with shellcode payloads, and detects UAC…
 mrt4ntr4/ntwarden
Windows Analysis and Research Toolkit
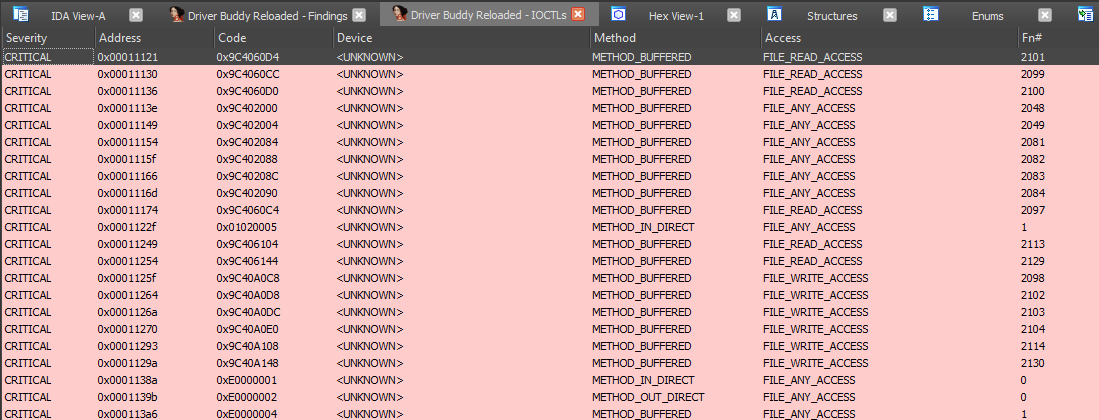 voidsec/driverbuddyreloaded
Driver Buddy Reloaded is an IDA Pro Python plugin that helps automate some tedious Windows Kernel Drivers reverse engineering tasks
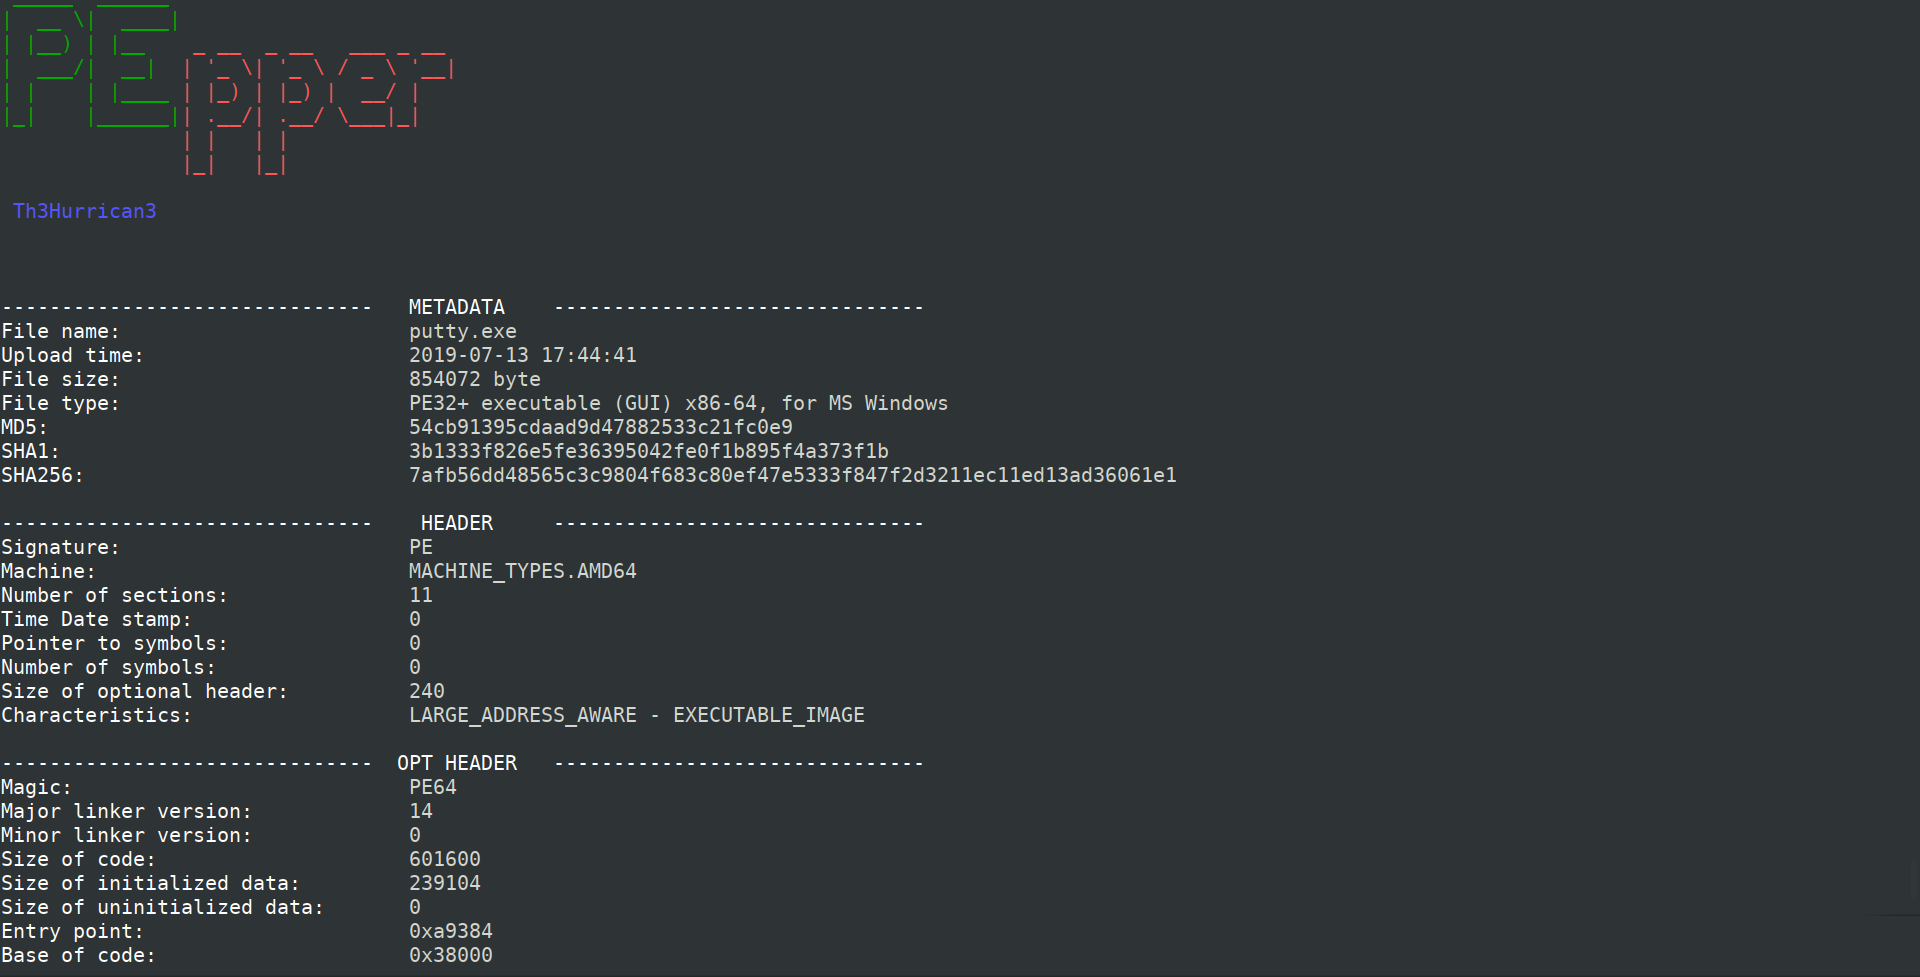 0x0be/pepper
An open source script to perform malware static analysis on Portable Executable
 hfiref0x/wdextract
Extract Windows Defender database from vdm files and unpack it
 nirizr/rematch
REmatch, a complete binary diffing framework that is free and strives to be open source and community driven.
 iamsopotatoe-coder/tinyload
Open source Windows x64 PE packer and crypter. Compresses and encrypts executables with a custom virtual machine into a self extracting stub.
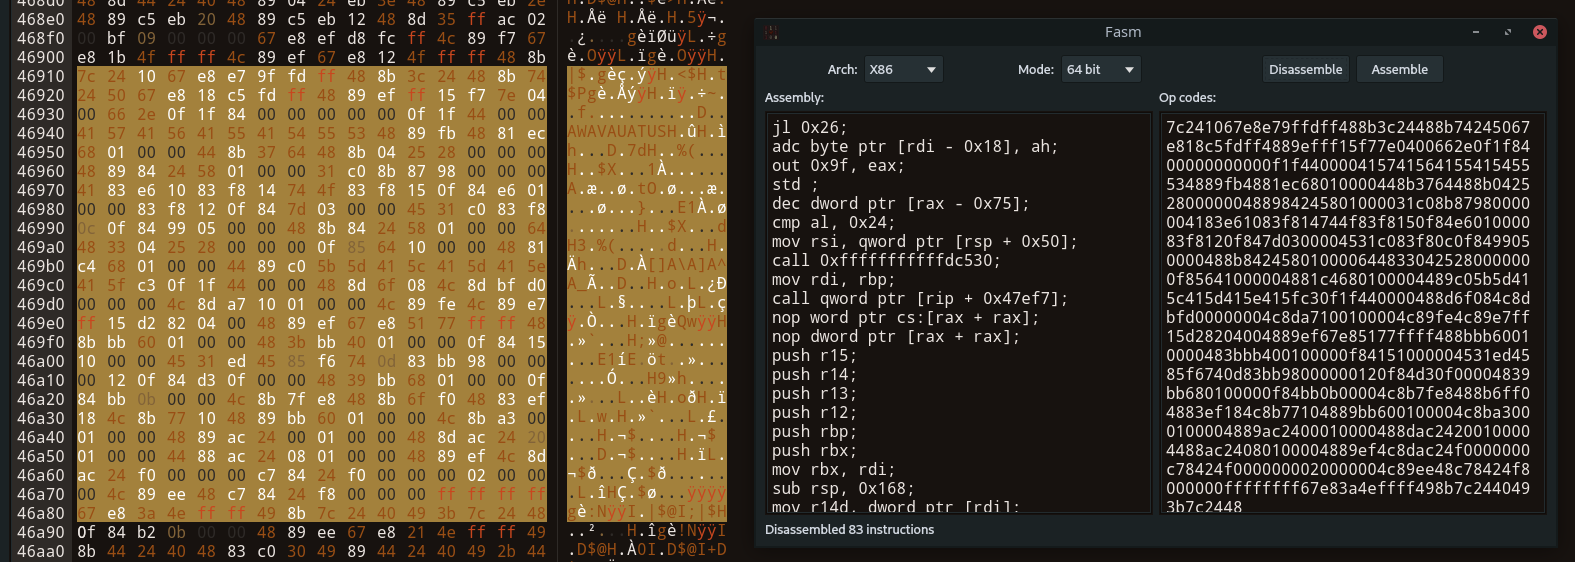 echo-devim/fhex
A Full-Featured HexEditor compatible with Linux/Windows/MacOS
 gpoulios/ropinjector
Patching ROP-encoded shellcodes into PEs
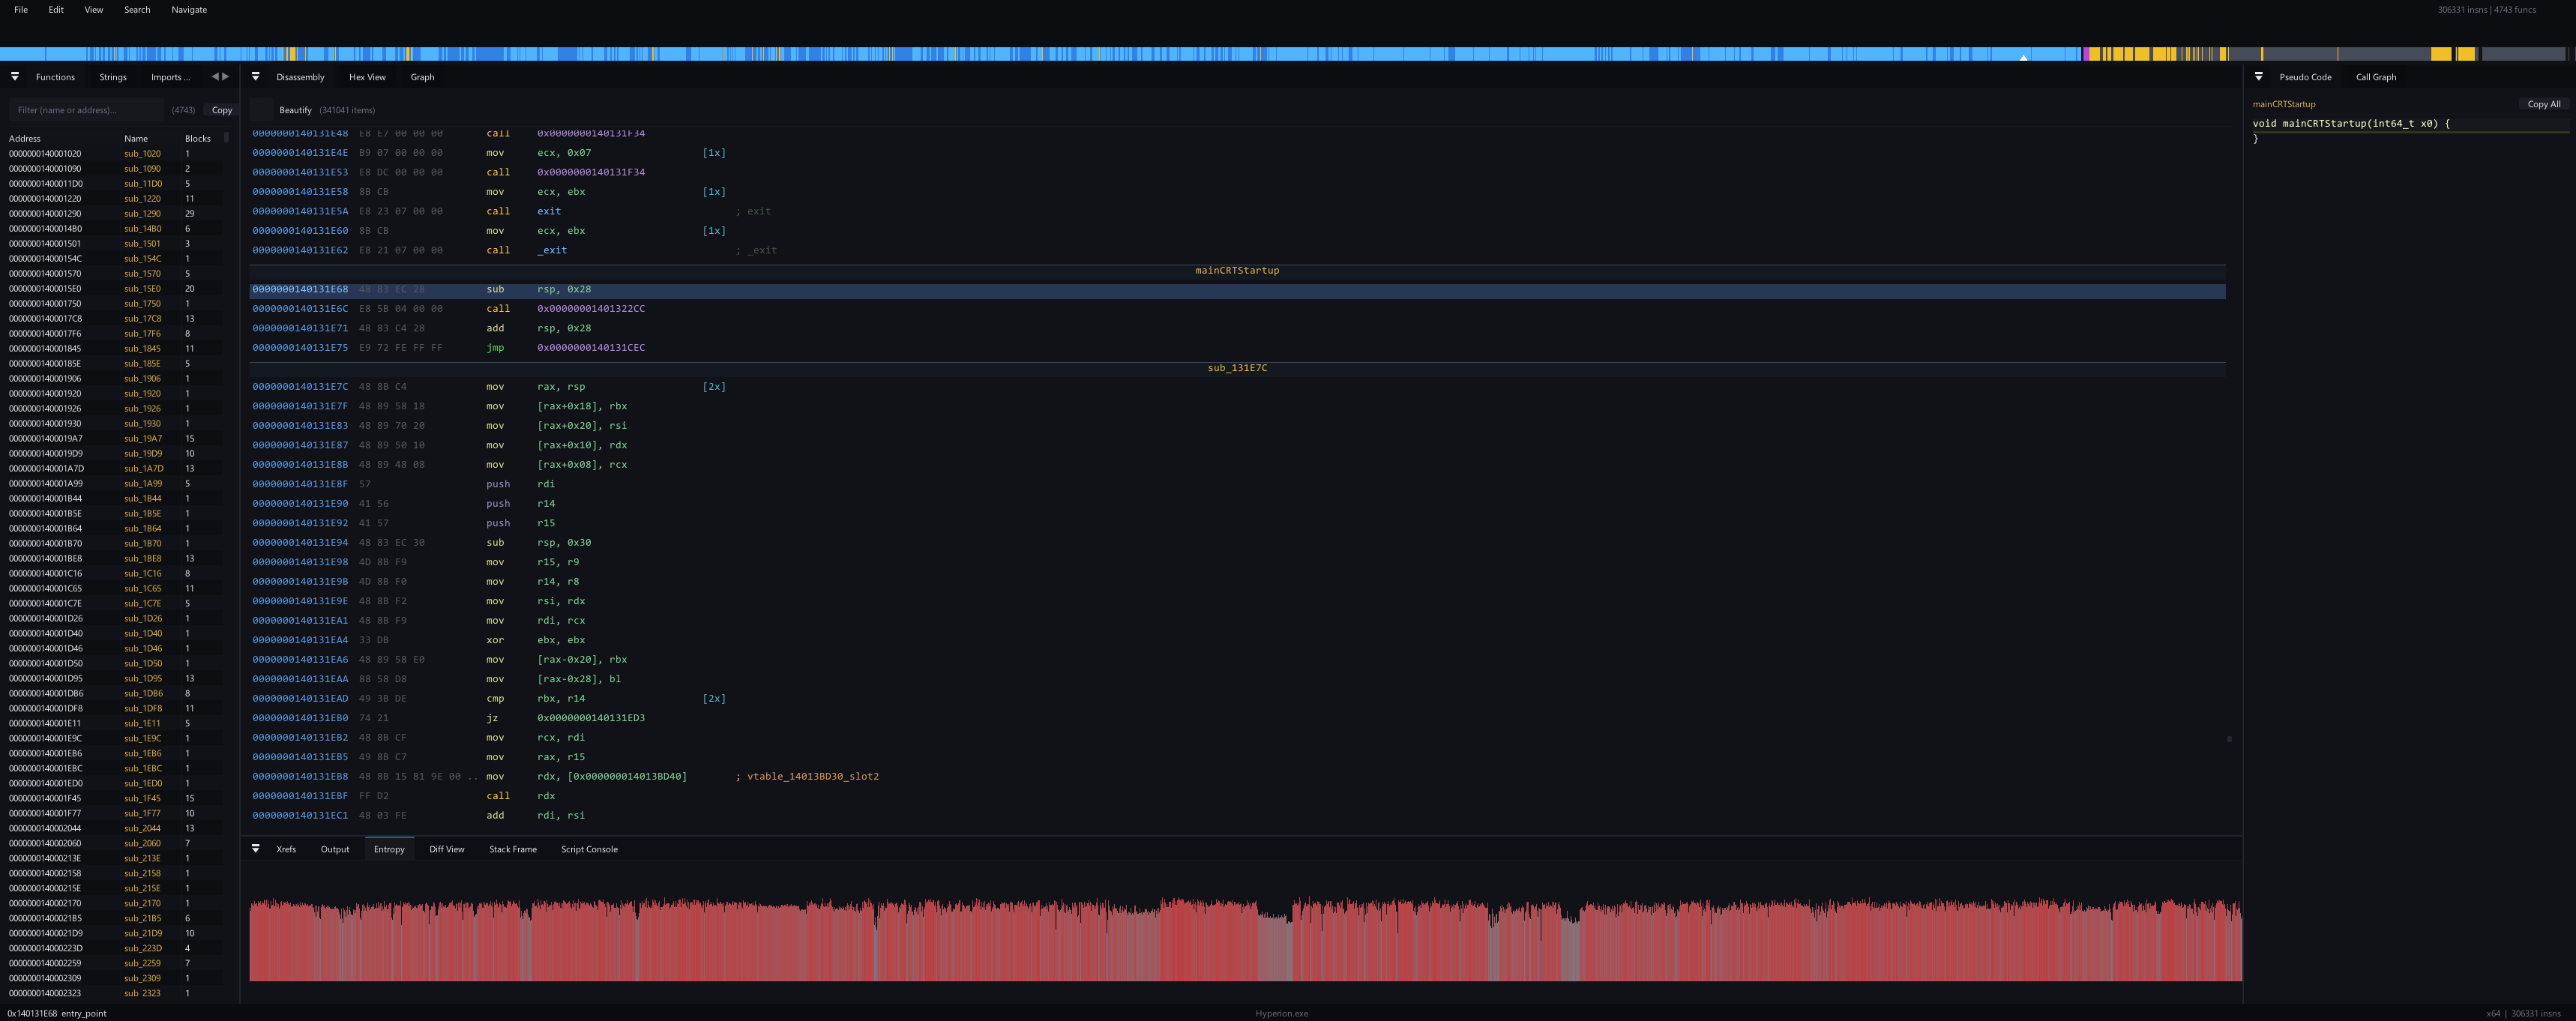 sidenai/hyperion-disassembler
Native multi-arch disassembler & decompiler - PE/ELF/Mach-O, x86/x64/ARM64, Lua scripting, RTTI recovery
 lucamassarelli/yarasafe
SAFE embeddings to match functions in yara
 nozominetworks/upx-recovery-tool
Automates repair of malformed UPX headers in ELF binaries, restoring magic, filesize, blocksize, and overlay fields so standard unpackers can process…
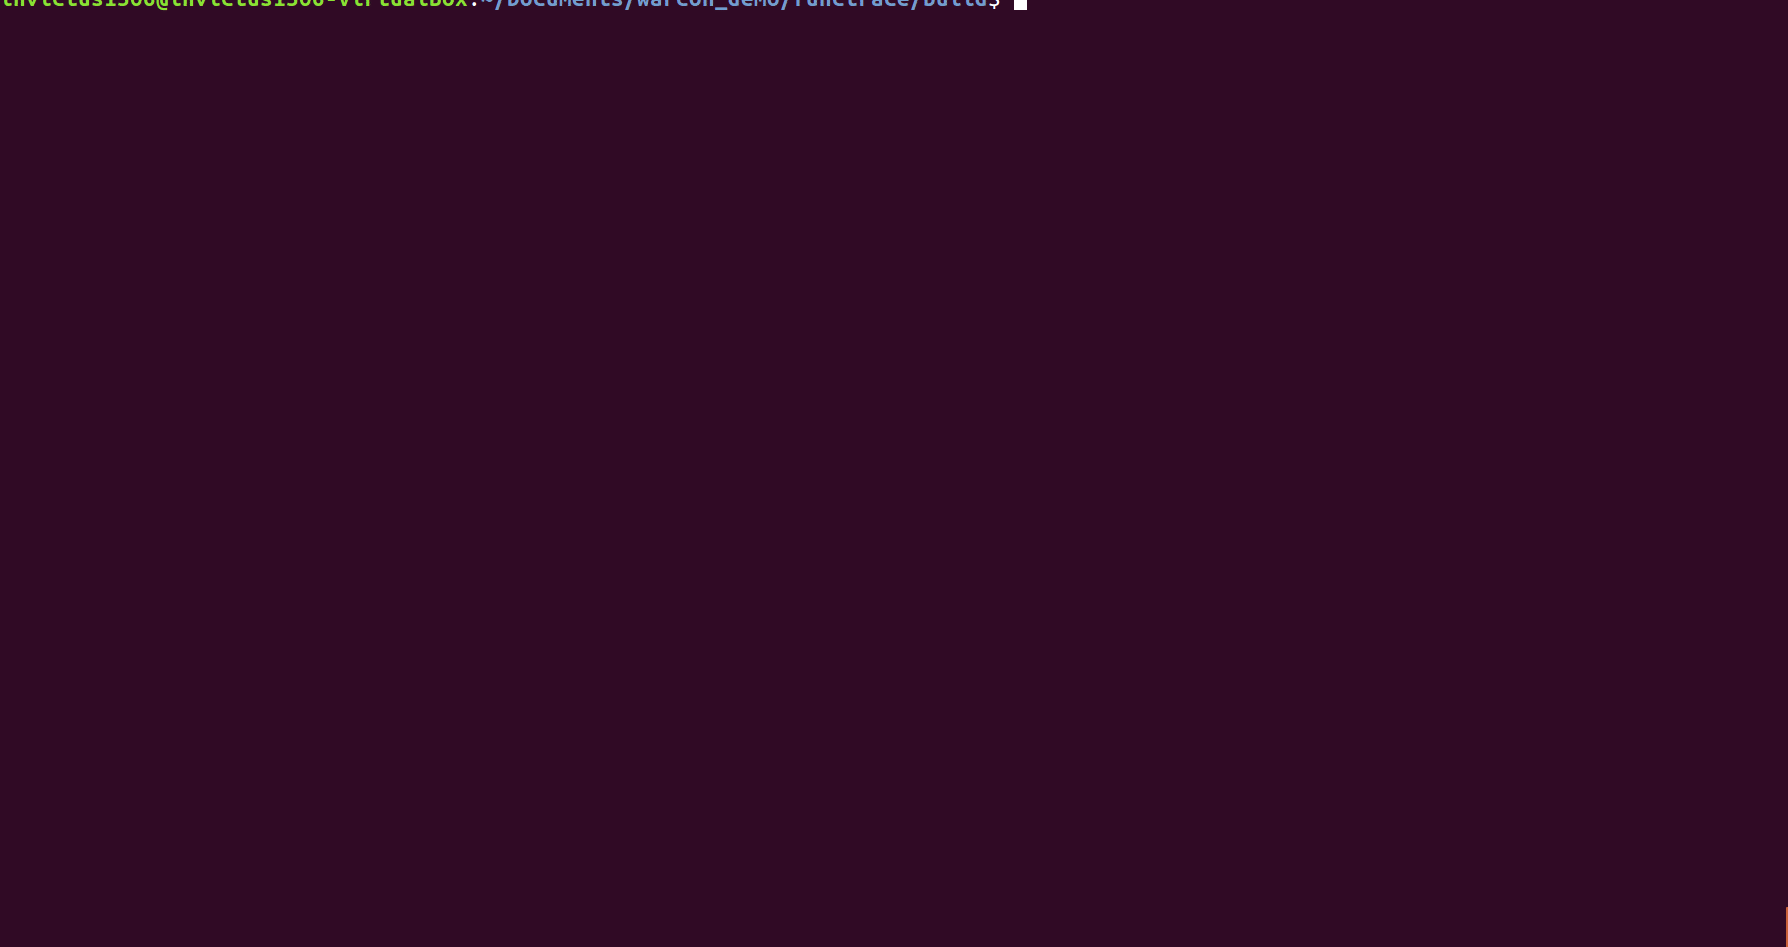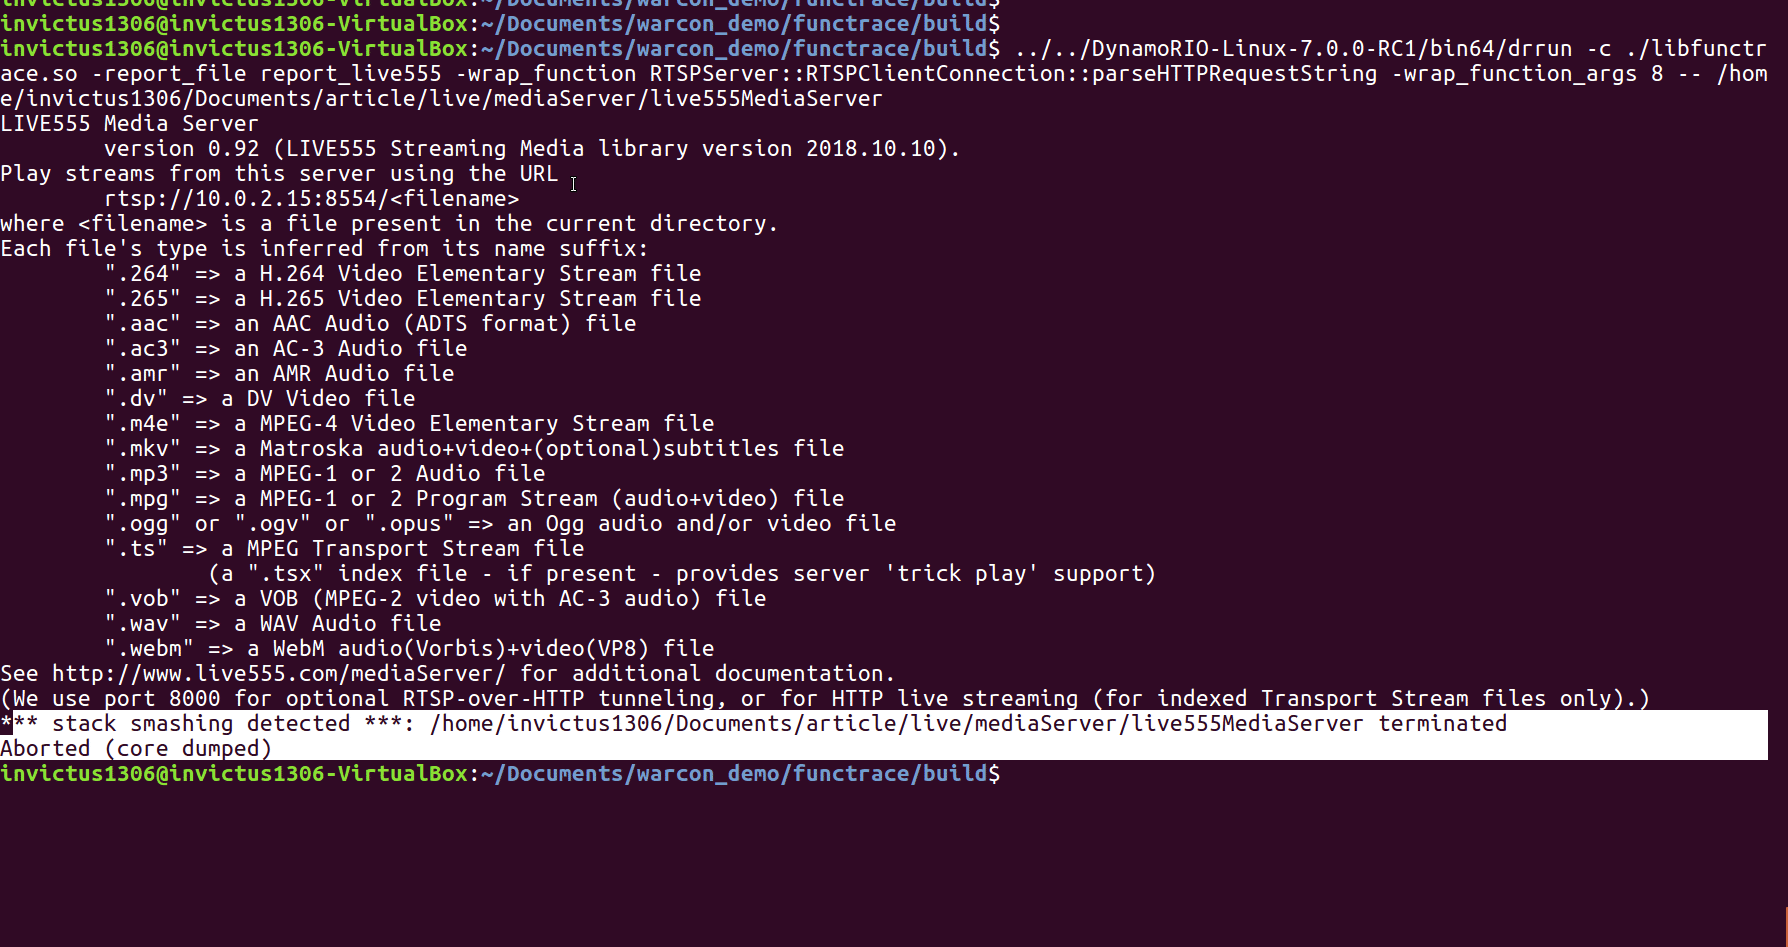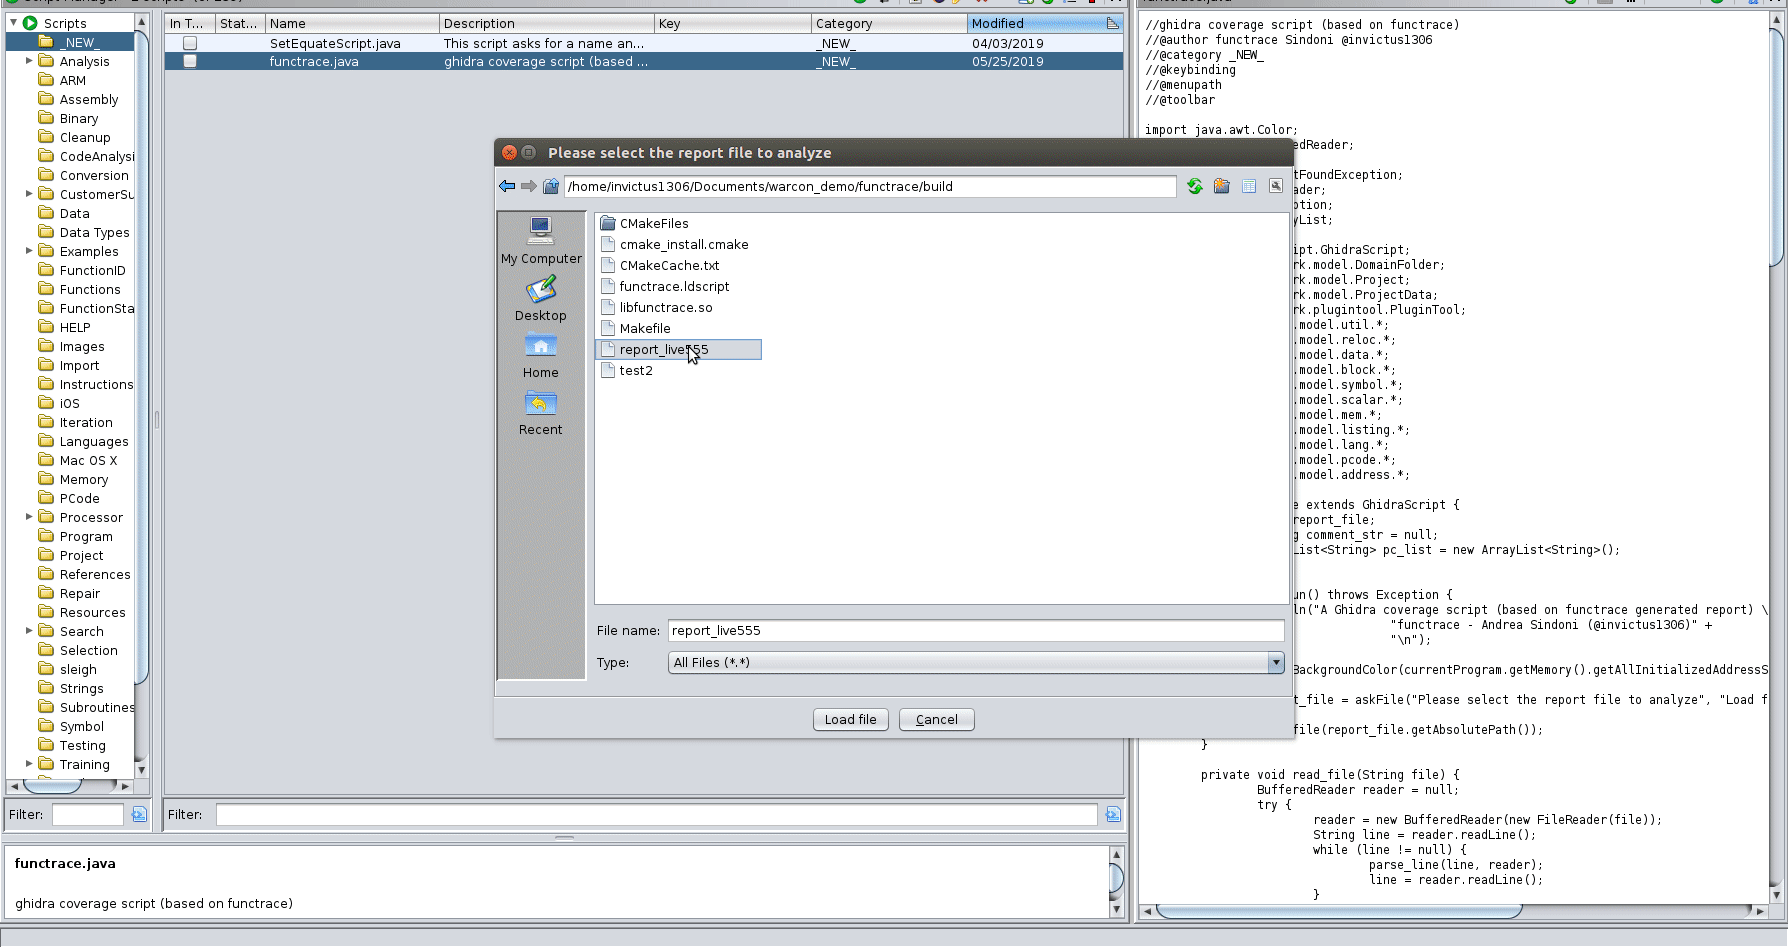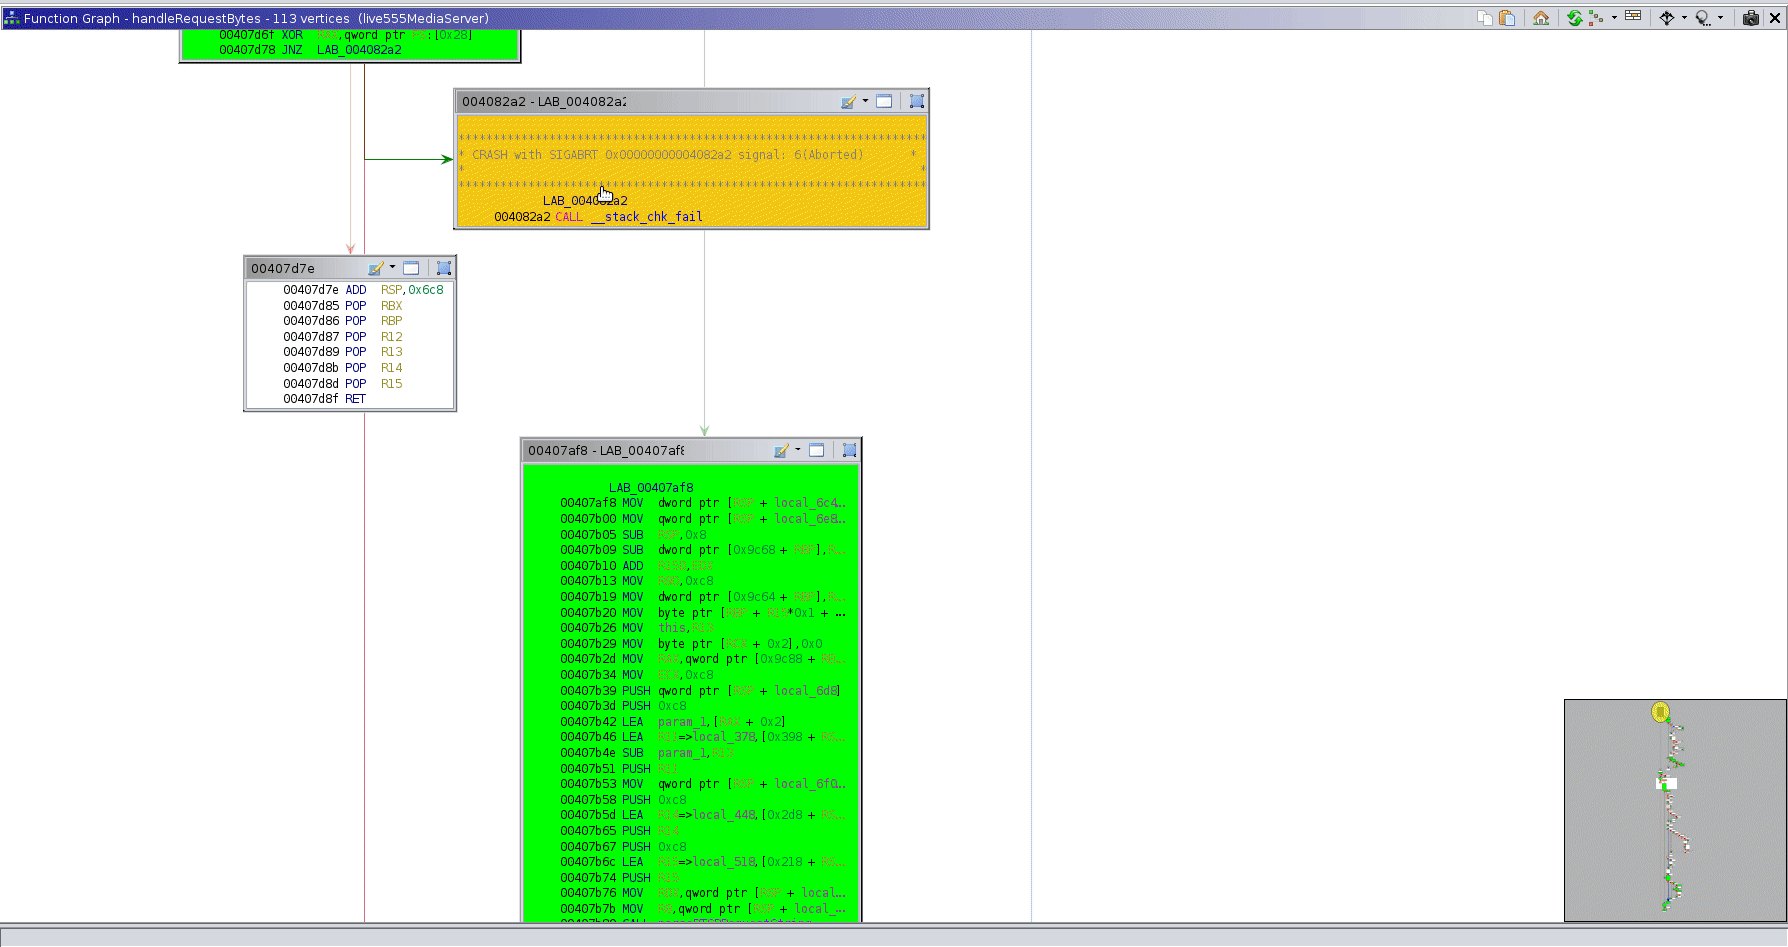 invictus1306/functrace
A function tracer
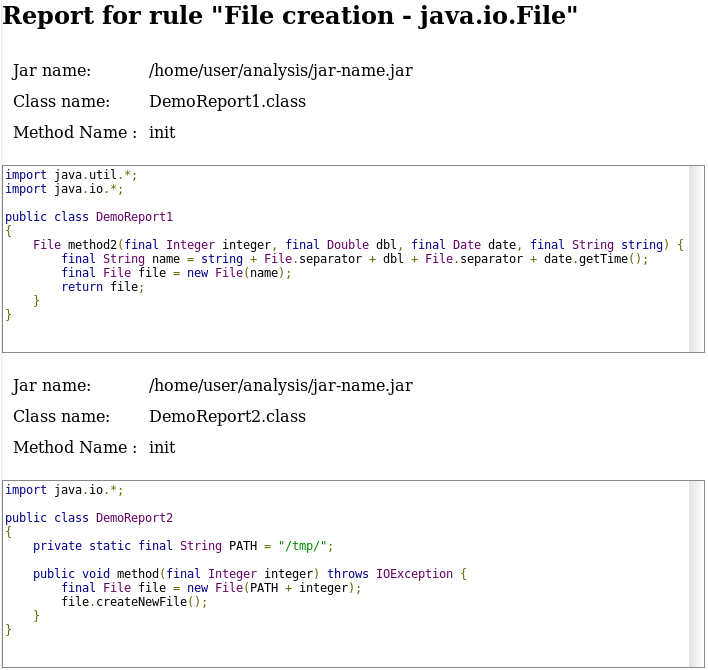 fergarrui/custom-bytecode-analyzer
Java bytecode analyzer customizable via JSON rules
 paul-tew/lifer
Windows link file (shortcuts) examiner