

z3
 z3prover/z3
High-performance SMT solver for automated theorem proving, constraint solving, and program verification. Supports multiple theories and language…
binary-analysiscryptographyeducation+2
12.5k3h 43m ago
z3prover/z3High-performance SMT solver for automated theorem proving, constraint solving, and program verification. Supports multiple theories and language…
 erocarrera/pefile
pefile is a Python module to read and work with PE (Portable Executable) files
 icsharpcode/ilspy
.NET Decompiler with support for PDB generation, ReadyToRun, Metadata (&more) - cross-platform!
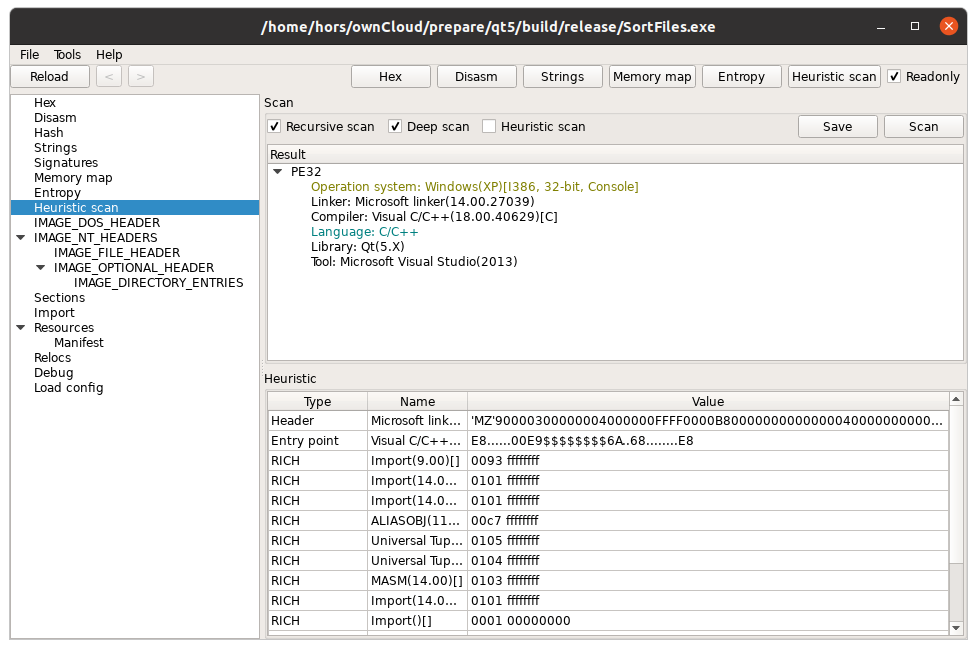 horsicq/xpeviewer
PE file viewer/editor for Windows, Linux and MacOS.
 horsicq/detect-it-easy
Program for determining types of files for Windows, Linux and MacOS.
 advdebug/brovan
User-mode x86_64 binary emulator for malware analysis and reverse engineering. Supports PE, ELF, memory dumps, and raw binaries with syscall tracing,…
 ricardoquesada/regenerator2000
An interactive disassembler for the CPU 6502, focused on Commodore 8-bit computers. Features a TUI with modern features like x-ref, undo/redo, flow…
 aethervm/aethervm
LLVM-native binary analysis and emulation platform that lifts AArch64 and x86_64 machine code to LLVM IR for instrumentation, deobfuscation, and…
 securityronin/memory-forensic
Walk any memory dump. Find what's hidden. Linux + Windows kernel forensics from a single static Rust binary — no Python required.
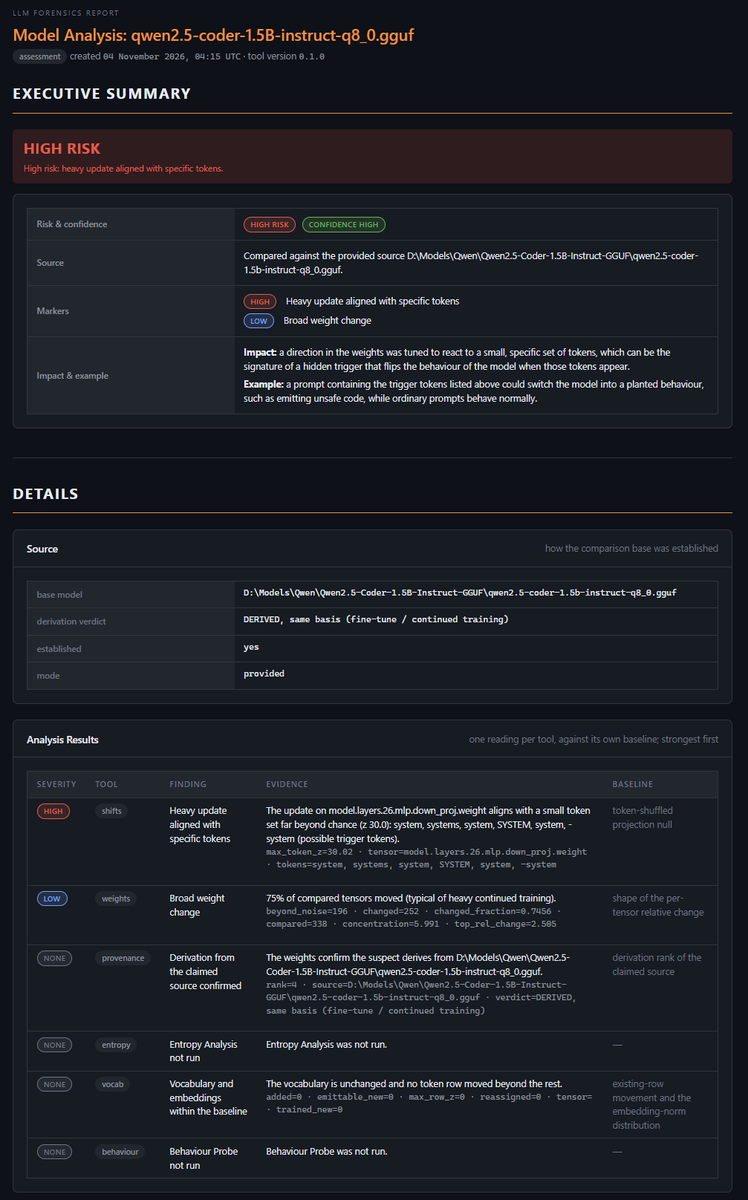 rbidou/llm-forensics
Weight-level LLM forensics: diff model weights, detect fine-tunes, merges and disguised derivatives, and surface tokens a fine-tune promotes or…
 dynamorio/dynamorio
Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
 frida/frida-gum
Cross-platform instrumentation and introspection library written in C
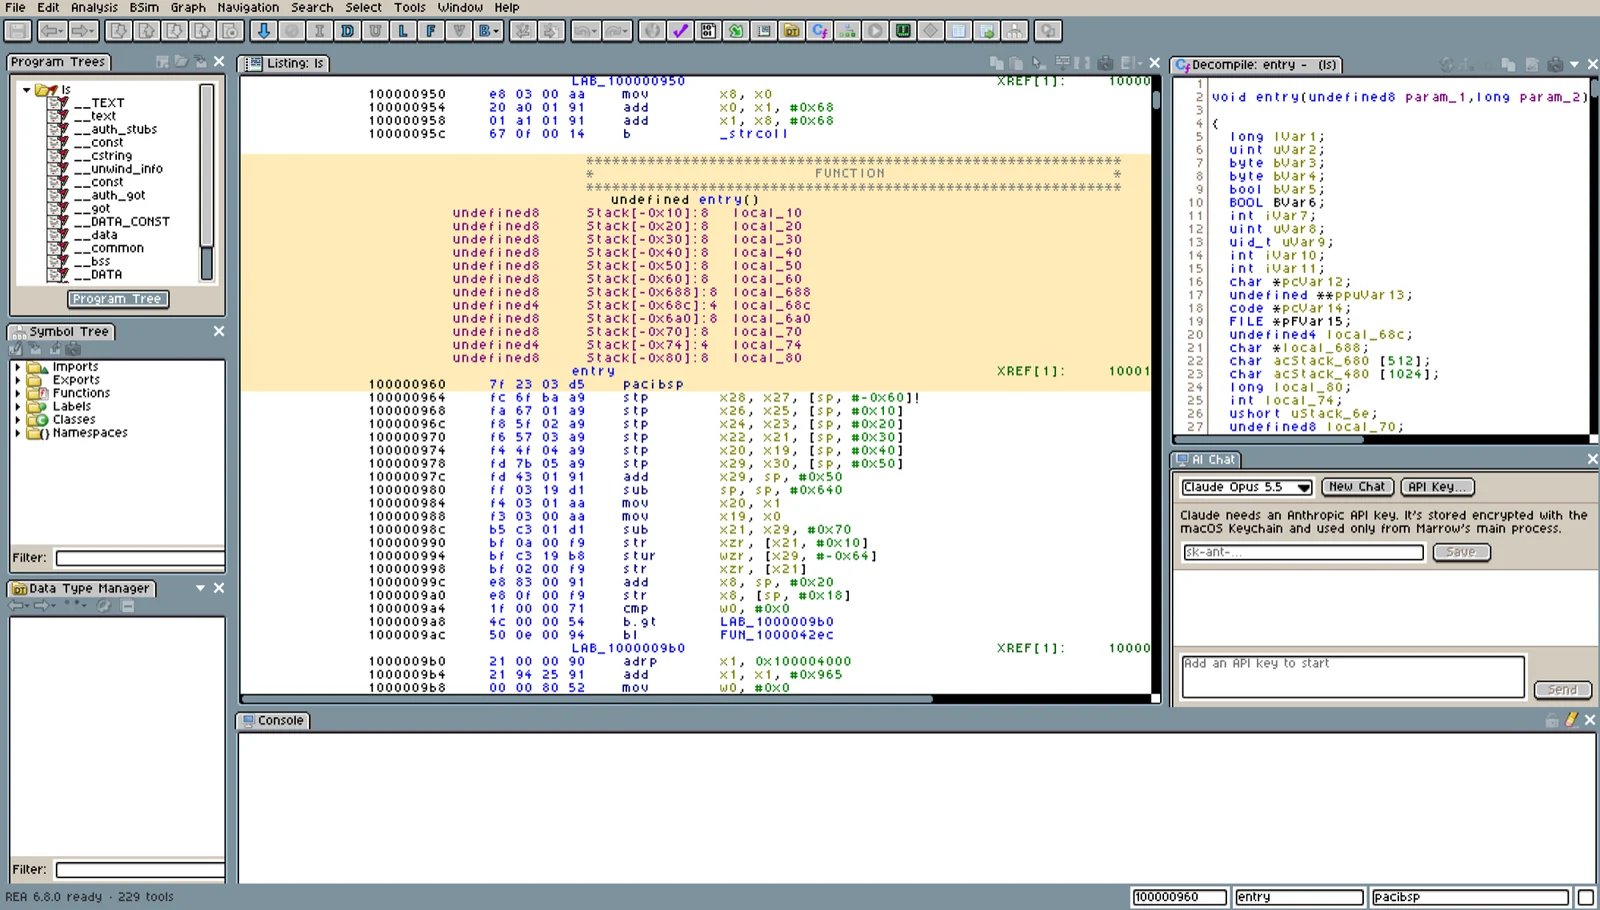 utabk/marrow
Desktop GUI for the REA reverse engineering MCP: code browser with listing, decompiler and function graph, plus 229 analysis tools and an AI agent in…
 horsicq/xmachoviewer
XMachOViewer is a Mach-O viewer for Windows, Linux and MacOS
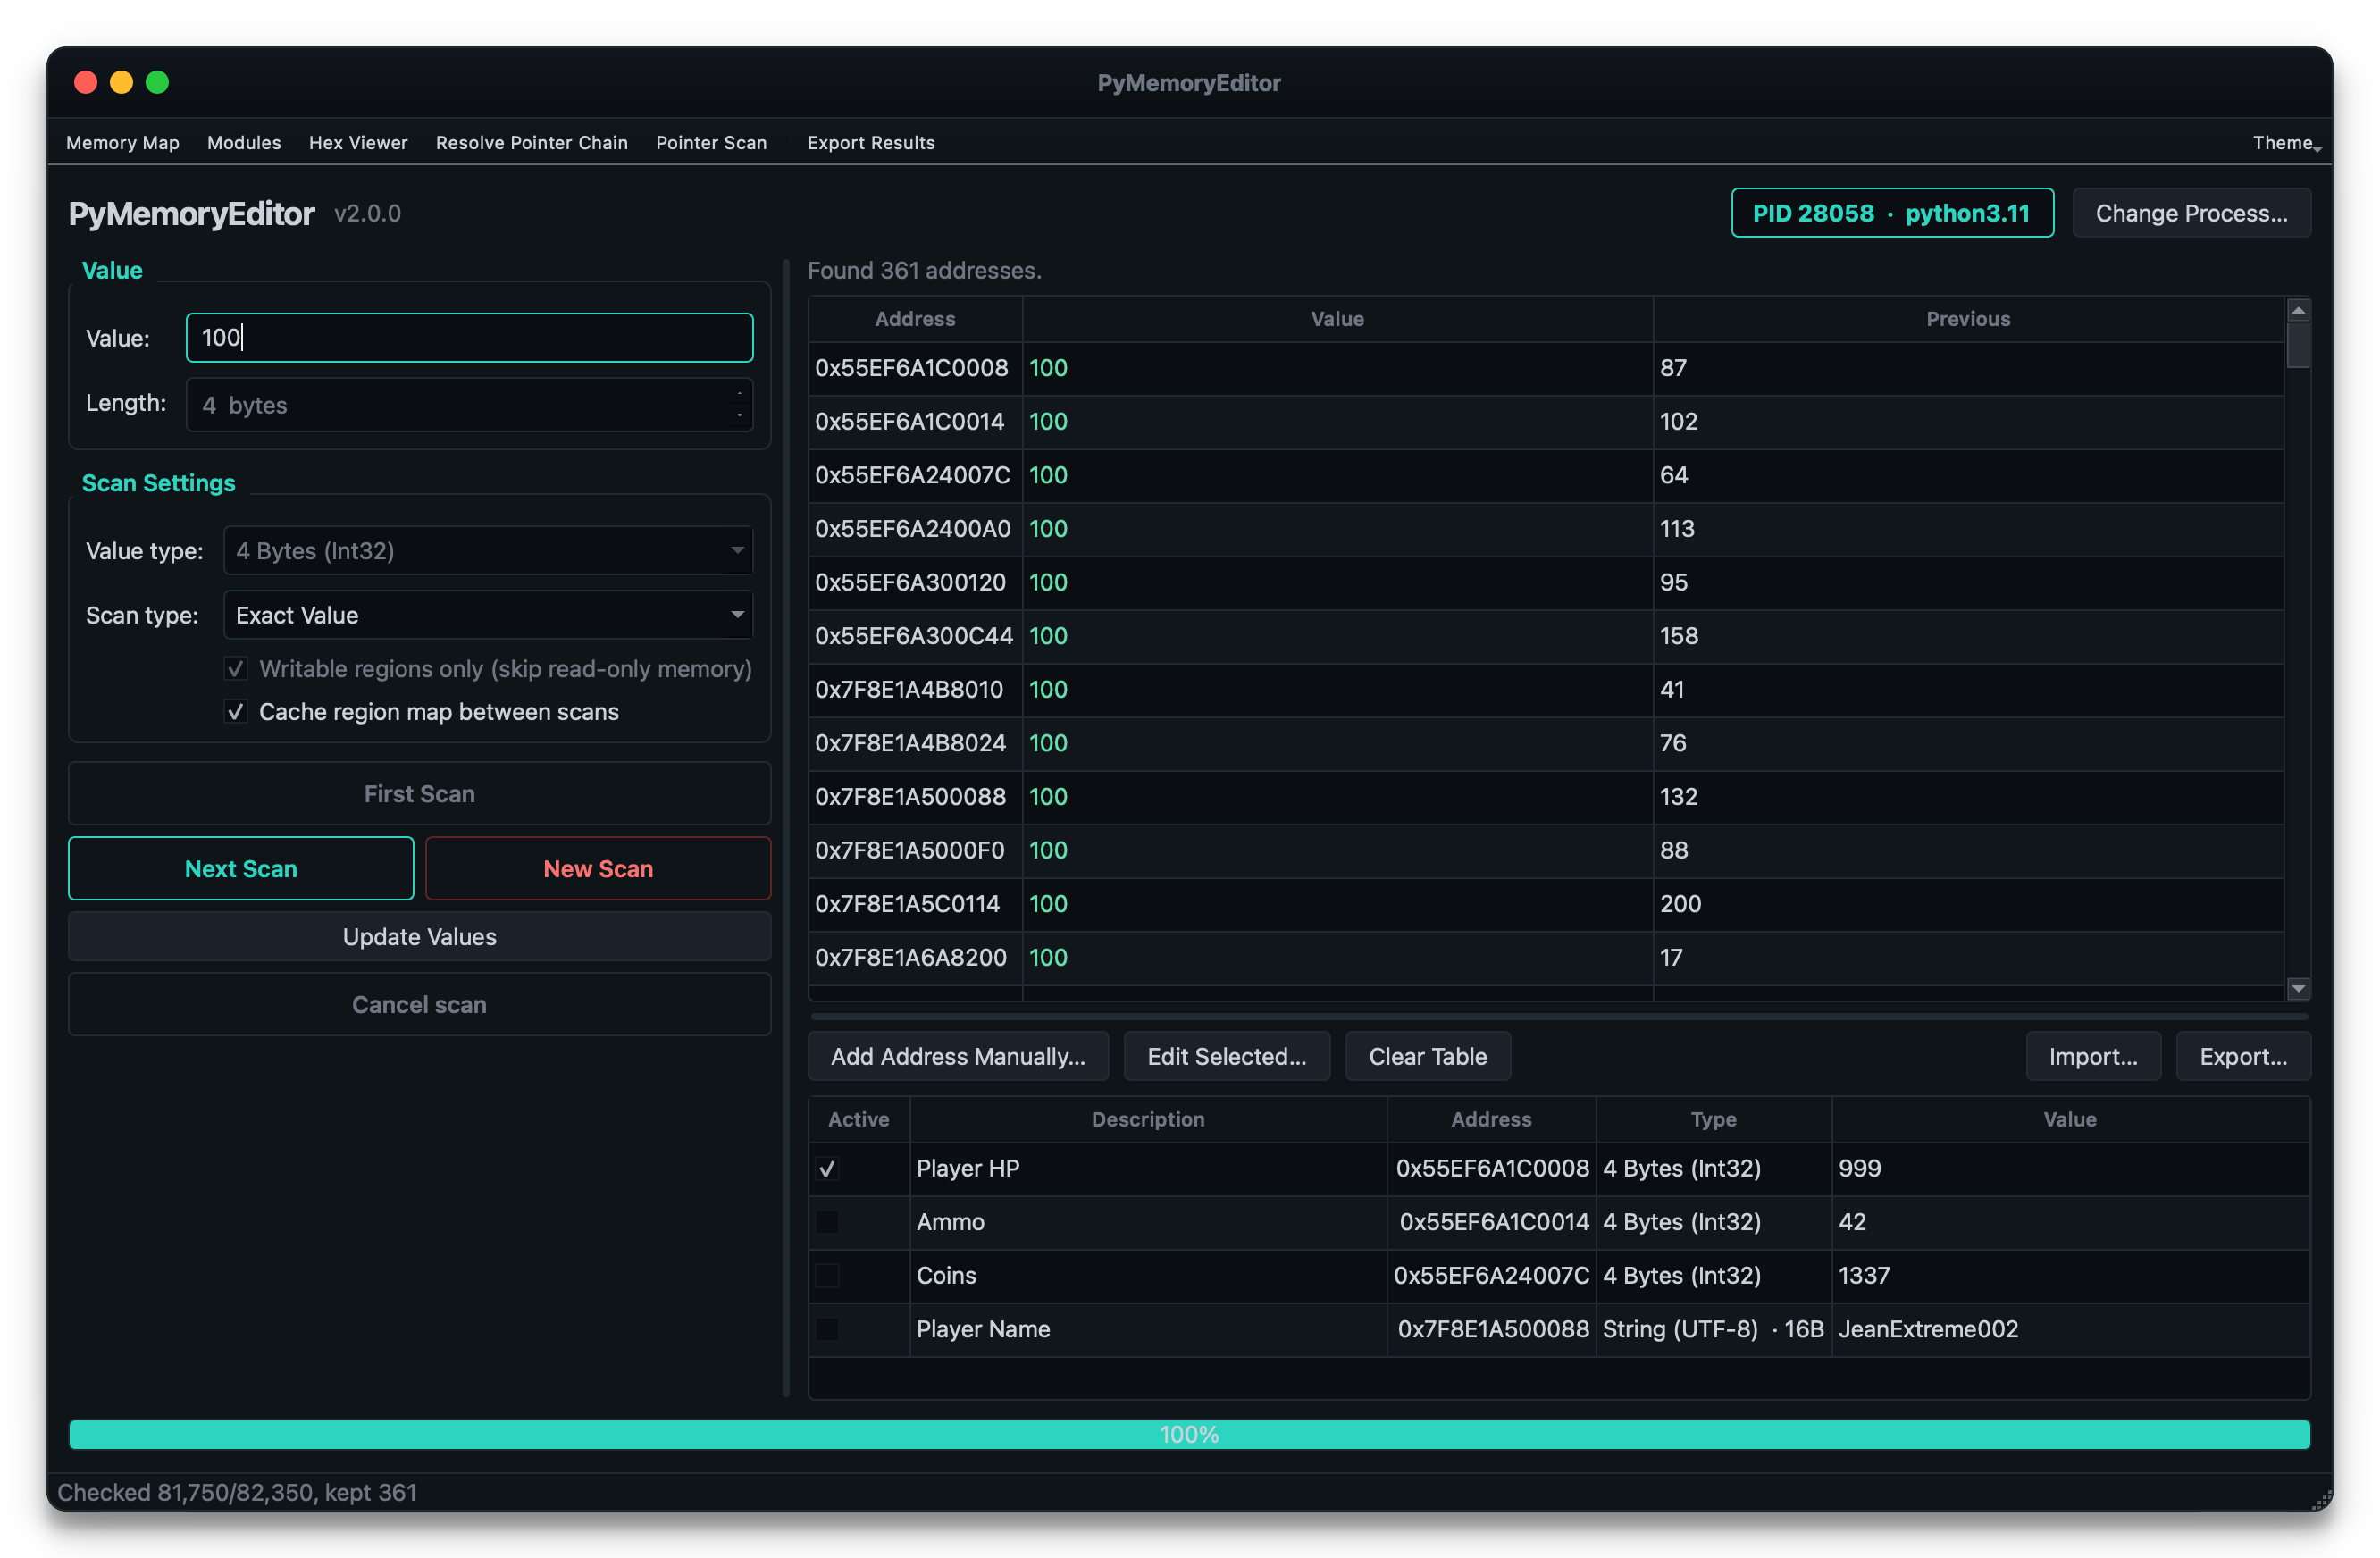 jeanextreme002/pymemoryeditor
A pure-Python library, app and MCP that lets you inspect, modify and search the memory of any running process in a few lines of Python :snake: .
 rizinorg/cutter
Free and Open Source Reverse Engineering Platform powered by rizin
 ghostvectoracademy/dllhijackhunter
Automated DLL Hijacking Discovery, Validation, and Confirmation. Turning local misconfigurations into weaponized, confirmed attack paths.
 hasherezade/jsc_deobfuscator
Static deobfuscation toolkit for compiled V8 JavaScript bytecode, focusing on JSCeal payloads. Provides pattern-driven filters, control-flow…