
Reverse-Engineering
 mytechnotalent/reverse-engineering
A FREE comprehensive reverse engineering tutorial covering x86, x64, 32-bit/64-bit ARM, 8-bit AVR and 32-bit RISC-V architectures.
binary-analysisctfdebuggers+5
14.3k
mytechnotalent/reverse-engineeringA FREE comprehensive reverse engineering tutorial covering x86, x64, 32-bit/64-bit ARM, 8-bit AVR and 32-bit RISC-V architectures.
 b2r2-org/b2r2
B2R2 is a fully managed binary analysis framework written in F#. It provides a rich set of algorithms, functions, and tools for reverse engineering,…
 we5ter/scanners-box
A powerful and open-source toolkit for hackers and security automation - 安全行业从业者自研开源扫描器合辑
 ghostvectoracademy/dllhijackhunter
Automated DLL Hijacking Discovery, Validation, and Confirmation. Turning local misconfigurations into weaponized, confirmed attack paths.
 z3prover/z3
High-performance SMT solver for automated theorem proving, constraint solving, and program verification. Supports multiple theories and language…
 horsicq/xmachoviewer
XMachOViewer is a Mach-O viewer for Windows, Linux and MacOS
 sjkim1127/reversecore_mcp
A security-first MCP server that empowers AI agents to perform automated reverse engineering, malware analysis, forensics, vulnerability research,…
 tjnel/certgraveyard_yara
Automated YARA rule generation from the Cert Central compromised certificate database.

 dynamorio/dynamorio
Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
 llnl/oghidra
OGhidra bridges Large Language Models (LLMs) via Ollama with the Ghidra reverse engineering platform, enabling AI-driven binary analysis through…
 nowsecure/r2frida
Radare2 and Frida better together.
 northpolesec/santa
A binary and file access authorization system for macOS.
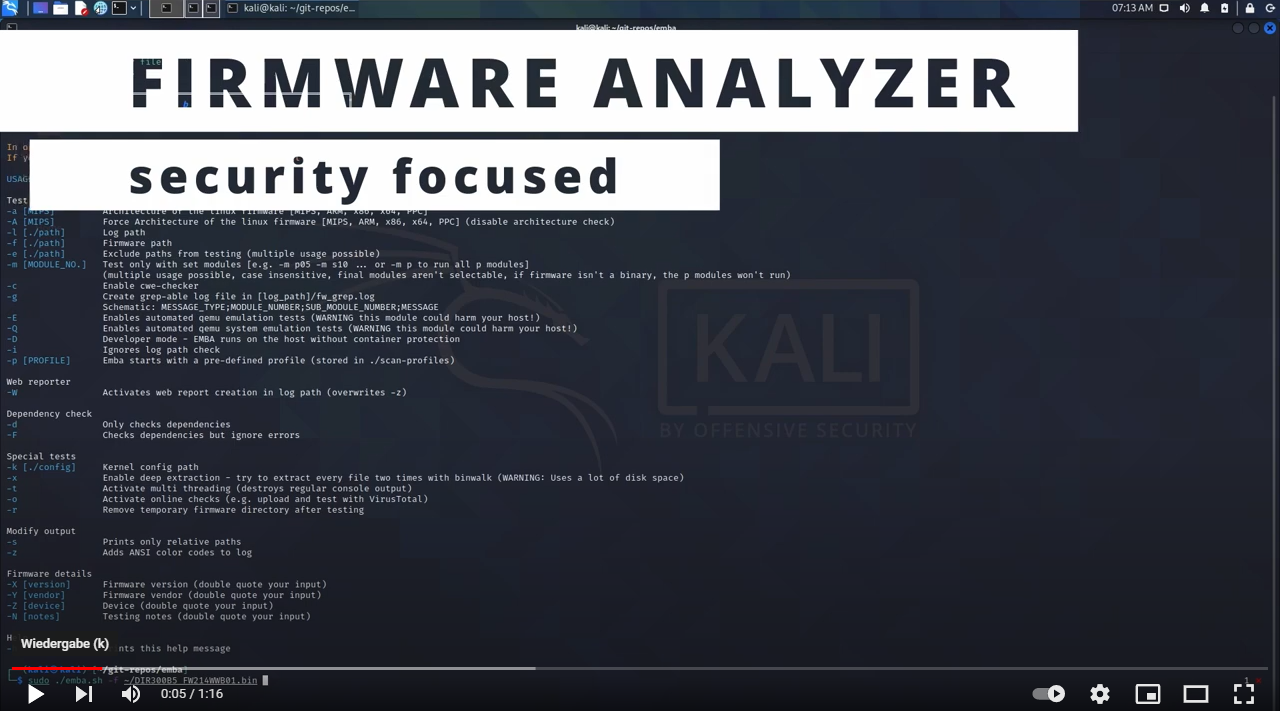 e-m-b-a/emba
EMBA - The firmware security analyzer
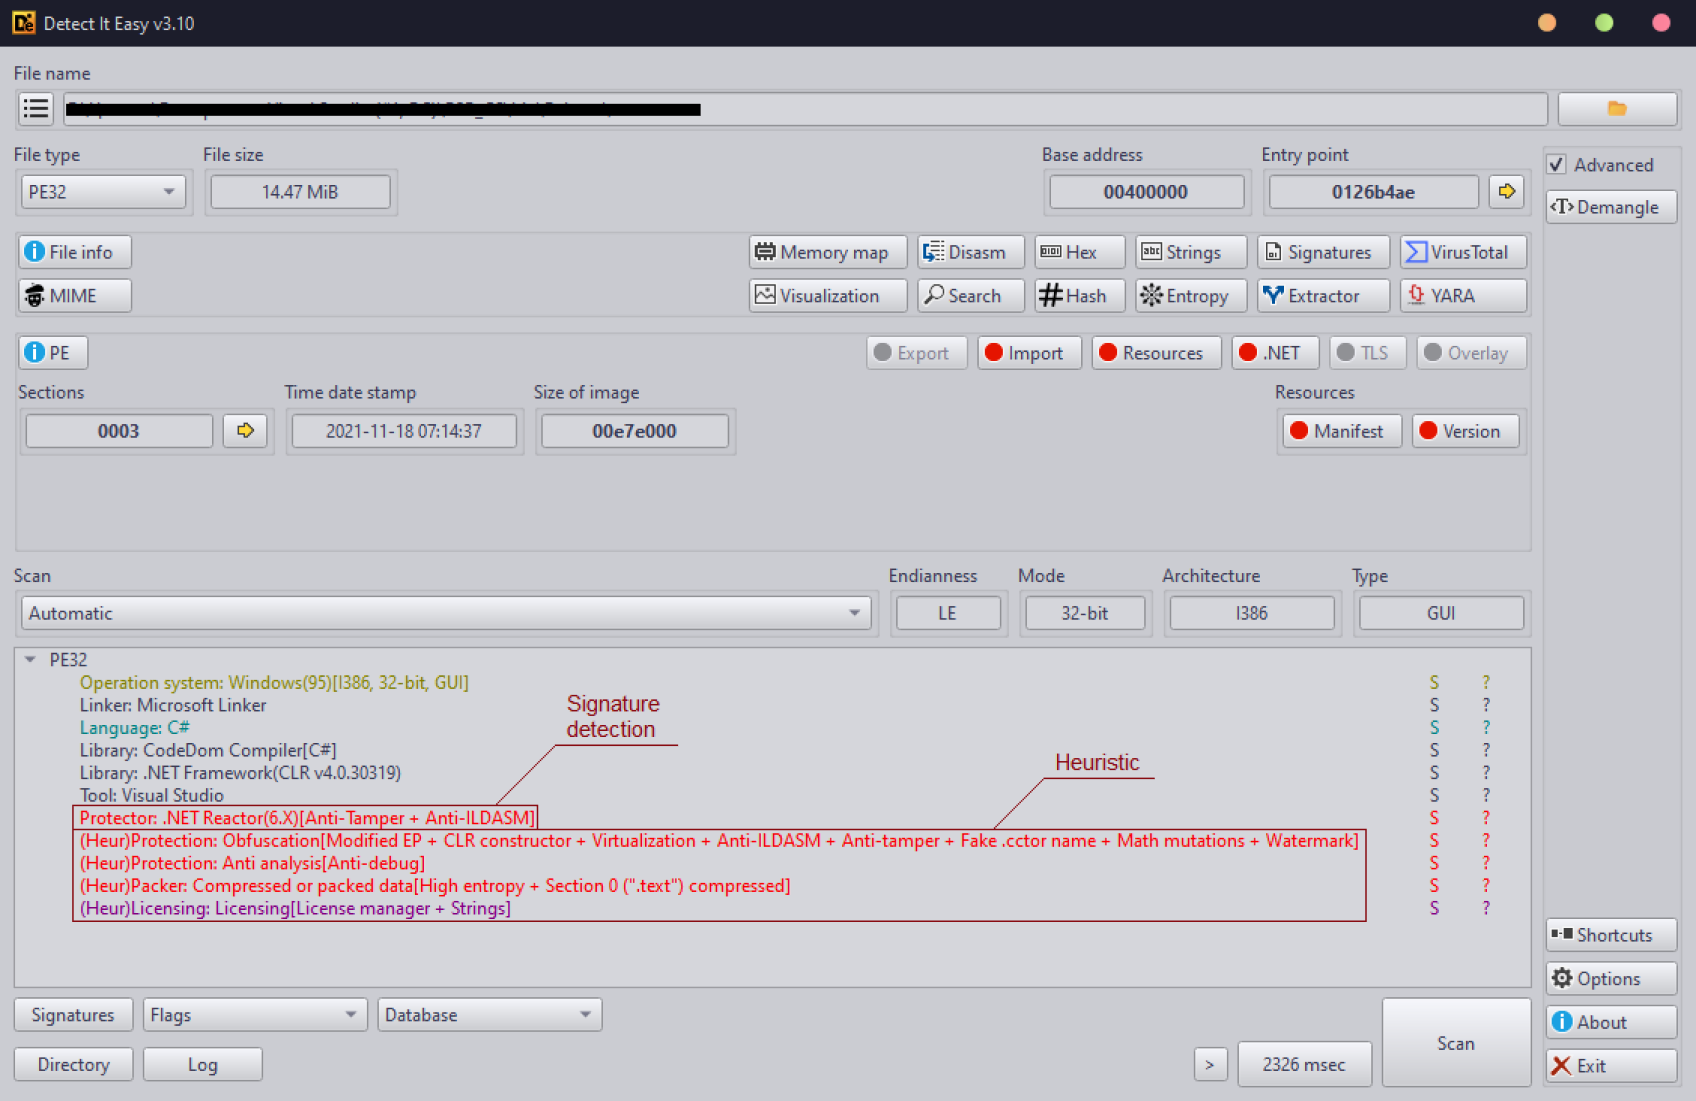 horsicq/detect-it-easy
Program for determining types of files for Windows, Linux and MacOS.
 gchq/cyberchef
The Cyber Swiss Army Knife - a web app for encryption, encoding, compression and data analysis
 frida/frida
Main repo for hosting release binaries