
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
22 results
binviz preview

binviz

GitHubkarankantaria/binviz

Binary visualiser and triage tool — entropy, byte-class and Hilbert surfaces, dot plots and control-flow graphs over one shared address-space model.
binary-analysiseducationforensics+4
8
1 month ago
msf_shellcode_analysis preview

msf_shellcode_analysis

GitHubyo-yo-yo-jbo/msf_shellcode_analysis

Static analysis walkthrough of a Metasploit Windows shellcode: PowerShell payload decoding, XOR obfuscation, PEB walking, and Export Address Table…
binary-analysiseducationmalware-analysis+3
292 months ago
ida-cli preview

ida-cli

GitHubcpkt9762/ida-cli

Headless IDA Pro MCP server for AI-assisted binary analysis, powered by idalib
ai-assisted-reversingbinary-analysisreverse-engineering
282 months ago
PSI_BOF preview

PSI_BOF

GitHubwhokilleddb/psi_bof

A BOF designed to inspect processes memory and addresses
binary-analysisdebuggersmemory-forensics+4
415 months ago
userland-exec preview

userland-exec

GitHubhardenedlinux/userland-exec

Userland exec PoC to be used as attack vector technique
binary-analysisexploitationids-ips-evasion+2
1465 months ago
page_table_walk preview

page_table_walk

GitHubjazho76/page_table_walk

Walk x86-64 page tables by hand in qemu and gdb. Decompose a virtual address, follow cr3 through all levels of physical memory, and extract a flag…
binary-analysisctfdebuggers+4
286 months ago
ret-sync preview

ret-sync

GitHubbootleg/ret-sync

ret-sync is a set of plugins that helps to synchronize a debugging session (WinDbg/GDB/LLDB/OllyDbg2/x64dbg) with IDA/Ghidra/Binary Ninja…

binary-analysisdebuggersdynamic-analysis-sandboxing+2
2.4k7 months ago
DarkWidow preview

DarkWidow

GitHubreveng007/darkwidow

Indirect Dynamic Syscall, SSN + Syscall address sorting via Modified TartarusGate approach + Remote Process Injection via APC Early Bird + Spawns a…

binary-analysiseducationexploitation+6
8108 months ago
Hunt-Sleeping-Beacons preview

Hunt-Sleeping-Beacons

GitHubtheflink/hunt-sleeping-beacons

Callstack scanner that identifies IOCs of unpacked or injected C2 agents by analyzing thread idle behavior, unbacked memory, module stomping, APCs,…
binary-analysisdefensive-toolsforensics+3
6818 months ago
moonwalk preview

moonwalk

GitHubteach2breach/moonwalk

find dll base addresses without PEB WALK
binary-analysiseducationpayload-development+2
1691 year ago
WhacAMole preview

WhacAMole

GitHubignacioj/whacamole

Live memory analysis detecting malware IOCs in processes, modules, handles, tokens, threads, .NET assemblies, memory address space and environment…
binary-analysisdebuggersdigital-forensics+9
442 years ago
DRMBinViaOrdinalImports preview

DRMBinViaOrdinalImports

GitHubmaldev-academy/drmbinviaordinalimports

Create Anti-Copy DRM Malware

adversarial-attackbinary-analysismalware-analysis+2
712 years ago
frameworks_base_android-6.0.1_r22_CVE-2023-20921 preview

frameworks_base_android-6.0.1_r22_CVE-2023-20921

GitHubtrinadh465/frameworks_base_android-6.0.1_r22_cve-2023-20921

Android framework base repository for Android 6.0.1 r22, modified to address CVE-2023-20921, providing a patched version for security analysis and…
android-securitybinary-analysisexploitation+2
2 years ago
lst2x64dbg preview

lst2x64dbg

GitHubutkonos/lst2x64dbg

Extract labels from IDA, Ghidra, Binary Ninja, and Relyze files and export x64dbg database. Including radare2 main address.
binary-analysisdebuggersreverse-engineering+1
1162 years ago
frameworks_base_AOSP-4.2.2_r1_CVE-2023-21272 preview

frameworks_base_AOSP-4.2.2_r1_CVE-2023-21272

GitHubtrinadh465/frameworks_base_aosp-4.2.2_r1_cve-2023-21272

Android framework base repository for AOSP 4.2.2_r1, modified to address CVE-2023-21272, a vulnerability in the Android framework.
android-securitybinary-analysisexploitation+2
3 years ago
Amsi-Killer preview

Amsi-Killer

GitHubzeromemoryex/amsi-killer

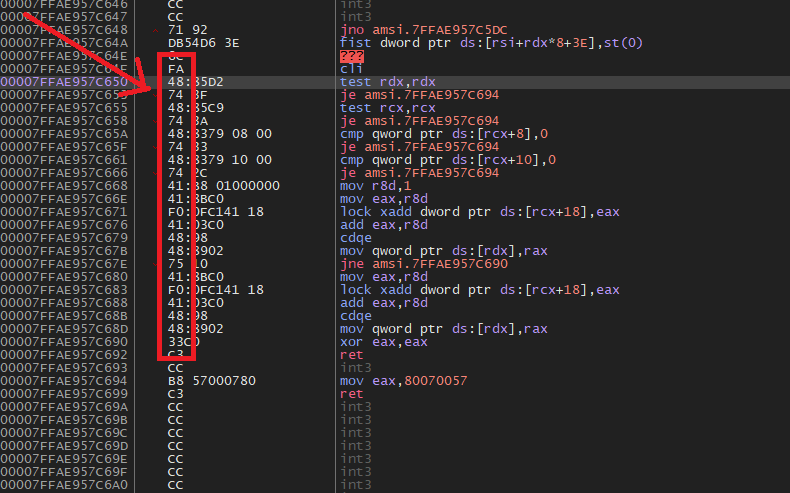
Lifetime AMSI bypass
adversarial-attackbinary-analysisred-teaming+1
6863 years ago
IATelligence preview

IATelligence

GitHubfr0gger/iatelligence

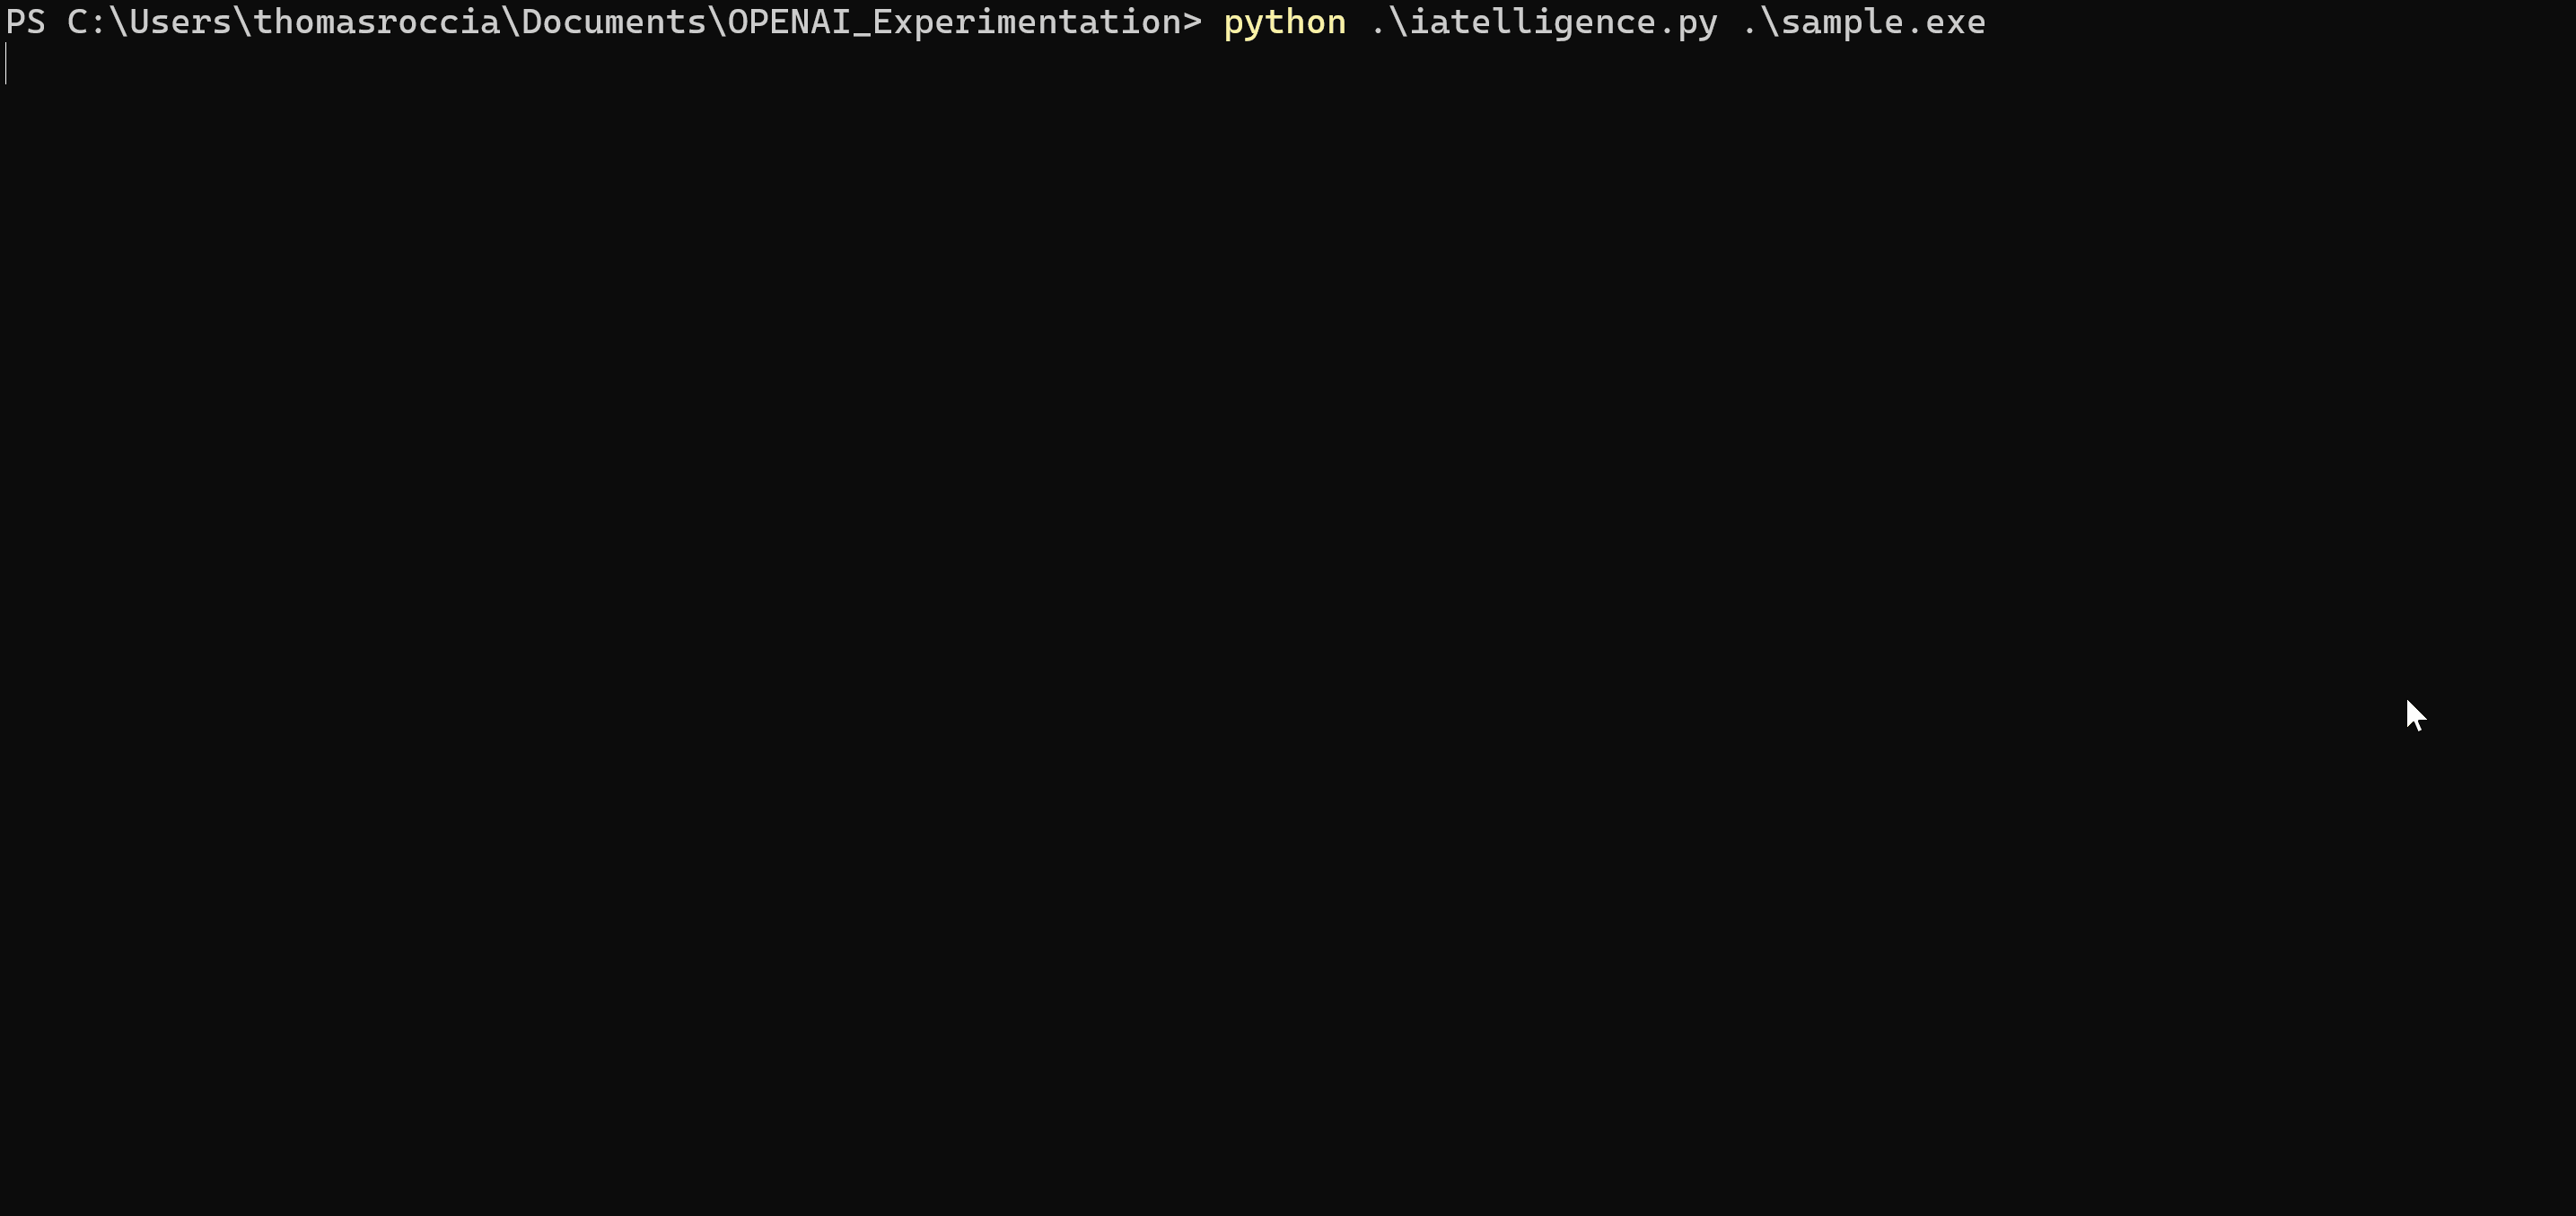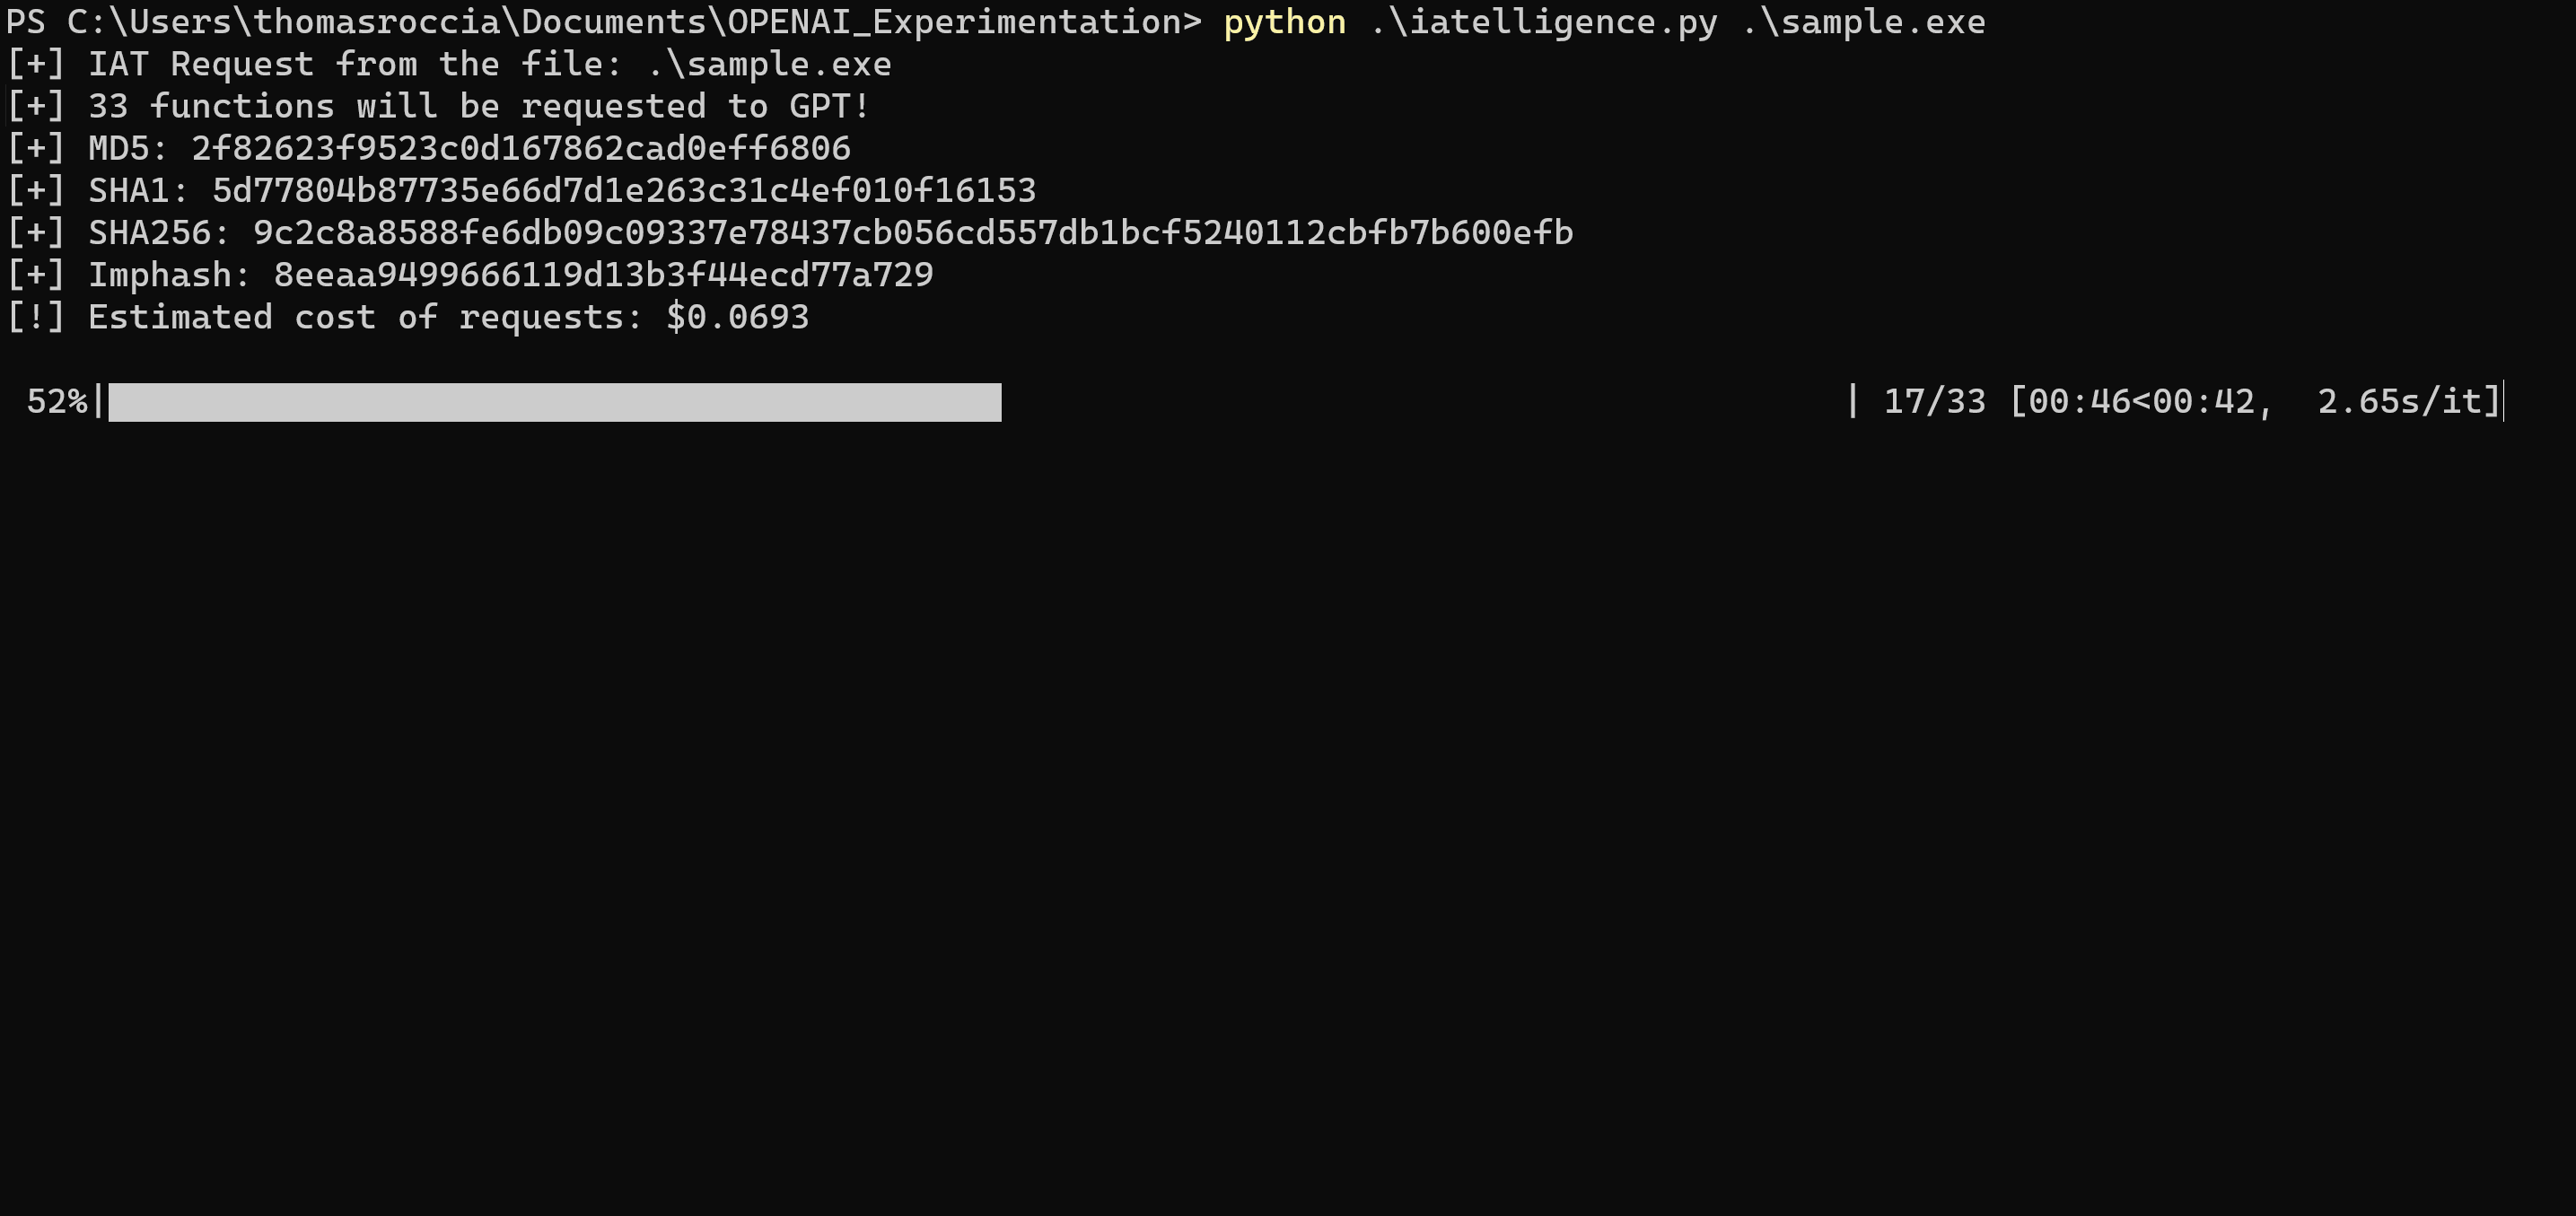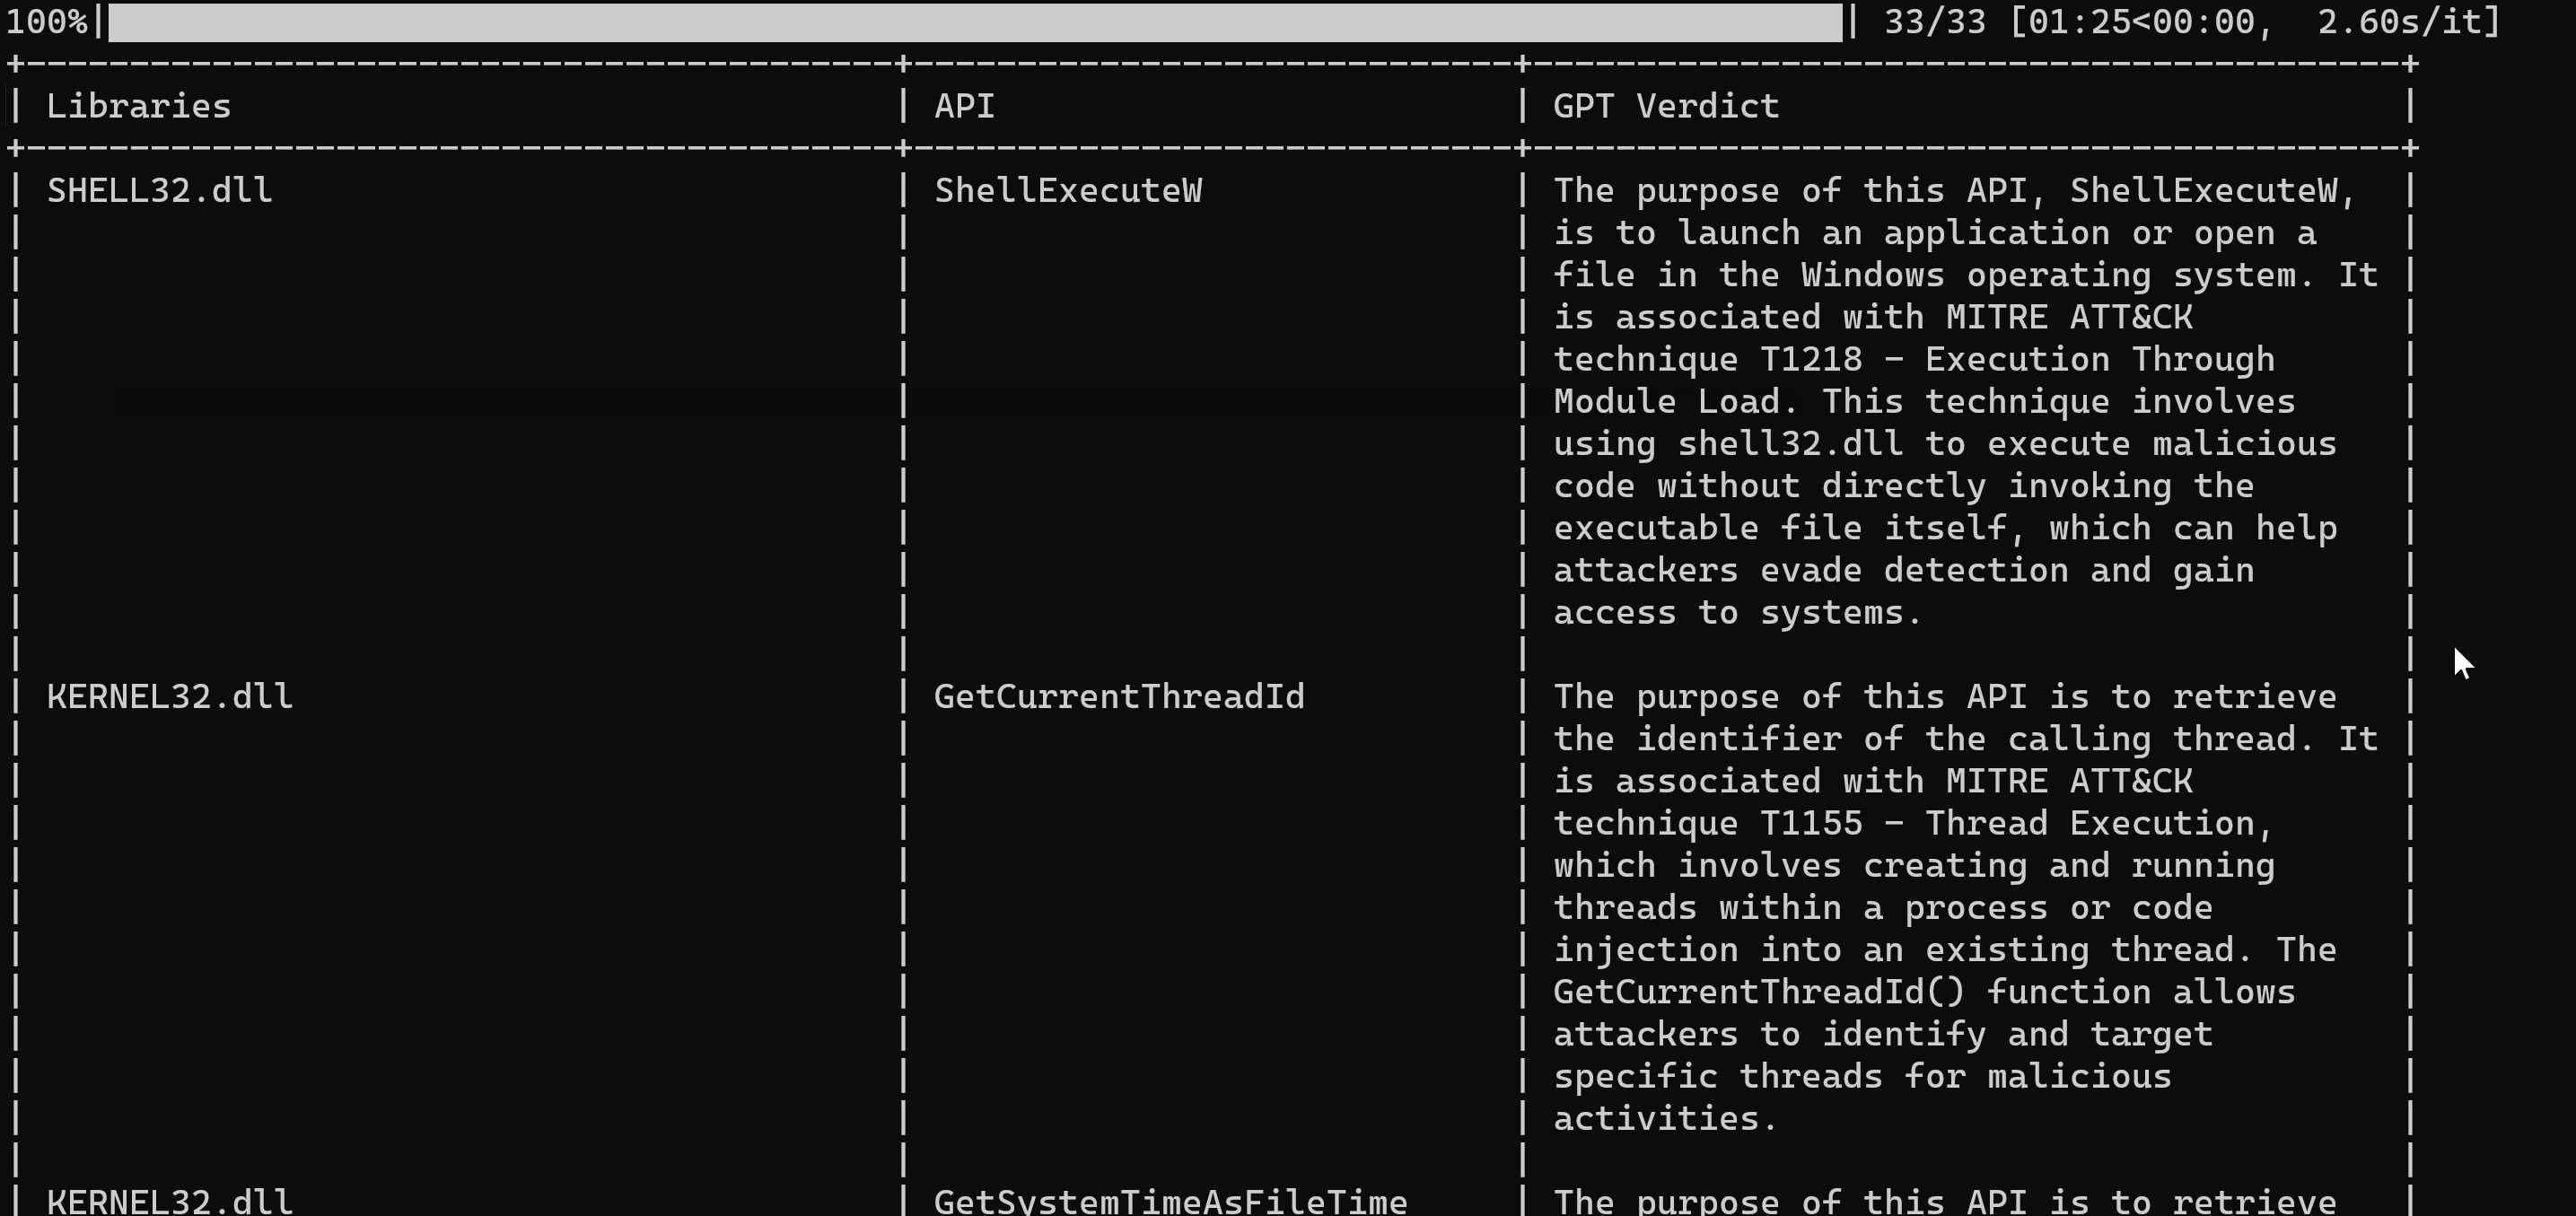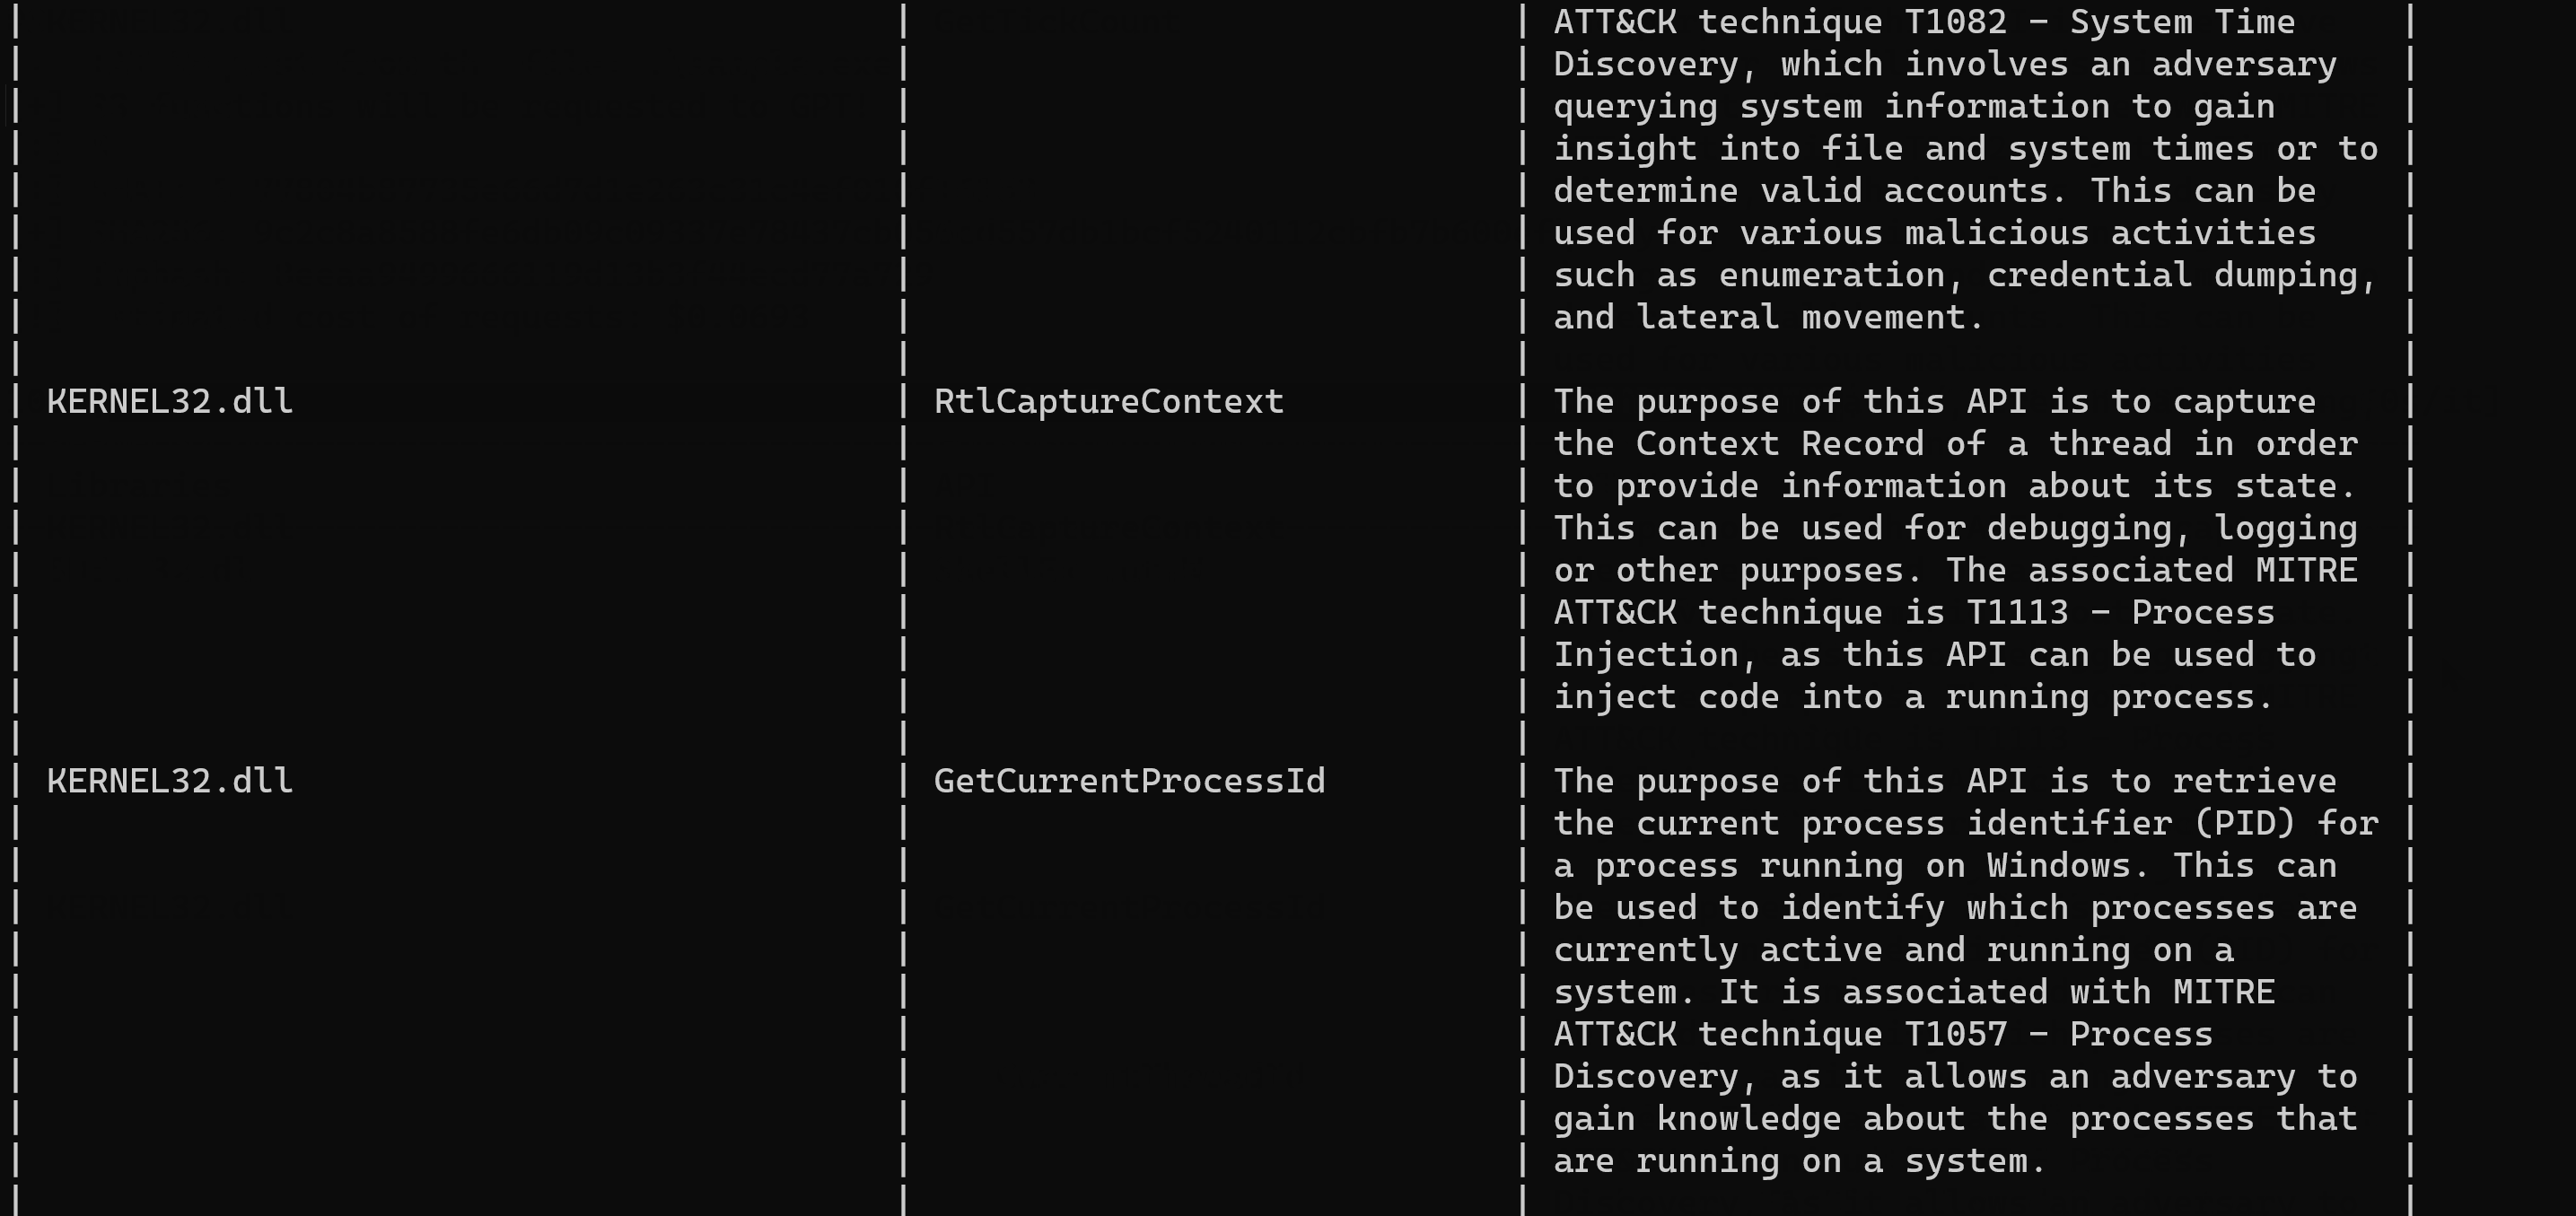
IATelligence is a Python script that will extract the IAT of a PE file and request GPT to get more information about the API and the ATT&CK matrix…

ai-assisted-reversingbinary-analysismalware-analysis+3
3853 years ago
Driver-HideKernelThread-IoCancelIrp preview

Driver-HideKernelThread-IoCancelIrp

GitHubgmh5225/driver-hidekernelthread-iocancelirp

Windows kernel driver technique that hides kernel threads by abusing IoCancelIrp and IRP cancel routines, with detection methods for identifying…

binary-analysisdefensive-toolsmalware-analysis+1
94 years ago
Previous12Next