
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
74 results
upx preview

upx

GitHubupx/upx

UPX - the Ultimate Packer for eXecutables

binary-analysisgeneral-purpose-utilitiesreverse-engineering
17.9k14h 5m ago
jadx preview

jadx

GitHubskylot/jadx

Command-line and GUI tool for decompiling Android Dex and APK files into readable Java source code, with resource decoding, deobfuscation, and Smali…
android-securitybinary-analysisdebuggers+5
50.7k1 day ago
windiff preview

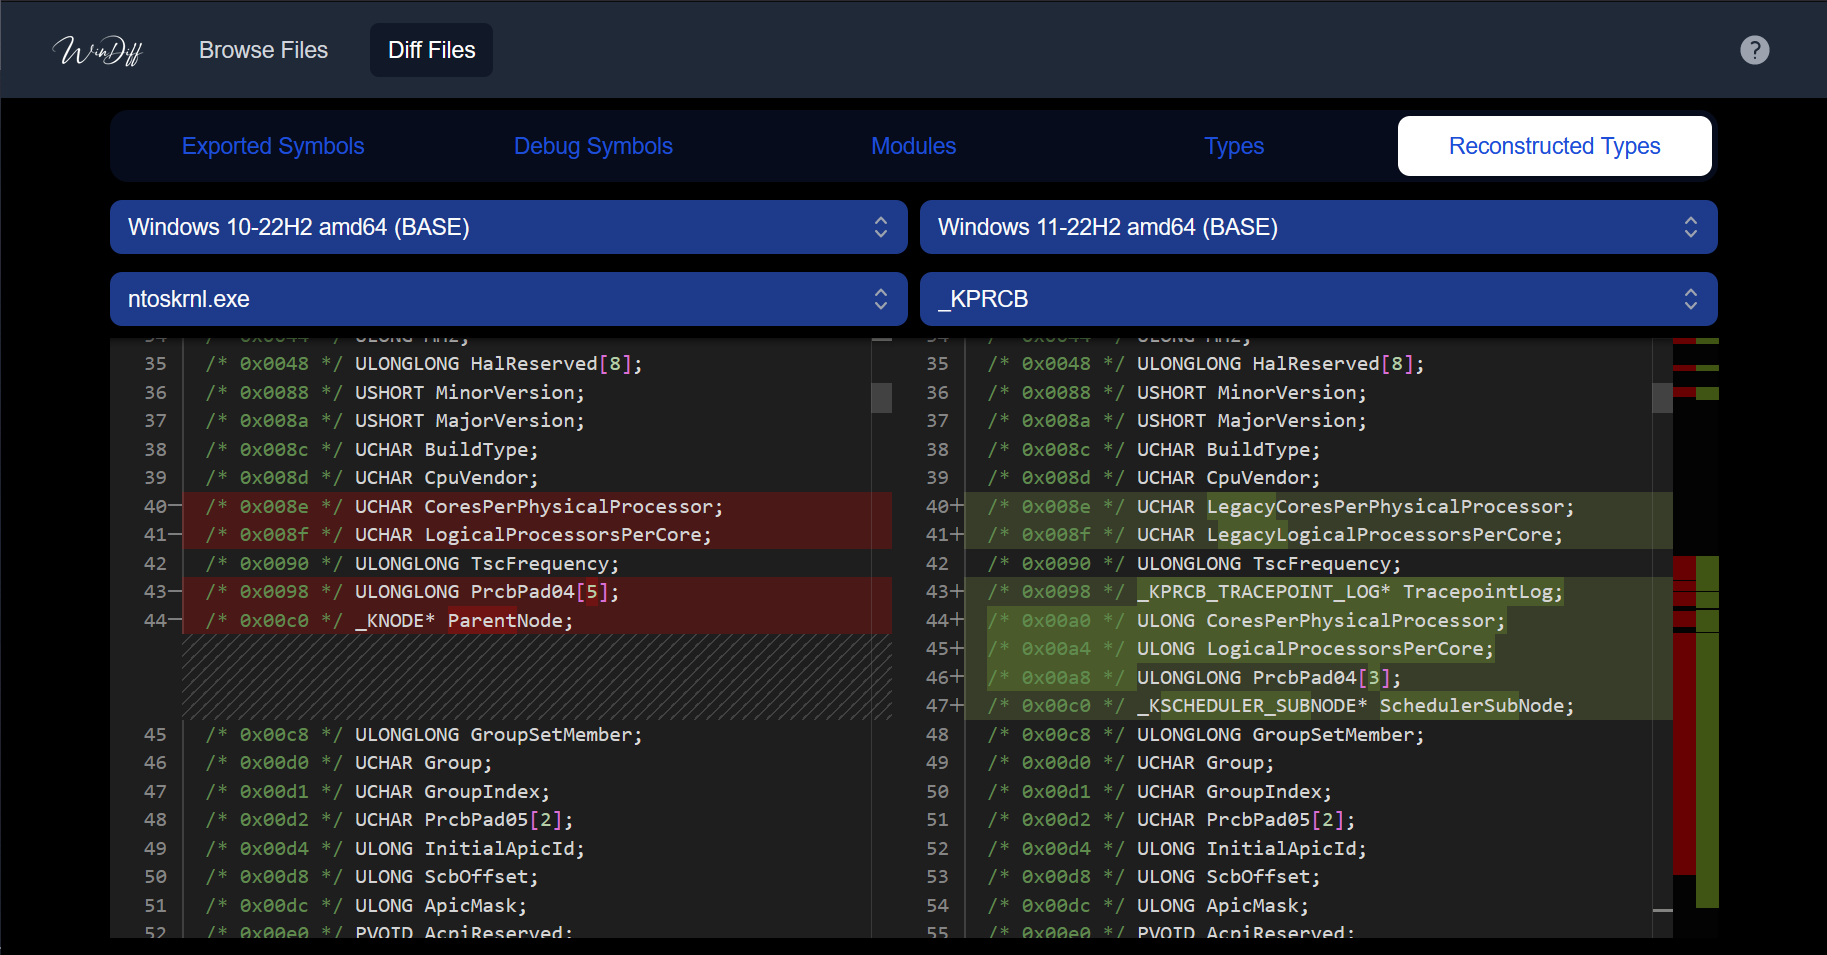
windiff

GitHubergrelet/windiff

Tool that allows comparing symbol, type and syscall information of Microsoft Windows binaries across different versions of the OS, using a Web UI…
binary-analysisinformation-gatheringreverse-engineering+1
3905 days ago
bindiff preview

bindiff

GitHubgoogle/bindiff

Quickly find differences and similarities in disassembled code

binary-analysiseducationfirmware-analysis+5
3.2k14 days ago
capa preview

capa

GitHubmandiant/capa

Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
ai-assisted-reversingbinary-analysiscode-analysis+10
6.2k24 days ago
Manalyze preview

Manalyze

GitHubjusticerage/manalyze

Static analyzer for PE executables with plugin-based detection of packers, compilers, suspicious imports, cryptographic constants, and ClamAV…

binary-analysismalware-analysisreverse-engineering+2
1.1k1 month ago
magic-extractor preview

magic-extractor

GitHubxchwarze/magic-extractor

Universal Windows extraction tool that detects unknown files and routes them to the right bundled extractor.
binary-analysisdata-recoverydigital-forensics+8
431 month ago
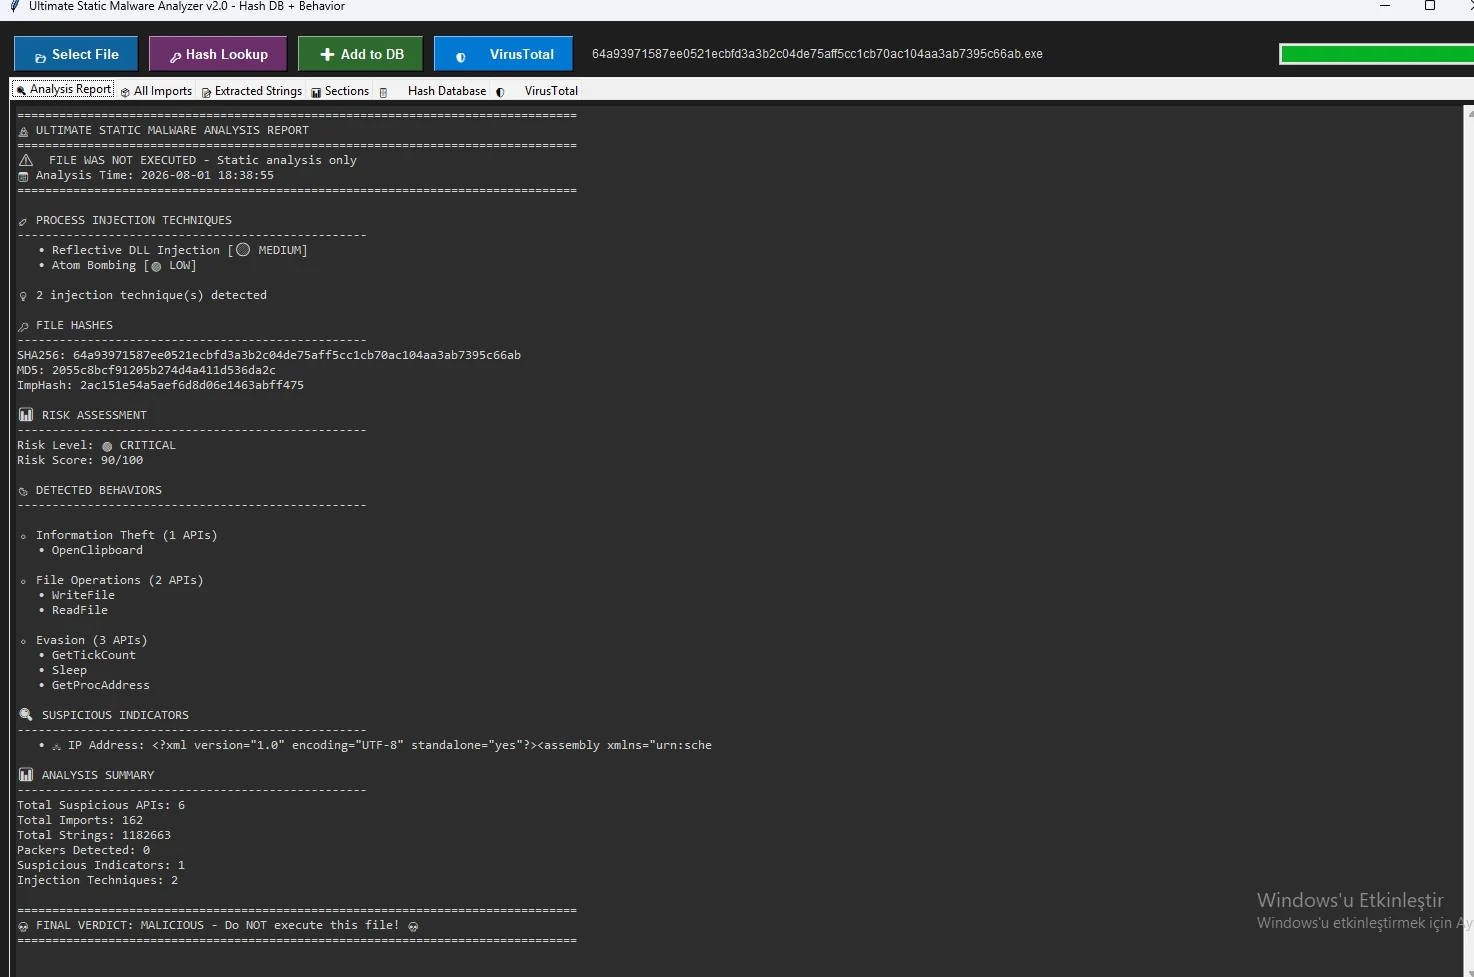
MalwareForge---Advanced-Static-Malware-Analyzer preview

MalwareForge---Advanced-Static-Malware-Analyzer

GitHubkaandemir993/malwareforge---advanced-static-malware-analyzer

Advanced Static malware analyzer that reveals 8 injection techniques, critical API calls, hidden strings, exports PE sections (.text, .rdata) as…

binary-analysishash-analysismalware-analysis+2
41 month ago
keystone preview

keystone

GitHubkeystone-engine/keystone

Multi-architecture assembler framework that converts assembly source into machine code for Arm, x86, MIPS, PowerPC, RISC-V, and more, with a…
binary-analysisbinary-exploitationgeneral-purpose-utilities+4
2.6k2 months ago
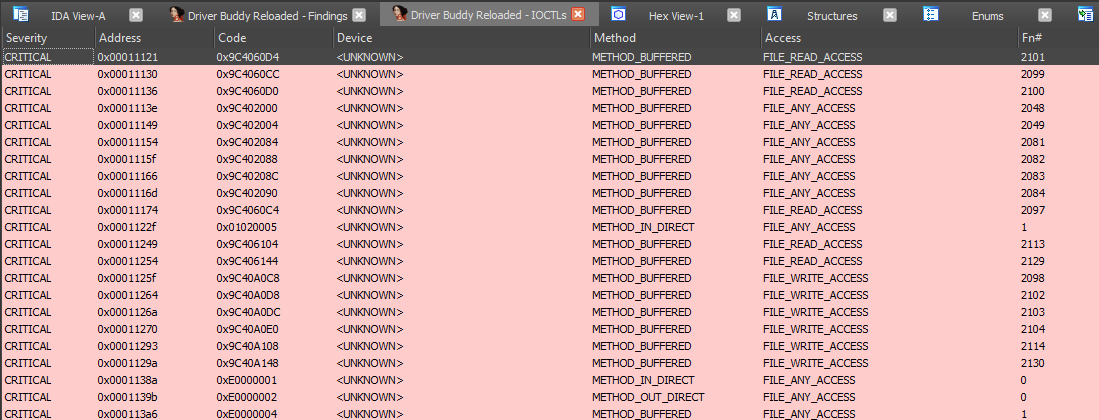
DriverBuddyReloaded preview

DriverBuddyReloaded

GitHubvoidsec/driverbuddyreloaded

Driver Buddy Reloaded is an IDA Pro Python plugin that helps automate some tedious Windows Kernel Drivers reverse engineering tasks

binary-analysisdebuggersreverse-engineering+2
4672 months ago
aether preview

aether

GitHub0xsp-srd/aether

Windows memory-forensics and threat hunting tool that scans live process memory for malicious patterns, injection techniques, and reflectively loaded…
binary-analysiscommand-and-controldigital-forensics+7
672 months ago
manticore preview
Archived

manticore

GitHubtrailofbits/manticore

Symbolic execution tool
binary-analysisdynamic-analysis-sandboxingeducation+3
3.9k3 months ago
ioctlance preview

ioctlance

GitHubzeze-zeze/ioctlance

A tool that is used to hunt vulnerabilities in x64 WDM drivers

binary-analysisdynamic-analysis-sandboxingexploit-frameworks+4
4733 months ago
Darkcloak preview

Darkcloak

GitHub0x574r/darkcloak

Linux process identity cloaking tool that spoofs comm, argv, cmdline, environ, exe path, and VMAs via an 11-phase prctl pipeline to impersonate…
binary-analysisfingerprint-spoofingids-ips-evasion+6
123 months ago
pe-sieve preview

pe-sieve

GitHubhasherezade/pe-sieve

Scans a given process. Recognizes and dumps a variety of potentially malicious implants (replaced/injected PEs, shellcodes, hooks, in-memory patches).
binary-analysisforensicsmalware-analysis+2
3.9k3 months ago
TS_LLMLib preview

TS_LLMLib

GitHubtrustedsec/ts_llmlib

Python library for local LLM-powered security analysis with Ghidra binary analysis, C/C++ vulnerability scanning, and MCP tool integration for…
ai-securitybinary-analysiscode-analysis+7
14 months ago
zkar preview

zkar

GitHubphith0n/zkar

Go-based Java serialization protocol analyzer that parses, dumps, and generates deserialization payloads with ysoserial gadget support and a library…

binary-analysisexploitationpayload-generation+1
6535 months ago
EDRs preview

EDRs

GitHubmr-un1k0d3r/edrs

Red team tool for EDR evasion: dynamically resolves syscall IDs, patches ntdll stubs, unhooks IAT hooks, and lists hooked APIs from major EDR vendors.

binary-analysiscurated-resourcesids-ips-evasion+3
2.2k6 months ago
Previous12345Next