

dynamorio
 dynamorio/dynamorio
Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
binary-analysiscode-analysisdebuggers+3
3.2k
dynamorio/dynamorioRuntime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
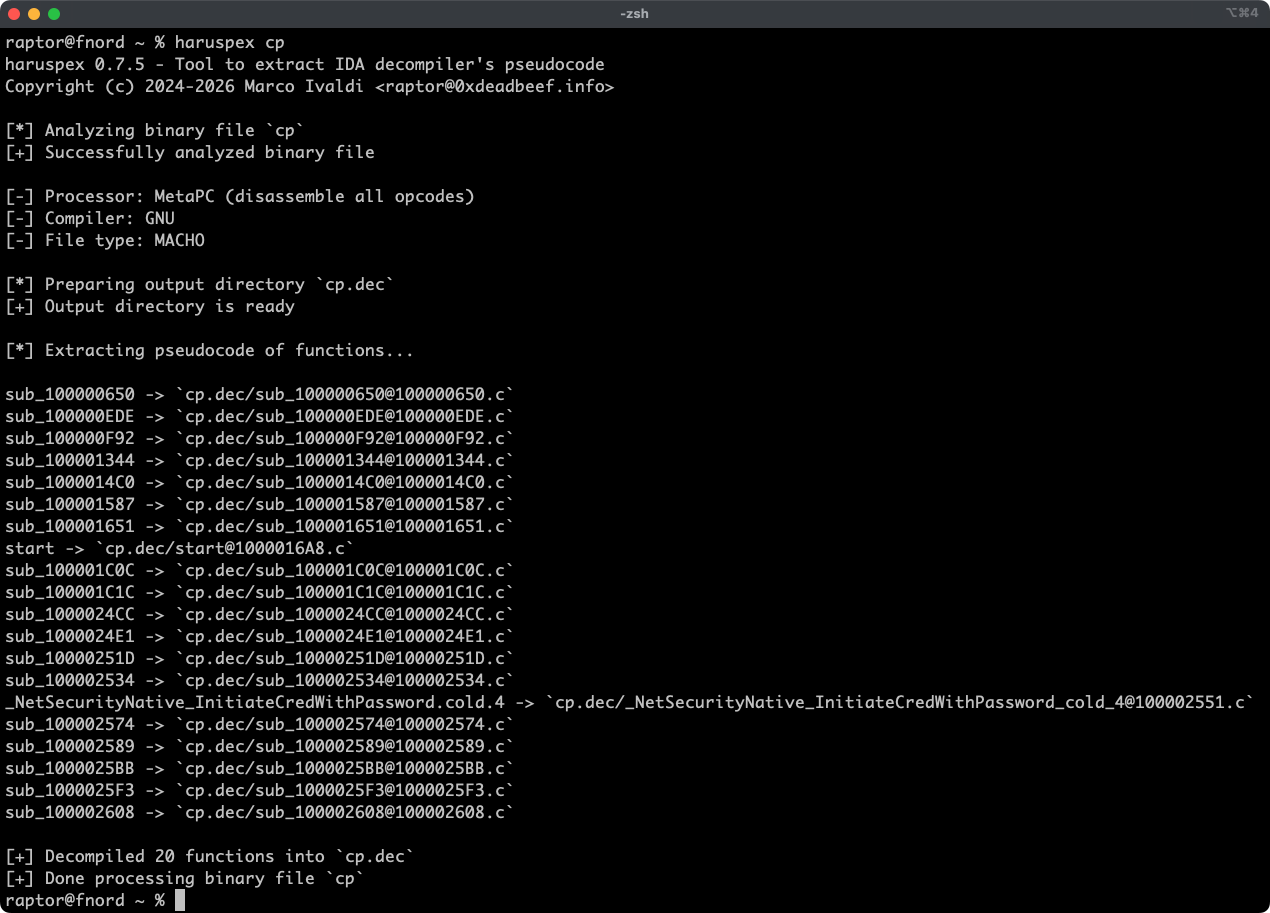 0xdea/haruspex
Vulnerability research assistant that extracts pseudocode from the IDA Hex-Rays decompiler.
 skylot/jadx
Command-line and GUI tool for decompiling Android Dex and APK files into readable Java source code, with resource decoding, deobfuscation, and Smali…
 atomdrift-project/scan
0-day malware detection for binaries, source & scripts (that doesn't suck)
 mandiant/speakeasy
Windows malware emulation framework that executes binaries, drivers, and shellcode in a modeled runtime, emulating APIs, process/thread behavior,…
 nowsecure/r2frida
Radare2 and Frida better together.
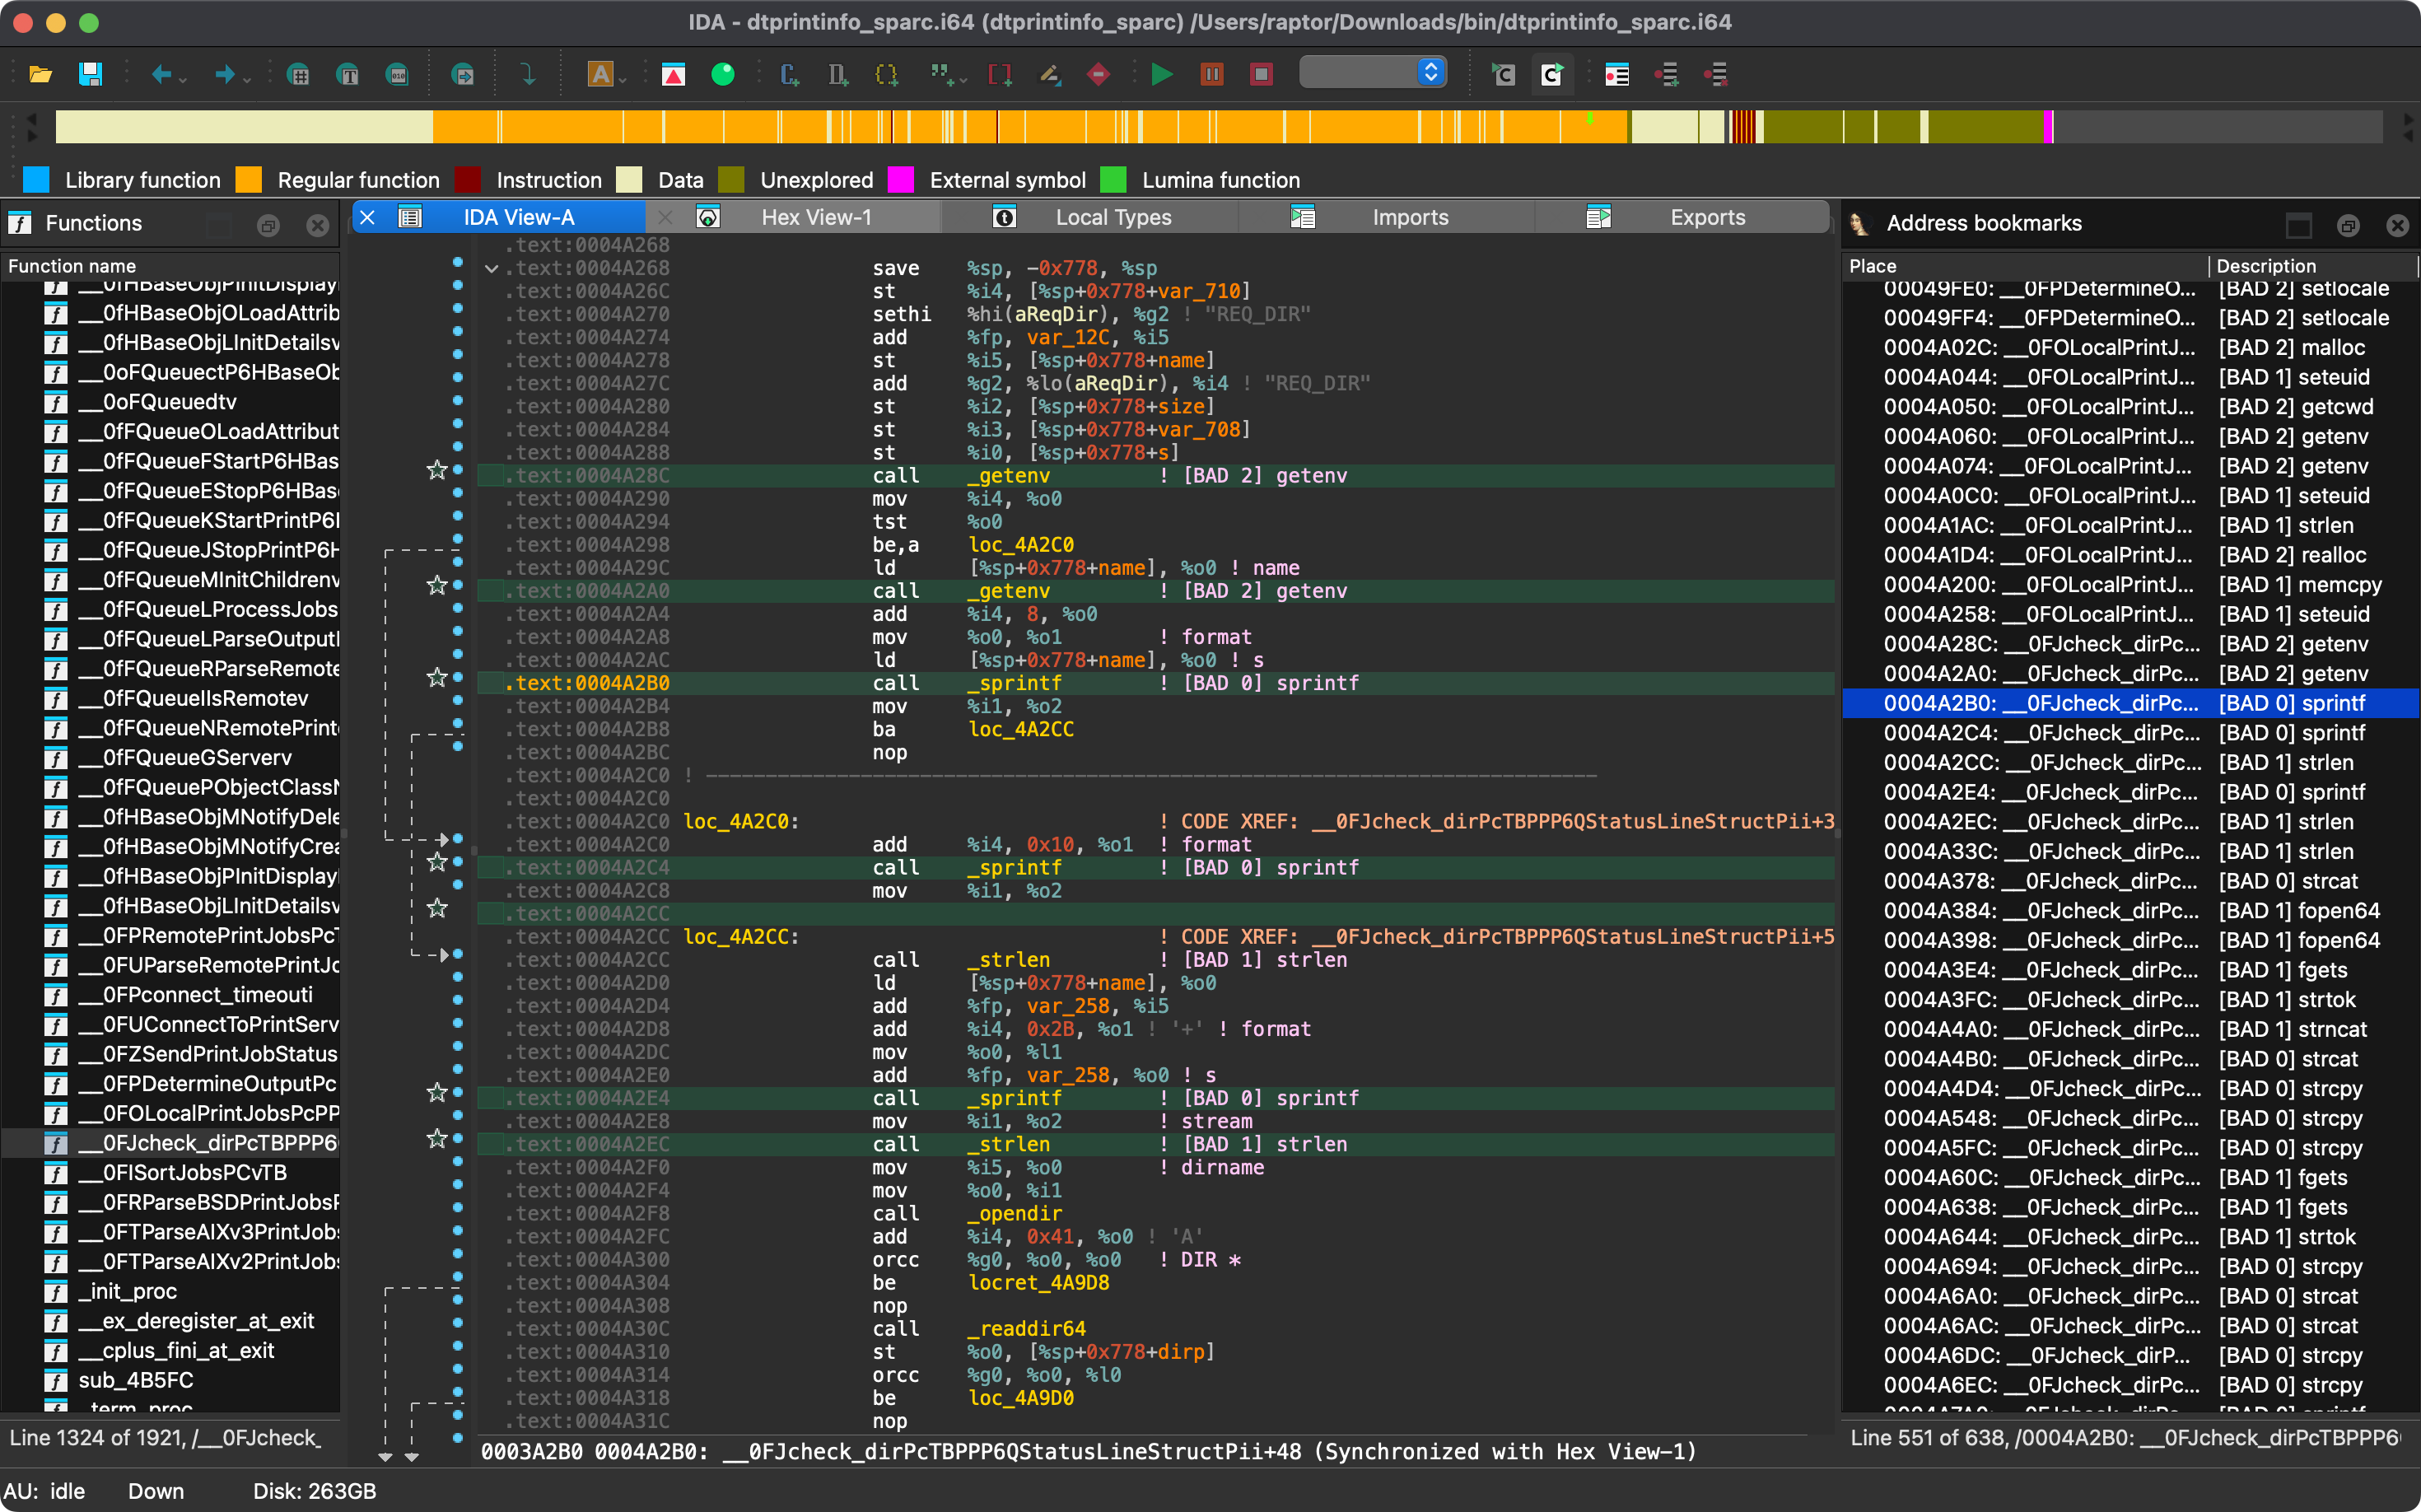 0xdea/rhabdomancer
Vulnerability research assistant that locates calls to potentially insecure API functions in a binary file.
 mg1937/asc
Fast Android APK decompiler front-end that queries compiled DEX artifacts directly, extracting classes and cross-references in milliseconds without…
 416rehman/deepzero
Find zero-days while you sleep. DeepZero is an automated vulnerability research framework that parses, decompiles, and analyzes thousands of Windows…
 mandiant/capa
Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
 aethervm/aethervm
LLVM-native binary analysis and emulation platform that lifts AArch64 and x86_64 machine code to LLVM IR for instrumentation, deobfuscation, and…
 1llu50ry/mcp-reverse
MCP server exposing 180+ reverse-engineering tools that aggregate Ghidra, IDA, x64dbg, Frida and 56 other backends with native binary parsers and a…
 google/silifuzz
Fuzzes CPU implementations by generating test inputs from software proxies, then executes them on real hardware to detect microarchitecture defects…
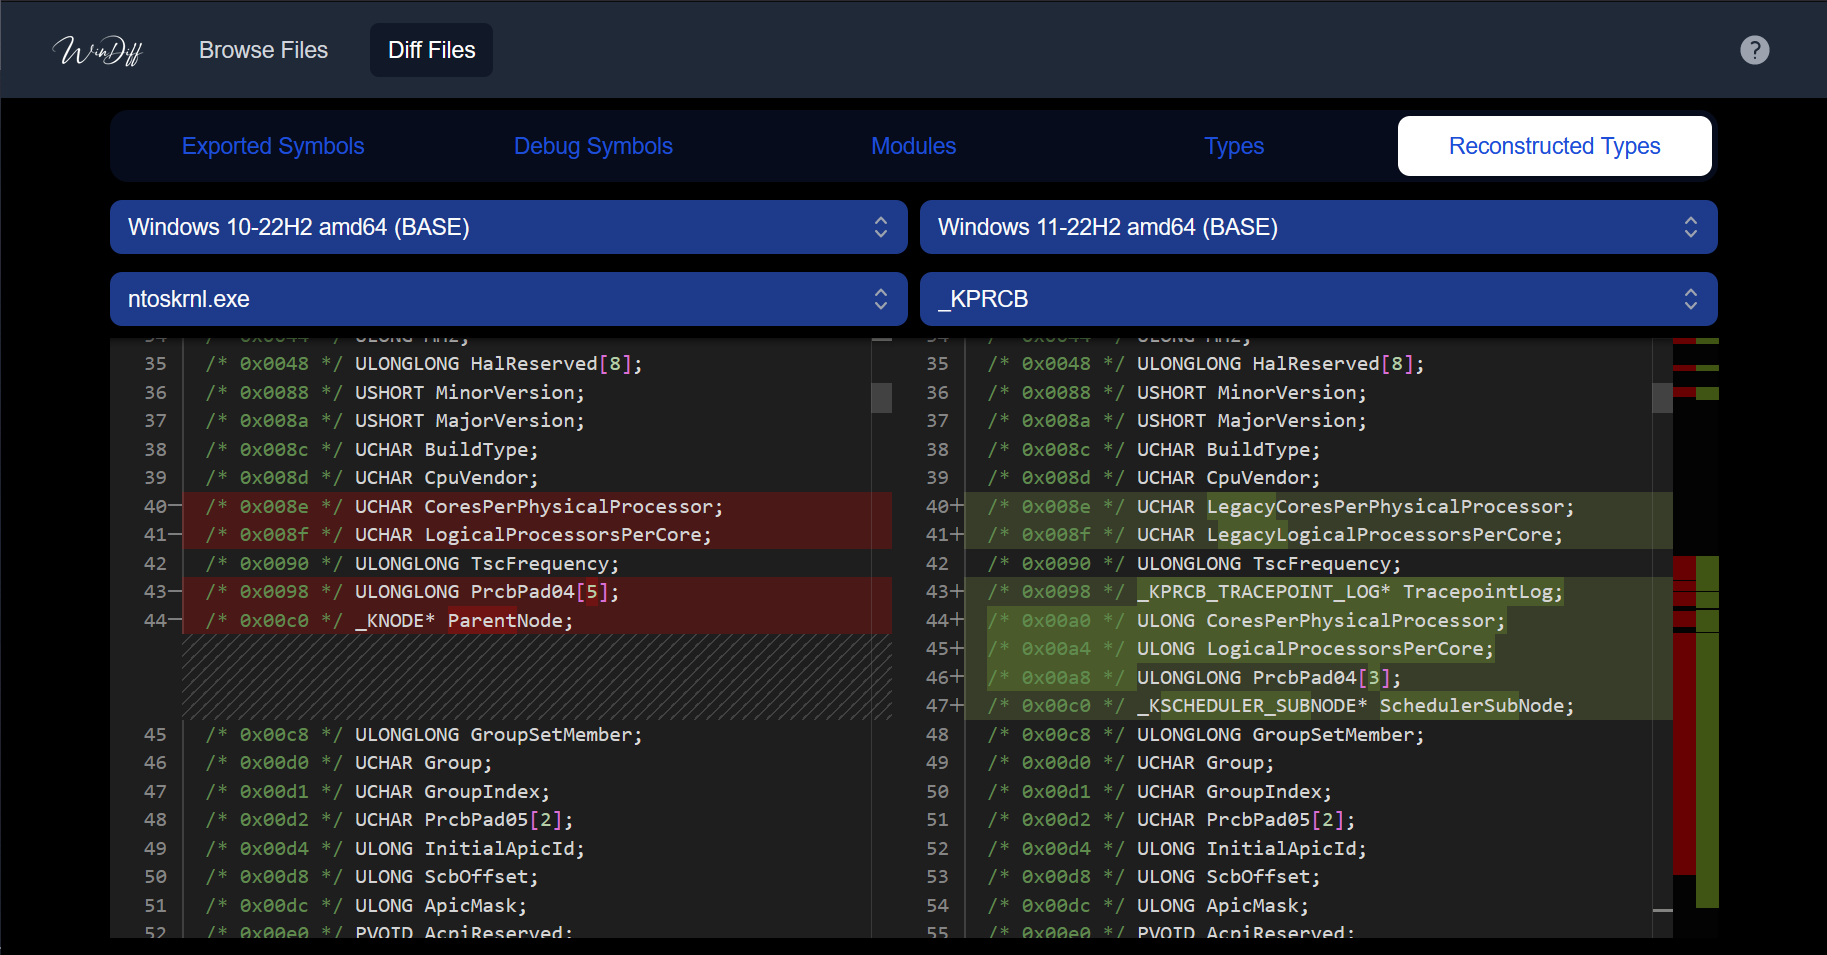 ergrelet/windiff
Tool that allows comparing symbol, type and syscall information of Microsoft Windows binaries across different versions of the OS, using a Web UI…
 st0rn/siglens
Windows artifact analysis toolkit that maps AV detections to PE offsets, sections, RVA/VA and strings, with YARA, AMSI, capa and multi-engine…
 pwndbg/pwndbg
Exploit Development and Reverse Engineering with GDB & LLDB Made Easy
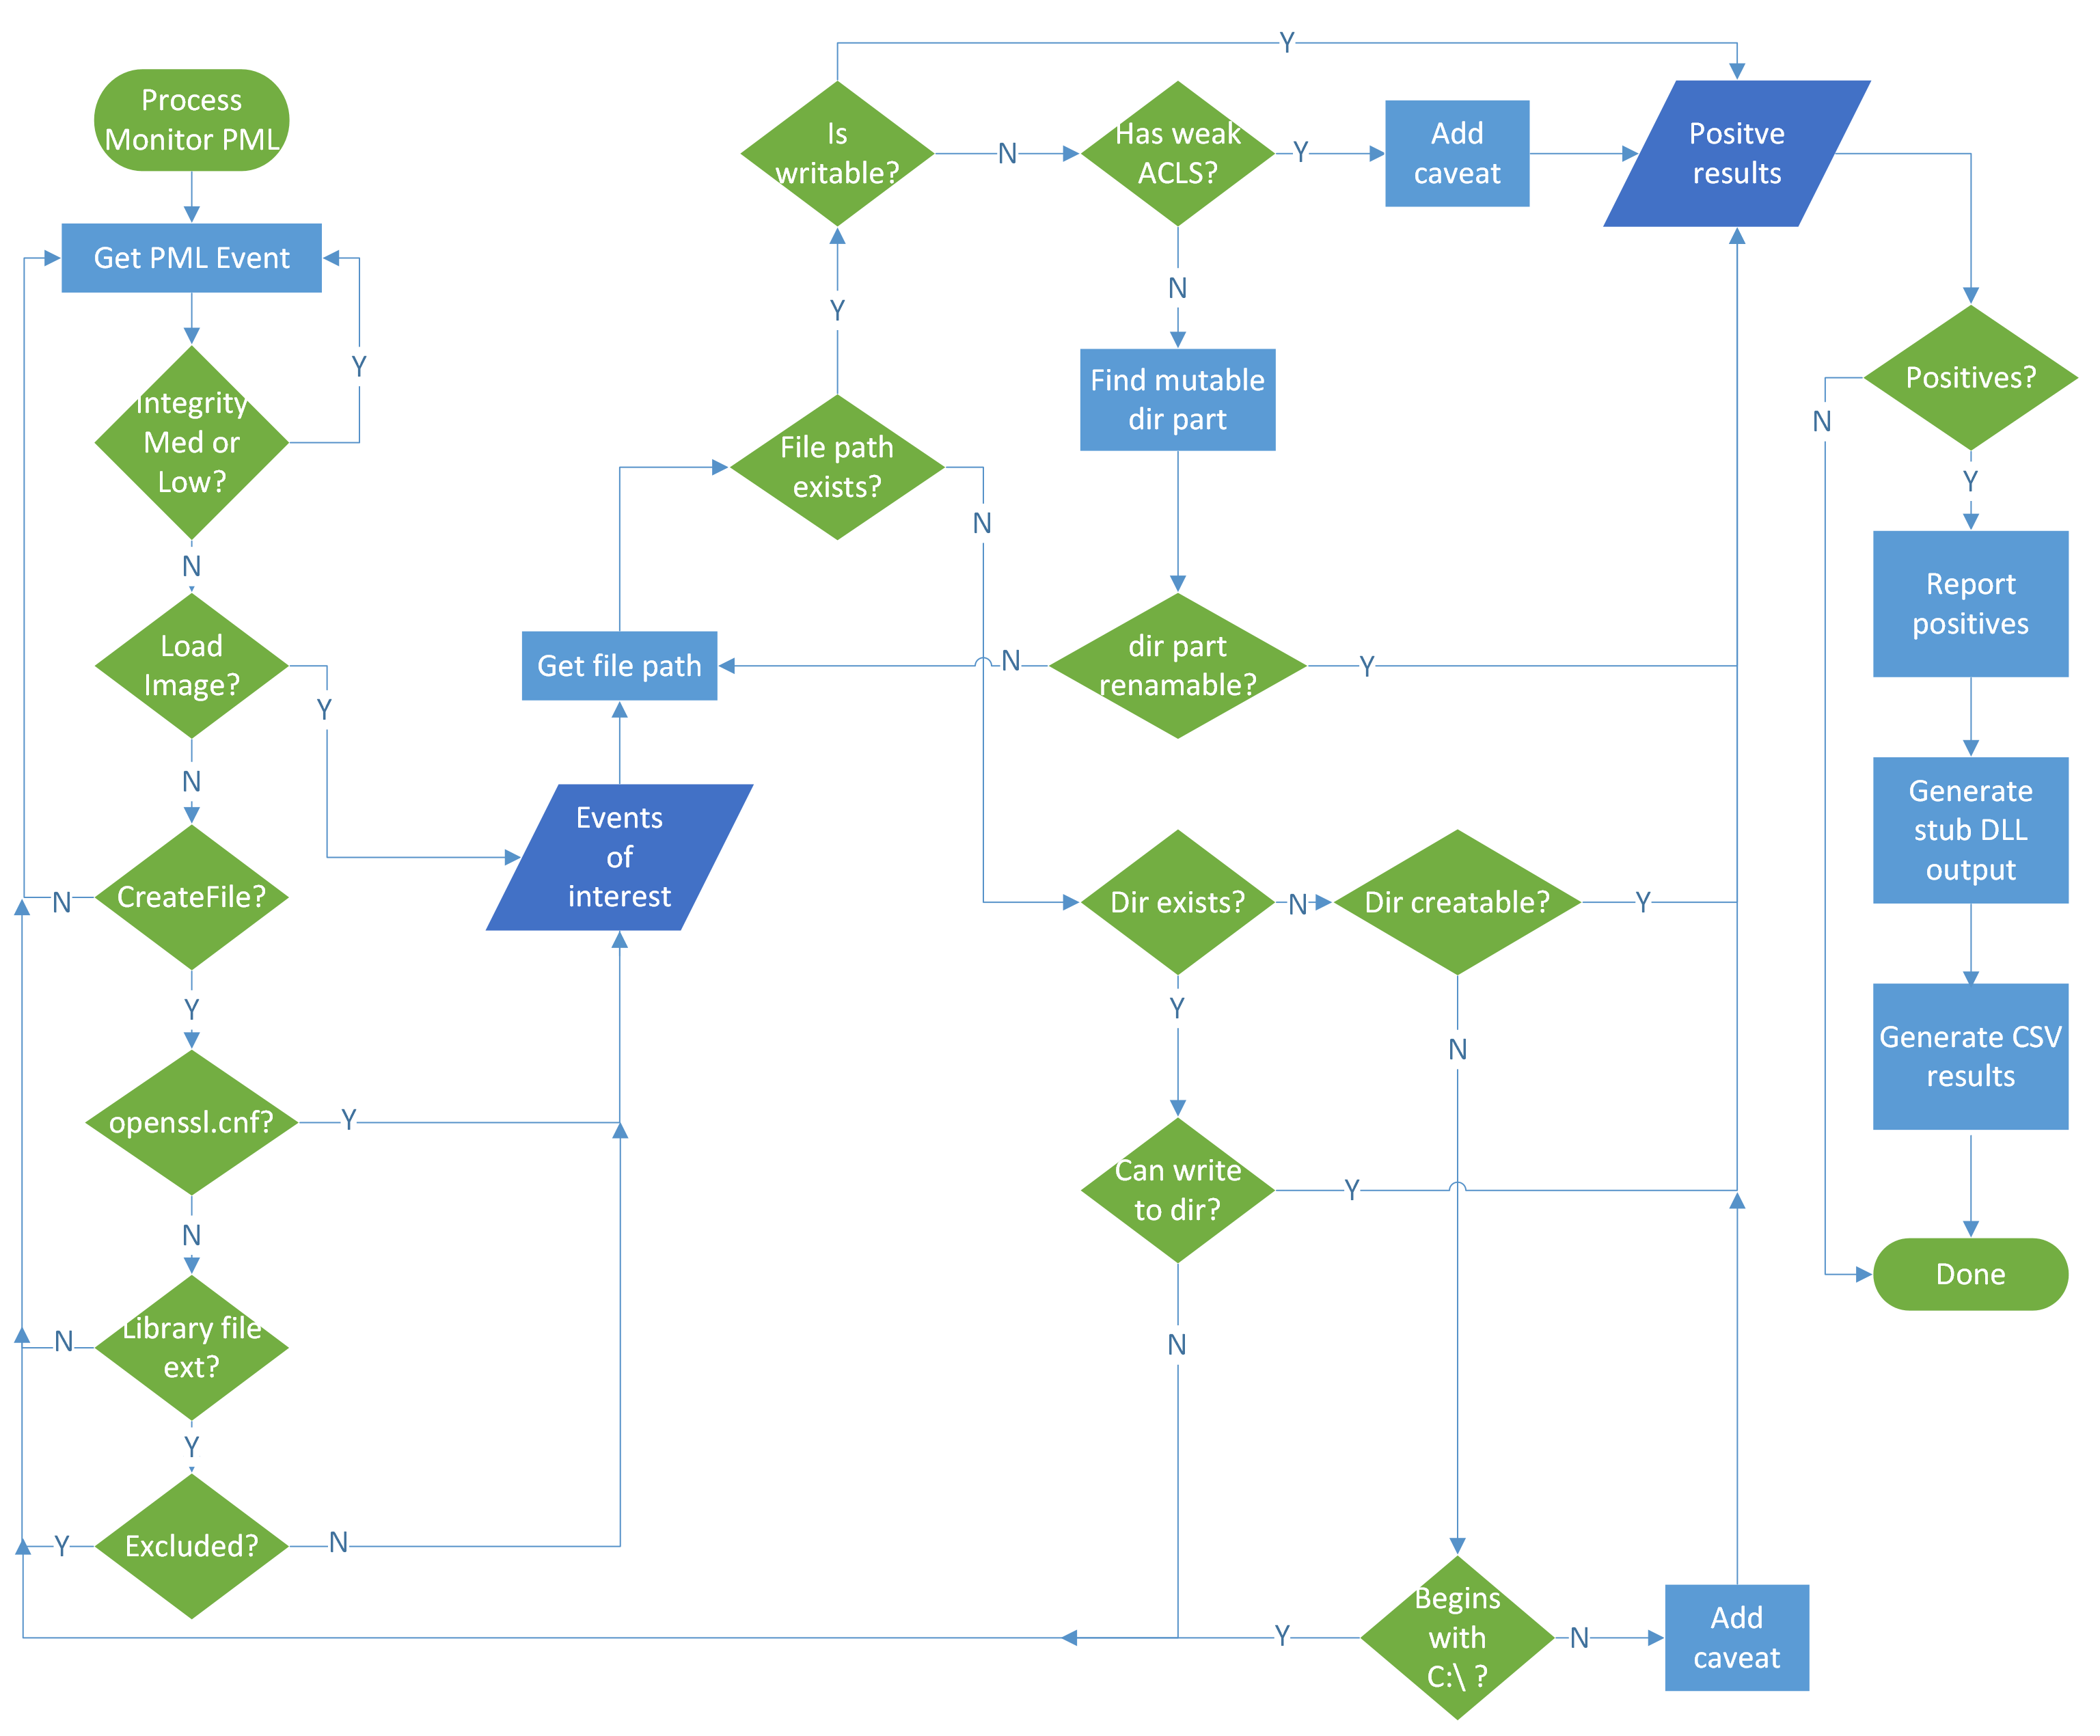 vu-ls/crassus
Windows privilege escalation discovery tool that parses Process Monitor boot logs to identify DLL hijacking, weak ACLs, and other elevation paths,…