
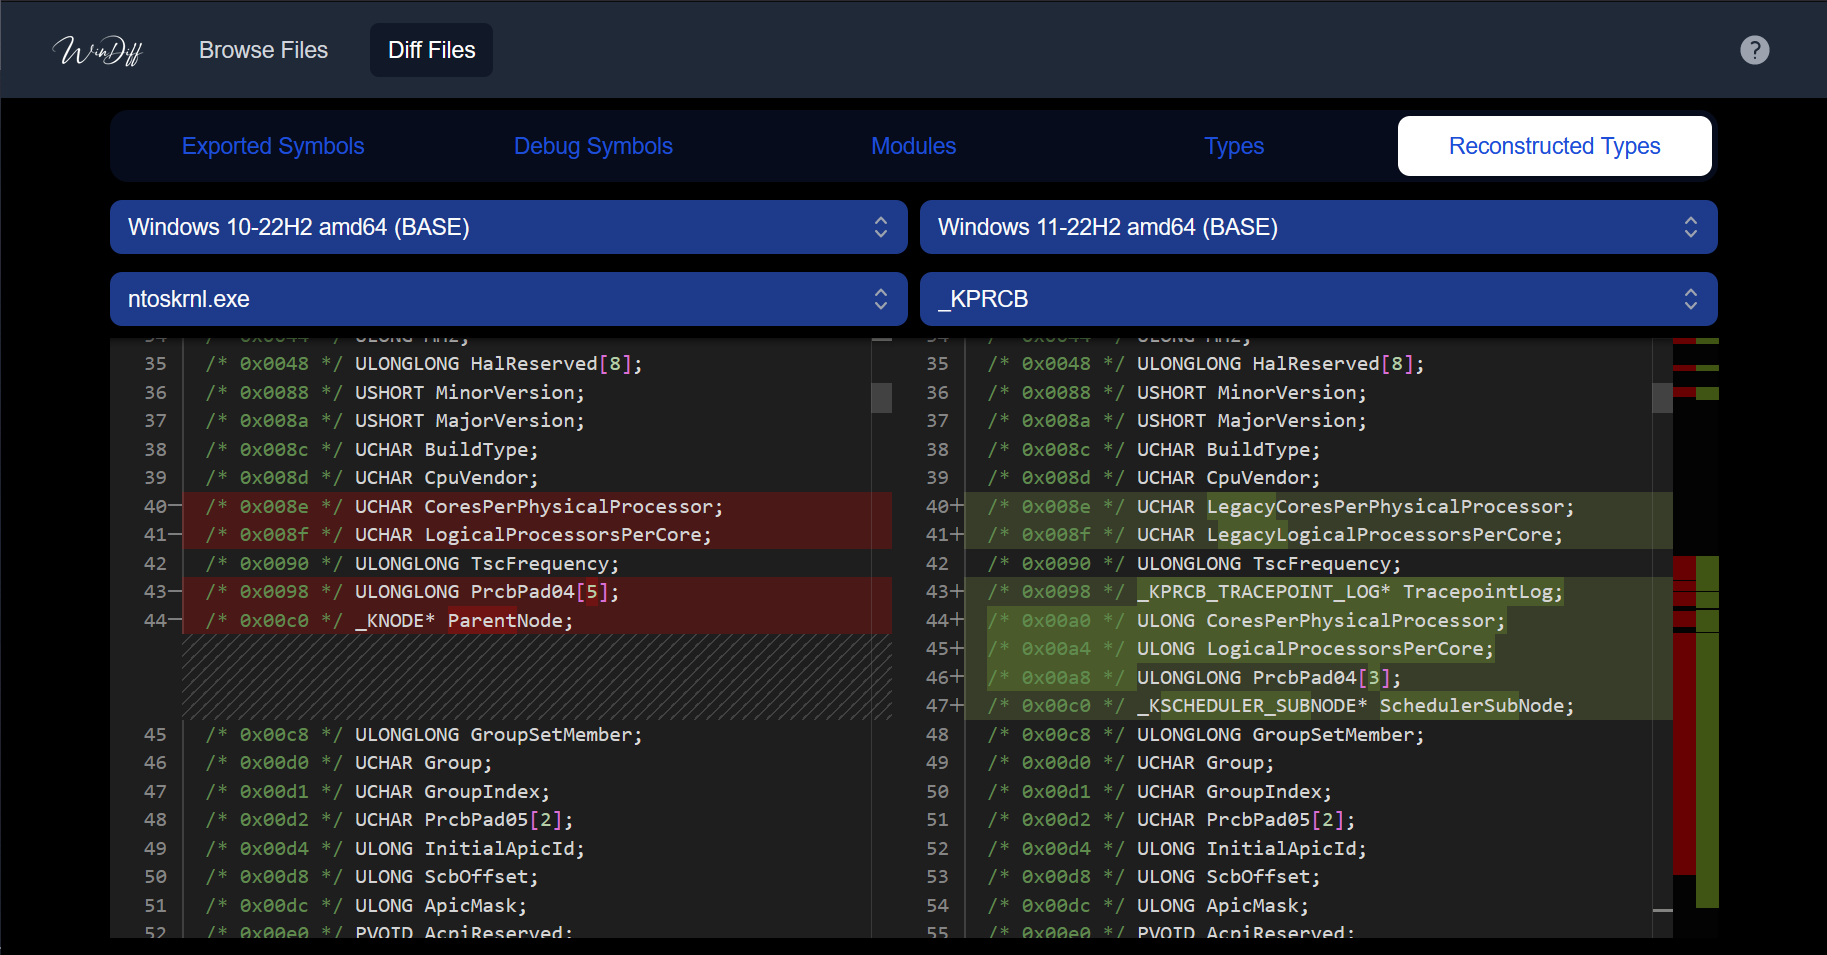
windiff
 ergrelet/windiff
Tool that allows comparing symbol, type and syscall information of Microsoft Windows binaries across different versions of the OS, using a Web UI…
binary-analysisinformation-gatheringreverse-engineering+1
390
ergrelet/windiffTool that allows comparing symbol, type and syscall information of Microsoft Windows binaries across different versions of the OS, using a Web UI…
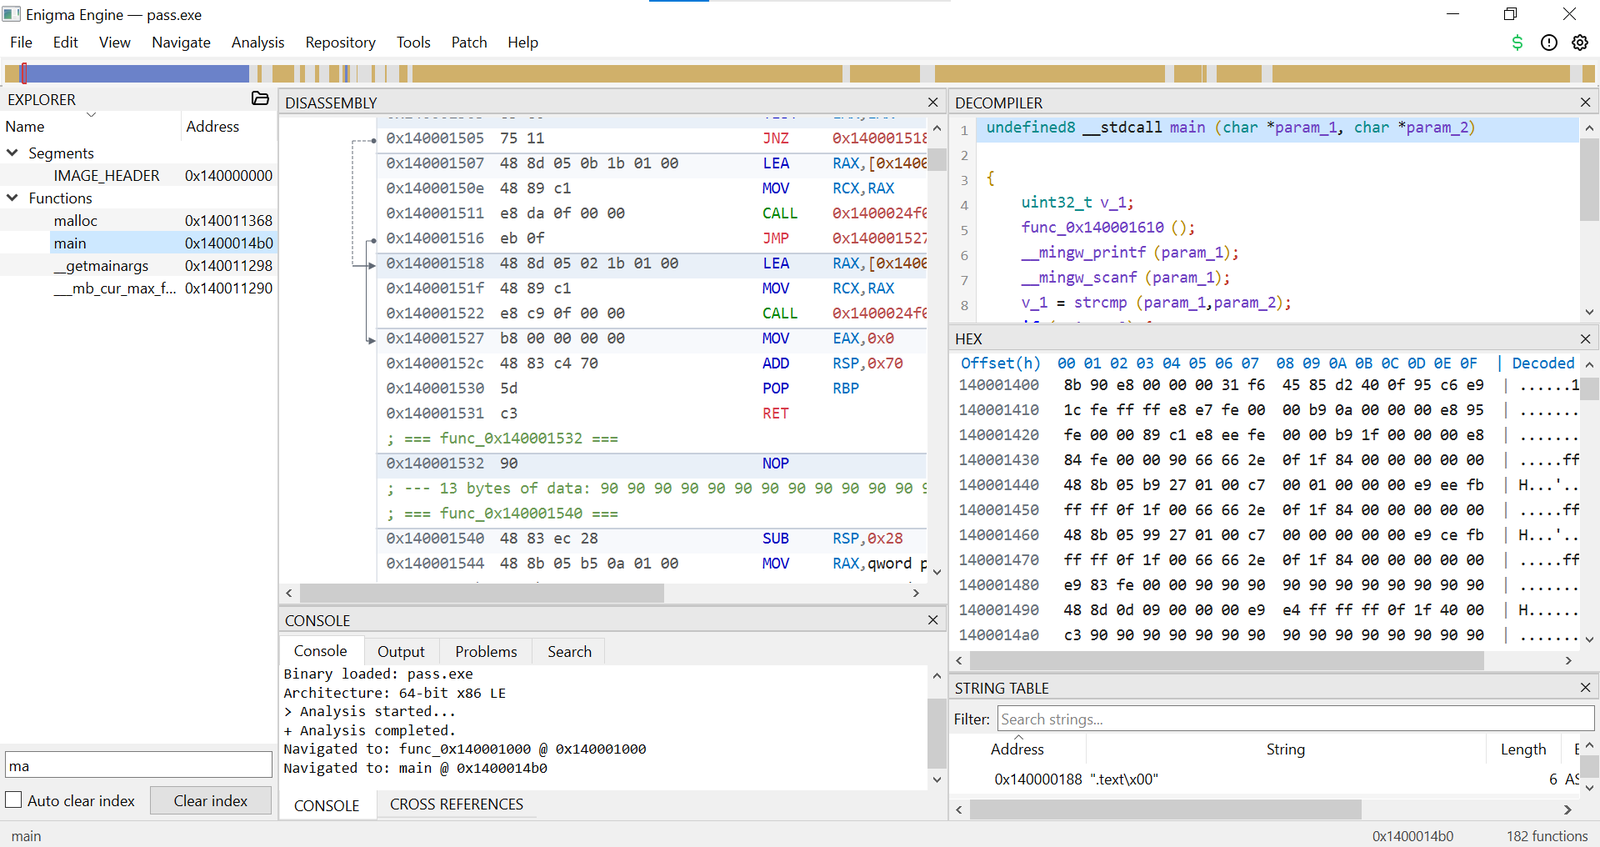 bunnybuzz/enigma
Native C++ reverse-engineering engine with disassembly, decompilation, and analysis pipeline for PE/ELF binaries, featuring interactive GUI and…
 aflplusplus/libafl
Advanced Fuzzing Library - Slot your Fuzzer together in Rust! Scales across cores and machines. For Windows, Android, MacOS, Linux, no_std, ...
 416rehman/deepzero
Find zero-days while you sleep. DeepZero is an automated vulnerability research framework that parses, decompiles, and analyzes thousands of Windows…
 simoneavogadro/android-reverse-engineering-skill
Decompiles Android APK/XAPK/JAR/AAR files and extracts HTTP APIs, authentication patterns, and call flows using jadx, with R8-resistant Kotlin name…
 talha-nazeef-ahmed/rpc-triage
A zero-symbol static analysis engine that extracts and mathematically ranks the Windows RPC attack surface using an AHP-based risk model.
 atlas0fd00m/vivisection
Analysis Plugin and Tools for Vivisect
 0xsp-srd/aether
Windows memory-forensics and threat hunting tool that scans live process memory for malicious patterns, injection techniques, and reflectively loaded…
 blacksnufkin/maverick
Adaptix C2 agent using Crystal Palace PIC linker and PICO module system
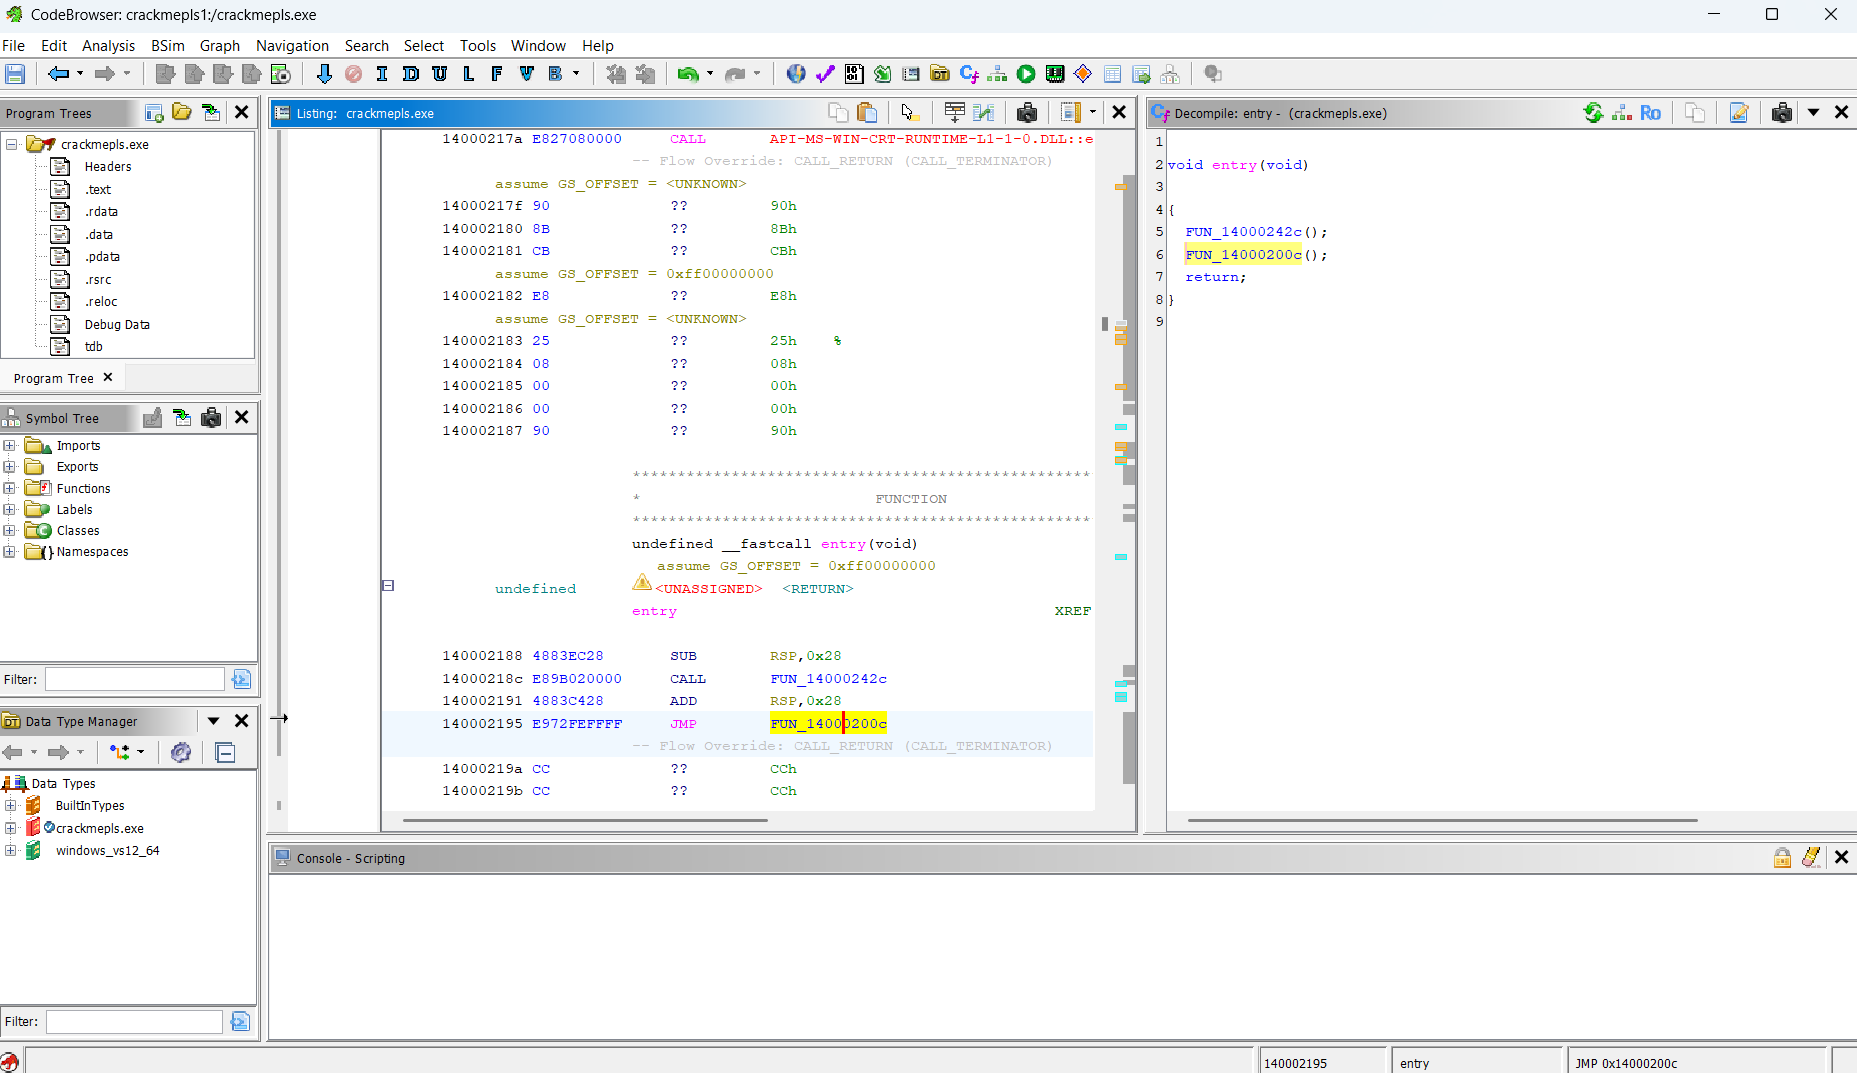 markoglasgow/gemma_crackme_tutorial
Step-by-step tutorial on using Google's Gemma 4 E4B local AI model to reverse engineer a Windows crackme with Ghidra, including setup for local…
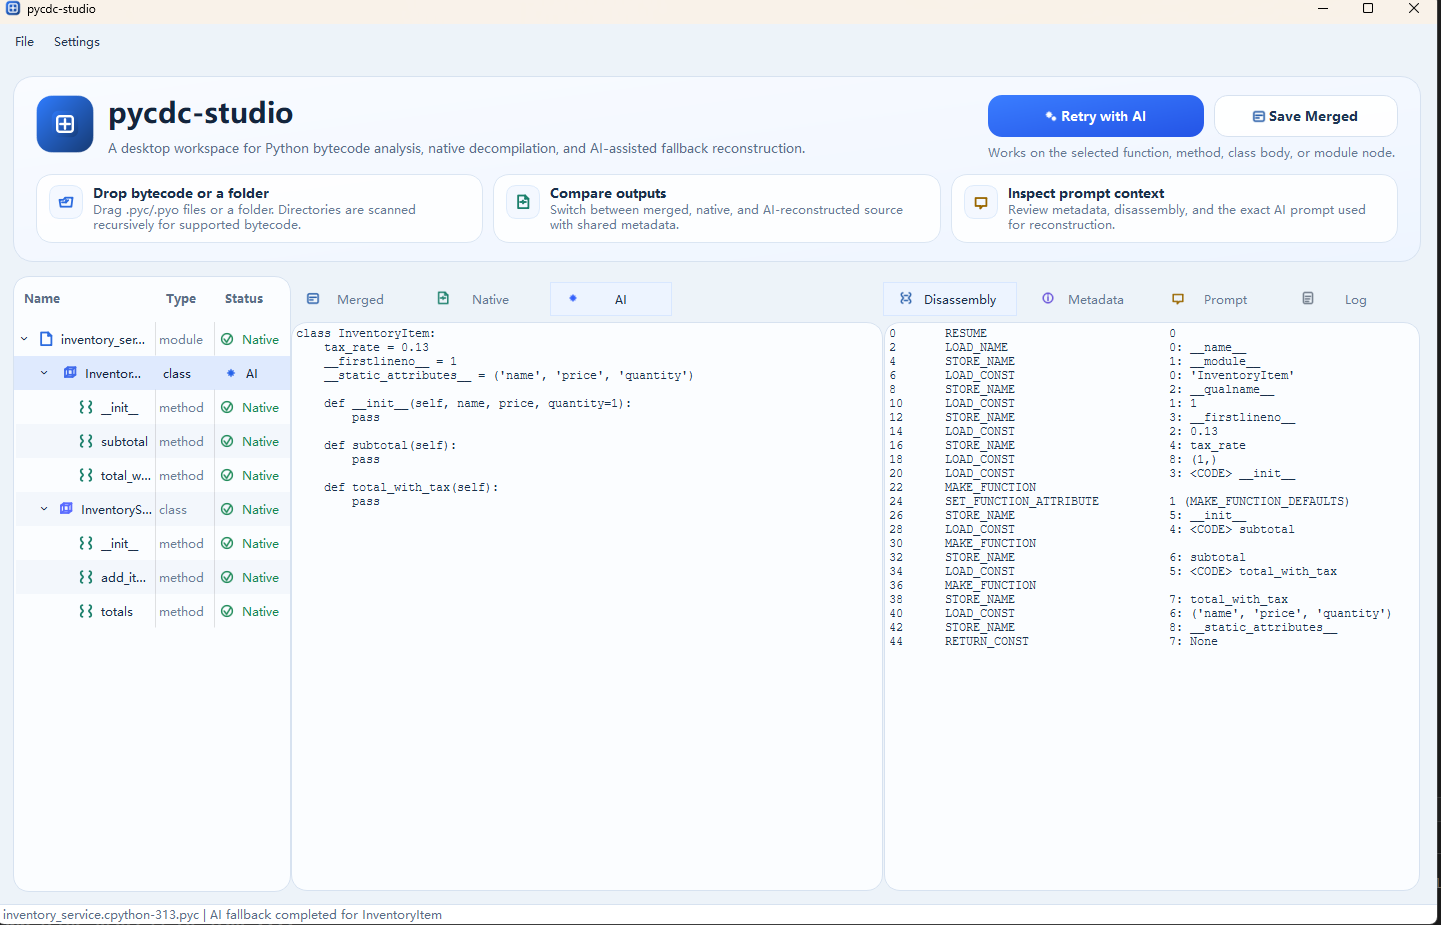 ddouworld/pycdc-studio
A Qt Widgets desktop UI for exploring Python bytecode with pycdc/pycdas, inspecting native decompilation, and using AI fallback for unsupported code…
 synacktiv/thats_no_pipe
Windows named pipe hooking toolkit
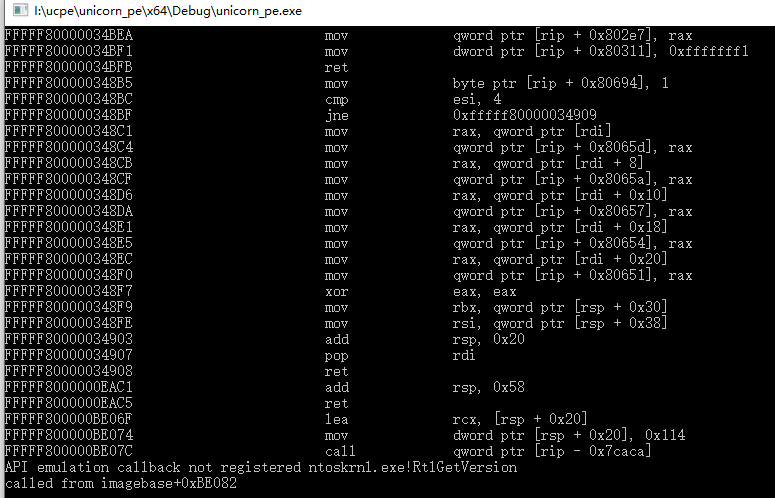 hzqst/unicorn_pe
Emulates Windows PE execution using Unicorn engine for malware analysis, unpacking packed binaries, and decrypting VMProtect strings and imports.
 forentfraps/pe-signgen
Universal signature generation for any system function from all Windows Builds using Winbindex
 amperclock/cve-2025-9491_poc
Proof-of-Concept of the CVE-2025-9491 using invisible characters in the arguments of a Windows shortcut file (.lnk)
 oldboy21/shgenob
Python based tool for generating Shellcode from PIC C
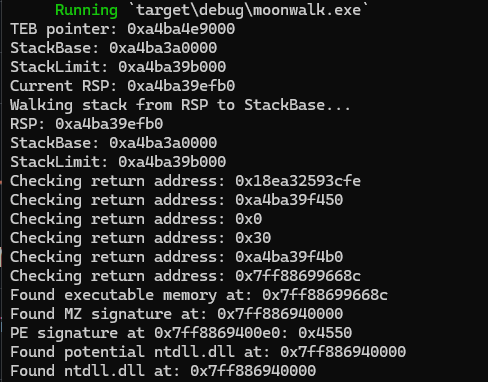 teach2breach/moonwalk
find dll base addresses without PEB WALK
 personnumber3377/windows_tcpip_fuzz
This is my attempt at fuzzing the tcpip.sys driver in windows via using scapy. This is inspired by this vulnerability here:…