

radare2
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
ai-assisted-reversingandroid-securitybinary-analysis+16
radareorg/radare2UNIX-like reverse engineering framework and command-line toolset
 dosx-dev/obfus.h
Macro-header for compile-time C obfuscation (tcc, win x86/x64)
 mahmoudimus/static_asm
Header-only C++2x compile-time assembler for x86/x86-64 instruction encoding
 sjkim1127/reversecore_mcp
A security-first MCP server that empowers AI agents to perform automated reverse engineering, malware analysis, forensics, vulnerability research,…
 onekey-sec/unblob
Extract files from any kind of container formats
 ejfkdev/jscd
Reverse bytenode .jsc (V8 code cache) to JavaScript — static, pure Rust, no patched V8/Node. Node 8→26 / V8 5.8–14.6; 25k .jsc tested, 0 fail.
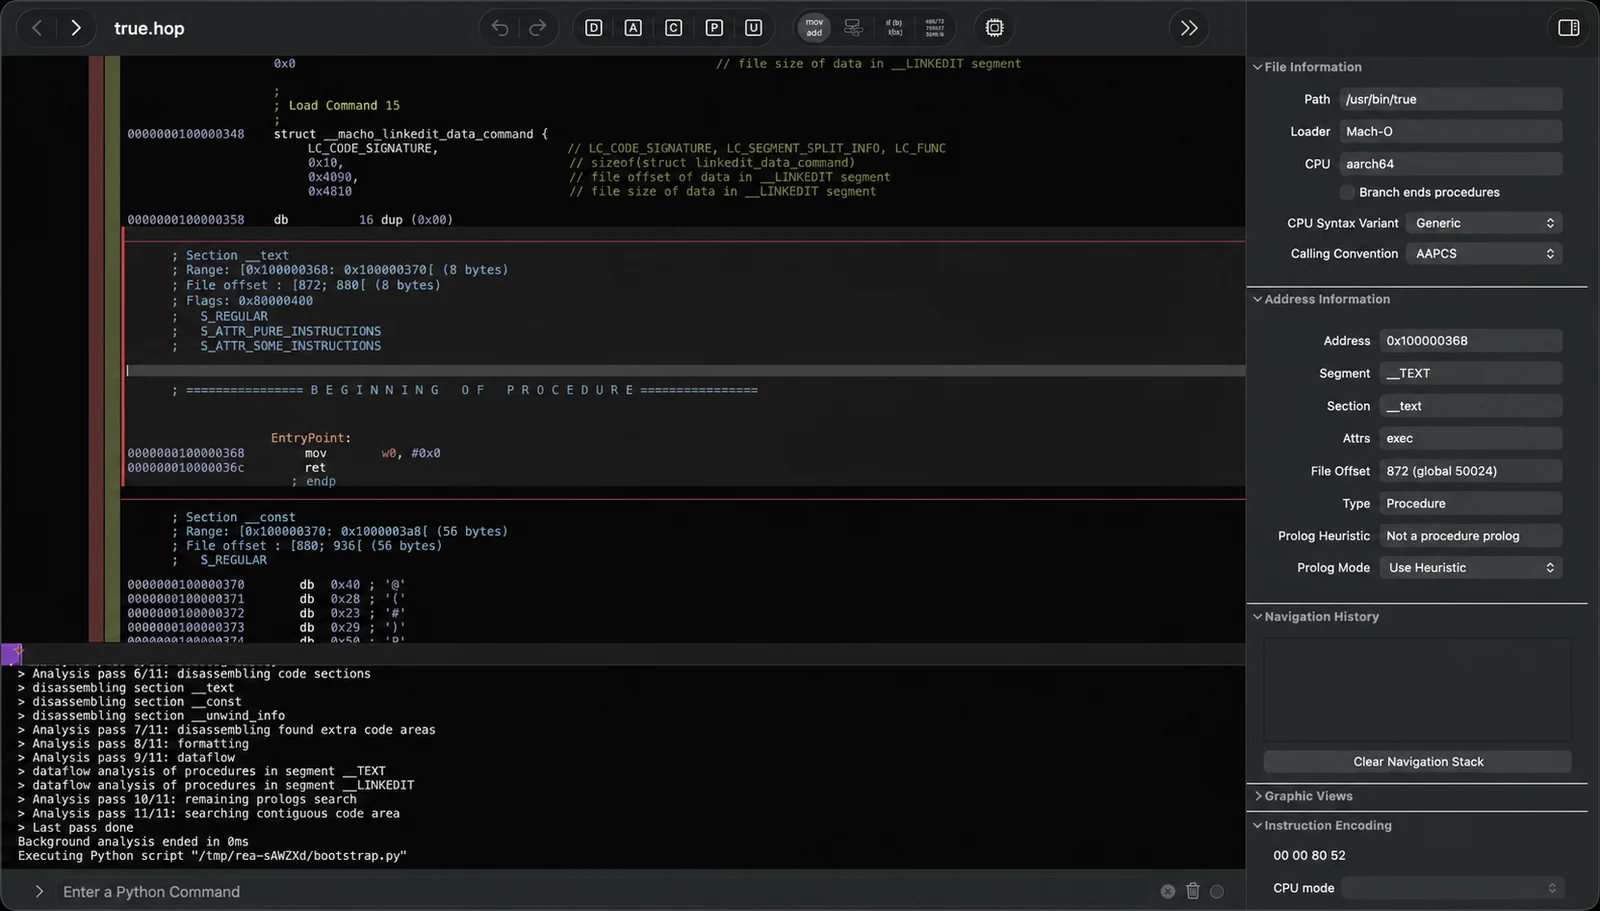 morluto/rea
Reverse engineer anything with agents, from app behavior down to native binaries.
 0sec-labs/0
Full-stack AI security OS for your browser, terminal, and agents. Find, verify, and fix vulnerabilities. Prioritized by business impact instead of…
 atomdrift-project/scan
0-day malware detection for binaries, source & scripts (that doesn't suck)
 gmh5225/awesome-llvm-security
Curated collection of LLVM security resources covering binary lifting, code obfuscation, static analysis, symbolic execution, sanitizers, and…
 sunnypatell/basalt
World's first hazard checker for NVIDIA Blackwell (sm_120), with an assembler and scheduler matched against their own compiler byte for byte. The…
 mg1937/asc
Fast Android APK decompiler front-end that queries compiled DEX artifacts directly, extracting classes and cross-references in milliseconds without…
 sdodson/cve-2026-46595-proof
Go proof-of-concept demonstrating CVE-2026-46595 in golang.org/x/crypto/ssh, using symbol inspection of stripped binaries and image scans to verify…
 robertdfrench/ifuncd-up
GNU IFUNC is the real culprit behind CVE-2024-3094
 1rhino2/fnprint
match functions in binaries by what they do, not what their bytes look like. behavioral function fingerprinting via microexecution.
 worksbutnottested/lightkeeper
Maps execution-coverage data onto Ghidra disassembly to highlight visited code paths and accelerate reverse-engineering workflows.