
uefi-firmware-parser
 theopolis/uefi-firmware-parser
Parse BIOS/Intel ME/UEFI firmware related structures: Volumes, FileSystems, Files, etc
binary-analysisembedded-systems-securityfirmware-analysis+2
933
theopolis/uefi-firmware-parserParse BIOS/Intel ME/UEFI firmware related structures: Volumes, FileSystems, Files, etc
 rizinorg/rz-ghidra
Deep ghidra decompiler and sleigh disassembler integration for rizin
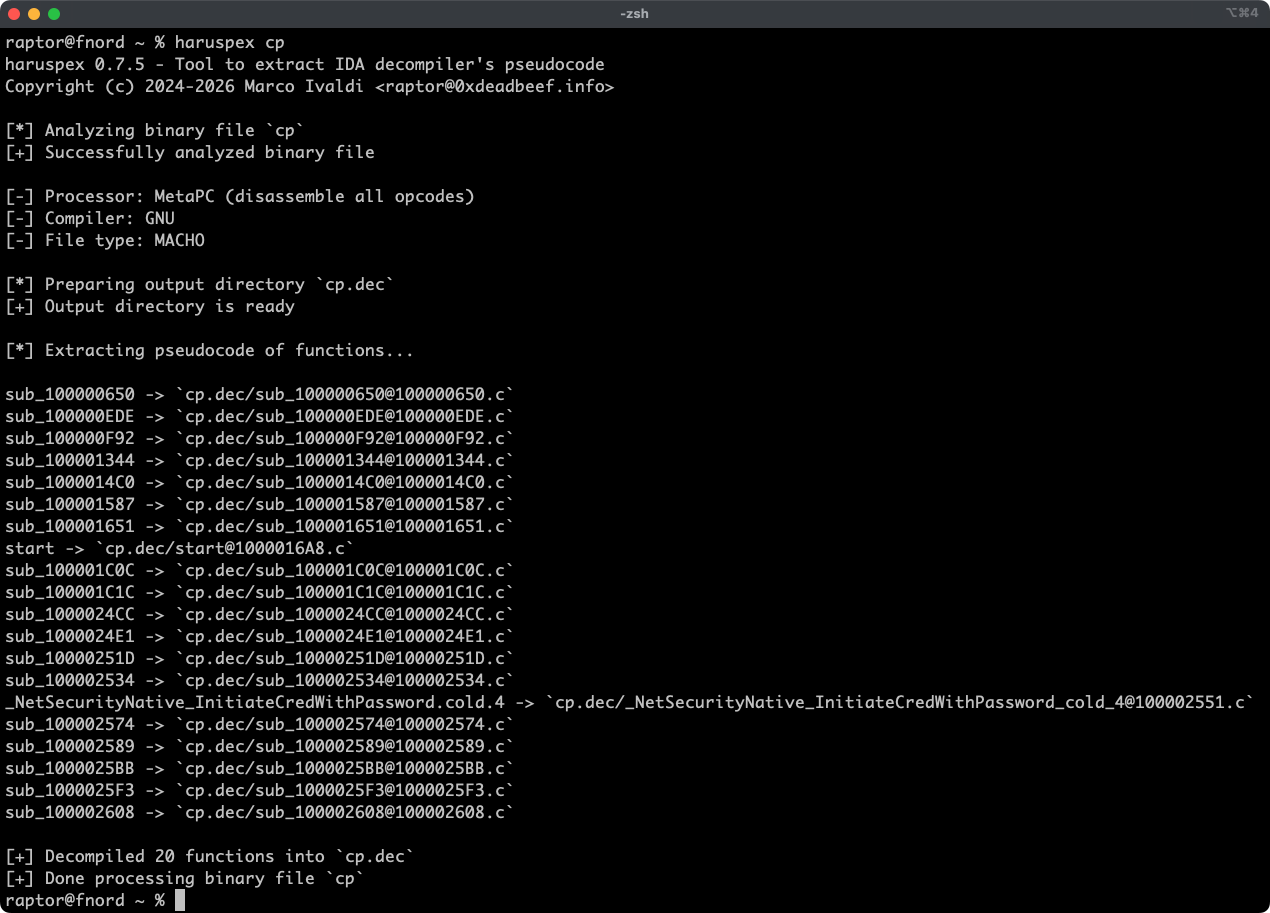 0xdea/haruspex
Vulnerability research assistant that extracts pseudocode from the IDA Hex-Rays decompiler.
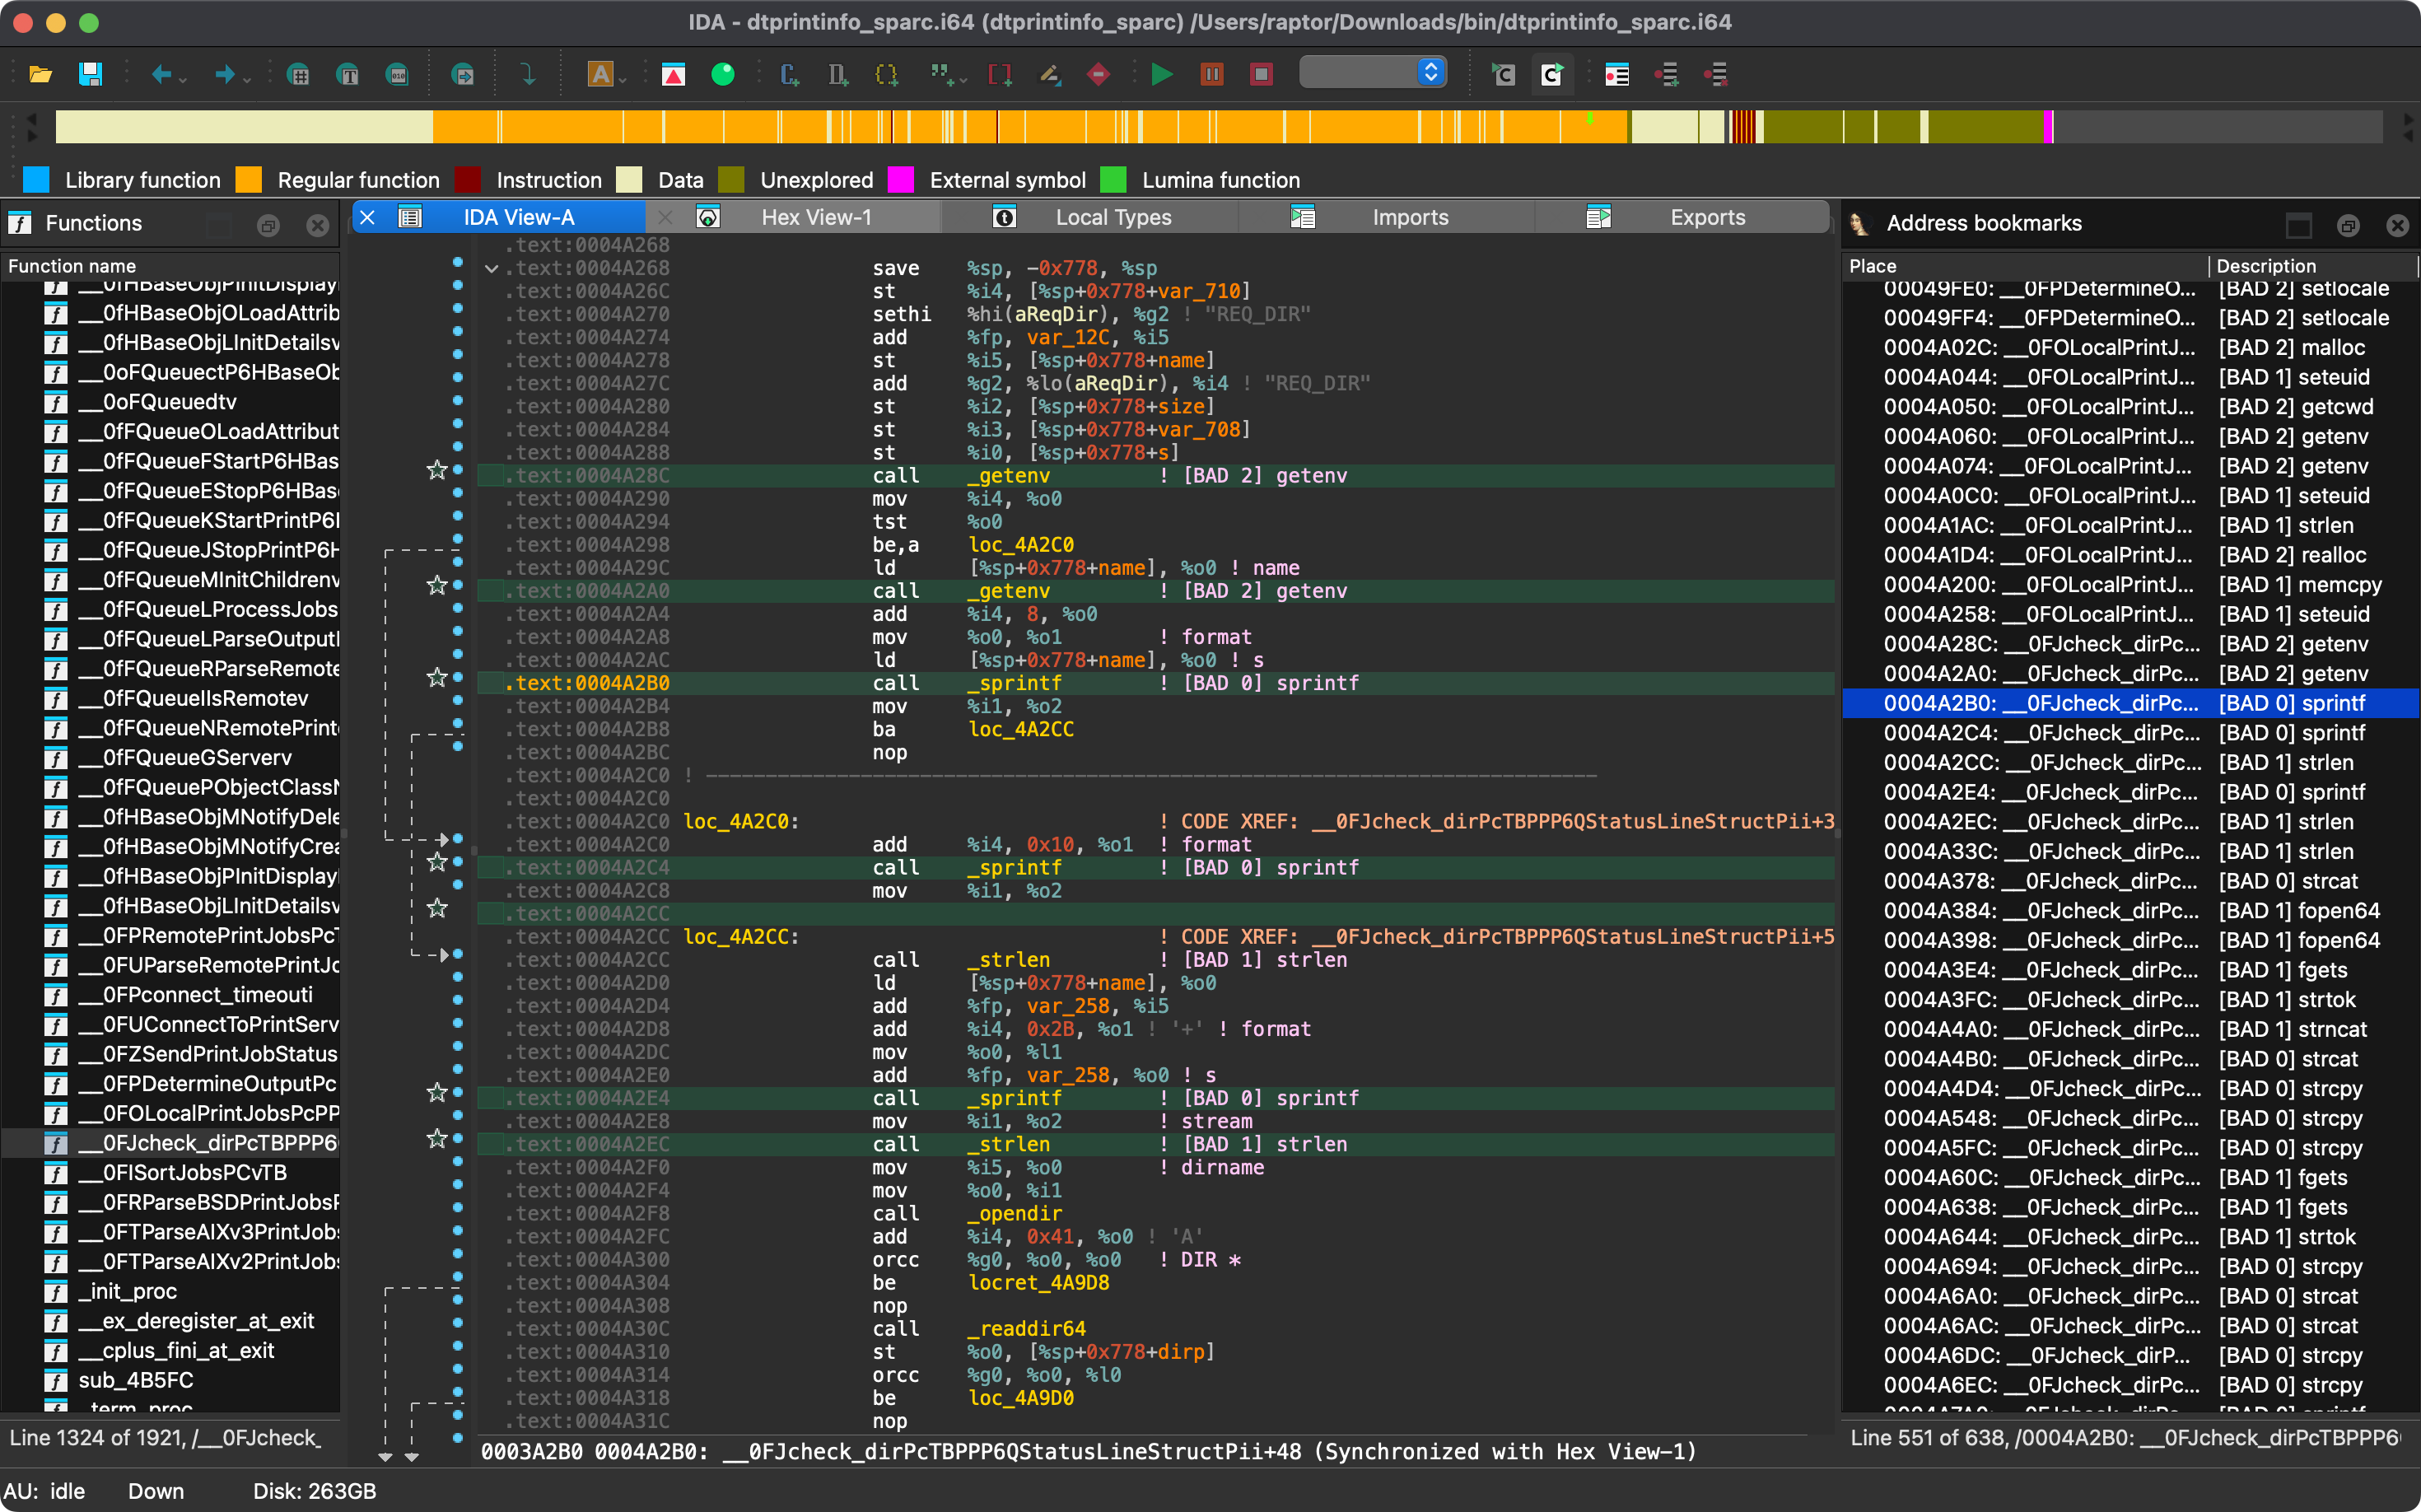 0xdea/rhabdomancer
Vulnerability research assistant that locates calls to potentially insecure API functions in a binary file.
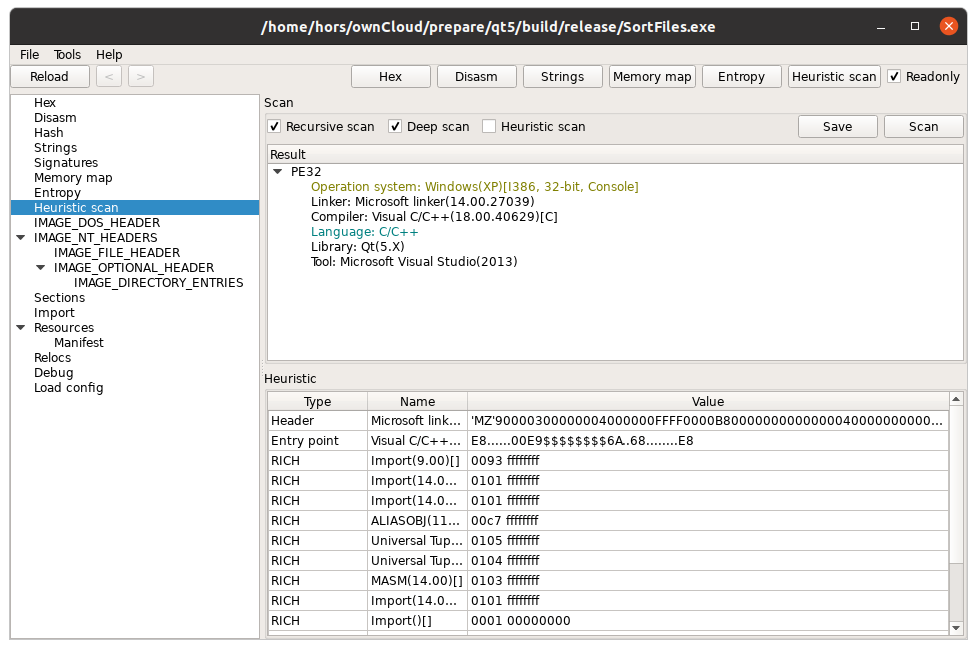 horsicq/xpeviewer
PE file viewer/editor for Windows, Linux and MacOS.
 rehints/efixplorer
IDA plugin and loader for UEFI firmware analysis and reverse engineering automation
 nmatt0/moria
IoT firmware identification and extraction
 storyyeller/krakatau
Java decompiler, assembler, and disassembler
 onekey-sec/unblob
Extract files from any kind of container formats
 jetbrains/fernflower
Decompiler from Java bytecode to Java, used in IntelliJ IDEA.
 marin-m/vmlinux-to-elf
A tool to recover a fully analyzable .ELF from a raw kernel, through extracting the kernel symbol table (kallsyms)
 m4b/goblin
An impish, cross-platform binary parsing crate, written in Rust
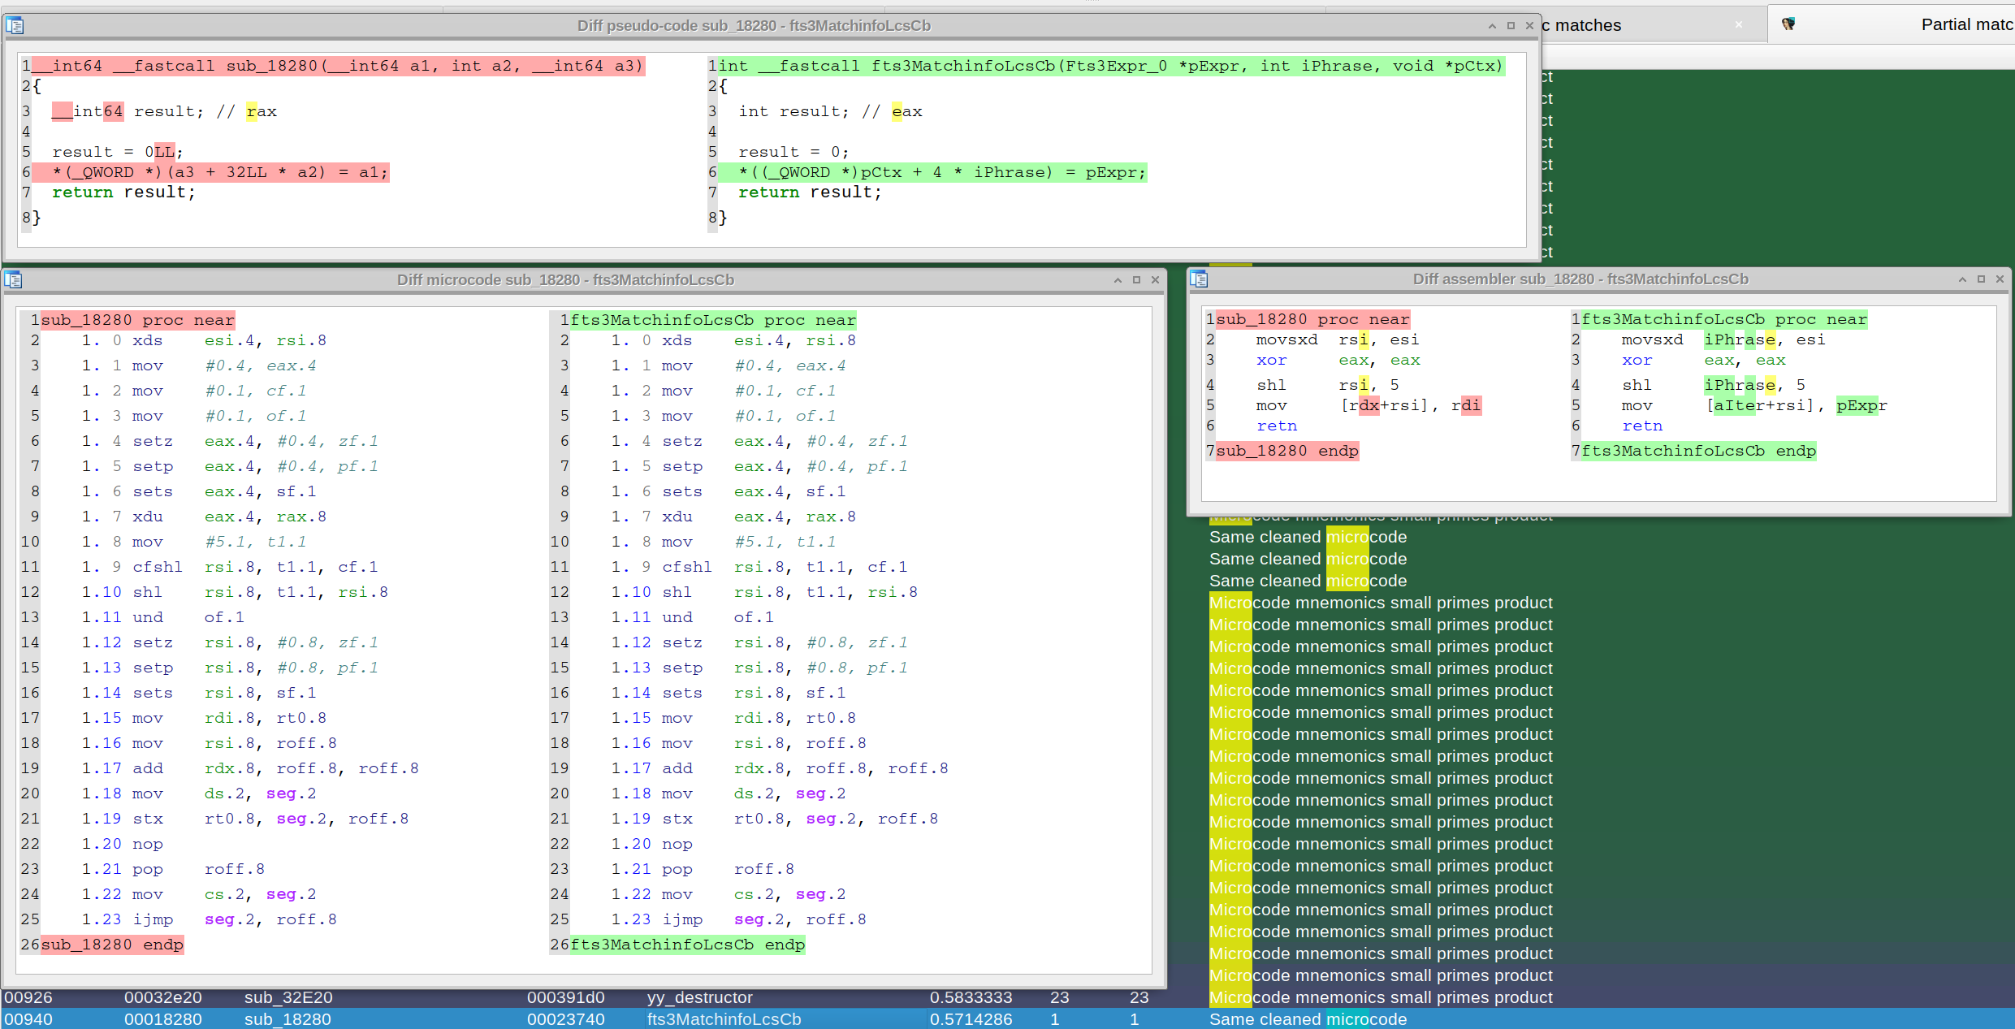 joxeankoret/diaphora
Diaphora, the most advanced Free and Open Source program diffing tool.
 eset/ipyida
IPython console integration for IDA Pro
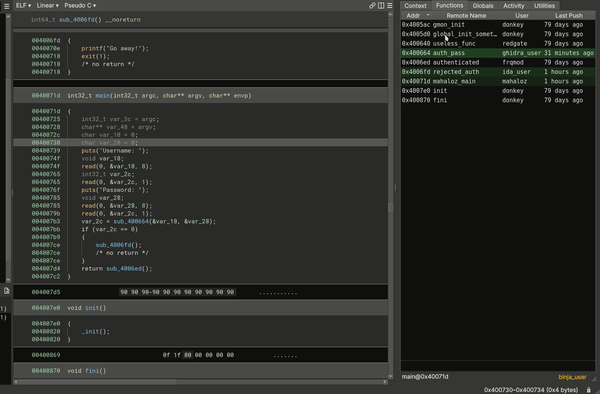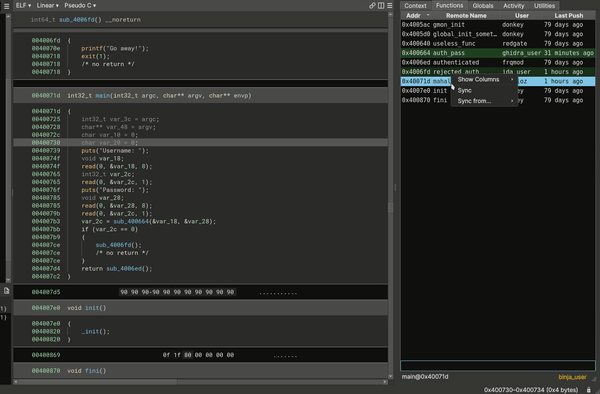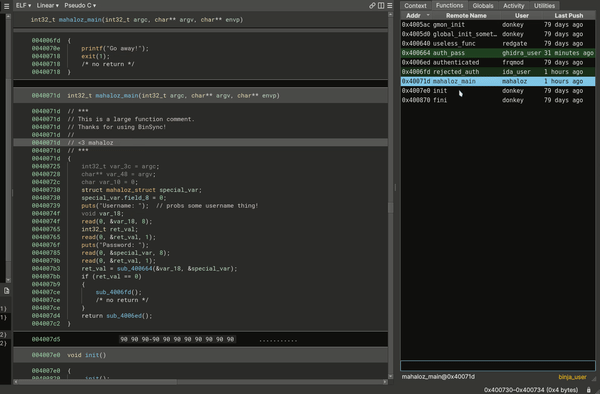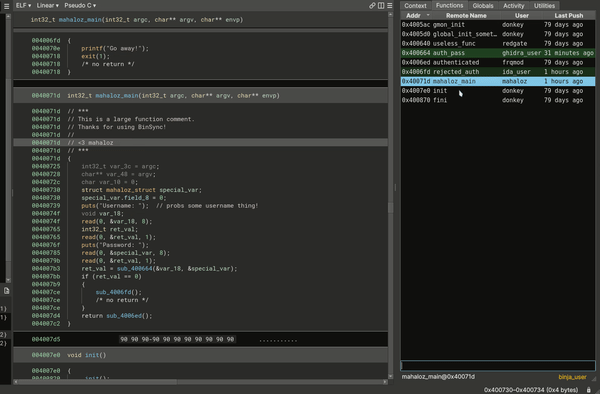 binsync/binsync
A reversing plugin for cross-decompiler collaboration, built on git.
 0xdea/ghidra-scripts
Curated Ghidra scripts to automate reverse engineering and vulnerability analysis: locate insecure functions, extract decompiler pseudocode, fix…
 kraxel/virt-firmware
Toolkit for decoding, inspecting, and modifying UEFI firmware volumes and variable stores. Supports secure boot certificate enrollment, PE binary…