

sogen
 momo5502/sogen
🪅 Windows & Linux userspace emulator
binary-analysisdebuggersdynamic-analysis-sandboxing+3
momo5502/sogen🪅 Windows & Linux userspace emulator

 icsharpcode/ilspy
.NET Decompiler with support for PDB generation, ReadyToRun, Metadata (&more) - cross-platform!
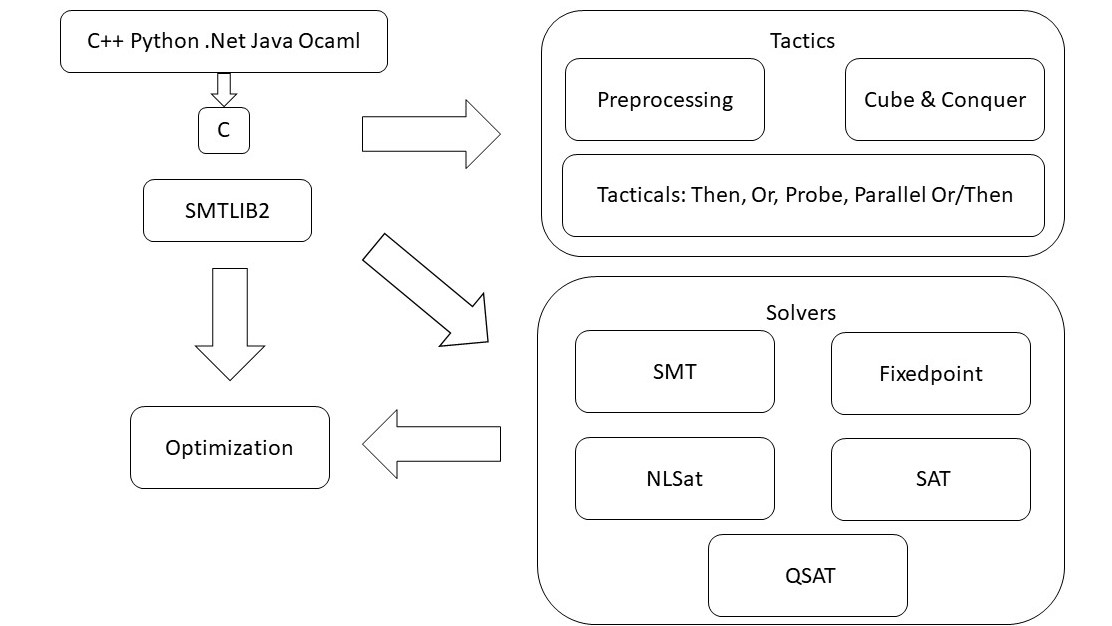 z3prover/z3
High-performance SMT solver for automated theorem proving, constraint solving, and program verification. Supports multiple theories and language…
 gmh5225/awesome-game-security
Curated index of game security research: anti-cheat internals, DMA attacks, reverse engineering, kernel/mobile protections, and graphics API hooking…
 vmoranv/jshookmcp
A search-first, profile-aware reverse-engineering workspace for AI agents — 735 tools across 36 domains in one MCP server.
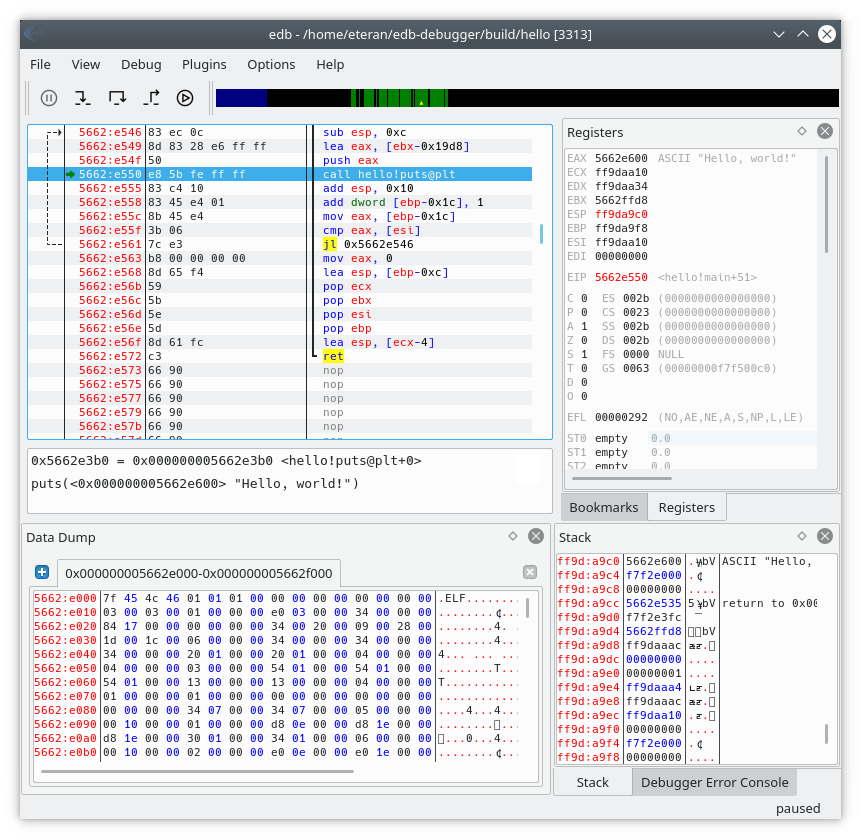 eteran/edb-debugger
edb is a cross-platform AArch32/x86/x86-64 debugger.

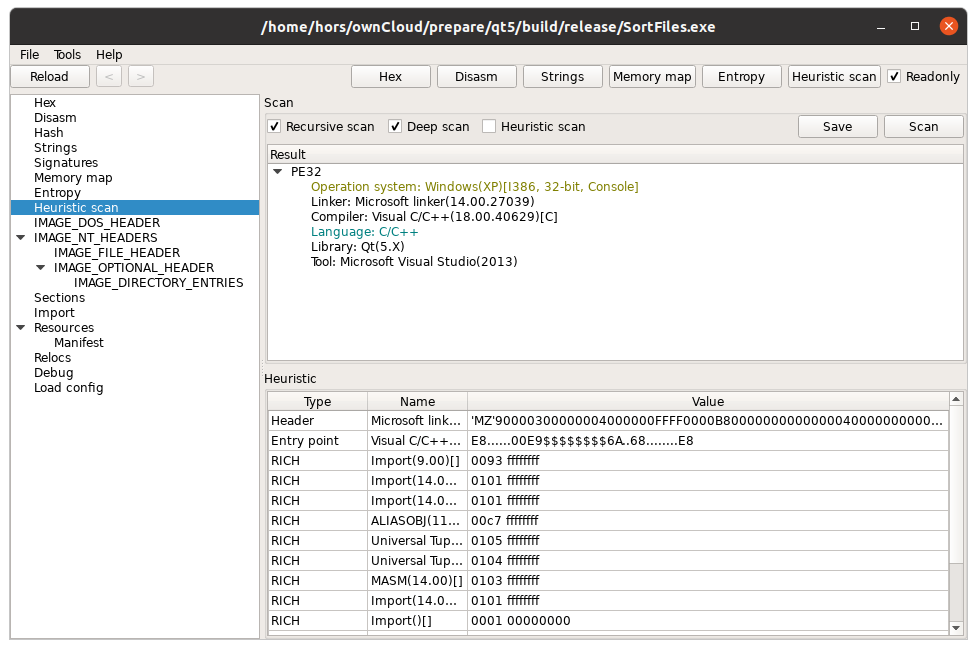 horsicq/xpeviewer
PE file viewer/editor for Windows, Linux and MacOS.
 horsicq/detect-it-easy
Program for determining types of files for Windows, Linux and MacOS.
 bethington/ghidra-mcp
MCP server bridging Ghidra's reverse engineering with AI tools: 256 tools for decompilation, P-code emulation, live debugging, data flow analysis,…
 mytechnotalent/reverse-engineering
A FREE comprehensive reverse engineering tutorial covering x86, x64, 32-bit/64-bit ARM, 8-bit AVR and 32-bit RISC-V architectures.
 joernio/joern
Open-source code analysis platform for C/C++/Java/Binary/Javascript/Python/Kotlin based on code property graphs. Discord https://discord.gg/vv4MH284Hc
 rizinorg/rz-ghidra
Deep ghidra decompiler and sleigh disassembler integration for rizin
 capstone-engine/capstone
Multi-architecture disassembly framework providing a lightweight, thread-safe API for binary analysis, reverse engineering, and malware research…
 revng/revng
Open source binary analysis framework and decompiler built on LLVM and QEMU, lifting binaries to a readable intermediate representation for reverse…

 e-m-b-a/emba
EMBA - The firmware security analyzer