

lightkeeper
 worksbutnottested/lightkeeper
Maps execution-coverage data onto Ghidra disassembly to highlight visited code paths and accelerate reverse-engineering workflows.
binary-analysiscode-analysisdynamic-code-analysis+1
77
worksbutnottested/lightkeeperMaps execution-coverage data onto Ghidra disassembly to highlight visited code paths and accelerate reverse-engineering workflows.
 ghostvectoracademy/dllhijackhunter
Automated DLL Hijacking Discovery, Validation, and Confirmation. Turning local misconfigurations into weaponized, confirmed attack paths.
 1rhino2/fnprint
match functions in binaries by what they do, not what their bytes look like. behavioral function fingerprinting via microexecution.
 binsec/xyntia
Xyntia, the black-box deobfuscator
 r00tkitsmm/pishi
Pishi is a code coverage tool like kcov for macOS.
 smackers/smack
Modular software verification toolchain that translates LLVM IR into Boogie intermediate verification language for bounded and experimental unbounded…
 trailofbits/polytracker
An LLVM-based instrumentation tool for universal taint tracking, dataflow analysis, and tracing.
 robertdfrench/ifuncd-up
GNU IFUNC is the real culprit behind CVE-2024-3094
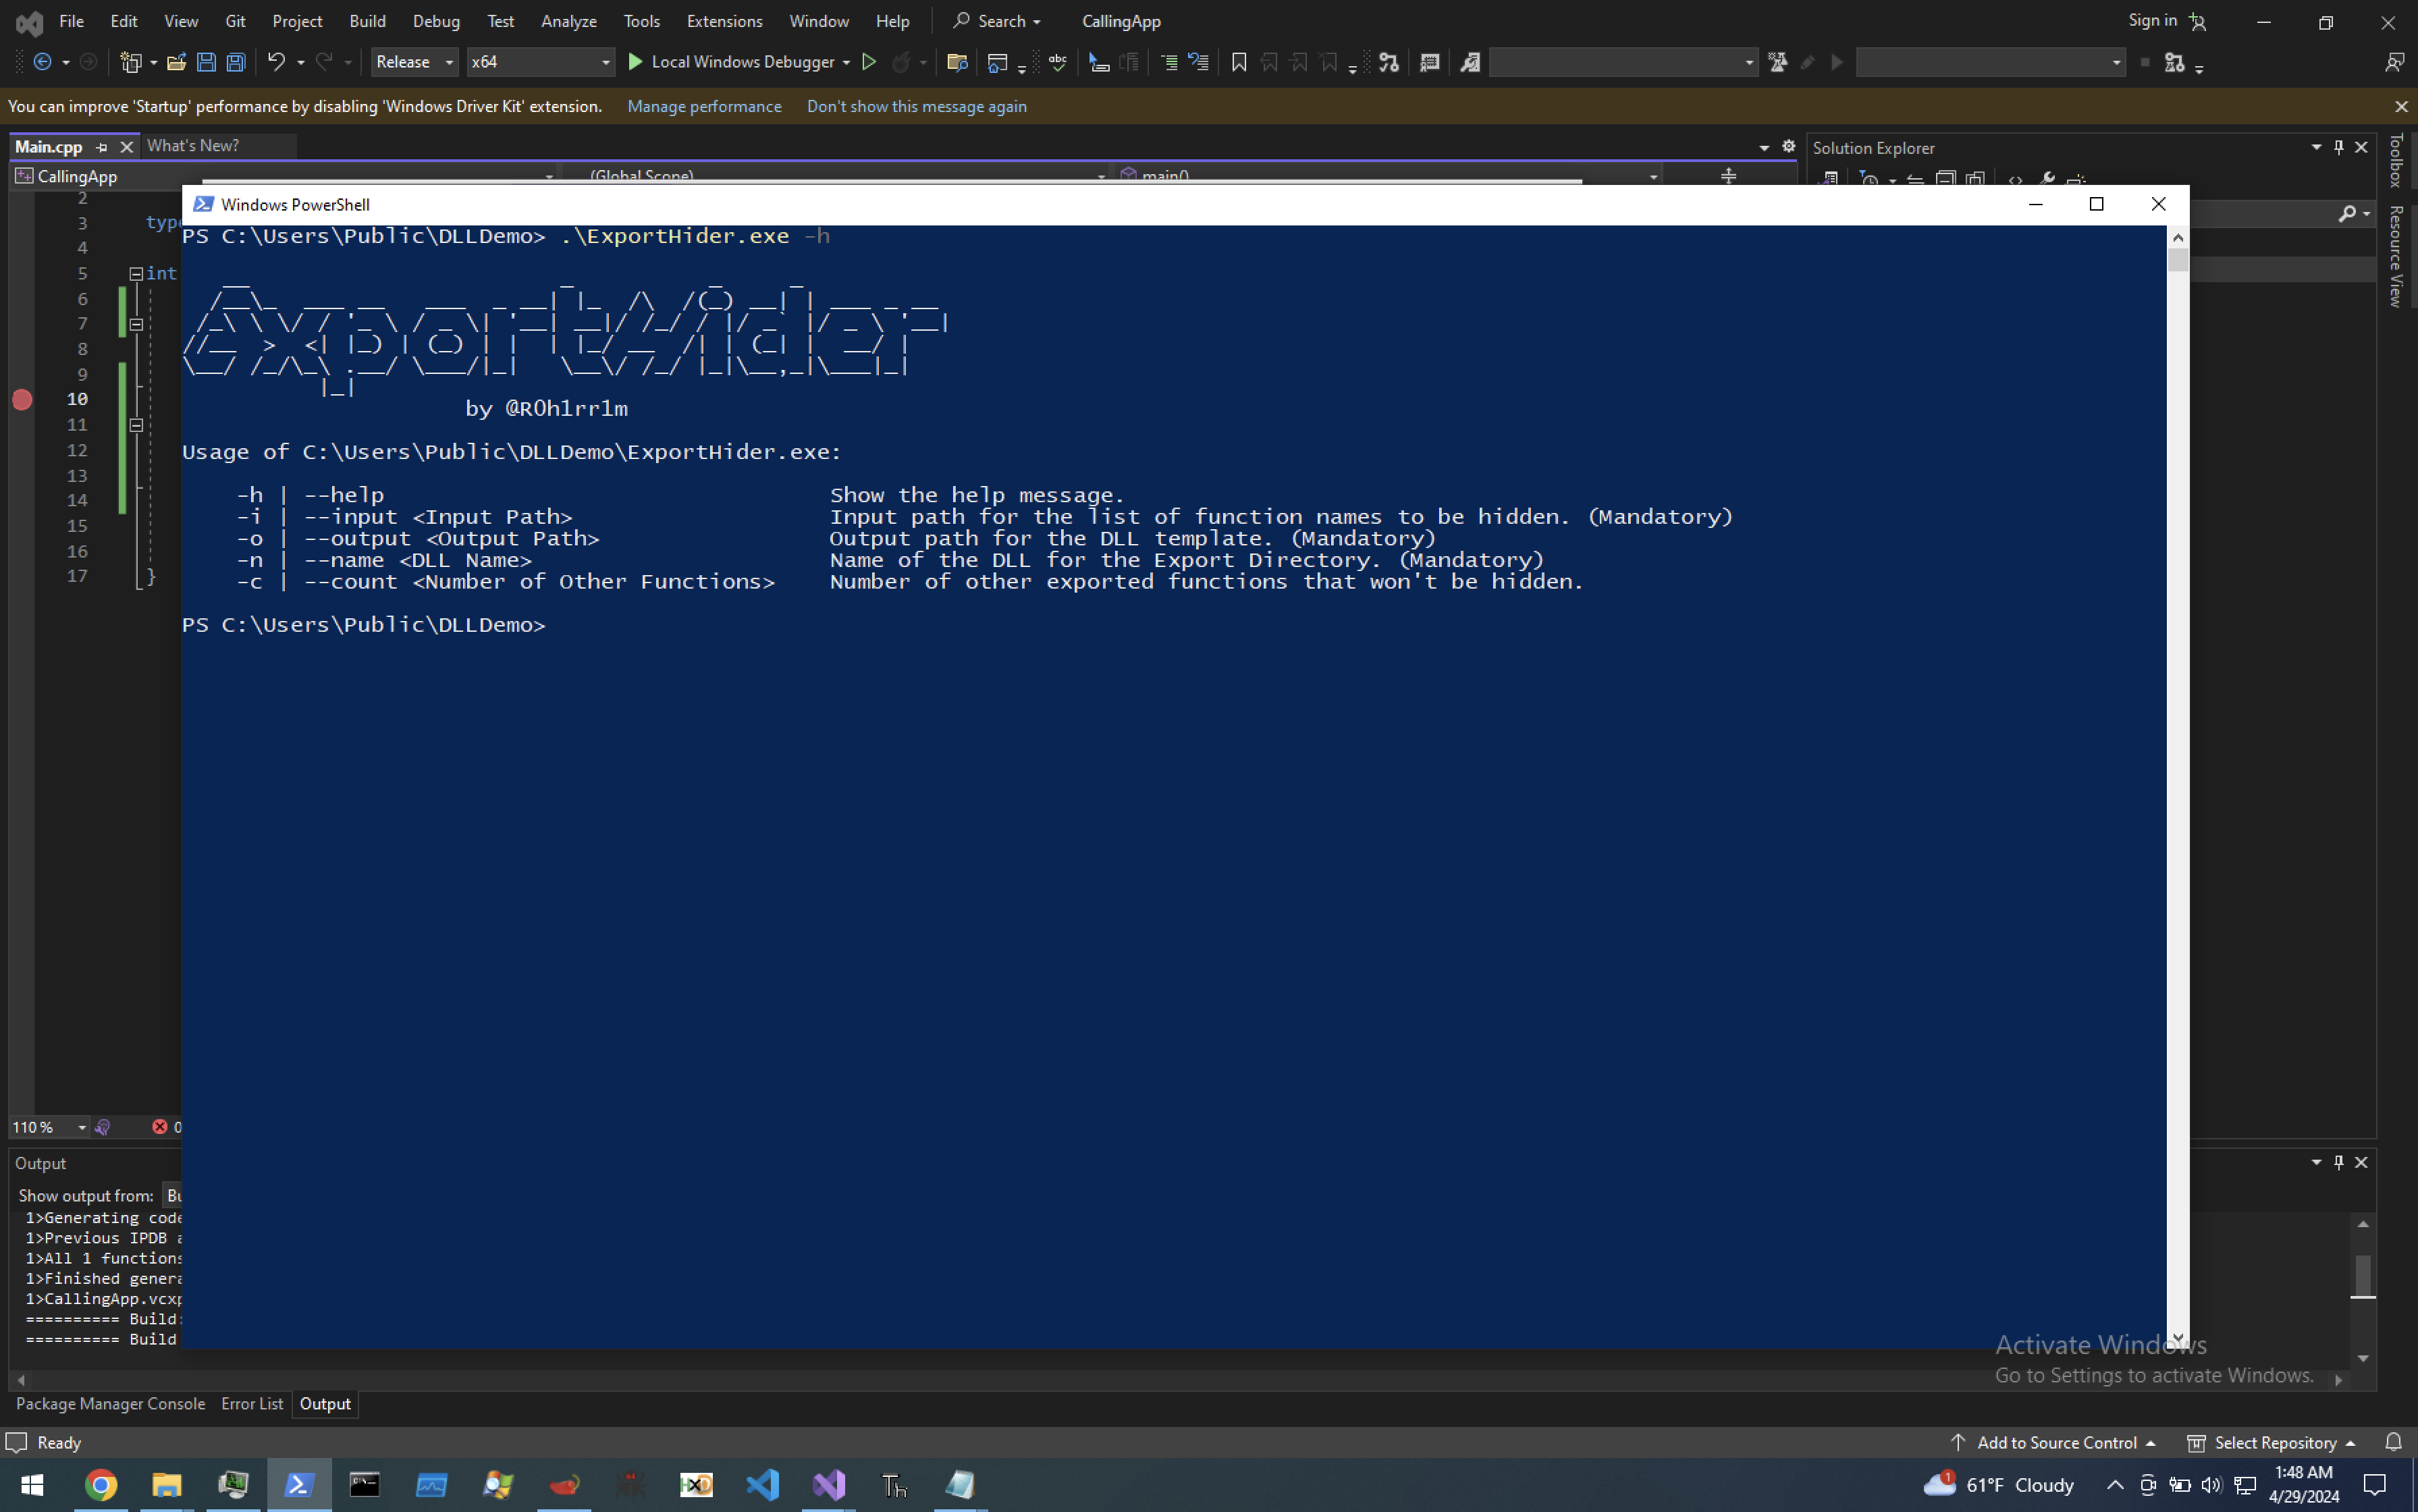 frkngksl/exporthider
ExportHider: Generating Export Table during Runtime to Hide the Exported Functions from the DLL File.
 zxgio/ghidra_stack_strings
A script to detect stack-strings by using emulation (leveraging Unicorn)
 aftermathlabs/vmp2
Unpack and deobfuscate VMProtect 2 protected binaries with an emulation-based VM explorer, handler profiler, and experimental LLVM recompiler for…
 sentinel-one/peafl64
Static Binary Instrumentation tool for Windows x64 executables
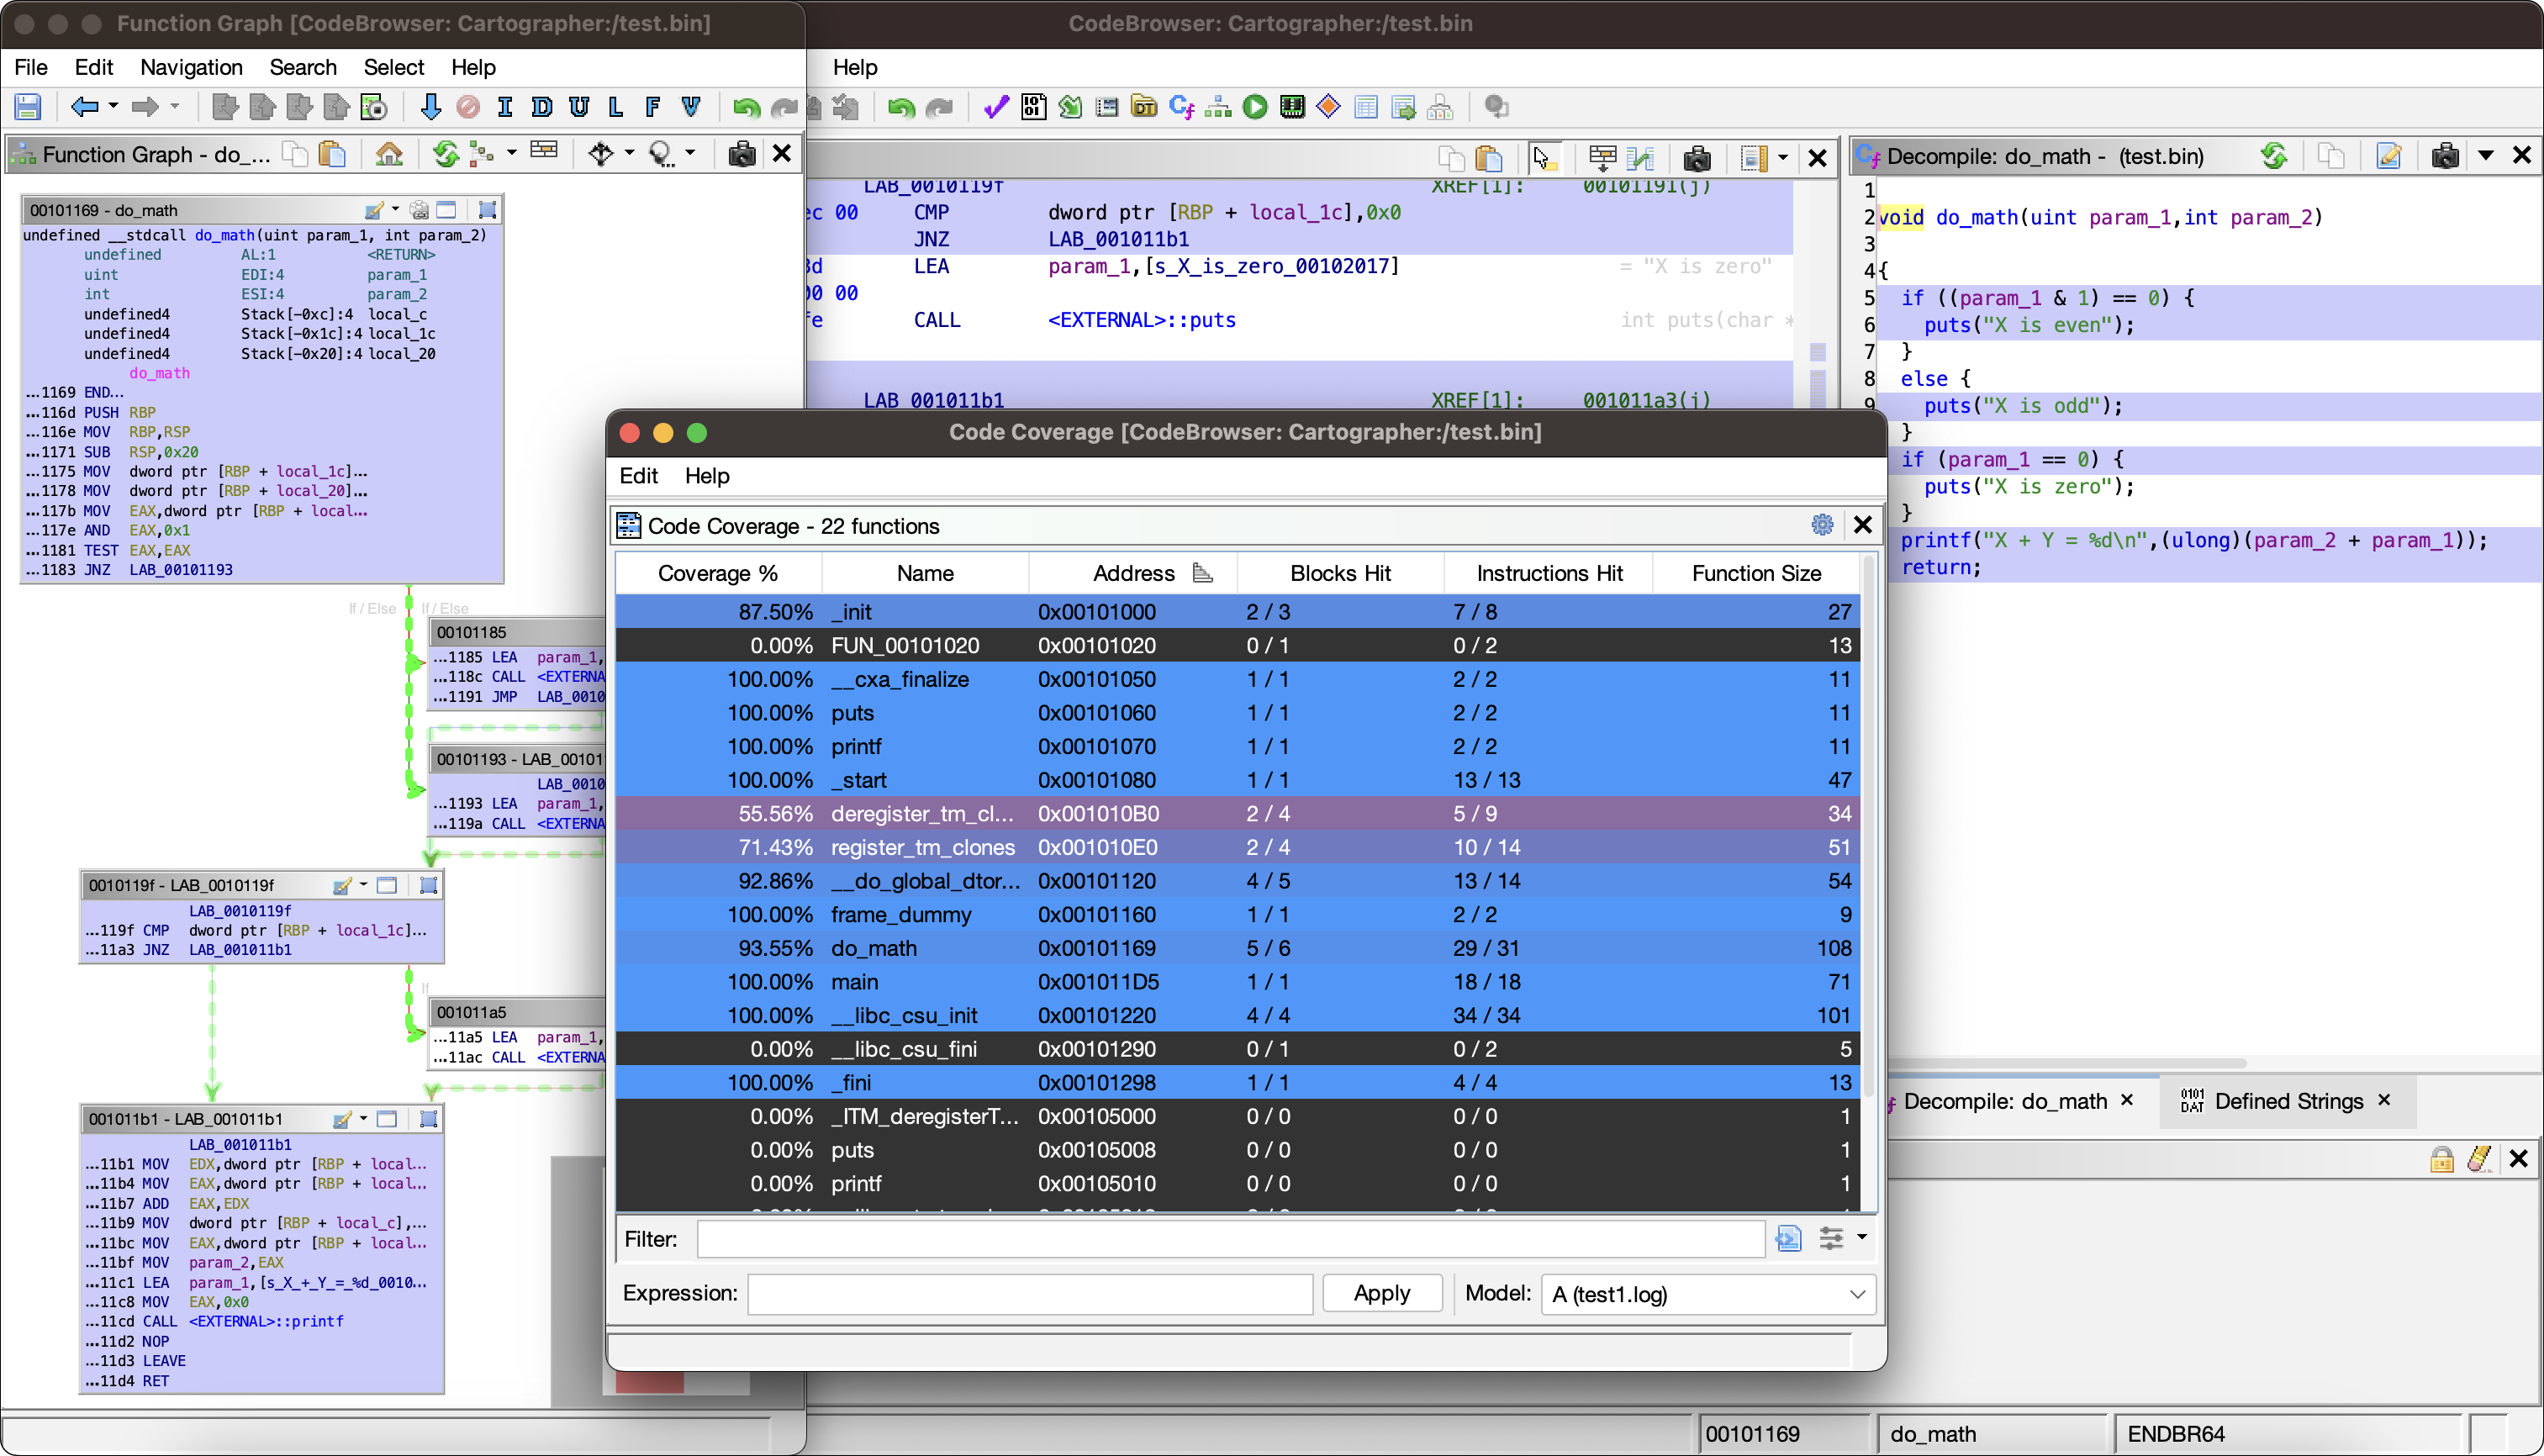 nccgroup/cartographer
Code Coverage Exploration Plugin for Ghidra
 hasherezade/pesieve-go
Golang bindings for PE-sieve
 zer0condition/reversekit
x64 Dynamic Reverse Engineering Toolkit
 redteamsocietegenerale/dllirant
DLLirant is a tool to automatize the DLL Hijacking researches on a specified binary.
 void-stack/vmunprotect.dumper
VMUnprotect.Dumper can dynamically untamper VMProtected Assembly.
 tca-iscas/cooper-ndss-2022
A tool for effective testing the binding layer of scripting languages