
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Binary Analysis — Tools — Page 2 | Kitploit

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
1205 results
z3 preview

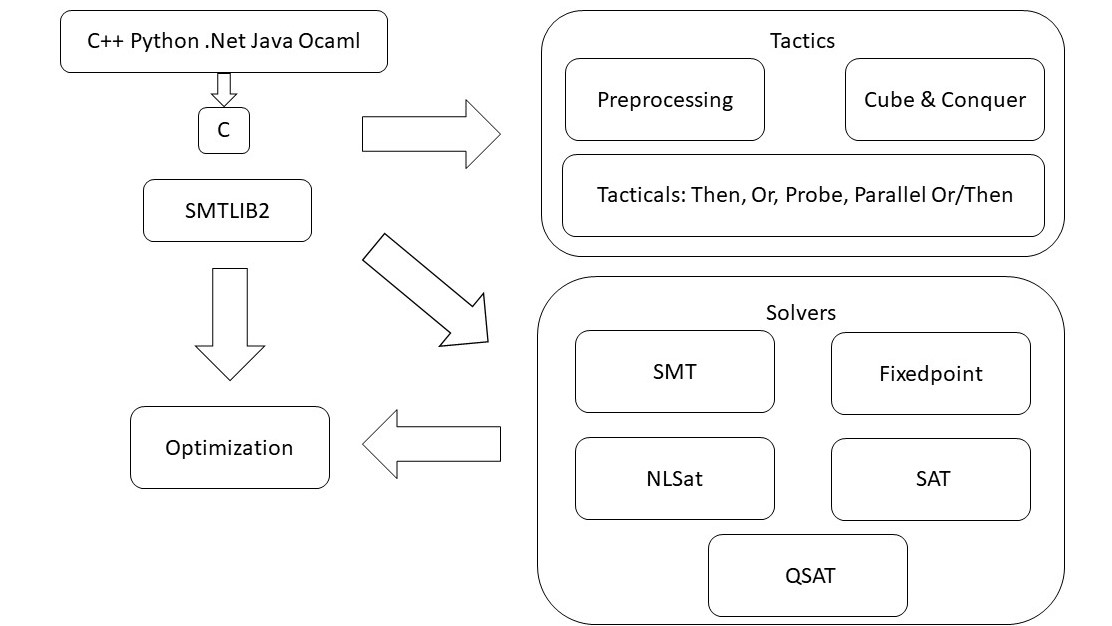
z3

GitHubz3prover/z3

High-performance SMT solver for automated theorem proving, constraint solving, and program verification. Supports multiple theories and language…

static-analysiscryptographybinary-analysis+2
12.5k11h 6m ago
unblob preview

unblob

GitHubonekey-sec/unblob

Extract files from any kind of container formats

embedded-systems-securityreverse-engineeringforensics+3
2.5k12h 38m ago
rr preview

rr

GitHubrr-debugger/rr

Record and replay framework for deterministic debugging of multi-threaded applications, enabling reverse execution, hardware watchpoints, and…

dynamic-code-analysisdebuggersbinary-analysis
10.7k17h 15m ago
Brovan preview

Brovan

GitHubadvdebug/brovan

User-mode x86_64 binary emulator for malware analysis and reverse engineering. Supports PE, ELF, memory dumps, and raw binaries with syscall tracing,…

dynamic-analysis-sandboxingdynamic-code-analysisreverse-engineering+3
15519h 39m ago
dezlock-dump preview

dezlock-dump

GitHubdougwithseismic/dezlock-dump

Runtime schema + RTTI extraction tool for Deadlock, CS2, Dota, and others (Source 2). No source2gen required.

reconnaissancememory-forensicsdynamic-code-analysis+6
8221h 51m ago
capstone preview

capstone

GitHubcapstone-engine/capstone

Multi-architecture disassembly framework providing a lightweight, thread-safe API for binary analysis, reverse engineering, and malware research…

embedded-systems-securitystatic-analysisreverse-engineering+7
8.9k0 days ago
LIEF preview

LIEF

GitHublief-project/lief

Cross-platform library to parse, modify, and abstract ELF, PE, and MachO executable formats. Supports C++, Python, and Rust APIs with disassembler,…

android-securityembedded-systems-securitystatic-analysis+12
5.5k0 days ago
asmsense preview

asmsense

GitHubkrxi/asmsense

Small language model that names and describes functions in stripped x86-64 binaries, with an open dataset, baselines, and LoRA fine-tuning…

static-analysisreverse-engineeringbinary-analysis+6
161 day ago
raptor preview

raptor

GitHubgadievron/raptor

Autonomous security research framework integrating static analysis, binary analysis, fuzzing, LLM-powered vulnerability validation, exploit…

penetration-testing-frameworksdynamic-analysis-sandboxingexploit-frameworks+7
3.6k1 day ago
Reverse-Engineering preview

Reverse-Engineering

GitHubmytechnotalent/reverse-engineering

A FREE comprehensive reverse engineering tutorial covering x86, x64, 32-bit/64-bit ARM, 8-bit AVR and 32-bit RISC-V architectures.
embedded-systems-securityreverse-engineeringdebuggers+5
14.1k1 day ago
windiff preview

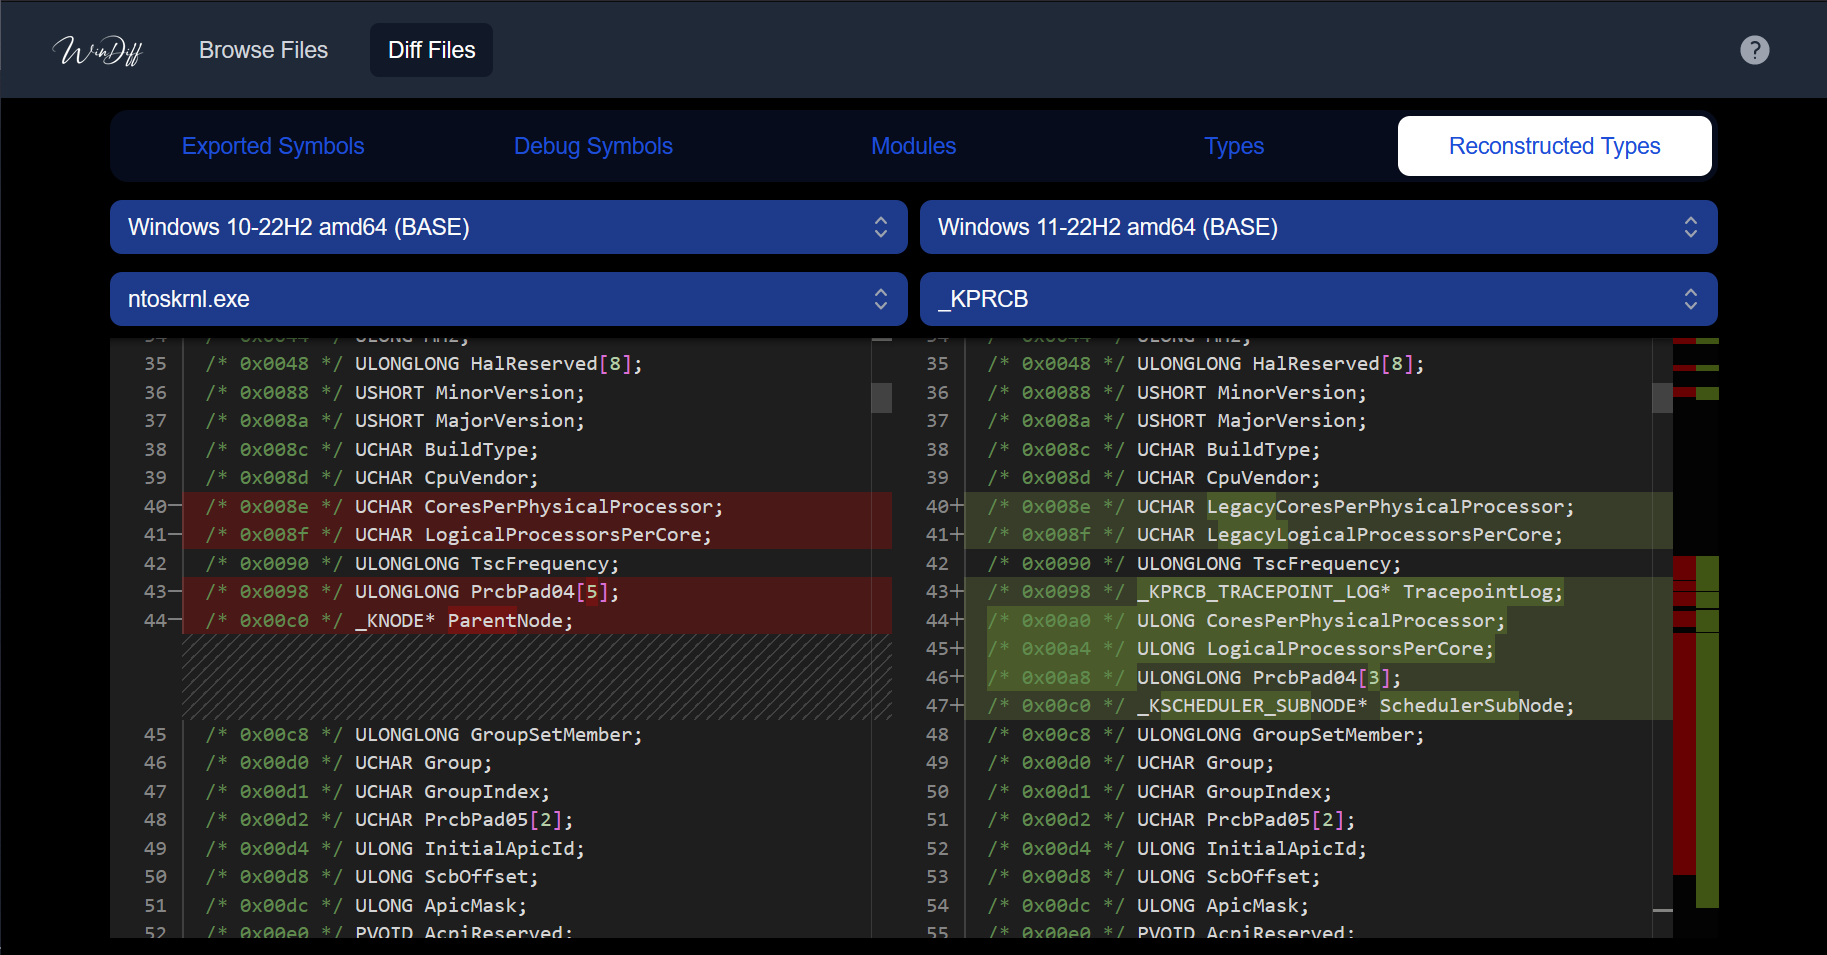
windiff

GitHubergrelet/windiff

Tool that allows comparing symbol, type and syscall information of Microsoft Windows binaries across different versions of the OS, using a Web UI…

vulnerability-analysisreverse-engineeringinformation-gathering+1
3921 day ago
frida preview

frida

GitHubfrida/frida

Main repo for hosting release binaries

android-securitydynamic-analysis-sandboxingios-security+9
21.4k1 day ago
x64dbg preview

x64dbg

GitHubx64dbg/x64dbg

An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.

static-analysisdynamic-analysis-sandboxingmemory-forensics+7
49.1k1 day ago
mwemu preview

mwemu

GitHubmwemuorg/mwemu

Pure Rust x86 hardware emulator and Windows process simulator for malware analysis, shellcode emulation, and payload unpacking. Supports 32/64-bit PE…

exploit-frameworksreverse-engineeringshellcode+2
3131 day ago
semgrep-rules preview

semgrep-rules

GitHub0xdea/semgrep-rules

A collection of my Semgrep rules to facilitate vulnerability research.

static-code-analysisvulnerability-analysiscode-analysis+3
8661 day ago
dynamorio preview

dynamorio

GitHubdynamorio/dynamorio

Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
code-analysisdynamic-code-analysisreverse-engineering+3
3.2k1 day ago
chimera preview

chimera

GitHubpenberg/chimera

Sandbox untrusted code with safe access to the host.

dynamic-analysis-sandboxingcode-analysissecurity-virtualization+3
1231 day ago
wrongsecrets-binaries preview

wrongsecrets-binaries

GitHubowasp/wrongsecrets-binaries

Source code for the Binaries of OWASP WrongSecrets

static-analysisvulnerability-analysiscode-analysis+6
111 day ago
Previous123…67Next