

pwndbg
 pwndbg/pwndbg
Exploit Development and Reverse Engineering with GDB & LLDB Made Easy
embedded-systems-securitystatic-analysismemory-forensics+12
pwndbg/pwndbgExploit Development and Reverse Engineering with GDB & LLDB Made Easy
 rr-debugger/rr
Record and replay framework for deterministic debugging of multi-threaded applications, enabling reverse execution, hardware watchpoints, and…
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 icsharpcode/ilspy
.NET Decompiler with support for PDB generation, ReadyToRun, Metadata (&more) - cross-platform!
 dougwithseismic/dezlock-dump
Runtime schema + RTTI extraction tool for Deadlock, CS2, Dota, and others (Source 2). No source2gen required.
 attify/firmware-analysis-toolkit
Firmware security research platform combining binary analysis, taint tracing, and emulation across IoT, edge AI, mobile devices, and robotics.
 capstone-engine/capstone
Multi-architecture disassembly framework providing a lightweight, thread-safe API for binary analysis, reverse engineering, and malware research…
 lief-project/lief
Cross-platform library to parse, modify, and abstract ELF, PE, and MachO executable formats. Supports C++, Python, and Rust APIs with disassembler,…
 rizinorg/rizin
UNIX-like reverse engineering framework and command-line toolset.
 krxi/asmsense
Small language model that names and describes functions in stripped x86-64 binaries, with an open dataset, baselines, and LoRA fine-tuning…
 advdebug/brovan
User-mode x86_64 binary emulator for malware analysis and reverse engineering. Supports PE, ELF, memory dumps, and raw binaries with syscall tracing,…
 gadievron/raptor
Autonomous security research framework integrating static analysis, binary analysis, fuzzing, LLM-powered vulnerability validation, exploit…
 momo5502/sogen
🪅 Windows & Linux userspace emulator
 mytechnotalent/reverse-engineering
A FREE comprehensive reverse engineering tutorial covering x86, x64, 32-bit/64-bit ARM, 8-bit AVR and 32-bit RISC-V architectures.
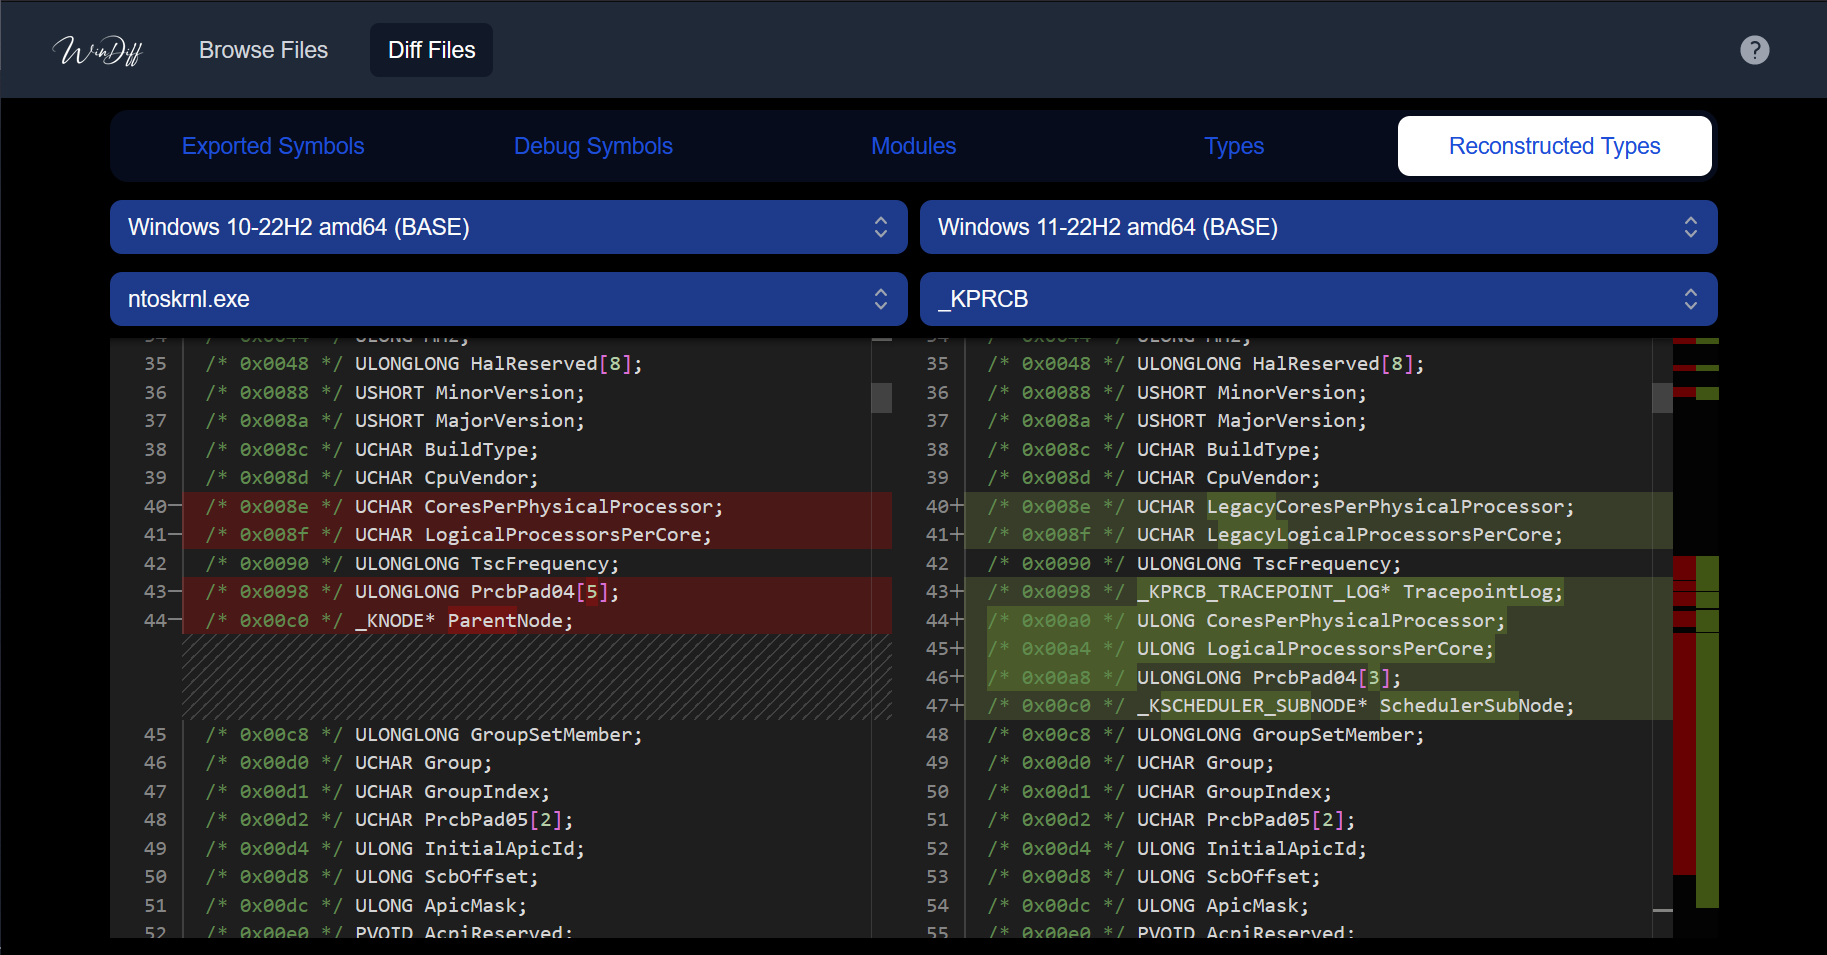 ergrelet/windiff
Tool that allows comparing symbol, type and syscall information of Microsoft Windows binaries across different versions of the OS, using a Web UI…
 horsicq/detect-it-easy
Program for determining types of files for Windows, Linux and MacOS.
 frida/frida
Main repo for hosting release binaries
 x64dbg/x64dbg
An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.