
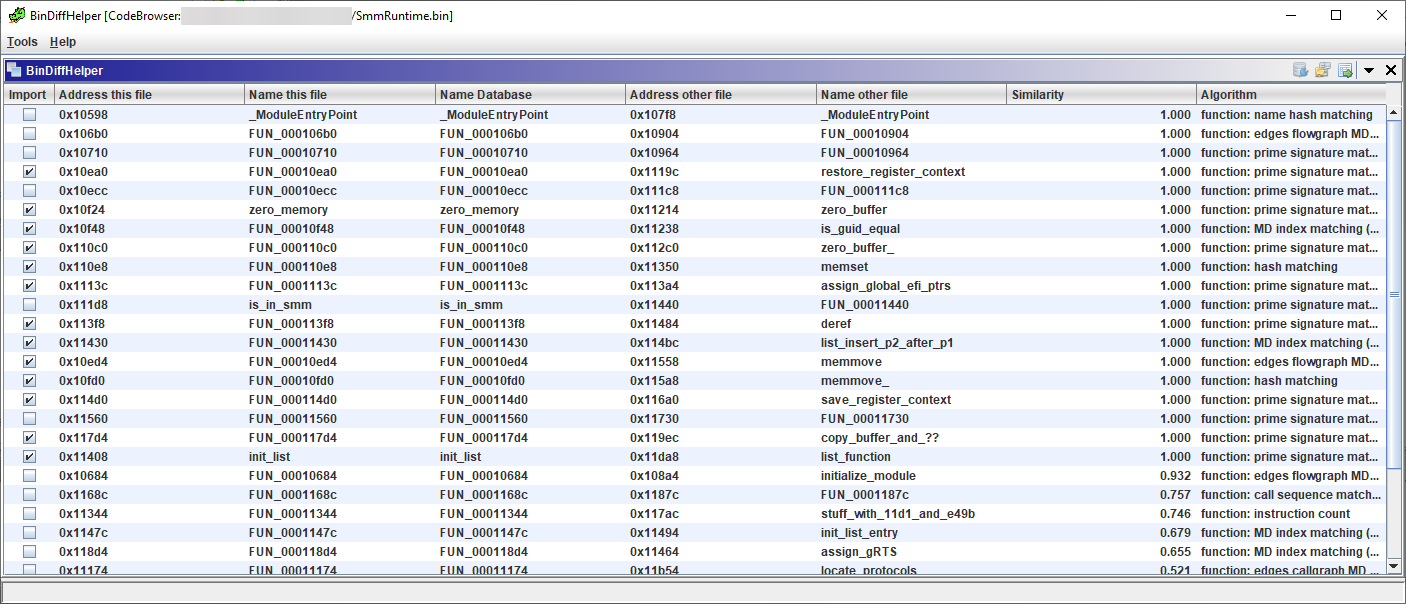
BinDiffHelper
 ubfx/bindiffhelper
Ghidra Extension to integrate BinDiff for function matching
binary-analysisbinary-exploitationcode-analysis+4
29622 days ago
ubfx/bindiffhelperGhidra Extension to integrate BinDiff for function matching
 gmh5225/kernelmode-driver
Kernel Driver for x64 Window System which allows you to read/write Virtual/Physical Memory hooking Win32k
 gmh5225/keypatchx
KeyPatch Enhanced — IDA Pro plugin for symbol-aware x86/x64 assembly patching, powered by Keystone Engine. Fork of Keypatch with automatic IDA symbol…
 gmh5225/kli-ex
Extended kernel lazy importer for Windows drivers that resolves APIs at runtime with encrypted, cached import names to hide kernel function usage…
 kaandemir993/python-shellcode-anydesk-apc-injection-remote-ip-address-analysis
Reverse engineering write-up of Python shellcode that APC-injects into AnyDesk, exfiltrates to a C2 over HTTPS with AES/RSA, and persists via…
 vvirei333/abrake27
iOS 27 kernelcache RE: SEP dispatch map, AMFI diff, Ghidra workflow
 frida/frida-gum
Cross-platform instrumentation and introspection library written in C
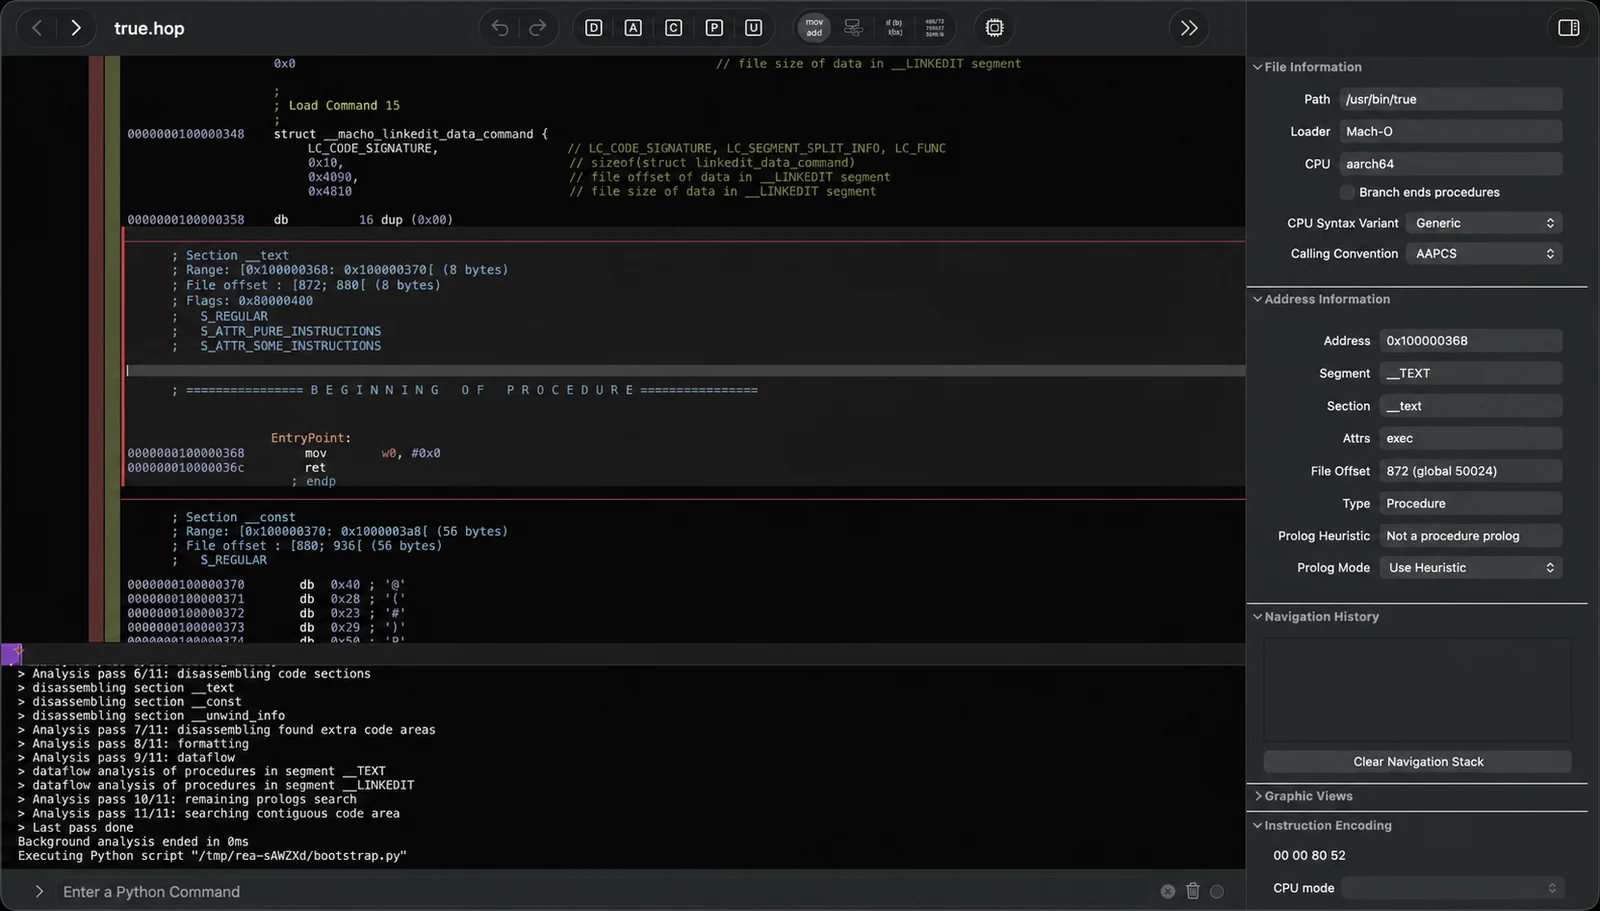 morluto/rea
Reverse engineer anything with agents, from app behavior down to native binaries.
 xf1les/fsop-finder
Binary Ninja plugin that scans glibc libio for FSOP code paths capable of hijacking control flow and stack pointer, aiding heap exploitation research.
 therealsaumil/static-arm-bins
Statically compiled ARM binaries for debugging and runtime analysis
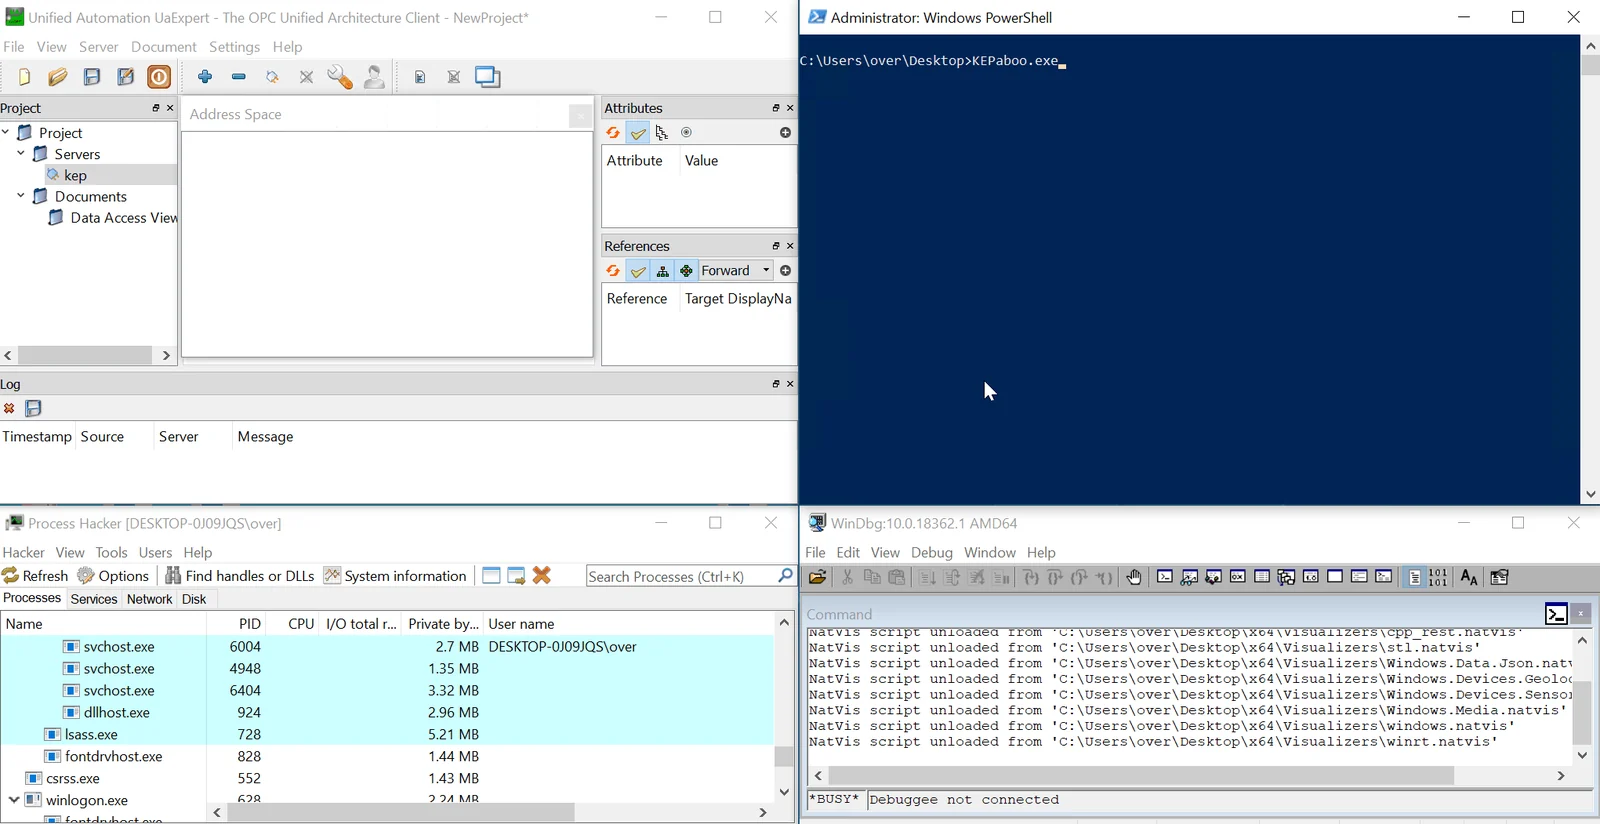 0vercl0k/kepaboo
Neutralize KEPServerEX anti-debugging techniques
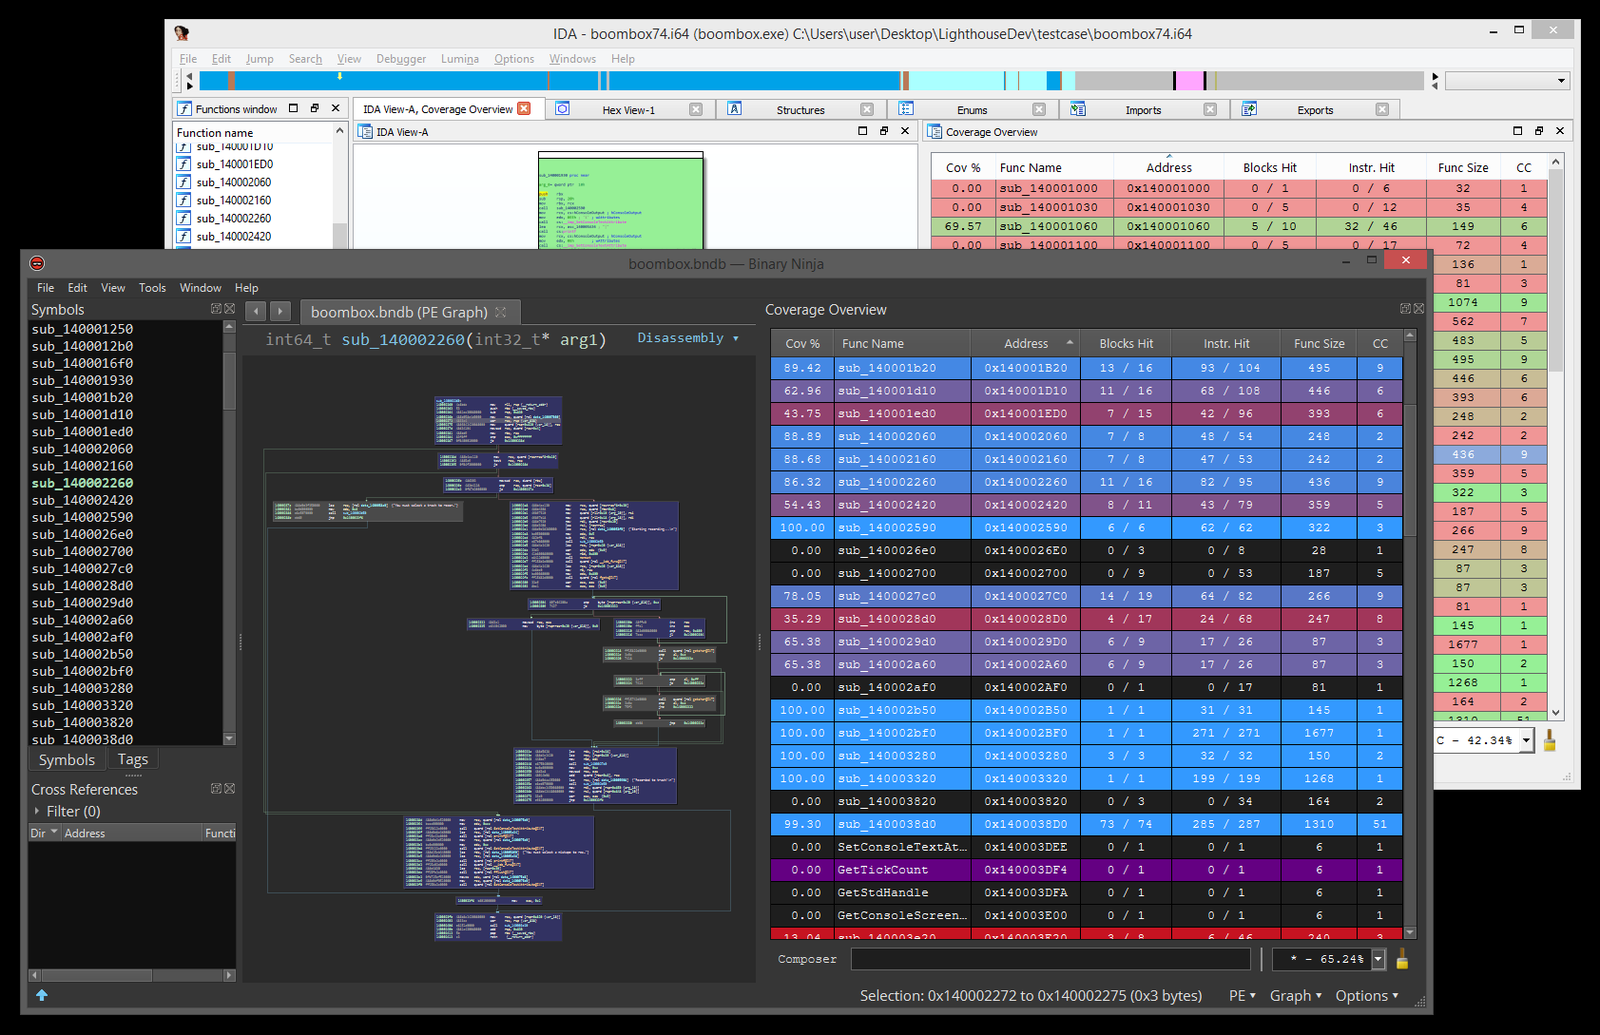 gaasedelen/lighthouse
A Coverage Explorer for Reverse Engineers
 googleprojectzero/jackalope
Binary, coverage-guided fuzzer for Windows, macOS, Linux and Android
 volexity/donut-decryptor
Extracts and decrypts inner payloads from Donut obfuscator samples by detecting loader shellcode signatures, parsing the DONUT_INSTANCE structure,…
 trustedsec/lazzzy_dump
Statically extracts and decrypts AES-CBC/XOR-obfuscated shellcode from laZzzy-wrapped PE binaries via signature matching and RIP-relative address…
 ejfkdev/jscd
Reverse bytenode .jsc (V8 code cache) to JavaScript — static, pure Rust, no patched V8/Node. Node 8→26 / V8 5.8–14.6; 25k .jsc tested, 0 fail.
 superkhung/luadec-tplink
Modified luadec version to decompile TP-Link Archer C7 LUA firmware.