
no-access-protection-x86
 gmh5225/no-access-protection-x86
It encrypts the text section and set the protection to NO_ACCESS.
anti-botbinary-analysisdefensive-tools+4
1
gmh5225/no-access-protection-x86It encrypts the text section and set the protection to NO_ACCESS.
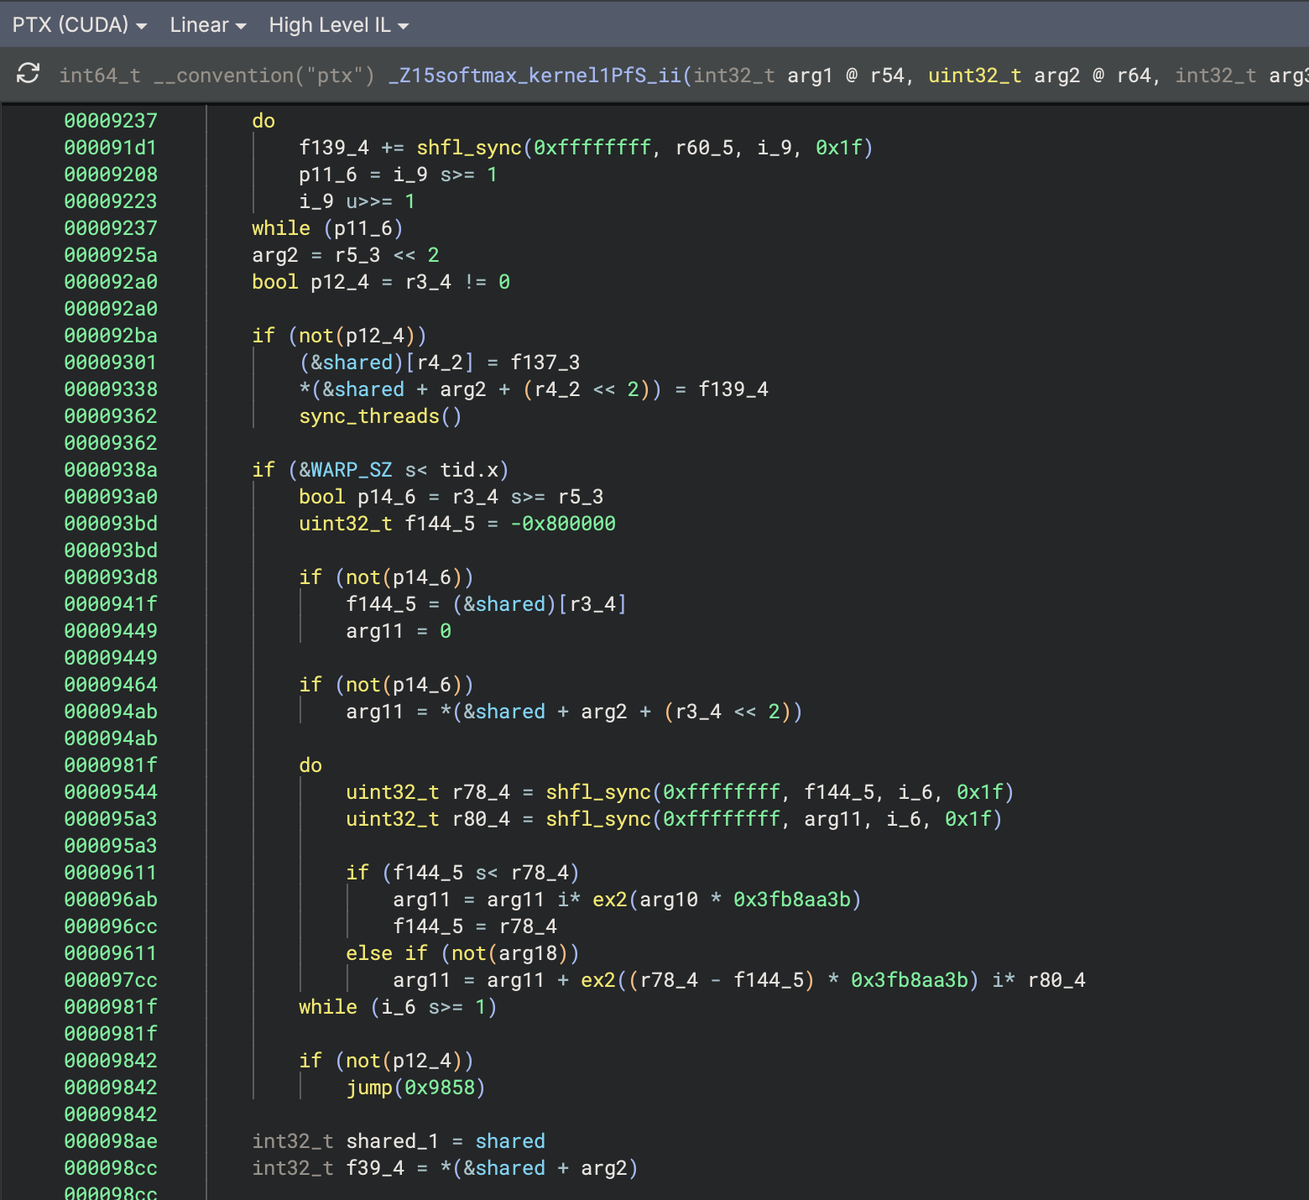 seekbytes/ptxninja
Binary Ninja plugin for reverse engineering PTX -- the virtual instruction set architecture of CUDA-based GPUs.
 withsecurelabs/garbageman
GarbageMan is a set of tools for analyzing .NET binaries through heap analysis.
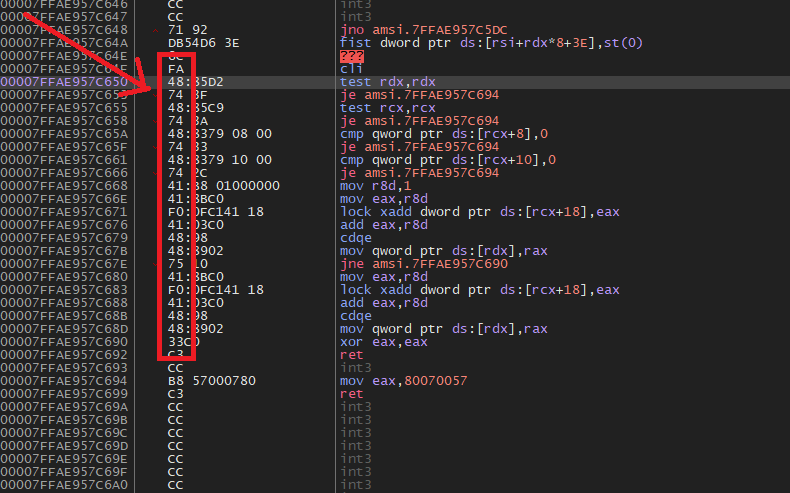 zeromemoryex/amsi-killer
Lifetime AMSI bypass
 nccgroup/asafw
Set of scripts to deal with Cisco ASA firmware [pack/unpack etc.]
 nccgroup/blackboxprotobuf
Blackbox Protobuf is a set of tools for working with encoded Protocol Buffers (protobuf) without the matching protobuf definition.
 denuvosoftwaresolutions/simba
Efficient Deobfuscation of Linear Mixed Boolean-Arithmetic Expressions
 trailofbits/gosentry
Security-oriented Go toolchain, focused on state-of-the-art fuzzing capabilities.
 theqmaks/phantom-frida
Build anti-detection Frida server from source. ~90 patches covering 16 detection vectors, weekly auto-builds with random names.
 mistymntncop/cve-2023-4863
Proof-of-concept for CVE-2023-4863, a heap buffer overflow in WebP image decoding. Demonstrates the code_lengths trigger mechanism discovered by…
 hugsy/gef
GEF (GDB Enhanced Features) - a modern experience for GDB with advanced debugging capabilities for exploit devs & reverse engineers on Linux
 kevinbackhouse/djvulibre-poc-cve-2025-53367
Proof-of-concept exploit for CVE-2025-53367, a vulnerability in the DjVuLibre library. Demonstrates exploitation of a memory corruption bug in DjVu…
 duality084/cve-2023-33381-mitrastar-gpt-2741gnac
Proof-of-concept exploit for OS command injection (CVE-2023-33381) in MitraStar GPT-2741GNAC routers. Demonstrates bypass of restricted shell via…
 theopolis/uefi-firmware-parser
Parse BIOS/Intel ME/UEFI firmware related structures: Volumes, FileSystems, Files, etc
 b2r2-org/b2r2
B2R2 is a fully managed binary analysis framework written in F#. It provides a rich set of algorithms, functions, and tools for reverse engineering,…
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
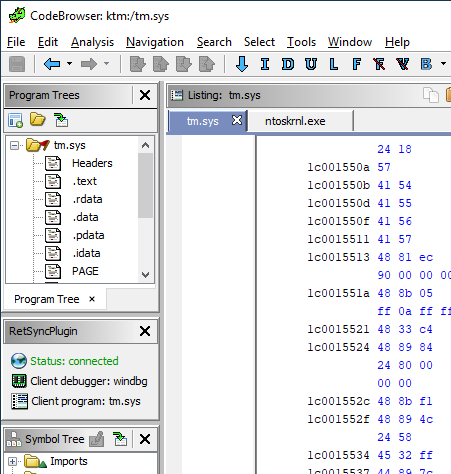 bootleg/ret-sync
ret-sync is a set of plugins that helps to synchronize a debugging session (WinDbg/GDB/LLDB/OllyDbg2/x64dbg) with IDA/Ghidra/Binary Ninja…
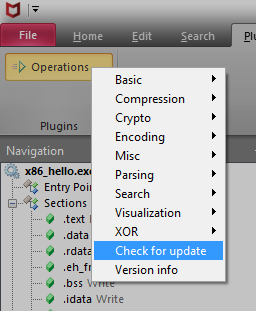 nmantani/fileinsight-plugins
FileInsight-plugins: decoding toolbox of McAfee FileInsight hex editor for malware analysis