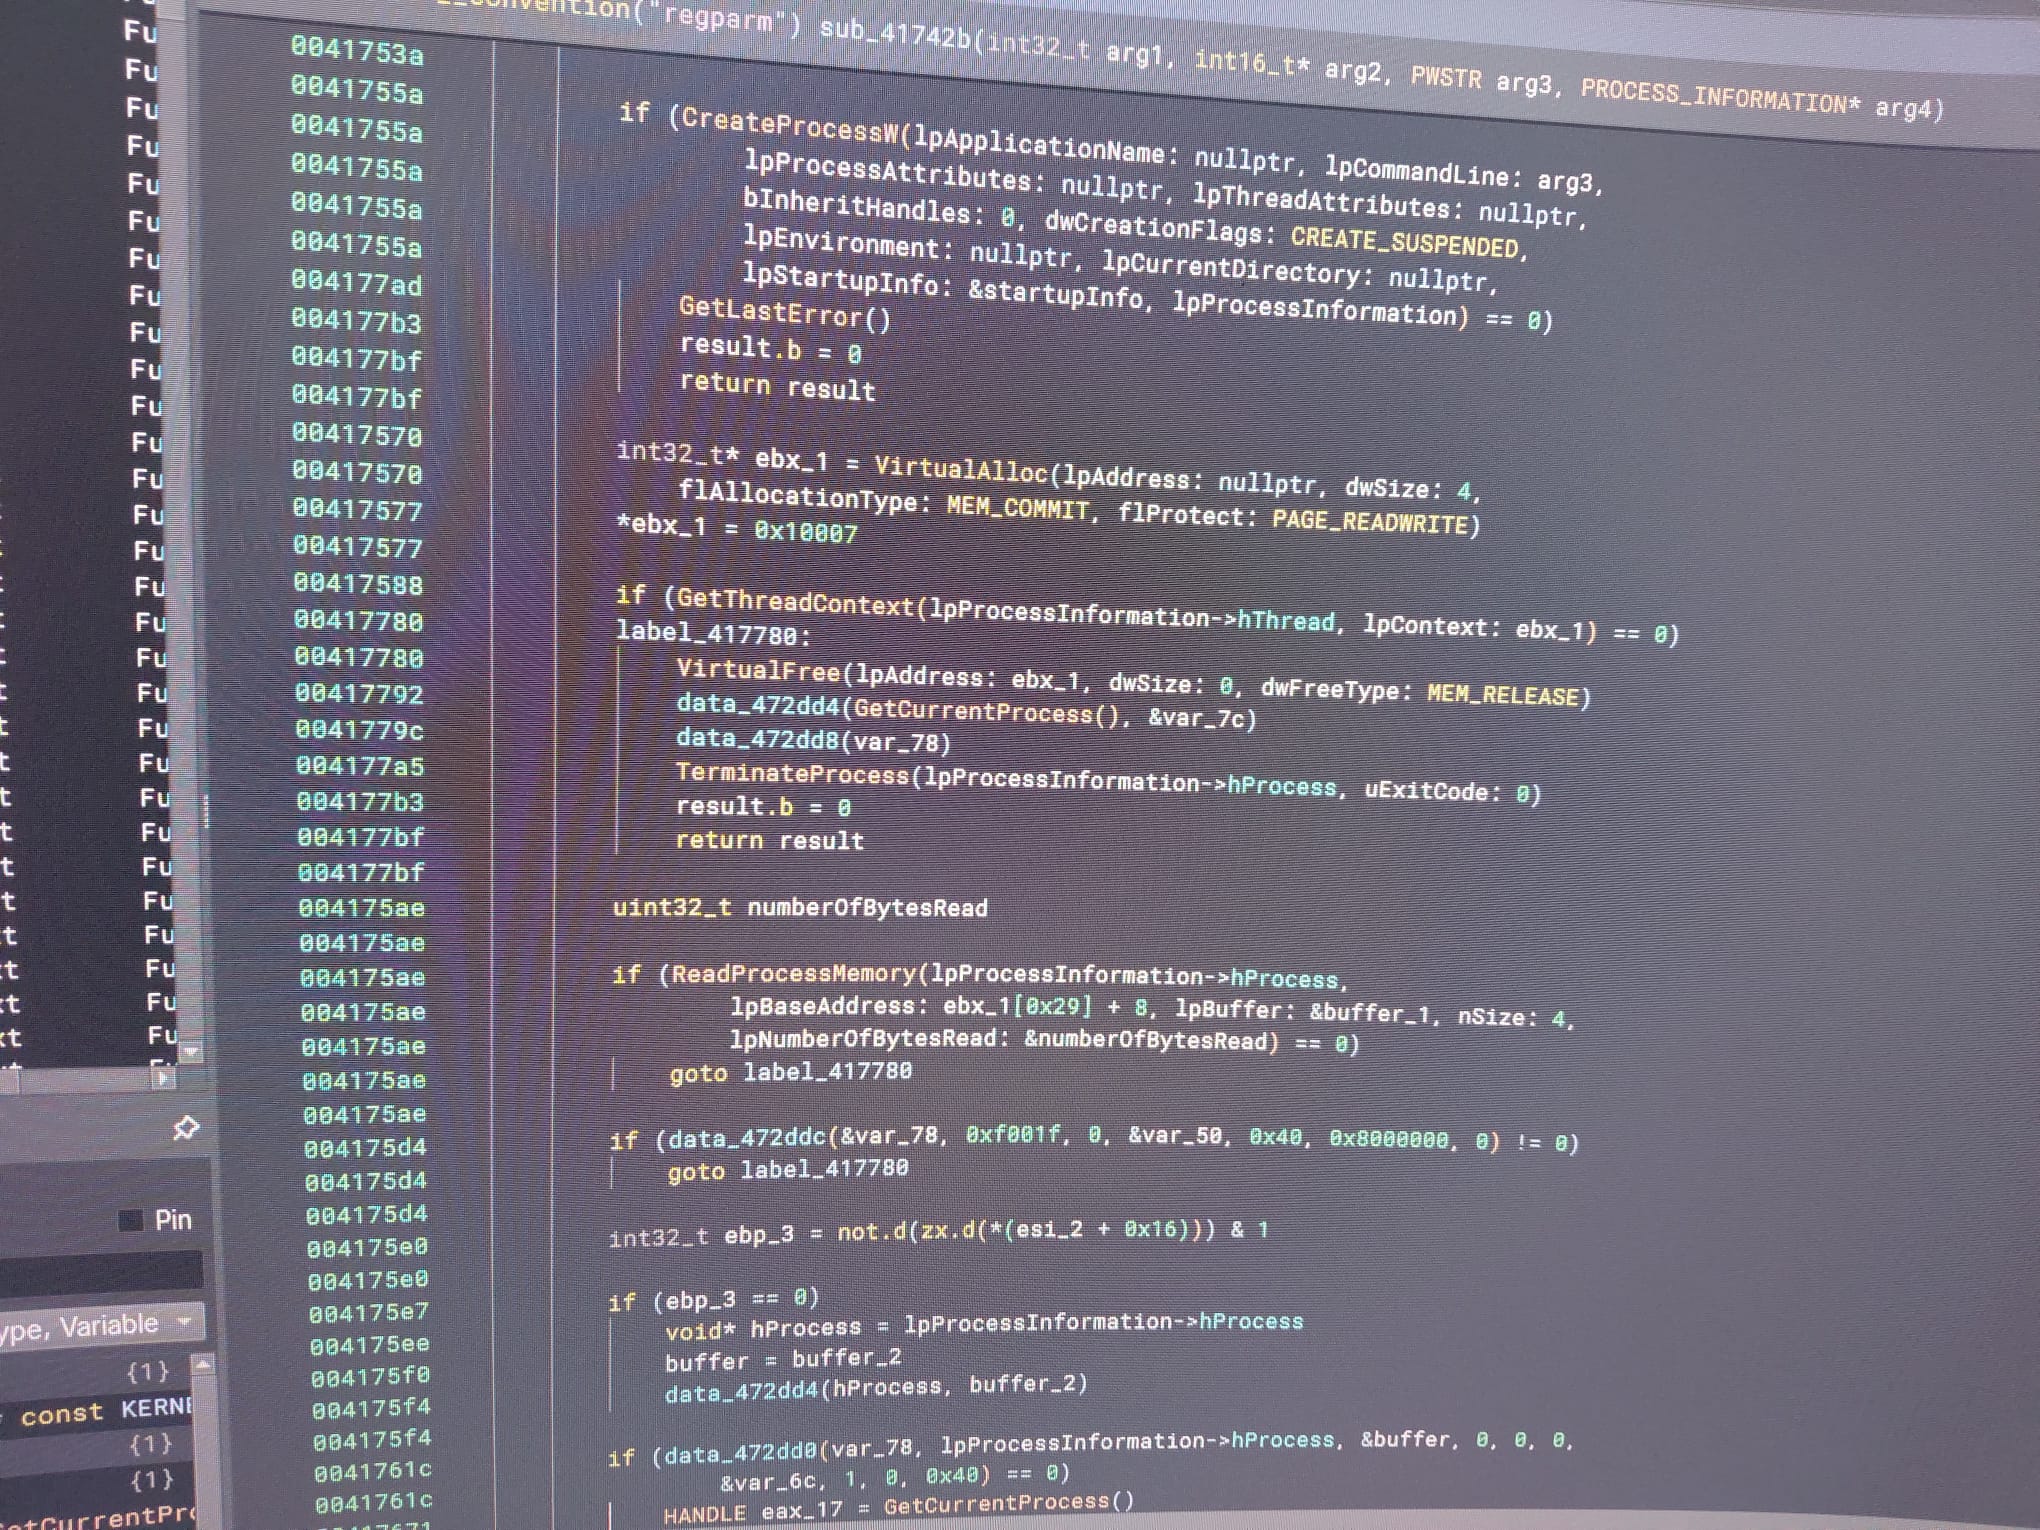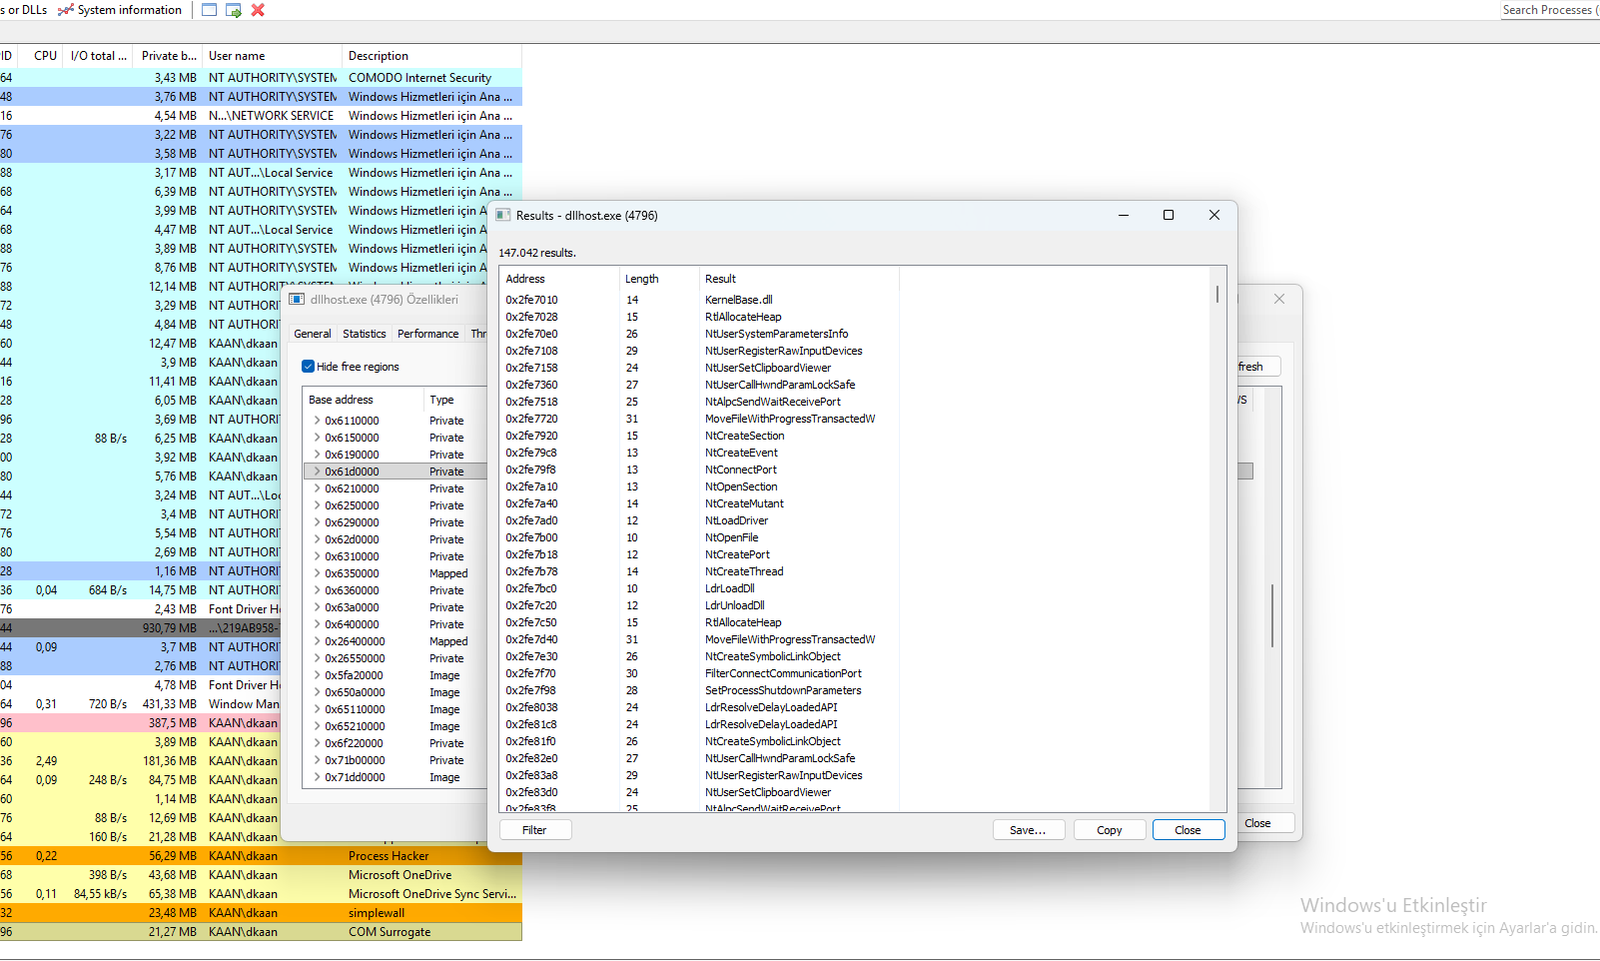
Lumma-Stealer-dllhost-Hollowing-C2-Domains-Payload-Extraction-Analysis

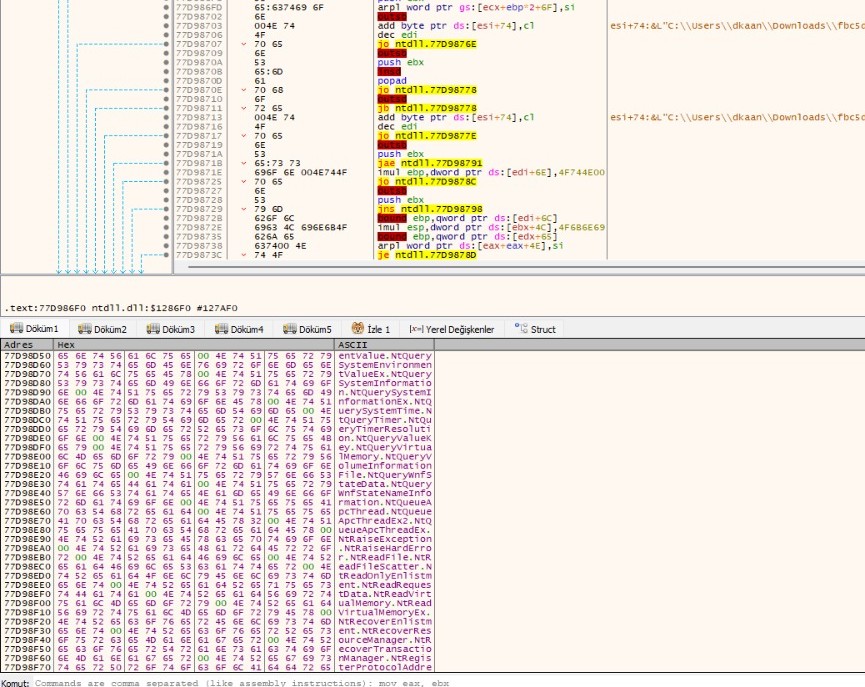
In-depth reverse engineering analysis of Lumma Stealer, an info-stealer using process hollowing, Native API calls, and C2 communication. Includes…

In-depth reverse engineering analysis of Lumma Stealer, an info-stealer using process hollowing, Native API calls, and C2 communication. Includes…

Reverse-engineered runtime engine for Roblox/Luau with VM hooking, opcode remapping, capability escalation, and UNC script environment for executing…

Proxies sensitive API calls from shellcode to artifacts for CET-compatible clean call stacks, enabling stealthy payload execution and call stack…

Reverse engineering analysis of Dropper GCleaner, a malware that uses a resilient C2 infrastructure, kernel driver loading, PowerShell/Conhost…

"Reverse engineering analysis of Agent Tesla, a .NET-based info-stealer that uses APC injection, token manipulation, and registry persistence.…

Simulates the Windows PE loader to identify DLL hijacking vulnerabilities, generates weaponized DLLs with shellcode payloads, and detects UAC…

Run Beacon Object Files (BOFs) outside Cobalt Strike by parsing 64-bit COFF object files, with Beacon-compatible argument generation and helper…

Static analysis walkthrough of a Metasploit Windows shellcode: PowerShell payload decoding, XOR obfuscation, PEB walking, and Export Address Table…

Generate a proxy dll for arbitrary dll

Lnk crafting and research tools

DLL sideloading/proxying with Nim!

Sickle - Payload Development Kit

Some Rust program I wrote while learning Malware Development

CVE 2025 27237 Zabbix LPE proof of concept.

A bin2bin code virtualizer for x86-64 PE's

Microsoft-Office-Word-MSHTML-Remote-Code-Execution-Exploit

Proof-of-concept exploit and custom payload generator for CVE-2018-5146, including crafted OGG POC file and HTML-based exploit with CRC32 calculation…

"Reverse engineering analysis of a fileless Remcos RAT variant that injects into svchost.exe via Native API calls. Covers obfuscated payload…