
luadec-tplink
 superkhung/luadec-tplink
Modified luadec version to decompile TP-Link Archer C7 LUA firmware.
binary-analysisembedded-systems-securityfirmware-analysis+4
33
superkhung/luadec-tplinkModified luadec version to decompile TP-Link Archer C7 LUA firmware.
 heapframe/seetong-ts81xxd3x-rce
CVE-2026-100886 | Unauthenticated Remote Code Execution toolkit.
 nmatt0/moria
IoT firmware identification and extraction
 whoami-012/cve-2026-96515
Technical report and authenticated reverse-shell PoC for CVE-2026-96515, a root command execution flaw in the Netlink HG323RW router's BOA diagnostic…
 themalwareguardian/uefi-security-research-howyar-sysreturn-netcopy
Post CVE-2024-7344 analysis of Howyar SysReturn NetCopy - reverse engineering notes, vulnerable binaries, vendor correspondence, and proof-of-concept…
 s1eezer/cve-2026-8069
Technical write-up and proof-of-concept for CVE-2026-8069, a local privilege escalation in Acer NitroSense and PredatorSense services, exploiting a…
 al3xtjames/ghidra-firmware-utils
Ghidra extension for PC firmware reverse engineering, providing loaders for PCI option ROMs, Intel Flash Descriptor, coreboot CBFS, and UEFI firmware…
 dsecurity/efiseek
Ghidra plugin that automates UEFI firmware analysis by identifying known GUIDs, protocols, SMI handlers, and interrupt functions, with headless…
 gdbinit/efiswissknife
IDA plugin to enhance (U)EFI binary reversing with batch analysis, GUID database, and service usage statistics for firmware security research.
 p-state/ida-efitools2
IDA plugin for extending UEFI reverse engineering capabilities
 snare/ida-efiutils
Some scripts for IDA Pro to assist with reverse engineering EFI binaries
 isukasanuj/cve-2026-85769
Proof-of-concept exploit for CVE-2026-85769, a heap out-of-bounds read in libtpms TPM 2.0 state deserialization, demonstrating denial of service via…
 pelock/crackmez3s-ctf-crackme-tutorial
How to write a CrackMe for a CTF competition. Source code, technical explanation, anti-debugging and anti reverse-engineering tricks.
 exploiteoom/cve-2026-31431
Exploit for CVE-2026-31431 that escalates privileges by altering user ID, with a verification script and mitigation instructions for the algif_aead…
 jatinkapilaq1/intel-me-research
Talk to your Intel Management Engine directly — zero-dependency Python tool. Finds memory leaks, partition manifest, live MKHI probing. First public…
 gimminse/firmware-analysis
Rediscovered CVE-2020-25279, a critical vulnerability in the Shannon baseband used in Samsung Exynos chipsets
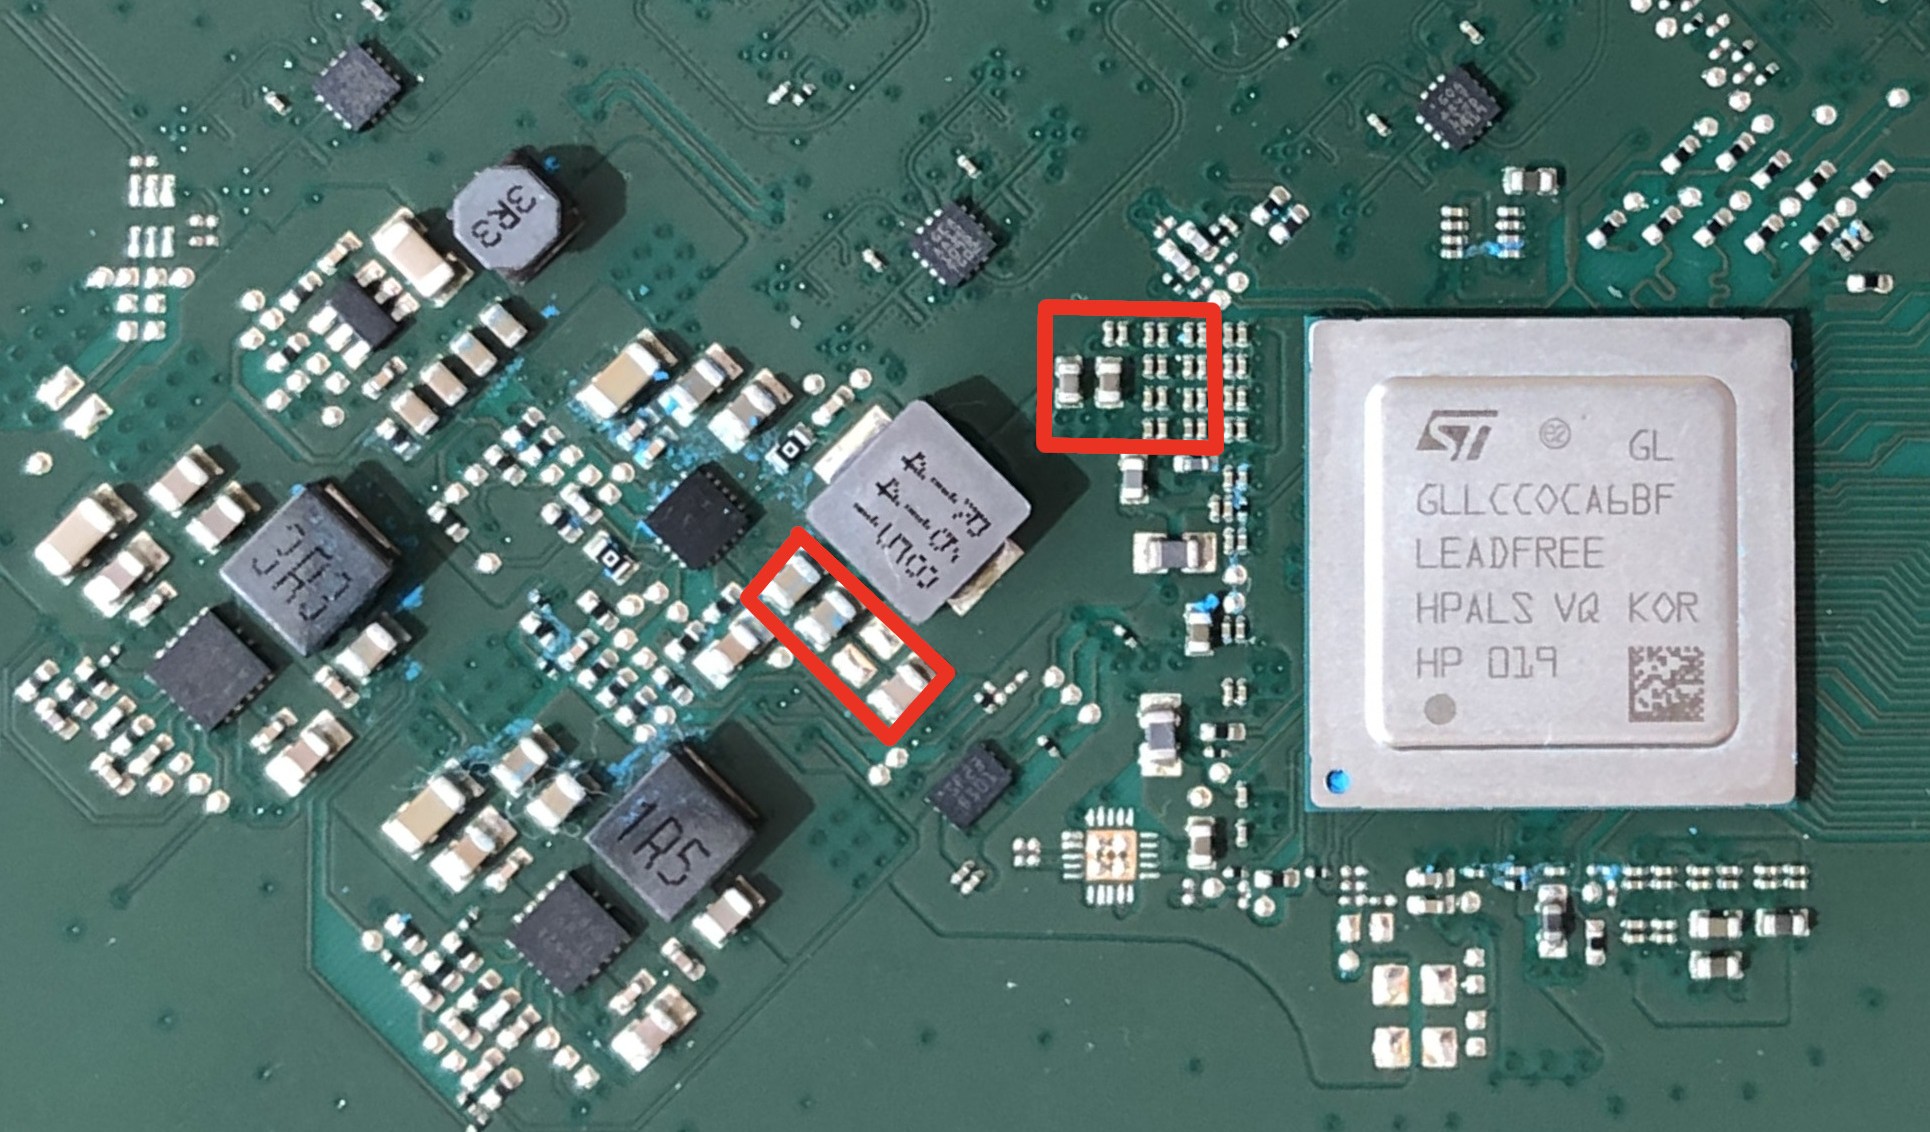 kuleuven-cosic/starlink-fi
Voltage fault-injection modchip for black-box security evaluation of Starlink terminals, bypassing bootloader signature verification to execute…
 binarly-io/fwhunt-scan
Tools for analyzing UEFI firmware and checking UEFI modules with FwHunt rules