Formbook-Payload-Extraction-XOR-Decryption-Net-Assembly-Analysis

Reverse engineering analysis of Formbook, an info-stealer that uses .NET assembly manipulation and XOR decryption. Full payload extracted via x32dbg,…

Reverse engineering analysis of Formbook, an info-stealer that uses .NET assembly manipulation and XOR decryption. Full payload extracted via x32dbg,…

GUI analyzer for deep-diving into PDF files. Detect malicious payloads, understand object relationships, and extract key information for threat…

IoT firmware identification and extraction

Reverse engineering analysis of PureRAT RAT abusing msbuild.exe, extracting C2 infrastructure, .NET evasion APIs, file system manipulation, and…

Browser-local security monorepo with six modules for mobile APK/IPA triage, client-side DAST fuzzing, OSINT directories, offline AI threat scoring,…

The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…

The PoC of information disclosure in Microsoft Desktop Windows Management.

A zero-symbol static analysis engine that extracts and mathematically ranks the Windows RPC attack surface using an AHP-based risk model.

Talk to your Intel Management Engine directly — zero-dependency Python tool. Finds memory leaks, partition manifest, live MKHI probing. First public…

A OWASP Based Checklist With 80+ Test Cases


My musings with PowerShell

Proof-of-concept exploit and vulnerability disclosure for HiSilicon hi3520d DVR/NVR devices. Demonstrates RCE via web interface, backdoor…

Security profiling for blackbox iOS

"Reverse engineering analysis of Salat Stealer, a Go-based info-stealer that uses a Telegram proxy decoy, C2 communication, and encrypted memory…

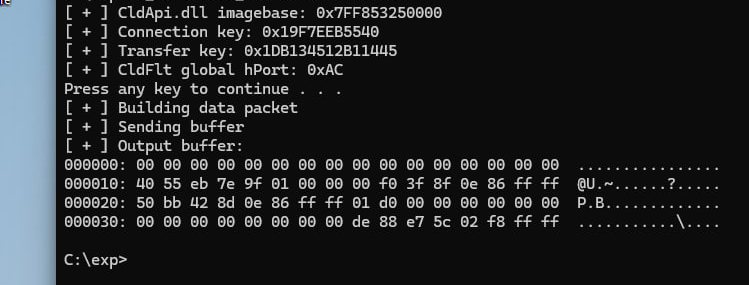
cldflt.sys information disclosure vulnerability (KB5034765 - KB5035853, Win 11).

Find Electron Apps Vulnerable to CVE-2023-4863 / CVE-2023-5129

Proof-of-concept for CVE-2018-9950, an out-of-bounds read vulnerability in Foxit Reader/PhantomPDF leading to information disclosure and potential…