

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
524 results
brotli-checker preview

brotli-checker

GitHubtrailofbits/brotli-checker

Claude Code and Codex skill for finding potentially vulnerable Brotli copies and guiding updates for CVE-2026-111497.
ai-securitybinary-analysiscode-analysis+7
10
5 days ago
OBS-graphics-hook32-Hook preview

OBS-graphics-hook32-Hook

GitHubgmh5225/obs-graphics-hook32-hook

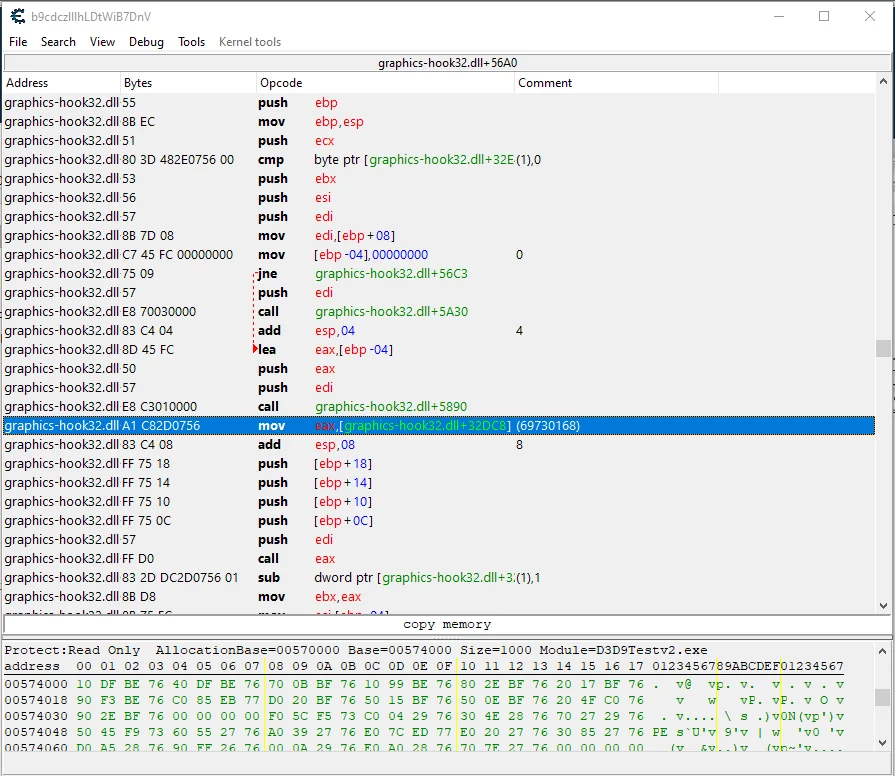
Demonstrates hooking OBS graphics-hook32.dll's D3D9 Present pointer to achieve stream-proof rendering that evades anti-cheat game capture detection.

anti-botbinary-analysiseducation+4
24 years ago
ollytlscatch preview

ollytlscatch

GitHubgmh5225/ollytlscatch

OllyDbg plugin that intercepts and dumps TLS/SSL plaintext traffic during debugging sessions, aiding reverse engineering and malware analysis of…

binary-analysisdebuggersdynamic-code-analysis+2
13 years ago
dsh-infinite-gen-5 preview

dsh-infinite-gen-5

GitHubminglink/dsh-infinite-gen-5

DeepSeek v4.1 flash 逆向工具(无限五代) 求 Star 收藏 ⭐欢迎大家提交项目的改进

ai-assisted-reversingbinary-analysisbinary-exploitation+8
3.4k8 days ago
Vidar-Stealer-Chrome-Injection-Malicious-JS-Targeting-Google-Reddit-Sessions-Analysis preview

Vidar-Stealer-Chrome-Injection-Malicious-JS-Targeting-Google-Reddit-Sessions-Analysis

GitHubkaandemir993/vidar-stealer-chrome-injection-malicious-js-targeting-google-reddit-sessions-analysis

Reverse engineering Vidar Stealer: From obfuscated memory strings to Chrome process injection, malicious JS execution, and active session hijacking…

binary-analysisdigital-forensicsdynamic-analysis-sandboxing+6
26 days ago
SuperGhidra preview

SuperGhidra

GitHubyuatemycat/superghidra

High-Performance Ghidra Architecture & GPU Acceleration Suite: LZ4/Zstd B-Tree Codec, Persistent Lock-Free Daemon, WGPU ARM64 Scanner, Z3 SMT Prover,…

ai-assisted-reversingandroid-securitybinary-analysis+8
17 days ago
no-access-protection-x86 preview

no-access-protection-x86

GitHubgmh5225/no-access-protection-x86

It encrypts the text section and set the protection to NO_ACCESS.

anti-botbinary-analysisdefensive-tools+4
13 years ago
NtStrace preview

NtStrace

GitHubgmh5225/ntstrace

frida-stalker based system call tracer on windows(x64).

binary-analysisdebuggersdynamic-analysis-sandboxing+2
12 years ago
decomp.anything preview

decomp.anything

GitHubgiveen/decomp.anything

decomp.wtf fork: Windows PE matching, MinGW/clang-cl toolchains, and an optional REA MCP bridge

ai-assisted-reversingai-securityandroid-security+7
5712h 45m ago
nmmp preview

nmmp

GitHubmaoabc/nmmp

dex-vm used to protect the android classes.dex file

android-securitybinary-analysiscode-analysis+5
1.2k1 year ago
GoReSym preview

GoReSym

GitHubmandiant/goresym

Parses Go binaries to recover symbols, function metadata, types, file paths, and embedded strings, including stripped or UPX-packed samples, with IDA…

binary-analysisdebuggersdigital-forensics+4
1.1k1 month ago
tvm-recover preview

tvm-recover

GitHubneurosaki987/tvm-recover

Devirtualizes Tencent VM .tvm0 sections: lifts VM handlers to guest-level listings and LLVM IR, recovers CFG and dispatch, and patches recovered code…
binary-analysisbinary-exploitationcode-analysis+5
258 days ago
miniDumpReader preview

miniDumpReader

GitHubgmh5225/minidumpreader

Parses Windows MiniDump (MDMP) files with Kaitai Struct, extracting memory strings and scanning them against YARA rules for forensic and malware…

binary-analysisdigital-forensicsforensics+3
3 years ago
hexvero preview

hexvero

GitHubmaximilianfeix/hexvero

Know what changed inside your Electron release: diff two builds for IPC, preload, windows, fuses and hosts, with file:line. CLI, CI gate, MCP server.

ai-securityandroid-securitybinary-analysis+9
84 days ago
hermit preview

hermit

GitHubxv4l3x/hermit

Inspects, decompiles and structurally patches Hermes bytecode (HBC) from React Native apps, with a GDB-style REPL, CFG, decompiler and re-serializing…
android-securitybinary-analysiscode-analysis+7
614 days ago
mysql-mysqldump-show-tables-overflow preview

mysql-mysqldump-show-tables-overflow

GitHubabraxas/mysql-mysqldump-show-tables-overflow

MySQL Community Server 26.7.0 - High - mysqldump SHOW TABLES stack overflow - crash dump UID
binary-analysiscryptographyexploitation+3
922 days ago
sqlite-fts5-securedel preview

sqlite-fts5-securedel

GitHubabraxas/sqlite-fts5-securedel

SQLite 3.53.4 - High - Local - Crash - FTS5 secure-delete PutVarint footer overrun
binary-analysisdatabase-securityexploitation+5
19 days ago
sqlite-rtree-rowid0 preview

sqlite-rtree-rowid0

GitHubabraxas/sqlite-rtree-rowid0

SQLite 3.53.4 - High - Local - UAF - rtree last_insert_rowid 0 node hash

binary-analysisdatabase-securitydynamic-analysis-sandboxing+5
19 days ago
Previous12…30Next