
netprobe-cve-2026-98432
 xen0bit/netprobe-cve-2026-98432
Black-box remote probe that detects CVE-2026-98432, a Linux IPv4 TCP ireq_opt use-after-free, via differential SYN-ACK option echo, plus static…
binary-analysisexploitationfuzzing+4
6
xen0bit/netprobe-cve-2026-98432Black-box remote probe that detects CVE-2026-98432, a Linux IPv4 TCP ireq_opt use-after-free, via differential SYN-ACK option echo, plus static…
 1llu50ry/mcp-reverse
MCP server exposing 180+ reverse-engineering tools that aggregate Ghidra, IDA, x64dbg, Frida and 56 other backends with native binary parsers and a…
 trailofbits/brotli-checker
Claude Code and Codex skill for finding potentially vulnerable Brotli copies and guiding updates for CVE-2026-111497.
 backdoorskid/win-def-clickfix
A scanner that estimates whether Microsoft Defender is likely to flag a command as ClickFix.
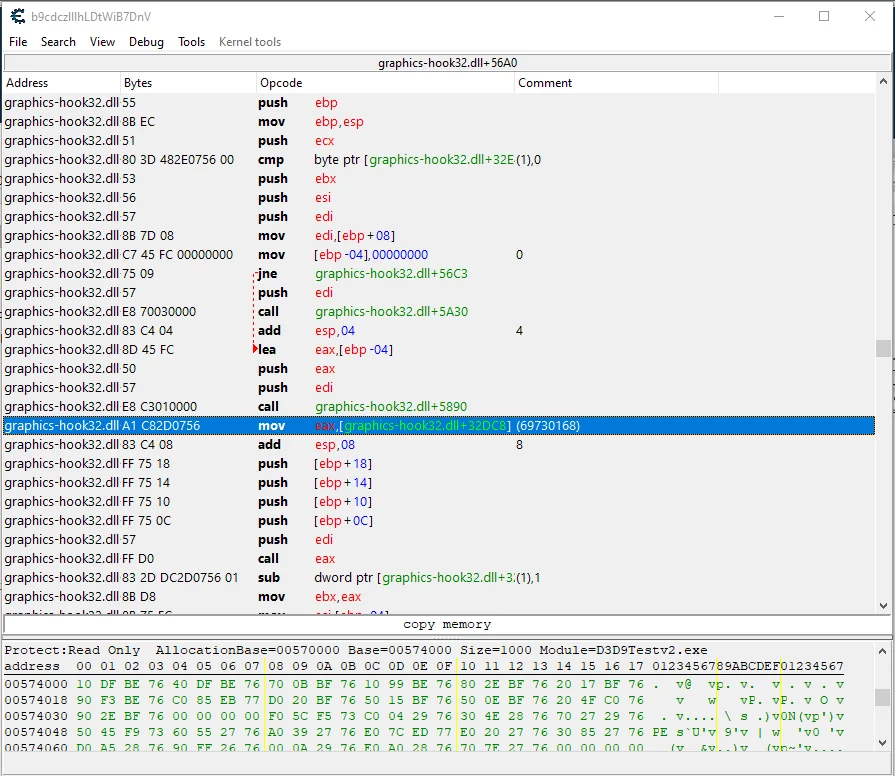 gmh5225/obs-graphics-hook32-hook
Demonstrates hooking OBS graphics-hook32.dll's D3D9 Present pointer to achieve stream-proof rendering that evades anti-cheat game capture detection.
 gmh5225/ollytlscatch
OllyDbg plugin that intercepts and dumps TLS/SSL plaintext traffic during debugging sessions, aiding reverse engineering and malware analysis of…
 mandiant/goresym
Parses Go binaries to recover symbols, function metadata, types, file paths, and embedded strings, including stripped or UPX-packed samples, with IDA…
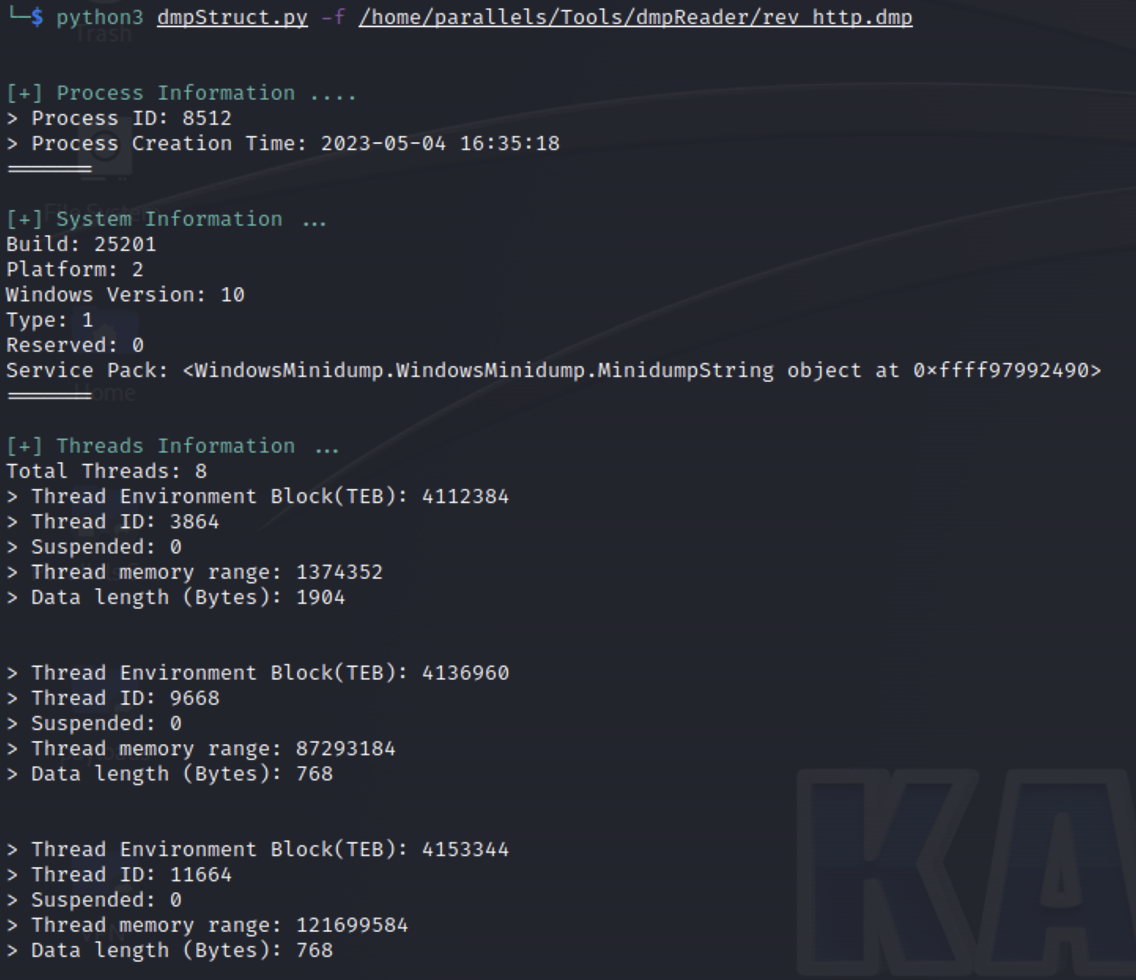 gmh5225/minidumpreader
Parses Windows MiniDump (MDMP) files with Kaitai Struct, extracting memory strings and scanning them against YARA rules for forensic and malware…
 maximilianfeix/hexvero
Know what changed inside your Electron release: diff two builds for IPC, preload, windows, fuses and hosts, with file:line. CLI, CI gate, MCP server.
 aethervm/aethervm
LLVM-native binary analysis and emulation platform that lifts AArch64 and x86_64 machine code to LLVM IR for instrumentation, deobfuscation, and…
 oscarsantanaarias/ida-ghidra-bridge
TCP JSON bridge servers for IDA Pro and Ghidra exposing decompilation, xrefs, symbols, vtables, RTTI and memory patching to external scripts and…
 reverserid/jurig
a fully autonomous AI agent for reverse engineering
 krxi/asmsense
Small language model that names and describes functions in stripped x86-64 binaries, with an open dataset, baselines, and LoRA fine-tuning…
 googleprojectzero/p0tools
Collection of Google Project Zero vulnerability research documents and small standalone security tools, including exploitation and…
 llvmparty/striga
Experimental x86-64 to LLVM IR lifter in Python that translates machine code into analyzable IR for reverse engineering, optimization, and VM handler…
 gmh5225/letmegg
Windows kernel proof-of-concept demonstrating an anti-debugging technique that prevents WinDbg from breaking by manipulating the kernel exception…
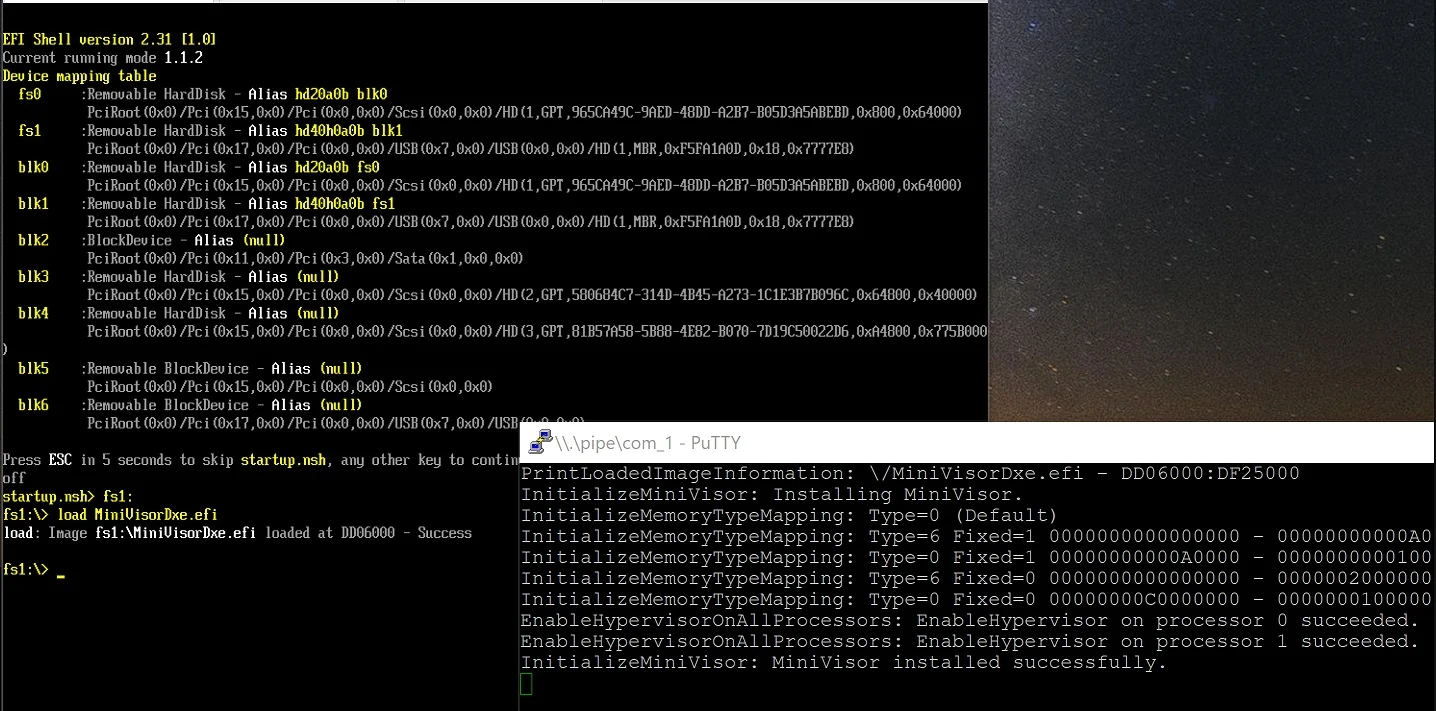 tandasat/minivisorpkg
The research UEFI hypervisor that supports booting an operating system.
 mrexodia/titanhide
Windows kernel driver that hooks Nt* SSDT functions to hide debuggers and processes from anti-debug checks, with an x64dbg plugin for stealth…