
velum-vmm
 dovughs/velum-vmm
Windows x64 research hypervisor using Intel VT-x and per-CPU EPT hooks to intercept Nt/Ex/Mm routines, apply request policies, and stream live kernel…
binary-analysisdebuggersdynamic-analysis-sandboxing+4
26
dovughs/velum-vmmWindows x64 research hypervisor using Intel VT-x and per-CPU EPT hooks to intercept Nt/Ex/Mm routines, apply request policies, and stream live kernel…
 trailofbits/brotli-checker
Claude Code and Codex skill for finding potentially vulnerable Brotli copies and guiding updates for CVE-2026-111497.
 c8dhjp4tyv-bit/jbl-wave-buds2-firmware-research
Reverse-engineering notes and Python tooling for JBL Wave Buds 2 (BES1306) firmware: OTA container format, flash layout, BLE/GATT protocol, and…
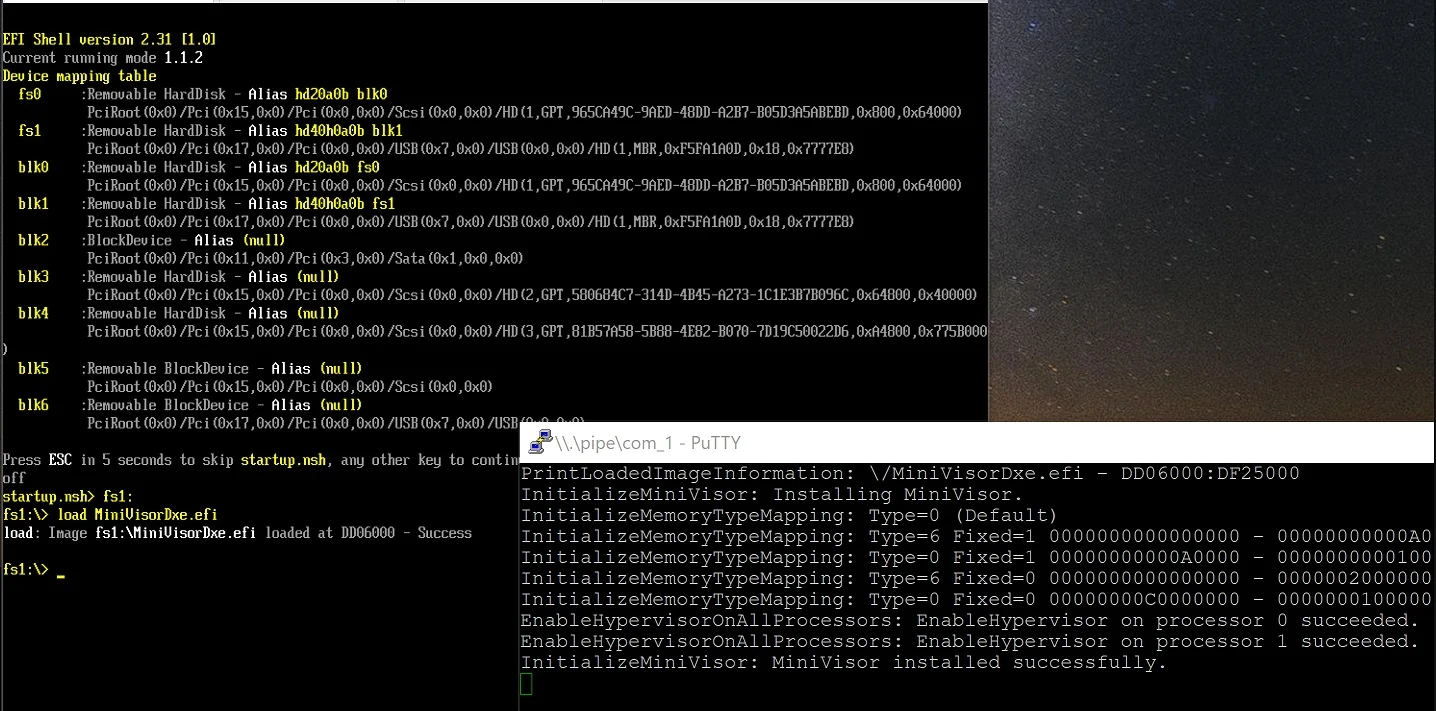 tandasat/minivisorpkg
The research UEFI hypervisor that supports booting an operating system.
 darthton/hyperbone
Minimalistic VT-x hypervisor for Windows x64 providing syscall, MSR, IDT, and kernel inline hooks plus EPT-based page substitution and TLB splitting.
 ionescu007/simplevisor
Minimal Intel VT-x hypervisor for Windows and UEFI that virtualizes a live host for introspection, supporting dynamic hyperjacking, unhyperjacking,…
 abraxas/gatex
FortinetHunter (@YogSoth0) binary cracking application. Part of CTF for FortinetHunter. ELF door: a stripped Nuitka onefile, an XOR-scrambled…
 sdodson/cve-2026-46595-proof
Go proof-of-concept demonstrating CVE-2026-46595 in golang.org/x/crypto/ssh, using symbol inspection of stripped binaries and image scans to verify…
 atomdrift-project/scan
0-day malware detection for binaries, source & scripts (that doesn't suck)
 gmh5225/gmh5225
LLVM-based security research toolchain: NeverC, a C23 cross-compiler, and NeverD, a binary analysis and decompilation engine that lifts PE, ELF,…
 crissyfield/super-trouper
MCP server exposing Frida instrumentation as tools for coding agents to connect to devices, inspect processes, manage sessions, and load JavaScript…
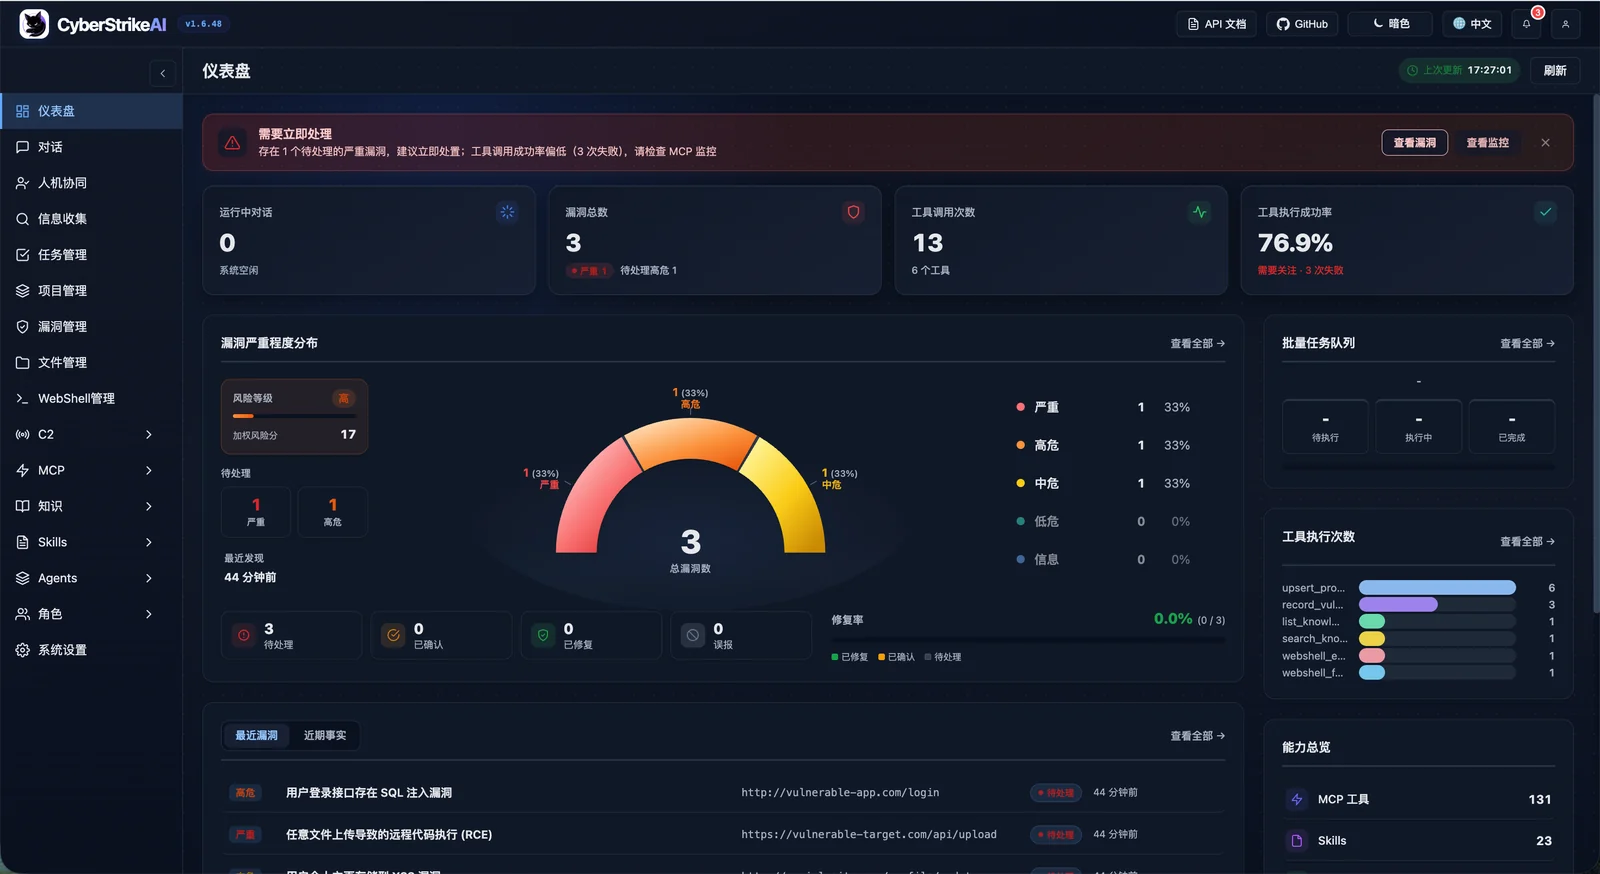 aipentest/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
 szybnev/cve-2026-7482
Reproduces CVE-2026-7482 heap out-of-bounds read in Ollama GGUF loading and quantization, with differential analysis of quantized artifacts to…
 0x0oz/cve-2026-7482-poc
Proof-of-concept exploit for CVE-2026-7482, an unauthenticated heap out-of-bounds read in Ollama's GGUF loader, demonstrating memory exfiltration via…
 johanneslks/cve-2026-32945
PJSIP DNS Compression Pointer Heap OOB Read (Remote DoS)
 trailofbits/polytracker
An LLVM-based instrumentation tool for universal taint tracking, dataflow analysis, and tracing.
 vivianuba/grandstream-cve-2026-2329-analysis
Defensive vulnerability-research project comparing vulnerable and patched Grandstream GXP1600 firmware for CVE-2026-2329, using SquashFS extraction,…
 mandiant/stringsifter
A machine learning tool that ranks strings based on their relevance for malware analysis.