

NativeMirror
 habanada/nativemirror
Native Delphi implementation of PE-sieve functionality with a reusable library, CLI, and PE-sieve-compatible DLL for HollowsHunter integration.
binary-analysisdefensive-toolsdigital-forensics+4
7
habanada/nativemirrorNative Delphi implementation of PE-sieve functionality with a reusable library, CLI, and PE-sieve-compatible DLL for HollowsHunter integration.
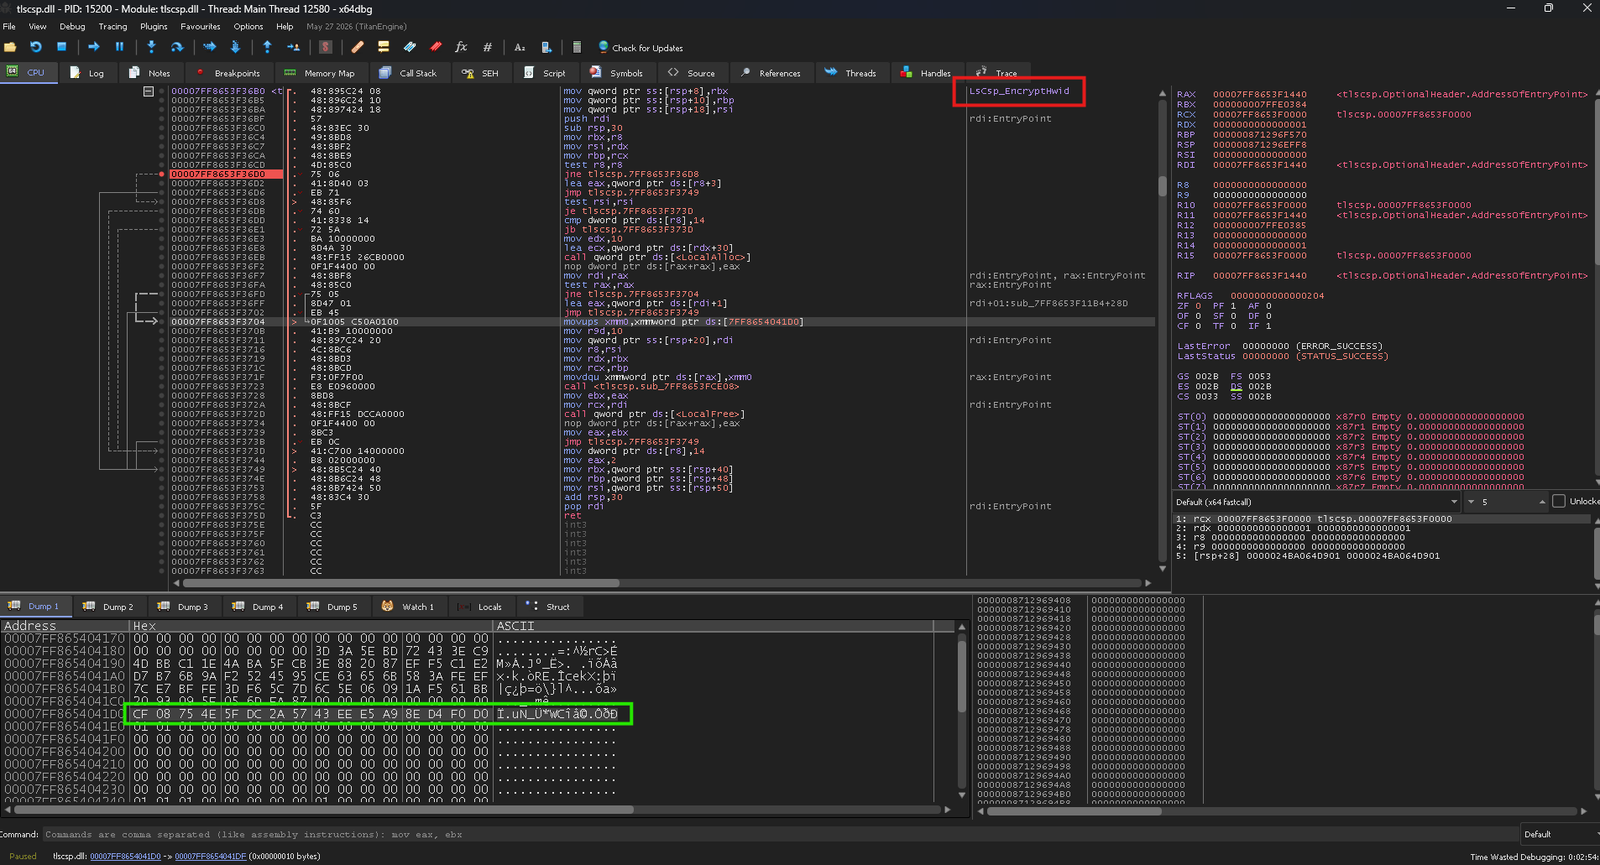 weedhashpeddler/rc4decryption
Abuses the Microsoft-signed tlscsp.dll LOLBin to run RC4 encrypt/decrypt via LsCsp_EncryptHwid, patching the hardcoded key in memory for BYOK…
 strivexjun/memorymodulepp
C++ library to load DLLs directly from memory without touching disk, with exception handling support, enabling stealthy code execution and evasion of…
 yawataa/cve-2025-60749
SketchUp Desktop 2025 DLL Hijacking Vulnerability
 nexxus67/cve-2026-25676
Research and proof-of-concept for CVE-2026-25676, a DLL search path hijacking vulnerability in M-Track Duo HD installer, including root cause…
 vollragm/ghostdebug
Debugger utilizing stealth hooks to hide from debugger detection
 gmh5225/0xguard
Simple Anti-cheat library for applications that use C++ on windows. #PastedProtection
 iilegacyyii/exportdumper
A small tool I made to dump the export table of PE files. The primary use case was intended for use within DLL proxying.
 playboisk8/poc-cve-2017-8464-opencalculator
Exploiting the .lnk vulnerability and operating system handling mechanisms regarding explorer.exe and USB drives.
 cybereason/siofra
Simulates the Windows PE loader to identify DLL hijacking vulnerabilities, generates weaponized DLLs with shellcode payloads, and detects UAC…
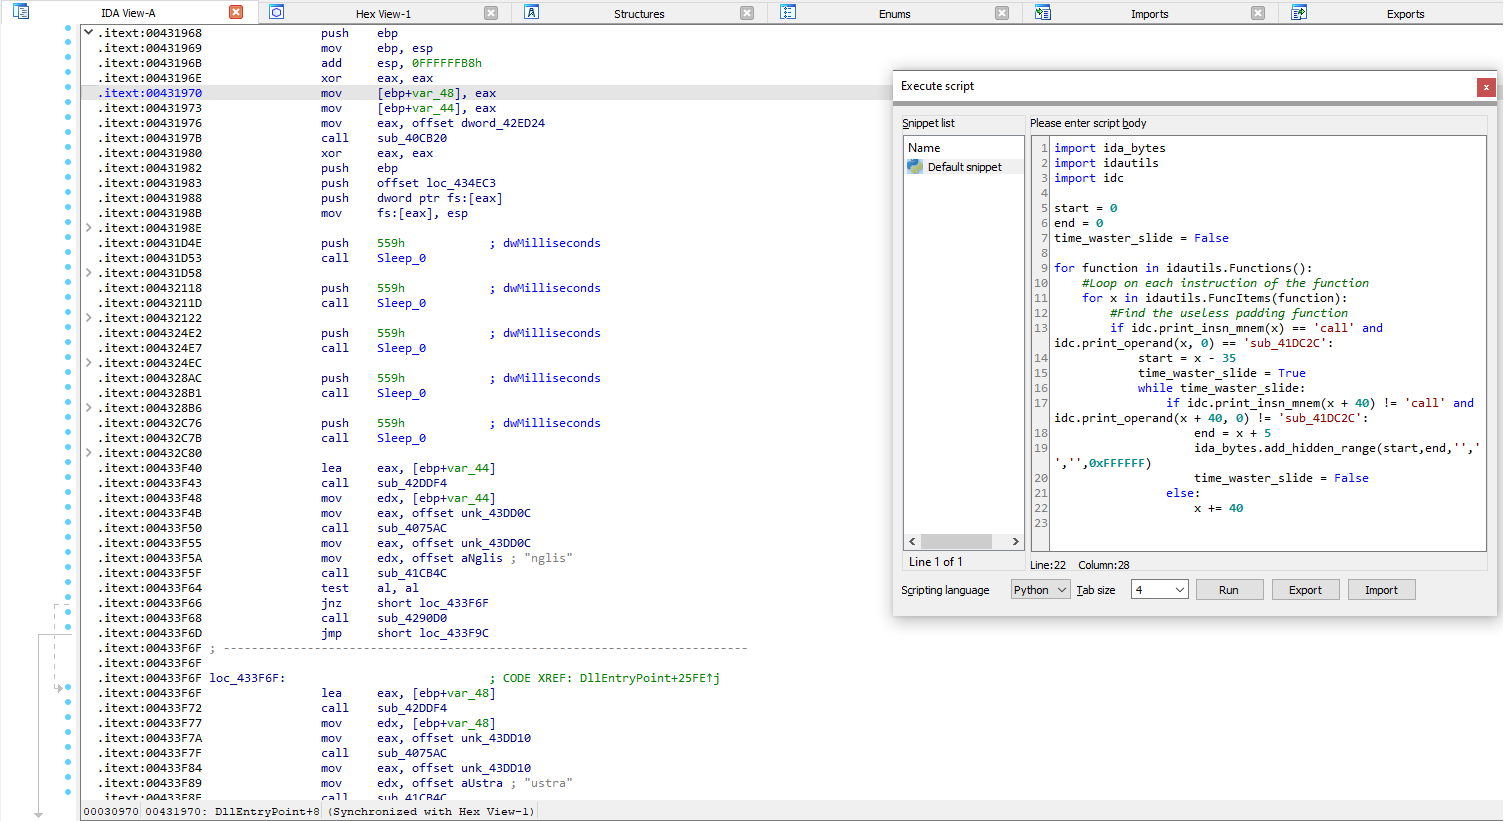 dodo-sec/astaroth-deobfuscator
IDA python script for deobfuscating Astaroth/Guildma injector DLL
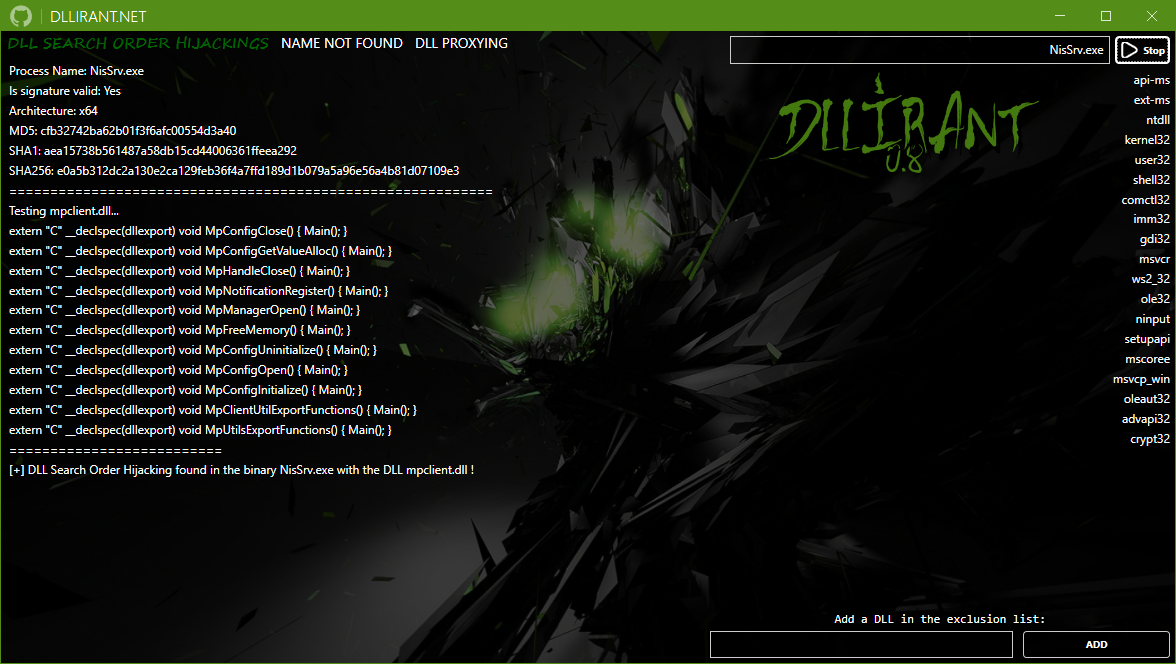 redteamsocietegenerale/dllirant
DLLirant is a tool to automatize the DLL Hijacking researches on a specified binary.
 7etsuo/windows-api-function-cheatsheets
A reference of Windows API function calls, including functions for file operations, process management, memory management, thread management,…
 namazso/dll-proxy-generator
Generate a proxy dll for arbitrary dll
 rad9800/pmd
Practical Windows malware development course: API hashing, DLL sideloading, shellcode execution, PE manipulation, payload hosting, and delivery labs.
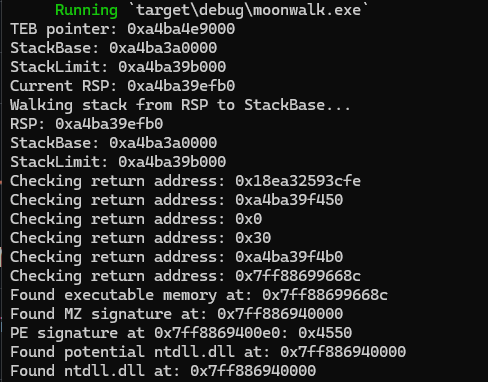 teach2breach/moonwalk
find dll base addresses without PEB WALK
 byt3bl33d3r/nimdllsideload
DLL sideloading/proxying with Nim!
 kernelm0de/cve-2018-8090
DLL Hijacking in Quickheal Total Security/ Internet Security/ Antivirus Pro (Installers)