

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
159 results
retrokit preview

retrokit

GitHubnemo22/retrokit

Headless-Ghidra toolkit for reverse engineering 32-bit DOS and Win32 games (1993-2010): own LE/LX loader, Watcom calling conventions, library…

ai-assisted-reversingai-securitybinary-analysis+5
16
6 days ago
lazy_importer preview

lazy_importer

GitHubjustasmasiulis/lazy_importer

library for importing functions from dlls in a hidden, reverse engineer unfriendly way

anti-botbinary-analysisexploitation+6
1.9k3 years ago
BinDiffHelper preview

BinDiffHelper

GitHububfx/bindiffhelper

Ghidra Extension to integrate BinDiff for function matching

binary-analysisbinary-exploitationcode-analysis+4
2971 month ago
kli-ex preview

kli-ex

GitHubgmh5225/kli-ex

Extended kernel lazy importer for Windows drivers that resolves APIs at runtime with encrypted, cached import names to hide kernel function usage…

binary-analysiscryptographydefensive-tools+4
343 years ago
lighthouse preview

lighthouse

GitHubgaasedelen/lighthouse

A Coverage Explorer for Reverse Engineers

binary-analysiscode-analysisdebuggers+6
2.6k2 years ago
KernelFlirt preview

KernelFlirt

GitHubakatorich/kernelflirt

Windows kernel-level debugger with OllyDbg/IDA-style UI, software and hardware breakpoints, PDB symbols, decompiler, and 17 plugins for reverse…
ai-assisted-reversingai-securityanti-bot+9
494 months ago
obfuscation_analysis preview

obfuscation_analysis

GitHubmrphrazer/obfuscation_analysis

Binary Ninja plugin to analyze and simplify obfuscated code

binary-analysiscode-analysismalware-analysis+3
2585 months ago
binary-cartography preview

binary-cartography

GitHubmrphrazer/binary-cartography

Technical webinars on reverse engineering, malware analysis, and software protection.

ai-assisted-reversingai-securitybinary-analysis+7
14827 days ago
javajive preview

javajive

GitHubyaklang/javajive

Pure-Go Java Decompiler and Serialization Operator
binary-analysiscode-analysismalware-analysis+4
225 days ago
antidbg preview

antidbg

GitHubnotrequiem/antidbg

A stealthy, fully syscalled C/C++ userland anti-debugging library for Windows, designed to protect software from reverse engineering

anti-botbinary-analysisdefensive-tools+4
34629 days ago
frida-medit preview

frida-medit

GitHubgmh5225/frida-medit

Cross-platform CUI process memory scanner built on Frida for finding, filtering, patching, and dumping live process memory during reverse engineering…
binary-analysisdebuggersdynamic-analysis-sandboxing+3
3 years ago
0xCr0ssCrush preview

0xCr0ssCrush

GitHubdeathshotxd/0xcr0sscrush

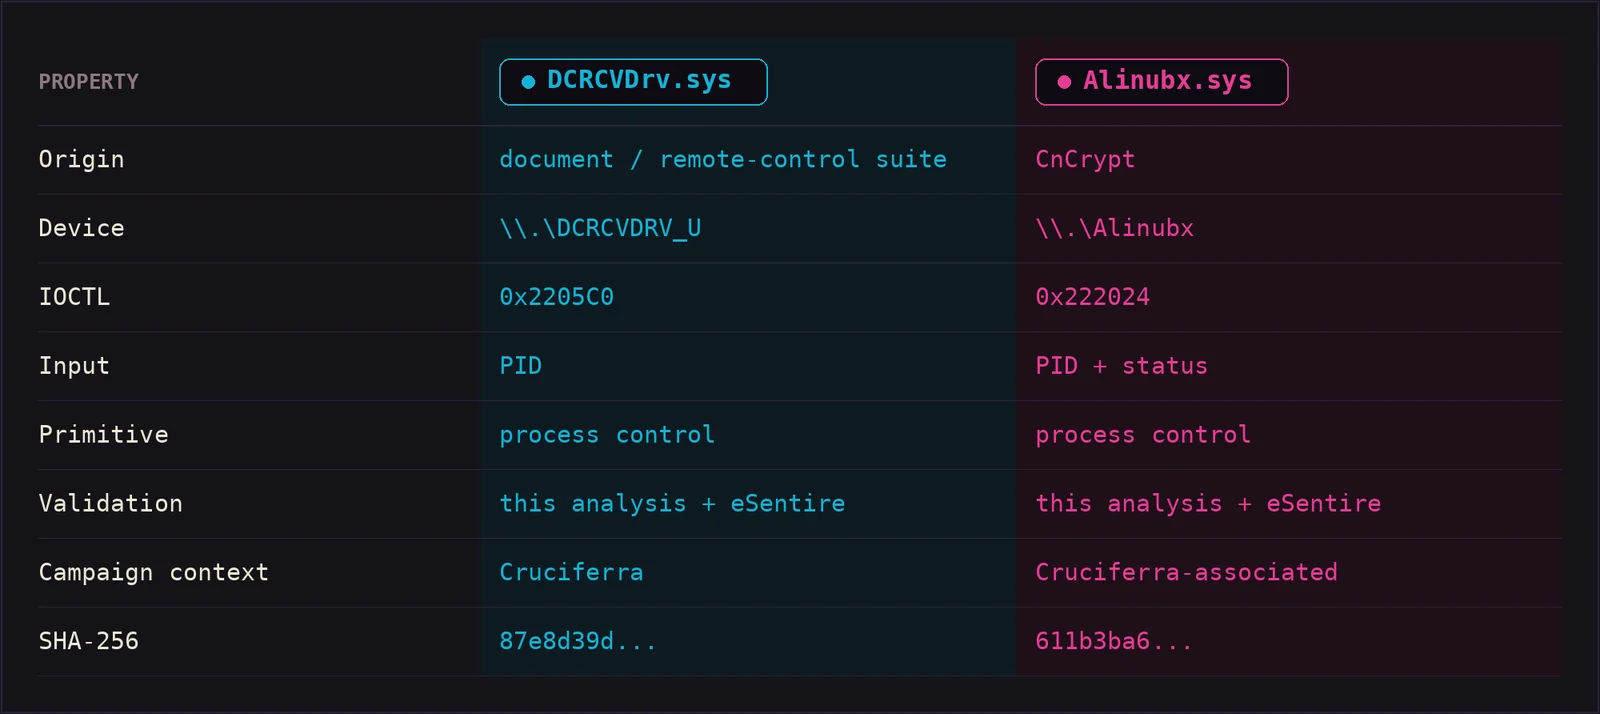
Windows BYOVD research on DCRCVDrv.sys and Alinubx.sys, reverse engineering their kernel primitives, IOCTL surfaces, and detection opportunities.

binary-analysisdefensive-toolsexploitation+4
3820 days ago
Driver-HideKernelThread-IoCancelIrp preview

Driver-HideKernelThread-IoCancelIrp

GitHubgmh5225/driver-hidekernelthread-iocancelirp

Windows kernel driver technique that hides kernel threads by abusing IoCancelIrp and IRP cancel routines, with detection methods for identifying…

binary-analysisdefensive-toolsmalware-analysis+1
94 years ago
Driver-KeAttachProcess-KeDetachProcess-rebuild preview

Driver-KeAttachProcess-KeDetachProcess-rebuild

GitHubgmh5225/driver-keattachprocess-kedetachprocess-rebuild

Rebuild of Windows kernel driver functions KeAttachProcess and KeDetachProcess, used for process attachment and anti-cheat bypass research.

binary-analysismalware-analysisreverse-engineering
24 years ago
Driver-SoulExtraction preview

Driver-SoulExtraction

GitHubgmh5225/driver-soulextraction

SoulExtraction is a windows driver library for extracting cert information in windows drivers

binary-analysismalware-analysisreverse-engineering
243 years ago
Philips-PM-5139-5138A-5136-Firmware-Project preview

Philips-PM-5139-5138A-5136-Firmware-Project

GitHubdoctormord/philips-pm-5139-5138a-5136-firmware-project

Firmware reverse engineering of the Philips PM5139 / PM5138A / PM5136 function generators: 8051 emulators used as measuring instruments, 35 sections…
binary-analysisdynamic-analysis-sandboxingeducation+6
41 month ago
deobf-Arxan-Deob-C preview

deobf-Arxan-Deob-C

GitHubgmh5225/deobf-arxan-deob-c

Simple C program to quickly deobfuscate windows executables protected with Arxan.
binary-analysisdefensive-toolsmalware-analysis+1
153 years ago
CVE-2026-8069 preview

CVE-2026-8069

GitHubs1eezer/cve-2026-8069

Technical write-up and proof-of-concept for CVE-2026-8069, a local privilege escalation in Acer NitroSense and PredatorSense services, exploiting a…

binary-analysisexploitationexploit-frameworks+3
1 month ago
Previous12…9Next