
CVE-2026-96515
 whoami-012/cve-2026-96515
Technical report and authenticated reverse-shell PoC for CVE-2026-96515, a root command execution flaw in the Netlink HG323RW router's BOA diagnostic…
binary-analysisembedded-systems-securityexploitation+7
whoami-012/cve-2026-96515Technical report and authenticated reverse-shell PoC for CVE-2026-96515, a root command execution flaw in the Netlink HG323RW router's BOA diagnostic…
 aipentest/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
 synacktiv/captainhook
Traces user inputs to detect injection vulnerabilities in Java methods via JDWP and Frida, identifying potential command and SQL injection points.
 nccgroup/mtk_bp
Tools for analyzing and reverse engineering MediaTek baseband firmware, including file extraction, symbol parsing, and Ghidra integration for modem…
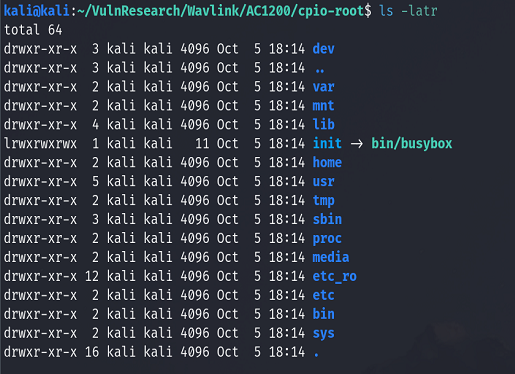 l41kaa/cve-2024-48705
Wavlink AC1200 with firmware versions M32A3_V1410_230602 and M32A3_V1410_240222 are vulnerable to a post-authentication command injection while…
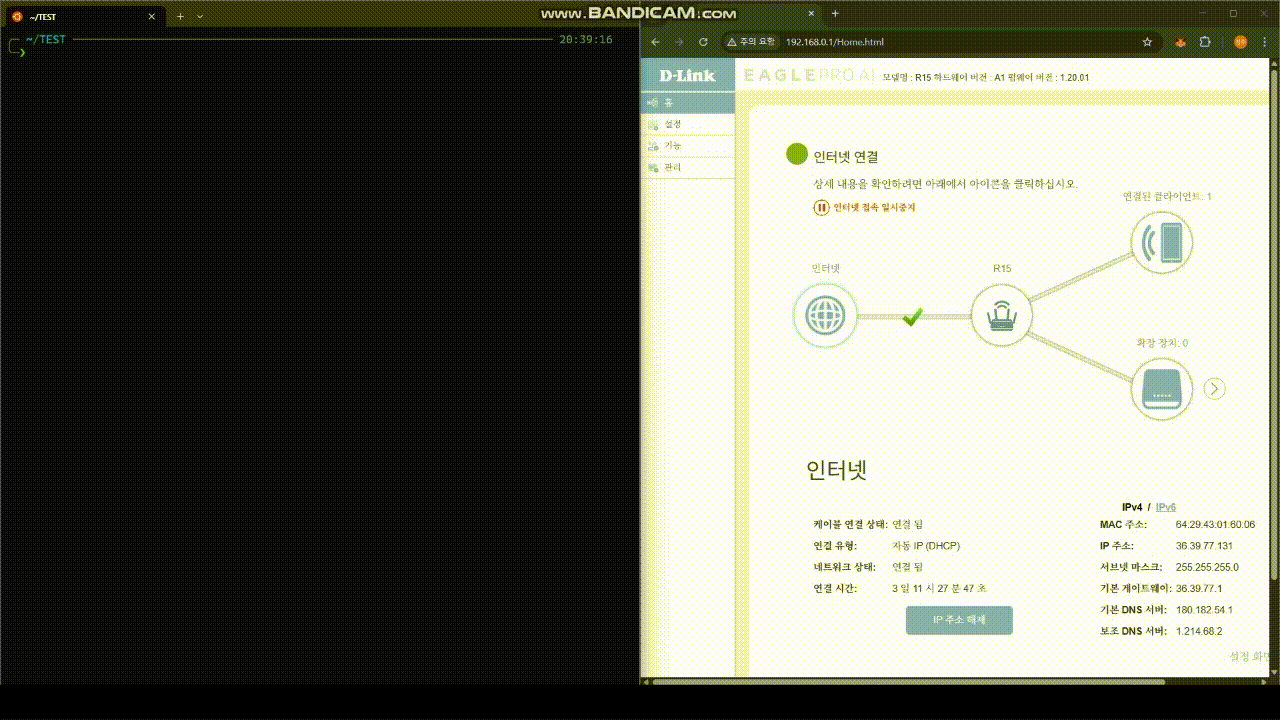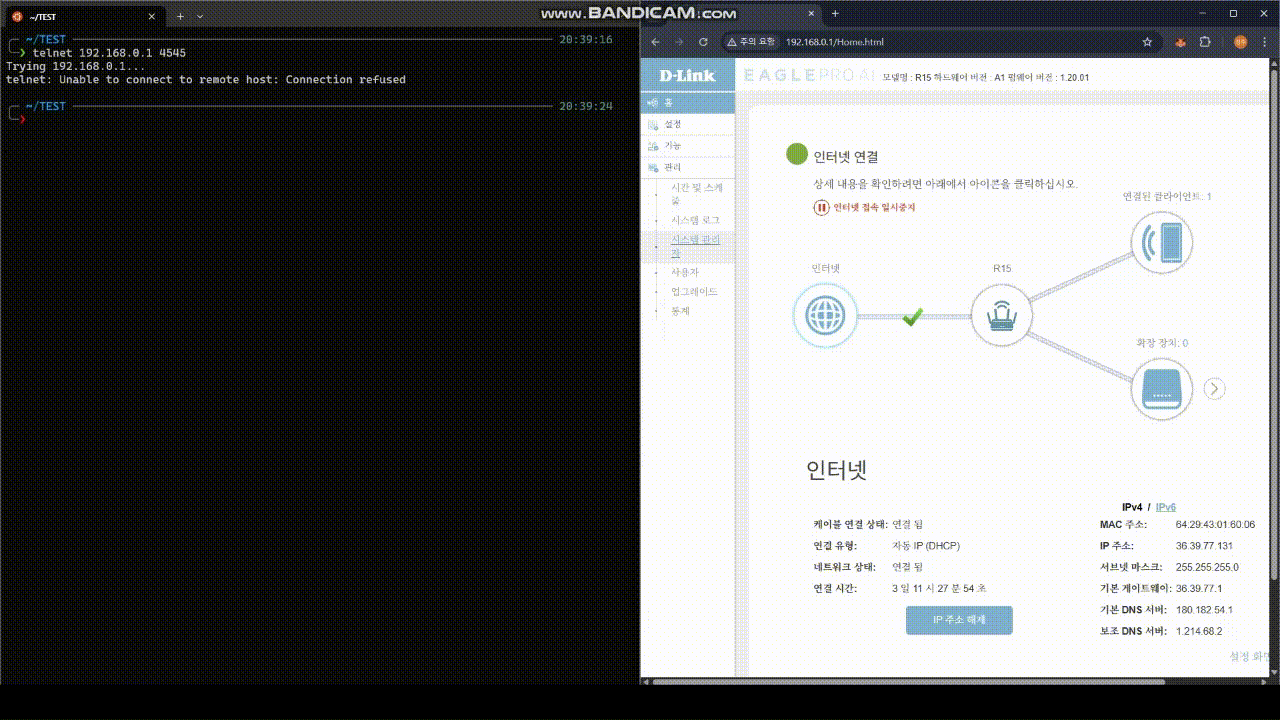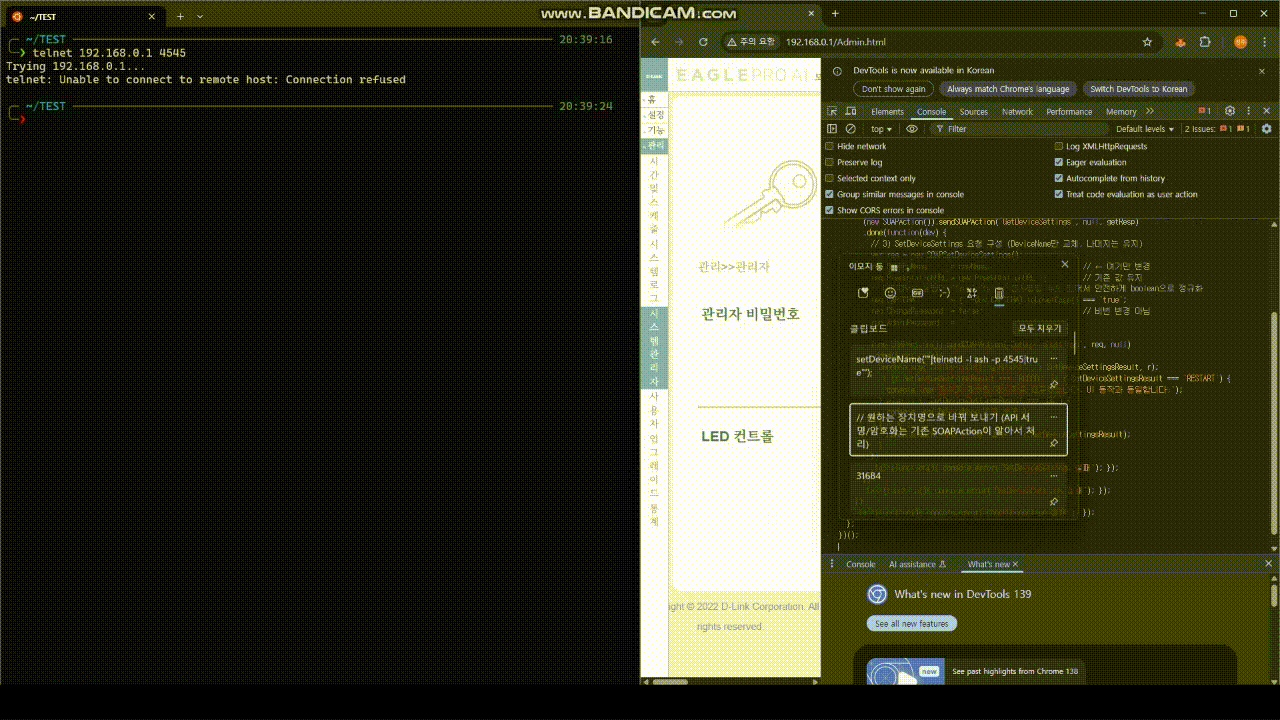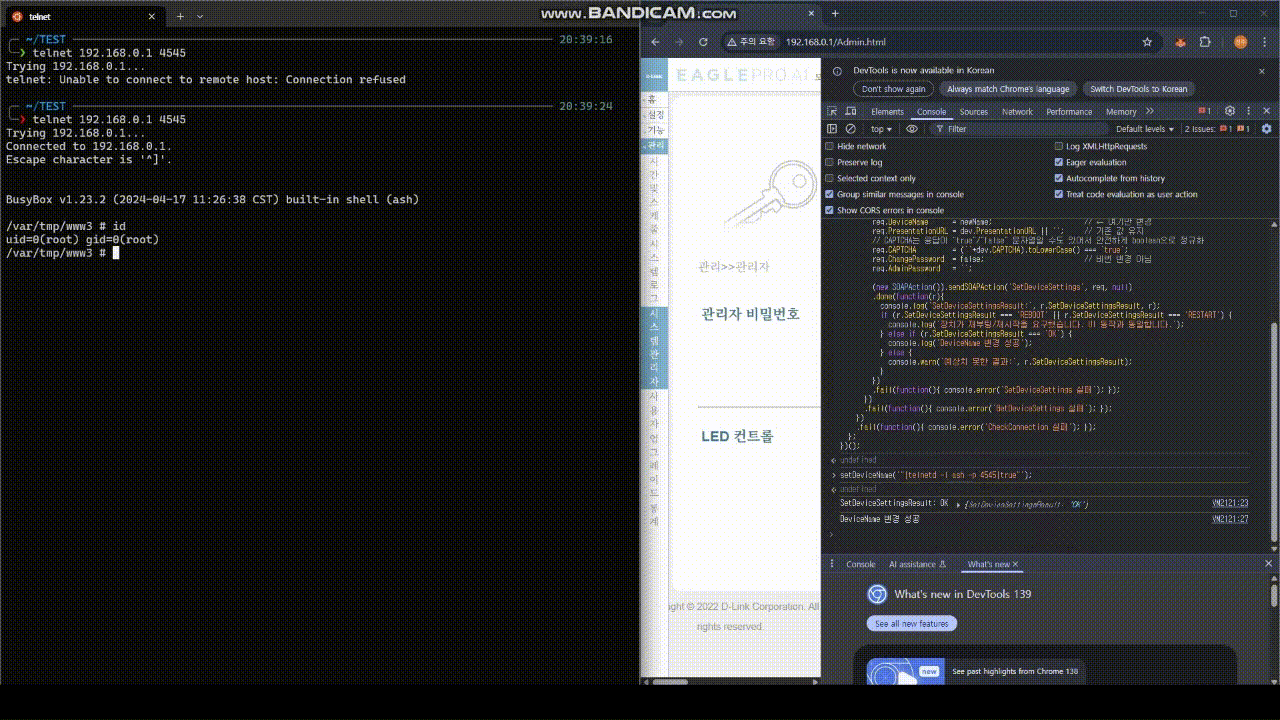 k0n9-log/cve-2025-60854
D-link AX1500 Vulnerability
 ed1s0nz/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
 0xsp-srd/aether
Windows memory-forensics and threat hunting tool that scans live process memory for malicious patterns, injection techniques, and reflectively loaded…
 hacefresko/cve-2021-4045
Exploit for command injection vulnerability found in uhttpd binary from TP-Link Tapo c200 IP camera
 duality084/cve-2023-33381-mitrastar-gpt-2741gnac
Proof-of-concept exploit for OS command injection (CVE-2023-33381) in MitraStar GPT-2741GNAC routers. Demonstrates bypass of restricted shell via…
 scorpion-security-labs/cve-2020-12124
Proof-of-concept exploit for CVE-2020-12124 targeting Wavlink AC1200 router, demonstrating unauthenticated command injection and stack buffer…
 m0n1x90/elfxtract
Automated ELF binary analysis tool for CTF/PWN challenges. Extracts security mitigations, ROP gadgets, PLT/GOT tables, and decompiles ASM to C using…
 keensecuritylab/binabsinspector
Static binary vulnerability scanner using abstract interpretation on Ghidra Pcode. Detects CWE classes like buffer overflows, use-after-free, and…