

hexvero
 maximilianfeix/hexvero
Know what changed inside your Electron release: diff two builds for IPC, preload, windows, fuses and hosts, with file:line. CLI, CI gate, MCP server.
ai-securityandroid-securitybinary-analysis+9
8
maximilianfeix/hexveroKnow what changed inside your Electron release: diff two builds for IPC, preload, windows, fuses and hosts, with file:line. CLI, CI gate, MCP server.
 reverserid/jurig
a fully autonomous AI agent for reverse engineering
 wheregoes/byd-dolphin-hacking
Reverse engineering the BYD Dolphin head unit — CAN bus, AVAS, NFC keys, OTA, and more. DiLink 3 / Android 10.
 ariyanpegu/ghostlock-app
GhostLock One-Tap Execution App (CVE-2026-43499)
 ejfkdev/ddc
Android DEX → Java decompiler in Rust, built for speed — full apps in seconds, queries in milliseconds. Progressive analysis, javac-verified output,…
 ejfkdev/dae
Config-driven Dart AOT snapshot analyzer that exports blutter-compatible symbols and structs for IDA, radare2 and Frida, and decompiles functions…
 1-3-7/disrobe
Rust CLI suite that statically decompiles, deobfuscates, and unpacks native code, bytecode, scripts, firmware, and app packages across 15+ ecosystems…
 danieldev23/frida-ssl-bypass
Frida toolkit that bypasses SSL/TLS certificate pinning on Android apps, hooking Java TrustManager, OkHttp, Conscrypt, and native OpenSSL/BoringSSL…
 lkimuk/reark
An intelligent reverse engineering and AI-assisted analysis tool for HarmonyOS NEXT (HAP/APP/ABC), Android (APK/AAB), iOS (IPA), and native…
 crissyfield/super-trouper
MCP server exposing Frida instrumentation as tools for coding agents to connect to devices, inspect processes, manage sessions, and load JavaScript…
 lyravoid/kernelpatch
Patches and hooks the Linux kernel using only a stripped kernel image, extracting symbols and injecting code for inline and syscall hooking on arm64.
 michalbednarski/thelastbundlemismatch
Writeup and exploit for CVE-2023-45777, bypass for Intent validation inside AccountManagerService on Android 13 despite "Lazy Bundle" mitigation
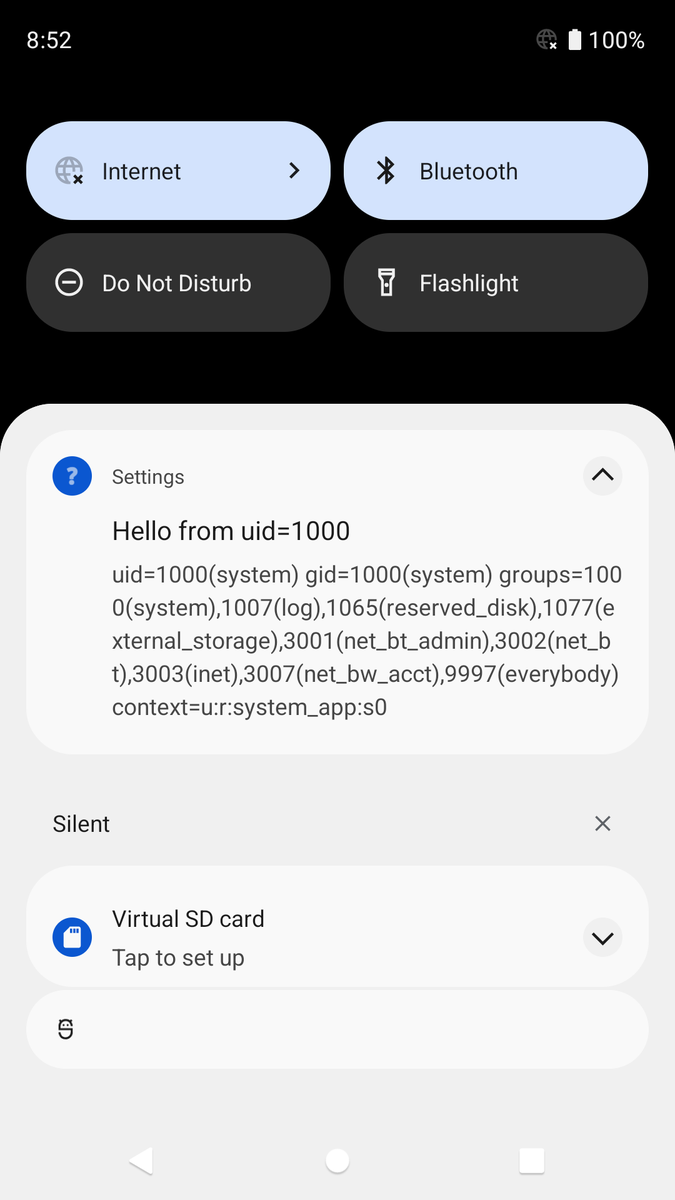 michalbednarski/reparcelbug2
Writeup and exploit for installed app to system privilege escalation on Android 12 Beta through CVE-2021-0928, a `writeToParcel`/`createFromParcel`…
 shaikusaf/system_bt_aosp10_r33_cve-2021-0475
Android Bluetooth stack (Fluoride) with build instructions for AOSP and Linux, including dependency setup and GN/Ninja build steps.
 shaikusaf/system_bt_aosp10_r33_cve-2021-0435
AOSP Bluetooth stack repository modified for CVE-2021-0435, providing a patched or vulnerable version for analysis and testing of Bluetooth…
 shaikusaf/system_bt_aosp10_r33_cve-2021-0431
Android Bluetooth stack (Fluoride) with a specific patch for CVE-2021-0431, enabling analysis and testing of Bluetooth vulnerabilities in AOSP 10.
 trinadh465/platform_system_netd_aosp10_r33_cve-2023-40084
Android netd vulnerability analysis and exploitation research for CVE-2023-40084, focusing on the platform's network daemon.
 trinadh465/frameworks_av_aosp10_r33_cve-2021-0509
Android media framework vulnerability fix for CVE-2021-0509, addressing a use-after-free in audio flinger to prevent local privilege escalation.