polytracker
 trailofbits/polytracker
An LLVM-based instrumentation tool for universal taint tracking, dataflow analysis, and tracing.
binary-analysisdynamic-code-analysiseducation+4
599
trailofbits/polytrackerAn LLVM-based instrumentation tool for universal taint tracking, dataflow analysis, and tracing.
 1rhino2/fnprint
match functions in binaries by what they do, not what their bytes look like. behavioral function fingerprinting via microexecution.
 worksbutnottested/lightkeeper
Maps execution-coverage data onto Ghidra disassembly to highlight visited code paths and accelerate reverse-engineering workflows.
 zxgio/ghidra_stack_strings
A script to detect stack-strings by using emulation (leveraging Unicorn)
 binsec/xyntia
Xyntia, the black-box deobfuscator
 zer0condition/reversekit
x64 Dynamic Reverse Engineering Toolkit
 hasherezade/pesieve-go
Golang bindings for PE-sieve
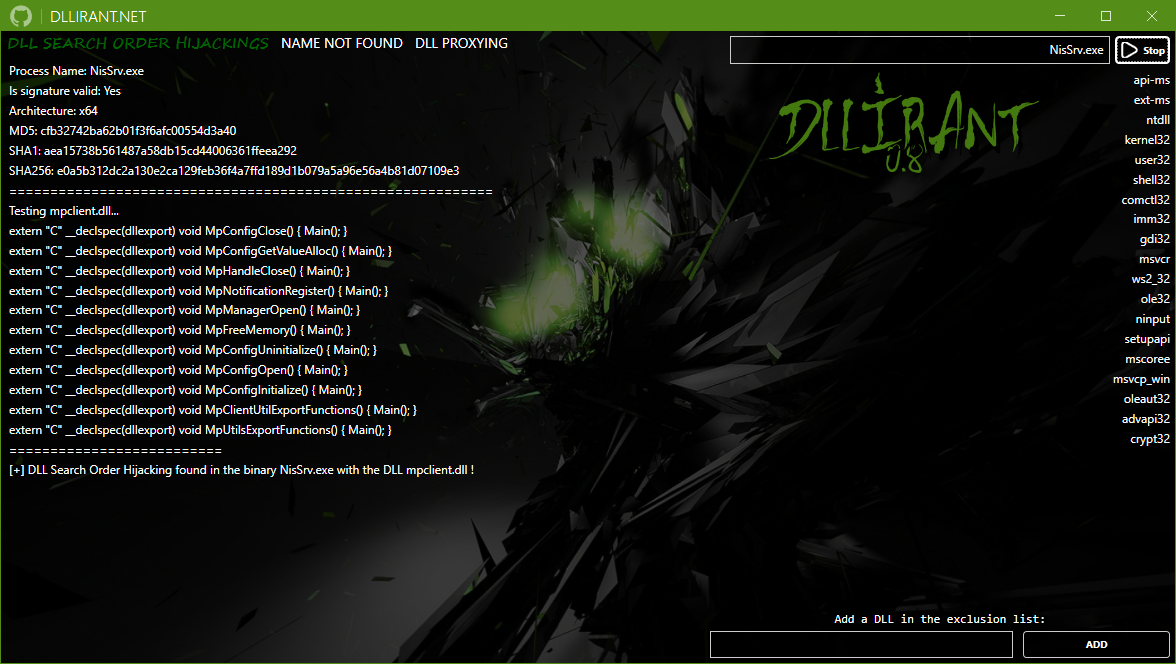 redteamsocietegenerale/dllirant
DLLirant is a tool to automatize the DLL Hijacking researches on a specified binary.
 r00tkitsmm/pishi
Pishi is a code coverage tool like kcov for macOS.
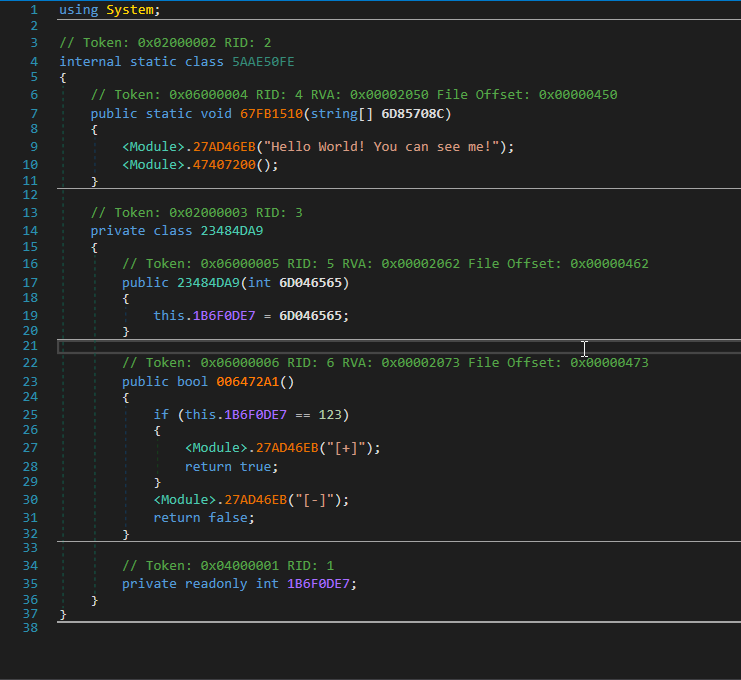 void-stack/vmunprotect.dumper
VMUnprotect.Dumper can dynamically untamper VMProtected Assembly.
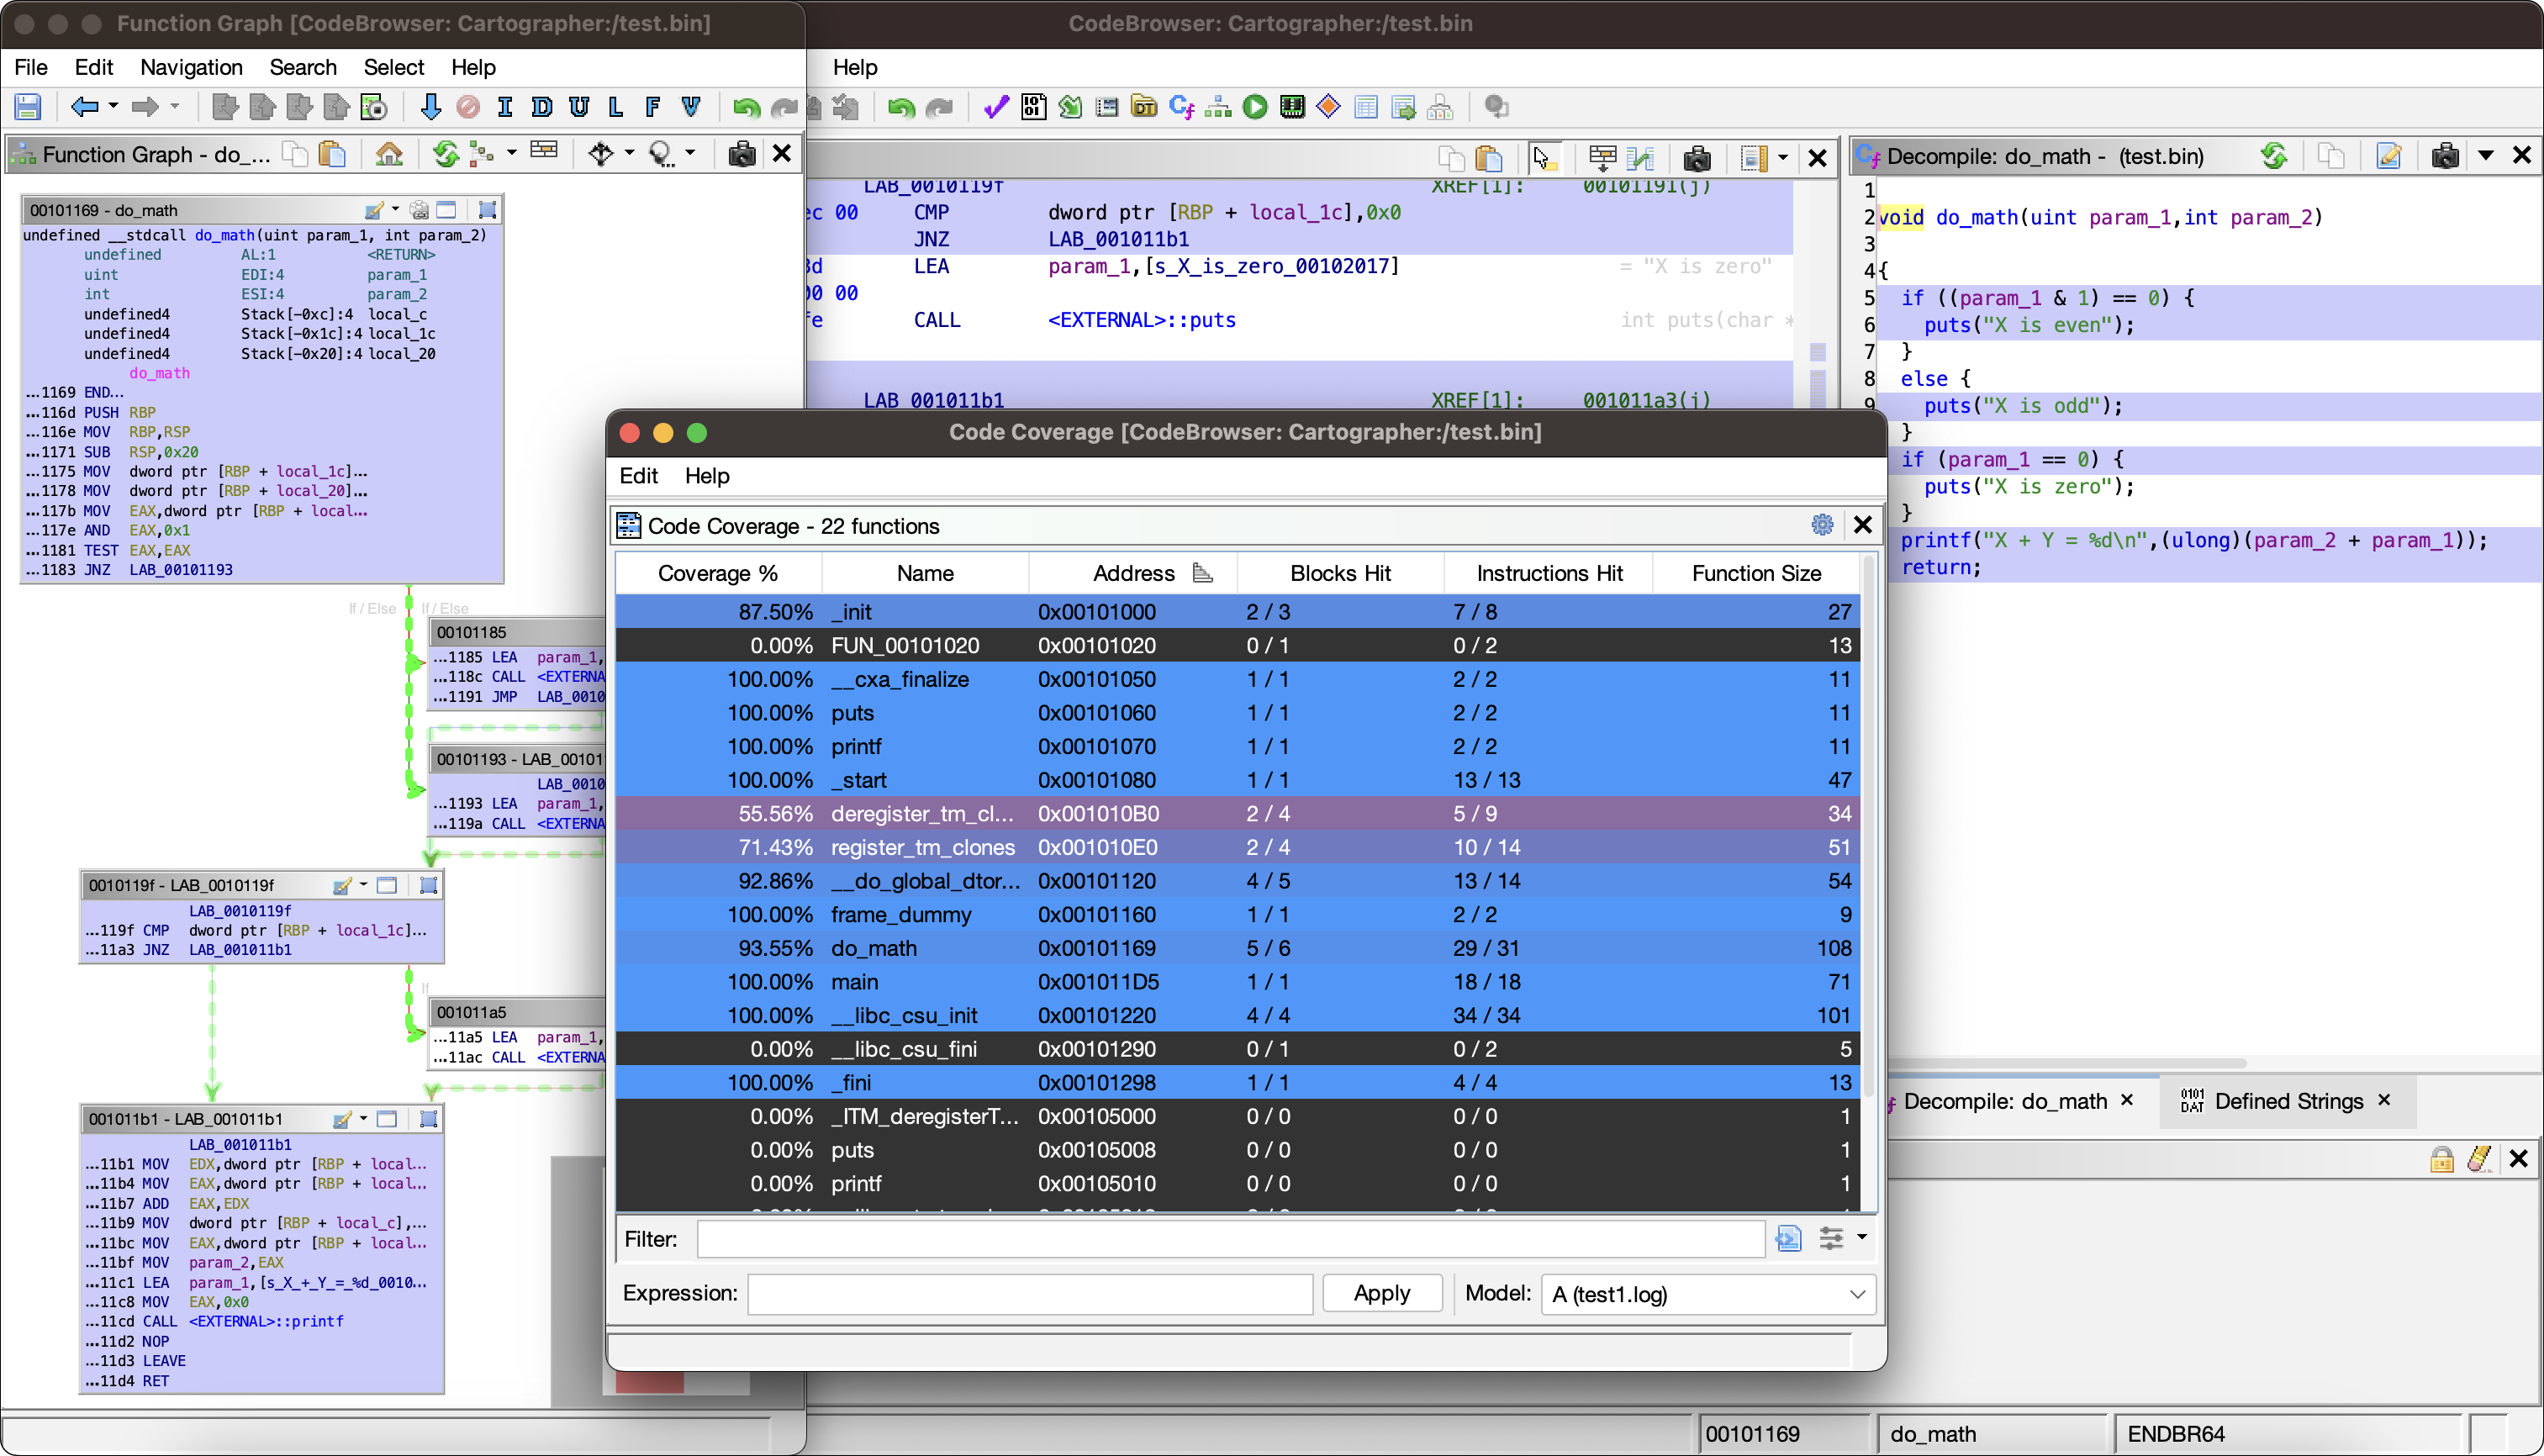 nccgroup/cartographer
Code Coverage Exploration Plugin for Ghidra
 nccgroup/winstrument
Winstrument is a framework of modular scripts to aid in instrumenting Windows software using Frida for reverse engineering and attack surface…
 tca-iscas/cooper-ndss-2022
A tool for effective testing the binding layer of scripting languages
 robertdfrench/ifuncd-up
GNU IFUNC is the real culprit behind CVE-2024-3094
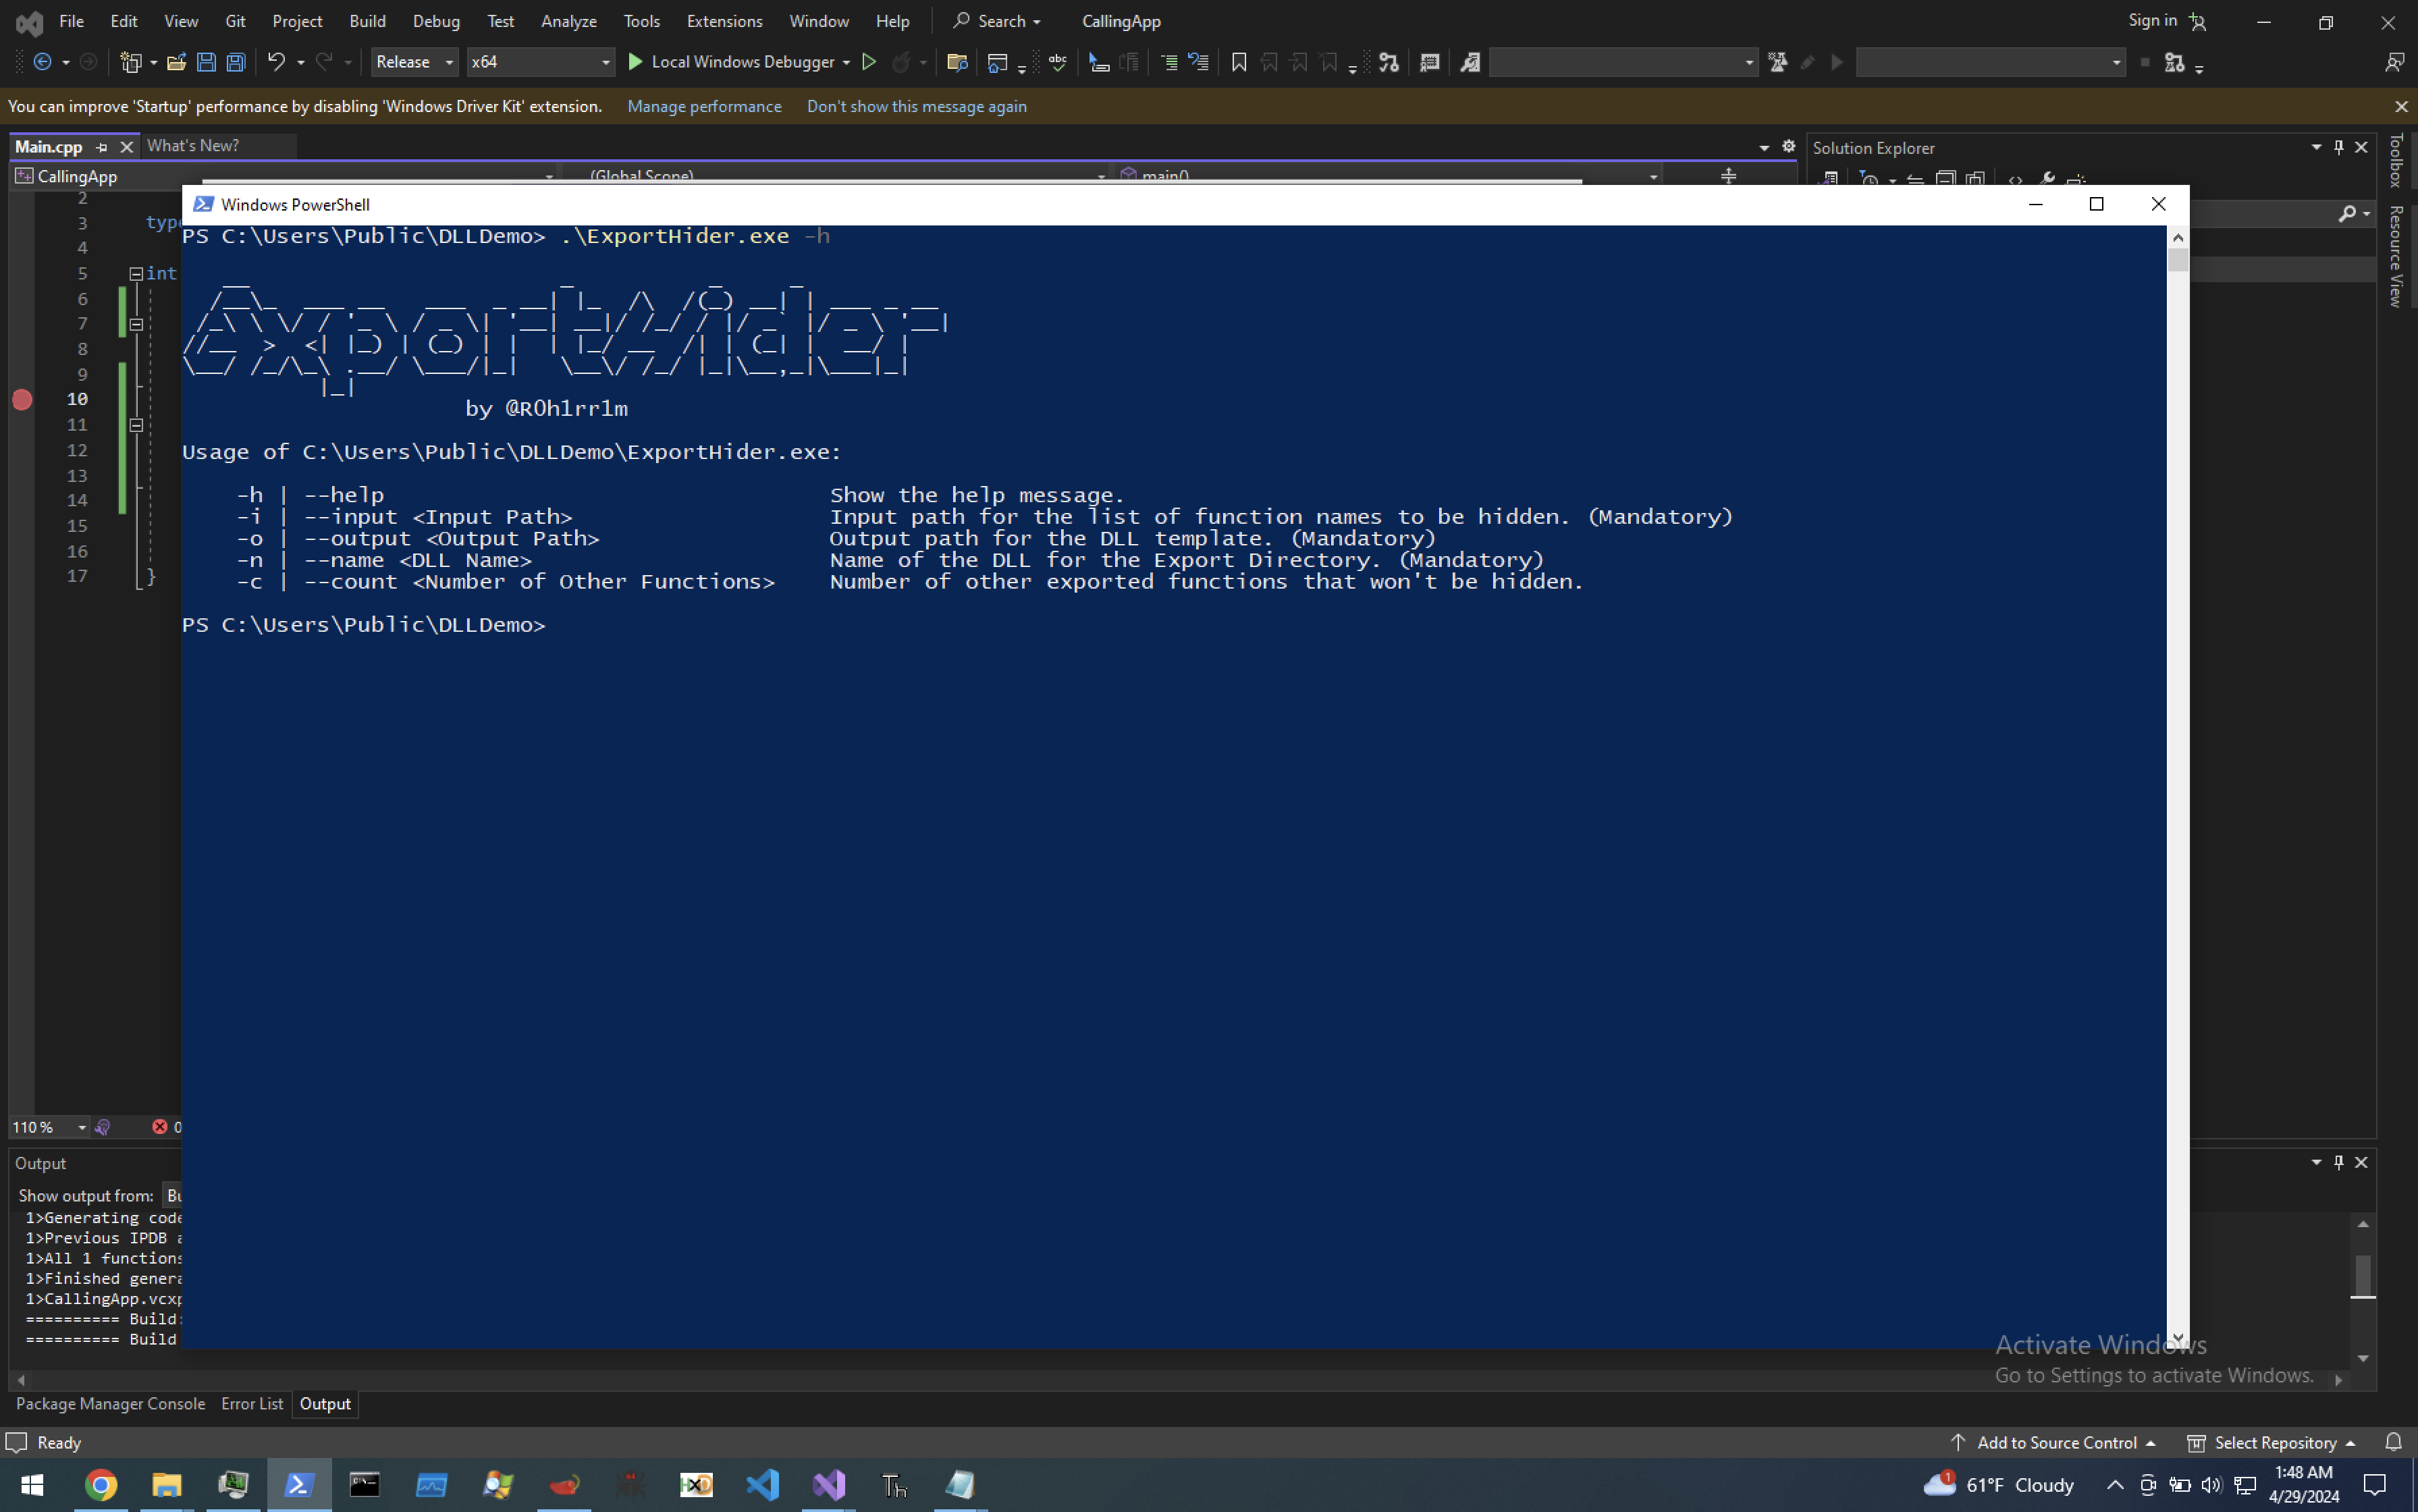 frkngksl/exporthider
ExportHider: Generating Export Table during Runtime to Hide the Exported Functions from the DLL File.
 ghostvectoracademy/dllhijackhunter
Automated DLL Hijacking Discovery, Validation, and Confirmation. Turning local misconfigurations into weaponized, confirmed attack paths.
 smackers/smack
Modular software verification toolchain that translates LLVM IR into Boogie intermediate verification language for bounded and experimental unbounded…