LinusWare-Source-Code-Internal

Reverse-engineered runtime engine for Roblox/Luau with VM hooking, opcode remapping, capability escalation, and UNC script environment for executing…

Reverse-engineered runtime engine for Roblox/Luau with VM hooking, opcode remapping, capability escalation, and UNC script environment for executing…

shell script protector (obfuscation, embedded interpreter, DRM) - invisible to kernel tracing

Open source Windows x64 PE packer and crypter. Compresses and encrypts executables with a custom virtual machine into a self extracting stub.

Binary Ninja plugin to analyze and simplify obfuscated code

C++ library to load DLLs directly from memory without touching disk, with exception handling support, enabling stealthy code execution and evasion of…

Obfuscates x86-64 assembly with instruction injection, junk code, constant obfuscation, and runtime decryption to hinder reverse engineering and…

List of mixed boolean-arithmetic resources

Some Rust program I wrote while learning Malware Development

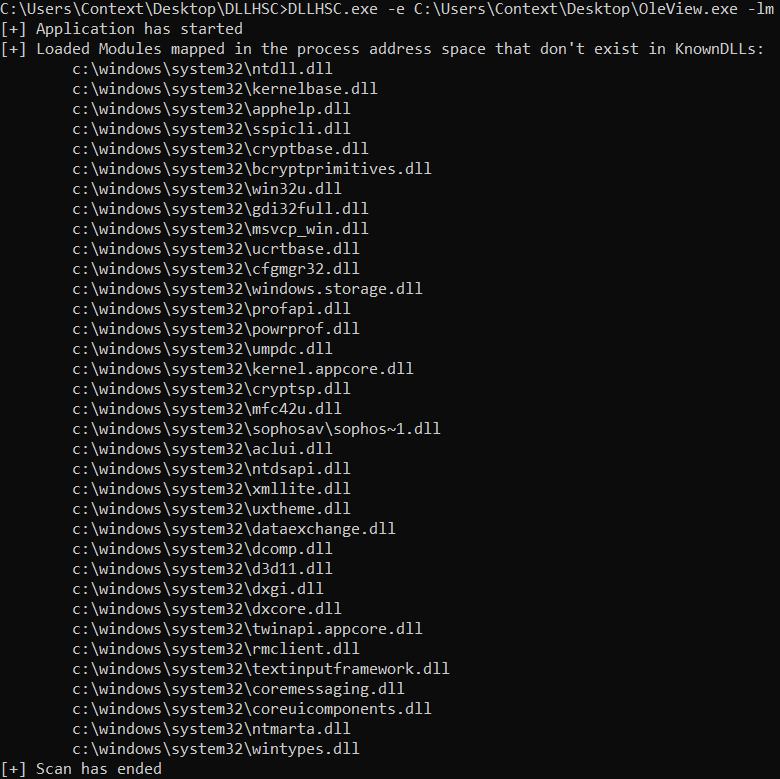
Automated scanner for discovering DLL search order hijacking candidates in Windows executables, featuring import table parsing, runtime module…

A bin2bin code virtualizer for x86-64 PE's

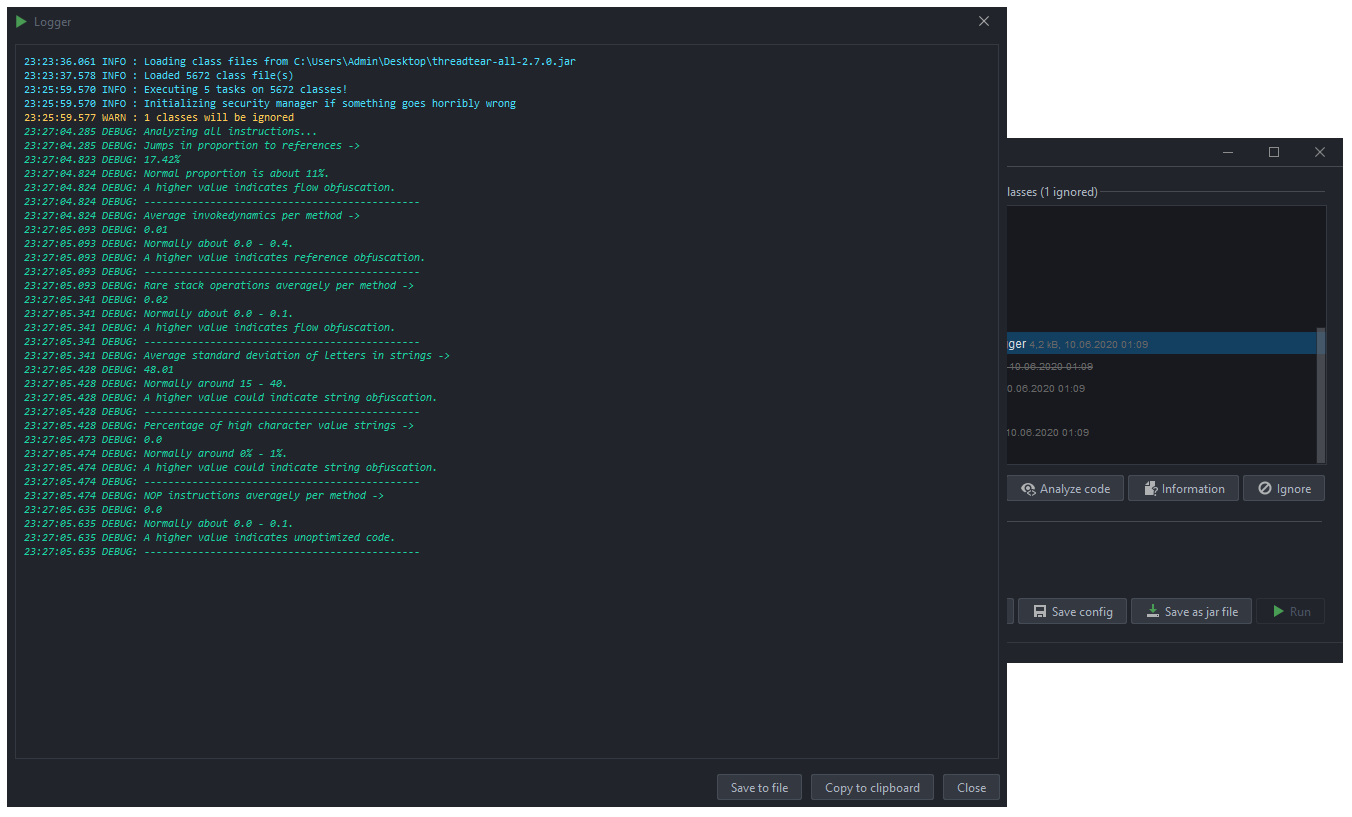
Multifunctional java deobfuscation tool suite

Static analysis walkthrough of a Metasploit Windows shellcode: PowerShell payload decoding, XOR obfuscation, PEB walking, and Export Address Table…

Mangle is a tool that manipulates aspects of compiled executables (.exe or DLL) to avoid detection from EDRs

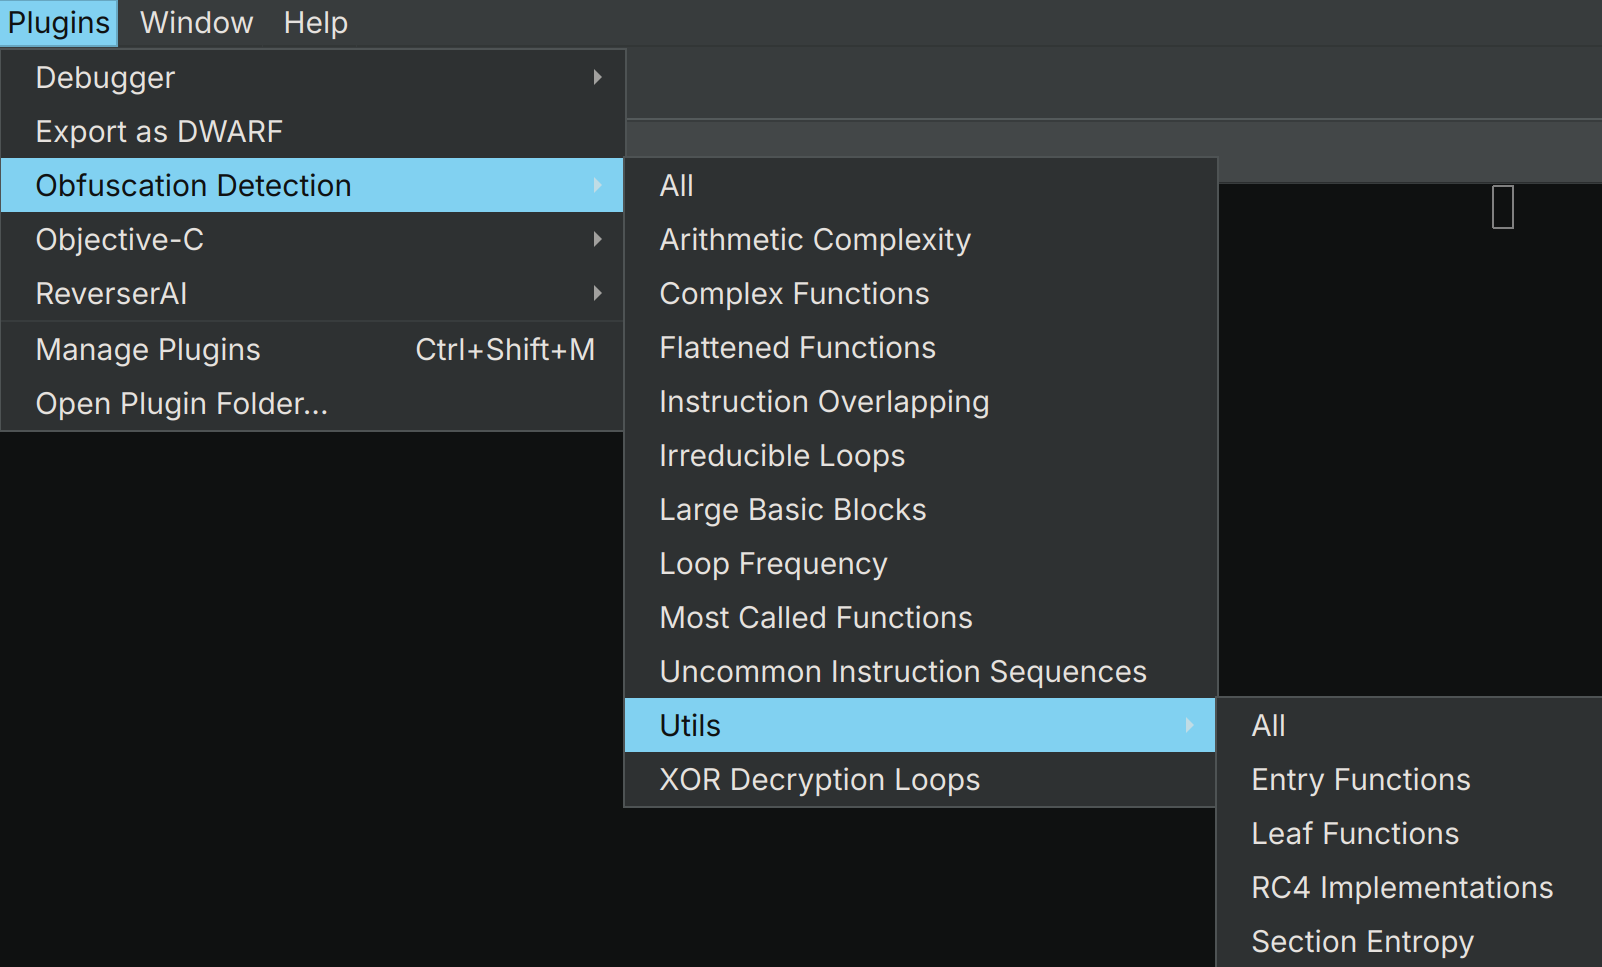
Binary Ninja plugin to identify obfuscated code and other interesting code constructs

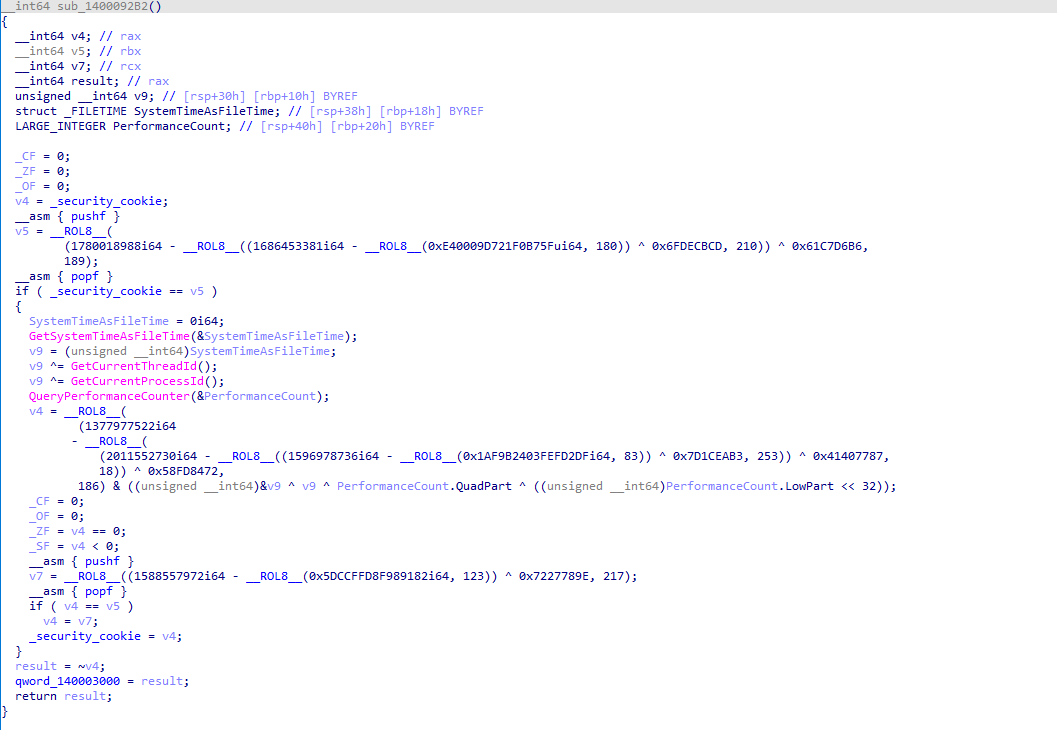
Static deobfuscator for Themida, WinLicense and Code Virtualizer 3.x's mutation-based obfuscation.

Python AV Evasion Tools

x64 binary obfuscator for PE files with control flow flattening, anti-disassembly, import obfuscation, and instruction mutation to hinder reverse…

An application to test windows and linux shellcodes