
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
69 results
hexstrike-ai preview

hexstrike-ai

GitHub0x4m4/hexstrike-ai

MCP server enabling AI agents to autonomously execute 150+ cybersecurity tools for automated penetration testing, vulnerability discovery, bug bounty…

binary-analysiscloud-securityctf+9
12.1k
1 month ago
CyberStrikeAI preview

CyberStrikeAI

GitHubaipentest/cyberstrikeai

The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
ai-securitybinary-analysiscloud-security+8
7.0k8 days ago
antidbg preview

antidbg

GitHubnotrequiem/antidbg

A stealthy, fully syscalled C/C++ userland anti-debugging library for Windows, designed to protect software from reverse engineering

anti-botbinary-analysisdefensive-tools+4
3214 days ago
PureRAT-msbuild.exe--C2-Extraction--Net-Evasion-Analysis preview

PureRAT-msbuild.exe--C2-Extraction--Net-Evasion-Analysis

GitHubkaandemir993/purerat-msbuild.exe--c2-extraction--net-evasion-analysis

Reverse engineering analysis of PureRAT RAT abusing msbuild.exe, extracting C2 infrastructure, .NET evasion APIs, file system manipulation, and…
binary-analysiscommand-and-controldefensive-tools+6
4 days ago
KasperMeow preview

KasperMeow

GitHubmein-0/kaspermeow

Proof-of-concept that exploits a Kaspersky driver vulnerability to leak kernel pointers and bypass KASLR on Windows, enabling kernel exploit chain…
binary-analysisexploitationreverse-engineering+1
1419 days ago
HPE-Aruba-AOS8-Vulnerabilities preview

HPE-Aruba-AOS8-Vulnerabilities

GitHubjm00nj/hpe-aruba-aos8-vulnerabilities

ArubaOS 8.13.2.0 pre-auth attack surface research. XXE+SSRF, ICMP reflection, buffer over-read, hardcoded credentials — all submitted to HPE…
binary-analysisexploitationfirmware-analysis+3
43 months ago
AllTools preview

AllTools

GitHubzodiacon/alltools

All reasonably stable tools
binary-analysisdebuggersgeneral-purpose-utilities+1
1.4k3 months ago
grapefruit preview

grapefruit

GitHubchichou/grapefruit

Open-source mobile security testing suite for iOS and Android. Previously Passionfruit
android-securitybinary-analysisdynamic-code-analysis+5
1.4k1 month ago
Crassus preview

Crassus

GitHubvu-ls/crassus

Windows privilege escalation discovery tool that parses Process Monitor boot logs to identify DLL hijacking, weak ACLs, and other elevation paths,…
binary-analysisexploitationpenetration-testing+1
6327 months ago
netzob preview

netzob

GitHubnetzob/netzob

Open-source toolkit for reverse engineering, modeling, and fuzzing communication protocols. Infers message formats and state machines from network…
binary-analysisfuzzingnetwork-security+1
8363 years ago
FalconEye preview

FalconEye

GitHubrajiv2790/falconeye

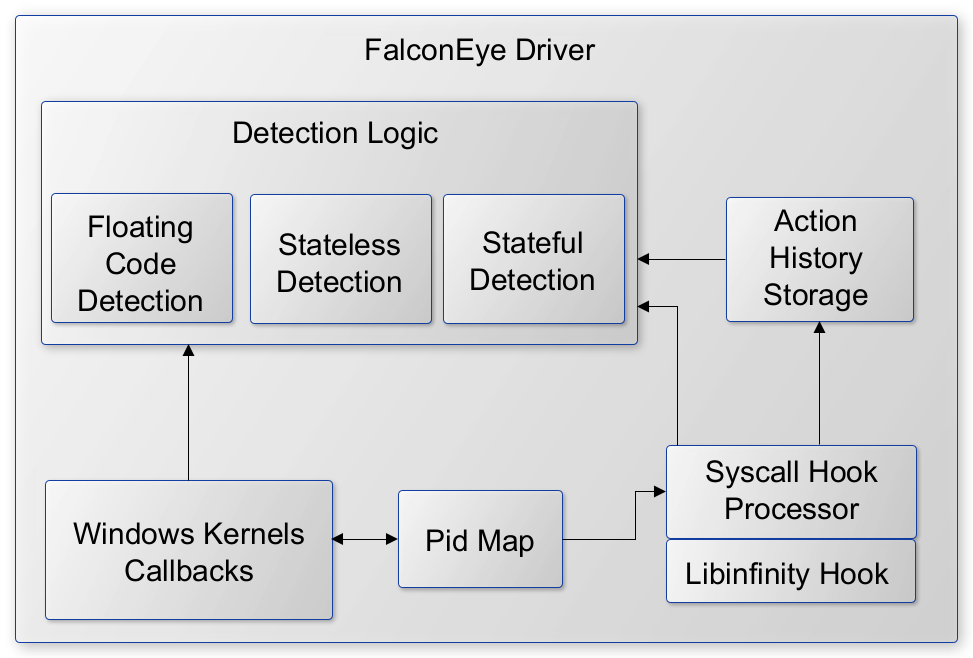
Kernel-mode Windows driver for real-time detection of process injection techniques, including shellcode, DLL, and reflective injection, with syscall…
binary-analysisdefensive-toolsintrusion-detection+1
3105 years ago
CyberChef preview

CyberChef

GitHubgchq/cyberchef

The Cyber Swiss Army Knife - a web app for encryption, encoding, compression and data analysis

binary-analysiscryptographyctf+9
36.0k19h 31m ago
sandsifter preview

sandsifter

GitHubxoreaxeaxeax/sandsifter

The x86 processor fuzzer

binary-analysisfuzzinghardware-security+2
5.1k9 years ago
Dnstracer-1.9-Fix preview

Dnstracer-1.9-Fix

GitHubj0lama/dnstracer-1.9-fix

Patched version of dnstracer fixing CVE-2017-9430 stack-based buffer overflow via argv[0] length validation. Traces DNS server chains for hostname…

binary-analysisdns-analysisexploitation+2
8 years ago
yara-x preview

yara-x

GitHubvirustotal/yara-x

A rewrite of YARA in Rust.

binary-analysisdata-recoverydefensive-tools+14
1.3k21h 34m ago
radmin-vpn-linux preview

radmin-vpn-linux

GitHubbaptisterajaut/radmin-vpn-linux

Run Radmin VPN on Linux via Wine — custom driver, TAP bridge, zero packet loss

binary-analysishardware-iot-securitylateral-movement+5
21516 days ago
CrimsonEDR preview

CrimsonEDR

GitHubhelixo32/crimsonedr

Simulate the behavior of AV/EDR for malware development training.
binary-analysisdefensive-toolsdynamic-analysis-sandboxing+3
5662 years ago
Cisco-ASA-vulnerability-research preview

Cisco-ASA-vulnerability-research

GitHubcobbbex/cisco-asa-vulnerability-research

Systematic reverse engineering of Cisco ASA's lina binary to discover and analyze memory corruption vulnerabilities, including CVE-2025-20333 and…

binary-analysisexploitationfuzzing+4
1 month ago
Previous1234Next