

lfi
 lfi-project/lfi
Top-level repository for LFI: Practical, Efficient, and Secure Software-based Sandboxing
binary-analysiscode-analysisdynamic-analysis-sandboxing+4
1228 months ago
lfi-project/lfiTop-level repository for LFI: Practical, Efficient, and Secure Software-based Sandboxing
 sunnypatell/basalt
World's first hazard checker for NVIDIA Blackwell (sm_120), with an assembler and scheduler matched against their own compiler byte for byte. The…
 platomav/mcextractor
Intel, AMD, VIA & Freescale Microcode Extraction Tool
 unsignedchad/bcm4360-wpa3
wpa3 functionality for the wifi chip in a 2014 macbook pro
 malrev/abd
Course materials for Advanced Binary Deobfuscation by NTT Secure Platform Laboratories
 themalwareguardian/uefi-security-research-howyar-sysreturn-netcopy
Post CVE-2024-7344 analysis of Howyar SysReturn NetCopy - reverse engineering notes, vulnerable binaries, vendor correspondence, and proof-of-concept…
 tobss8/gigabyte-h510m-k-v2-bios-smm-reverse-engineering-cve-2025-7026-7027-7028-7029-research
Static reverse-engineering of a GIGABYTE H510M K V2 (`H510MKV2.F3`) BIOS image: full UEFI firmware-volume extraction analysis of the PI-spec SMM Core…
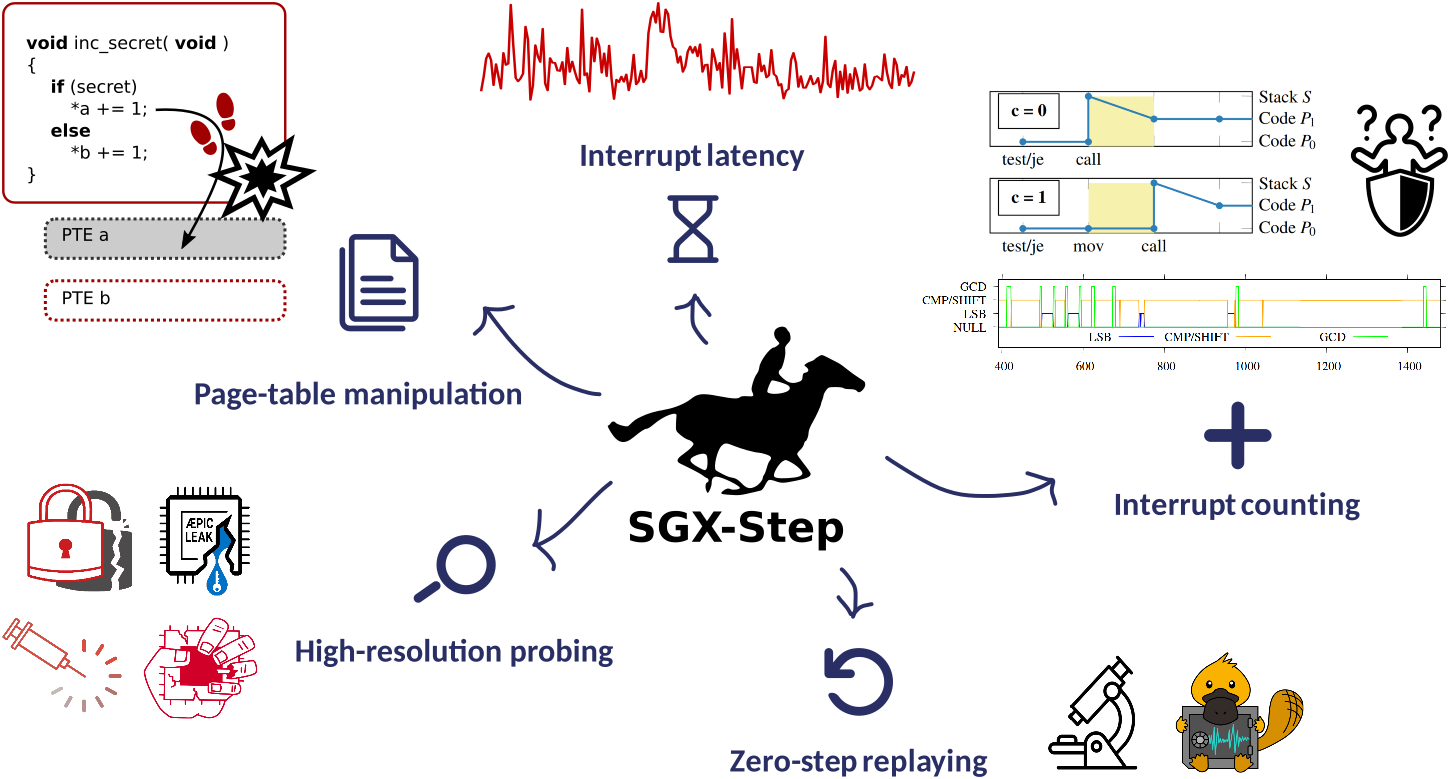 jovanbulck/sgx-step
A practical attack framework for precise enclave execution control
 demining/phoenix-rowhammer-attack-cve-2025-6202
Phoenix Rowhammer Attack: Systemic Risk of Bitcoin Wallet Private Key Compromise in Global Blockchain Infrastructure Due to a Critical SK Hynix DDR5…
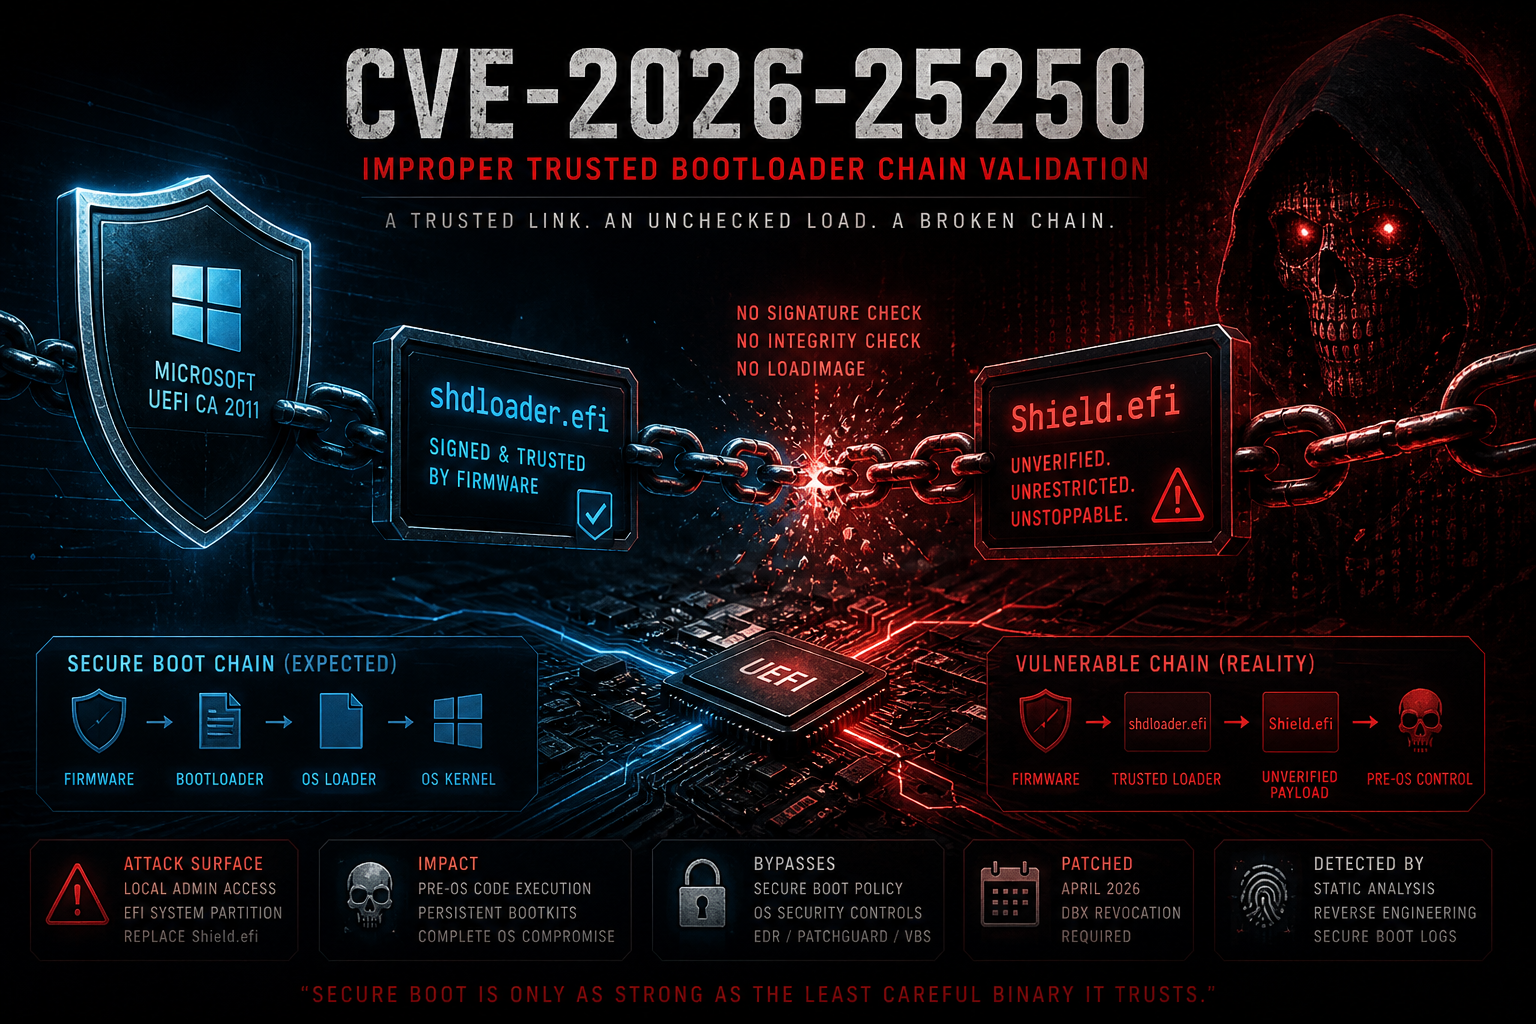 themalwareguardian/cve-2026-25250
Analysis and exploit for CVE-2026-25250, a Secure Boot bypass in Horizon DataSys Reboot Restore where shdloader.efi loads Shield.efi without…
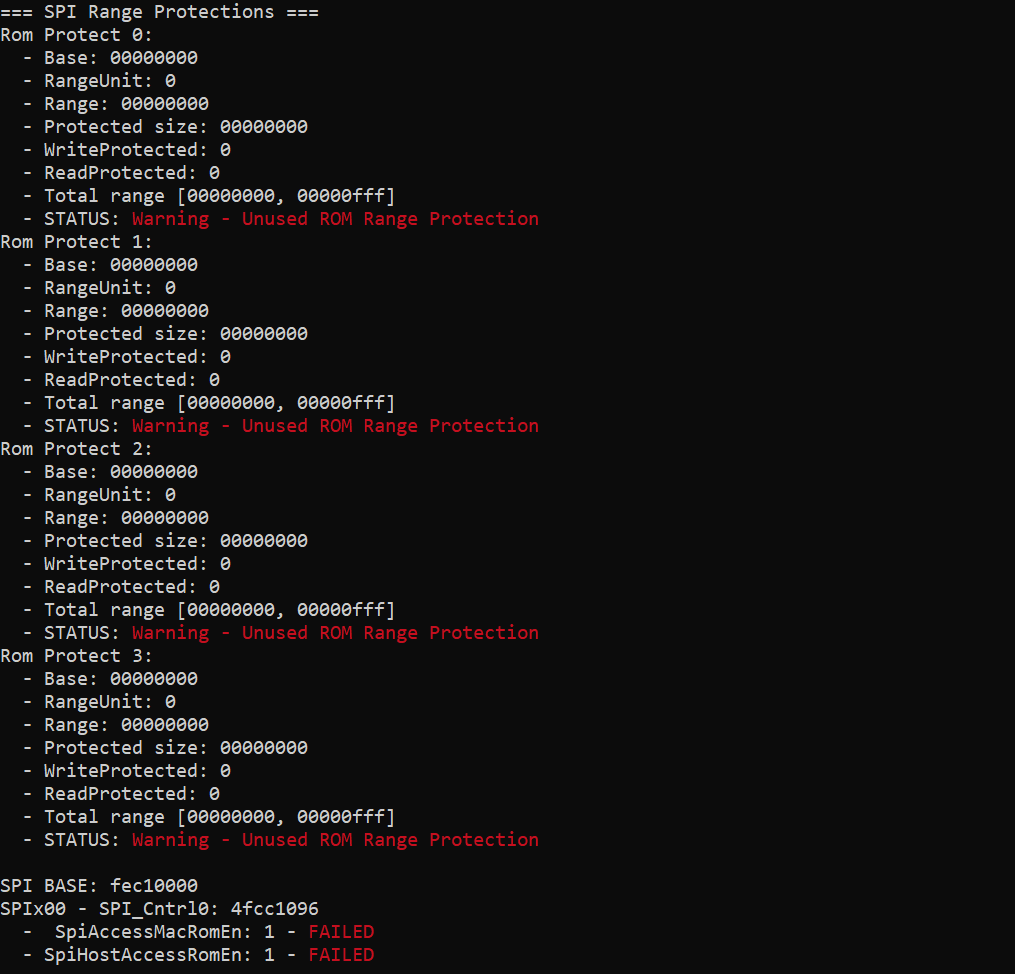 ioactive/platbox
Platform security assessment tool for dumping and analyzing UEFI/SMM registers, PCI config space, physical memory, SPI flash, and S3 bootscripts with…
 xoreaxeaxeax/schrodingers-toctou
Detect compiler-invented memory loads that turn secure C into TOCTOU vulnerabilities. Includes automated source audits, Unicorn-based binary…
 themalwareguardian/cve-2025-4275
Analysis and exploitation of CVE-2025-4275 (Hydr0ph0bia), a Secure Boot trust-chain weakness where firmware variables are used to introduce…
 google/silifuzz
Fuzzes CPU implementations by generating test inputs from software proxies, then executes them on real hardware to detect microarchitecture defects…
 kraxel/virt-firmware
Toolkit for decoding, inspecting, and modifying UEFI firmware volumes and variable stores. Supports secure boot certificate enrollment, PE binary…
 typeconfused/cve-2025-14174-analysis
Analysis and PoC for CVE-2025-14174 - ANGLE Metal OOB write (iOS Safari, macOS Chrome)