

 capstone-engine/capstone
Multi-architecture disassembly framework providing a lightweight, thread-safe API for binary analysis, reverse engineering, and malware research…
 immunityinc/libptrace
An event driven multi-core process debugging, tracing, and manipulation framework.
 qilingframework/qiling
A True Instrumentable Binary Emulation Framework
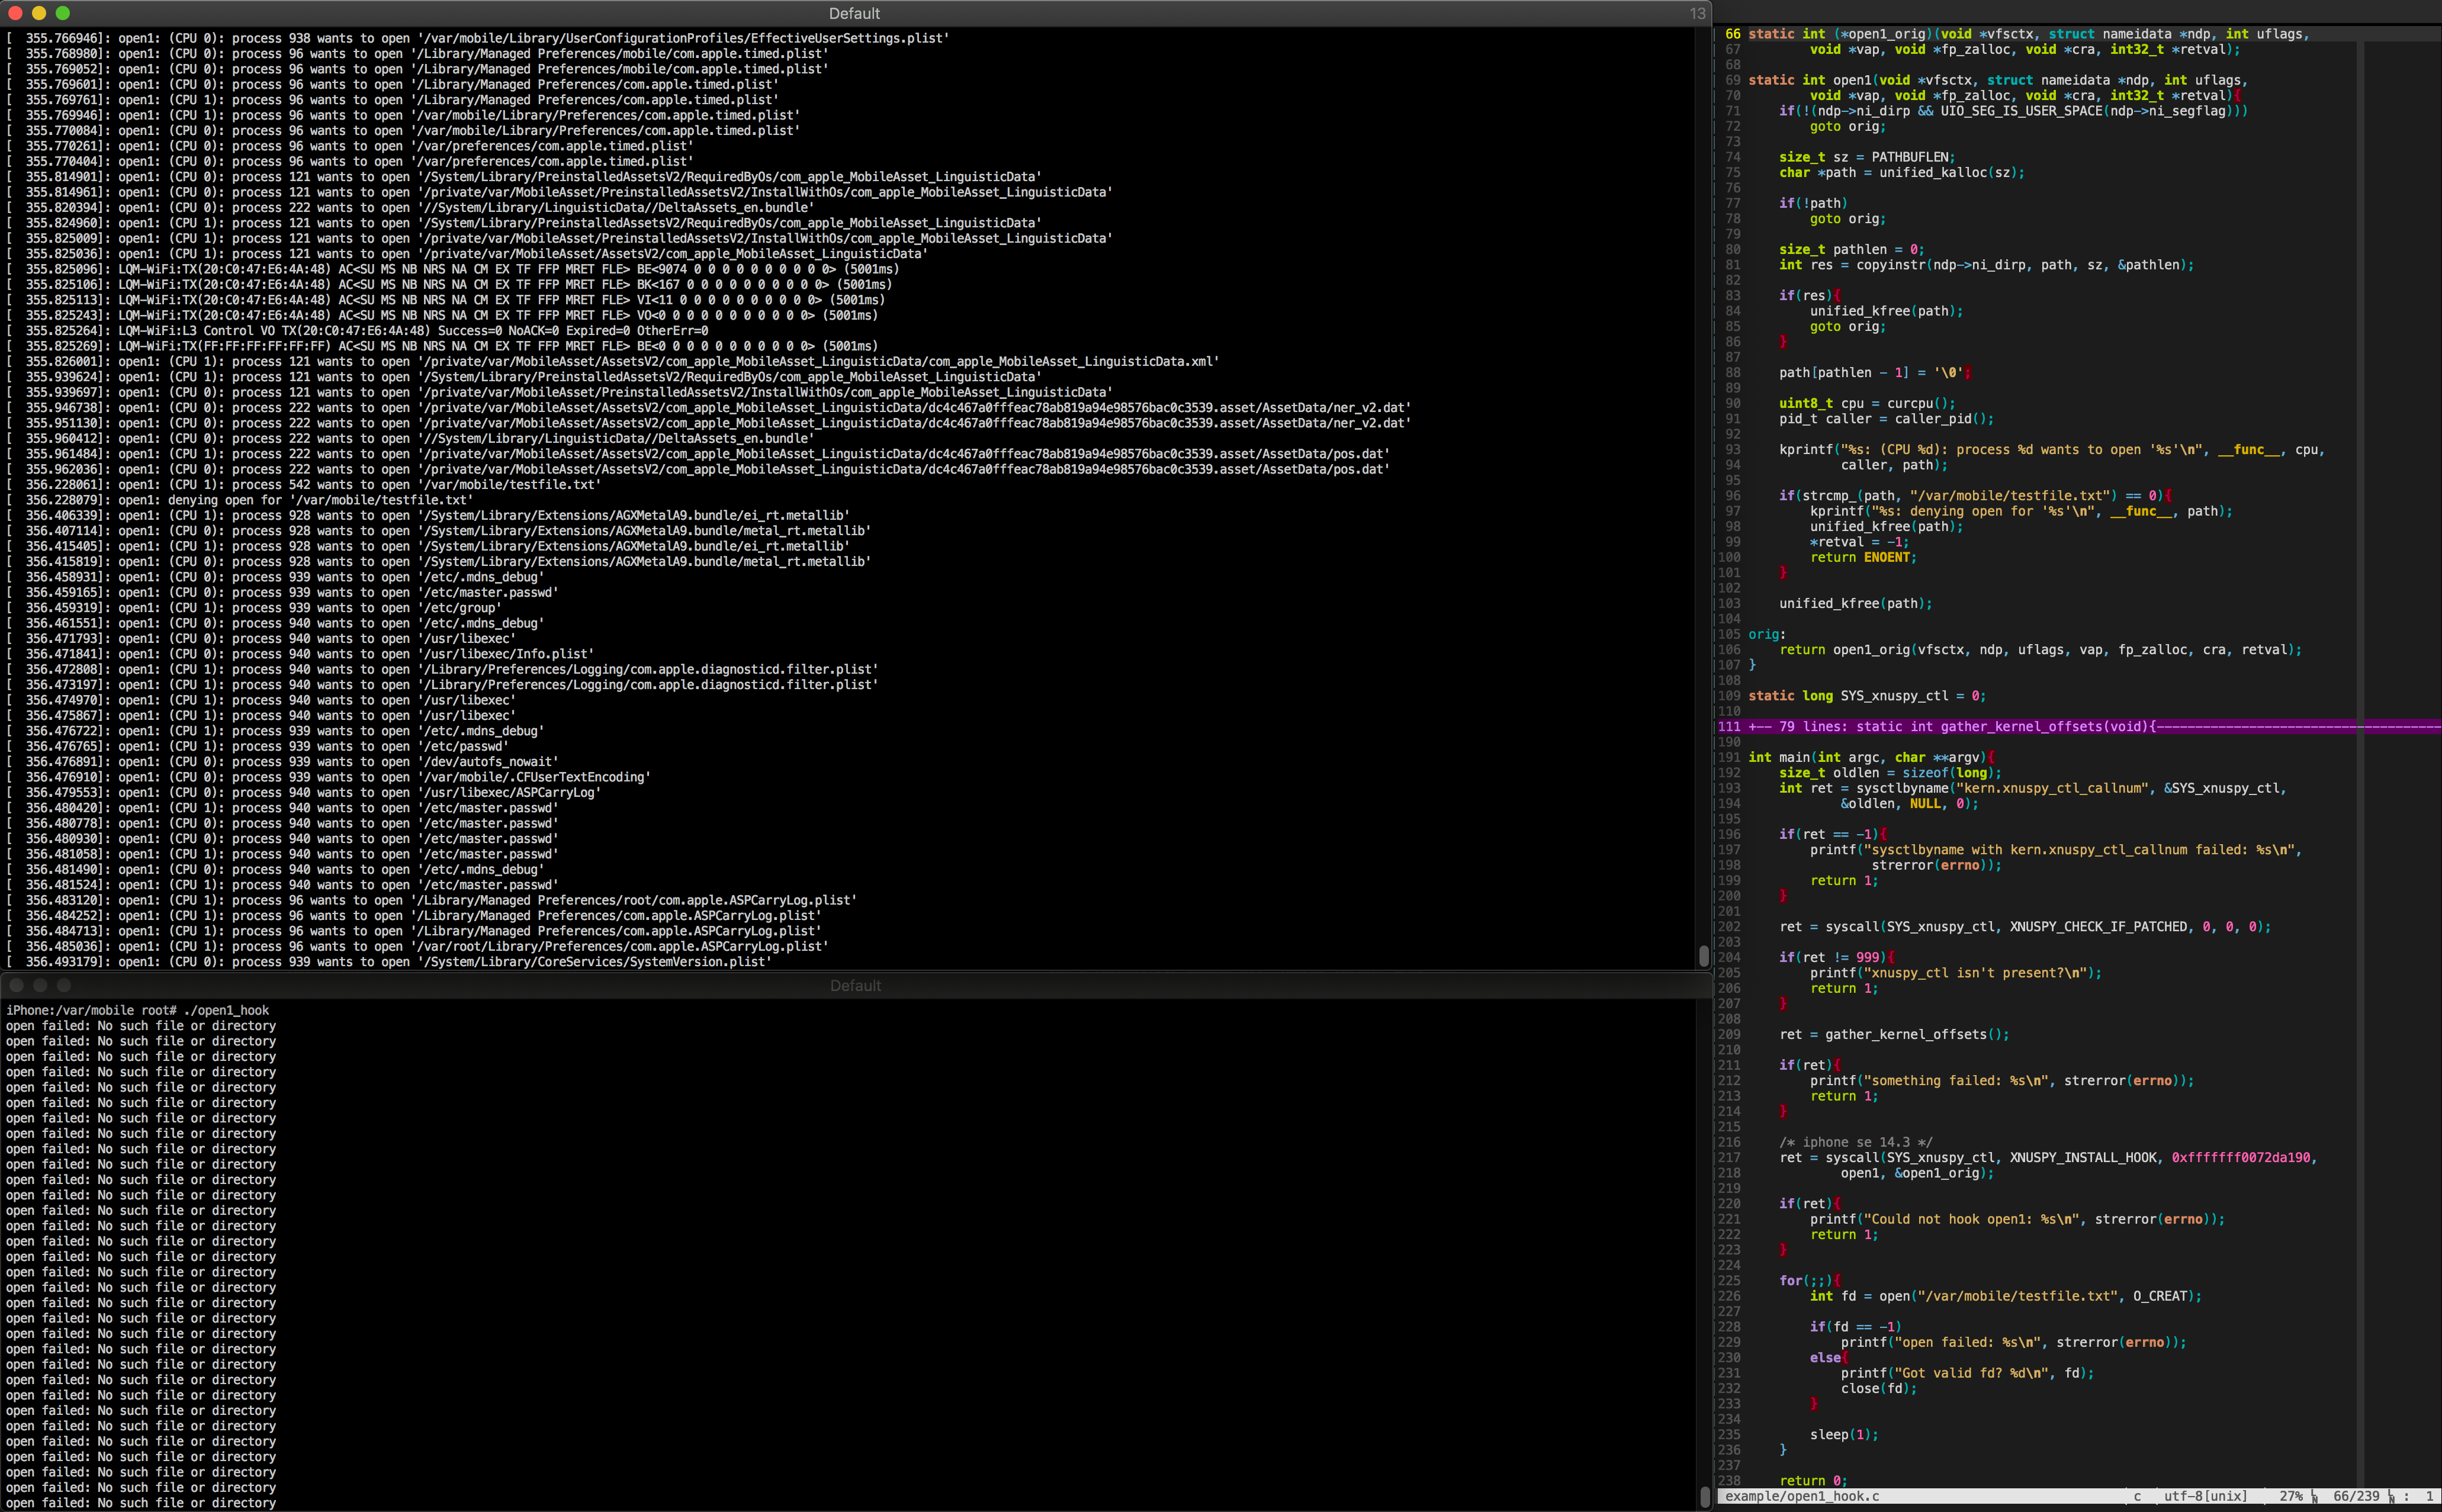 jsherman212/xnuspy
an iOS kernel function hooking framework for checkra1n'able devices
 ohjeongwook/shellcodeemulator
Shellcode emulator written with Unicorn Framework With Process Dump Emulation Environment
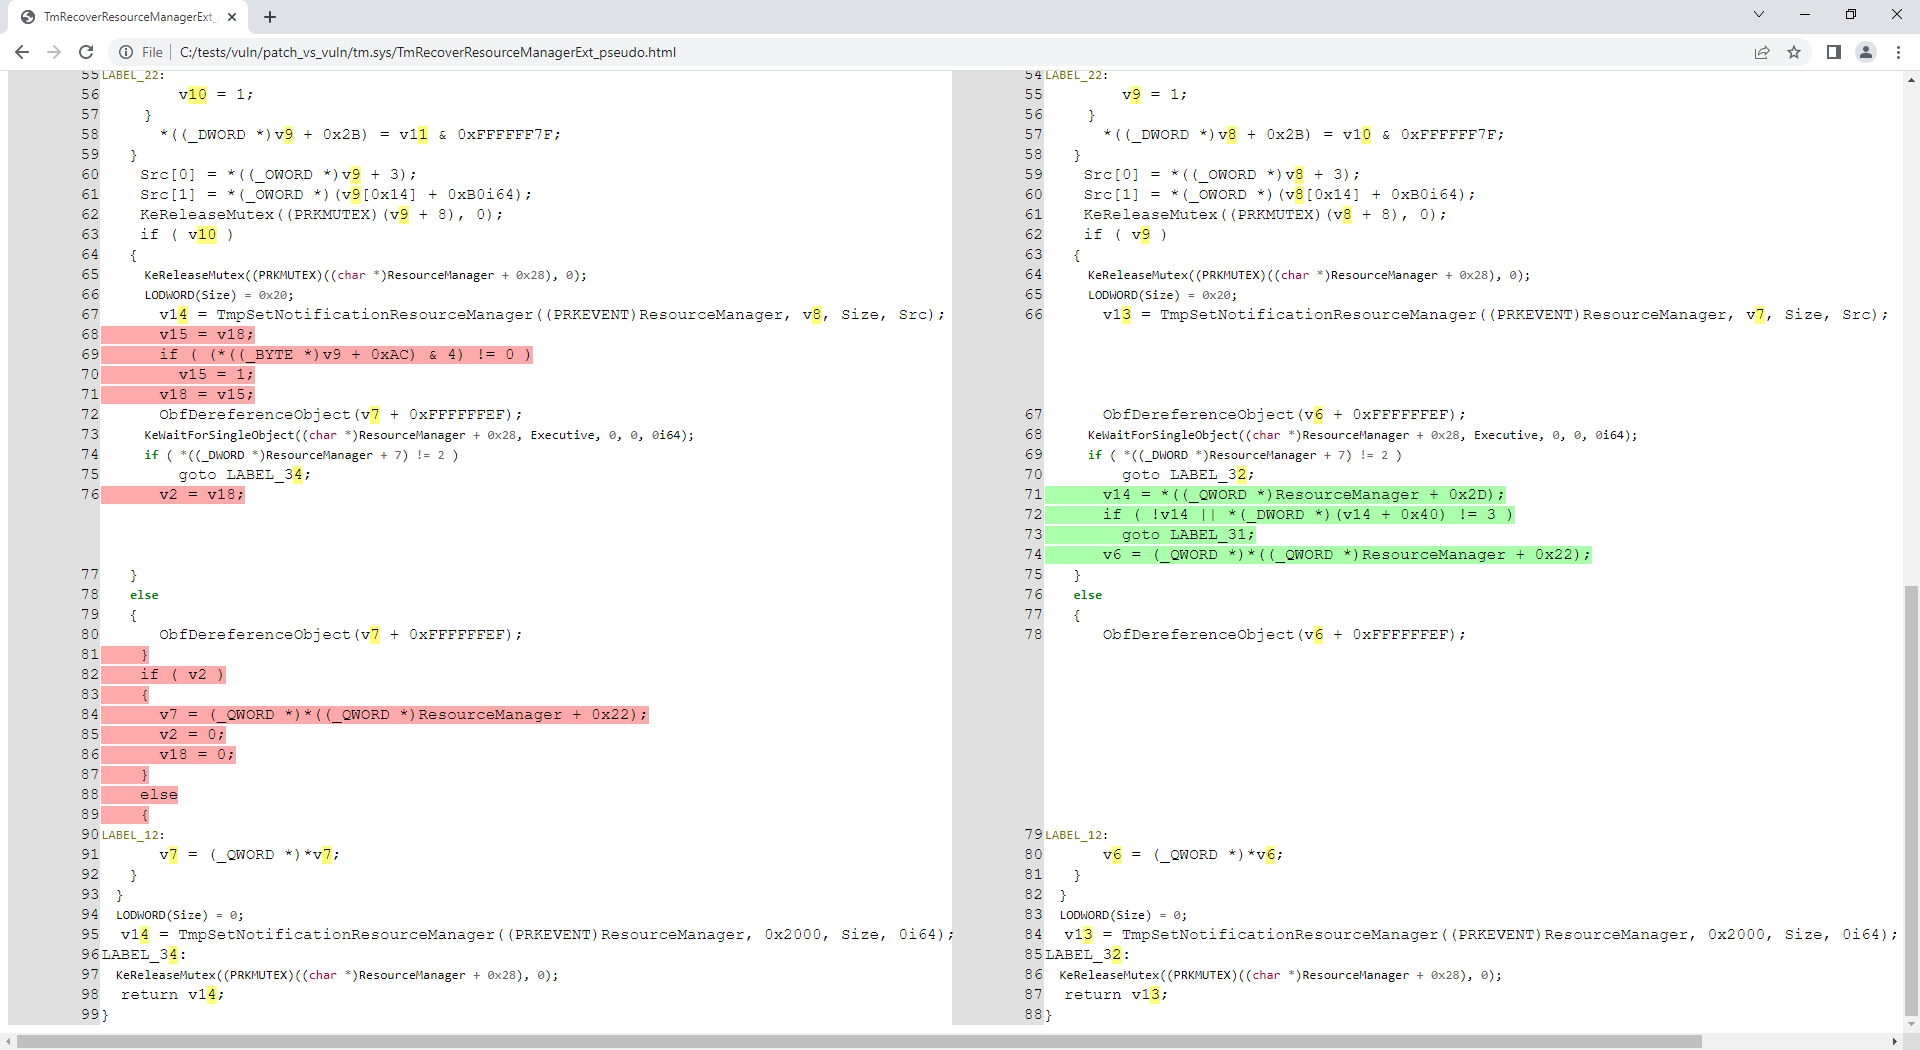 nccgroup/idahunt
idahunt is a framework to analyze binaries with IDA Pro and hunt for things in IDA Pro
 chris1sflaggin/lcsajdump
An ML powered Graph-Based Multi-Architecture Approach for ROP Gadget Detection
 jackofmosttrades/gadgetinspector
A byte code analyzer for finding deserialization gadget chains in Java applications
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 sashs/ropper
Display information about files in different file formats and find gadgets to build rop chains for different architectures (x86/x86_64, ARM/ARM64,…
 thisistfs/rogue-framework
Desktop workbench for AFL++ fuzzing, cross-architecture QEMU emulation, harness development, Ghidra headless analysis, custom mutators, and patch…
 vollragm/ghostdebug
Debugger utilizing stealth hooks to hide from debugger detection
 mandiant/flare-emu
Scriptable binary emulation framework integrating IDA Pro/Radare2 with Unicorn engine for automated malware analysis, string decryption, and code…
 rizinorg/rizin
UNIX-like reverse engineering framework and command-line toolset.
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 angr/angr
A powerful and user-friendly binary analysis platform!
 gadievron/raptor
Autonomous security research framework integrating static analysis, binary analysis, fuzzing, LLM-powered vulnerability validation, exploit…