
pftriage
 idiom/pftriage
Python tool and library to help analyze files during malware triage and analysis.
binary-analysisdigital-forensicsdynamic-analysis-sandboxing+4
79
idiom/pftriagePython tool and library to help analyze files during malware triage and analysis.
 kvesel/zipbrk
Zip file format fuzzer and multi-tool.
 dimareverse/nuitka-static-unpacker
Static-first research tool for unpacking Nuitka-compiled binaries: extracts constants, modules, recovers .pyc files, and generates analysis reports.
 skylot/jadx
Command-line and GUI tool for decompiling Android Dex and APK files into readable Java source code, with resource decoding, deobfuscation, and Smali…
 mandiant/capa
Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
 dsecurity/efiseek
Ghidra plugin that automates UEFI firmware analysis by identifying known GUIDs, protocols, SMI handlers, and interrupt functions, with headless…
 onekey-sec/unblob
Extract files from any kind of container formats
 med0x2e/sigflip
SigFlip is a tool for patching authenticode signed PE files (exe, dll, sys ..etc) without invalidating or breaking the existing signature.
 lolbas-project/lolbas
Living Off The Land Binaries And Scripts - (LOLBins and LOLScripts)
 google/bindiff
Quickly find differences and similarities in disassembled code
 erocarrera/pefile
pefile is a Python module to read and work with PE (Portable Executable) files
 suleram/view8
Decompiles serialized V8 bytecode (JSC files) into high-level readable JavaScript-like code, with support for multiple V8 versions, tree output, and…
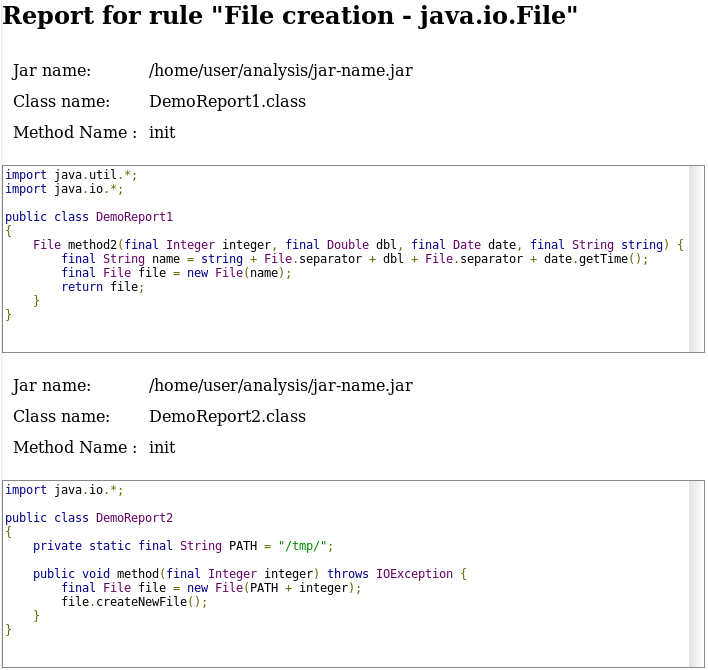 fergarrui/custom-bytecode-analyzer
Java bytecode analyzer customizable via JSON rules
 pealeap/cve-2026-21045_and_cve-2026-21048
Generates crafted TIFF/DNG files to trigger out-of-bounds writes in Samsung's libimagecodec.quram.so, including binary analysis and reproduction…
 kjcracks/clutch
Jailbreak-only iOS utility that decrypts installed app executables and dumps them as .ipa or raw binary files for security research and…
 mhelwig/adwind-decryptor
Simple decrypter for Java AdWind, jRAT, jBifrost trojan
 spiralbl0ck/analysis-for-stage1-shellcode-loader-from-hacking-
Analysis for stage1 shellcode loader from hacking
 hiddenillusion/nomorexor
Tool to help guess a files 256 byte XOR key by using frequency analysis