
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
28 results
efiSeek preview

efiSeek

GitHubdsecurity/efiseek

Ghidra plugin that automates UEFI firmware analysis by identifying known GUIDs, protocols, SMI handlers, and interrupt functions, with headless…
binary-analysisembedded-systems-securityfirmware-analysis+3
407
2 years ago
xnuspy preview

xnuspy

GitHubjsherman212/xnuspy

an iOS kernel function hooking framework for checkra1n'able devices
binary-analysisdebuggersexploitation+1
6065 years ago
pefile preview

pefile

GitHuberocarrera/pefile

pefile is a Python module to read and work with PE (Portable Executable) files
binary-analysisforensicsmalware-analysis+3
2.1k2 days ago
0xGUARD preview

0xGUARD

GitHubgmh5225/0xguard

Simple Anti-cheat library for applications that use C++ on windows. #PastedProtection
anomaly-detectionbinary-analysiscode-analysis+1
22 years ago
ghidra-evm preview

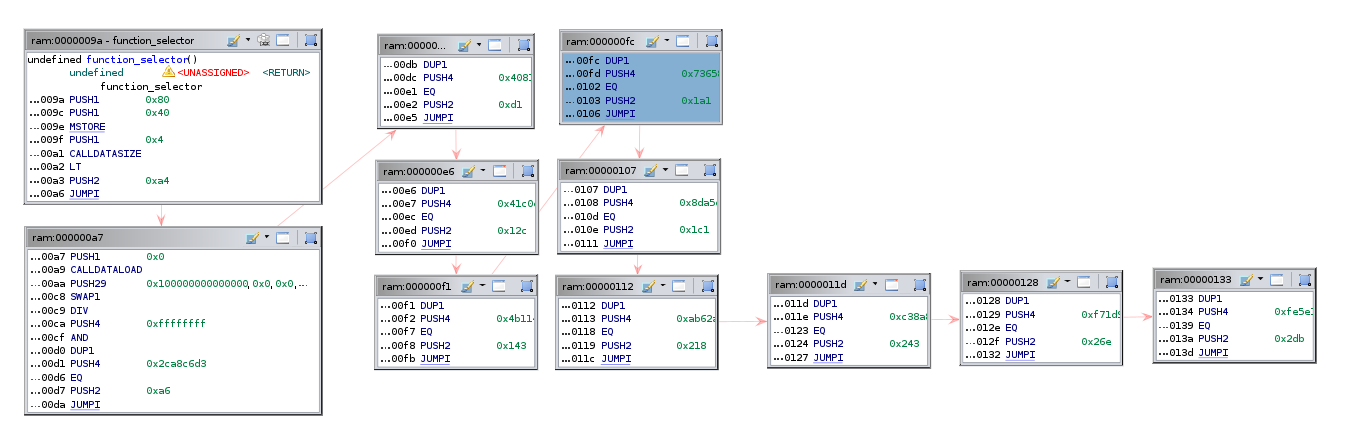
ghidra-evm

GitHubadelapie/ghidra-evm

Ghidra module for disassembling, decompiling, and analyzing Ethereum smart contract bytecode. Detects insecure instructions, extracts hidden methods,…
binary-analysisreverse-engineeringstatic-analysis+1
1495 years ago
DLLHSC preview

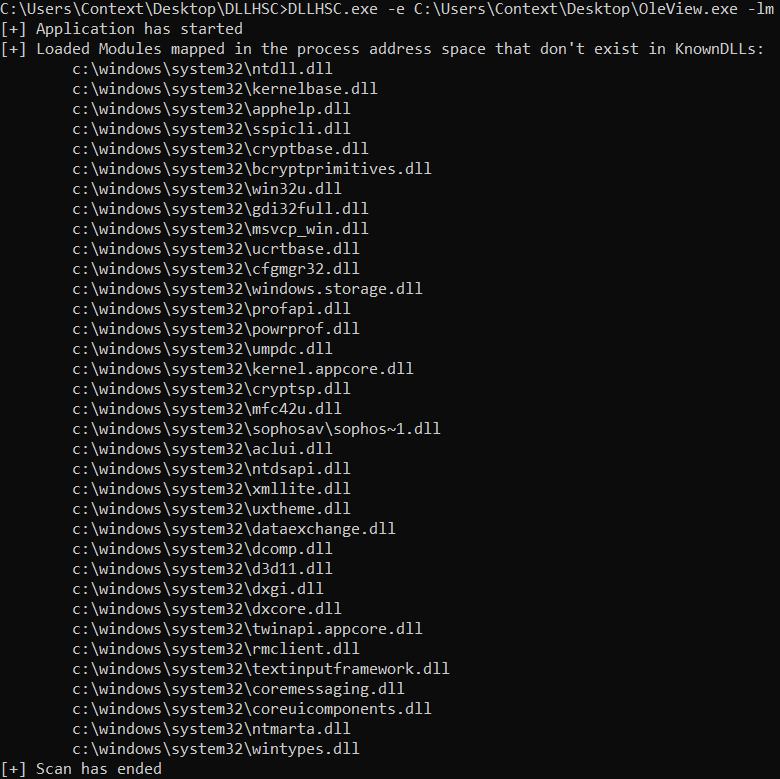
DLLHSC

GitHubctxis/dllhsc

Automated scanner for discovering DLL search order hijacking candidates in Windows executables, featuring import table parsing, runtime module…

binary-analysisexploitationpayload-development+1
1586 years ago
cve-2021-33909 preview

cve-2021-33909

GitHubbaerwolf/cve-2021-33909

This module fixes an issue in the kernels filesystem layer (CVE-2021-33909) by kprobe-replacing vulnerable functions during runtime

binary-analysisexploitationincident-response+1
65 years ago
PowerShellArsenal preview

PowerShellArsenal

GitHubmattifestation/powershellarsenal

A PowerShell Module Dedicated to Reverse Engineering
binary-analysisdebuggersdynamic-analysis-sandboxing+6
9015 years ago
pe_tree preview
Archived

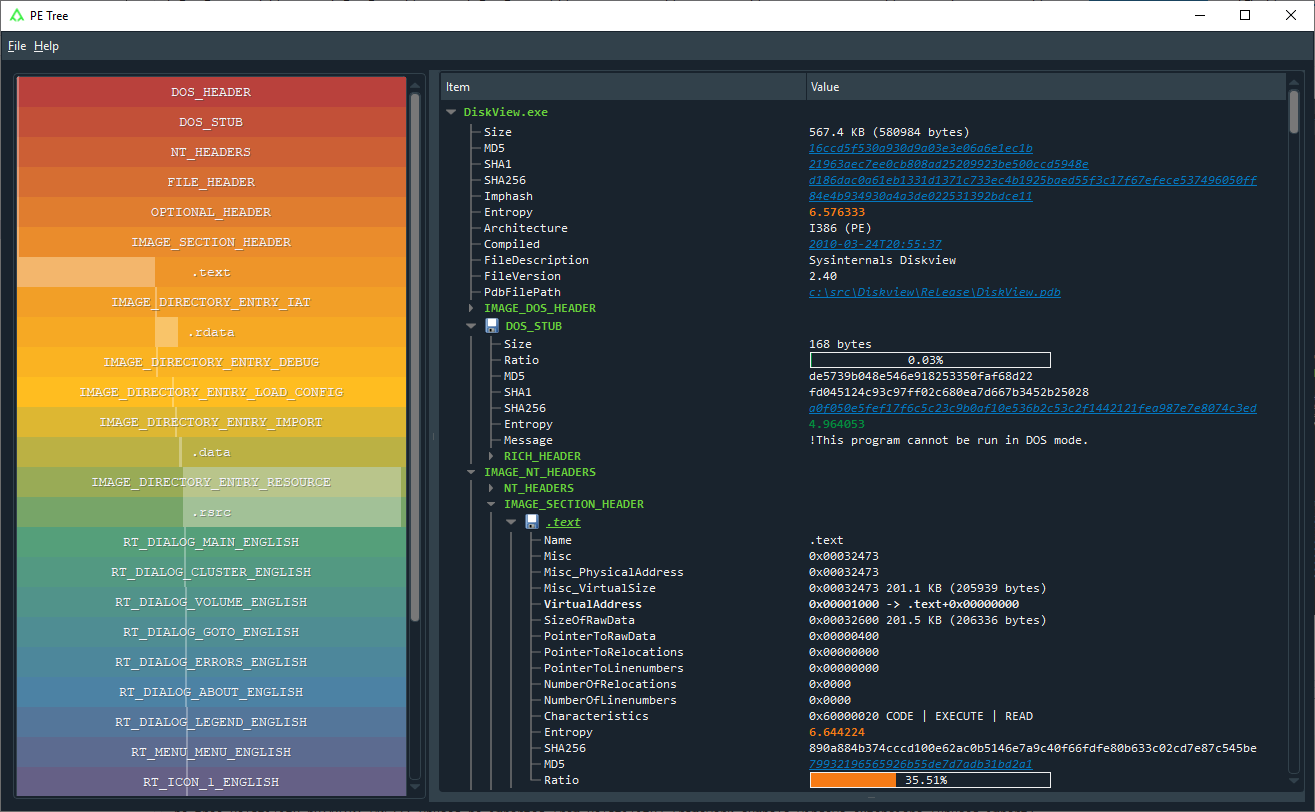
pe_tree

GitHubblackberry/pe_tree

Python module for viewing Portable Executable (PE) files in a tree-view using pefile and PyQt5. Can also be used with IDA Pro and Rekall to dump…
binary-analysisdebuggersdigital-forensics+5
1.3k4 years ago
octopus preview
Archived

octopus

GitHubfuzzinglabs/octopus

Security Analysis tool for WebAssembly module (wasm) and Blockchain Smart Contracts (BTC/ETH/NEO/EOS)

binary-analysisdynamic-analysis-sandboxingfuzzing+2
4912 years ago
uefi-firmware-parser preview

uefi-firmware-parser

GitHubtheopolis/uefi-firmware-parser

Parse BIOS/Intel ME/UEFI firmware related structures: Volumes, FileSystems, Files, etc

binary-analysisembedded-systems-securityfirmware-analysis+2
9284 months ago
Hunt-Sleeping-Beacons preview

Hunt-Sleeping-Beacons

GitHubtheflink/hunt-sleeping-beacons

Callstack scanner that identifies IOCs of unpacked or injected C2 agents by analyzing thread idle behavior, unbacked memory, module stomping, APCs,…
binary-analysisdefensive-toolsforensics+3
6838 months ago
ida_kcpp preview

ida_kcpp

GitHubcellebrite-labs/ida_kcpp

An IDAPython module for enhancing c++ support on top of ida_kernelcache

binary-analysisios-securitymobile-security+2
1441 month ago
patriot preview

patriot

GitHubjoe-desimone/patriot

In-memory stealth detection tool that identifies process hollowing, module stomping, unbacked executable regions, and anomalous CONTEXT structures…

anomaly-detectionbinary-analysisdefensive-tools+3
1654 years ago
Get-PDInvokeImports preview

Get-PDInvokeImports

GitHubdump-guy/get-pdinvokeimports

PowerShell module for automatic detection of P/Invoke, Dynamic P/Invoke, and D/Invoke in .NET assemblies. Reveals unmanaged API calls, MDTokens, and…

binary-analysismalware-analysisreverse-engineering+1
544 years ago
Maverick preview

Maverick

GitHubblacksnufkin/maverick

Adaptix C2 agent using Crystal Palace PIC linker and PICO module system
binary-analysiscommand-and-controlencryption-decryption-tools+5
1204 months ago
Ghidra_v810_v830 preview

Ghidra_v810_v830

GitHub20enderdude20/ghidra_v810_v830

Ghidra processor description module for NEC/Renesas v810 and v830 families
binary-analysisembedded-systems-securityfirmware-analysis+3
76 months ago
magisk-renef preview

magisk-renef

GitHubvichhka-git/magisk-renef

Magisk module that auto-packages renef_server (dynamic instrumentation for Android)

android-securitybinary-analysisdynamic-analysis-sandboxing+3
365 months ago
Previous12Next